
17159661
Description

Quiz by Evelia Escobedo Ramírez, updated more than 1 year ago

|
Created by Evelia Escobedo Ramírez
over 7 years ago
|
|
Question 1
Question
During the initial phase of the Guardium deployment, the Guardium administrator wants to
figure out an ideal time period to purge data from the appliance based on the data load.
Which predefined Guardium report(s) allows the administrator to determine the current
database disk usage of the Guardium Appliance?
Answer
-
Disk UtiI report
-
Aggregation/Archive log
-
DB Server throughput report
-
System Monitor report
Question 2
Question
In a centrally managed environment, while executing the report 'Enterprise Buffer Usage
Monitor', a Guardium administrator gets an empty report. Why is the report empty?
Answer
-
Sniffers are not running on the Collectors.
-
The report is not executed with a remote source on the Collector.
-
The report is not executed with a remote source on the Aggregator.
-
Correct custom table upload is not scheduled on the Central Manager
Question 3
Question
An administrator has a new standalone Guardium appliance that will be placed into
production next week. The appliance will monitor traffic from a number of databases with a
high volume of traffic. The administrator needs to configure the schedule to ensure the
appliance internal database does not get full with incoming data.
Which data management function does the administrator need to configure?
Answer
-
Purge
-
Data Export
-
Data Restore
-
System Backup
Question 4
Question
A Guardium administrator needs to use both CLI and GrdAPI functions to manage the
system.
Which are the two commands that the administrator can use to search for the required
commands and their syntax from within either CLI or GrdAPI?
Answer
-
CLI: commands <search option> GrdApi: grdapi <search option> --help
-
CLI: help <search option> GrdApi: grdapi --help <search option>
-
CLI: commands <search option> GrdAPI: grdapi command <search option>
-
CLI: <search option> -help GrdApi: grdapi <search option> -help=true
Question 5
Question
An administrator just installed the Guardium product using the Guardium ISO image. Which
step must the administrator perform as part of the initial set-up of the new appliance?
Answer
-
Generate the GUI certificate request.
-
Configure network settings on the appliance.
-
Restart the sniffer process from the CLI command prompt.
-
Obtain the passwords for the databases to be monitored by the appliance.
Question 6
Question
During a Guardium deployment planning meeting, the team decides to deploy all S-TAP
agents on all Unix/Linux database systems. A Unix/Linux system administrator team
manager asks a Guardium administrator if there are any differences between Guardium S-
TAPs for AIX and Linux systems that the team should be aware of.
What should be the Guardium administrator's response?
Answer
-
A-TAP is required on all AIX DB Servers.
-
A server reboot is required to capture shared memory traffic from all databases on AIX
-
K-TAP is required on the AIX DB servers. The exact uname -a output is required to determine the correct K-TAP module for the server.
-
K-TAP is required on the Linux DB servers. The exact uname -a output is required to determine the correct K-TAP module for the server.
Question 7
Question
A company wants to deploy S-TAPs for 2 groups of database servers located in 2 different
data centers. The current set of Collectors are fully utilized. The Aggregators and Central
Manager can handle more load.
What should a Guardium administrator recommend?
Answer
-
Deploy 2 new Collectors, 1 in each data center.
-
Connect S-TAPs directly to Aggregators to avoid network latency.
-
Connect S-TAPs directly to the Central Manager to avoid network latency.
-
Deploy 2 new Collectors in the third data center located in between the 2 data centers.
Question 8
Question
A Guardium administrator installed an S-TAP but is not seeing any data in reports on the
collector. The administrator discovered that an Inspection Engine is not configured for that
S-TAP.
What is an Inspection Engine?
Answer
-
A piece of software residing on the Collectors.
-
Another software to be installed on the Database server.
-
The same thing as the policy and it runs on the S-TAP to inspect the traffic in real-time.
-
A set of parameters needed for the S-TAP to define how to monitor traffic for a particular database instance on a server.
Question 9
Question
A Guardium administrator is preparing a command to install Configuration Auditing System
(CAS) on a Linux server using the command line method. Which parameter is required?
Answer
-
dir
-
tapip
-
java-home
-
sqlguardip
Question 10
Question
A Guardium administrator needs to check the traceroute information between one
appliance and its Central Manager. Which CLI command should the administrator run?
Answer
-
iptraf
-
support show iptables
-
show network routes operational
-
support must_gather network_issues
Question 11
Question
A Guardium administrator is preparing commands to install or upgrade an S-TAP using the
command line method. Which operating system can use the ktap_allow_module_combos
parameter for the installation and upgrade?
Answer
-
AIX
-
Linux
-
Solaris
-
HP-UX
Question 12
Question
A Guardium administrator observes certain changes to the configuration and policies. How
would the administrator identify the changes that were made and who made them?
Answer
-
Review the Audit Process Log report.
-
Review the sniffer buffer usage report.
-
Review the /var/log/messages log file.
-
Review the results of 'Detailed Guardium User Activity' report.
Question 13
Question
A Guardium administrator is creating a policy to alert on actions by users that are stored on
an LDAP server. How can the administrator populate a group to use in the policy?
Answer
-
Schedule the LDAP user import into the group.
-
Schedule the LDAP user import from accessmgr and run portal user sync.
-
Schedule the LDAP user import from accessmgr and populate the group from a query.
-
Populate the group from a query in access domain with a condition on the LDAP server as the Server IP.
Question 14
Question
Which use cases are covered with the File Activity Monitoring feature? (Select two.)
Answer
-
Classify sensitive files on mainframe systems.
-
Encrypts database data files on file systems based on policies.
-
Selectively redacts sensitive data patterns in files based on policies.
-
Provides audit trail of access to files, alert and/or block when unauthorized users or processes attempt access.
-
Identifies files containing Personally Identifiable Information (Pll) or proprietary confidential information on Linux Unix Windows (LUW) systems.
Question 15
Question
A Guardium administrator noticed that while the data activity monitoring is working fine, the
Guardium appliance is slower than usual. The administrator wants to check the current
CPU load of the Guardium appliance.
Which predefined Guardium report(s) allows the administrator to determine the current
system CPU load of the Guardium Appliance?
Answer
-
CPU Util report
-
CPU Tracker report
-
Unit summary and CPU Util report
-
Buff Usage Monitor report
Question 16
Question
A Guardium administrator needs to monitor changes to the Oracle configuration file on a
production Oracle database server. Assuming all valid licenses are applied, which
Guardium component does the administrator need to install and where?
Answer
-
Guardium Installation Manager (GIM) on the Database Server
-
Configuration Auditing System (CAS) on the Database Server.
-
Configuration Auditing System (CAS) on the Guardium Collector.
-
Configuration Auditing System (CAS) on the Database Server and on the Guardium Collector.
Question 17
Question
A Guardium administrator must configure real time policy alerts to be sent to a remote
SIEM for every SQL statement run on a sensitive object. There is no requirement for the
data to be viewed or reported on in the Guardium appliance.
Which policy action would achieve that task and store the least amount of data in the
Guardium internal database?
Answer
-
Log Only
-
Alert Only
-
Alert Daily
-
Alert Per Match
Question 18
Question
A Guardium administrator needs to upgrade BUNDLE-STAP on a Linux server to the latest
version using GIM. What parameter should the administrator set to ensure the upgrade will
not require a reboot of the server?
Answer
-
KTAP_ENABLED=1
-
KTAP_NO_ROLLBACK=1
-
KTAP_LIVE_UPDATE=Y
-
KTAP_ALLOW_MODULE_COMBOS=Y
Question 19
Question
An administrator manages a Guardium environment including 4 Collectors exporting data
to an Aggregator. The Collectors export their data daily at 2, 3, 4 and 5 am Eastern
Standard Time (EST) respectively. The Collectors receive traffic every day. The logs on all
the Collectors confirm data is exported daily without errors, and all the exported files
always have data. A Session report is run on the Aggregator at noon EST for data from the
last day.
Which of the following will ensure there is data in the report?
Answer
-
Schedule Data Purge on the Aggregator to run every day after 5 am EST.
-
Schedule Data Import on the Aggregator to run at any time of the day.
-
Schedule Data Import in the Aggregator to run every day before 2 am EST.
-
Schedule Data Import on the Aggregator to run every day at 6 am EST or later.
Question 20
Question
A Guardium administrator is registering a new Collector to a Central Manager (CM). The
registration failed. As part of the investigation, the administrator wants to identify if the
firewall ports are open-How can the administrator do this?
Answer
-
Ask the company's network administrators.
-
Ask IBM technical support to login as root and verify.
-
Login as CLI and execute telnet <ip address><port number>
-
Login as CLI and execute support show port open <ip address> <port number>
Question 21
Question
Simple Mail Transfer Protocol (SMTP) has recently been configured on a Guardium
appliance. How can the administrator confirm the configuration is correct? (Select 2)
Answer
-
Restart the Anomaly detection process
-
Send a test email with CLI diag command
-
From the GUI Alerter page, test the SMTP connection
-
Create a query in access domain to see the sent messages
-
Obtain the syslog file from fileserver and check for SMTP messages
Question 22
Question
The Quick Search window does not show up on the GUI of a standalone Collector What
technical feature should the Guardium administrator check first?
Answer
-
That the Collector has at least 24 GB.
-
That the Collector has at least 32 GB.
-
That the Collector has at least 64 GB.
-
Check the contract and verify whether that feature was purchased.
Question 23
Question
An infrastructure manager is presented with a few new servers that are available to deploy
as a Guardium Collector appliance as part of Guardium project expansion. The Guardium
administrator is asked which server option is best for a Guardium Collector.
Which server option can the Guardium administrator use for the new Collector?
Answer
-
ja64 Intel Processor with quad-core CPU, 32GB memory, 4 NICs, 2TB disk
-
x86_64 Intel Processor with 8-core CPU, 32GB memory, 2 NICs, 1 TB disk
-
x86_64 Intel Processor with dual-core CPU, 24GB memory, and 2 NICs, and 200GB disk
-
Iinuxppc64 Power Processor with 8-core CPU, 24GB memory, and 4 NICs, and 4TB disk
Question 24
Question
AGuardium administrator just finished installing the Guardium product to build a Collector.
The administrator wants to make sure the Collector has the licenses needed to provide
functionality for data activity monitoring, masking and blocking (terminate).
Which of the following lists the minimum licenses the administrator needs to install?
Answer
-
Base Collector license.
-
None, the licenses required are already installed automatically by the Guardium product installer.
-
Base Collector license plus IBM Security Guardium Standard Activity Monitor for Databases (DAM Standard).
-
Base Collector license plus IBM Security Guardium Advanced Activity Monitor for Databases (DAM Advanced).
Question 25
Question
A Guardium administrator needs to install and configure a physical appliance to ensure
network redundancy. Which port should the administrator use to configure IP teaming
(bonding)?
Answer
-
eth1 only
-
eth2 only
-
eth3 only
-
any port
Question 26
Question
A Guardium administrator needs to monitor an Oracle database on a production database
server.
Which component does the administrator need to install on this database server that will
monitor the traffic?
Answer
-
S-TAP
-
Guardium Collector
-
Guardium Installation Manager (GIM)
-
Configuration Auditing System (CAS)
Question 27
Question
Which port must be open for encrypted communication between UNIX S-TAP and
Collector?
Answer
-
9500
-
16016
-
16017
-
16018
Question 28
Question
A Guardium administrator manages portal user synchronization by using a Central
Manager.
When a change is made on the Central Manager such as, for example, adding a Guardium
user to a Guardium group, how long should be allowed for the update to be synced with the
managed units in a fully working environment?
Answer
-
0 minutes
-
15 minutes
-
30 minutes
-
60 minutes
Question 29
Question
A Guardium administrator is using the Classification, Entitlement and Vulnerability
assessment features of the product. Which of the following are correct with regards to
these features? (Select two.)
Answer
-
Vulnerability Assessment reports are populated to the Guardium appliance via S-TAP.
-
Classification for databases and files use the same mechanisms and patterns to search for sensitive data.
-
Entitlement reports are predefined database privilege reports and are populated to the Guardium appliance via S-TAP.
-
Vulnerability Assessment identifies and helps correct security vulnerabilities and threats in the database infrastructures.
-
The classification feature discovers sensitive assets including credit card numbers or national card numbers from various data sources.
Question 30
Question
A Guardium administrator needs to configure EMC Centera for Archive and/or Backup.
In addition to the server IP address, what else is required to establish connection with an
EMC Centera on the network?
Answer
-
ciipID
-
PEA file
-
Shared secret
-
Certificate signed request (CSR)
Question 31
Question
A Guardium administrator needs to use CLI commands to maintain the internal database,
clean static orphans, produce static system reports and to monitor live network traffic
filtered by IP addresses and port numbers.
Which combination of commands should the administrator use for these tasks?
Answer
-
diag and iptraf
-
diag and trace_route
-
iptraf and support must_gather
-
support must_gather and show network verify
Question 32
Question
An administrator previously had an issue with a Guardium system. This was resolved with
the assistance from the IBM Guardium support team, who provided the shell script, a CLI
command and the encrypted key to execute the uploaded shell script.
Which CLI command should the administrator use to review the commands that were
previously run?
Answer
-
fjieserver
-
support execute showlog
-
show log external state
-
support must_gather system_db_info
Question 33
Question
A Guardium administrator is setting up a Collector schedule to export data to an
Aggregator and Archive its data to an Archive storage unit for additional data safety.
Given this scenario, which is true regarding the purge schedule?
Answer
-
The Archive and the Export have independent purge schedules but should not be run at the same time.
-
The Guardium unit would run the Export and Archive before any purge, so you would only see the last purge run each day.
-
It would not be possible to configure both on a Collector, the Aggregator should do the archiving and only export from the Collector.
-
Any time that Data Export and Data Archive are both configured, the purge age must be greater than both the ageat which to export and the ageat which to archive.
Question 34
Question
A Guardium administrator must configure a policy to ignore all traffic from an application
with a known client IP. Due to the high amount of traffic from this application, performance
of the S-TAP and sniffer is a concern.
What action should the administrator use in the rule?
Answer
-
Ignore Session
-
Ignore S-TAP Session
-
Ignore SQL per Session
-
Ignore Responses per Session
Question 35
Question
The last Vulnerability Assessment tests performed in a company were run one year ago.
The company wants to ensure the Vulnerability Assessment tests keep up with the latest
database common vulnerabilities. The company wants to use the Guardium default tests
instead of customer designed tests.
What should the Guardium administrator do to update the tests that will be run?
Answer
-
Install the latest patch on the Guardium appliance.
-
Install the latest released Database Activity Monitor Content.
-
Ask the database administrators to provide the default tests.
-
Ask the Company Security Provider to supply the default tests
Question 36
Question
The guard_tap.ini of a UNIX S-TAP is configured with the following parameters:
firewall_installed=1
firewall_fail_close=1
firewall_default_state=1
firewall_timeout=10
The collector that this S-TAP is sending data to has become unavailable and there is no
failover option configured. A Guardium administrator must communicate the impact of this
outage to users of the monitored database.
What should the administrator advise is the expected behavior for a database session?
Answer
-
The session will not experience any latency or termination.
-
No SQL can be executed and after 10 seconds the session will be terminated.
-
In the first 10 seconds of the session SQL can be executed, then the session is terminated.
-
In the first 10 seconds of the session no SQL can be executed, then the session will work as normal.
Question 37
Question
A Guardium administrator plans to use the Guardium Installation Manager (GIM) to install
and upgrade agents. Where should the administrator manually install the GIM client for the
first time?
Answer
-
Collector
-
Aggregator
-
Database server
-
Central Manager
Question 38
Question
After a successful purge, a Guardium administrator observes that the full percentage of the
Guardium internal database is not decreasing. The administrator uses support show db-
top-tables all and finds the size of the largest tables has decreased significantly.
What should the administrator do?
Answer
-
Increase the retention period and rerun the purge.
-
Rebuild the appliance and restore from the backup.
-
Login to CLI and execute stop inspection-core.
-
Optimize the internal TURBINEdatabase using diag CLI command.
Question 39
Question
A Guardium administrator handles a large environment and has been asked to restore old
data for auditors to review. This old data needs to be restored so that it does not impact the
current data being collected or any merge settings. In order to keep the reports separate
(old datavs current data), the administrator sets up an Investigation Center.
Which is a key requirement for users of the Investigation Center?
Answer
-
The user must be in one of the groups INV_1, INV_2, or INV_3 (case-sensitive).
-
The users must login as one of the predefined user accounts INV_1, INV_2, orlNV_3 (case-sensitive).
-
A separate user must be used with a role of either INV_1, INV_2, or INV_3 (case- sensitive).
-
To correctly configure an investigation user, the user's Last Name must be set to the name of one of the three investigation databases, INV_1, INV_2, or INV_3 (case-sensitive).
Question 40
Question
A Guardium administrator needs to build new appliances with the latest version of
Guardium. How should the administrator obtain the ISO image?
Answer
-
Contact IBM Support.
-
Download from ibm.com
-
Download from IBM Fix Central.
-
Download from IBM Passport Advantage.
Question 41
Question
A Guardium administrator is planning to build an environment that contains an S-TAP with
one primary Collector and one failover Collector. What must the administrator ensure when
setting up this environment?
Answer
-
Both Collectors are centrally managed.
-
There is network connectivity between the S-TAP and both Collectors.
-
Guardium Installation Manager (GIM) is installed on the Database Server.
-
In the guard_tap.ini file of the S-TAP set participate_in_load_balancing=1
Question 42
Question
While looking at the S-TAP Status report on a Collector, a Guardium administrator notices
that the status of the S-TAPs is changing every few minutes. The administrator suspects
that the sniffer is restarting every few minutes and that is why the status change is
happening.
How can the Guardium administrator confirm if the sniffer is restarting every few minutes?
Answer
-
Review the Audit Process Log for 'Sniffer stopped' message.
-
Review the Aggregation/Archive Log for 'Sniffer is restarting message.
-
Review the Scheduled Jobs Exceptions for 'Sniffer process failed' message.
-
Review the Buff Usage Monitor for the column TID to see if it changed every few minutes.
Question 43
Question
Guardium reports are showing multiple records with client ip as 0.0.0.0. Users are unable
to identify which client the connections came from. The Guardium administrator has
identified that the databases are using encryption.
Which column can the administrator add that would help users to better identify the client?
Answer
-
Client OS
-
Client MAC
-
Address ID
-
Analyzed Client IP
Question 44
Question
A Guardium administrator is checking the scheduled jobs exceptions report on a standalone
Collector The following error is repeating every 15 minutes.
java.lang.NumberFormatException: empty String
The administrator also notices that the anomaly detection polling interval is 15 minutes.
What should the administrator do next to contribute troubleshooting the problem?
Answer
-
Pause all scheduled jobs and check if the exception comes back.
-
Identify the alert that is causing the problem by deactivating one alert at a time.
-
Check in the alert builder to see which alerts have accumulation interval of 15 minutes.
-
In the CLI run support must_gather aggjssues and send the file to IBM support.
Question 45
Question
During a Guardium deployment planning meeting, a database administrator indicated that
the mission critical databases were clustered. How should the Guardium administrator
handle S-TAP installation and configuration with respect to clustered databases?
Answer
-
Install S-TAP agents on all active nodes. Set ALL_CAN_CONTROL=1 to failover the S- TAP process to the passive nodes when a database failover occurs.
-
Install S-TAP agents on all active nodes Set WAIT_FOR_DB_EXEC=-1 to set the agent process to failover to the passive node when a database failover occurs.
-
Install S-TAP agents on all active and passive nodes. Set ALL_CAN_CONTROL=0 to disable all passive nodes until a database failover occurs.
-
Install S-TAP agents on all active and passive nodes: Set WAIT_FOR_DB_EXEC>0 on all nodes to start S-TAP processes without waiting for a correct DB home.
Question 46
Question
A Guardium administrator has an issue with Guardium. The administrator has not seen this
particular issue before and needs to get it fixed. To get this resolved, what should the
administrator do?
Answer
-
Log a PMR and request an answer from IBM Support.
-
Log a PMR so IBM Support can contact the customer. Then, while waiting, do a search of the Guardium Knowledge Center and Technotes for known issues and resolutions.
-
Request IBM Support to initiate a remote session and collect what they need to resolve the issue.
-
Search Guardium Knowledge Center and Technotes for known issues and resolutions. Then, if still needed, collect must_gather information and full problem details required for a new PMR so that IBM Support can review the Problem before contacting the customer.
Question 47
Question
Auditors request a report of all unsuccessful login attempts to a database monitored by
Guardium. How should a Guardium administrator create such a report?
Answer
-
Add a failed login rule to the policy.
-
Create a failed login query and report using access domain in Guardium.
-
Create a failed login query and report using exceptions domain in Guardium.
-
Create a failed login query and report using application data domain in Guardium.
Question 48
Question
A Guardium environment is set up to send daily reports to users. The users are complaining
that their report has not been delivered to their inbox for the past week. What is the first
action the Guardium administrator should take in order to diagnose the problem?
Answer
-
Open a ticket with IBM Support.
-
Pause the User Portal Sync process.
-
Check in the Aggregation/Archive log.
-
Check in the Scheduled Job Exceptions.
Question 49
Question
A Guardium administrator manages an environment containing four standalone Collectors.
The administrator has been asked to provide a weekly report showing all Data Manipulation
Language (DML) SQL statements performed by all database administrators on all
databases. The administrator does not want to run the report on each Collector.
What should the administrator do to simplify this task and run the report in only one place
every week?
Answer
-
Replace the 4 Collectors with one Aggregator.
-
Create an Enterprise Report on one Collector combining the data.
-
Add a Guardium Aggregator to the environment. Create and run the report on the Aggregator.
-
Install a Configuration Auditing System (CAS) on each Database Server. Configure the CAS Client to send data to a Collector. Create and run the report on the Collector.
Question 50
Question
A Guardium administrator installed the BUNDLE-STAP module and is monitoring the state
of the install. Which state requires a database server reboot to complete the installation
process?
Answer
-
Ip
-
IP-PR
-
FAILED
-
PENDING-UPDATE
Question 51
Question
A Guardium administrator has rebuilt an appliance, and wants now to restore a backup
image of the entire database, audit data, and all definitions from Data backup.Which CLI
command should the administrator use to accomplish this?
Answer
-
restore config
-
restore system
-
restore pre-patch-backup
-
restore certificate sniffer backup
Question 52
Question
A company is installing S-TAPS on new Database Clusters. The Guardium administrator
was provided with the PVU load of each node. The clusters are in active/passive mode.
The administrator is associating S-TAPs to Collectors using the PVU count.
How should the administrator treat the PVUs of passive nodes?
Answer
-
Include the PVU load of passive nodes.
-
Include half of the passive nodes PVU load.
-
Include a third of the passive nodes PVU load.
-
Not include the PVU load of passive nodes.
Question 53
Question
A company has recently acquired Guardium software entitlement to help meet their
upcoming PCI-DSS audit requirements. The company is entitled to Standard Guardium
DAM offering.
Which of the following features can the Guardium administrator use with the current
entitlement? (Select two.)
Answer
-
Run Vulnerability Assessment reports
-
Generate audit reports using PCI-DSS Accelerator
-
Block and quarantine an unauthorized database connection
-
Mask sensitive PCI-DSS information from web application interface
-
Log and alert all database activities that access PCI-DSS Sensitive Objects.
Question 54
Question
A Guardium administrator needs to configure daily purge.
What is the default value for purge data older than configured on the Guardium appliance?
Answer
-
60 days
-
90 days
-
180 days
-
365 days
Question 55
Question
During the installation phase, the Guardium administartor ensured that the same S-TAP installation procedures were performed on both Oracle 11 and DB2 10.5 systems. They both run on servers with the same version of Linux.
However, during the testing, it was found that all local DB2 connection activities were not captured in the activity report. Meanwhile, all activities on Oracle and all DB2 TCP activities were captured.
What additional step should the administartor take on the database server to capture the missing DB2 shared memory traffic?
Answer
-
Reboot the Linux
-
Restart the DB2 instance
-
Configure the DB2 EXIT Library
-
Configure both the A-TAP and DB2 EXIT Library
Question 56
Question
A Guardium administrator is notified by the Security Incident Event Manager (SIEM) administrator in the organization that Guardium is sending real time policy alerts to the SIEM in an incorrect format.
How can the Guardium administrator verify the format that is being used?
Answer
-
Check the policy violations report.
-
Check on the IBM Knowledge Center to find the template
-
On the GUI Anomaly Detection page, find the active alerts and check their definitions
-
On the GUI Global Profile page, check the Named Template used in the policy action
Question 57
Question
A Guardium administrator is building a policy to monitor files on a datasource. Which actions can the administrator use in the policy? (Select two)
Answer
-
Allow
-
Audit only
-
Alert and Audit Alert per match
-
Ignore S-TAP Session
Question 58
Question
An audit process is currently scheduled to run with User1 as a receiver, the Guardium administrator is asked to replace User1 with User2.
User1 leaves the company. How can the administrator achieve this?
Answer
-
Create another audit process with User2 as the receiver
-
Modify the audit process to add the User2 as the receiver
-
Clone the current audit process, remove User1 and add User2
-
Modify the audit process , delete the User1 as the receiver, and add User2 as the receiver
Question 59
Question
A Guardium administrator has a standalone Collector which is monitoring critical production databases during the working day. Archive are taken daily before work starts and purges take place on all data older than 5 days, This is all working well. However, an auditor arrives at 10:00 am local time and wants to review data from 3 weeks ago.
When can the administrator restore the data for the auditor?
Answer
-
The restore can be done in the morning as it will not impact data collection
-
The restore can be done at lunch time, to avoid a performance impact during high volume of current traffic
-
The restore can only take place outside of working hours as the data cannot be captured during the restore process
-
The restore can be done anytime, but might need to accept some data loss if the performance is impacted too much
Question 60
Question
What is the least free space that the /var partition must have?
Answer
-
10 GB
-
20 GB
-
15 GB
-
30 GB
Question 61
Question
Which is the network adapter recommended for a virtual machine?
Answer
-
E1000
-
VMXNET 3
-
VMXNET 2
-
Flexible
Question 62
Question
Which commands can we use to show the IP address of Guardium system? (Select two)
Answer
-
show network interface all
-
show ip
-
show network verify
-
show network interface inventory
Question 63
Question
How can we display the parameters for a particular grdapi command?
Answer
-
grdapi <command> help
-
grdapi <command> --help
-
<command> --help=true
-
grdapi <command> --help=true
Question 64
Question
How can we display the list of grdapi commands availables? (Select two)
Answer
-
grdapi list
-
grdapi commands
-
grdapi
-
grdapi --help=true
Question 65
Question
Which is the purpose of the system shared secret function? (Select two)
Answer
-
Check for open sessions that have not been active for a specified period of time
-
Control the specific S-TAP hosts whose clients are allowed access to the Guardium system
-
Encrypt files that are exported from the appliance by archive/export activities
-
Establish secure communications between Central Managers and managed units
Question 66
Question
We have a physical environment with 20 Collectors, 3 Aggregators and 1 Central Manager, and we want the same environment but in a virtual machine, how many collectors, aggregators and CM do we need?
Answer
-
20 collectors, 3 aggregators y 1 CM
-
25 collectors, 1 aggregators y 1 CM
-
30 collectors, 4 aggregators y 1 CM
-
45 collectors, 5 aggregators y 1 CM
Question 67
Question
If we need IBM Technical Support, they will use the root password to gain access to the appliance as root.
How can we see the current root password?
Answer
-
support show passkey root
-
show password root
-
show passkey root
-
show password validation
Question 68
Question
Which is the default license that is installed automatically by the Guardium product installer?
Answer
-
DAM Standard
-
Collector
-
DAM Advanced
-
No license is installed
Question 69
Question
How is the upgrade hierarchical of appliances?
Answer
-
Central Manager - Aggregator - Collector
-
Collector - Aggregator - Central Manager
-
S-TAP - Aggregator - Collector
-
Central Manager - Collector - S-TAP
Question 70
Question
Where can we download patches and agents for Guardium system?
Answer
-
IBM Knowledge Center
-
IBM Guardium GUI
-
IBM Fix Central
-
IBM Passport Advantage
Question 71
Question
Which port is for Windows S-TAP heartbeat signal (two-way traffic)?
Answer
-
8076
-
9500
-
8071
-
8075
Question 72
Question
Which port must be open for GIM authenticated TLS, both directions, between the GIM client and the GIM server (on the Central Manager or collector)?
Answer
-
8446
-
8445
-
8081
-
8443
Question 73
Question
What happend if a PMR Severity 4 is sent to IBM Support and the answer doesn't work?
Answer
-
Need to wait 3 days to a new answer
-
IBM change the severity to the next level and is attended the next business day
-
IBM change the severity to the next level and is attended in 3 days
-
IBM Support will resolve the PMR in the next 24 hours
Question 74
Question
What set of commands can be run through the CLI to generate specific information about the state of any Guardium system?
Answer
-
store must_gather
-
show must_gather
-
support must_gather
-
support show must_gather
Question 75
Question
If you receive a HTTP error 403, when you refresh the Guardium GUI, you can disable the Cross-Site Request Forgery (CSRF) protection feature to prevent the error.
How can we do that using CLI commands?
Answer
-
store gui csrf_status off
-
show gui csrf_status off
-
support gui csrf_status off
-
csrf_status off
Question 76
Question
The Guardium internal database is filling up and most of the data is in the GDM_POLICY_VIOLATIONS_LOG table, as a result the Guardium collector is affected.
How can we resolve the problem? (Select two)
Answer
-
Run the CLI command support show db-top-tables all.
-
Check the Incident Management report to identify which policy rule is getting triggered constantly. Then, adjust the policy rule to prevent it from getting triggered as often.
-
Clean data manually from GDM_POLICY_VIOLATIONS_LOG table, use the command support clean policy_violations.
-
Clean data manually from GDM_POLICY_VIOLATIONS_LOG table, use the command support clean DAM_data policy_violations<start_date><end_date>.
Question 77
Question
By default, the log files rotate weekly and keep five files. However, you can change the log rotation strategy for the log files.
What is the purpose of doing this?
Answer
-
To keep more messages in the system.
-
To prevent the file system fills up and approaches 100%
-
To prevent the internal database fills up and approaches 100%
-
To keep more log files in the internal database
Question 78
Question
When you view an Audit report (in .csv format) in Microsoft Excel, you notice that certain rows are filled with unexpected characters. The characters might look similar to what you find in the full SQL column. The problem is not seen in .pdf reports or in GUI reports.
Which could be the cause?
Answer
-
Microsoft Excel has a limit on what a cell can contain of 15,000 characters. If your captured SQL is longer than this limit, it will spill over onto the next row.
-
Microsoft Excel version
-
Microsoft Excel has a limit on what a cell can contain of 32,767 characters. If your captured SQL is longer than this limit, it will spill over onto the next row.
Question 79
Question
While Guardium is decrypting the traffic, the IP address is initially recorded as 0.0.0.0 because the sniffer does not know what the actual IP address is.
What can we do to view the correct client IP for newer traffic?
Answer
-
CLI command show network ip address
-
Add the field Ecryption Type from the session domain to the report
-
Add the field Client IP from the client/server domain to the report
-
Add the field Analyzed Client IP from the client/server domain to the report
Question 80
Question
When you run a report in Guardium, you receive the following error message "Request was interrupted or quota exceeded".
What can we do to resolve the problem? (Select two)
Answer
-
Run the report as an audit process.
-
Restart the Guardium system
-
Divide the report into pieces of a shorter reporting interval. If a report exceeds 4 GB, it causes a MYSQL table data pointer size exhaustion.
-
Wait a few minutes and refresh the report
Question 81
Question
If a rule with a value in the policy command field does not trigger as expected, we need to reconfigure the rule. The cause is a misconfiguration in the command field. The Guardium parser does not consider the command modifiers to be a part of a command. To resolve the problem, the value in the Command field of the rule must match a value exactly that is shown in SQL Verb, plus a wildcard (%) as needed.
Which of the following examples are correct? (Select two)
Answer
-
GRANT%
-
GRANT
-
GRANT% TO PUBLIC
-
%GRANT% ADMIN OPTION%
Question 82
Question
After you upgrade S-TAP using the Guardium Installation Manager (GIM), you cannot configure the database path parameters in the Inspection Engine in Guardium even though the installation results for the module show as successful.
How can we resolve the problem? (Select two)
Answer
-
Set K-TAP_LIVE _UPDATE=Y
-
Set KTAP_ALLOW_MODULE_COMBOS=Y
-
Set ATAP_ENABLED=Y and reinstall the new S-TAP.
-
Set K-TAP_ENABLED=Y and reinstall the new S-TAP.
Question 83
Question
What is the first step to follow when you lost the Guardium accessmgr password and cannot log in to the GUI?
Answer
-
Open a PMR with IBM Guardium support
-
Restart the system
-
Log in to the CLI and run the command: support reset-password accessmgr<N>|random.
-
Use the command: unlock accessmgr
Question 84
Question
How can we convert a Guardium collector to a Central Manager/Aggregator using CLI commands? (Select two)
Answer
-
Using the command "store unit type manager"
-
Using the command "support unit type aggregator"
-
A collector cannot be converted to an aggregator with a CLI command. We need to reinstall the Guardium product and select aggregator as the unit type during installation.
-
A collector cannot be converted to an aggregator with a CLI command. Install the aggregator at the beginning, and convert it to a central manager aggregator with the command "store unit type manager"
Question 85
Question
You attempt to save new settings for the data export and get the error when you click Apply to save the configuration:
"Please correct the following errors and try again:
A test data file could not be sent to this host with the parameters given. Please confirm the hostname or IP address is entered correctly, the host is online, the target directory exists and can be written to by the user given, and the password given is correct for that user"
Which could be the cause of this problem?
Answer
-
The passkey on this system does not match the passkey on the aggregator you are trying to set this system to export to.
-
The shared secret on this system does not match the shared secret on the aggregator you are trying to set this system to export to.
-
There is no a configured password
-
The user and password on this system does not match the user and password on the aggregator you are trying to set this system to export to.
Question 86
Question
A user is disabled in the managed unit. The user's account is re-enabled in the Central Manager but the user is still showing as disabled in the managed unit. The user's account shows as enabled in the Central Manager.
How can we resolve the problem?
Answer
-
Reset users and passwords in the Central Manager
-
Synchronize the current user status between the Central Manager and the managed unit, running a Portal user sync.
-
Contact the IBM Guardium Technical Support for assistance.
-
Synchronize the current user status between the Central Manager and the managed unit, using the CLI command support user sync
Question 87
Question
The operating system fails when you install or upgrade Guardium S-TAP on AIX 6.1. The AIX crash memory dump shows the following stack trace:
What can we do to resolve te problem?
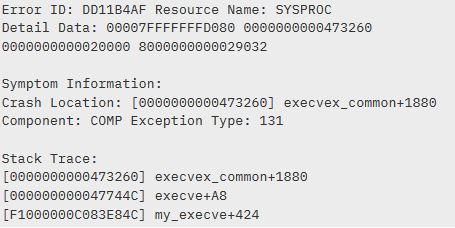
Answer
-
Uninstall and reinstall Guardium S-TAP
-
Apply the Fix Pack AIX 6.1 6100-08-04
-
Apply the Fix Pack S-TAP 6.1 6100-08-04
-
Contact IBM Support
Question 88
Question
After you configure DB2 COMM_EXIT_LIST to use Guardium libguard and restart the DB2 server, you get the following error in the DB2 diag log:
.......
.......
Error opening shared memory area errno=2 err=8
This message indicates that the Guardium library is unable to create the shared memory device that it requires.
What can we do to resolve the problem?
Answer
-
The DB2 instance owner must be added as an authorized user by using the guardctl command.
-
Stop the DB2 instance and start it again
-
Change DB2 version
-
Re-enable DB2 using db2 UPDATE DBM CFG USING COMM_EXIT_LIST libguard_db2_exit_64
Question 89
Question
A Guardium system had a problem and the administrator did the following:
Checked the inspection engine configuration to ensure that the value in the Process Name field matches the result of the following command on the database server: ls -lrt /INFORMIXTMP/.inf.* (For Informix with Linux, example: /home/informix11/bin/oninit )
What was the problem?
Answer
-
A-TAP was not activated
-
Guardium S-TAP did not collect any traffic from any databases.
-
Guardium S-TAP did not collect shared memory traffic from Informix.
-
Guardium library was unable to create the shared memory device that it requires.
Question 90
Question
Which of the following situations could be a common cause for a high CPU or I/O usage? (Select two)
Answer
-
The firewall is disabled
-
An error in the configuration of one of the inspection engines
-
The User ID Chain (UID chain) feature is disabled
-
The K-TAP portion of the S-TAP is sending connection information along with a confirmation request to the S-TAP
Question 91
Question
A message similar to the following is reported one or more times in Guardium system log (messages) or Alerts:
"Nanny process error condition. The nanny process killed the sniffer. VmData was number and was over the limit."
Which could be the cause and the solution for the problem?
Answer
-
The disk space reached over 90% of the available space and the nanny process has restarted it. Reduce traffic to this Guardium system to resolve this message.
-
The sniffer memory usage reached over 50% of the available memory and the nanny process has restarted it. Reduce traffic to this Guardium system to resolve this message.
-
There was a lot of failed logins to the appliance and the nanny process has restarted it. Unlock the login to the applaince to resolve this message.
-
The sniffer memory usage reached over 90% of the available memory and the nanny process has restarted it. Reduce traffic to this Guardium system to resolve this message.
Question 92
Question
What can we do If pages do not load correctly in Guardium GUI?
Answer
-
Restart the database server
-
Refresh the page
-
Restart the GUI or use a different browser
-
Shutdown the system
Question 93
Question
What should we do if the changes are not saved when we add an inspection engine?
Answer
-
Wait for a couple of minutes
-
Check that the parameters are valid
-
Check that the values are valid
-
Uninstall and reinstall the inspection engine
Question 94
Question
What can we do If the Guardium internal database is filling up?
Answer
-
Purge the data manually
-
Restart the collector
-
Purge the data daily
-
Clean the static values
Question 95
Question
The sniffer starts with six threads by default. When you specify a different number of threads, such as 20, by using the command snif -t 20, what could happend? (Select two)
Answer
-
The sniffer cannot connect to the UNIX S-TAP.
-
In the GUI console, the status of the S-TAP is inactive.
-
Nothing happends
-
The connection between sniffer and S-TAP wil be slower
Question 96
Question
The S-TAP cannot start and issues the following messages:
"mmap: Not enough space
Can't initialize: Can't mmap buffer file /tmp/stapbuf/192.168.100.107.0.buf
Error Initializing: Stap cannot initialize SQLGuard queue"
What can we do to resolve the problem?
Answer
-
Reduce the buffer file size for the S-TAP, in the buffer_file_size parameter in the guard_tap.ini file.
-
Reduce the buffer mmap file for the S-TAP, in the buffer_mmap_file parameter in the guard_tap.ini file.
-
Reduce the buffer file size for the S-TAP, in the buffer_file_size parameter in the GIM
-
Change the S-TAP buffer file location
Question 97
Question
What can we do if UNIX S-TAP cannot read more than 16 inspection engines?
Answer
-
Use PCAP for TCP connections by setting ktap_local_tcp=1 and devices=<device_name>
-
Use port_range_start and port_range_end parameters to include all of the required ports in the first inspection engine definition
-
Uninstall and reinstall all the inspection engines
-
Open the port 9500
Question 98
Question
Which could be a cause for the S-TAP on a Windows server does not start and crashes with error ID 1000?
Answer
-
The wrong TAP_IP is specified in the guard_tap.ini file.
-
The wrong SQLGUARD_IP is specified in the guard_tap.ini file.
-
The KTAP_LOCAL_TCP parameter in the guard_tap.ini file must be set in 1
-
The KTAP_LOCAL_TCP parameter in the guard_tap.ini file must be set in 0
Question 99
Question
z/OS S-TAP fails to show active on the Guardium system after you start it for the first time. The policy is correctly configured with a DB2 or IMS Collection Profile and installed. The z/OS S-TAP is properly configured to use port 16022. All messages on the mainframe indicate connectivity.
What can we do to resolve the problem?
Answer
-
Restart the inspection-core by using the CLI command restart inspection-core
-
Restart the services previously stopped by using the CLI command restart stopped_services
-
Ensure the TAP_IP parameter in the guard_tap.ini configuration file matches the correct IP address of the server.
-
Change the port 16022
Question 100
Question
Which could be the problem if the /etc/event.d/ directory does not exist on a system with upstart? (Select two)
Answer
-
The S-TAP agent for DB2 or Oracle does not start automatically on Linux
-
The GIM agent does not install properly
-
The S-TAP agent for Informix does not start automatically on Linux
-
The S-TAP agent does not install properly
Question 101
Question
Which could be a cause for the Guardium Installation Manager (GIM) service does not start in Windows, after a succesful installation?
Answer
-
The disk space is not enough, GIM requires 500 MB minimum of disk space, and 700 MB if FAM module is also being installed.
-
GIM is a 32-bit application. If you are using a Windows 64 bit, GIM might be installed in Program Files instead of Program Files(x86).
-
GIM is a 64-bit application. If you are using a Windows 32 bit, GIM might be installed in Program Files instead of Program Files(x86).
-
The -UNATTENDED parameter is not required for silent or command-line installation.
Question 102
Question
If SSLv3 is enabled on your system, this vulnerability allows attackers to force an SSL/TLS fallback to SSLv3, break the encryption, and intercept network traffic in plaintext. What we should do?
Answer
-
Restart the system
-
Shutdown the database server
-
Close the firewall with Advanced Security
-
Disabling SSLv3 on all systems to prevent the POODLE exploit
Want to create your own Quizzes for free with GoConqr? Learn more.