
Mapa mental
Crypto U12, SSL
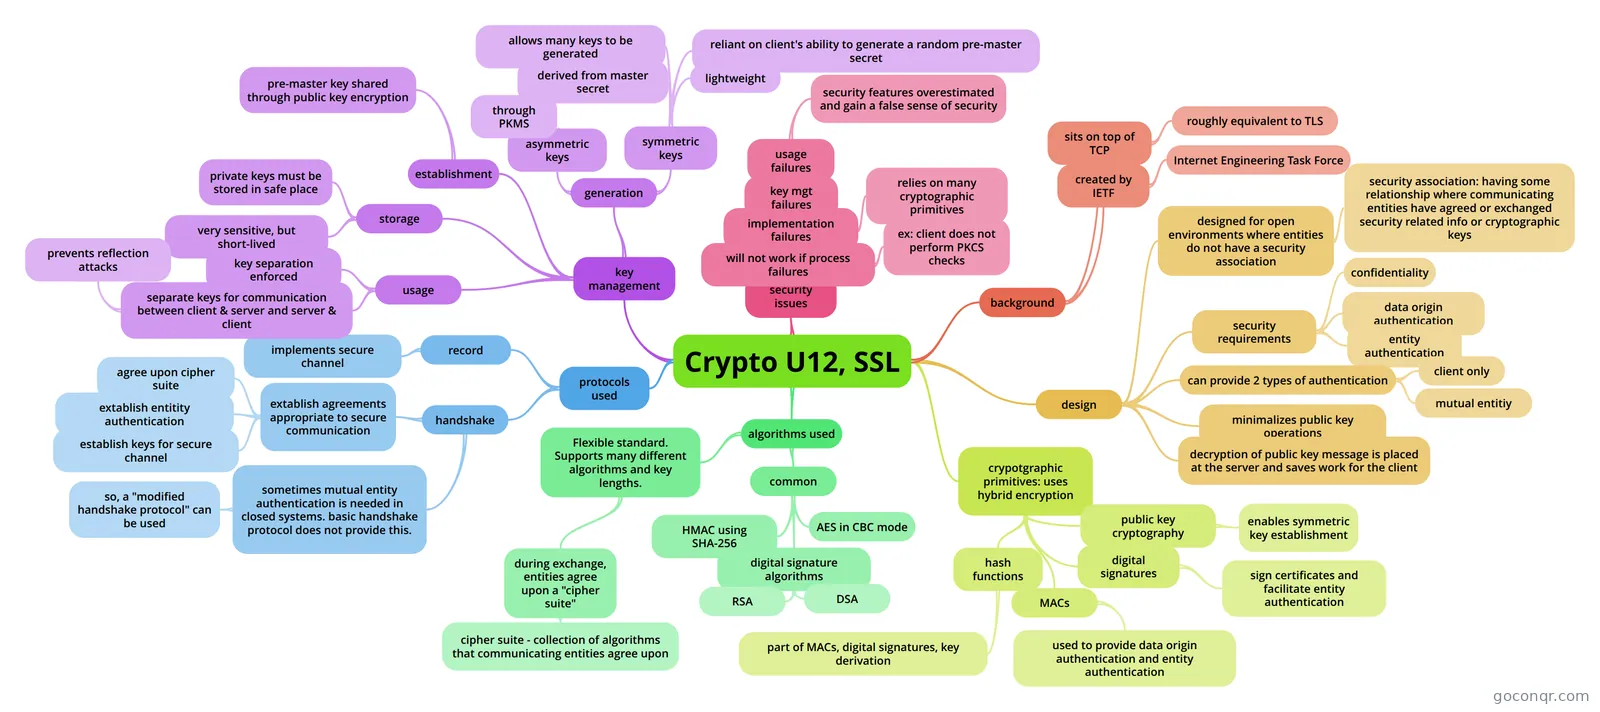
Mind map: SSL
Contenido del mapa
Crypto U12, SSL
background
- sits on top of TCP
- roughly equivalent to TLS
- created by IETF
- Internet Engineering Task Force
- sits on top of TCP
design
- designed for open environments where entities do not have a security association
- security association: having some relationship where communicating entities have agreed or exchanged security related info or cryptographic keys
- security requirements
- confidentiality
- data origin authentication
- entity authentication
- can provide 2 types of authentication
- client only
- mutual entitiy
- minimalizes public key operations
- decryption of public key message is placed at the server and saves work for the client
- designed for open environments where entities do not have a security association
crypotgraphic primitives: uses hybrid encryption
- public key cryptography
- enables symmetric key establishment
- digital signatures
- sign certificates and facilitate entity authentication
- MACs
- used to provide data origin authentication and entity authentication
- hash functions
- part of MACs, digital signatures, key derivation
- public key cryptography
algorithms used
- Flexible standard. Supports many different algorithms and key lengths.
- during exchange, entities agree upon a "cipher suite"
- cipher suite - collection of algorithms that communicating entities agree upon
- during exchange, entities agree upon a "cipher suite"
- common
- AES in CBC mode
- HMAC using SHA-256
- digital signature algorithms
- RSA
- DSA
- Flexible standard. Supports many different algorithms and key lengths.
protocols used
- handshake
- extablish agreements appropriate to secure communication
- agree upon cipher suite
- extablish entitity authentication
- establish keys for secure channel
- sometimes mutual entity authentication is needed in closed systems. basic handshake protocol does not provide this.
- so, a "modified handshake protocol" can be used
- extablish agreements appropriate to secure communication
- record
- implements secure channel
- handshake
security issues
- will not work if process failures
- ex: client does not perform PKCS checks
- implementation failures
- relies on many cryptographic primitives
- key mgt failures
- usage failures
- security features overestimated and gain a false sense of security
- will not work if process failures
key management
- generation
- asymmetric keys
- through PKMS
- symmetric keys
- derived from master secret
- lightweight
- allows many keys to be generated
- reliant on client's ability to generate a random pre-master secret
- asymmetric keys
- establishment
- pre-master key shared through public key encryption
- storage
- private keys must be stored in safe place
- very sensitive, but short-lived
- usage
- key separation enforced
- separate keys for communication between client & server and server & client
- prevents reflection attacks
- generation
Información
- Descripción
- (Unit 12 - Crypto Systems) IYM002 Mapa Mental sobre Crypto U12, SSL, creado por jjanesko el 28/04/2013.
- Creado por
- jjanesko
- Visitas
- 136
- Etiquetas
- Valoración