
Mapa mental
Security Mgt U2, summary
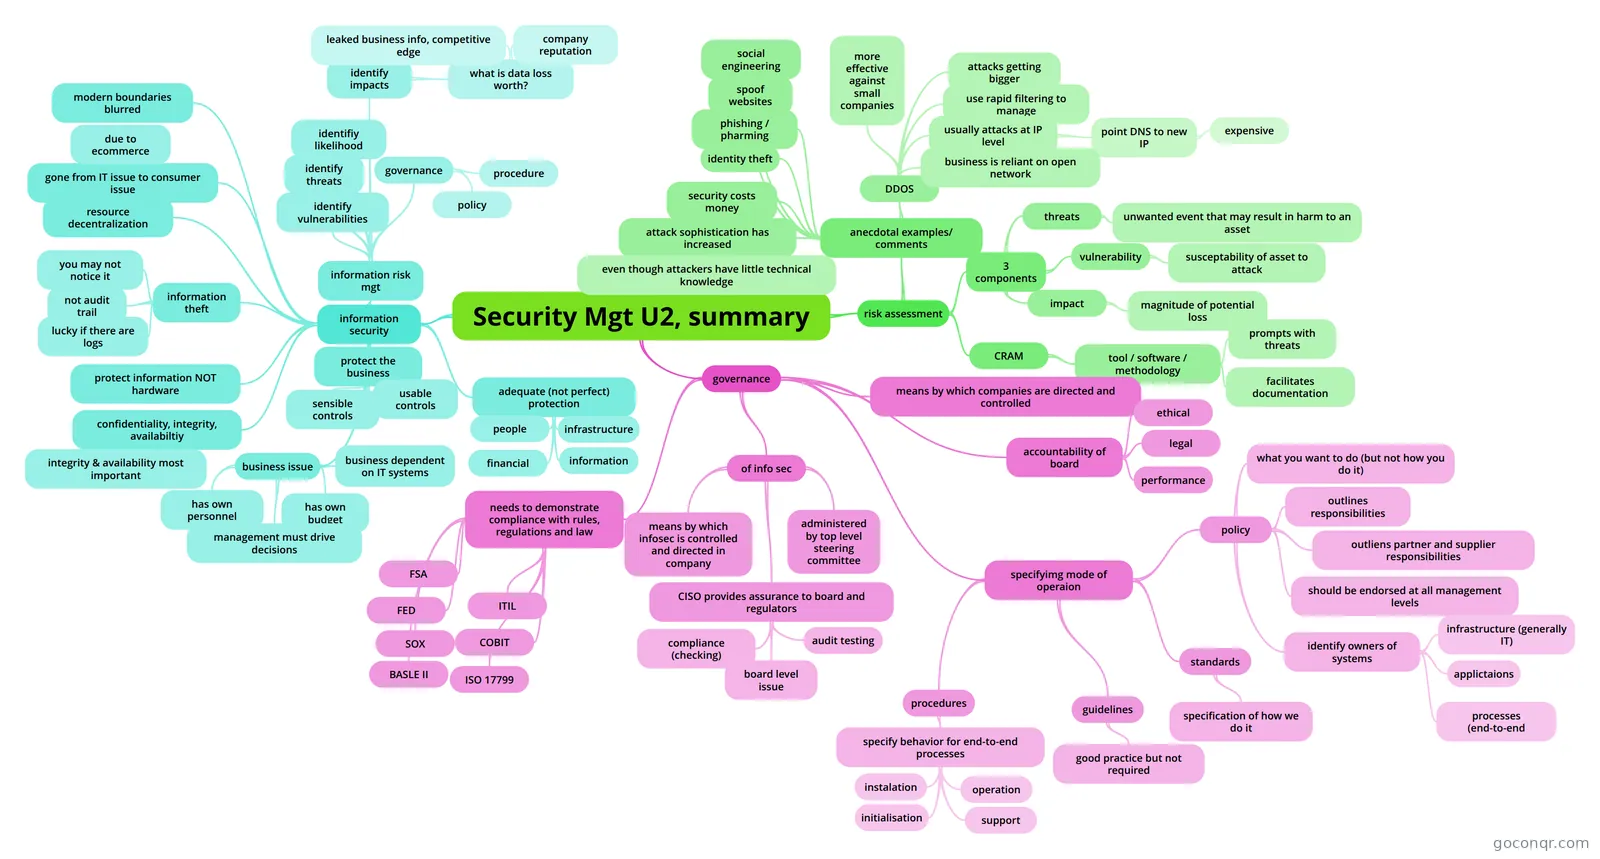
Mind map: Security management unit 2
Conteúdo do mapa
Security Mgt U2, summary
information security
- business issue
- has own budget
- has own personnel
- management must drive decisions
- business dependent on IT systems
- modern boundaries blurred
- gone from IT issue to consumer issue
- due to ecommerce
- confidentiality, integrity, availabiltiy
- integrity & availability most important
- resource decentralization
- protect information NOT hardware
- protect the business
- sensible controls
- usable controls
- information theft
- you may not notice it
- not audit trail
- lucky if there are logs
- information risk mgt
- identify threats
- identifiy likelihood
- identify impacts
- what is data loss worth?
- company reputation
- leaked business info, competitive edge
- what is data loss worth?
- identify vulnerabilities
- governance
- policy
- procedure
- adequate (not perfect) protection
- people
- financial
- information
- infrastructure
- business issue
risk assessment
- 3 components
- threats
- unwanted event that may result in harm to an asset
- vulnerability
- susceptability of asset to attack
- impact
- magnitude of potential loss
- threats
- CRAM
- tool / software / methodology
- prompts with threats
- facilitates documentation
- tool / software / methodology
- anecdotal examples/ comments
- attack sophistication has increased
- even though attackers have little technical knowledge
- security costs money
- identity theft
- phishing / pharming
- spoof websites
- social engineering
- DDOS
- more effective against small companies
- attacks getting bigger
- use rapid filtering to manage
- usually attacks at IP level
- point DNS to new IP
- expensive
- point DNS to new IP
- business is reliant on open network
- attack sophistication has increased
- 3 components
governance
- means by which companies are directed and controlled
- accountability of board
- ethical
- legal
- performance
- needs to demonstrate compliance with rules, regulations and law
- FSA
- FED
- SOX
- BASLE II
- ISO 17799
- COBIT
- ITIL
- of info sec
- means by which infosec is controlled and directed in company
- administered by top level steering committee
- CISO provides assurance to board and regulators
- compliance (checking)
- audit testing
- board level issue
- specifyimg mode of operaion
- policy
- what you want to do (but not how you do it)
- outlines responsibilities
- outliens partner and supplier responsibilities
- should be endorsed at all management levels
- identify owners of systems
- infrastructure (generally IT)
- applictaions
- processes (end-to-end
- standards
- specification of how we do it
- guidelines
- good practice but not required
- procedures
- specify behavior for end-to-end processes
- instalation
- operation
- initialisation
- support
- specify behavior for end-to-end processes
- policy
Informações
- Descrição
- IYM001 Mapa Mental sobre Security Mgt U2, summary, criado por jjanesko em 01-04-2013.
- Criado por
- jjanesko
- Visualizações
- 152
- Tags
- Avaliação