
Mapa mental
FIREWALLs
Conteúdo do mapa
FIREWALLs
Defination
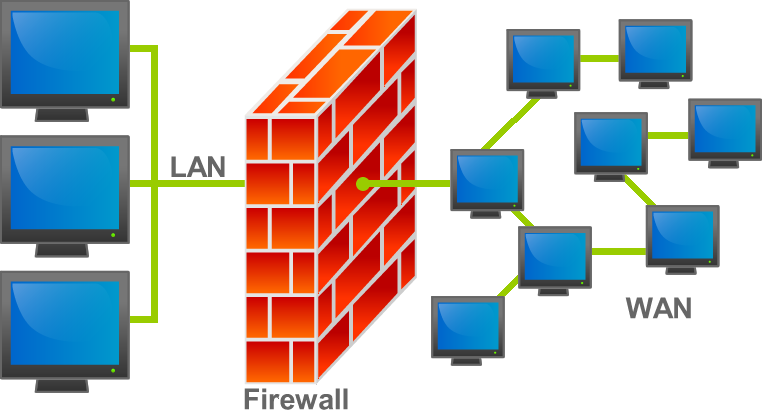
- Firewalls is a device that filter all trafic between a protected ('inside') network and a less trustworthy ('outside) network.
Type
- Packet filtering gateaway
- - control access to packet based on packet address (source/destination), specific transport protocol - just see nametag but not ID (only IP but nit packet content) - cannot choose between allowable TELNET and non-allowable ones - can block packets from ‘outside’ trying to disguise to be one from ‘inside’-> trying to forge an IP address
- Stateful inspection firewalls
- - Maintain state information between packet in an input stream - Can be used to thwart attack that are split across 2 or more packet
- Application proxies
- - a.k.a bastion host - it check the content of a packet and only allows action that are in the given guidelines - caching popular sites for easy retrieval - proxies can be tailored to specific requirements, like logging details of access
- Guards
- -add functionality to a proxy firewall until it starts to look like a guard - receives protocol data, interprets them and passes through - Sort of a twin of proxy firewall
- Personal firewalls
- -an application program that runs on a workstation to block unwanted traffic - The user decides who to trust and who not to
- Packet filtering gateaway
Level
- Application
- - More advanced - Can make decisions based on the actual content of the packet (not just header) - Can contain extra authentication and do more logging - Acts as a proxy: must "understand" the application protocols used. Needs a proxy server for each application type such as HTTP, FTP, Telnet, etc.
- Network
- - often in hardware - make decision based on the source, destination address and ports in individual packets - a specially configured router -very fast -transparent to user
- Application