
Quiz
Quix10 - D7 - 50Q
Fragen in diesem Quiz (50)
1Joe wants to test a program he suspects may contain malware. What
technology can he use to isolate the program while it runs?- AA. ASLR
- BB. Sandboxing
- CC. Clipping
- DD. Process isolation
2Which one of the following is an example of a manmade disaster?
- AA. Hurricane
- BB. Flood
- CC. Mudslide
- DD. Transformer failure
3Which of the following is not true about the (ISC)2 code of ethics?
- AA. Adherence to the code is a condition of certification.
- BB. Failure to comply with the code may result in revocation of
certification. - CC. The code applies to all members of the information security
profession. - DD. Members who observe a breach of the code are required to report
the possible violation.
4Javier is verifying that only IT system administrators have the ability
to log on to servers used for administrative purposes. What principle
of information security is he enforcing?- AA. Need to know
- BB. Least privilege
- CC. Two-person control
- DD. Transitive trust
5Which one of the following is not a basic preventative measure that
you can take to protect your systems and applications against attack?- AA. Implement intrusion detection and prevention systems.
- BB. Maintain current patch levels on all operating systems and
applications. - CC. Remove unnecessary accounts and services.
- DD. Conduct forensic imaging of all systems.
6Tim is a forensic analyst who is attempting to retrieve information
from a hard drive. It appears that the user attempted to erase the data,
and Tim is trying to reconstruct it. What type of forensic analysis is
Tim performing?- AA. Software analysis
- BB. Media analysis
- CC. Embedded device analysis
- DD. Network analysis
7Which one of the following is an example of a computer security
incident?- AA. Completion of a backup schedule
- BB. System access recorded in a log
- CC. Unauthorized vulnerability scan of a file server
- DD. Update of antivirus signatures
8Which one of the following technologies would provide the most
automation of an inventory control process in a cost-effective manner?- AA. IPS
- BB. WiFi
- CC. RFID
- DD. Ethernet
9Connor’s company recently experienced a denial of service attack that
Connor believes came from an inside source. If true, what type of
event has the company experienced?- AA. Espionage
- BB. Confidentiality breach
- CC. Sabotage
- DD. Integrity breach
10What type of attack is shown in the following figure?
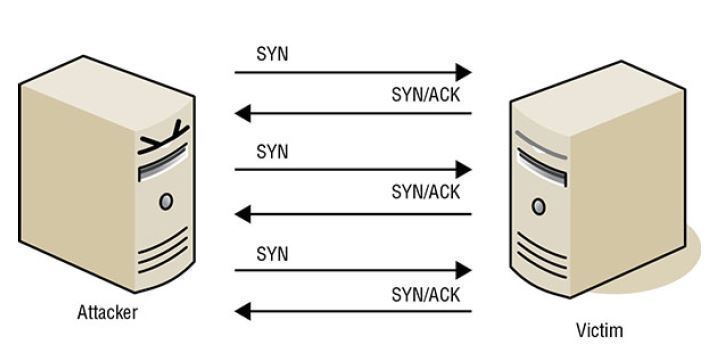
- AA. SYN flood
- BB. Ping flood
- CC. Smurf
- DD. Fraggle
11Florian is building a disaster recovery plan for his organization and
would like to determine the amount of time that a particular IT service
may be down without causing serious damage to business operations.
What variable is Florian calculating?- AA. RTO
- BB. MTD
- CC. RPO
- DD. SLA
12Which one of the following statements best describes a zero-day
vulnerability?- AA. An attacker who is new to the world of hacking
- BB. A database attack that places the date 00/00/0000 in data tables
in an attempt to exploit flaws in business logic - CC. An attack previously unknown to the security community
- DD. An attack that sets the operating system date and time to
00/00/0000 and 00:00:00
13Which one of the following is not a canon of the (ISC)2 code of ethics?
- AA. Protect society, the common good, necessary public trust and
confidence, and the infrastructure. - BB. Promptly report security vulnerabilities to relevant authorities.
- CC. Act honorably, honestly, justly, responsibly, and legally.
- DD. Provide diligent and competent service to principals.
- AA. Protect society, the common good, necessary public trust and
14During an incident investigation, investigators meet with a system
administrator who may have information about the incident but is not
a suspect. What type of conversation is taking place during this
meeting?- AA. Interview
- BB. Interrogation
- CC. Both an interview and an interrogation
- DD. Neither an interview nor an interrogation
15What technique has been used to protect the intellectual property in
the following image?
- AA. Steganography
- BB. Clipping
- CC. Sampling
- DD. Watermarking
16You are working to evaluate the risk of flood to an area and consult the
flood maps from the Federal Emergency Management Agency
(FEMA). According to those maps, the area lies within a 200-year
flood plain. What is the annualized rate of occurrence (ARO) of a flood
in that region?- AA. 200
- BB. 0.01
- CC. 0.02
- DD. 0.005
17Which one of the following individuals poses the greatest risk to
security in most well-defended organizations?- AA. Political activist
- BB. Malicious insider
- CC. Script kiddie
- DD. Thrill attacker
18Veronica is considering the implementation of a database recovery
mechanism recommended by a consultant. In the recommended
approach, an automated process will move database backups from the
primary facility to an offsite location each night. What type of database
recovery technique is the consultant describing?- AA. Remote journaling
- BB. Remote mirroring
- CC. Electronic vaulting
- DD. Transaction logging
19When designing an access control scheme, Hilda set up roles so that
the same person does not have the ability to provision a new user
account and assign superuser privileges to an account. What
information security principle is Hilda following?- AA. Least privilege
- BB. Separation of duties
- CC. Job rotation
- DD. Security through obscurity
20Reggie recently received a letter from his company’s internal auditors
scheduling the kickoff meeting for an assessment of his group. Which
of the following should Reggie not expect to learn during that
meeting?- AA. Scope of the audit
- BB. Purpose of the audit
- CC. Expected timeframe
- DD. Expected findings
21Which one of the following events marks the completion of a disaster
recovery process?- AA. Securing property and life safety
- BB. Restoring operations in an alternate facility
- CC. Restoring operations in the primary facility
- DD. Standing down first responders
22Melanie suspects that someone is using malicious software to steal
computing cycles from her company. Which one of the following
security tools would be in the best position to detect this type of
incident?- AA. NIDS
- BB. Firewall
- CC. HIDS
- DD. DLP
23Brandon observes that an authorized user of a system on his network
recently misused his account to exploit a system vulnerability against a
shared server that allowed him to gain root access to that server. What
type of attack took place?- AA. Denial of service
- BB. Privilege escalation
- CC. Reconnaissance
- DD. Brute force
24Carla has worked for her company for 15 years and has held a variety
of different positions. Each time she changed positions, she gained
new privileges associated with that position, but no privileges were
ever taken away. What concept describes the sets of privileges she has
accumulated?- AA. Entitlement
- BB. Aggregation
- CC. Transitivity
- DD. Isolation
25During what phase of the incident response process do administrators
take action to limit the effect or scope of an incident?- AA. Detection
- BB. Response
- CC. Mitigation
- DD. Recovery
26Ann is a security professional for a midsized business and typically
handles log analysis and security monitoring tasks for her
organization. One of her roles is to monitor alerts originating from
the organization’s intrusion detection system. The system typically
generates several dozen alerts each day, and many of those alerts
turn out to be false alarms after her investigation.
This morning, the intrusion detection system alerted because the
network began to receive an unusually high volume of inbound
traffic. Ann received this alert and began looking into the origin of
the traffic.
At this point in the incident response process, what term best
describes what has occurred in Ann’s organization?- AA. Security occurrence
- BB. Security incident
- CC. Security event
- DD. Security intrusion
27handles log analysis and security monitoring tasks for her
organization. One of her roles is to monitor alerts originating from
the organization’s intrusion detection system. The system typically
generates several dozen alerts each day, and many of those alerts
turn out to be false alarms after her investigation.
This morning, the intrusion detection system alerted because the
network began to receive an unusually high volume of inbound
traffic. Ann received this alert and began looking into the origin of
the traffic.
Ann continues her investigation and realizes that the traffic generating
the alert is abnormally high volumes of inbound UDP traffic on port
53. What service typically uses this port?- AA. DNS
- BB. SSH/SCP
- CC. SSL/TLS
- DD. HTTP
28Ann is a security professional for a midsized business and typically
handles log analysis and security monitoring tasks for her
organization. One of her roles is to monitor alerts originating from
the organization’s intrusion detection system. The system typically
generates several dozen alerts each day, and many of those alerts
turn out to be false alarms after her investigation.
This morning, the intrusion detection system alerted because the
network began to receive an unusually high volume of inbound
traffic. Ann received this alert and began looking into the origin of
the traffic.
As Ann analyzes the traffic further, she realizes that the traffic is
coming from many different sources and has overwhelmed the
network, preventing legitimate uses. The inbound packets are
responses to queries that she does not see in outbound traffic. The
responses are abnormally large for their type. What type of attack
should Ann suspect?- AA. Reconnaissance
- BB. Malicious code
- CC. System penetration
- DD. Denial of service
29Ann is a security professional for a midsized business and typically
handles log analysis and security monitoring tasks for her
organization. One of her roles is to monitor alerts originating from
the organization’s intrusion detection system. The system typically
generates several dozen alerts each day, and many of those alerts
turn out to be false alarms after her investigation.
This morning, the intrusion detection system alerted because the
network began to receive an unusually high volume of inbound
traffic. Ann received this alert and began looking into the origin of
the traffic.
Now that Ann understands that an attack has taken place that violates
her organization’s security policy, what term best describes what has
occurred in Ann’s organization?- AA. Security occurrence
- BB. Security incident
- CC. Security event
- DD. Security intrusion
30Gordon suspects that a hacker has penetrated a system belonging to
his company. The system does not contain any regulated information,
and Gordon wishes to conduct an investigation on behalf of his
company. He has permission from his supervisor to conduct the
investigation. Which of the following statements is true?- AA. Gordon is legally required to contact law enforcement before
beginning the investigation. - BB. Gordon may not conduct his own investigation.
- CC. Gordon’s investigation may include examining the contents of hard
disks, network traffic, and any other systems or information
belonging to the company. - DD. Gordon may ethically perform “hack back” activities after
identifying the perpetrator.
- AA. Gordon is legally required to contact law enforcement before
31Frank is seeking to introduce a hacker’s laptop in court as evidence
against the hacker. The laptop does contain logs that indicate the
hacker committed the crime, but the court ruled that the search of the
apartment that resulted in police finding the laptop was
unconstitutional. What admissibility criteria prevents Frank from
introducing the laptop as evidence?- AA. Materiality
- BB. Relevance
- CC. Hearsay
- DD. Competence
32Which one of the following tools provides an organization with the
greatest level of protection against a software vendor going out of
business?- AA. Service level agreement
- BB. Escrow agreement
- CC. Mutual assistance agreement
- DD. PCI DSS compliance agreement
33Fran is considering new human resources policies for her bank that
will deter fraud. She plans to implement a mandatory vacation policy.
What is typically considered the shortest effective length of a
mandatory vacation?- AA. Two days
- BB. Four days
- CC. One week
- DD. One month
34Which of the following events would constitute a security incident?
1. An attempted network intrusion
2. A successful database intrusion
3. A malware infection
4. A violation of a confidentiality policy
5. An unsuccessful attempt to remove information from a secured area- AA. 2, 3, and 4
- BB. 1, 2, and 3
- CC. 4 and 5
- DD. All of the above
35Which one of the following traffic types should not be blocked by an
organization’s egress filtering policy?- AA. Traffic destined to a private IP address
- BB. Traffic with a broadcast destination
- CC. Traffic with a source address from an external network
- DD. Traffic with a destination address on an external network
36Allie is responsible for reviewing authentication logs on her
organization’s network. She does not have the time to review all logs,
so she decides to choose only records where there have been four or
more invalid authentication attempts. What technique is Allie using to
reduce the size of the pool?- AA. Sampling
- BB. Random selection
- CC. Clipping
- DD. Statistical analysis
37You are performing an investigation into a potential bot infection on
your network and wish to perform a forensic analysis of the
information that passed between different systems on your network
and those on the Internet. You believe that the information was likely
encrypted. You are beginning your investigation after the activity
concluded. What would be the best and easiest way to obtain the
source of this information?- AA. Packet captures
- BB. Netflow data
- CC. Intrusion detection system logs
- DD. Centralized authentication records
38Which one of the following tools helps system administrators by
providing a standard, secure template of configuration settings for
operating systems and applications?- AA. Security guidelines
- BB. Security policy
- CC. Baseline configuration
- DD. Running configuration
39What type of disaster recovery test activates the alternate processing
facility and uses it to conduct transactions but leaves the primary site
up and running?- AA. Full interruption test
- BB. Parallel test
- CC. Checklist review
- DD. Tabletop exercise
40During which phase of the incident response process would an analyst
receive an intrusion detection system alert and verify its accuracy?- AA. Response
- BB. Mitigation
- CC. Detection
- DD. Reporting
41In what virtualization model do full guest operating systems run on
top of a virtualization platform?- AA. Virtual machines
- BB. Software-defined networking
- CC. Virtual SAN
- DD. Application virtualization
42What level of RAID is also known as disk mirroring?
- AA. RAID-0
- BB. RAID-1
- CC. RAID-5
- DD. RAID-10
43Bruce is seeing quite a bit of suspicious activity on his network. It
appears that an outside entity is attempting to connect to all of his
systems using a TCP connection on port 22. What type of scanning is
the outsider likely engaging in?- AA. FTP scanning
- BB. Telnet scanning
- CC. SSH scanning
- DD. HTTP scanning
44The historic ping of death attack is most similar to which of the
following modern attack types?- AA. SQL injection
- BB. Cross-site scripting
- CC. Buffer overflow
- DD. Brute-force password cracking
45Roger recently accepted a new position as a security professional at a
company that runs its entire IT infrastructure within an IaaS
environment. Which one of the following would most likely be the
responsibility of Roger’s firm?- AA. Configuring the network firewall
- BB. Applying hypervisor updates
- CC. Patching operating systems
- DD. Wiping drives prior to disposal
46What technique can application developers use to test applications in
an isolated virtualized environment before allowing them on a
production network?- AA. Penetration testing
- BB. Sandboxing
- CC. White box testing
- DD. Black box testing
47Gina is the firewall administrator for a small business and recently
installed a new firewall. After seeing signs of unusually heavy network
traffic, she checked the intrusion detection system, which reported
that a SYN flood attack was under way. What firewall configuration
change can Gina make to most effectively prevent this attack?- AA. Block SYN from known IPs.
- BB. Block SYN from unknown IPs.
- CC. Enable SYN-ACK spoofing at the firewall.
- DD. Disable TCP.
48Renee is a software developer who writes code in Node.js for her
organization. The company is considering moving from a self-hosted
Node.js environment to one where Renee will run her code on
application servers managed by a cloud vendor. What type of cloud
solution is Renee’s company considering?- AA. IaaS
- BB. CaaS
- CC. PaaS
- DD. SaaS
49What type of trust relationship extends beyond the two domains
participating in the trust to one or more of their subdomains?- AA. Transitive trust
- BB. Inheritable trust
- CC. Nontransitive trust
- DD. Noninheritable trust
50Timber Industries recently got into a dispute with a customer. During
a meeting with his account representative, the customer stood up and
declared, “There is no other solution. We will have to take this matter
to court.” He then left the room. When does Timber Industries have an
obligation to begin preserving evidence?- AA. Immediately
- BB. Upon receipt of a notice of litigation from opposing attorneys
- CC. Upon receipt of a subpoena
- DD. Upon receipt of a court order
Informationen
- Beschreibung
- Good Luck!
- Autor
- Requiemdust Sheena
- Sprache
- English
- Aufrufe
- 269
- Schlagwörter
- Bewertung
- 5,0 von 5 · 1 Bewertung Bewerte dieses Quiz