
Quiz
Module 09: Firewalls Exam ECSS
Dieses Quiz enthält Fragetypen, die sich im gewohnten Player öffnen.
Fragen in diesem Quiz (34)
1Firewall is a [blank_start]hardware or software[blank_end] or [blank_start]combination[blank_end] of both designed to prevent unauthorized access
- Ahardware or software
- Bcombination
2Número de NIC`s
bastion - [blank_start]1[blank_end]
Screen/DMZ - [blank_start]2 o 3[blank_end]
Multil - [blank_start]several[blank_end]- A1
- B2 o 3
- Cseveral
3ROLES OF FIREWALLS IN NETWORK:
[blank_start]SINGLE POINT:[blank_end] todo tráfico ha de pasar por allí
[blank_start]CONTROLLED TRAFFIC[blank_end] : mirar credenciales (user-pass)
[blank_start]LOGGED TRAFFIC[blank_end]: se guardan logs de todo lo que pasa- ASINGLE POINT:
- BCONTROLLED TRAFFIC
- CLOGGED TRAFFIC
4Firewalls:
filter the network traffic based on source or destination [blank_start]addresses and ports[blank_end]
perform User [blank_start]Authentication[blank_end]
Prevent Network from [blank_start]scanning[blank_end]
Perform [blank_start]NAT[blank_end]
Filtering [blank_start]services and packets[blank_end]- Aaddresses and ports
- BAuthentication
- Cscanning
- Dservices and packets
- ENAT
5Firewall Architecture
[blank_start]Bastion Host: The bastion host[blank_end] designed for defending the network against attacks. It acts
as a mediator between inside and outside networks.
[blank_start]Screened Subnet: A screened subnet[blank_end] is a protected network created with a two- or three-
homed firewall behind a screening firewall, and is a name commonly used to refer to the
[blank_start]DMZ[blank_end]. When using a three-homed firewall, connect the first interface to the Internet, the
second interface to the DMZ, and the third to the intranet.
The advantage of screening a subnet away from the intranet is that public requests can be
responded to without allowing traffic into the intranet.
[blank_start]Multi-homed Firewall:[blank_end] A multi-homed firewall is a node with multiple NICs that connects
to two or more networks. Connect each interface to the separate network segments
logically and physically. A multi-homed firewall helps in increasing efficiency and reliability
of an IP network.- ABastion Host: The bastion host
- BScreened Subnet: A screened subnet
- CMulti-homed Firewall:
- DDMZ
61 firewall - [blank_start]bastion[blank_end]
2 o 3 firewall- [blank_start]Screened Subnet o DMZ.[blank_end]
multi NIC`s conecting several networks - [blank_start]Multi-home firewall[blank_end]- Abastion
- BScreened Subnet o DMZ.
- CMulti-home firewall
7LEE CON DETENIMIENTO
TIPOS DE FIREWALL
Packet Filtering Firewall
OSI: Layer 3 Network
TCP/IP: Red/capa2
Mira los puertos, las ip, los protocolos, intrfaces etc || reglas de filtrado
NO MIRA DENTRO DEL PAQUETE
Circuit-Levek Gateaway Firewall
OSI: Layer 5 Session
TCP/IP: APP capa/4
comprueban TCP Handshaking (secuencia ), que la sesión sea legítima
No filtran paquetes individuales
hide information about the private network they protect (supongo que esto todos)
Se denomina GW ya que los paquetes cuando se pasan y son recibidos parece que se han originado en ese GW
Application-Level Firewall / Proxy Server
OSI: APP layer , 7
al ser en la app level, puede examinar comanos, como post y get de http
SE MIRA DENTRO DEL PAQUETE Y SE RECREAR/HACE OTRO NUEVO
IMPORTANTE: si los paquetes de una app que se recibe no pueden usar proxy, se descartan.
Statefull Multilayer Inspection Firewall
OSI: app, session, network
Combinaciónde Packet, Circuit gateway and App firewalls
Determina si la sesión es genuina, se evalua los contenido del paquete y se aplican reglas de filtrado
Añade de manera dinámica reglas en función a la comunicación que recibe
EJEPLO: FTP que se conect al 21 y transferencia en 20. TRANSFORMA y crea una regla para que ene lugar del 20 se use un puerto aleatorio
CISCO PIX es este tipo de firewall
Proporciona logs y tracks de esas transformaciones
ROLES OF FIREWALLS IN NETWORK:
SINGLE POINT: todo tráfico ha de pasar por allí
CONTROLLED TRAFFIC : mirar credenciales (user-pass)
LOGGED TRAFFIC: se guardan logs de todo lo que pasa- ARichtig
- BFalsch
8Esquema FIREWALLS
Capa OSI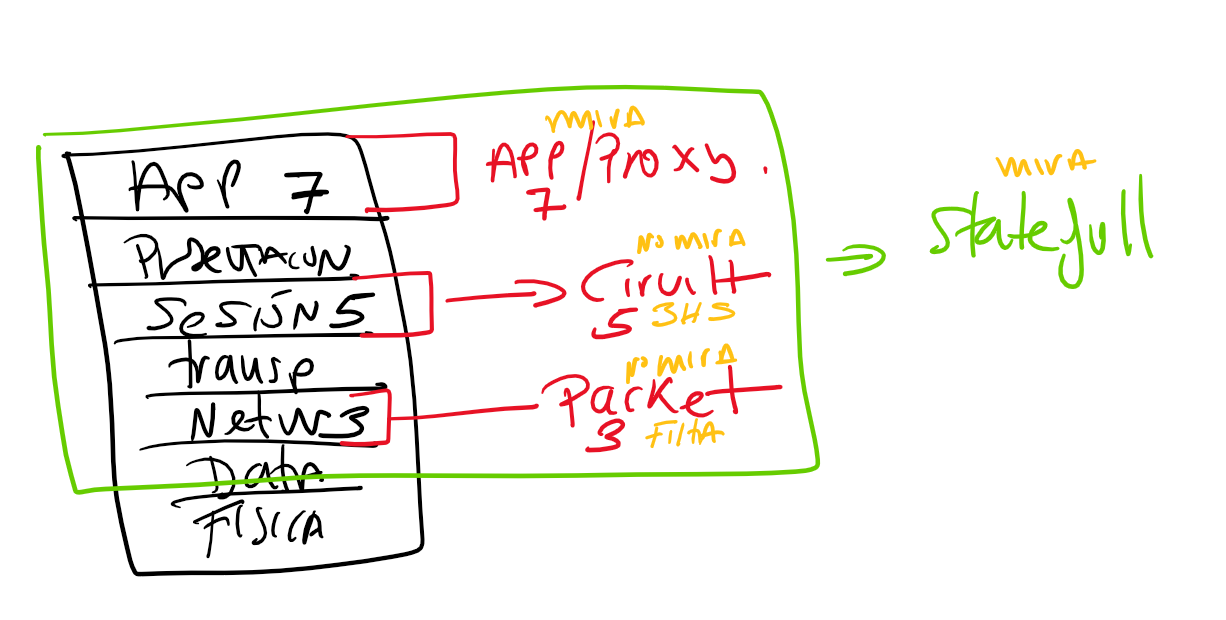
- Anone
9filtra por direccion/puertos/interfaces - [blank_start]Packet firewall[blank_end]
mira el 3 HANDSHAKE de TCP - [blank_start]Circuit-Levek Gateaway Firewall[blank_end]
abre los paquetes y es un proxy - [blank_start]Application-Level Firewall / Proxy Serve[blank_end]r
hace todo lo demas y además crear reglas automáticas - [blank_start]Statefull Multilayer Inspection Firewall[blank_end]- APacket firewall
- BCircuit-Levek Gateaway Firewall
- CApplication-Level Firewall / Proxy Serve
- DStatefull Multilayer Inspection Firewall
10Limitaciones de los FIREWALL:
- Ason el primer vector del ataque
- Bno pueden hacer nada contra los backdoor attacks (ya esta el atacante instalado en la red)
- Cpodría generar bottleneck si mal configurado
- Dpodría impedir el paso de usuarios o tráfico legítimo si mal configurado
- Eno protegen de ataques del interior
11BASTION (en un firewall puede haber uno o varios bastiones)
especial diseñado para aguantar [blank_start]ataques[blank_end]
será quizás el ún[blank_start]ico host conectado directamente a la red[blank_end] junto con quizás uno de los routers
configurado con [blank_start]servicios limitados[blank_end] y solo los extrictamente necesarios.
si el atacante gana acceso al bastion, accede a toda la red
- se configura habitualemente en algunas topologías como cabeza de turco para ganar tiempo en un ataque
- se conoce como perimeter network
- en una DMZ que no tiene data sensible
- packet filtering y proxy services
en entornos cloud se ubica como punto de entrada al cloud y se denomina bastion de salto- Aataques
- Bservicios limitados
- Cico host conectado directamente a la red
12PRINCIPIOS BASICOS PARA CREAR UN BASTION
- minimos [blank_start]privilegios[blank_end] y mínimos [blank_start]servicios[blank_end]
- siempre listo para ser [blank_start]comprometido[blank_end]
- ubicar entre el [blank_start]servidos interno y la red exterior[blank_end]
- los admin deben ser [blank_start]alertados[blank_end] (via mensaje) si algo sucede
- si el bastion cae, los servidores interiores must [blank_start]verify services provided by the bastion[blank_end]- Aprivilegios
- Bservicios
- Cservidos interno y la red exterior
- Dalertados
- Everify services provided by the bastion
- Fcomprometido
13AUDITANDO EL BASTION
create a [blank_start]benchmark or baseline[blank_end] for performance measurement
[blank_start]IPSentry[blank_end] can be used to monitor and send alerts
[blank_start]compare every audit[blank_end] is performed with the baseline to know how the bastions handles situation and how secure it is- Abenchmark or baseline
- BIPSentry
- Ccompare every audit
14TIPOS DE BASTION:
[blank_start]SINGLE-HOMED[blank_end]
- one interface
- all the traffic is routed throught the bastion
[blank_start]MULTI-HOMED[blank_end]
- at least two interfaces
- capable of separating interanl and external networks
[blank_start]INTERNAL BASTION HOST[blank_end]
- inside internal network
- pueden ser single or multi homed
- the internal interfaces (from host) comunicate with the internal bastion
- los del interior suelen proveer servicios como mail o ftp
- los externos son fundamentalmente de protección
[blank_start]NON-ROUTING DUAL-HOME HOSTS[blank_end]
- at least dual home topology
-multiple network interfaces NOT INTERACT WITH EACH OTHER
[blank_start]VICTIM MACHINES[blank_end]
- para probar apps/servicios que no son del todo conocidadas
[blank_start]EXTERNAL SERVICES HOST[blank_end]
- para servicios exclusivos de internet
- visibles para todos (imagina un servidos de pagina que aloja la página de la compañia)
[blank_start]ONE-BOX FIREWALLS[blank_end]
- no hay red de firewall, este host es el único firewall
- se necesita asegurar la absoluta seguridad de este host- ASINGLE-HOMED
- BMULTI-HOMED
- CINTERNAL BASTION HOST
- DNON-ROUTING DUAL-HOME HOSTS
- EVICTIM MACHINES
- FEXTERNAL SERVICES HOST
- GONE-BOX FIREWALLS
15Screened subnet se conoce tambien como
- ADMZ
- BTri-home firewall
16qué es un DMZ
is a [blank_start]computer host[blank_end] (bastion) or [blank_start]small nwtwork[blank_end] (servidores) inserted as a "neutral zone" betwen company lan and internet
the firewall within the DMZ screened subnet is also know as thress-pronge or [blank_start]tri-home firewall[blank_end]
- it is conected to three distinct networks and wit a diferent nic for each network
- the internet
- the DMZ subnet
- the secure lan or intranet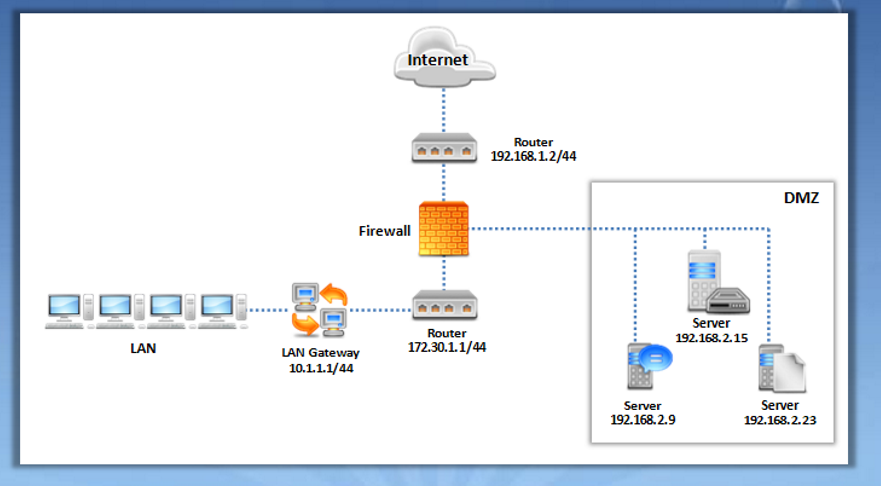
- Acomputer host
- Bsmall nwtwork
- Ctri-home firewall
17Major beneficts of DMZ
- adds [blank_start]security[blank_end]
- exploits if discovered can not [blank_start]be exploited[blank_end]
- no [blank_start]single point[blank_end] of failure- Asecurity
- Bbe exploited
- Csingle point
18Formas de crear un DMZ
[blank_start]- tri-home firewall[blank_end]: 3 nics; internet, dmz, lan
- [blank_start]sandwich DMZ:[blank_end] fire - dmz - firewall -- internet
-- no ideal ya que si cae el priner host(firewall) se compromete la nic que conecta a internet- A- tri-home firewall
- Bsandwich DMZ:
19PROXY SERVERS
- [blank_start]intermediary[blank_end] servers betwen the client and server
- worl as [blank_start]shields to hide[blank_end] the lan
---hide IP from users
- --hide lan topology
--- capable of encrypting information
--- increase anonymity in mail
- to send and recive packets from [blank_start]specific applications[blank_end]
- [blank_start]filtering[blank_end] (ACL, BLACKLIST IP, etc )
--- restrictions task
--- prevent malicious content enter the server
--- offers user authentication
- as [blank_start]cache[blank_end] for data request repeatedly
Hoy se usan sobre todo para evitar que los usuarios salgan de la lan hacia internet a visitar ciertas IP`s
IMPORTANTE
¿cuál es la diferencia clave entre un proxi que hace filtering y una app que filtra packetes?
-- que el proxy [blank_start]si conoce la app[blank_end] que envia los paquetes y puede discriminar por esa categoría también.
Proxi servers work at the app layer. if its act as gattewat for packets can be named [blank_start]application gateway[blank_end]- Aintermediary
- Bshields to hide
- Cspecific applications
- Dfiltering
- Ecache
- Fsi conoce la app
- Gapplication gateway
20¿Como funcionan un proxy?
internal host request
proxy [blank_start]examines the header and packet[blank_end] based in a rule
proxy [blank_start]reconstructs[blank_end] the packet with a diferent source ip address
---transmits the packet that conceals the actual end user
if data is returned : examines, reconstructed and [blank_start]send to the source computer[blank_end]
this type of service increase the secirity of the network as [blank_start]no packets can go straight[blank_end] fromthe client to the the destony server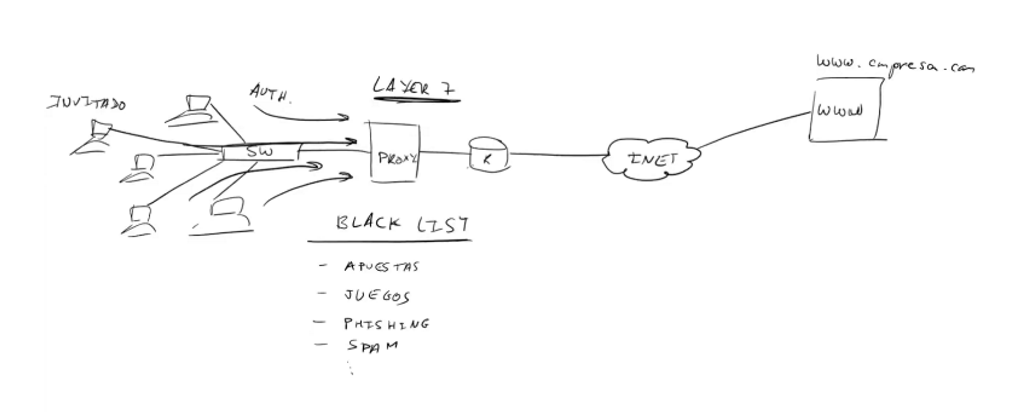
- Aexamines the header and packet
- Breconstructs
- Cno packets can go straight
- Dsend to the source computer
21LEE CON ATEMCIÖPN
Proxy Server-to-Proxy Server Linking
Within an organization, linking of proxy server provides a facility to run a proxy server as a local
cache on behalf of a department. Each individual department has control over the server and
cache.
For example, a departmental proxy server might be permitted all URL requests. The
organizational proxy server, as corporate policy, might be set to reject all URL requests for
specific online publications.- ARichtig
- BFalsch
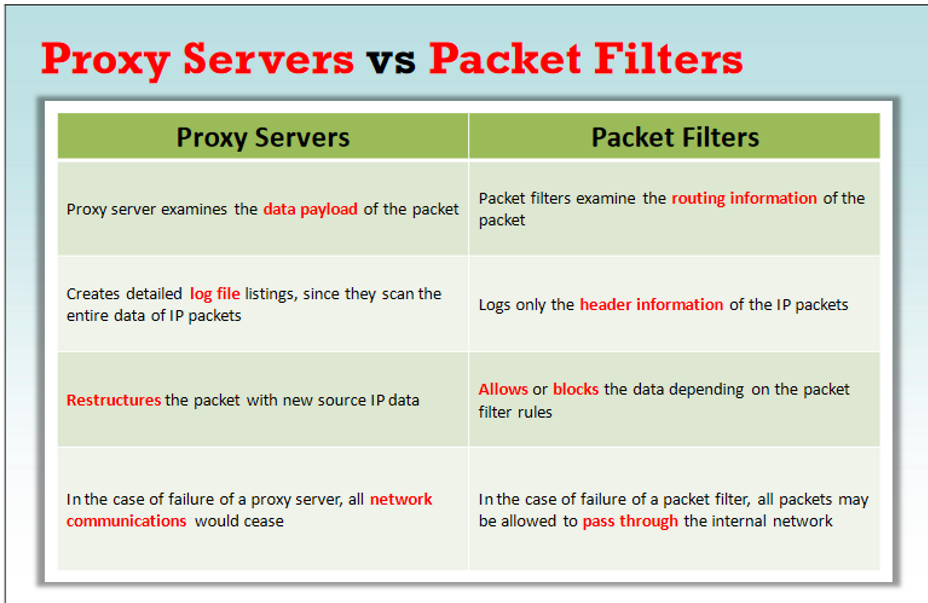
22examina data, reestructura el paquete - [blank_start]proxy[blank_end]
allow / block, examina routing (destino, origen etc) - [blank_start]filter[blank_end]- Aproxy
- Bfilter
23mira y escribe las difeencias clave
- Adata
- Blog
- Crestructures
- Dnetwork
- Erouting
- Fheader
- Gfilter
- Hpass
24mira el paquete- [blank_start]firewall[blank_end]
solo mira el header - [blank_start]filter[blank_end]
reescructura el paquete - [blank_start]firewall[blank_end]
permite o niega el paso - [blank_start]filter[blank_end]
crea detallados logs dado que pueden ver el paquete - [blank_start]firewall[blank_end]
solo crea logs acerca del IP routing/header - [blank_start]filter[blank_end]
si fallan la comunicación se detiene - [blank_start]firewall[blank_end]
si fallan puede que se de la circustancia que todo se permita o se niegue - [blank_start]filter[blank_end]- Afirewall
- Bfilter
- Cfirewallf
- Dfilterr
- Efirewallll
- Ffilterll
- Gfirewalllll
- Hfilterllll
25TYPES OF PROXY SERVERS
NOTA todo proxy que no sea puerto 80 y hhtp es considerado de una forma y otra application proxy
[blank_start]TRANSPARENT[blank_end].
transparente para el usuario
port 80
[blank_start]NON TRANSPARENT/ EXPLICIT[blank_end]
requieres configuring
each client program has to be se up to route all request to a single port
[blank_start]APPLICATION / APP LEVEL GATEWAY[blank_end]
works as a proxy server
filters connections for especific services/apps/protocols
a ftp proxy will allow traffic while other services will be blocked
good at logging
reduce load as they are capble of caching
perform user level authenticationa
[blank_start]SOCKS[blank_end]
it is considered as a internet toolkit
allows only TCP-based applications to execute on proxy servers.
it is called because use sockets internally to keep track of the clients individual connections.
request clients and if it valid, bind the request to the information exchange, usually a HTTP
ANONYMOUS
nada que añadir
[blank_start]REVERSE[blank_end]
situated closer to the server
optimize content by compressing in order to speed up loading times
client es unaware
acts as intermediate server, sits betwen client and actual server- ATRANSPARENT
- BNON TRANSPARENT/ EXPLICIT
- CAPPLICATION / APP LEVEL GATEWAY
- DSOCKS
- EREVERSE
26LIMIRACIONES PROXY SERVERS
[blank_start]point of failure[blank_end] in an event of attack if not properly secured
because data is reroute web pages can [blank_start]load slowy[blank_end]
[blank_start]personal information[blank_end] is passed throught external server can be [blank_start]accessed and compromised[blank_end]- Apoint of failure
- Bload slowy
- Caccessed and compromised
- Dpersonal information
27NAT
[blank_start]separates[blank_end] IP into two sets and enables LAN to use the [blank_start]addresses for internal and external traf[blank_end]fic
m[blank_start]odify[blank_end] the packets that routers sends and h[blank_start]ide the lan[blank_end]
has the ability to change the address of the packet and make as from valid address- Aaddresses for internal and external traf
- Bseparates
- Codify
- Dide the lan
28LEE CON ATENCIÓN
SCHEMES FOR NAT
assigning one externar host address for each internat address.
dynamically allocate an external host address without modifiying the port numbers
port mapping so multiple internal machines use the same external address
dynamically allocate external host addresss and port to pair each time an internal host initates a connection. this is the most efficiente
ADVANTAGES AND DISADVANTAGES
enforce firewalls control
restricts incoming traffic to ony packets that are part of a current interaction
hide the internal lan
interferes with encrytion and authentication
dynamic may interfere with packet filtering.- ARichtig
- BFalsch
29VPN Virtual Private Network
A VPN is an attempt to combine both the [blank_start]advantages of public and private[blank_end] networks
A VPN is a network that provides [blank_start]secure access to the network[blank_end] through the internet.
Used for connecting wide area networks (WAN).
It employs [blank_start]encryption and integrity[blank_end] protection helping you to use a public network as a private network.
A VPN performs encryption and the decryption outside the packet-filtering perimeter to [blank_start]allow the inspection of packets[blank_end] coming from other sites.
A VPN [blank_start]encapsulates[blank_end] packets sent over the Internet.
VPNs have no relation to firewall technology, but firewalls are convenient for adding VPN features as they help in providing secure remote services.- Aadvantages of public and private
- Bsecure access to the network
- Cencryption and integrity
- Dallow the inspection of packets
- Eencapsulates
30HONEYPOT
A honeypot is a system that is intended to [blank_start]attract and trap people[blank_end] who try unauthorized or illicit utilization of the host system.
Whenever there is any interaction with a honeypot, it is most likely to be a [blank_start]malicious activity.[blank_end]
They are a highly flexible tool with many different security applications.
Some honeypots can be used to help pre[blank_start]vent attacks[blank_end]
Others can be used to det[blank_start]ect attacks[blank_end]
While a few honeypots can be used for infor[blank_start]mation gathering and research[blank_end]
Any existing system can be "honeypot-ized." For example, on WinNT, it is possible to rename
the default administrator account and then create a dummy account called "administrator"
with no password. WinNT allows extensive logging of a person's activities, so this honeypot
tracks users who are attempting to gain administrator access and exploit that access.- Aattract and trap people
- Bmalicious activity.
- Cvent attacks
- Dect attacks
- Emation gathering and research
31TYPES OF HONEYPOTS
Low-intereaction
- [blank_start]emulating[blank_end] servicies and programs
- if attacker does something unexpected, they ge[blank_start]nerate an error[blank_end]
- catures li[blank_start]mited information[blank_end]
- [blank_start]specter, honeyed, kfsensor[blank_end]
High-interaction
- entire system of computers , [blank_start]real programs and apps[blank_end]
- let the attacker in, but outbound is tig[blank_start]htlly controlled[blank_end]
- captures far [blank_start]more information[blank_end]: eje: keystrokes
- [blank_start]symantec decoy server, honeynets[blank_end]- Aemulating
- Breal programs and apps
- Cnerate an error
- Dhtlly controlled
- Emited information
- Fmore information
- Gspecter, honeyed, kfsensor
- Hsymantec decoy server, honeynets
32LEE CON ATENCIÓN
BYPASSING FIREWALLS
- scan ports , find a weakness
- some firewalls will uniqueelu identify themselves usion simple ports scans: ejeplo: MS proxy server, TCP 1080 and 1745- ARichtig
- BFalsch
33FIREWALKING
Firewalking is a method used to [blank_start]collect information about remote network[blank_end]s behind firewalls.
Firewalking involves sending TCP or UDP packets into the firewall with [blank_start]TTL value is one hop greater[blank_end] than the targeted firewall.
If the packet makes it through the gateway, the system forwards it to the next hop, where the TTL equals one and prompts an ICMP error message at the point of rejection with a 'ITTL exceeded in transit" message.
Using this method, possible access to the firewall can be determined if successive probe packets are sent.
It has two phases:
a net[blank_start]work discovery phase[blank_end]
a sca[blank_start]nning phase.[blank_end]
The scanning phase requires three hosts:
[blank_start]Firewalking Host:[blank_end] The firewalking host is the system outside the target network
[blank_start]Gateway Host[blank_end]: The gateway host is the suspected firewall system on the target network,
[blank_start]Destination Host:[blank_end] The destination host is the target system on the target network to
which the data packets are addressed.- Acollect information about remote network
- BTTL value is one hop greater
- Cwork discovery phase
- Dnning phase.
- EFirewalking Host:
- FGateway Host
- GDestination Host:
34[blank_start]Source Routing[blank_end]
Using this technique, the sender of the packet designates the route that a packet
should take through the network, in such a way that the designated route should bypass the firewall node.
Using this technique, the attacker can evade firewall restrictions.
Source routing takes two approaches:
loose source routing In loose source routing, the sender specifies [blank_start]on or more stages[blank_end] the packet must go through
strict source routing, the sender specifies the [blank_start]exact route the packet must go[blank_end] through.
BYPASS BLOCKED SITES USING URL
Inted of using the url tyoe its IP
this method fails if the software blocking the web tracks also its IP
BYPASS BLOCKED SITES USING ANONYMOUS WEBSITE SURFING SITES
usar paginas web que nos devuelvel la página que está baneada
BYPASS BLOCKED SITES USING A PROXY
usar el proxy que viene por defecto en los navegadores.
es sumilar a las dos últimas opciones- ASource Routing
- Bon or more stages
- Cexact route the packet must go
Informationen
- Beschreibung
- Module 09: Firewalls Exam ECSS
- Sprache
- English
- Aufrufe
- 8
- Verlauf
- Erstellt am 22 Sep 2021 · aktualisiert am 25 Sep 2021
- Schlagwörter
- Bewertung
- Noch keine Bewertungen Bewerte dieses Quiz