
Karteikarten
Internet Security
Karten in diesem Stapel (39)
- 1What's the purpose of a firewall?To control access to the network
- 2What do firewalls use to control what enters and leaves the networkFilters
- 3What was the earliest example of a firewall?A router
- 4Do firewalls use a combination of hardware and software to prevent unauthorised access?Yes
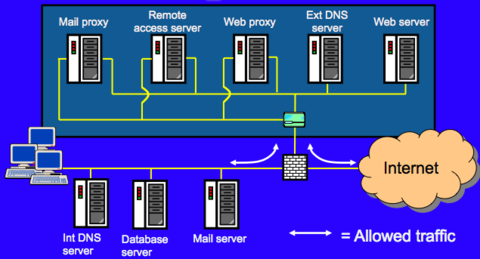
- 5What are Perimeter networks used for?Protecting a network from vulnerabilities that come from services which need a connection to an untrusted network i.e. the Internet
- 6What are perimeter networks also known as?Demilitarised Zone (DMZ)
- 7What are the 5 services included in DMZMail server front end, eg WebMail – NOT the actual mail server
Web server(s), but NOT any backend databases
External DNS servers
Remote access server(s)
Proxy server(s) - 8What is this an example of ?Demilitarised Zone (DMZ)
- 9What does each firewall have?IN(INGRESS) & OUT(ENGRESS)
- 10What does the IN & OUT do?IN direction is going into the firewall and OUT direction is going out of the firewall
- 11Name the 4 type of firewallsStatic Packet filtering firewall
Circuit-level firewall
Application-level firewall
Stateful multilayer inspection firewall - 12What layer does the Static Packet filtering firewall on in the TCP/IP stackNetwork layer
- 13What does the Static Packet filtering firewall do?It inspects information such as:
Destination & Source IP Address
Destination & Source Port numbers
Protocol Type - 14What are the advantages of Static Packet filtering firewallThey're cheap
They're fast
Good as a border device - 15How does the traffic get filtered with a Static Packet filtering firewall?Traffic is filtered according to, eg, source and destination IP addresses and port numbers.
Unknown traffic is allowed up to the Network layer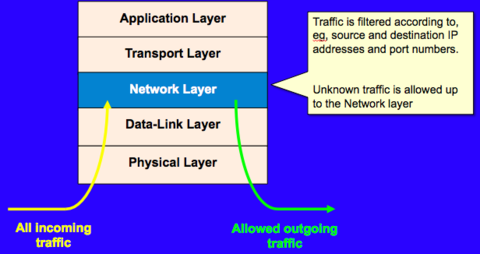
- 16What layer does the Circuit-level firewalls on in the TCP/IP stackTransport Layer
- 17What does the Circuit-level firewalls do?They decide if a request for communication is part of a legitimate session or not
- 18What 2 key points do Circuit-level firewalls do?They don't forward packets from the client to the destination – they rebuild them from the network layer down, replacing the IP and MAC addresses of the original client with the IP and MAC address of the ‘public’ interface of the server
Usually require software to be installed on the client - 19How does the traffic get filtered with a Circuit-level firewalls?Traffic is filtered according to, session related rules, eg, has a session been initiated?
Unknown traffic is allowed up to the Transport layer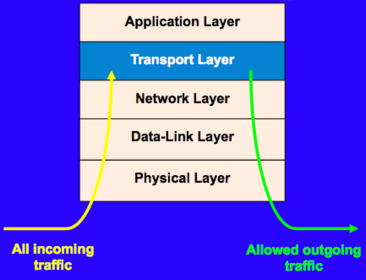
- 20What layer does the Application-level firewalls on in the TCP/IP stackApplication-level
- 21What does the Application-level firewalls do and what are they also known as?Proxies and they:
Cache web pages
Doesn't forward (like a circuit-level firewall)
Can filter on the basis of group membership, time of day
& detail of request - 22Can browsers work with a built proxy?Yes
- 23How does the traffic get filtered with a Application-level firewalls?Traffic is filtered according to application and then application-specific information, eg is this a GET or POSt request.
Unknown traffic is allowed up to the Application layer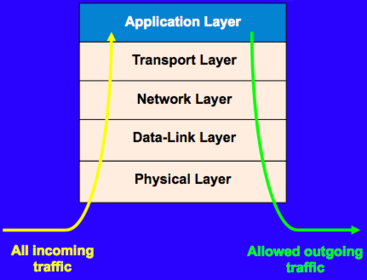
- 24What layer does the Stateful-multilayer inspection firewalls on in the TCP/IP stackApplication
Transport
Network - 25What does the Stateful-multilayer inspection firewalls do and what are they also known as?Filter packets at network layer
Filter based on session information
Filter based on application information
Allow a direct connection between source and destination - 26What are the pros and cons of Stateful-multilayer inspection firewalls?Pro:
Most secure firewall
Con:
Complex to administer - 27How does the traffic get filtered with a Circuit-level firewalls?Traffic is filtered at all three levels based on application, session and packet filtering rules.
Unknown traffic is allowed up to the Network layer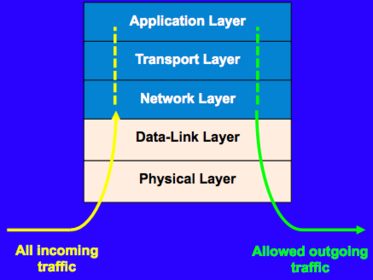
- 28Why are packets filtered at the network layerTo prevent malicious packets getting into the OS’s TCP/IP stack, and thus gaining control of the OS
- 29What are private IP Addresses?IP Addresses that don't function on the Internet
- 30What are the ranges for private IP Addresses?Class A 10.0.0.0 – 10.255.255.255
Class B 172.16.0.0 – 172.31.255.255
Class C 192.168.0.0 – 192.168.255.255 - 31What type of firewalls do you need to forward packets using Private IP AddressesYou need to use a circuit-level firewall or an application-level firewall
- 32What does a socket do and contain ?A socket identifies a service (application) on a computer
It contains IP Address, Transport protocols & Port Numbers - 33Name 3 well known port numbersHTTP - 80
FTP - 21 & 20
SMTP - 25
HTTPS - 443
IMAP - 143
POP3 - 110 - 34What do Access Control Lists do ?On the interfaces define they rules for that interface, one for IN and one for OUT
- 35What are ACL made up ofA list of statements about what is permitted
Statements can be very broad or very specific, as required - 36How are they applied ?The first that applies to the traffic concerned is used to decide what to do with it
- 37Which service used TCP 53 & UDP 53DNS
- 38Why would you need public IP addresses on your internal network if you wanted to use a stateful-multilayer inspection firewall?They allow a direct connection between source and destination computer and so they do not perform any network translation, so the IP address of the source has to be usable on the Internet.
- 39What traffic would the following filter on a packet filtering firewall allow through? permit UDP host 67.31.45.123 eq 53 any eq53It would allow traffic from UDP port 53 on a computer with an IP address of 67.31.45.123 to go to any other IP address provided it was going to UDP port 53 on the destination. In other words, this is traffic between DNS servers.