
Karteikarten
Ohne Titel
Karten in diesem Stapel (28)
- 1Three components of NAC systemsAccess Requester (AR): Node that is attempting to access the network and may be any device that is managed by the NAC system.
Policy Server: Determines what access should be granted. Often relies on backend systems.
Network Access Server (NAS): Functions as an access control point for users in remote locations connecting to an enterprise’s internal network. - 2Common NAC Enforcement MethodsIEEE 802.1X
VLANS
Firewall
DHCP management - 3Cloud Computing ElementsEssential Characteristics: Broad Network Access, Rapid Elasticity, Measured Service, Measured Service, On-demand Self-service, Resource pooling.
Service Models: Software as service (SAS) -> Platform as a service (PaaS) -> Infrastructure as a service. (IaaS).
Development Models: Public, Private, Hybrid, Community. - 4NIST Cloud Computing Reference Architecture5 Major Actors:
Cloud consumer
Cloud Auditor
Cloud Provider
Cloud Broker
Cloud Carrier - 5Cloud Security RisksInsecure interfaces and APIs, Shared technology issues, Data loss or leakage.
Account or service hijacking/Unknown Risk - 6Data Protection in the CloudThe threat of data compromise increases in the cloud.
Multi-instance Model: Provides a unique DBMS running on a VM instance for each cloud subscriber. This gives the subscriber complete control over role definition, user authorization.
Multi-tenant Model: Provides a predefined environment for the cloud subscriber that is shared with other tenants, typically through tagging data. - 7TLS connectionsA transport that provides a suitable type of service
For TLS such connections are peer-to-peer relationships.
Connections are transient
Every connection is associated with one session. - 8TLS Sessions:An association between a client & a server
Created by the Handshake Protocol
Are used to avoid the expensive negotiation of new security parameters - 9TLS Record Protocol OperationApplication Data
Fragment
Compress
Add MAC
Encrypt
Appen TLS/Record Header
divided into smaller pieces and compresses, applies MAC value and calculates it. - 10Heartbeat ProtocolIt is typically used to monitor the availability of a protocol entity
request and response protocol and is used to see if the other client/machine is running currently.
Runs on top of the TLS Record Protocol which consists of two message types, heartbeat_request & heartbeat_response.
Serves two purposes: It assures the sender that the recipient is still alive. It generates activity across the connection during idle periods. - 11SSL/TLS AttacksAttacks on the handshake protocol
Attacks on the record and application data protocols
Attacks on the PKI
Other attacks - 12SSH Transport Layer Protocol Packet FormationServer authentication occurs at the transport layer, based on the server possessing a public/private key pair.
A server may have multiple host keys using multiple different asymmetric encryption algorithms.
Multiple hosts may share the same host key.
The server host key is used during key exchange to authenticate the identity of the host. - 13Port ForwardingOne of the most useful features of SSH
Provides the ability to convert any insecure TCP connection into secure SSH connection
Incoming TCP traffic is delivered to the appropriate application on basis of the port number. - 14[DH protocol] Suppose that the shared public values between Alice and Bob are g=5 and p=7. The private value of Alice and Bob is 2 and 4, respectively. Calculate the value of the shared session key.Shared Key+/= 4
- 15For the given p=3 and q=5, calculate the public and private RSA keys.(15,3) (15,11)
- 16User Authentication PrinciplesUser authentication is the fundamental building block and primary line of defense
User authentication is the basis for most types of access control and user accountability.
Authentication Architectural Model includes: Registration Authority(RA), Credential Service Provider, Relying party, Verifier. - 17Means of AuthenticationPasswords
Biometric Scan
Badge/ID Tag
PIN Code
Something the individual possesses - 18KerberosUses symmetric encryption, no public key, provides a centralized authentication server.
Key distribution and user authentication service developed by MIT.
AS (authentication Server) identifies who you are.
Ticket Granting Server (TGS) users subsequently request access to other services from TGS on basis of users TGT
Complex protocol using DES
figure 4.2 sequence of communication - 19Key Distribution using Asymmetric EncryptionOne of the major roles of public-key encryption is to address the problem of key distribution.
Two distinct aspects of public-key encryption in this are the distribution of public keys & the use of public-key encryption to distribute secret keys.
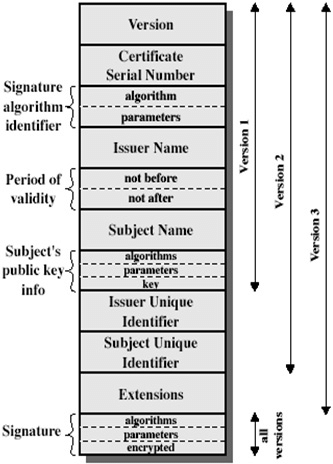
Public key certificates consist of a public key plus a user ID of the key owner with the whole block signed by a trusted third party.
Always check the public key certificate to verify it is the actual one. - 20Revocation of CertificatesEach certificate includes a period of validity
Typically, a new certificate is issued just before the expiration of the old one.
Certificates can be revoked when: the user’s private key is assumed to be compromised or the CA’s certificate is assumed to be compromised. - 21Identity ManagementA centralized, automated approach to provide enterprise wide access to resources by employees and other authorized individuals.
- 22Identity Management examplesAuthentication
Authorization
Accounting
Provisioning
Workflow automation
Delegated Administration
Password Synchronization
Self-Service Password Reset
Federation - 23Identity FederationIt is an extension of identity management to multiple security domains.
Another key function would be identity mapping.
Federated IM refers to the agreements, standards, and technologies that enable the portability of identities, Identity attributes and entitlements across enterprises. - 24Kerberos in action
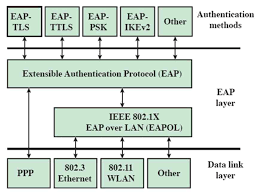
- 25EAP Layered Context
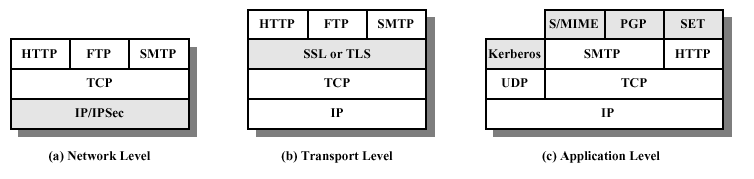
- 26Location of TLS in the TCP/IP Protocol Stack
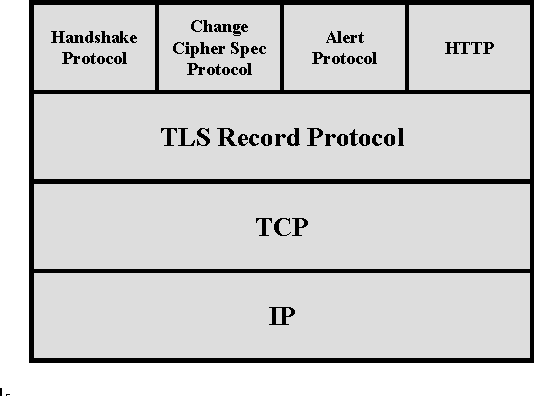
- 27TLS Protocol Stack
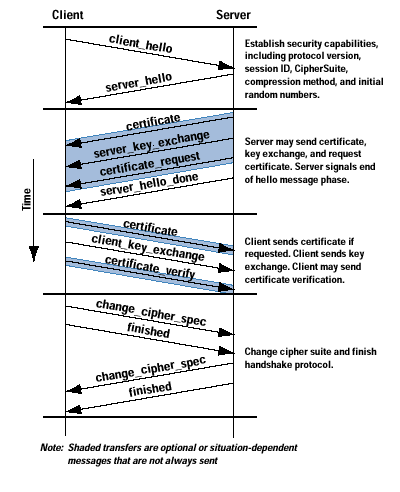
- 28Handshake Protocol Action
Informationen
- Beschreibung
- Cybersecurity Exam 2 Karteikarten am Ohne Titel, erstellt von Kimberly Zavala am 16/11/2022.
- Erstellt von
- Kimberly Zavala
- Aufrufe
- 0
- Bewertung