
Mindmap
Access Control 2 - intermediary controls
Inhalt der Mindmap
Access Control 2 - intermediary controls
Intermediate Controls
- Groups
- users with similar access rights collected in groups
- Given permissions to access objects
- Groups
Negative Permission
- operation user cant do
- policy conflict - resolved by reference monitor
Priviliges
- collection of rights to execute certain operations
- avtivities such as admin, back up and network access
Role Based Access Control
- Priviliges come predefined with OS
- Role
- Collection of application specific operations
- Subjects derive access rights from their role - admin etc
Roles and Layers
- Layers between subject & objects
- Roles
- Collection of procedures, assigned to users
- Procedures
- High level access control methods
Evaluating Security Policies
- Most basic: check against ACE - Access Control Entry
- Andrew Cant Eat
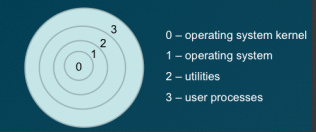
- Protection Rings
- hardware based access control
- each subject and object are assigned a number depending on importance
- Decision made by comparing subject and objects numbers
- Partial Ordering
- student group + year group for example
- partial orderings provide relations between subsets
- Security policy: grant access if object label <= subject label
- Multi-level security
- access to info should only be granted if it is necessary to perform ones duties
- Most basic: check against ACE - Access Control Entry
sandboxing
- run code in restricted environment ( JVM )
- android sandboxing
- app defined permissions
- isolates your app data from other apps
- app framework - with cryptography and robust implementation of permissions
- app defined permissions
Virtualisation
- emulate other machines
Trusted computing
- verifiable state of software/ hardware
- Nexus
Bilder und Dateien der Mindmap
Informationen
- Beschreibung
- Mindmap am Access Control 2 - intermediary controls, erstellt von Jack Evans0219 am 20/05/2015.
- Erstellt von
- Jack Evans0219
- Aufrufe
- 1
- Bewertung