
Mindmap
Computer Security U9 - Software Security
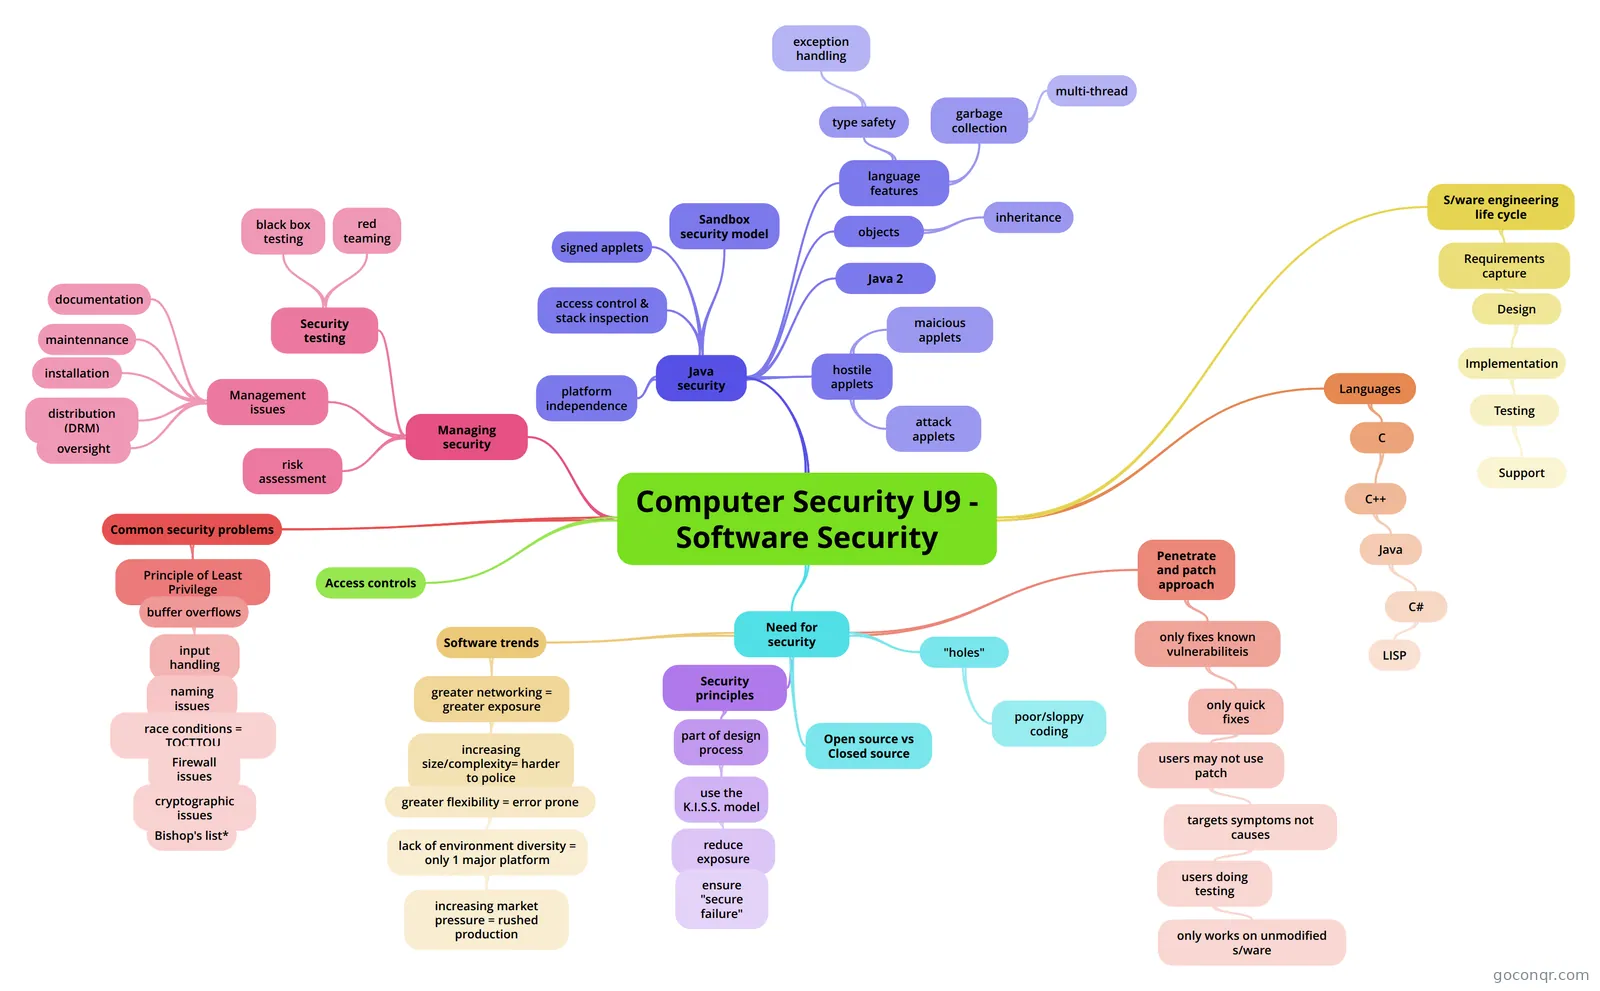
Mind map: Computer security software security
Inhalt der Mindmap
Computer Security U9 - Software Security
Need for security
- "holes"
- poor/sloppy coding
- Software trends
- greater networking = greater exposure
- increasing size/complexity= harder to police
- greater flexibility = error prone
- lack of environment diversity = only 1 major platform
- increasing market pressure = rushed production
- lack of environment diversity = only 1 major platform
- greater flexibility = error prone
- increasing size/complexity= harder to police
- greater networking = greater exposure
- Penetrate and patch approach
- only fixes known vulnerabiliteis
- only quick fixes
- users may not use patch
- targets symptoms not causes
- users doing testing
- only works on unmodified s/ware
- users doing testing
- targets symptoms not causes
- users may not use patch
- only quick fixes
- only fixes known vulnerabiliteis
- Open source vs Closed source
- Security principles
- part of design process
- use the K.I.S.S. model
- reduce exposure
- ensure "secure failure"
- reduce exposure
- use the K.I.S.S. model
- part of design process
- "holes"
S/ware engineering life cycle
- Requirements capture
- Design
- Implementation
- Testing
- Support
- Testing
- Implementation
- Design
- Requirements capture
Languages
- C
- C++
- Java
- C#
- LISP
- C#
- Java
- C++
- C
Access controls
Common security problems
- Principle of Least Privilege
- buffer overflows
- input handling
- naming issues
- race conditions = TOCTTOU
- Firewall issues
- cryptographic issues
- Bishop's list*
- cryptographic issues
- Firewall issues
- race conditions = TOCTTOU
- naming issues
- input handling
- buffer overflows
- Principle of Least Privilege
Managing security
- risk assessment
- Security testing
- black box testing
- red teaming
- Management issues
- distribution (DRM)
- installation
- maintennance
- documentation
- oversight
Java security
- objects
- inheritance
- platform independence
- language features
- type safety
- exception handling
- garbage collection
- multi-thread
- type safety
- Sandbox security model
- signed applets
- Java 2
- access control & stack inspection
- hostile applets
- maicious applets
- attack applets
- objects
Informationen
- Beschreibung
- Mindmap am Computer Security U9 - Software Security, erstellt von Nick.Bell2013 am 27/04/2013.
- Erstellt von
- Nick.Bell2013
- Aufrufe
- 83
- Bewertung