
Quiz
Firewall Authentication
Dieses Quiz enthält Fragetypen, die sich im gewohnten Player öffnen.
Fragen in diesem Quiz (16)
1Fortigate methods of firewall authentication (Select 3)
- ALocal password authentication
- Bserver-based password authentication
- Ctwo-factor authentication
- DLDAP
- EToken
- FTACACS+
2Remote authentication server (Select 4)
- APOP3
- BRADIUS
- CLDAP
- DTACACS+
- EToken Server
- FFortiAuthenticator
3POP3 is the only server that requires an email address as the login credential.
- ARichtig
- BFalsch
4Tokens use a specific algorithm to generate an OTP. The algorithm consists of:
- AThe time: obtained from an accurate internal clock.
A seed: a unique, randomly-generated number that does not change in time. - BA seed: obtained from an accurate internal clock.
The time : a unique, randomly-generated number that does not change in time.
- AThe time: obtained from an accurate internal clock.
5Authentication methods and active authentication types :
- AActive
Passive - BLocal
Remote
- AActive
6[blank_start]Active[blank_end] :
User receives a login prompt
Must manually enter credentials to authenticate
POP3, LDAP, RADIUS, Local and TACACS+
[blank_start]Passive[blank_end] :
User does not receive a login prompt
Credentials are determined automatically
-Method varies depending on type of authentication used
FSSO, RSSO, and NTLM- AActive
- BPassive
7Port used for LDAP:
- ATCP Port 389
- BTCP Port 398
- CTCP Port 983
8?
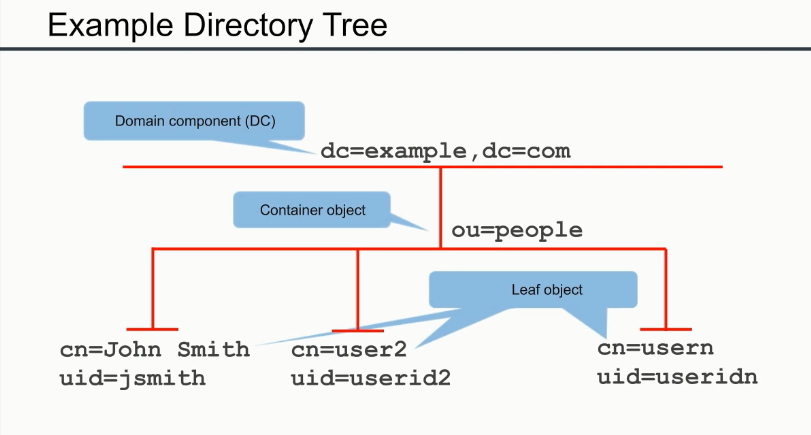
- AExample Directory Tree
- BExample Organizational Domain Tree
- CExample LDAP hierarchy
9Testing LDAP query:
- Adiagnose test authserver ldap <server> <username> <password>
- Bdiagnose authserver <serverip> ldap <username> <password>
10When FortiGate uses RADIUS server for remote authentication, which statement about RADIUS is true?
- Aa. FortiGate must query remote RADIUS server using the distinguished name (dn).
- Bb. RADIUS group memberships are provided by vendor specific attributes (VSAs) configured on the RADIUS server.
11Which of the following is a valid reply from a RADIUS server to an ACCESS-REQUEST packet from FortiGate?
- Aa. ACCESS-PENDING
- Bb. ACCESS-REJECT
12A remote LDAP user is trying to authenticate with a user name and password. How does FortiGate verify the login credentials?
- Aa. FortiGate queries its own database for user credentials.
- Bb. FortiGate sends the user entered credentials to the remote server for verification.
13Which statement about guest user groups is true?
- Aa. Guest user group accounts are temporary.
- Bb. Guest user group account passwords are temporary.
14Which statement about active authentication is true?
- Aa. Active authentication is always used before passive authentication.
- Bb. The firewall policy must allow the HTTP, HTTPS, FTP, and/or Telnet protocols in order for the user to be prompted for credentials.
15[blank_start]ACCESS—ACCEPT[blank_end], which means that the user credentials are ok
[blank_start]ACCESS—REJECT[blank_end], which means that the credentials are wrong
[blank_start]ACCESS—CHALLENGE[blank_end], which means that the server is requesting a secondary password ID, token, or certificate. This is typically the reply from the server when using two-factor authentication.- AACCESS—ACCEPT
- BACCESS—REJECT
- CACCESS—CHALLENGE
16[blank_start]The Common Name identifier[blank_end] setting is the attribute name used to find the user name. Some schemas allow you to use the attribute uid. Active Directory most commonly uses sAMAccountName or cn, but can use others as well.
[blank_start]The Distinguished Name[blank_end] setting identifies the top of the tree where the users are located, which is generally the dc value; however, it can be a specific container or ou. You must use the correct X.500 or LDAP format.
[blank_start]The Bind Type[blank_end] setting depends on the security settings of the LDAP server. The setting Regular (to specify a regular bind) is required if you are searching across multiple domains and require the credentials of a user that is authorized to perform LDAP queries (for example, an LDAP administrator).- AThe Common Name identifier
- BThe Distinguished Name
- CThe Bind Type
Informationen
- Beschreibung
- Der Nutzer hat seine Fachbereichs-Information gelöscht. Quiz am Firewall Authentication, erstellt von Gelöschter Nutzer am 20/09/2018.
- Autor
- Gelöschter Nutzer
- Sprache
- English
- Aufrufe
- 39
- Verlauf
- Erstellt am 20 Sep 2018 · aktualisiert am 11 Apr 2019
- Schlagwörter