
Quiz
CyberSecurity Week 2 Study Guide
Erstelle ein kostenloses Konto, um dieses Quiz zu beenden
Speichere deinen Fortschritt und sieh dir dein Endergebnis an.
oder mit deiner E-Mail registrieren
Schon ein Konto? Anmelden
Fragen in diesem Quiz (27)
1Which of the following statements correctly describes biometric methods?
- AThey are the least expensive and provide the most protection.
- BThey are the most expensive and provide the least protection.
- CThey are the least expensive and provide the least protection.
- DThey are the most expensive and provide the most protection.
2Which of the following statements correctly describes passwords?
- AThey are the least expensive and most secure.
- BThey are the most expensive and least secure.
- CThey are the least expensive and least secure.
- DThey are the most expensive and most secure.
3How is a challenge/response protocol utilized with token device
implementations?- AThis protocol is not used; cryptography is used.
- BAn authentication service generates a challenge, and the smart token
generates a response based on the challenge. - CThe token challenges the user for a username and password.
- DThe token challenges the user’s password against a database of stored
credentials.
4Which access control method is considered user-directed?
- ANondiscretionary
- BMandatory
- CIdentity-based
- DDiscretionary
5Which item is not part of a Kerberos authentication implementation?
- AMessage authentication code
- BTicket granting service
- CAuthentication service
- DUsers, programs, and services
6If a company has a high turnover rate, which access control structure is best?
- ARole-based
- BDecentralized
- CRule-based
- DDiscretionary
7The process of mutual authentication involves _______________.
- AA user authenticating to a system and the system authenticating to the user
- BA user authenticating to two systems at the same time
- CA user authenticating to a server and then to a process
- DA user authenticating, receiving a ticket, and then authenticating to a service
8In discretionary access control security, who has delegation authority to grant
access to data?- AUser
- BSecurity officer
- CSecurity policy
- DOwner
9Which could be considered a single point of failure within a single sign-on
implementation?- AAuthentication server
- BUser’s workstation
- CLogon credentials
- DRADIUS
10What role does biometrics play in access control?
- AAuthorization
- BAuthenticity
- CAuthentication
- DAccountability
11What determines if an organization is going to operate under a discretionary,
mandatory, or nondiscretionary access control model?- AA. Administrator
- BSecurity policy
- CCulture
- DSecurity levels
12Which of the following best describes what role-based access control offers
companies in reducing administrative burdens?- AIt allows entities closer to the resources to make decisions about who can
and cannot access resources. - BIt provides a centralized approach for access control, which frees up
department managers. - CUser membership in roles can be easily revoked and new ones established
as job assignments dictate. - DIt enforces enterprise-wide security policies, standards, and guidelines.
- AIt allows entities closer to the resources to make decisions about who can
13Which of the following is the best description of directories that are used in
identity management technology?- AMost are hierarchical and follow the X.500 standard.
- BMost have a flat architecture and follow the X.400 standard.
- CMost have moved away from LDAP.
- DMany use LDA.
14Which of the following is not part of user provisioning?
- ACreation and deactivation of user accounts
- BBusiness process implementation
- CMaintenance and deactivation of user objects and attributes
- DDelegating user administration
15What is the technology that allows a user to remember just one password?
- APassword generation
- BPassword dictionaries
- CPassword rainbow tables
- DPassword synchronization
16Which of the following is not considered an anomaly-based intrusion
protection system?- AStatistical anomaly–based
- BProtocol anomaly–based
- CTemporal anomaly–based
- DTraffic anomaly–based
17The next graphic covers which of the following:
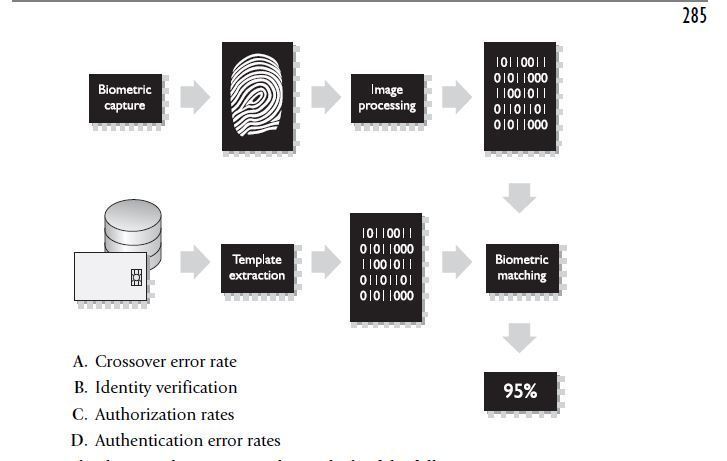
- AA
- BB
- CC
- DD
18The diagram shown next explains which of the following concepts:
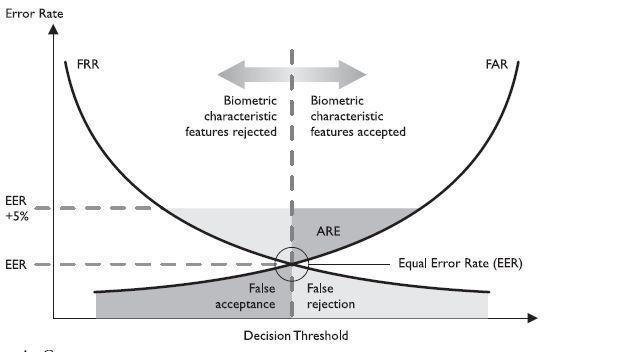
- AA
- BB
- CC
- DD
19The graphic shown here illustrates how which of the following works:
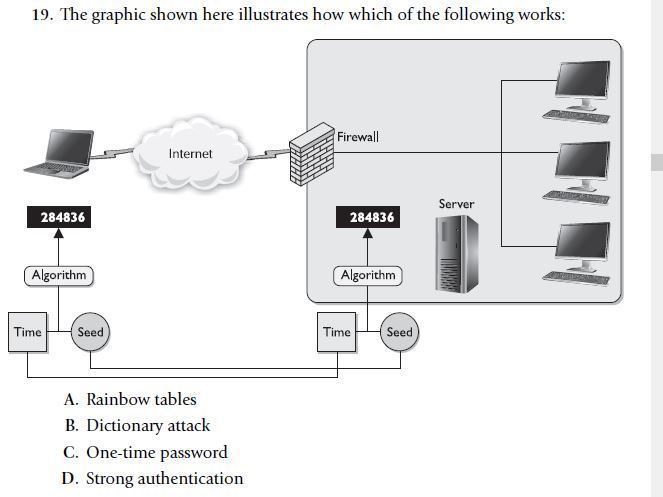
- ARainbow tables
- BDictionary attack
- COne-time password
- DStrong authentication
20Which of the following has the correct definition mapping?
i. Brute force attacks Performed with tools that cycle through many
possible character, number, and symbol combinations to uncover a
password.
ii. Dictionary attacks Files of thousands of words are compared to the user’s
password until a match is found.
iii. Social engineering An attacker falsely convinces an individual that she
has the necessary authorization to access specific resources.
iv. Rainbow table An attacker uses a table that contains all possible
passwords already in a hash format.- AA. i, ii
- BB. i, ii, iv
- CC. i, ii, iii, iv
- DD. i, ii, iii
21George is responsible for setting and tuning the thresholds for his company’s
behavior-based IDS. Which of the following outlines the possibilities of not
doing this activity properly?- AIf the threshold is set too low, nonintrusive activities are considered attacks
(false positives). If the threshold is set too high, then malicious activities
are not identified (false negatives). - BIf the threshold is set too low, nonintrusive activities are considered attacks
(false negatives). If the threshold is set too high, then malicious activities
are not identified (false positives). - CIf the threshold is set too high, nonintrusive activities are considered
attacks (false positives). If the threshold is set too low, then malicious
activities are not identified (false negatives). - DIf the threshold is set too high, nonintrusive activities are considered
attacks (false positives). If the threshold is set too high, then malicious
activities are not identified (false negatives).
- AIf the threshold is set too low, nonintrusive activities are considered attacks
22Use the following scenario to answer Questions 22–24.Tom is a new security manager for a
retail company, which currently has an identity management system (IdM) in place.
The data within the various identity stores update more quickly than the current IDM
software can keep up with, so some access decisions are made based upon obsolete
information. While the IDM currently provides centralized access control of internal
network assets, it is not tied into the web-based access control components that are
embedded within the company’s partner portals. Tom also notices that help-desk technicians
are spending too much time resetting passwords for internal employees.
Which of the following changes would be best for Tom’s team to implement?- AMove from namespaces to distinguished names.
- BMove from meta-directories to virtual directories.
- CMove from RADIUS to TACACS+.
- DMove from a centralized to a decentralized control model.
23Use the following scenario to answer Questions 22–24.Tom is a new security manager for a
retail company, which currently has an identity management system (IdM) in place.
The data within the various identity stores update more quickly than the current IDM
software can keep up with, so some access decisions are made based upon obsolete
information. While the IDM currently provides centralized access control of internal
network assets, it is not tied into the web-based access control components that are
embedded within the company’s partner portals. Tom also notices that help-desk technicians
are spending too much time resetting passwords for internal employees.
Which of the following components should Tom make sure his team puts
into place?- ASingle sign-on module
- BLDAP directory service synchronization
- CWeb access management
- DX.500 database
24Use the following scenario to answer Questions 22–24.Tom is a new security manager for a
retail company, which currently has an identity management system (IdM) in place.
The data within the various identity stores update more quickly than the current IDM
software can keep up with, so some access decisions are made based upon obsolete
information. While the IDM currently provides centralized access control of internal
network assets, it is not tied into the web-based access control components that are
embedded within the company’s partner portals. Tom also notices that help-desk technicians
are spending too much time resetting passwords for internal employees.
Tom has been told that he has to reduce staff from the help-desk team.
Which of the following technologies can help with the company’s help-desk
budgetary issues?- AA. Self-service password support
- BB. RADIUS implementation
- CC. Reduction of authoritative IdM sources
- DD. Implement a role-based access control model
25Use the following scenario to answer Questions 25–27. Lenny is a new security manager for
a retail company that is expanding its functionality to its partners and customers. The
company’s CEO wants to allow its partners’ customers to be able to purchase items
through their web stores as easily as possible. The CEO also wants the company’s partners
to be able to manage inventory across companies more easily. The CEO wants to
be able to understand the network traffic and activities in a holistic manner, and he
wants to know from Lenny what type of technology should be put into place to allow
for a more proactive approach to stopping malicious traffic if it enters the network. The
company is a high-profile entity constantly dealing with zero-day attacks.
Which of the following is the best identity management technology that Lenny
should consider implementing to accomplish some of the company’s needs?- ALDAP directories for authoritative sources
- BDigital identity provisioning
- CActive Directory
- DFederated identity
26Use the following scenario to answer Questions 25–27. Lenny is a new security manager for
a retail company that is expanding its functionality to its partners and customers. The
company’s CEO wants to allow its partners’ customers to be able to purchase items
through their web stores as easily as possible. The CEO also wants the company’s partners
to be able to manage inventory across companies more easily. The CEO wants to
be able to understand the network traffic and activities in a holistic manner, and he
wants to know from Lenny what type of technology should be put into place to allow
for a more proactive approach to stopping malicious traffic if it enters the network. The
company is a high-profile entity constantly dealing with zero-day attacks.
Lenny has a meeting with the internal software developers who are responsible
for implementing the necessary functionality within the web-based system.
Which of the following best describes the two items that Lenny needs to be
prepared to discuss with this team?- AService Provisioning Markup Language and the eXtensible Access Control
Markup Language - BStandard Generalized Markup Language and the Generalized Markup
Language - CExtensible Markup Language and the HyperText Markup Language
- DService Provisioning Markup Language and the Generalized Markup
Language
- AService Provisioning Markup Language and the eXtensible Access Control
27Use the following scenario to answer Questions 25–27. Lenny is a new security manager for
a retail company that is expanding its functionality to its partners and customers. The
company’s CEO wants to allow its partners’ customers to be able to purchase items
through their web stores as easily as possible. The CEO also wants the company’s partners
to be able to manage inventory across companies more easily. The CEO wants to
be able to understand the network traffic and activities in a holistic manner, and he
wants to know from Lenny what type of technology should be put into place to allow
for a more proactive approach to stopping malicious traffic if it enters the network. The
company is a high-profile entity constantly dealing with zero-day attacks.
Pertaining to the CEO’s security concerns, what should Lenny suggest the
company put into place?- ASecurity event management software, intrusion prevention system, and
behavior-based intrusion detection - BSecurity information and event management software, intrusion detection
system, and signature-based protection - CIntrusion prevention system, security event management software, and
malware protection - DIntrusion prevention system, security event management software, and war
dialing protection
- ASecurity event management software, intrusion prevention system, and
Informationen
- Beschreibung
- CyberSecurity CISSP Quiz am CyberSecurity Week 2 Study Guide, erstellt von Eric Booker am 27/06/2018.
- Autor
- Eric Booker
- Sprache
- English
- Aufrufe
- 5
- Schlagwörter
- Bewertung
- Noch keine Bewertungen Bewerte dieses Quiz