
Quiz
2b Software vulnerabilities
Dieses Quiz enthält Fragetypen, die sich im gewohnten Player öffnen.
Fragen in diesem Quiz (12)
1Typical memory corruption bugs:
- Astack based buffer overflow
- Bheap overflow
- Coff-by-one overflow
- Duse- after-free
2Buffer overflow: Simple [blank_start]overwrite[blank_end]
struct {
char name[8];
long is_admin;
} info;
> in debugger can we see that is_admin is 8 bytes after name
>>> print &info.name
(char (*)[40]) 0x7fffffffdce0
>>> print &info.is_admin
(long *)0x7fffffffdd08
By write more than [blank_start]40[blank_end] bytes we can overwrite info.is_admin!- A40
- Boverwrite
3In the stack [blank_start]rsp[blank_end] ([blank_start]stack pointer[blank_end]) keep track of [blank_start]top[blank_end] of the stack.
The stack grows [blank_start]downwards[blank_end] >> [blank_start]rsp[blank_end] is [blank_start]decremented[blank_end] when pushing.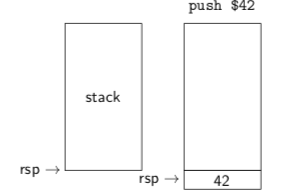
- Arsp
- Besp
- Ctop
- Dbottom
- Estack pointer
- Fframe pointer
- Gdownwards
- Hupwards
- Irsp
- Jebp
- Kdecremented
- Lincremented
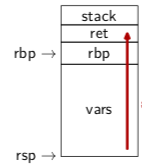
4This is stack..?
- Aoverflow
5Order of operations: (type 1, 2, 3, 4) when calling a function (returning is in the other sense)
[blank_start]3[blank_end]) decrease [blank_start]stack[blank_end] pointer to make space for variables
[blank_start]1[blank_end]) push current r[blank_start]b[blank_end]p onto stack
[blank_start]2[blank_end]) set new rbp to rsp (top of stack)- A3
- Bstack
- C1
- Db
- E2
6Injecting shellcode:
> Shellcode = snippet of e[blank_start]xecutable[blank_end] code that we write in memory with a buffer [blank_start]overflow[blank_end], and having the [blank_start]retur[blank_end]n address pointing to the beginning of our code
> when function reaches the end:
>> [blank_start]local[blank_end] variables are deallocated from the stack
>> [blank_start]rbp[blank_end] is popped from the stack
>> r[blank_start]i[blank_end]p is popped from the stack
>> execution continues at the r[blank_start]et[blank_end] address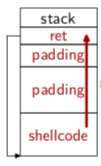
- Aet
- Bxecutable
- Cretur
- Dlocal
- Erbp
- Fi
- Goverflow
7To protect against overflows:
> [blank_start]Stack[blank_end] c[blank_start]anarie[blank_end]s: push a r[blank_start]andom[blank_end] value on the stack at the beginning of the function, before returning, verify that the value has not been m[blank_start]odifi[blank_end]ed (done by default by gcc)
>> :( : can be by-passed by writing the return address / other address d[blank_start]irectl[blank_end]y
>> :( : we can use [blank_start]format[blank_end] string vulnerability to r[blank_start]ead[blank_end] the value of the canary- AStack
- Banarie
- Candom
- Directl
- Eformat
- Fead
- Godifi
8Non executable memory:
Typically you do not want to set x permission on a page that can be written during execution:
> The pages that contain code are e[blank_start]xecut[blank_end]able but not w[blank_start]rite[blank_end]able
> The pages that contain data are w[blank_start]rite[blank_end]able but not e[blank_start]xecut[blank_end]able
>> We can by-pass this by doing [blank_start]Return[blank_end] [blank_start]oriented[blank_end] programming (ROP)
Instead of writing ur code on the sack search for piece of code (gadgets) in the program that end with a r[blank_start]eturn[blank_end] instruction.
Put the a[blank_start]ddress[blank_end]es of these gadgets on the stack
The gadgets will be executed in sequence
- AReturn
- Boriented
- Ceturn
- Dddress
- Execut
- Frite
- Grite
- Hxecut
9A[blank_start]ddress[blank_end] s[blank_start]pace[blank_end] l[blank_start]ayout[blank_end] r[blank_start]andomisation[blank_end]:
> Every time a program is started, it is loaded at a r[blank_start]andom[blank_end] address
> Every time the system boots, the OS is loaded at r[blank_start]andom[blank_end] address
We can bypass ASLR:
> ASLR works by shifting addresses by a c[blank_start]onstant[blank_end] value
> The program might leak the address of a function / variable
> We can calculate other addresses based on that- Address
- Bpace
- Cayout
- Dandomisation
- Eandom
- Fandom
- Gonstant
10FormatString vulnerabilities:
> The [blank_start]first[blank_end] parameter is the format string
> %[blank_start]s[blank_end], parameter is the address of a string
> %[blank_start]d[blank_end], parameter is an integer
> parameters are read from the s[blank_start]tack[blank_end]
> printf doesn't know [blank_start]how[blank_end] many parameters are received
>> Peter%p%p%[blank_start]p[blank_end]%p%p%p%p%p%p will dump address that are on the stack, and we can read arbitrary memory with %[blank_start]s[blank_end] ( we can read the data at this address)
>> %[blank_start]n[blank_end] format spec allows to write the number of chars outputted by printf at the address given by the correspond- ing parameter!
To avoid that:
> the first parameter to printf should be a c[blank_start]onstant[blank_end]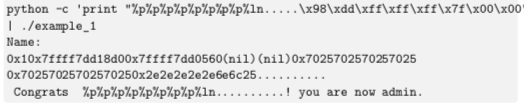
- Aonstant
- Bfirst
- Cd
- Ds
- Ehow
- Ftack
- Gp
- Hs
- In
11Stack canary not protect against format string exploits
- ARichtig
- BFalsch
12Stack canary can have a fixed value.
- ARichtig
- BFalsch
Informationen
- Beschreibung
- - Information security (2 Web app & Software vulnerabilities) Quiz am 2b Software vulnerabilities, erstellt von Yawen Hou am 08/06/2019.
- Autor
- Yawen Hou
- Sprache
- English
- Aufrufe
- 1
- Schlagwörter
- Bewertung
- Noch keine Bewertungen Bewerte dieses Quiz