
Quiz
TEST CERT
Erstelle ein kostenloses Konto, um dieses Quiz zu beenden
Speichere deinen Fortschritt und sieh dir dein Endergebnis an.
oder mit deiner E-Mail registrieren
Schon ein Konto? Anmelden
Fragen in diesem Quiz (116)
1For FortiGate devices equipped with Network Processor (NP) chips, which are true? (Choose three.)
- A For each new IP session, the first packet always goes to the CPU.
- BThe kernel does not need to program the NPU. When the NPU sees the traffic, it determines by itself whether it can process the traffic.
- C Once offloaded, unless there are errors, the NP forwards all subsequent packets. The CPU does not process them.
- D When the last packet is sent or received, such as a TCP FIN or TCP RST signal, the NP returns this session to the CPU for tear down.
- ESessions for policies that have a security profile enabled can be NP offloaded.
2In "diag debug flow" output, you see the message “Allowed by Policy-1: SNAT”. Which is true?
- AThe packet matched the topmost policy in the list of firewall policies.
- B The packet matched the firewall policy whose policy ID is 1.
- CThe packet matched a firewall policy which allows the packet and skips UTM checks.
- DThe policy allowed the packet and applied session NAT.
3Which is NOT true about the settings for an IP pool type port block allocation?
- AA Block Size defines the number of connections.
- BBlocks Per User defines the number of connection blocks for each user.
- C An Internal IP Range defines the IP addresses permitted to use the pool.
- DAn External IP Range defines the IP addresses in the pool.
4If you enable the option "Generate Logs when Session Starts", what effect does this have on the number of traffic log messages generated for each session?
- A No traffic log message is generated.
- BOne traffic log message is generated.
- CTwo traffic log messages are generated.
- DA log message is only generated if there is a security event.
5Which traffic can match a firewall policy's "Services" setting? (Choose three.)
- A HTTP
- BSSL
- CDNS
- DRSS
- E HTTPS
6Which correctly define "Section View" and "Global View" for firewall policies? (Choose two.)
- ASection View lists firewall policies primarily by their interface pairs.
- BSection View lists firewall policies primarily by their sequence number.
- CGlobal View lists firewall policies primarily by their interface pairs.
- DGlobal View lists firewall policies primarily by their policy sequence number.
- EThe 'any' interface may be used with Section View.
7Which is true of FortiGate's session table?
- ANAT/PAT is shown in the central NAT table, not the session table.
- B It shows TCP connection states.
- CIt shows IP, SSL, and HTTP sessions.
- D It does not show UDP or ICMP connection state codes, because those protocols are connectionless.
8Which is true about incoming and outgoing interfaces in firewall policies?
- A A physical interface may not be used.
- B A zone may not be used.
- CMultiple interfaces may not be used for both incoming and outgoing.
- DSource and destination interfaces are mandatory.
9Which is NOT true about source matching with firewall policies?
- A A source address object must be selected in the firewall policy.
- B A source user/group may be selected in the firewall policy.
- CA source device may be defined in the firewall policy.
- DA source interface must be selected in the firewall policy.
- EA source user/group and device must be specified in the firewall policy.
10Which define device identification? (Choose two.)
- ADevice identification is enabled by default on all interfaces.
- BEnabling a source device in a firewall policy enables device identification on the source interfaces of that policy.
- CYou cannot combine source user and source device in the same firewall policy.
- DFortiClient can be used as an agent based device identification technique.
- EOnly agentless device identification techniques are supported.
11Which are valid replies from a RADIUS server to an ACCESS-REQUEST packet from a FortiGate? (Choose two.)
- AACCESS-CHALLENGE
- BACCESS-RESTRICT
- C ACCESS-PENDING
- DACCESS-REJECT
12Which methods can FortiGate use to send a One Time Password (OTP) to Two-Factor Authentication users? (Choose three.)
- AHardware FortiToken
- BWeb Portal
- C Email
- D USB Token
- ESoftware FortiToken (FortiToken mobile)
13Which best describes the authentication timeout?
- A How long FortiGate waits for the user to enter his or her credentials.
- BHow long a user is allowed to send and receive traffic before he or she must authenticate again.
- CHow long an authenticated user can be idle (without sending traffic) before they must authenticate again.
- DHow long a user-authenticated session can exist without having to authenticate again.
14Which authentication methods does FortiGate support for firewall authentication? (Choose two.)
- ARemote Authentication Dial in User Service (RADIUS)
- BLightweight Directory Access Protocol (LDAP)
- CLocal Password Authentication
- DPOP3
- ERemote Password Authentication
15Which does FortiToken use as input when generating a token code? (Choose two.)
- AUser password
- BTime
- C User name
- DSeed
16Which authentication scheme is not supported by the RADIUS implementation on FortiGate?
- ACHAP
- BMSCHAP2
- CPAP
- D FSSO
17What protocol cannot be used with the active authentication type?
- ALocal
- BRADIUS
- C LDAP
- D RSSO
18Which user group types does FortiGate support for firewall authentication? (Choose three.)
- ARSSO
- BFirewall
- CLDAP
- DNTLM
- EFSSO
19What is not true of configuring disclaimers on the FortiGate?
- A Disclaimers can be used in conjunction with captive portal.
- BDisclaimers appear before users authenticate.
- CDisclaimers can be bypassed through security exemption lists.
- DDisclaimers must be accepted in order to continue to the authentication login or originally intended destination.
20When configuring LDAP on the FortiGate as a remote database for users, what is not a part of the configuration?
- AThe name of the attribute that identifies each user (Common Name Identifier).
- BThe user account or group element names (user DN).
- CThe server secret to allow for remote queries (Primary server secret).
- DThe credentials for an LDAP administrator (password).
21Which statement best describes what SSL VPN Client Integrity Check does?
- A Blocks SSL VPN connection attempts from users that has been blacklisted.
- BDetects the Windows client security applications running in the SSL VPN client's PCs
- C Validates the SSL VPN user credential.
- DVerifies which SSL VPN portal must be presented to each SSL VPN user.
- E Verifies that the latest SSL VPN client is installed in the client's PC.
22Which statement best describes what SSL.root is?
- AThe name of the virtual network adapter required in each user's PC for SSL VPN Tunnel mode.
- Bhe name of a virtual interface in the root VDOM where all the SSL VPN user traffic comes from
- CA Firewall Address object that contains the IP addresses assigned to SSL VPN users.
- D The virtual interface in the root VDOM that the remote SSL VPN tunnels connect to.
23Which of the following authentication methods can be used for SSL VPN authentication? (Choose three.)
- A Remote Password Authentication (RADIUS, LDAP)
- BTwo-Factor Authentication
- C Local Password Authentication
- DFSSO
- ERSSO
24A FortiGate is configured with the 1.1.1.1/24 address on the wan2 interface and HTTPS Administrative Access, using the default tcp port, is enabled for that interface. Given the SSL VPN settings in the exhibit. Which of the following SSL VPN login portal URLs are valid? (Choose two.)
- Ahttp://1.1.1.1:443/Training
- Bhttps://1.1.1.1:443/STUDENTS
- Chttps://1.1.1.1/login
- D https://1.1.1.1/
25Which of the following statements are correct regarding SSL VPN Web-only mode? (Choose two.)
- A It can only be used to connect to web services.
- BIP traffic is encapsulated over HTTPS.
- CAccess to internal network resources is possible from the SSL VPN portal.
- DThe standalone FortiClient SSL VPN client CANNOT be used to establish a Web-only SSL VPN.
- E It is not possible to connect to SSH servers through the VPN.
26Which statement is not correct regarding SSL VPN Tunnel mode?
- A IP traffic is encapsulated over HTTPS.
- BThe standalone FortiClient SSL VPN client can be used to establish a Tunnel mode SSL VPN.
- CA limited amount of IP applications are supported.
- DThe FortiGate device will dynamically assign an IP address to the SSL VPN network adapter.
- A IP traffic is encapsulated over HTTPS.
27Which of the following statements are true about IPsec VPNs? (Choose three.)
- AIPsec increases overhead and bandwidth.
- BIPsec operates at the layer 2 of the OSI model.
- CEnd-user's network applications must be properly pre-configured to send traffic across the IPsec VPN.
- DIPsec protects upper layer protocols.
- EIPsec operates at the layer 3 of the OSI model.
28Which of the following statements is true regarding the differences between route-based and policy-based IPsec VPNs? (Choose two.)
- AThe firewall policies for policy-based are bidirectional. The firewall policies for route-based are unidirectional.
- BIn policy-based VPNs the traffic crossing the tunnel must be routed to the virtual IPsec interface. In route-based, it does not.
- CThe action for firewall policies for route-based VPNs may be Accept or Deny, for policy-based VPNs it is Encrypt.
- DPolicy-based VPN uses an IPsec interface, route-based does not.
29Which of the following IPsec configuration modes can be used for implementing L2TP-over-IPSec VPNs?
- APolicy-based IPsec only.
- BRoute-based IPsec only.
- CBoth policy-based and route-based VPN.
- DL2TP-over-IPSec is not supported by FortiGate devices.
30Which of the following authentication methods are supported in an IPsec phase 1? (Choose two.)
- AAsymmetric Keys
- BCA root digital certificates
- CRSA signature
- DPre-shared keys
31How many packets are interchanged between both IPSec ends during the negotiation of a main-mode phase 1?
- A5
- B3
- C2
- D6
32Which of the following IPsec configuration modes can be used when the FortiGate is running in NAT mode?
- APolicy-based VPN only
- BBoth policy-based and route-based VPN.
- CRoute-based VPN only.
- DD. IPSec VPNs are not supported when the FortiGate is running in NAT mode.
33Which portion of the configuration does an administrator specify the type of IPsec configuration (either policy-based or route-based)?
- AUnder the IPsec VPN global settings.
- BUnder the phase 2 settings.
- CUnder the phase 1 settings.
- DUnder the firewall policy settings.
34Which of the following IKE modes is the one used during the IPsec phase 2 negotiation
- AAggressive mode
- BQuick mode
- CMain mode
- DFast mode
35Which of the following options best defines what Diffie-Hellman is?
- AA symmetric encryption algorithm.
- BA "key-agreement" protocol.
- CA "Security-association-agreement" protocol.
- DAn authentication algorithm
36What action does an IPsec Gateway take with the user traffic routed to an IPsec VPN when it does not match any phase 2 quick mode selector?
- ATraffic is dropped.
- BTraffic is routed across the default phase 2.
- CTraffic is routed to the next available route in the routing table.
- DTraffic is routed unencrypted to the interface where the IPsec VPN is terminating.
37An Internet browser is using the WPAD DNS method to discover the PAC file’s URL. The DNS server replies to the browser’s request with the IP address 10.100.1.10. Which URL will the browser use to download the PAC file?
- ATest
FortiGate I: 07. Explicit Proxy Quiz
Question 1 of 6
An Internet browser is using the WPAD DNS method to discover the PAC file’s URL. The DNS server replies to the browser’s request with the IP address 10.100.1.10. Which URL will the browser use to download the PAC file?
http://10.100.1.10/proxy.pac
https://10.100.1.10/
http://10.100.1.10/wpad.dat
https://10.100.1.10/proxy.pac - Bhttps://10.100.1.10/
- Chttp://10.100.1.10/wpad.dat
- Dhttps://10.100.1.10/proxy.pac
- ATest
38Which of the following statements is true regarding the TCP SYN packets that go from a client, through an implicit web proxy (transparent proxy), to a web server listening at TCP port 80? (Choose three.)
- AThe source IP address matches the client IP address.
- BThe source IP address matches the proxy IP address.
- CThe destination IP address matches the proxy IP address.
- DThe destination IP address matches the server IP addresses.
- EThe destination TCP port number is 80.
39
Review the exhibit of an explicit proxy policy configuration. If there is a proxy connection attempt coming from the IP address 10.0.1.5, and from a user that has not authenticated yet, what action does the FortiGate proxy take?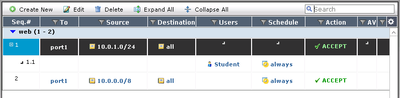
- AUser is prompted to authenticate. Traffic from the user Student will be allowed by the policy #1. Traffic from any other user will be allowed by the policy #2.
- BUser is not prompted to authenticate. The connection is allowed by the proxy policy #2.
- CUser is not prompted to authenticate. The connection will be allowed by the proxy policy #1.
- DUser is prompted to authenticate. Only traffic from the user Student will be allowed. Traffic from any other user will be blocked.
40Which protocol can an Internet browser use to download the PAC file with the web proxy configuration?
- AHTTPS
- BFTP
- CTFTP
- DHTTP
41Which of the following are benefits of using web caching? (Choose three.)
- ADecrease bandwidth utilization
- BReduce server load
- CReduce FortiGate CPU usage
- DReduce FortiGate memory usage
- EDecrease traffic delay
42Question 6 of 6
Which of the following statements is true regarding the use of a PAC file to configure the web proxy settings in an Internet browser? (Choose two.)- AMore than one proxy is supported.
- BCan contain a list of destinations that will be exempt from the use of any proxy.
- CCan contain a list of URLs that will be exempted from the FortiGate web filtering inspection.
- DCan contain a list of users that will be exempted from the use of any proxy.
43What is longest length of time allowed on a FortiGate device for the virus scan to complete?
- A20 seconds
- B30 seconds
- C45 seconds
- D10 seconds
44Which type of conserve mode writes a log message immediately, rather than when the device exits conserve mode?
- AKernel
- BProxy
- CSystem
- DDevice
45Files that are larger than the oversized limit are subjected to which Antivirus check?
- AGrayware
- BVirus
- CSandbox
- DHeuristic
46Files reported to be infected by the "Suspicious" virus were subject to which Antivirus check?
- AGrayware
- BVirus
- CSandbox
- DHeuristic
47Which are the three different types of Conserve Mode that can occur on a FortiGate device? (Choose three.)
- AProxy
- BOperating system
- CKernel
- DSystem
- EDevice
48A FortiGate device is configure to perform an AV & IPS scheduled update every hour. Given the information in the exhibit, when will the next update happen?
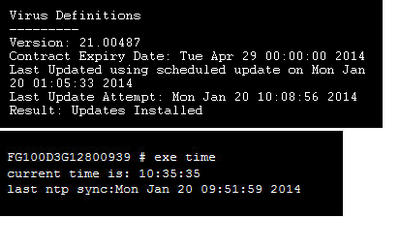
- A01:00
- B02:05
- C11:00
- D11:08
49What is the maximum number of different virus databases a FortiGate can have?
- A5
- B2
- C3
- D4
50Which of the following are possible actions for static URL filtering? (Choose three.)
- AAllow
- BBlock
- CExempt
- DWarning
- EShape
51Which of the following are possible actions for FortiGuard web category filtering? (Choose three.)
- AAllow
- BBlock
- CExempt
- DWarning
- EShape
52Examine the following log message attributes and select two correct statements from the list below. (Choose two.) hostname=www.youtube.com profiletype="Webfilter_Profile" profile="default" status="passthrough" msg="URL belongs to a category with warnings enabled"
- AThe traffic was blocked.
- BThe user failed authentication.
- CThe category action was set to warning.
- DThe website was allowed.
53Which of the following actions can be used with the FortiGuard quota feature? (Choose three.)
- AAllow
- BBlock
- CMonitor
- DWarning
- EAuthenticate
54Which of the following statements are true regarding the web filtering modes? (Choose two.)
- AProxy based mode allows for customizable block pages to display when sites are prevented.
- BProxy based mode requires more resources than flow-based.
- CFlow based mode offers more settings under the advanced configuration section of the GUI.
- DProxy based mode offers higher throughput than flow-based mode.
55Which of the following web filtering modes can inspect the full URL? (Choose two.)
- AProxy based
- BDNS based
- CPolicy based
- DFlow based
56The exhibit is a screen shot of an Application Control profile. Different settings are circled and numbered. Select the number identifying the setting which will provide additional information about YouTube access, such as the name of the video watched.
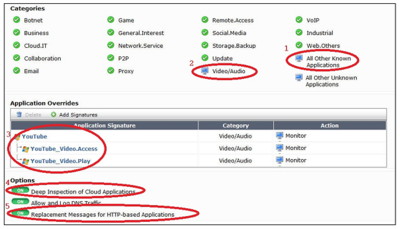
- A1
- B2
- C3
- D4
- E5
57Which of the following statements are true regarding application control? (Choose two.)
- AApplication control is based on TCP destination port numbers.
- BApplication control is proxy based.
- CEncrypted traffic can be identified by application control.
- DTraffic shaping can be applied to the detected application traffic.
58Which answer best describes what an "Unknown Application" is?
- AAll traffic that matches the internal signature for unknown applications.
- BTraffic that does not match the RFC pattern for its protocol.
- CAny traffic that does not match an application control signature.
- DA packet that fails the CRC check.
59What actions are possible with Application Control? (Choose three.)
- AWarn
- BAllow
- CBlock
- DTraffic Shaping
- EQuarantine
60How do application control signatures update on a FortiGate device?
- AThrough FortiGuard updates.
- BUpgrade the FortiOS firmware to a newer release.
- CBy running the Application Control auto-learning feature.
- DSignatures are hard coded to the device and cannot be updated.
61The exhibit shows two static routes to the same destination subnet 172.20.168.0/24. Which of the following statements correctly describes this static routing configuration? (Choose two.)
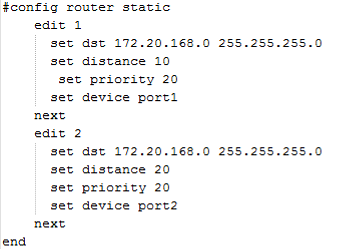
- ABoth routes will show up in the routing table.
- BThe FortiGate unit will evenly share the traffic to 172.20.168.0/24 between both routes.
- COnly one route will show up in the routing table.
- DThe FortiGate will route the traffic to 172.20.168.0/24 only through one route.
62Which of the following fields contained in the IP/TCP/UDP headers can be used to make a routing decision when using policy-based routing? (Choose three.)
- ASource IP address
- BTCP flags
- CSource TCP/UDP port
- DType of service
- EChecksum
63Which of the following statements are true regarding WAN Link Load Balancing? (Choose two.)
- AThere can be only one virtual WAN Link per VDOM.
- BFortiGate can measure the quality of each link based on latency, jitter, or lost packets percentage.
- CLink health check can be performed over each link member of the virtual WAN interface.
- DDistance and priority values are configured in each link member of the virtual WAN interface.
64The exhibit shows a FortiGate routing table. Which of the following statements are correct? (Choose two.)
- AThere is only one active default route.
- BThe distance value for the route to 192.168.1.0/24 is 200.
- CAn IP address in the subnet 172.16.78.0/24 has been assigned to the dmz interface.
- DThe FortiGate will route the traffic to 172.17.1.2 to the next hop with the IP address 192.168.11.254.
65Which of the following statements best describes what a FortiGate does when packets match a black hole route?
- APackets are dropped.
- BPackets are routed based on the information in the policy-based routing table.
- CAn ICMP error message is sent back to the originator.
- DPackets are routed back to the originator.
66The exhibit shows three static routes. Which static route(s) will be used to route the packets to the destination IP address 172.20.168.1?
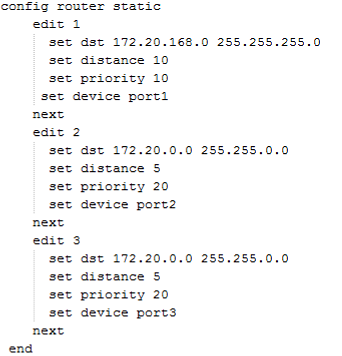
- AThe routes with the ID numbers 2 and 3.
- BOnly the route with the ID number 3.
- COnly the route with the ID number 2.
- DOnly the route with the ID number 1.
67What must be configures in order to keep two static routes to the same destination in the routing table?
- AThe same priority.
- BThe same distance and same priority.
- CThe same distance.
- DThe same metric.
68Which action does the FortiGate take when link health monitor times out?
- AAll routes to the destination subnet configured in the link health monitor are removed from the routing table.
- BThe distance values of all routes using the interface configured in the link health monitor are increased.
- CThe priority values of all routes using the interface configured in the link health monitor are increased.
- DAll routes using the next-hop gateway configured in the link health monitor are removed from the routing table.
69In the debug command output shown in the exhibit, which of the following best describes the MAC address 00:09:0f:69:03:7e?
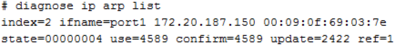
- AIt is one of the secondary MAC addresses of the port1 interface.
- BIt is the primary MAC address of the port1 interface.
- CIt is the MAC address of another network device located in the same LAN segment as the FortiGate unit’s port1 interface.
- DIt is the HA virtual MAC address.
70Examine the network topology diagram in the exhibit; the workstation with the IP address 212.10.11.110 sends a TCP SYN packet to the workstation with the IP address 212.10.11.20. Which of the following sentences best describes the result of the reverse path forwarding (RPF) check executed by the FortiGate on the SYN packet? (Choose two.)
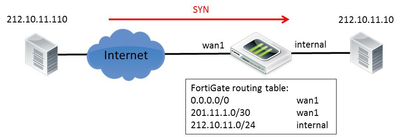
- APacket is allowed if RPF is configured as loose.
- BPacket is allowed if RPF is configured as strict.
- CPacket is blocked if RPF is configured as loose.
- DPacket is blocked if RPF is configured as strict.
71A FortiGate device has two VDOMs in NAT/route mode. Which of the following solutions can be implemented by a network administrator to route traffic between the two VDOMs? (Choose two.)
- AUse the inter-VDOM links automatically created between all VDOMS.
- BManually create and configure an inter-VDOM link between your two VDOMs.
- CInterconnect and configure an external physical interface in one VDOM to another physical interface in the second VDOM.
- DConfigure both VDOMs to share the same routing table.
72Which of the following settings can be configured per VDOM? (Choose three.)
- AOperating mode (NAT/route or transparent)
- BStatic routes
- CHostname
- DSystem time
- EFirewall policies
73Which of the following statements are correct regarding FortiGate virtual domains (VDOMs)? (Choose two.)
- AVDOMs divide a single FortiGate unit into two or more independent firewalls.
- BA management VDOM handles SNMP, logging, alert email, and FortiGuard updates.
- CEach VDOM can run different firmware versions.
- DAdministrative users with a ‘super_admin’ profile can administrate only one VDOM.
74Which of the following statements is correct concerning multiple VDOMs configured in a FortiGate device?
- AFortiGate devices, from the FGT/FWF 60D and above, all support VDOMS.
- BAll FortiGate devices scale to 250 VDOMS.
- CEach VDOM requires its own FortiGuard license.
- DFortiGate devices support more NAT/Route VDOMs than Transparent Mode VDOMs.
75A FortiGate device is configured with two VDOMs. The management VDOM is 'root', and is configured in transparent mode, 'vdom1' is configured as NAT/route mode. Which traffic is generated only by 'root' and not 'vdom1'? (Choose three.)
- ASNMP traps
- BFortiGuard
- CARP
- DNTP
- EICMP redirect
76A FortiGate unit is operating in NAT/route mode and configured with two VLAN sub-interfaces on the same physical interface. Which of the following statement is correct regarding the VLAN IDs in this scenario?
- AThe two VLAN sub-interfaces can have the same VLAN ID only if they have IP addresses in different subnets.
- BThe two VLAN sub-interfaces must have different VLAN IDs.
- CThe two VLAN sub-interfaces can have the same VLAN ID only if they belong to different VDOMs.
- DThe two VLAN sub-interfaces can have the same VLAN ID if they are connected to different L2 IEEE 802.1Q compliant switches.
77A FortiGate unit has multiple VDOMs in NAT/route mode with multiple VLAN interfaces in each VDOM. Which of the following statements is correct regarding the IP addresses assigned to each VLAN interface?
- ADifferent VLANs can share the same IP address as long as they have different VLAN IDs.
- BDifferent VLANs can share the same IP address as long as they are in different physical interfaces.
- CDifferent VLANs can share the same IP address as long as they are in different VDOMs.
- DDifferent VLANs can never share the same IP addresses.
78A FortiGate device is configured with four VDOMs: 'root' and 'vdom1' are in NAT/route mode; 'vdom2' and 'vdom3' are in transparent mode. The management VDOM is 'root'. Which of the following statements are true? (Choose two.)
- AAn inter-VDOM link between 'root' and 'vdom1' can be created.
- BAn inter-VDOM link between 'vdom1' and 'vdom2' can be created.
- CAn inter-VDOM link between 'vdom2 ' and 'vdom3' can be created.
- DInter-VDOM link links must be manually configured for FortiGuard traffic.
79Which of the following statements are correct differences between NAT/route and transparent mode? (Choose two.)
- AIn transparent mode, interfaces do not have IP addresses.
- BFirewall policies are only used in NAT/route mode.
- CStatic routes are only used in NAT/route mode.
- DOnly transparent mode permits inline traffic inspection at layer 2.
80What is the default criteria for selecting the HA master unit in a HA cluster?
- Aport monitor, priority, uptime, serial number
- Bport monitor, uptime, priority, serial number
- Cpriority, uptime, port monitor, serial number
- Duptime, priority, port monitor, serial number
81Which of the following statements describes the objective of the gratuitous ARP packets sent by an HA cluster?
- ATo synchronize the ARP tables in all the FortiGate units that are part of the HA cluster.
- BTo notify the network switches that a new HA master unit has been elected.
- CTo notify the master unit that the slave devices are still up and alive.
- DTo notify the master unit about the physical MAC addresses of the slave units.
82What information is synchronized between two FortiGate units that belong to the same HA cluster? (Choose three.)
- AIP addresses assigned to DHCP enabled interfaces.
- BThe master device's hostname.
- CRouting configuration and state.
- DReserved HA management interface IP configuration.
- EFirewall policies and objects.
83What are required to be the same for two FortiGate units to form an HA cluster? (Choose two.)
- AFirmware
- BModel
- CHostname
- DSystem time zone
84Which statement describes how traffic flows in sessions handled by a slave unit in an active-active HA cluster?
- APackets are sent directly to the slave unit using the slave physical MAC address.
- BPackets are sent directly to the slave unit using the HA virtual MAC address.
- CPackets arrive at both units simultaneously, but only the slave unit forwards the session.
- DPackets are first sent to the master unit, which then forwards the packets to the slave unit.
85Which of the following statements correctly describes the use of the “diagnose sys ha reset-uptime” command?
- ATo force an HA failover when the HA override setting is disabled.
- BTo force an HA failover when the HA override setting is enabled.
- CTo clear the HA counters.
- DTo restart a FortiGate unit that is part of an HA cluster.
86Which of the following statements are correct regarding a master HA unit? (Choose two.)
- AThere should be only one master unit is each HA virtual cluster.
- BThe master synchronizes cluster configuration with slaves.
- COnly the master has a reserved management HA interface.
- DHeartbeat interfaces are not required on a master unit.
87Which of the following statements are correct concerning the FortiGate session life support protocol? (Choose two.)
- ABy default, UDP sessions are not synchronized.
- BUp to four FortiGate devices in standalone mode are supported.
- COnly the master unit handles the traffic.
- DAllows per-VDOM session synchronization.
88What configuration objects are automatically added when using the FortiGate's FortiClient VPN Configuration Wizard? (Choose two.)
- AStatic route
- BPhase 1
- CUser group
- DPhase 2
89Which of the following statements are correct concerning IPsec dialup VPN configurations for FortiGate devices? (Choose two.)
- AMain mode must be used when there is more than one IPsec dialup VPN configure on the same FortiGate device.
- BA FortiGate device with an IPsec VPN configured as dialup can initiate the tunnel connection to any remote IP address.
- CPeer ID must be used when there is more than one aggressive-mode IPsec dialup VPN on the same FortiGate device.
- DThe FortiGate will automatically add a static route to the source quick mode selector address received from each remote peer.
90Which statement is correct concerning an IPsec VPN with the remote gateway setting configured as 'Dynamic DNS'?
- AThe FortiGate will accept IPsec VPN connections from any IP address.
- BThe FQDN resolution of the local FortiGate IP address where the VPN is terminated must be provided by a dynamic DNS provider.
- CThe FortiGate will accept IPsec VPN connections only from IP addresses included in a dynamic DNS access list.
- DThe remote gateway IP address can change dynamically.
91The exhibit shows a part output of the diagnostic command 'diagnose debug application ike 255', taken during the establishment of a VPN. Which of the following statements are correct concerning this output? (Choose two.)
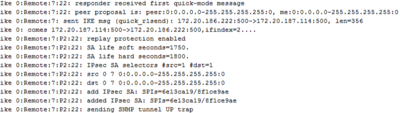
- AThe quick mode selectors negotiated between both IPsec VPN peers is 0.0.0.0/32 for both the source and destination addresses.
- BThe output corresponds to a phase 2 negotiation.
- CNAT-T is enabled and there is a third device in the path performing NAT of the traffic between both IPsec VPN peers.
- DThe IP address of the remote IPsec VPN peer is 172.20.187.114.
92Which of the following combinations of two FortiGate device configurations (side A and side B), can be used to successfully establish an IPsec VPN between them? (Choose two.)
- ASide A: main mode, remote gateway as static IP address, policy-based VPN. Side B: aggressive Mode, remote Gateway as static IP address, policy-based VPN.
- BSide A: main mode, remote gateway as static IP Address, policy-based VPN. Side B: main mode, remote gateway as static IP address, route-based VPN.
- CSide A: main mode, remote gateway as static IP address, route-based VPN. Side B: main mode, remote gateway as dialup, route-based VPN.
- DSide A: main mode, remote gateway as dialup, policy-based VPN. Side B: main mode, remote gateway as dialup, policy-based VPN.
93Which of the following statements are correct concerning the IPsec phase 1 and phase 2, shown in the exhibit? (Choose two.)
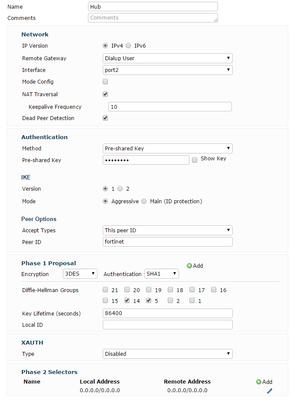
- AThe quick mode selector in the remote site must also be 0.0.0.0/0 for the source and destination addresses.
- BOnly remote peers with the peer ID 'fortinet' will be able to establish a VPN.
- CThe FortiGate device will automatically add a static route to the source quick mode selector address received from each remote VPN peer.
- DThe configuration will work only to establish FortiClient-to-FortiGate tunnels. A FortiGate-to-FortiGate tunnel requires a different configuration.
94What is required in a FortiGate configuration to have more than one dialup IPsec VPN using aggressive mode?
- AAll the aggressive mode dialup VPNs MUST accept connections from the same peer ID.
- BEach peer ID MUST match the FQDN of each remote peer.
- CEach aggressive mode dialup MUST accept connections from different peer ID.
- DThe peer ID setting must NOT be used.
95Which of the following protocols are defined in the IPsec Standard? (Choose two.)
- AAH
- BGRE
- CSSL/TLS
- DESP
96Which of the following statements are correct concerning IKE mode config? (Choose two.)
- AIt can dynamically assign IP addresses to IPsec VPN clients.
- BIt can dynamically assign DNS settings to IPsec VPN clients.
- CIt uses the ESP protocol.
- DIt can be enabled in the phase 2 configuration.
97You have configured the DHCP server on a FortiGate's port1 interface (or internal, depending on the model) to offer IPs in a range of 192.168.1.65-192.168.1.253. When the first host sends a DHCP request, what IP will the DHCP offer?
- A 192.168.1.99
- B192.168.1.253
- C192.168.1.65
- D192.168.1.66
98Which is not a FortiGate feature?
- A Database auditing
- B Intrusion prevention
- CWeb filtering
- D Application control
99Which UTM feature sends a UDP query to FortiGuard servers each time FortiGate scans a packet (unless the response is locally cached)?
- AAntivirus
- B VPN
- C IPS
- DWeb Filtering
100You have created a new administrator account, and assign it the prof_admin profile. Which is false about that account's permissions?
- AIt cannot upgrade or downgrade firmware.
- BIt can create and assign administrator accounts to parts of its own VDOM.
- CIt can reset forgotten passwords for other administrator accounts such as "admin".
- DIt has a smaller permissions scope than accounts with the "super_admin" profile.
101When an administrator attempts to manage FortiGate from an IP address that is not a trusted host, what happens?
- A FortiGate will still subject that person's traffic to firewall policies; it will not bypass them.
- B FortiGate will drop the packets and not respond.
- C FortiGate responds with a block message, indicating that it will not allow that person to log in.
- DFortiGate responds only if the administrator uses a secure protocol. Otherwise, it does not respond.
102Acme Web Hosting is replacing one of their firewalls with a FortiGate. It must be able to apply port forwarding to their back-end web servers while blocking virus uploads and TCP SYN floods from attackers. Which operation mode is the best choice for these requirements?
- ANAT/route
- BNAT mode with an interface in one-arm sniffer mode
- CTransparent mode
- DNo appropriate operation mode exists
103if you have lost your password for the "admin" account on your FortiGate, how should you reset it?
- ALog in with another administrator account that has "super_admin" profile permissions, then reset the password for the "admin" account.
- BReboot the FortiGate. Via the local console, during the boot loader, use the menu to format the flash disk and reinstall the firmware. Then you can log in with the default password.
- CPower off the FortiGate. After several seconds, restart it. Via the local console, within 30 seconds after booting has completed, log in as "maintainer" and enter the CLI commands to set the password for the "admin" account.
- DReboot the FortiGate. Via the local console, during the boot loader, use the menu to log in as "maintainer" and enter the CLI commands to set the password for the "admin" account.
104A backup file begins with this line: #config-version=FGVM64-5.02-FW-build589-140613:opmode=0:vdom=0:user=admin #conf_file_ver=3881503152630288414 #buildno=0589 #global_vdom=1 Can you restore it to a FortiWiFi 60D?
- AYes
- BYes, but only if you replace the "#conf_file_ver" line so that it contains the serial number of that specific FortiWiFi 60D.
- CYes, but only if it is running the same version of FortiOS, or a newer compatible version.
- DNo
105Which protocols can you use for secure administrative access to a FortiGate? (Choose two)
- ASSH
- BTelnet
- CNTLM
- DHTTPS
106A new version of FortiOS firmware has just been released. When you upload new firmware, which is true?
- A If you upload the firmware image via the boot loader's menu from a TFTP server, it will not preserve the configuration. But if you upload new firmware via the GUI or CLI, as long as you are following a supported upgrade path, FortiOS will attempt to convert the existing configuration to be valid with any new or changed syntax.
- B No settings are preserved. You must completely reconfigure.
- CNo settings are preserved. After the upgrade, you must upload a configuration backup file. FortiOS will ignore any commands that are not valid in the new OS. In those cases, you must reconfigure settings that are not compatible with the new firmware.
- DYou must use FortiConverter to convert a backup configuration file into the syntax required by the new FortiOS, then upload it to FortiGate.
107In a Crash log, what does a status of 0 indicate?
- AAbnormal termination of a process
- BA process closed for any reason
- CNormal shutdown with no abnormalities
- DDHCP process crashed
108Which of the following are considered log types? (Choose three.)
- AForward log
- BTraffic log
- CSyslog
- DEvent log
- ESecurity log
109What determines whether a log message is generated or not?
- AFirewall policy setting
- BLog Settings in the GUI
- C 'config log' command in the CLI
- DSyslog
- EWebtrends
110Where are most of the security events logged?
- ASecurity log
- BForward Traffic log
- CEvent log
- DAlert log
- E Alert Monitoring Console
111What are the ways FortiGate can monitor logs? (Choose three.)
- AMIB
- BSMS
- CAlert Emails
- DSNMP
- EFortiAnalyzer
- FAlert Message Console
112What attributes are always included in a log header? (Choose three.)
- Apolicyid
- Blevel
- Cuser
- Dtime
- Esubtype
- Fduration
113Examine this log entry. What does the log indicate? (Choose three.) date=2013-12-04 time=09:30:18 logid=0100032001 type=event subtype=system level=information vd="root" user="admin" ui=http(192.168.1.112) action=login status=success reason=none profile="super_admin" msg="Administrator admin logged in successfully from http(192.168.1.112)"
- AIn the GUI, the log entry was located under “Log & Report > Event Log > User”.
- B In the GUI, the log entry was located under “Log & Report > Event Log > System”.
- CIn the GUI, the log entry was located under “Log & Report > Traffic Log > Local Traffic”.
- DThe connection was encrypted
- EThe connection was unencrypted.
- F The IP of the FortiGate interface that “admin” connected to was 192.168.1.112.
- GThe IP of the computer that “admin” connected from was 192.168.1.112.
114To which remote device can the FortiGate send logs? (Choose three.)
- ASyslog
- BFortiAnalyzer
- C Hard drive
- DMemory
- EFortiCloud
115What log type would indicate whether a VPN is going up or down?
- AEvent log
- BSecurity log
- CForward log
- DSyslog
116There are eight (8) log severity levels that indicate the importance of an event. Not including Debug, which is only needed to log diagnostic data, what are both the lowest AND highest severity levels?
- ANotification, Emergency
- B Information, Critical
- CError, Critical
- D Information, Emergency
- E Information, Alert
Informationen
- Beschreibung
- Test de Certificación
- Autor
- sebastianzo
- Sprache
- Español
- Aufrufe
- 2.992
- Schlagwörter
- Bewertung
- 3,0 von 5 · 1 Bewertung Bewerte dieses Quiz