
Quiz
Cyber Security Test-1
Erstelle ein kostenloses Konto, um dieses Quiz zu beenden
Speichere deinen Fortschritt und sieh dir dein Endergebnis an.
oder mit deiner E-Mail registrieren
Schon ein Konto? Anmelden
Fragen in diesem Quiz (120)
1Security is a state or quality of being secure to be free from--------------.
- AVulnerability
- BAttack
- CThreat
- DDanger
2Which term among the following is correct?
- ACybersecurity
- BCyber-security
- Ccyber security
- DAll are correct
3What does “cyber” meanin the context of Information Technology?
- ASoftware
- BHardware
- CNetwork
- DOnline World
4Cyber security affects individuals, organizations, society and --------------------
- AGovernment
- BInstitution
- CDepartment
- DFirms
5Choose the odd one
- APhishing attack
- BDenial of Service attack
- CSQL Injection
- DMan in the middle attack
- EImporting data
6Restricting unauthorized access and misuse of physical assets helps in achieving physical security of an organization.
- ARichtig
- BFalsch
7Cybersecurity is the collection of tools, policies, security concepts, security safeguards, guidelines, risk management approaches, actions, training, best practices, assurance and technologies that can be used to protect the cyber environment , organization and
- Ausers’ cyber assets
- Buser personal information
- Ccyberspace
- Dresource
8The general security objectives comprise -------------------,Availability and Integrity
- AConfidentiality
- BAccountability
- CAuthorization
- DAuthentication
9Network security involves protection of items, objects, or facilities.
- ARichtig
- BFalsch
10What term describes the quality or state of ownership or control of information?
- Aconfidentiality
- Bpossession
- Cauthenticity
- Dintegrity
11Fill in the blanks
The McCumber Cube has -------------------dimensions with -------cells representing areas that must be addressed to secure today’s information systems.- A7 and 21
- B4 and 27
- C3 and 18
- D3 and 27
12------------------is a weakness or fault in a system or protection mechanism that opens it to attack or damage.
- AThreat
- BVulnerability
- CRisk
- DAttack
13Which of the following is not a component of an organization’s Information System?
(1) Software (2) Vendors (3) People (4) Government (5) ISPs- A1&3
- B1,2 &4
- C4 & 5
- D2,4, & 5
14True or False:
The person responsible for the storage, maintenance, and protection of information is the data custodian.- ARichtig
- BFalsch
15Biometric data collected from users is used for-------------------------------------------- process.
- AAuthentication
- BAuthorization
- CAccountability
- DPrivacy
16Select the right options of the C.I.A. triad
(1) Assurance that information is shared only among authorized people or organizations
(2) Assurance that the information is complete and uncorrupted
(3) Assurance that information systems and the necessary data are not available for use when needed- A(1) True (2) False (3) True
- B(1) False (2) False (3) True
- C(1) True (2) True (3) True
- D(1) True (2) True (3) False
17Match the following:
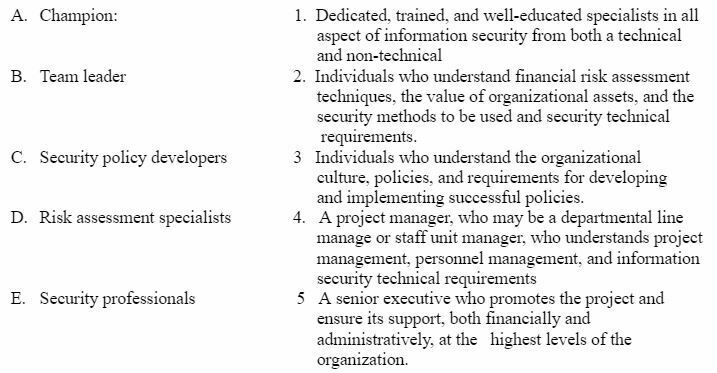
- AA-1, B-3, C-4, D-2, E-5
- BA-3, B-4, C-5, D-1, E-2
- CA-5, B-4, C-3, D-2, E-1
- DA-1, B-2, C-3, D-4, E-5
18Who are responsible for the security and use of a particular set of information?
- AData users
- BData exporter
- CData custodians
- DData owner
19True or False:
If information has a state of being genuine or original and is not a fabrication, it has the characteristic of authenticity.- ARichtig
- BFalsch
20Which of the following terms best describe the specification of a model to be followed during the design, selection, and initial and ongoing implementation of all subsequent security controls?
- ABlueprint
- BNIST handbook
- CAn information security framework
- DSecurity plan
21True or False: SP 800-18, Guide for Developing Security Plans, is considered the foundation for a comprehensive security blueprint and framework.
- ARichtig
- BFalsch
22One of the foundations of security architectures is the requirement to implement security in layers. This layered approach is referred to as:
- Amanagerial controls
- Bsecurity domain
- Credundancy
- Ddefense in depth
23Control Objectives for Information and Related Technologies is a framework created by ------ for information technology (IT) management and -------------
- AHIPPA, & Information officer
- BSO, & Security officer
- CISACA, & IT governance
- DCISO, & Chief officer
24Three approaches to cyber security management are
1. Governance-Risk-Compliance (GRC) approach
2. ---------------------------------------------------
3. Organizational planning approach- AInformation-driven approach
- BSecurity-driven approach
- CStandards-driven approach
- DProcedure-driven approach
25SO/IEC 27032:2012 involves guidelines for -----------------
- ANetwork security
- BCyber security
- CRisk Management
- DGovernance of information security
26The five goals of information security governance are
1. -----------------of information security with business strategy to support organizational objectives
2. ---------------- by executing appropriate measures to manage and mitigate threats to information resources
3. -----------------by utilizing information security knowledge and infrastructure efficiently and effectively
4. -----------------by measuring, monitoring, and reporting information security governance metrics to ensure that organizational objectives are achieved
5. -----------------by optimizing information security investments in support of organizational objectives.
A. Strategic alignment
B. Risk management
C. Resource management
D. Performance measurement
E. Value delivery
Match the following- A1-B,2-C,3-D,4-C,5-A,
- B1-C,2-B,3-A,4-B,5-E
- C1-E,2-C,3-A,4-B,5-D
- D1-A,2-B,3-C,4-D,5-E,
27Match ISO Series with the corresponding topic
(A) 27000 (1)Series Overview and Terminology
(B) 27003 (2)Information Security Management Systems Implementation Guidelines
(C) 27004 (3) Information Security Measurements and Metrics
(D) 27005 (4) ISMS Risk Management
(E) 27006 (5) Requirements for Bodies Providing Audit and Certification of ISMS- AA-1, B-2,C-3, D-4, E-5
- BA-4, B-2, C-3, D-1, E-5
- CA-2,B-1,C-3,D-5,E-4
- DA-3,B-2,C-1,D-5,E-4
28(1)------------------ is authorized by policy from senior management and is usually carried out by senior IT and information security executives, such as the(2)---------and-(3)-------
- A1- ISG 2- CIO, 3- CISO
- B1-CO,2, 2-CIO,3- CISO
- C1-CISO, 2-CIO, 3-CO
- D1-CISO, 2-ISG, 3-CO
29Which term is used to describe detailed statements of what must be done to comply with policy?
- APolicies
- BStandards
- CEthics
- DGovernance
30Management must use -------------------as the basis for all information security planning, design, and deployment.
- AStandards
- BProcedures
- CPolicies
- DBest business practices
31Which type of planning ensures that critical business functions continue if a catastrophic incident or disaster occurs?
- ABusiness continuity planning (BCP)
- BContingency planning (CP)
- CBusiness resumption planning (BRP)
- DDisaster recovery planning (DRP)
32-------------- policy can be separated into two general groups (a) managerial guidance and (b) technical specifications. Select the correct options
- ASystems-Specific Security
- BIssue-Specific Security
- CEnterprise Information Security
- DNone of these
33The actions taken during and after a disaster falls under ----------------
- AImpact assessment
- BRisk management
- CCrisis management
- DBoth (a) & (b)
34Special Publication 800-14 of the National Institute of Standards and Technology (NIST) defines three types of security policy and chooses the
- AViolations of Policy, Business continuity planning, Response planning
- BA disaster recovery, Incident response planning, and Business continuity planning
- CIssue-specific security, Systems-specific security, Enterprise information security
- DEnterprise information security, Violations of Policy, Response planning
35What are the elements of a business impact analysis?
1. Threat attack identification
2. Business unit analysis
3. Attack success scenario development
4. Potential damage assessment
5. Subordinate plan classification
6. Risk management
7. Disaster management
The elements of a business impact analysis are:- A1,2,3,4,5 correct
- B1,2,3,5,6 correct
- C2,3,5,6,7 correct
- DAll are correct
36Access control lists (ACLs) that govern the rights and privileges of users consist of the
1. User access lists,
2. Matrices,
3. Capability, and
4. Dedicated hardware
Choose the correct answer- A1,2,3,4 are true
- B1,2,3 are true
- COnly 4 is true
- DAll are true
37The instructions a system administrator codes into a server, networking device, or a device to specify how it operates is called
- AAdministration rule
- BConfiguration rules
- CNetworking rules
- DSecurity rule
38Information security safeguards focus on administrative planning, organizing, leading, and controlling and that are designed by strategic planners and implemented by the organization’s security administration. These safeguards include governance and risk management together known as
- AManagerial controls
- BOperational controls
- CTechnical controls
- DNone of these
39A lattice-based access control with rows of attributes associated with a particular subject such as a user is called
- AAccess control matrix
- BCapabilities table
- CConfiguration table
- DAll of above
40What type of policy addresses specific areas of technology, requires frequent updates, and contains a statement on the organization’s position on a specific issue?
- AEnterprise information security policy (EISP)
- BSystems-specific security policy (SysSP)
- CAutomated policy (AP)
- DIssue-specific security policy (ISSP)
41What are the defence strategies’ three common methods?
1. Application of policy
2. Education and training
3. Business impact analysis
4. Risk management
5. Application of technology
Choose the correct answer.- A1,2,3
- B1,2,4
- C2,4,5
- D1,2,5
42Policy administrator is responsible for -----------
1. creation,
2. revision,
3. implementation
4. distribution, and
5. storage
of policy in an organization. Choose the correct option- A1,2
- B3
- C3,4
- D5
43Which type of policy is frequently codified as standards and procedures to be used when configuring or maintaining systems?
- AEnterprise information security policy (EISP)
- BSystems-specific security policy (SysSP)
- CAutomated policy (AP)
- DIssue-specific security policy (ISSP)
44Which of the following is used to direct how issues should be addressed and technologies must be used in an organization?
- Apolicies
- Bstandards
- Cethics
- Dgovernance
45The boundary in the network within which an organization attempts to maintain security controls for securing information from threats from untrusted network areas is called ----
- ASecurity peripheral
- BSecurity perimeter
- CSecurity measure
- DSecurity principle
46Consider the following statements
1. Statement of Purpose -What the policy is for
2. Information Technology Security Elements – Defines information security
3. Need for Information Technology Security – Justifies the irrelevance of information security in the organization
4. Information Technology Security Responsibilities and Roles - Defines organizational overall business planning and security investment plan.
Identify the components of the EISP- A3, 4
- B2, 3, 4
- C1, 2
- Dall are true
47Access Control Lists specify
1. who can --------the system
2. what ---------users can access
3. when authorised users can --------the system
4. where authorised users can access the system from
Chose the correct words or expressions to fill in the blanks, in sequence:- Ause, authorised, access
- Bauthorised, access, create
- Cauthorised, access, use
- Dadminister, access, accountable
48The goals of (A)------------------------------ are:
1.------------------ of information security with business strategy to support organizational objectives
2 ------------------ by executing appropriate measures to manage and mitigate threats to information resources
3. ------------------ by using information security knowledge and infrastructure efficiently and effectively
Choose the correct answer:- AA-Financial security gov, 1- Tactical alignment, 2- Performance mgmt., 3- Resource mgmt.,
- BA-Information security governance,1-Strategic alignment, 2- Risk mgmt., 3- Resource mgmt.
- CA-Data security gov, 1-Operational management, 2- Resource mgmt., 3- Risk mgmt.,
- DA-Bord of governance,1-Operational alignment, 2- Risk mgmt., 3- Resource mgmt
49Match 1 & 2 with A& B following
1. Residual risk
2. Risk appetite
A: The risk to information assets that remains even after current controls have been applied.
B: The quantity and nature of risk that organizations are willing to accept as they evaluate the trade-offs between perfect security and unlimited accessibility.
Choose the correct answer:- A1-A, 2-B
- B1-B, 2-A
50True or False:
The information technology community of interest must assist in risk management by configuring and operating information systems in a secure fashion.- ARichtig
- BFalsch
51The process of examining how each threat will affect an organization is called:
- ARisk assessment
- BData classification
- CThreat assessment
- DVulnerability classification
52The probability that a specific vulnerability within an organization will be the target of an attack is known as:
- ALoss Magnitude
- BManageability
- CLikelihood
- DPracticability
53The calculation of the value associated with the most likely loss from an attack is called:
- AAnnualised Rate of Occurrence (ARO)
- BAnnualised Loss Expectancy (ALE)
- CCost Benefit Analysis (CBA)
- DSingle Loss Expectancy (SLE)
54----------------------is the formal assessment and presentation of the economic expenditures needed for particular security control, contrasted with its projected value to the organization.
- AFeasibility analysis
- BCost-benefit analysis
- CRisk-benefit analysis
- DEconomic impact analysis
55A document that compares the relative importance of prioritised assets to prioritised threats and highlights any weaknesses in the asset/threat pairs.
- AThreats-Vulnerabilities document
- BThreats-Vulnerabilities-Assets (TVA) worksheet
- CThreats-Vulnerabilities-Assets log file
- DAttack Vulnerability Asset document
56Match the following:
(A) Internal Used for the most sensitive corporate information that must be tightly controlled, even
within the company. Access to information with this classification is strictly on a
need-to-know basis or as required by the terms of a contract. Information with
this classification may also be referred to as “sensitive” or “proprietary.”
(B) Confidential Used for all internal information that does not meet the criteria
for the confidential category. Internal information is to be
viewed only by corporate employees, authorized contractors,
and other third parties.
(C) External All information that has been approved by management for public release.- AA-2, B-1, C-3
- BA-1, B-2, C-3
- CA-3, B-2, C-1
- DA-1, B-3, C-2
57------------------- varies among organisations because they maintain different balances between the expense of controlling vulnerabilities and the possible losses if the vulnerabilities are exploited. The key for each organisation is to find the proper balance in its decision-making and feasibility analyses, to use experience and facts instead of ignorance or wishful thinking.
- ARisk appetite
- BRisk control
- CResidual Risk
- DRisk Assessment
58Malware dictation Software has its own (Asset) internal personnel database behind a firewall. Industry reports indicate a 5 % chance of an attack. The information security and IT departments report that if the organization is attacked, the attack has a 15 % chance of success based on current asset vulnerabilities and protection mechanisms. The asset is valued at a score of 35 on a scale of 0 to 100, and information security and IT staff expect that 60 % of the asset would be lost or compromised by a successful attack, because not all of the asset is stored in a single location. You estimate that the assumptions and data are 90 % accurate. Calculating Risk.
- A0.1575
- B0.1733
- C0.2887
- D0.5575
59xyzbuy.com has an estimated value of Rs 50,00,000, as determined by an asset valuation and a cracker defacement scenario indicates that a deliberate act of sabotage or vandalism could damage 25 per cent of xyzbuy.com, then the single loss expectancy for the xyzbuy.com would be?
- A16,50,000
- B15,20,000
- C11,11,000
- D12,50,000
60Which VPN technology uses leased circuits from a service provider and conducts packet switching over these leased circuits?
- ASecure VPN
- BHybrid VPN
- CTrusted VPN
- DTransport VPN
61The biometric technology criteria that describe the number of legitimate users who are denied access because of a failure in the biometric device in known as
- AFalse reject rate
- BFalse accept rate
- CCrossover error rate
- DAccountability rate
62True or False: All traffic exiting from the trusted network should be filtered.
- ARichtig
- BFalsch
63What term is used to describe decoy systems designed to lure potential attackers away from critical systems?
- ATrap
- BHoneypot
- CTrace
- DSniffer
64True or False: Signature-based IDPS technology is widely used because many attacks have clear and distinct signatures.
- ARichtig
- BFalsch
65The method by which systems determine whether and how to admit a user into a trusted area of the organization is known as
- AAttribute
- BAccountability
- CAccess control
- DAudibility
66------------------denotes the rate at which fraudulent users or nonusers are allowed access to systems or areas as a result of a failure in the biometric device. This failure is also known as --------------
- AFalse reject rate, Type I error
- BFalse accept rate, Type 2 error
- CFalse accept rate, Type I error
- DFalse reject rate, Type 2 error
67Fill in the blank
------------------denotes the rate at which authorised users are denied access to systems or areas as a result of a failure in the biometric device. This failure is also known as ------------.
Choose the correct option- AFalse reject rate, Type I error
- BFalse accept rate, Type 2 error
- CFalse accept rate, Type I error
- DFalse reject rate, Type 2 error
68Match the following
A. Thresholds 1 Signature-based detection
B. Blacklists and whitelists: 2 Anomaly-based detection
C. Alert settings: 3 Detection-related related programs
D. Code viewing and editing: 4 Specifying which prevention capabilities
Choose the correct option- AA-2, B-3, C-1, D-4
- BA-2, B-1, C-3, D-4
- CA-1, B-2, C-3, D-4
- DA-2, B-1, C-4, D-3
69Choose the right option to fill in the blanks
(1) --------------- initiates network traffic to find and evaluate service ports whereas (2) ---------------- uses traffic from the target network segment to evaluate the service ports available from hosts on that segment.- A1-active vulnerability scanners, 2-passive vulnerability scanners
- B1-passive vulnerability scanners, 2-active vulnerability scanners
70Which of the following terms describes the process of making and using codes to secure the transmission of information?
- AAlgorithm
- BCryptography
- CSteganography
- DCryptanalysis
71What is term is used to describe a cryptographic method that incorporates mathematical operations involving both a public key and a private key to encipher or decipher a message?
- APrivate-key encryption
- BSymmetric encryption
- CAdvanced Encryption Standard (AES)
- DAsymmetric encryption
72A substitution cipher that incorporates two or more alphabets in the encryption process is called-------------------
- AMonoalphabetic substitution
- BBlock cipher substitution
- CStream cipher substitution
- DPolyalphabetic substitution
73The current standard for the encryption of data, as specified by NIST --------- is based on the Rijndael algorithm, which was developed by Vincent Rijmen and Joan Daemen.
- ADES
- BRSA
- CAES
- DMessage Digest
74True or False:
Nonrepudiation means that customers or partners can be held accountable for transactions, such as online purchases, which they cannot later deny.- ARichtig
- BFalsch
75Limited-use symmetric keys for temporary communications during an online session is called
- ASession keys
- BOne-time padding
- CAES
- DDES
76Match the folowing
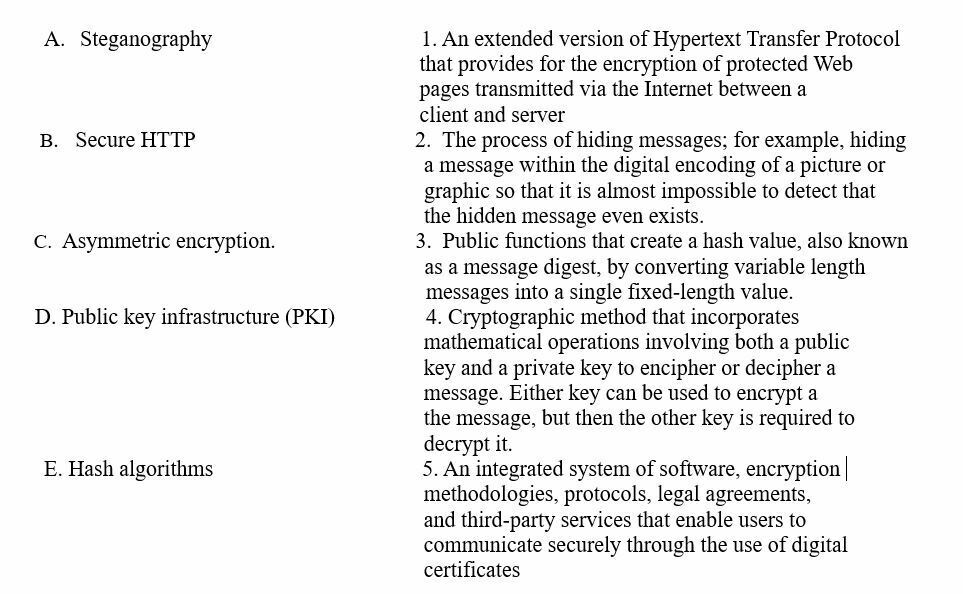
- AA-3, B-5, C-4, D-1, E-2
- BA-2, B-1, C-4, D-5, E-3
- CA-4, B-2, C-3, D-1, E-1
- DA-5, B-2, C-3, D-1, E-4
77Suppose that everyone in a group of N people wants to communicate secretly with the N-1 others using a symmetric key cryptographic system. Communication between any two persons should not be decodable by others in the group. The number of keys required in the system as a whole to satisfy the confidentiality requirement is
- A2N
- BN(N-1)
- CN(N-1)/2
- D(N-1)2
78Decrypt the following message if it was encrypted using a shift cipher with a shift of 3.
Message: NPTELINFORMATION- AQ S W H O L Q I R U P W L R Q
- BQ S W H O L Q I T U P W L R Q
- CQ S W F O L Q I R V P W L R Q
- DQ S W H O L Q I R V P W L R Q
79------------security protocols are used to protect e-mail
- ASMTP
- BHTTPS
- CS/MIME, PEM, and PGP
- DTelnet
80What is the most popular encryption system used over the Web?
- ADiffie Hellman key exchange
- BRSA
- CBlock cipher
- DDES
81What is the maximum fine for GDPR non-compliance?
- AEUR 10mn or 2% global turnover
- BEUR 15mn or 3% global turnover
- CEUR 20mn or 4% global turnover
- DEUR 25mn or 5% global turnover
82Richards and Solove (2007) suggest that while the American derivation of general privacy is grounded in one's --------------------
- Ainviolate personality
- Bviolate personality
- Cserious personality
- Dfunny personality
83Cohenretism treats privacy as a
- APermission
- BOrder
- CFreedom
- DDistinct right
84True/ or False?
Confidentiality is concerned with the externalization of restricted but accurate information to a specific entity.- ARichtig
- BFalsch
85Being observed, while the subject doesn’t know is
- APanopticon
- BTransparency
- CPrevention
- DAnonymity
86Concerns for Information Privacy (CFIP) has four constructs. Which is a construct that is not part of the CFIP?
- ACollection
- BUnauthorized access
- CAutonomy
- DErrors
87According to --------------------- privacy is not a distinct value concept because it could be conceptually reduced to other values, like liberty
- ACoherentism
- BReductionism
- CPrivacy
- DSecurity
88……………… determines the purposes and means of processing personal data
- AData fiduciary
- BData processor
- CData principle
- DData users
89A IPL team management contracts a market research specialist team to carry out players satisfaction survey. The IPL team specifies the budget and the deadline, but the market research team determines sample sizes and interview methods. The market research team decides which player to select for the interview, what information will be collected, how the information will be collected, and how the information will be presented to the IPL team management. Who is the data controller in this situation?
- AAn IPL team management
- BMarket research firm
- CBoth a & b are controllers
- DNone of them are controllers
90Fair Information Practice (FIP) principles were developed the United States in response to increasing privacy concerns resulting from massive computerization. What is an issue FIP does not address?
- Asecret record-keeping systems
- Baccess by data subject to information stored in record keeping systems
- Cability by data subject to correct errors in one’s own data
- Ddata localization
91GDPR makes provisions for the individual member states to add their own exemptions
- ARichtig
- BFalsch
92The GDPR introduces a new data protection principle that requires organizations to
- Ademonstrate compliance with the principles
- Boptional compliance with the privacy regulation
- Cflexibility to report data protection breaches
- Daccept data breaches
93In which of these circumstances could a data subject exercise their right to be forgotten?
- AWhere they have withdrawn consent for data processing
- BWhere the data is no longer necessary for the purposes for which it was collected
- CWhere erasure is necessary to comply with a legal obligation
- DAll are true
- EAll are false
94According to GDPR a group of companies or public authorities may appoint a single data protection officer to represent them all
- ARichtig
- BFalsch
95--------------------- is a system for publicly sharing information about a dataset by describing the patterns of groups within the dataset while withholding information about individuals in the dataset.
- ADifferential privacy (DP)
- BPrivacy calculus
- CPrivacy paradox
- DPrivacy theory
96A release of data is said to have the k-anonymity property if the information for each person contained in the release cannot be distinguished from at ---------individuals whose information also appears in the release
- Aleast k−1
- Bleast k+1
- Cleast k +/- 1
- Dleast k*1
97consider the diagram:
In the First wave of the economic theory of privacy, work did not consist of formal economic models, but rather general ------------around the value or the damage that individuals, and society, may incur when personal information is protected, thereby making potentially useful information unavailable to the marketplace
Choose the correct answer: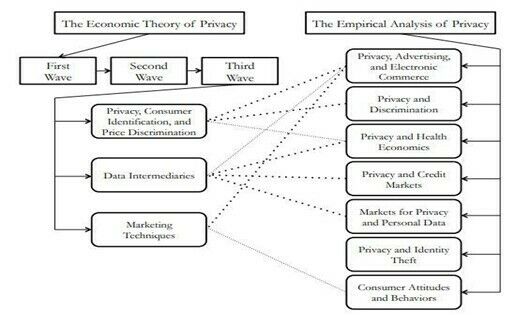
- Ainformation privacy
- Beconomic arguments
- Ceconomic value
- Deconomic benefit
98The economics of privacy concerns the tradeoffs associated with the balancing of --------------------spheres between individuals, organizations, and governments.
- Apublic and private
- Binternal and external
- Clow and high
- Dindividual vs group
99The goal of privacy-preserving data mining is to develop data mining methods without increasing the risk of misuse of the ---------
- Aprivacy
- Bdata
- Canonymity
- DPrivacy-related content
- Edatabase
100___________ is a dichotomy between a person’s intention to protect their online privacy versus how they actually behave online and as a result compromise their privacy
- APrivacy paradox
- BPrivacy calculus
- CDifferential calculus
- DCoherentism
101The personal data that has been de-identified, ----------------but can be used to re-identify a person remains personal data and falls within the scope of the GDPR.
- Apseudonymized
- Bdecrypted
- CAnonymize
- DSecrete
102The area of philosophy that examines the basis for moral judgment, as well as its nature, standards, sources, and logic, is called ------------------
- AMoral principle
- BMoral value
- CEthics
- DLaw
103Choose the correct option that represents HIPAA’s fundamental principle
- AProducer control of medical information
- BNo restrictions on how medical data may be used
- CAccountability to maintain the privacy of specified types of information
- DBalance of public responsibility for the use of medical information for the greater good measured against no impact on the individual
- ESecurity of health information
104True or False:
The cornerstone of many current computer-related criminal laws in the US is the Computer Fraud and Abuse Act of 1986.- ARichtig
- BFalsch
105Which one of these activities falls outside the scope of the GDPR?
- Aprocessing for marketing purposes
- Bprocessing for domestic and household purposes
- Cprocessing for the purposes of crime and investigations
- Dprocessing for the purposes of journalism literature and art
106What types of information are covered by the GDPR?
1. Personal data
2. Data related to the public domain
3. All data of a person that can be identified by their identifier, directly or indirectly
4. Garbage data
Choose the correct option.- A1,2
- B2,4
- C1,3
- D4,3
107Which of the following are not GDPR fundamental rights?
- AThe right to be informed, the right of access
- BThe ability to learn from mistakes, the freedom to transfer data
- CThe right to object, rights related to automated decision-making
- DAll are correct
108Match topics of interest to IT Professionals with US Laws
(A) Cryptography (1) Electronic Communications Privacy Act
(B) IP (2) Federal Privacy Act
(C) Encryption and digital signatures (3) No Electronic Theft Act amends
(D) Privacy (4) Security and Freedom through Encryption Act
Choose the correct option- AA-3, B-1, C-4, D-2.
- BA-4, B-3, C-1, D-2.
- CA-1, B-3, C-4, D-2.
109INDIAN COPYRIGHT ACT was drafted in --------------------by Shalu Gothi and Daisy Jain
- A2000
- B1857
- C1957
- D1967
110What is the software that comes hidden in free downloadable software and tracks your online movements, mine the information stored on your computer or use your computer’s CPU and storage for some task you know nothing about?
- AWeblog
- BClickstream
- CAnonymous web browsing service
- DNone of above
111What are the primary examples of public law?
- ACriminal, administrative, and constitutional law
- BCivil, Legislative and public service
- CIPC, administrative, service, constitutional law
- DAll are the primary examples of public law.
112The Aadhaar project is the world’s largest national identity project, launched by the government of India, which seeks to collect the following data about residents and store these in a centralized database.
- ABiometric data
- BDemographic data of residents
- CLife style data of citizens
- DAll of these
113Personal Data Protection Bill 2019 had the following provision.
(1) Provide for the protection of the privacy of individuals relating to their personal data,
(2) Specify demerits of the flow and usage of personal data,
(3) Create a mysterious relationship of trust between persons and entities processing personal data,
(4) Protect the fundamental rights of individuals whose personal data are processed
Choose which of the options listed above are false?- A1,2,3
- B2,3
- C1,4
- D1,2
114The Aadhaar Act attempts to create a method for--------------- of individuals so as to provide services, subsidies and other benefits to the residents of the country.
- AIdentification
- BAuthentication
- CAuthorization
- DAccountability
115------------------- gathers personally identifying information from Aadhaar holders, prepares the data for transmission, and receives the authentication.
- ASystem Terminal
- BBarcode reader
- CAuthentication device
- DRFID
116According to standard notions of digital authentication, a security principal (a user or a computer), while requesting access to a service, must provide two independent pieces of information, which are:
- AIdentity and Authentication.
- BVerification and Authentication
- CValidation and Authorization
- DValidation and Authentication
117Identity provides an answer to the question ------------------ Anonymity is when nobody knows who you are but potentially, they know ---------------------------
- Ahow are you? & how you do
- Bwho are you? & what you do
- Chow are you feeling? & what you do
- Dwho are you? & what you know about others
118Which of the following is odd about Aadhaar authentication?
- AIt enables authentication using a One-Time-Password (OTP) issued to the resident's listed email address or cellphone number in the CIDR.
- BIt enables authentication combining OTP, fingerprint, and iris authentication for residents.
- CIt offers a 2-factor authentication with OTP as one factor and multimodal biometric as the second factor for authenticating residents.
- DIt enables Aadhaar authentication by matching Aadhaar numbers and demographic attributes of residents.
119Personal Data Protection Bill sought to ensure privacy rights of the individual. Select the odd option
- AObtain confirmation from the fiduciary on whether their personal data has been processed
- BSeek correction of inaccurate, incomplete, or out-of-date personal data
- CHave personal data transferred to any other data fiduciary in certain circumstances
- DRestrict continuing disclosure of their personal data by a fiduciary, if it is no longer necessary Or consent is withdrawn
- EProvide advice on security safeguards like data encryption
120Which of the following act enforces individual privacy in online space, after scrapping a similar bill:
- APDP Bill 2018
- BDigital Personal Data Protection Bill 2023
- CGDPR
- DIT Act, 2000
Informationen
- Beschreibung
- Quiz am Cyber Security Test-1, erstellt von Bishal Jena am 05/10/2023.
- Autor
- Bishal Jena
- Sprache
- English
- Aufrufe
- 154
- Bewertung
- 4,5 von 5 · 2 Bewertungen Bewerte dieses Quiz