
Test
642-813
Crea una cuenta gratis para terminar este test
Guarda tu progreso y consulta tu resultado final.
¿Ya tienes cuenta? Inicia sesión
Preguntas del test (132)
1Which statement is true about RSTP topology changes?
- AAny change in the state of the port generates a TC BPDU
- BOnly non-edge ports moving to the forwarding state generate a TC BPDU.
- CIf either an edge port or a non-edge port moves to a block state, then a TC BPDU is generated.
- DOnly edge ports moving to the blocking state generate a TC BPDU.
- EAny loss of connectivity generates a TC BPDU.
2Refer to the exhibit.
Why are users from VLAN 100 unable to ping users on VLAN 200?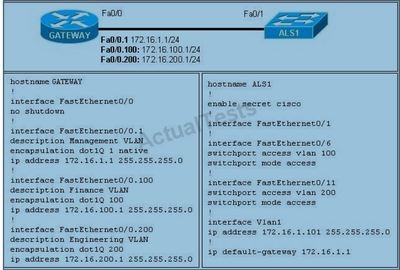
- AEncapsulation on the switch is wrong.
- BTrunking must be enabled on Fa0/1.
- CThe native VLAN is wrong.
- DVLAN 1 needs the no shutdown command.
- EIP routing must be enabled on the switch.
3Refer to the exhibit.
The link between switch SW1 and switch SW2 is configured as a trunk, but the trunk failed to establish connectivity between the switches.
Based on the configurations and the error messages received on the console of SW1, what is the cause of the problem?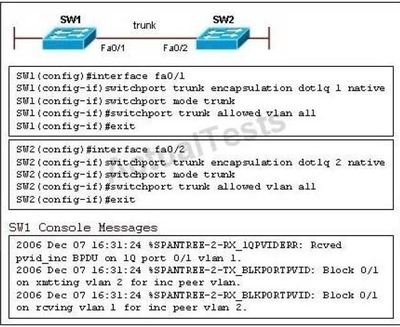
- AThe two ends of the trunk have different duplex settings.
- BThe two ends of the trunk have different EtherChannel configurations.
- CThe two ends of the trunk have different native VLAN configurations.
- DThe two ends of the trunk allow different VLANs on the trunk.
4When you create a network implementation for a VLAN solution, what is one procedure that you should include
in your plan?- APerform an incremental implementation of components.
- BImplement the entire solution and then test end-to-end to make sure that it is performing as designed.
- CImplement trunking of all VLANs to ensure that traffic is crossing the network as needed before performing
any pruning of VLANs. - DTest the solution on the production network in off hours.
5You have just created a new VLAN on your network.
What is one step that you should include in your VLAN-based implementation and verification plan?- AVerify that different native VLANs exist between two switches for security purposes.
- BVerify that the VLAN was added on all switches with the use of the show vlan command.
- CVerify that the switch is configured to allow for trunking on the switch ports.
- DVerify that each switch port has the correct IP address space assigned to it for the new VLAN.
6Which two statements describe a routed switch port on a multilayer switch? (Choose two.)
- ALayer 2 switching and Layer 3 routing are mutually supported.
- BThe port is not associated with any VLAN.
- CThe routed switch port supports VLAN subinterfaces.
- DThe routed switch port is used when a switch has only one port per VLAN or subnet.
- EThe routed switch port ensures that STP remains in the forwarding state.
7On a multilayer Cisco Catalyst switch, which interface command is used to convert a Layer 3 interface to a Layer 2 interface?
- Aswitchport
- Bno switchport
- Cswitchport mode access
- Dswitchport access vlan vlan-id
8Refer to the exhibit.
All network links are FastEthernet. Although there is complete connectivity throughout the network, Front Line users report that they experience slower network performance when accessing the server farm than the Reception office experiences.
Which two statements are true? (Choose two.)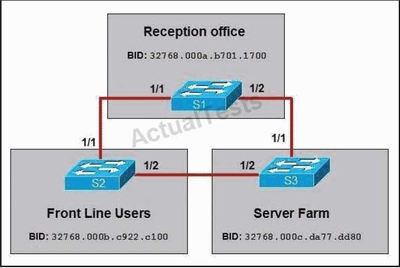
- AChanging the bridge priority of S1 to 4096 would improve network performance.
- BChanging the bridge priority of S1 to 36864 would improve network performance.
- CChanging the bridge priority of S2 to 36864 would improve network performance.
- DChanging the bridge priority of S3 to 4096 would improve network performance.
- EDisabling the Spanning Tree Protocol would improve network performance.
- FUpgrading the link between S2 and S3 to Gigabit Ethernet would improve performance.
9Refer to the exhibit.
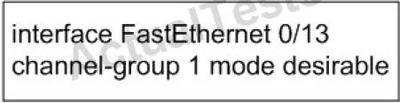
- Aenables LACP unconditionally
- Benables PAgP only if a PAgP device is detected
- Cenables PAgP unconditionally
- Denables EtherChannel only
- Eenables LACP only if an LACP device is detected
10Refer to the exhibit.
Which two statements are true? (Choose two.)- AInterface gigabitethernet 0/1 has been configured as Layer 3 ports.
- BInterface gigabitethernet 0/1 does not appear in the show vlan output because switchport is enabled.
- CVLAN2 has been configured as the native VLAN for the 802.1q trunk on interface gigabitethernet 0/1.
- DTraffic on VLAN 1 that is sent out gigabitethernet 0/1 will have an 802.1q header applied.
- ETraffic on VLAN 2 that is sent out gigabitethernet 0/1 will have an 802.1q header applied.
- FInterface gigabitethernet 0/1 does not appear in the show vlan output because it is configured as a trunk
interface.
11Refer to the exhibit and the partial configuration of switch SW_A and SW_B.
STP is configured on all switches in the network. SW_B receives this error message on the console port:
00:06:34: %CDP-4-DUPLEX_MISMATCH: duplex mismatch discovered on FastEthernet0/5
(not half duplex), with SW_A FastEthernet0/4 (half duplex), with TBA05071417
(Cat6K-B) 0/4 (half duplex).
What is the possible outcome of the problem?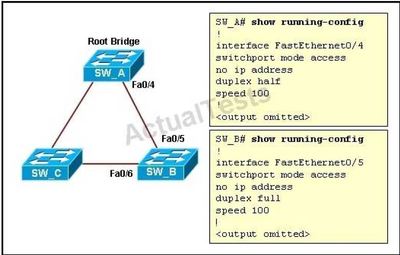
- AThe root port on switch SW_A will automatically transition to full-duplex mode.
- BThe root port on switch SW_B will fall back to full-duplex mode.
- CThe interfaces between switches SW_A and SW_B will transition to a blocking state.
- DInterface Fa 0/6 on switch SW_B will transition to a forwarding state and create a bridging loop.
12What is the result of entering the command port-channel load-balance src-dst-ip on an EtherChannel link?
- APackets are distributed across the ports in the channel based on the source and destination MAC addresses.
- BPackets are distributed across the ports in the channel based on both the source and destination IP
addresses. - CPackets are balanced across the ports in the channel based first on the source MAC address, then on the
destination MAC address, then on the IP address. - DPackets are distributed across the access ports in the channel based first on the source IP address and
then on the destination IP addresses.
13Which statement about the Port Aggregation Protocol is true?
- AConfiguration changes made on the port-channel interface apply to all physical ports assigned to the portchannel
interface. - BConfiguration changes made on a physical port that is a member of a port-channel interface apply to the
port-channel interface - CConfiguration changes are not permitted with Port Aggregation Protocol.
Instead, the standardized Link Aggregation Control Protocol should be used if configuration changes are
required. - DThe physical port must first be disassociated from the port-channel interface before any configuration
changes can be made.
- AConfiguration changes made on the port-channel interface apply to all physical ports assigned to the portchannel
14Refer to the exhibit.
For the configuration shown, which is the recommended method of providing interVLAN routing?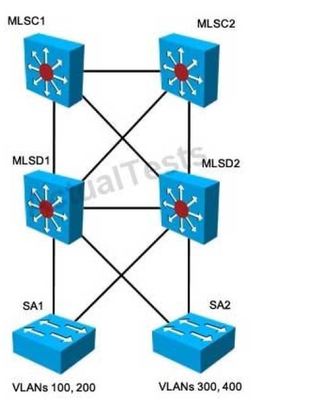
- Adetermine which switch is the root bridge then connect a router on a stick to it
- Bconfigure SVIs on the core switches
- Cconfigure SVIs on the access layer switches
- Dconfigure SVIs on the distribution switches
15Under what circumstances should an administrator prefer local VLANs over end-to-end VLANs?
- AEighty percent of traffic on the network is destined for Internet sites.
- BThere are common sets of traffic filtering requirements for workgroups located in multiple buildings.
- CEighty percent of a workgroup's traffic is to the workgroup's own local server.
- DUsers are grouped into VLANs independent of physical location.
- ENone of the other alternatives apply
- AEighty percent of traffic on the network is destined for Internet sites.
16What are some virtues of implementing end-to-end VLANs? (Choose two)
- AEnd-to-end VLANs are easy to manage.
- BUsers are grouped into VLANs independent of a physical location.
- CEach VLAN has a common set of security and resource requirements for all members.
- DResources are restricted to a single location.
17Which of the following statements is true about the 80/20 rule (Select all that apply)?
- A20 percent of the traffic on a network segment should be local
- Bno more than 20 percent of the network traffic should be able to move across a backbone.
- Cno more than 80 percent of the network traffic should be able to move across a backbone.
- D80 percent of the traffic on a network segment should be local
18What are three results of issuing the switchport host command? (Choose three.) Select 3 response(s).
- A enables PortFast
- Bdisables trunking
- Cdisables Cisco Discovery Protocol
- Denables port security
- Eenables loopguard
- Fdisables EtherChannel
- A enables PortFast
19Given the configurations on SwitchA and SwitchB, which statement is true?
- AThe link is set to auto-negotiate trunking, and it will automatically become a trunk link unless configured
otherwise. - BThe link is a trunking link and by default all VLANs will be transmitted across this trunk.
- CThe link is prevented from generating DTP frames, turning the Negotiation of Trunking off.
- DThe link is not a trunk link so both interfaces must be on the same VLAN and only that single VLAN is
transmitted across the link.
- AThe link is set to auto-negotiate trunking, and it will automatically become a trunk link unless configured
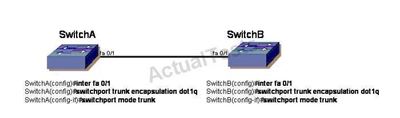
20Given the configurations on SwitchA and SwitchB, which two statements are true? (Choose two.)
- AThe trunk is currently using the ISL trunking protocol.
- BThe trunk is currently using the 802.1q trunking protocol.
- CBy default, the trunk can only support one VLAN, and only that single VLAN is transmitted across the trunk.
- DBy default, SwitchA and SwitchB's Fast Ethernet 0/1 port will not generate DTP messages.
- E
By default, all VLANs will be transmitted across this trunk.
21A network administrator enters the following switch commands:
Switch(config)#interface range fa0/0-5
Switch(config-if-range)#switchport access vlan 2
What is the result of these commands?- ATwo new vlans are created on six switch ports
- BOne new vlan is created on five switch ports
- CSix new vlans are created on six switch ports
- DOne new vlan is created with the vlan number 2
22When a VLAN port configured as a trunk receives an untagged frame, what will happen?
- AThe frame will be dropped.
- BThe frame will cause an error message to be sent.
- C The frame will be processed as a native VLAN frame
- DThe frame will first be tagged, then processed as a native VLAN frame.
23By default, which statement is correct when an IEEE 802.1Q trunk port receives an untagged frame?
- AThe frame is considered in the native VLAN and forwarded to the ports associated with that VLAN.
- BThe frame is encapsulated and tagged as in the native VLAN.
- CThe frame is broadcast on all ports regardless of VLAN association.
- DThe frame is dropped.
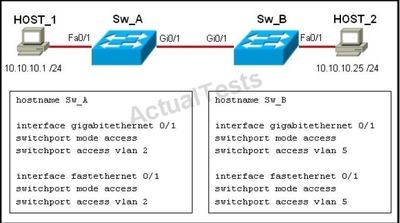
24Both host stations are part of the same subnet but are in different VLANs.
On the basis of the information presented in the exhibit, which statement is true about an attempt to ping from
host to host?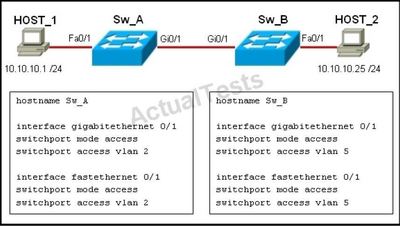
- AA trunk port will need to be configured on the link between Sw_A and Sw_B for the ping command to be
successful. - BThe two different hosts will need to be in the same VLAN in order for the ping command to be successful.
- CA Layer 3 device is needed for the ping command to be successful.
- DThe ping command will be successful without any further configuration changes.
- AA trunk port will need to be configured on the link between Sw_A and Sw_B for the ping command to be
25Refer to the exhibit. VLAN 1 and VLAN 2 are configured on the trunked links between Switch A and Switch B.
Port Fa 0/2 on Switch B is currently in a blocking state for both VLANs.
What should be done to load balance VLAN traffic between Switch A and Switch B?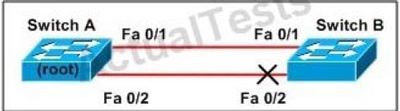
- ALower the port priority for VLAN 1 on port 0/1 for Switch A.
- BLower the port priority for VLAN 1 on port 0/2 for Switch A.
- CMake the bridge ID of Switch B lower than the ID of Switch A.
- DEnable HSRP on the access ports
26Refer to the exhibit.
What information can be derived from the output?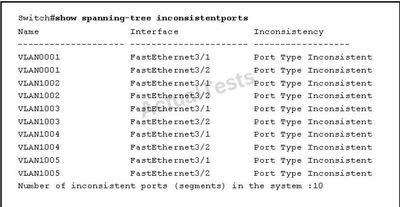
- AInterfaces FastEthernet3/1 and FastEthernet3/2 are connected to devices that are sending BPDUs with a
superior root bridge parameter and no traffic is forwarded across the ports.
After the sending of BPDUs has stopped, the interfaces must be shut down administratively, and brought
back up, to resume normal operation. - BDevices connected to interfaces FastEthernet3/1 and FastEthernet3/2 are sending BPDUs with a superior
root bridge parameter, but traffic is still forwarded across the ports. - CDevices connected to interfaces FastEthernet3/1 and FastEthernet3/2 are sending BPDUs with a superior
root bridge parameter and no traffic is forwarded across the ports.
After the inaccurate BPDUs have been stopped, the interfaces automatically recover and resume normal
operation. - DInterfaces FastEthernet3/1 and FastEthernet3/2 are candidates for becoming the STP root port, but neither
can realize that role until BPDUs with a superior root bridge parameter are no longer received on at least
one of the interfaces.
- AInterfaces FastEthernet3/1 and FastEthernet3/2 are connected to devices that are sending BPDUs with a
27What are three results of issuing the switchport host command? (Choose three.)
- Adisables EtherChannel
- Benables port security
- Cdisables Cisco Discovery Protocol
- Denables PortFast
- Edisables trunking
- Fenables loopguard
28Refer to exhibit
All links in this network are layer 2, fast Ethernet 100 Mb/s and operating as trunks.
After a failure, the link between ASW-1 and DSW-1 has incorrectly come back up at 10Mb/s although it is
connected.
Which one of the following will occur as a result of this failure?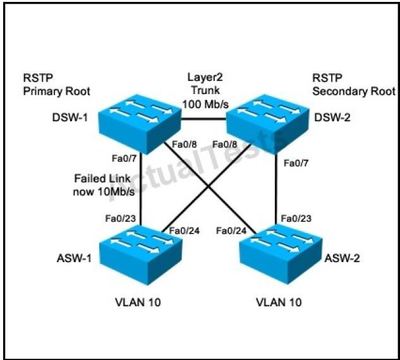
- AThere will be no change to the forwarding path of traffic from ASW-1
- BASW1 will block Fa0/24 in order to maintain the shortest path to the root bridge DSW-1
- CASW-1 will block Fa0/23 in order to maintain the shortest path to the root bridge DSW-1
- DASW-1 will elect DSW-2 as the root primary since it is closer than DSW-1
29What is the result of entering the command spanning-tree loopguard default?
- AThe command enables loop guard and root guard.
- BThe command changes the status of loop guard from the default of disabled to enabled.
- CThe command activates loop guard on point-to-multipoint links in the switched network.
- DThe command disables EtherChannel guard.
30What is the effect of applying the switchport trunk encapsulation dot1q command to a port on a Cisco Catalyst
switch?- ABy default, native VLAN packets going out this port are tagged.
- BWithout an encapsulation command, 802.1Q is the default encapsulation if DTP fails to negotiate a trunking
protocol. - CThe interface supports the reception of tagged and untagged traffic.
- DIf the device connected to this port is not 802.1Q-enabled, it is unable to handle 802.1Q packets.
31Refer to the exhibit.
Switch S1 has been configured with the command spanning-tree mode rapid-pvst. Switch S3 has been
configured with the command spanning-tree mode mst. Switch S2 is running the IEEE 802.1D instance of
Spanning Tree. What is the result?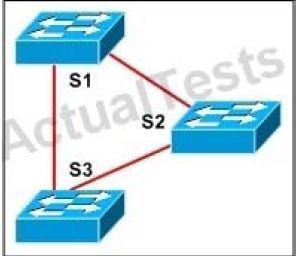
- AIEEE 802.1w and IEEE 802.1s are compatible. IEEE 802.1d is incompatible.
Switches S1 and S3 can pass traffic between themselves. Neither can pass traffic to switch S2. - BSwitches S1, S2, and S3 can pass traffic between themselves.
- CSwitches S1, S2, and S3 can pass traffic between themselves.
However, if the topology is changed, switch S2 does not receive notification of the change. - DIEEE 802.1d, IEEE 802.1w, and IEEE 802.1s are incompatible.
All three switches must use the same standard or no traffic can pass between any of the switches.
- AIEEE 802.1w and IEEE 802.1s are compatible. IEEE 802.1d is incompatible.
32Which statement about 802.1Q trunking is true?
- ABoth switches must be in the same VTP domain.
- BThe encapsulation type on both ends of the trunk does not have to match.
- CThe native VLAN on both ends of the trunk must be VLAN 1.
- D In 802.1Q trunking, all VLAN packets are tagged on the trunk link, except the native VLAN.
- ABoth switches must be in the same VTP domain.
33Refer to the exhibit.
Which three statements are true? (Choose three.)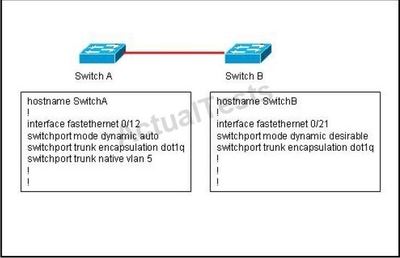
- AA trunk link will be formed.
- BOnly VLANs 1-1001 will travel across the trunk link.
- CThe native VLAN for switch B is VLAN 1.
- DDTP is not running on switch A.
- EDTP packets are sent from switch B.
34The Company LAN is becoming saturated with broadcasts and multicast traffic.
What could you do to help a network with many multicasts and broadcasts?- ACreating smaller broadcast domains by implementing VLANs.
- BSeparate nodes into different hubs.
- CCreating larger broadcast domains by implementing VLANs.
- DSeparate nodes into different switches.
- EAll of the above.
35You are the network administrator tasked with designing a switching solution for the Company network.
Which of the following statements describing trunk links are INCORRECT? (Select all that apply)- AThe trunk link belongs to a specific VLAN.
- BMultiple trunk links are used to connect multiple end user devices.
- CA trunk link only supports native VLAN.
- D Trunk links use 802.10 to identify a VLAN.
- EThe native VLAN of the trunk link is the VLAN that the trunk uses for untagged packets.
- AThe trunk link belongs to a specific VLAN.
36Which of the following specifications is a companion to the IEEE 802.1w Rapid Spanning Tree Protocol
(RSTP) algorithm, and warrants the use multiple spanning-trees?- AIEEE 802.1s (MST)
- BIEEE 802.1Q (CST)
- CCisco PVST+
- DIEEE 802.1d (STP)
- ENone of the other alternatives apply
- AIEEE 802.1s (MST)
37Which of the following specification will allow you to: associate VLAN groups to STP instances so you can
provide multiple forwarding paths for data traffic and enable load balancing?- AIEEE 802.1d (STP)
- BIEEE 802.1s (MST)
- CIEEE 802.1Q (CST)
- DIEEE 802.1w (RSTP)
38Which two statements correctly describe VTP? (Choose two.)
- ATransparent mode always has a configuration revision number of 0.
- B Transparent mode cannot modify a VLAN database.
- CClient mode cannot forward received VTP advertisements.
- DClient mode synchronizes its VLAN database from VTP advertisements.
- EServer mode can synchronize across VTP domains.
39Which two DTP modes permit trunking between directly connected switches? (Choose two.)
- Adynamic desirable (VTP domain A) to dynamic desirable (VTP domain A)
- Bdynamic desirable (VTP domain A) to dynamic desirable (VTP domain B)
- Cdynamic auto (VTP domain A) to dynamic auto (VTP domain A)
- Ddynamic auto (VTP domain A) to dynamic auto (VTP domain B)
- Edynamic auto (VTP domain A) to nonegotiate (VTP domain A)
- Fnonegotiate (VTP domain A) to nonegotiate (VTP domain B)
40Which two RSTP port roles include the port as part of the active topology? (Choose two.)
- A root
- Bdesignated
- Calternate
- Dbackup
- Eforwarding
- Flearning
- A root
41Which two statements correctly describe characteristics of the PortFast feature? (Choose two.)
- ASTP is disabled on the port.
- B PortFast can also be configured on trunk ports.
- C PortFast is needed to enable port-based BPDU guard.
- DPortFast is used for STP and RSTP host ports.
. - E PortFast is used for STP-only host ports
42Which statement correctly describes the Cisco implementation of RSTP?
- APortFast, UplinkFast, and BackboneFast specific configurations are ignored in Rapid PVST mode.
- BRSTP is enabled globally and uses existing STP configuration.
- CRoot and alternative ports transition immediately to the forwarding state
- DConvergence is improved by using subsecond timers for the blocking, listening, learning, and forwarding
port states.
43You are the administrator of a switch and currently all host-connected ports are configured with the portfast
command. You have received a new directive from your manager that states that, in the future, any hostconnected
port that receives a BPDU should automatically disable PortFast and begin transmitting BPDUs.- ASwitch(config)#spanning-tree portfast bpduguard default
- BSwitch(config-if)#spanning-tree bpduguard enable
- CSwitch(config-if)#spanning-tree bpdufilter enable
- DSwitch(config)#spanning-tree portfast bpdufilter default
44A port in a redundant topology is currently in the blocking state and is not receiving BPDUs.
To ensure that this port does not erroneously transition to the forwarding state, which command should be
configured?- ASwitch(config)#spanning-tree loopguard default
- BSwitch(config-if)#spanning-tree bdpufilter
- CSwitch(config)#udld aggressive
- DSwitch(config-if)#spanning-tree bpduguard
45Which command can be issued without interfering with the operation of loop guard?
- ASwitch(config-if)#spanning-tree guard root
- BSwitch(config-if)#spanning-tree portfast
- C Switch(config-if)#switchport mode trunk
- DSwitch(config-if)#switchport mode access
46Which statement is a characteristic of multi-VLAN access ports?
- AThe port has to support STP PortFast.
- BThe auxiliary VLAN is for data service and is identified by the PVID.
- CThe port hardware is set as an 802.1Q trunk.
- DThe voice service and data service use the same trust boundary.
47Which two statements are true about recommended practices that are to be used in a local VLAN solution
design where layer 2 traffic is to be kept to a minimum? (Choose two.)- ARouting should occur at the access layer if voice VLANs are utilized. Otherwise, routing should occur at the
distribution layer. - BRouting may be performed at all layers but is most commonly done at the core and distribution layers.
- C. Routing should not be performed between VLANs located on separate switches.
- DVLANs should be local to a switch.
- EVLANs should be localized to a single switch unless voice VLANs are being utilized.
- ARouting should occur at the access layer if voice VLANs are utilized. Otherwise, routing should occur at the
48Refer to the exhibit.
BPDUGuard is enabled on both ports of SwitchA. Initially, LinkA is connected and forwarding traffic. A new
LinkB is then attached between SwitchA and HubA.
Which two statements about the possible result of attaching the second link are true? (Choose two.)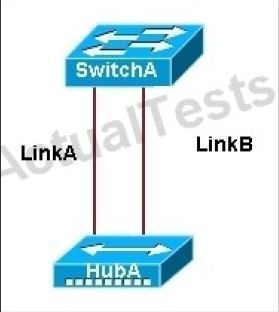
- AThe switch port attached to LinkB does not transition to up.
- BOne or both of the two switch ports attached to the hub goes into the err-disabled state when a BPDU is
received. - CBoth switch ports attached to the hub transitions to the blocking state.
- DA heavy traffic load could cause BPDU transmissions to be blocked and leave a switching loop.
- EThe switch port attached to LinkA immediately transitions to the blocking state.
49What action should a network administrator take to enable VTP pruning on an entire management domain?
- AEnable VTP pruning on any client switch in the domain.
- BEnable VTP pruning on every switch in the domain
- CEnable VTP pruning on any switch in the management domain.
- DEnable VTP pruning on a VTP server in the management domain.
50How does VTP pruning enhance network bandwidth?
- Aby restricting unicast traffic across VTP domains
- Bby reducing unnecessary flooding of traffic to inactive VLANs
- Cby limiting the spreading of VLAN information
- Dby disabling periodic VTP updates
51Refer to the exhibit.
The network operations center has received a call stating that users in VLAN 107 are unable to access
resources through router 1. What is the cause of this problem?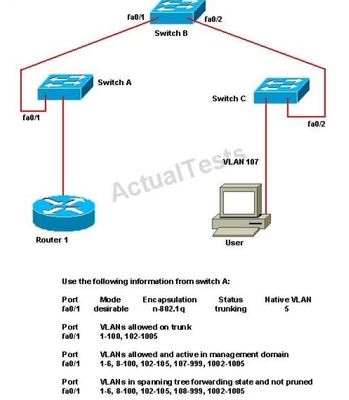
- AVLAN 107 does not exist on switch A.
- BVTP is pruning VLAN 107.
- CVLAN 107 is not configured on the trunk.
- DSpanning tree is not enabled on VLAN 107.
52What two things occur when an RSTP edge port receives a BPDU? (Choose two.)
- AThe port immediately transitions to the forwarding state.
- BThe switch generates a Topology Change Notification BPDU.
- CThe port immediately transitions to the err-disable state.
- DThe port becomes a normal STP switch port.
53What is the effect of configuring the following command on a switch?
Switch(config) # spanning-tree portfast bpdufilter default- AIf BPDUs are received by a port configured for PortFast, then PortFast is disabled and the BPDUs are
processed normally. - BIf BPDUs are received by a port configured for PortFast, they are ignored and none are sent.
- CIf BPDUs are received by a port configured for PortFast, the port transitions to the forwarding state.
- DThe command enables BPDU filtering on all ports regardless of whether they are configured for BPDU
filtering at the interface level.
- AIf BPDUs are received by a port configured for PortFast, then PortFast is disabled and the BPDUs are
54Which statement correctly describes enabling BPDU guard on an access port that is also enabled for
PortFast?- AUpon startup, the port transmits 10 BPDUs. If the port receives a BPDU, PortFast and BPDU guard are
disabled on that port and it assumes normal STP operation. - BThe access port ignores any received BPDU.
- CIf the port receives a BPDU, it is placed into the error-disable state.
- DBPDU guard is configured only globally and the BPDU filter is required for port-level configuration.
- AUpon startup, the port transmits 10 BPDUs. If the port receives a BPDU, PortFast and BPDU guard are
55Which three items are configured in MST configuration submode? (Select three)
- ARegion name
- BIST STP BPDU hello timer
- CCST instance map
- DPVST+ instance map
- EConfiguration revision number
- F VLAN instance map
- ARegion name
56By default, all VLANs will belong to which MST instance when using Multiple STP?
- AMST00
- BMST01
- CThe last MST instance configured
- DNone
- AMST00
57Which MST configuration statement is correct?
- AMST configurations can be propagated to other switches using VTP.
- BAfter MST is configured on a Switch, PVST+ operations will also be enabled by default.
- C MST configurations must be manually configured on each switch within the MST region.
- DMST configurations only need to be manually configured on the Root Bridge.
- EMST configurations are entered using the VLAN Database mode on Cisco Catalyst switches.
58Which trunking protocol inserts a four byte tag into the Ethernet frame and recalculates the CRC value?
- AVTP
- B802.1Q
- CDTP
- DISL
59Which description correctly describes a MAC address flooding attack?
- AThe attacking device crafts ARP replies intended for valid hosts. The MAC address of the attacking device
then becomes the destination address found in the Layer 2 frames sent by the valid network device. - BThe attacking device crafts ARP replies intended for valid hosts. The MAC address of the attacking device
then becomes the source address found in the Layer 2 frames sent by the valid network device. - CThe attacking device spoofs a destination MAC address of a valid host currently in the CAM table. The
switch then forwards frames destined for the valid host to the attacking device. - DThe attacking device spoofs a source MAC address of a valid host currently in the CAM table.
The switch then forwards frames destined for the valid host to the attacking device. - EFrames with unique, invalid destination MAC addresses flood the switch and exhaust CAM table space.The result is that new entries cannot be inserted because of the exhausted CAM table space, and traffic is subsequently flooded out all ports.
- FFrames with unique, invalid source MAC addresses flood the switch and exhaust CAM table space. The
result is that new entries cannot be inserted because of the exhausted CAM table space, and traffic is
subsequently flooded out all ports.
- AThe attacking device crafts ARP replies intended for valid hosts. The MAC address of the attacking device
60Refer to the exhibit.
An attacker is connected to interface Fa0/11 on switch A-SW2 and attempts to establish a DHCP server for a
man-in-middle attack. Which recommendation, if followed, would mitigate this type of attack?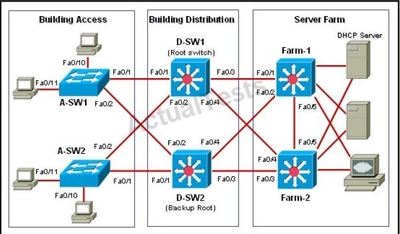
- AAll switch ports in the Building Access block should be configured as DHCP trusted ports.
- BAll switch ports in the Building Access block should be configured as DHCP untrusted ports.
- CAll switch ports connecting to hosts in the Building Access block should be configured as DHCP trusted
ports. - DAll switch ports connecting to hosts in the Building Access block should be configured as DHCP untrusted
ports. - EAll switch ports in the Server Farm block should be configured as DHCP untrusted ports.
- FAll switch ports connecting to servers in the Server Farm block should be configured as DHCP untrusted
ports.
61Refer to the exhibit.
The web servers WS_1 and WS_2 need to be accessed by external and internal users. For security reasons,
the servers should not communicate with each other, although they are located on the same subnet. However,
the servers do need to communicate with a database server located in the inside network. Which configuration
isolates the servers from each other?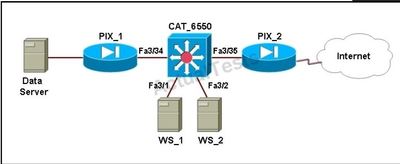
- AThe switch ports 3/1 and 3/2 are defined as secondary VLAN isolated ports.
The ports connecting to the two firewalls are defined as primary VLAN promiscuous ports. - BThe switch ports 3/1 and 3/2 are defined as secondary VLAN community ports.
The ports connecting to the two firewalls are defined as primary VLAN promiscuous ports. - CThe switch ports 3/1 and 3/2 and the ports connecting to the two firewalls are defined as primary VLAN
promiscuous ports. - DThe switch ports 3/1 and 3/2 and the ports connecting to the two firewalls are defined as primary VLAN
community ports.
- AThe switch ports 3/1 and 3/2 are defined as secondary VLAN isolated ports.
62What does the command udld reset accomplish?
- Aallows a UDLD port to automatically reset when it has been shut down
- B resets all UDLD enabled ports that have been shutdown
- Cremoves all UDLD configurations from interfaces that were globally enabled
- Dremoves all UDLD configurations from interfaces that were enabled per-port
63Refer to the exhibit
Dynamic ARP Inspection is enabled only on switch SW_A. Host_A and Host_B acquire their IP addresses
from the DHCP server connected to switch SW_A. What would the outcome be if Host_B initiated an ARP
spoof attack toward Host_A?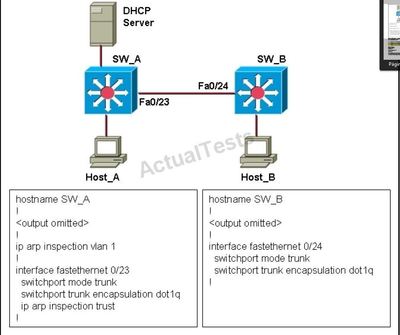
- AThe spoof packets are inspected at the ingress port of switch SW_A and are permitted.
- BThe spoof packets are inspected at the ingress port of switch SW_A and are dropped.
- CThe spoof packets are not inspected at the ingress port of switch SW_A and are permitted.
- DThe spoof packets are not inspected at the ingress port of switch SW_A and are dropped.
64Which statement is true about Layer 2 security threats?
- AMAC spoofing, in conjunction with ARP snooping, is the most effective counter-measure against
reconnaissance attacks that use Dynamic ARP Inspection to determine vulnerable attack points. - BDHCP snooping sends unauthorized replies to DHCP queries.
- CARP spoofing can be used to redirect traffic to counter Dynamic ARP Inspection.
- DDynamic ARP Inspection in conjunction with ARP spoofing can be used to counter DHCP snooping
attacks. - EMAC spoofing attacks allow an attacking device to receive frames intended for a different network host.
- FPort scanners are the most effective defense against Dynamic ARP Inspection.
- AMAC spoofing, in conjunction with ARP snooping, is the most effective counter-measure against
65On a Company switch named R1 you configure the following:
ip arp inspection vlan 10-12, 15
What is the purpose of this global configuration command made on R1?- ADiscards ARP packets with invalid IP-to-MAC address bindings on trusted ports
- BValidates outgoing ARP requests for interfaces configured on VLAN 10, 11, 12, or 15
- CIntercepts, logs, and discards ARP packets with invalid IP-to-MAC address bindings
- DIntercepts all ARP requests and responses on trusted ports
- ENone of the other alternatives apply
66Refer to the exhibit.
Which two of the following statements are true? (Choose two)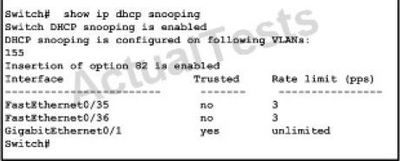
- ADHCP snooping is enabled for 155 Vlans
- BDHCP snooping is enabled for a single Vlan
- CDHCP Snooping is not enabled for any VLan
- DOption 82 is enabled for a VLAN 155
- EPorts Fa0/5 and Fa0/6 should be kept shutdown as these are untrusted ports
67What are two methods of mitigating MAC address flooding attacks? (Choose two.)
- APlace unused ports in a common VLAN.
- BImplement private VLANs.
- CImplement DHCP snooping.
- DImplement port security.
- EImplement VLAN access maps
68What is one method that can be used to prevent VLAN hopping?
- AConfigure ACLs.
- BEnforce username and password combinations.
- CConfigure all frames with two 802.1Q headers.
- DExplicitly turn off DTP on all unused ports.
- EConfigure VACLs.
69Why is BPDU guard an effective way to prevent an unauthorized rogue switch from altering the spanning-tree
topology of a network?- ABPDU guard can guarantee proper selection of the root bridge.
- BBPDU guard can be utilized along with PortFast to shut down ports when a switch is connected to the port.
- CBPDU guard can be utilized to prevent the switch from transmitting BPDUs and incorrectly altering the root
bridge election - DBPDU guard can be used to prevent invalid BPDUs from propagating throughout the network
70What two steps can be taken to help prevent VLAN hopping? (Choose two.)
- APlace unused ports in a common unrouted VLAN.
- BEnable BPDU guard.
- CImplement port security.
- DPrevent automatic trunk configurations.
- EDisable Cisco Discovery Protocol on ports where it is not necessary.
71When an attacker is using switch spoofing to perform VLAN hopping, how is the attacker able to gather
information?- AThe attacking station uses DTP to negotiate trunking with a switch port and captures all traffic that is
allowed on the trunk. - BThe attacking station tags itself with all usable VLANs to capture data that is passed through the switch,
regardless of the VLAN to which the data belongs. - CThe attacking station generates frames with two 802.1Q headers to cause the switch to forward the frames
to a VLAN that would be inaccessible to the attacker through legitimate means. - DThe attacking station uses VTP to collect VLAN information that is sent out and then tags itself with the
domain information to capture the data.
- AThe attacking station uses DTP to negotiate trunking with a switch port and captures all traffic that is
72Refer to the exhibit.
DHCP snooping is enabled for selected VLANs to provide security on the network. How do the switch ports
handle the DHCP messages?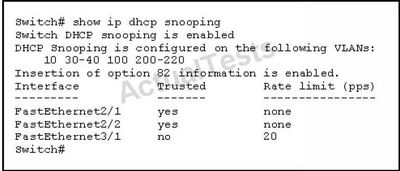
- AA DHCPOFFER packet from a DHCP server received on Ports Fa2/1 and Fa2/2 is dropped.
- BA DHCP packet received on ports Fa2/1 and Fa2/2 is dropped if the source MAC address and the DHCP
client hardware address does not match Snooping database. - C A DHCP packet received on ports Fa2/1 and Fa2/2 is forwarded without being tested
- DA DHCPRELEASE message received on ports Fa2/1 and Fa2/2 has a MAC address in the DHCP
snooping binding database, but the interface information in the binding database does not match the
interface on which the message was received and is dropped.
73Which three statements about Dynamic ARP Inspection are true? (Choose three.)
- AIt determines the validity of an ARP packet based on the valid MAC address-to-IP address bindings stored
in the DHCP snooping database. - BIt forwards all ARP packets received on a trusted interface without any checks.
- CIt determines the validity of an ARP packet based on the valid MAC address-to-IP address bindings stored
in the CAM table. - DIt forwards all ARP packets received on a trusted interface after verifying and inspecting the packet against
the Dynamic ARP Inspection table. - EIt intercepts all ARP packets on untrusted ports.
- FIt is used to prevent against a DHCP snooping attack.
- AIt determines the validity of an ARP packet based on the valid MAC address-to-IP address bindings stored
74You are tasked with designing a security solution for your network. What information should be gathered
before you design the solution?- AIP addressing design plans, so that the network can be appropriately segmented to mitigate potential
network threats - B a list of the customer requirements
- Cdetailed security device specifications
- Dresults from pilot network testing
- AIP addressing design plans, so that the network can be appropriately segmented to mitigate potential
75Which two components should be part of a security implementation plan? (Choose two.)
- Adetailed list of personnel assigned to each task within the plan
- Ba Layer 2 spanning-tree design topology
- Crollback guidelines
- Dplacing all unused access ports in VLAN 1 to proactively manage port security
- Eenabling SNMP access to Cisco Discovery Protocol data for logging and forensic analysis
76When creating a network security solution, which two pieces of information should you have obtained
previously to assist in designing the solution? (Choose two.)- Aa list of existing network applications currently in use on the network
- Bnetwork audit results to uncover any potential security holes
- Ca planned Layer 2 design solution
- Da proof-of-concept plan
- Edevice configuration templates
77What action should you be prepared to take when verifying a security solution?
- Ahaving alternative addressing and VLAN schemes
- B having a rollback plan in case of unwanted or unexpected results
- Crunning a test script against all possible security threats to insure that the solution will mitigate all potential
threats - Disolating and testing each security domain individually to insure that the security design will meet overall
requirements when placed into production as an entire system
78When you enable port security on an interface that is also configured with a voice VLAN, what is the maximum
number of secure MAC addresses that should be set on the port?- ANo more than one secure MAC address should be set.
- BThe default is set.
- CThe IP phone should use a dedicated port, therefore only one MAC address is needed per port.
- DNo value is needed if the switchport priority extend command is configured.
- ENo more than two secure MAC addresses should be set.
79Refer to the exhibit.
From the configuration shown, what can be determined?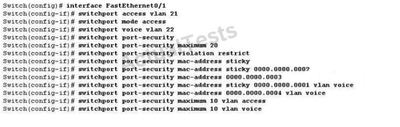
- AThe sticky addresses are only those manually configured MAC addresses enabled with the sticky keyword.
- BThe remaining secure MAC addresses are learned dynamically, converted to sticky secure MAC
addresses, and added to the running configuration. - CA voice VLAN is configured in this example, so port security should be set for a maximum of 2.
- DA security violation restricts the number of addresses to a maximum of 10 addresses per access VLAN and
voice VLAN. The port is shut down if more than 10 devices per VLAN attempt to access the port.
80By itself, what does the command aaa new-model enable?
- AIt globally enables AAA on the switch, with default lists applied to the VTYs.
- BNothing; you must also specify which protocol (RADIUS or TACACS) will be used for AAA.
- CIt enables AAA on all dot1x ports.
- DNothing; you must also specify where (console, TTY, VTY, dot1x) AAA is being applied.
81What is needed to verify that a newly implemented security solution is performing as expected?
- Aa detailed physical and logical topology
- Ba cost analysis of the implemented solution
- Cdetailed logs from the AAA and SNMP servers
- Dresults from audit testing of the implemented solution
82When configuring port security on a Cisco Catalyst switch port, what is the default action taken by the switch if
a violation occurs?- Aprotect (drop packets with unknown source addresses)
- Brestrict (increment SecurityViolation counter)
- Cshut down (access or trunk port)
- Dtransition (the access port to a trunking port)
83Refer to the exhibit.
What happens when one more user is connected to interface FastEthernet 5/1?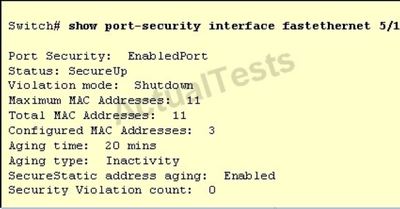
- AAll secure addresses age out and are removed from the secure address list. The security violation counter
increments. - BThe first address learned on the port is removed from the secure address list and is replaced with the new
address. - CThe interface is placed into the error-disabled state immediately, and an SNMP trap notification is sent.
- DThe packets with the new source addresses are dropped until a sufficient number of secure MAC
addresses are removed from the secure address list.
- AAll secure addresses age out and are removed from the secure address list. The security violation counter
84Refer to the exhibit.
What happens to traffic within VLAN 14 with a source address of 172.16.10.5?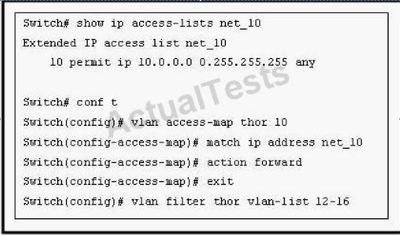
- AThe traffic is forwarded to the TCAM for further processing.
- BThe traffic is forwarded to the router processor for further processing.
- CThe traffic is dropped
- DThe traffic is forwarded without further processing
85What does the global configuration command ip arp inspection vlan 10-12, 15 accomplish?
- Avalidates outgoing ARP requests for interfaces configured on VLAN 10, 11, 12, or 15
- Bintercepts all ARP requests and responses on trusted ports
- Cintercepts, logs, and discards ARP packets with invalid IP-to-MAC address bindings
- Ddiscards ARP packets with invalid IP-to-MAC address bindings on trusted ports
86The DAI feature has been implemented in the ACME switched LAN. Which three statements are true about the
dynamic ARP inspection (DAI) feature? (Select three)- ADAI can be performed on ingress ports only.
- BDAI can be performed on both ingress and egress ports.
- CDAI is supported on access ports, trunk ports, EtherChannel ports, and private VLAN ports.
- DDAI should be enabled on the root switch for particular VLANs only in order to secure the ARP caches of
hosts in the domain. - EDAI should be configured on all access switch ports as untrusted and on all switch ports connected to other
switches as trusted. - FDAI is supported on access and trunk ports only.
- ADAI can be performed on ingress ports only.
87You are implementing basic switch security best practices.
Which of these is a tactic that you can use to mitigate compromises from being launched through the switch?- AMake all ports private VLAN ports.
- BPlace all unused ports in native VLAN 1 until needed.
- CProactively configure unused switch ports as access ports.
- DDisable Cisco Discovery Protocol globally.
88Which three statements apply to access control of both bridged and routed traffic for VLANs? (Choose three.)
- ARouter ACLs can be applied to the input and output directions of a VLAN interface.
- BBridged ACLs can be applied to the input and output directions of a VLAN interface.
- COnly router ACLs can be applied to a VLAN interface.
- DVLAN maps can be applied to a VLAN interface.
- EVLAN maps and router ACLs can be used in combination.
- ARouter ACLs can be applied to the input and output directions of a VLAN interface.
89Refer to the exhibit. Which statement is true about the show running-config output?
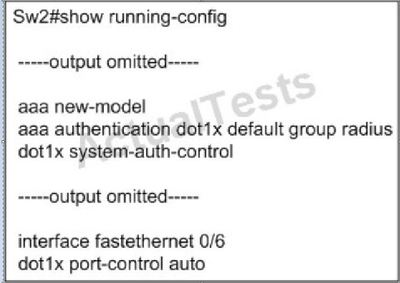
- ASw2 is configured for switch-based authentication using RADIUS.
- BInterface FastEthernet0/6 is configured with a SmartPort macro using RADIUS.
- CInterface FastEthernet0/6 is configured for 802.1X Authenticated Trunking Protocol (ATP).
- DInterface FastEthernet0/6 is configured for port-based traffic control.
- EInterface FastEthernet0/6 is configured for port-based authentication.
90Refer to the exhibit.
The show port-security interface fa0/1 command was issued on switch SW1. Given the output that was
generated,which two security statement are true? (Choose two.)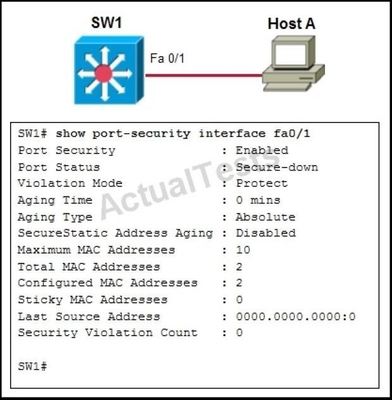
- AInterface FastEthernet 0/1 was configured with the switchport port-security aging command.
- BInterface FastEthernet 0/1 was configured with the switchport port-security protect command.
- CInterface FastEthernet 0/1 was configured with the switchport port-security violation restrict command.
- DWhen the number of secure IP addresses reaches 10, the interface will immediately shut down.
- EWhen the number of secure MAC addresses reaches 10, packets from unknown MAC addresses will be
dropped.
91What is a characteristic of a VLAN map that does not contain a match clause?
- Aimplicit deny feature at end of list
- B implicit forward feature at end of list
- C can only be implemented by the input direction within the VLAN
- Dcan only be implemented by the output direction within the VLAN
92Which three items are types of PVLAN ports? (Choose three.)
- Acommunity
- Bdedicated
- Cdesireable
- Disolated
- Enative
- Fpromiscuous
93Which optional feature of an Ethernet switch disables a port on a point-to-point link if the port does not receive
traffic while Layer 1 status is up?- ABackboneFast
- BUplinkFast
- CLoop Guard
- DUDLD aggressive mode
- EFast Link Pulse bursts
- FLink Control Word
94When configuring private VLANs, which configuration task must you do first?
- AConfigure the private VLAN port parameters.
- BConfigure and map the secondary VLAN to the primary VLAN.
- CDisable IGMP snooping.
- DSet the VTP mode to transparent.
95Which statement about the configuration and application of port access control lists is true?
- APACLs can be applied in the inbound or outbound direction of a Layer 2 physical interface.
- B At Layer 2, a MAC address PACL takes precedence over any existing Layer 3 PACL.
- CWhen you apply a port ACL to a trunk port, the ACL filters traffic on all VLANs present on the trunk port.
- DPACLs are not supported on EtherChannel interfaces.
96Refer to the exhibit.
Which statement about the command output is true?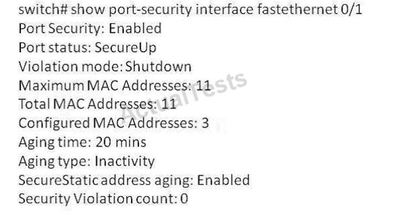
- AIf the number of devices attempting to access the port exceeds 11, the port shuts down for 20 minutes, as
configured. - BThe port has security enabled and has shut down due to a security violation.
- CThe port is operational and has reached its configured maximum allowed number of MAC addresses.
- DThe port allows access for 11 MAC addresses in addition to the three configured MAC addresses.
- AIf the number of devices attempting to access the port exceeds 11, the port shuts down for 20 minutes, as
97Refer to the exhibit.
Which statement is true?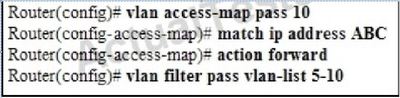
- AIP traffic matching access list ABC is forwarded through VLANs 5-10.
- BIP traffic matching VLAN list 5-10 is forwarded, and all other traffic is dropped.
- CAll VLAN traffic matching VLAN list 5-10 is forwarded, and all traffic matching access list ABC is dropped.
- DAll VLAN traffic in VLANs 5-10 that match access list ABC is forwarded, and all other traffic is dropped.
98Refer to the exhibit.
What can be concluded about VLANs 200 and 202?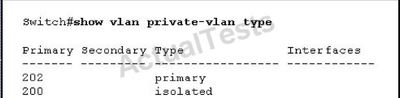
- AVLAN 202 carries traffic from promiscuous ports to isolated, community, and other promiscuous ports in
the same VLAN. VLAN 200 carries traffic between community ports and to promiscuous ports. - BVLAN 202 carries traffic from promiscuous ports to isolated, community, and other promiscuous ports in
the same VLAN. VLAN 200 carries traffic from isolated ports to a promiscuous port. - CVLAN 200 carries traffic from promiscuous ports to isolated, community, and other promiscuous ports in
the same VLAN. VLAN 202 carries traffic between community ports and to promiscuous ports. - DVLAN 200 carries traffic from promiscuous ports to isolated, community, and other promiscuous ports in
the same VLAN. VLAN 202 carries traffic from isolated ports to a promiscuous port.
- AVLAN 202 carries traffic from promiscuous ports to isolated, community, and other promiscuous ports in
99A switch has been configured with PVLANs. With what type of PVLAN port should the default gateway be
configured?- Aisolated
- Bpromiscuous
- Ccommunity
- Dprimary
- Etrunk
- Aisolated
100Refer to the exhibit.
Which statement about the private VLAN configuration is true?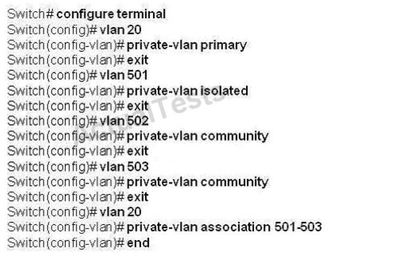
- AOnly VLAN 503 will be the community PVLAN, because multiple community PVLANs are not allowed.
- BUsers of VLANs 501 and 503 will be able to communicate.
- CVLAN 502 is a secondary VLAN.
- DVLAN 502 will be a standalone VLAN, because it is not associated with any other VLANs.
101Which Cisco IOS command globally enables port-based authentication on a switch?
- A aaa port-auth enable
- B radius port-control enable
- Cdot1x system-auth-control
- Dswitchport aaa-control enable
- A aaa port-auth enable
102Private VLANS can be configured as which three of these port types? (Choose three.)
- Aisolated
- Bprotected
- C private
- Dassociated
- Epromiscuous
- Fcommunity
- Aisolated
103What is the method used to filter traffic being bridged within a VLAN?
- AEthernet maps
- Brouter ACLs
- CVLAN maps
- DIP ACLs
104Which statement about when standard access control lists are applied to an interface to control inbound or
outbound traffic is true?- AThe best match of the ACL entries is used for granularity of control.
- BThey use source IP information for matching operations.
- CThey use source and destination IP information for matching operations.
- DThey use source IP information along with protocol-type information for finer granularity of control.
105Refer to the exhibit.
Which two statements about this Layer 3 security configuration example are true? (Choose two.)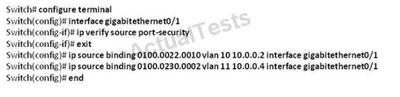
- AStatic IP source binding can be configured only on a routed port.
- BSource IP and MAC filtering on VLANs 10 and 11 will occur.
- CDHCP snooping will be enabled automatically on the access VLANs.
- DIP Source Guard is enabled.
- EThe switch will drop the configured MAC and IP address source bindings and forward all other traffic.
106A network administrator wants to configure 802.1x port-based authentication, however, the client workstation is
not 802.1x compliant.What is the only supported authentication server that can be used?- ATACACS with LEAP extensions
- BTACACS+
- CRADIUS with EAP extensions
- DLDAP
107Which statement about 802.1x port-based authentication is true?
- AHosts are required to have an 802.1x authentication client or utilize PPPoE.
- BBefore transmitting data, an 802.1x host must determine the authorization state of the switch.
- CRADIUS is the only supported authentication server type.
- DIf a host initiates the authentication process and does not receive a response, it assumes it is not
authorized.
108In the use of 802.1X access control, which three protocols are allowed through the switch port before
authentication takes place? Select three.- ASTP
- B CDP
- CEAP MD5
- DTACACS+
- E EAP-over-LAN
- Fprotocols not filtered by an ACL
- ASTP
109Which two characteristics apply to Cisco Catalyst 6500 Series Switch supervisor redundancy using NSF?
(Choose two.)- Asupported by RIPv2, OSPF, IS-IS, and EIGRP
- Buses the FIB table
- Csupports IPv4 and IPv6 multicast
- Dprevents route flapping
- Eindependent of SSO
- FNSF combined with SSO enables supervisor engine load balancing
110Which statement best describes implementing a Layer 3 EtherChannel?
- AEtherChannel is a Layer 2 feature and not a Layer 3 feature.
- BImplementation requires switchport mode trunk and matching parameters between switches.
- CImplementation requires disabling switchport mode.
- DA Layer 3 address is assigned to the physical interface.
111Refer to the exhibit.
You have configured an interface to be an SVI for Layer 3 routing capabilities. Assuming that all VLANs have been correctly configured, what can be determined?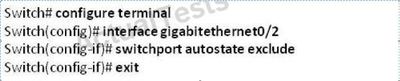
- AInterface gigabitethernet0/2 will be excluded from Layer 2 switching and enabled for Layer 3 routing.
- BThe command switchport autostate exclude should be entered in global configuration mode, not
subinterface mode, to enable a Layer 2 port to be configured for Layer 3 routing. - CThe configured port is excluded in the calculation of the status of the SVI.
- DThe interface is missing IP configuration parameters; therefore, it will only function at Layer 2.
112Refer to the exhibit.
Which statement is true?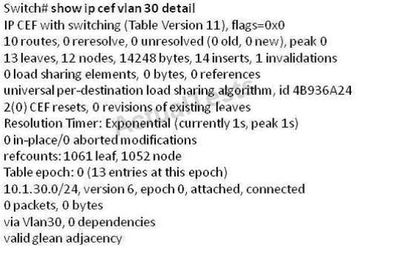
- ACisco Express Forwarding load balancing has been disabled.
- BSVI VLAN 30 connects directly to the 10.1.30.0/24 network due to a valid glean adjacency.
- CVLAN 30 is not operational because no packet or byte counts are indicated.
- DThe IP Cisco Express Forwarding configuration is capable of supporting IPv6.
113Refer to exhibit as:
Which statement about the EIGRP routing being performed by the switch is true?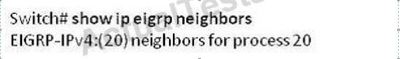
- AThe EIGRP neighbor table contains 20 neighbors.
- BEIGRP is running normally and receiving IPv4 routing updates.
- CEIGRP status cannot be determined. The command show ip eigrp topology would determine the routing
protocol status. - DThe switch has not established any neighbor relationships.
Further network testing and troubleshooting must be performed to determine the cause of the problem.
114You have configured a Cisco Catalyst switch to perform Layer 3 routing via an SVI and you have assigned that
interface to VLAN 20.
To check the status of the SVI, you issue the show interfaces vlan 20 command at the CLI prompt.
You see from the output display that the interface is in an up/up state.
What must be true in an SVI configuration to bring the VLAN and line protocol up?- AThe port must be physically connected to another Layer 3 device.
- BAt least one port in VLAN 20 must be active.
- CThe Layer 3 routing protocol must be operational and receiving routing updates from neighboring peer
devices. - DBecause this is a virtual interface, the operational status is always in an "up/up" state.
115Refer to the exhibit, which is from a Cisco Catalyst 3560 Series Switch.
Which statement about the Layer 3 routing functionality of the interface is true?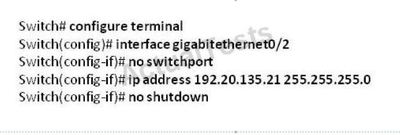
- AThe interface is configured correctly for Layer 3 routing capabilities.
- BThe interface needs an additional configuration entry to enable IP routing protocols.
- CSince the interface is connected to a host device, the spanning-tree portfast command must be added to
the interface. - DAn SVI interface is needed to enable IP routing for network 192.20.135.0.
116Refer to the exhibit.
Host A and Host B are connected to the Cisco Catalyst 3550 switch and have been assigned to their
respective VLANs.
The rest of the 3550 configuration is the default configuration.
Host A is able to ping its default gateway, 10.10.10.1, but is unable to ping Host B.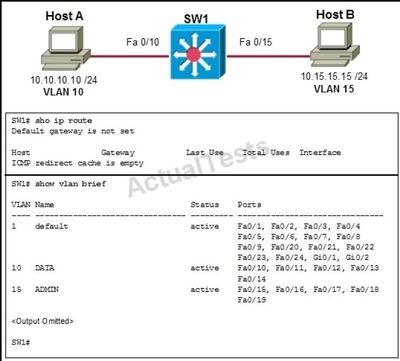
- AHSRP must be configured on SW1.
- BA separate router is needed to support inter-VLAN routing.
- CInterface VLAN 10 must be configured on the SW1 switch.
- DThe global configuration command ip routing must be configured on the SW1 switch.
- EVLANs 10 and 15 must be created in the VLAN database mode.
- FVTP must be configured to support inter-VLAN routing.
117Which three statements about routed ports on a multilayer switch are true? (Choose three.)
- AA routed port can support VLAN subinterfaces.
- BA routed port takes an IP address assignment.
- CA routed port can be configured with routing protocols.
- DA routed port is a virtual interface on the multilayer switch.
- EA routed port is associated only with one VLAN.
- FA routed port is a physical interface on the multilayer switch.
118Which two steps are necessary to configure inter-VLAN routing between multilayer switches? (Choose two.)
- AConfigure a dynamic routing protocol.
- BConfigure SVI interfaces with IP addresses and subnet masks.
- C Configure access ports with network addresses.
- DConfigure switch ports with the autostate exclude command.
- EDocument the MAC addresses of the switch ports.
- AConfigure a dynamic routing protocol.
119When configuring a routed port on a Cisco multilayer switch, which configuration task is needed to enable that
port to function as a routed port?- AEnable the switch to participate in routing updates from external devices with the router command in global
configuration mode. - BEnter the no switchport command to disable Layer 2 functionality at the interface level.
- CEach port participating in routing of Layer 3 packets must have an IP routing protocol assigned on a perinterface
level. - DRouting is enabled by default on a multilayer switch, so the port can become a Layer 3 routing interface by
assigning the appropriate IP address and subnet information.
- AEnable the switch to participate in routing updates from external devices with the router command in global
120A standalone wireless AP solution is being installed into the campus infrastructure. The access points appear
to boot correctly, but wireless clients are not obtaining correct access. You verify that this is the local switch
configuration connected to the access point:
interface ethernet 0/1
switchport access vlan 10
switchport mode access
spanning-tree portfast
mls qos trust dscp
What is the most likely cause of the problem?- AQoS trust should not be configured on a port attached to a standalone AP.
- BQoS trust for switchport mode access should be defined as "cos".
- Cswitchport mode should be defined as "trunk" with respective QoS.
- Dswitchport access vlan should be defined as "1".
121During the implementation of a voice solution, which two required items are configured at an access layer
switch that will be connected to an IP phone to provide VoIP communication? (Choose two.)- AA. allowed codecs
- Buntagged VLAN
- Cauxiliary VLAN
- DCisco Unified Communications Manager IP address
- E RSTP
- AA. allowed codecs
122Which two statements best describe Cisco IOS IP SLA? (Choose two.)
- Aonly implemented between Cisco source and destination-capable devices
- Bstatistics provided by syslog, CLI, and SNMP
- Cmeasures delay, jitter, packet loss, and voice quality
- Donly monitors VoIP traffic flows
- Eprovides active monitoring
123Which two items best describe a Cisco IOS IP SLA responder? (Choose two.)
- Arequired at the destination to implement Cisco IOS IP SLA services
- B improves measurement accuracy
- C required for VoIP jitter measurements
- Dprovides security on Cisco IOS IP SLA messages via LEAP or EAP-FAST authentication
- Eresponds to one Cisco IOS IP SLA operation per port
- Fstores the resulting test statistics
124What does the interface subcommand switchport voice vlan 222 indicate?
- AThe port is configured for both data and voice traffic.
- BThe port is fully dedicated to forwarding voice traffic.
- CThe port operates as an FXS telephony port.
- DVoice traffic is directed to VLAN 222.
125A campus infrastructure supports wireless clients via Cisco Aironet AG Series 1230, 1240, and 1250 access
points. With DNS and DHCP configured, the 1230 and 1240 access points appear to boot and operate
normally. However, the 1250 access points do not seem to operate correctly.
What is the most likely cause of this problem?- ADHCP with option 150
- BDHCP with option 43
- C PoE
- D DNS
- Eswitch port does not support gigabit speeds
126A network is deployed using recommended practices of the enterprise campus network model, including users
with desktop computers connected via IP phones. Given that all components are QoS-capable, where are the
two optimal locations for trust boundaries to be configured by the network administrator? (Choose two.)- Ahost
- BIP phone
- Caccess layer switch
- Ddistribution layer switch
- Ecore layer switch
127Refer to the exhibit.
Assume that Switch_A is active for the standby group and the standby device has only the default HSRP configuration. Which statement is true?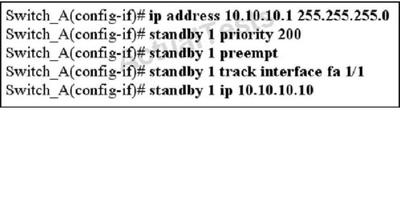
- AIf port Fa1/1 on Switch_A goes down, the standby device takes over as active.
- BIf the current standby device had the higher priority value, it would take over the role of active for the HSRP
- CIf port Fa1/1 on Switch_A goes down, the new priority value for the switch would be 190.
- DIf Switch_A had the highest priority number, it would not take over as active router.
128Refer to the exhibit.
GLBP has been configured on the network. When the interface serial0/0/1 on router R1 goes down, how is the traffic coming from Host1 handled?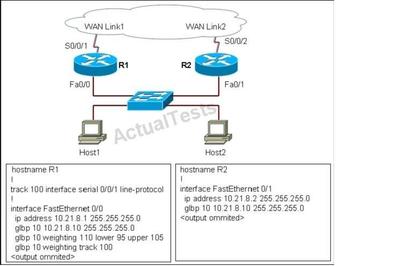
- AThe traffic coming from Host1 and Host2 is forwarded through router R2 with no disruption.
- BThe traffic coming from Host2 is forwarded through router R2 with no disruption. Host1 sends an ARP
request to resolve the MAC address for the new virtual gateway. - CThe traffic coming from both hosts is temporarily interrupted while the switchover to make R2 active occurs.
- DThe traffic coming from Host2 is forwarded through router R2 with no disruption. The traffic from Host1 is dropped due to the disruption of the load balancing feature configured for the GLBP group.
129Refer to the exhibit and the partial configuration on routers R1 and R2.
HSRP is configured on the network to provide network redundancy for the IP traffic. The network administrator noticed that R2 does not become active when the R1 serial0 interface goes down. What should be changed in the configuration to fix the problem?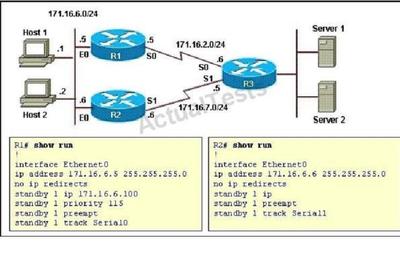
- AR2 should be configured with an HSRP virtual address.
- BR2 should be configured with a standby priority of 100.
- CThe Serial0 interface on router R2 should be configured with a decrement value of 20.
- Dthe Serial0 interface on router R1 should be configured with a decrement value of 20.
130The following command was issued on a router that is being configured as the active HSRP router.
standby ip 10.2.1.1
Which statement about this command is true?- AThis command will not work because the HSRP group information is missing.
- BThe HSRP MAC address will be 0000.0c07.ac00.
- CThe HSRP MAC address will be 0000.0c07.ac01.
- DThe HSRP MAC address will be 0000.070c.ac11.
- EThis command will not work because the active parameter is missing.
131Refer to the exhibit.
Three switches are configured for HSRP.
Switch1 remains in the HSRP listen state. What is the most likely cause of this status?
Exhibit: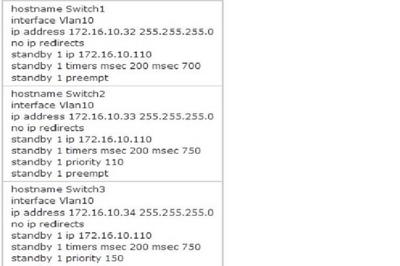
- AThis is normal operation.
- BThe standby group number does not match the VLAN number.
- CIP addressing is incorrect.
- DPriority commands are incorrect.
- EStandby timers are incorrect.
132Three Cisco Catalyst switches have been configured with a first-hop redundancy protocol. While reviewing some show commands, debug output, and the syslog, you discover the following information:
What conclusion can you infer from this information?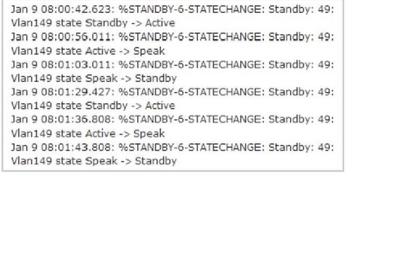
- AVRRP is initializing and operating correctly.
- BHSRP is initializing and operating correctly.
- CGLBP is initializing and operating correctly.
- DVRRP is not exchanging three hello messages properly.
- EHSRP is not exchanging three hello messages properly.
- FGLBP is not exchanging three hello messages properly.
Información
- Descripción
- Test sobre 642-813, creado por mapanuyaaguilaster el 08/12/2014.
- Autor
- mapanuyaaguilaster
- Idioma
- Español
- Visitas
- 184
- Etiquetas
- Valoración
- Aún sin valoraciones Valora este test