
Test
IPS II
Preguntas del test (23)
1Attacker’s sessions consume all resources—RAM, CPU, port numbers
Slows down or disables the target until it can’t serve legitimate requests- ADoS Attacks
- BAnomaly
- CExploit
2Types of DoS attacks (Select 3)
- ATCP SYN flood
- BICMP sweep
- CTCP port scan
- DTCP sweep
- EICMP SYN flood
3Attacker floods victim with incomplete TCP/IP connection requests
The victim’s connection table becomes full, so legitimate clients can’t connect- ATCP SYN flodd
- BICMP sweep
- CTCP port scan
4Attackers eends ICMP traffic to find targets
Attacker then attacks hosts that reply- ATCP SYN flood
- BICMP Sweep
- CTCP port scan
5Attacker probes a victim by sending TCP/IP connection requests to varying destination ports
Based on replies, attacker can map out which services are running on the victim system
Attacker then targets those destination ports to exploit the system- ATCP SYN flood
- BICMP sweep
- CTCP port scan
6You can apply DoS protection to four protocols:
- ATCP
- BUDP
- CICMP
- DSCTP
- EDST
- FSRC
- GSMTP
7detects a high volume of that specific protocol, or signal in the protocol.
- AFlood sensor
- BSweep/Scan
- CSource Signatures
- DDestination signatures
8detects probing attempts to map which of the host’s ports respond and, therefore, might be vulnerable.
- AFlood sensor
- BSweep/Scan
- CSource Signatures
- DDestination signatures
9look for large volumes of traffic originating from a single IP.
- AFlood sensor
- BSweep/Scan
- CSource Signatures
- DDestination signatures
10look for large volumes of traffic destined for a single IP.
- AFlood sensor
- BSweep/Scan
- CSource Signatures
- DDestination signatures
11Which of the following type of attack is a characteristic of a DoS attack?
- AA. Attempts to exploit a known application vulnerability
- BB. Attempts to overload a server with TCP SYN packets
12Which DOS anomaly sensor can be used to detect and block a port scanner’s probing attempts?
- AA. tcp_syn_flood
- BB. tcp_port_scan
13Web Application Firewall (WAF) is only available in proxy inspection mode
- AVerdadero
- BFalso
14?
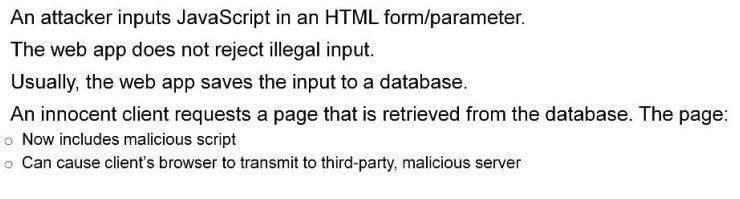
- AExample of a Web Attack-Cross-Site Scripting
- BExample of a Web Attack—SQL Injection
15The variety of attacks based on _______ is limitless, but they commonly include transmitting private data like authentication cookies or other session information to the attacker.
- Across-site scripting (XSS)
- BSQL injection
16?
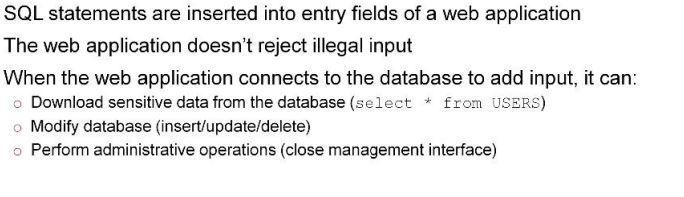
- AExample of a Web Attack—SQL Injection
- BExample of a Web Attack XSS
17WAF protocol constraints protect against what type of attacks?
- AA. Buffer overflow
- BB. ICMP Sweep
18To use the WAF feature, which inspection mode should be used?
- AA. Flow
- BB. Proxy
19Which chipset uses NTurbo to accelerate IPS sessions?
- AA. CP9
- BB. SoC3
20Which of the following features requires full SSL inspection to maximize it’s detection capability?
- AA. WAF
- BB. DoS
21If there are high-CPU use problems caused by the IPS, you can use the ____________ command with option 5 to isolate where the problem might be.
- Adiagnose test application ipsmonitor
- Bdiagnose test ipsmonitor
- Cdiagnose application ipsmonitor
22Which FQDN does FortiGate use to obtain IPS updates?
- Aupdate.fortiguard.net
- Bservice.fortiguard.com
23When IPS fail open is triggered, what is the expected behavior if the IPS fail open option is set to enabled?
- ANew packets will pass through
- BNew packets will be dropped
Información
- Descripción
- El usuario ha eliminado su información de asignaturas Test sobre IPS II, creado por Usuario eliminado el 20/09/2018.
- Autor
- Usuario eliminado
- Idioma
- English
- Visitas
- 55
- Historial
- Creado el 20 sep 2018 · actualizado el 11 abr 2019
- Etiquetas