
Test
Software Development Security
Crea una cuenta gratis para terminar este test
Guarda tu progreso y consulta tu resultado final.
¿Ya tienes cuenta? Inicia sesión
Preguntas del test (20)
1Angela’s software development team is working on a large-scale control package that will run a nuclear power plant for multiple decades. They want to select an SDLC that fits their needs, which include careful upfront planning and analysis, without any anticipated change during the coding process. What SDLC model should she choose?
- AWaterfall
- BSpiral
- CAgile Scrum
- DRapid Application Development
2During a Fagan code inspection, which process can redirect to the planning stage?
- AOverview
- BPreparation
- CMeeting
- DRework
3Adam is conducting software testing by reviewing the source code of the application. What type of cost testing is Adam conducting?
- AMutation testing
- BStatic code analysis
- CDynamic code analysis
- DFuzzing
4After a major patch is released for the web application that he is responsible for, Sam proceeds to run his web application security scanner against the web application to verify that it is still secure. What is the term for the process Sam is conducting?
- ACode review
- BRegression testing
- CStress testing
- DWhiffing
5How many phases does the Spiral model cycle through?
- AThree
- BFour
- CFive
- DSix
6Charles is worried about users conducting SQL injection attacks. Which of the following solutions will best address his concerns?
- AUsing secure session management
- BEnabling logging on the database
- CPerforming user input validation
- DImplementing TLS
7Susan’s team has been writing code for a major project for a year and recently released their third version of the code. During a post implementation regression test, an issue that was originally seen in version 1 reappeared. What type of tool should Susan implement to help avoid this issue in the future?
- AStress testing
- BA WAF
- CPair programming
- DSource control management
8Precompiled SQL statements that only require variables to be input are an example of what type of application security control?
- AParameterized queries
- BEncoding data
- CInput validation
- DAppropriate access controls
9What process checks to ensure that functionality meets customer needs?
- ACNA
- BStress testing
- CUAT
- DUnit testing
10What Agile process is used to determine whether application development is occurring at the speed that was expected?
- AVelocity tracking
- BSpeed traps
- CTimeboxing
- DPlanning poker
11Using TLS to protect application traffic helps satisfy which of the OWASP 2016 best practices?
- AParameterize queries
- BEncode data
- CValidate all inputs
- DProtect data
12Kristen wants to implement code review but has a distributed team that works at various times during the day. She also does not want to create any additional support load for her team with new development environment applications. What type of review process will work best for her needs?
- APair programming
- BPass-around
- COver-the-shoulder
- DTool-assisted
13During which phase would user stories be captured during an Agile sprint in the following graphic?
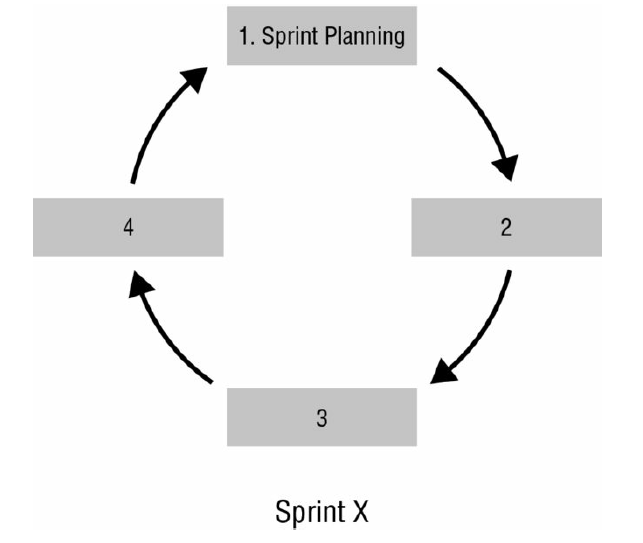
- A1
- B2
- C3
- D4
14Using the Agile sprint process, what step will occur at step 2 in the previous graphic?
- ADevelopment
- BDesign
- CTesting
- DGathering user stories
15When is the Agile sprint shown in the previous graphic complete?
- AAfter the demonstration
- BAfter testing is complete
- CWhen customers agree that the task is done
- DWhen sprint planning begins for the next sprint
16What process is used to ensure that an application can handle very high numbers of concurrent users or sessions?
- AFuzzing
- BFault injection
- CMutation testing
- DLoad testing
17Lauren wants to insert data into the response from her browser to a web application. What type of tool should she use if she wants to easily make manual changes in what her browser sends out as she interacts with the website?
- AAn interception proxy
- BA fuzzer
- CA WAF
- DA sniffer
18What type of testing focuses on inserting problems into the error handling processes and paths in an application?
- AFuzzing
- BStress testing
- CDynamic code analysis
- DFault injection
19What type of code review requires two programmers, one of whom explains their code to the other developer?
- APair programming
- BTool assisted
- COver-the-shoulder
- DPass-around
20What term is used to describe high-level requirements in Agile development efforts?
- ABacklogs
- BPlanning poker
- CVelocity tracking
- DUser stories
Información
- Descripción
- CompTIA CYSA+ Test sobre Software Development Security, creado por Luis Gallegos el 06/03/2019.
- Autor
- Luis Gallegos
- Idioma
- English
- Visitas
- 0
- Etiquetas
- Valoración
- Aún sin valoraciones Valora este test