
Test
Fundamentals of Information Security [State Exam | Part 1]
Preguntas del test (200)
1What is a potential risk when using a free and open wireless hotspot in a public location?
- AToo many users trying to connect to the Internet may cause a network traffic jam.
- BThe Internet connection can become too slow when many users access the wireless hotspot.
- CNetwork traffic might be hijacked and information stolen.
- DPurchase of products from vendors might be required in exchange for the Internet access.
2How does a security information and event management system (SIEM) in a SOC help the personnel fight against security threats?
- Aby integrating all security devices and appliances in an organization
- Bby analyzing logging data in real time
- Cby combining data from multiple technologies
- Dby dynamically implementing firewall rules
3Which statement best describes a motivation of hacktivists?
- AThey are part of a protest group behind a political cause.
- BThey are curious and learning hacking skills.
- CThey are trying to show off their hacking skills.
- DThey are interested in discovering new exploits.
4If a SOC has a goal of 99.999% uptime, how many minutes of downtime a year would be considered within its goal?
- AApproximately 5 minutes per year.
- BApproximately 10 minutes per year.
- CApproximately 20 minutes per year.
- DApproximately 30 minutes per year.
5Why do IoT devices pose a greater risk than other computing devices on a network?
- AMost IoT devices do not require an Internet connection and are unable to receive new updates.
- BIoT devices cannot function on an isolated network with only an Internet connection.
- CMost IoT devices do not receive frequent firmware updates.
- DIoT devices require unencrypted wireless connections.
6Which two services are provided by security operations centers? (Choose two.)
- Amanaging comprehensive threat solutions
- Bensuring secure routing packet exchanges
- Cresponding to data center physical break-ins
- Dmonitoring network security threats
- Eproviding secure Internet connections
7Users report that a database file on the main server cannot be accessed. A database administrator verifies the issue and notices that the database file is now encrypted. The organization receives a threatening email demanding payment for the decryption of the database file. What type of attack has the organization experienced?
- Aman-in-the-middle attack
- BDoS attack
- CRansomware
- DTrojan horse
8Which organization offers the vendor-neutral CySA+ certification?
- AIEEE
- BCompTIA
- C(ISC)²
- DGIAC
9What was used as a cyberwarfare weapon to attack a uranium enrichment facility in Iran?
- ADDoS
- BSQL injection
- CPSYOPS
- DStuxnet
10Which three technologies should be included in a SOC security information and event management system? (Choose three.)
- Afirewall appliance
- Bsecurity monitoring
- Clog management
- Dintrusion prevention
- Eproxy service
- Fthreat intelligence
11Which personnel in a SOC is assigned the task of verifying whether an alert triggered by monitoring software represents a true security incident?
- ASOC Manager
- BTier 2 personnel
- CTier 3 personnel
- DTier 1 personnel
12Which statement describes cyberwarfare?
- ACyberwarfare is an attack carried out by a group of script kiddies.
- BIt is a series of personal protective equipment developed for soldiers involved in nuclear war.
- CIt is simulation software for Air Force pilots that allows them to practice under a simulated war scenario.
- DIt is Internet-based conflict that involves the penetration of information systems of other nations.
13In the operation of a SOC, which system is frequently used to let an analyst select alerts from a pool to investigate?
- Asyslog server
- Bregistration system
- Cticketing system
- Dsecurity alert knowledge-based system
14What name is given to an amateur hacker?
- Ared hat
- Bscript kiddie
- Cblack hat
- Dblue team
15Which personnel in a SOC are assigned the task of hunting for potential threats and implementing threat detection tools?
- ATier 1 Analyst
- BSOC Manager
- CTier 2 Incident Reporter
- DTier 3 SME
16What utility is available on a Windows PC to view current running applications and processes?
- Anslookup
- Bipconfig
- CControl Panel
- DTask Manager
17A user logs in to Windows with a regular user account and attempts to use an application that requires administrative privileges. What can the user do to successfully use the application?
- ARight-click the application and choose Run as root.
- BRight-click the application and choose Run as Priviledge.
- CRight-click the application and choose Run as Administrator.
- DRight-click the application and choose Run as Superuser.
18A technician can ping the IP address of the web server of a remote company but cannot successfully ping the URL address of the same web server. Which software utility can the technician use to diagnose the problem?
- Anslookup
- Btracert
- Cnetstat
- Dipconfig
19Where are the settings that are chosen during the installation process stored?
- Ain the recovery partition
- Bin flash memory
- Cin the Registry
- Din BIOS
20What technology was created to replace the BIOS program on modern personal computer motherboards?
- ACMOS
- BMBR
- CRAM
- DUEFI
21Which two things can be determined by using the ping command? (Choose two.)
- Athe number of routers between the source and destination device
- Bthe destination device is reachable through the network
- Cthe average time it takes each router in the path between source and destination to respond
- Dthe IP address of the router nearest the destination device
- Ethe average time it takes a packet to reach the destination and for the response to return to the source
22What function is provided by the Windows Task Manager?
- AIt provides an active list of TCP connections.
- BIt maintains system logs.
- CIt selectively denies traffic on specified interfaces.
- DIt provides information on system resources and processes.
23Which type of Windows PowerShell command performs an action and returns an output or object to the next command that will be executed?
- Ascripts
- Bfunctions
- Ccmdlets
- Droutines
24What would be displayed if the netstat -abno command was entered on a Windows PC?
- Aall active TCP and UDP connections, their current state, and their associated process ID (PID)
- Bonly active TCP connections in an ESTABLISHED state
- Conly active UDP connections in an LISTENING state
- Da local routing table
25Which two commands could be used to check if DNS name resolution is working properly on a Windows PC? (Choose two.)
- Aipconfig /flushdns
- Bnet cisco.com
- Cnslookup cisco.com
- Dping cisco.com
- Enbtstat cisco.com
26Refer to the exhibit. A cyber security administrator is attempting to view system information from the Windows PowerShell and recieves the error message shown. “The requested operation requires elevation.”
What action does the administrator need to take to successfully run the command?- ARun the command from the command prompt.
- BInstall latest Windows updates.
- CRestart the abno service in Task Manager.
- DRun PowerShell as administrator.
27Refer to the exhibit. A cybersecurity analyst is investigating a reported security incident on a Microsoft Windows computer. Which tool is the analyst using?
- AEvent Viewer
- BPowerShell
- CTask Manager
- DPerformance Monitor
28For security reasons a network administrator needs to ensure that local computers cannot ping each other. Which settings can accomplish this task?
- Afirewall settings
- BMAC address settings
- Csmartcard settings
- Dfile system settings
29Consider the path representation in Windows CLI C:\Users\Jason\Desktop\mydocu.txt. What does the Users\Jason component represent?
- Afile directory and subdirectory
- Bcurrent file directory
- Cfile attribute
- Dstorage device or partition
30Which two user accounts are automatically created when a user installs Windows to a new computer? (Choose two.)
- Asuperuser
- Bguest
- Croot
- Dadministrator
- Esystem
31What term is used to describe a logical drive that can be formatted to store data?
- Apartition
- Btrack
- Csector
- Dcluster
- Evolume
32What is the purpose of entering the netsh command on a Windows PC?
- Ato create user accounts
- Bto test the hardware devices on the PC
- Cto change the computer name for the PC
- Dto configure networking parameters for the PC
33A technician is troubleshooting a PC unable to connect to the network. What command should be issued to check the IP address of the device?
- Aipconfig
- Bping
- Ctracert
- Dnslookup
34Refer to the exhibit. Which Microsoft Windows application is being used?
- AEvent Viewer
- BPowerShell
- CTask Manager
- DPerformance Monitor
35What are two reasons for entering the ipconfig command on a Windows PC? (Choose two.)
- Ato review the network configuration on the PC
- Bto check if the DNS server can be contacted
- Cto ensure that the PC can connect to remote networks
- Dto review the status of network media connections
- Eto display the bandwidth and throughput of the network connection
36What are two advantages of the NTFS file system compared with FAT32? (Choose two.)
- ANTFS allows the automatic detection of bad sectors.
- BNTFS is easier to configure.
- CNTFS allows faster formatting of drives.
- DNTFS provides more security features.
- ENTFS supports larger files.
- FNTFS allows faster access to external peripherals such as a USB drive.
37What is the purpose of using the net accounts command in Windows?
- Ato start a network service
- Bto display information about shared network resources
- Cto show a list of computers and network devices on the network
- Dto review the settings of password and logon requirements for users
38What are two reasons for entering the ping 127.0.0.1 command on a Windows PC? (Choose two.)
- Ato check if the NIC functions as expected
- Bto check if the default gateway is configured correctly
- Cto display the bandwidth and throughput of the network connection
- Dto check if the TCP/IP protocol suite is installed properly
- Eto ensure that the PC can connect to remote networks
39Why would a network administrator choose Linux as an operating system in the Security Operations Center (SOC)?
- AIt is easier to use than other operating systems.
- BIt is more secure than other server operating systems.
- CThe administrator has more control over the operating system.
- DMore network applications are created for this environment
40Which Linux command can be used to display the name of the current working directory?
- Achmod
- Bpwd
- Cps
- Dsudo
41Consider the result of the ls -l command in the Linux output below. What are the file permissions assigned to the sales user for the analyst.txt file?
ls –l analyst.txt
-rwxrw-r-- sales staff 1028 May 28 15:50 analyst.txt- Awrite only
- Bread, write, execute
- Cread, write
- Dread only
42A Linux system boots into the GUI by default, so which application can a network administrator use in order to access the CLI environment?
- Afile viewer
- Bpackage management tool
- Cterminal emulator
- Dsystem viewer
43The image displays a laptop that is acting as the SSH client that is communicating with an SSH server.
Refer to the exhibit. Which well-known port number is used by the server?- A23
- B22
- C21
- D25
44How is a server different from a workstation computer?
- AThe server works as a standalone computer.
- BThe server is designed to provide services to clients.
- CThe workstation has fewer applications installed.
- DThe workstation has more users who attach to it.
45Which two methods can be used to harden a computing device? (Choose two.)
- AAllow default services to remain enabled.
- BUpdate patches on a strict annual basis irrespective of release date.
- CEnforce the password history mechanism.
- DEnsure physical security.
- EAllow USB auto-detection.
46What is the main purpose of the X Window System?
- Ato provide a customizable CLI environment
- Bto provide a basic framework for a GUI
- Cto provide remote access to a Linux-based system
- Dto provide a basic set of penetration testing tools
47Which Linux command is used to manage processes?
- Akill
- Bgrep
- Cchrootkit
- Dls
48Why is Linux considered to be better protected against malware than other operating systems?
- Afewer deployments
- Bintegrated firewall
- Ccustomizable penetration and protection tools
- Dfile system structure, file permissions, and user account restrictions
49Which two Linux commands might be used before using the kill command? (Choose two.)
- Atop
- Bls
- Cgrep
- Dps
- Echroot
50What term is used for operating system updates?
- Apatches
- Bnew releases
- Cpenetration testing
- Dpackages
51What term describes a set of software tools designed to increase the privileges of a user or to grant access to the user to portions of the operating system that should not normally be allowed?
- Apenetration testing
- Bpackage manager
- Crootkit
- Dcompiler
52What is the well-known port address number used by DNS to serve requests?
- A60
- B110
- C25
- D53
53Which file system is the primary file system used by Apple in current Macintosh computers? (спорный вопрос = оба варианта ответа подходят, но в книге указан лишь HFS+).
- ACDFS
- BAPFS
- Cext3
- Dext2
- EHFS+
54Which type of tool allows administrators to observe and understand every detail of a network transaction?
- Amalware analysis tool
- Bpacket capture software
- Cticketing system
- Dlog manager
55Which command can be utilized to view log entries of NGINX system events in real time?
- Asudo journalctl –u nginx.service -f
- Bsudo journalctl –f
- Csudo journalctl –until "1 hour ago"
- Dsudo journalctl –u nginx.services
56What is the purpose of a Linux package manager?
- AIt provides access to settings and the shutdown function.
- BIt is used to compile code that creates an application.
- CIt is used to install an application.
- DIt provides a short list of tasks a particular application can perform.
57Which user can override file permissions on a Linux computer?
- Aonly the creator of the file
- Bany user that has 'group' permission to the file
- Cany user that has 'other' permission to the file
- Droot user
58Which Linux file system introduced the journaled file system, which can be used to minimize the risk of file system corruption in the event of a sudden power loss?
- Aext2
- Bext3
- CNFS
- DCDFS
59What is the method employed by a Linux kernel to create new processes for multitasking of a process?
- Acreating interdependent processes
- Bdynamic processes
- Cpipelining
- Dforking
60What is a purpose of apt-get commands?
- Ato configure an appointment for a specific date and time
- Bto configure and manage task (to-do) lists
- Cto update the operating system
- Dto apportion and configure a part of the hard disk for file storage
61How is a DHCPDISCOVER transmitted on a network to reach a DHCP server?
- AA DHCPDISCOVER message is sent with a multicast IP address that all DHCP servers listen to as the destination address.
- BA DHCPDISCOVER message is sent with the broadcast IP address as the destination address.
- CA DHCPDISCOVER message is sent with the IP address of the default gateway as the destination address.
- DA DHCPDISCOVER message is sent with the IP address of the DHCP server as the destination address.
62A high school in New York (school A) is using videoconferencing technology to establish student interactions with another high school (school B) in Russia. The videoconferencing is conducted between two end devices through the Internet. The network administrator of school A configures the end device with the IP address 209.165.201.10. The administrator sends a request for the IP address for the end device in school B and the response is 192.168.25.10. Neither school is using a VPN. The administrator knows immediately that this IP will not work. Why?
- AThis is a link-local address.
- BThis is a loopback address.
- CThere is an IP address conflict.
- DThis is a private IP address.
63What is a socket?
- Athe combination of the source and destination sequence numbers and port numbers
- Bthe combination of a source IP address and port number or a destination IP address and port number
- Cthe combination of the source and destination sequence and acknowledgment numbers
- Dthe combination of the source and destination IP address and source and destination Ethernet address
64What part of the URL, http://www.cisco.com/index.html, represents the top-level DNS domain?
- Awww
- Bhttp
- Cindex
- Dcom
65Refer to the exhibit. A cybersecurity analyst is viewing captured ICMP echo request packets sent from host A to host B on switch S2. What is the source MAC address of Ethernet frames carrying the ICMP echo request packets?
- A08-CB-8A-5C-D5-BA
- B00-D0-D3-BE-79-26
- C00-60-0F-B1-D1-11
- D01-90-C0-E4-55-BB
66Refer to the exhibit. A cybersecurity analyst is viewing captured packets forwarded on switch S1. Which device has the MAC address 50:6a:03:96:71:22?
- APC-A
- Brouter DG
- CDSN server
- Drouter ISP
- Eweb server
67Which term is used to describe the process of placing one message format inside another message format?
- Aencoding
- Bmultiplexing
- Cencapsulation
- Dsegmentation
68Which PDU format is used when bits are received from the network medium by the NIC of a host?
- Aframe
- Bfile
- Cpacket
- Dsegment
69What are two features of ARP? (Choose two.)
- AAn ARP request is sent to all devices on the Ethernet LAN and contains the IP address of the destination host and its multicast MAC address.
- BIf no device responds to the ARP request, then the originating node will broadcast the data packet to all devices on the network segment.
- CWhen a host is encapsulating a packet into a frame, it refers to the MAC address table to determine the mapping of IP addresses to MAC addresses.
- DIf a host is ready to send a packet to a local destination device and it has the IP address but not the MAC address of the destination, it generates an ARP broadcast.
- EIf a device receiving an ARP request has the destination IPv4 address, it responds with an ARP reply.
70In NAT translation for internal hosts, what address would be used by external users to reach internal hosts?
- Aoutside global
- Boutside local
- Cinside local
- Dinside global
71Refer to the exhibit. PC1 issues an ARP request because it needs to send a packet to PC2. In this scenario, what will happen next?
- ASW1 will send an ARP reply with the PC2 MAC address.
- BPC2 will send an ARP reply with its MAC address.
- CRT1 will send an ARP reply with its Fa0/0 MAC address.
- DRT1 will send an ARP reply with the PC2 MAC address.
- ESW1 will send an ARP reply with its Fa0/1 MAC address.
72Which two characteristics are associated with UDP sessions? (Choose two.)
- AUnacknowledged data packets are retransmitted.
- BDestination devices receive traffic with minimal delay.
- CDestination devices reassemble messages and pass them to an application.
- DTransmitted data segments are tracked.
- EReceived data is unacknowledged.
73Refer to the exhibit. What is the global IPv6 address of the host in uncompressed format?
- A2001:0DB8:0000:0000:0BAF:0000:3F57:FE94
- B2001:0DB8:0000:0BAF:0000:0000:3F57:FE94
- C2001:DB80:0000:0000:BAF0:0000:3F57:FE94
- D2001:0DB8:0000:0000:0000:0BAF:3F57:FE94
74What is the purpose of the routing process?
- Ato provide secure Internet file transfer
- Bto convert a URL name into an IP address
- Cto forward traffic on the basis of MAC addresses
- Dto encapsulate data that is used to communicate across a network
- Eto select the paths that are used to direct traffic to destination networks
75Which application layer protocol uses message types such as GET, PUT, and POST?
- ASMTP
- BPOP3
- CDHCP
- DHTTP
- EDNS
76Which transport layer feature is used to guarantee session establishment?
- AUDP sequence number
- BTCP 3-way handshake
- CTCP port number
- DUDP ACK flag
77What is the prefix length notation for the subnet mask 255.255.255.224?
- A/26
- B/27
- C/28
- D/25
78What are two potential network problems that can result from ARP operation? (Choose two.)
- AMultiple ARP replies result in the switch MAC address table containing entries that match the MAC addresses of hosts that are connected to the relevant switch port.
- BNetwork attackers could manipulate MAC address and IP address mappings in ARP messages with the intent of intercepting network traffic.
- COn large networks with low bandwidth, multiple ARP broadcasts could cause data communication delays.
- DManually configuring static ARP associations could facilitate ARP poisoning or MAC address spoofing.
- ELarge numbers of ARP request broadcasts could cause the host MAC address table to overflow and prevent the host from communicating on the network.
79Which TCP mechanism is used to identify missing segments?
- Asequence numbers
- BFCS
- Cacknowledgments
- Dwindow size
80What is the purpose of ICMP messages?
- Ato provide feedback of IP packet transmissions
- Bto monitor the process of a domain name to IP address resolution
- Cto inform routers about network topology changes
- Dto ensure the delivery of an IP packet
81What happens if part of an FTP message is not delivered to the destination?
- AThe message is lost because FTP does not use a reliable delivery method.
- BThe part of the FTP message that was lost is re-sent.
- CThe FTP source host sends a query to the destination host.
- DThe entire FTP message is re-sent.
82What is the primary purpose of NAT?
- Aconserve IPv4 addresses
- Ballow peer-to-peer file sharing
- Cenhance network performance
- Dincrease network security
83Why does a Layer 3 device perform the ANDing process on a destination IP address and subnet mask?
- Ato identify the network address of the destination network
- Bto identify the host address of the destination host
- Cto identify the broadcast address of the destination network
- Dto identify faulty frames
84Refer to the exhibit. Using the network in the exhibit, what would be the default gateway address for host A in the 192.133.219.0 network?
- A192.135.250.1
- B192.133.219.0
- C192.133.219.1
- D192.31.7.1
85Which three IP addresses are private ? (Choose three.)
- A192.167.10.10
- B10.1.1.1
- C192.168.5.5
- D172.16.4.4
- E172.32.5.2
- F224.6.6.6
86What are two types of addresses found on network end devices? (Choose two.)
- AUDP
- Breturn
- CIP
- DTCP
- EMAC
87Which OSI layer header is rewritten with new addressing information by a router when forwarding between LAN segments?
- ALayer 2
- BLayer 3
- CLayer 4
- DLayer 7
88Which protocol provides authentication, integrity, and confidentiality services and is a type of VPN?
- AMD5
- BAES
- CESP
- DIPsec
89What are two uses of an access control list? (Choose two.)
- AACLs can control which areas a host can access on a network.
- BACLs provide a basic level of security for network access.
- CStandard ACLs can restrict access to specific applications and ports.
- DACLs can permit or deny traffic based upon the MAC address originating on the router.
- EACLs assist the router in determining the best path to a destination.
90Which protocol or service is used to automatically synchronize the software clocks on Cisco routers?
- ASNMP
- BNTP
- CDHCP
- DDNS
91Which wireless parameter is used by an access point to broadcast frames that include the SSID?
- Apassive mode
- Bsecurity mode
- Cchannel setting
- Dactive mode
92A Cisco router is running IOS 15. What are the two routing table entry types that will be added when a network administrator brings an interface up and assigns an IP address to the interface? (Choose two.)
- Aroute that is learned via OSPF
- Broute that is learned via EIGRP
- Croute that is manually entered by a network administrator
- Ddirectly connected interface
- Elocal route interface
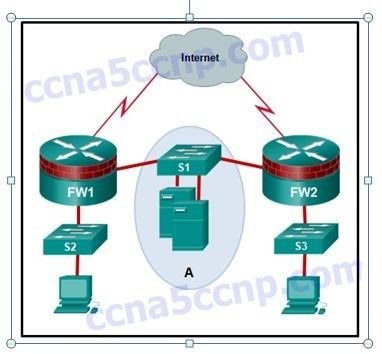
93Refer to the exhibit. The network "A" contains multiple corporate servers that are accessed by hosts from the Internet for information about the corporation. What term is used to describe the network marked as "A"?
- Aperimeter security boundary
- Binternal network
- CDMZ
- Duntrusted network
94What is the role of an IPS?
- Ato detect patterns of malicious traffic by the use of signature files
- Bto filter traffic based on defined rules and connection context
- Cto filter traffic based on Layer 7 information
- Dto enforce access control policies based on packet content
95Which two features are included by both TACACS+ and RADIUS protocols? (Choose two.)
- ASIP support
- Bpassword encryption
- C802.1X support
- Dseparate authentication and authorization processes
- Eutilization of transport layer protocols
96What does the TACACS+ protocol provide in a AAA deployment?
- AAAA connectivity via UDP
- Bcompatibility with previous TACACS protocols
- Cauthorization on a per-user or per-group basis
- Dpassword encryption without encrypting the packet
97Which parameter is commonly used to identify a wireless network name when a home wireless AP is being configured?
- AESS
- BSSID
- Cad hoc
- DBESS
98What information within a data packet does a router use to make forwarding decisions?
- Athe destination service requested
- Bthe destination IP address
- Cthe destination host name
- Dthe destination MAC address
99Which protocol creates a virtual point-to-point connection to tunnel unencrypted traffic between Cisco routers from a variety of protocols?
- AGRE
- BIPsec
- COSPF
- DIKE
100Which two statements are true about NTP servers in an enterprise network? (Choose two.)
- ANTP servers at stratum 1 are directly connected to an authoritative time source.
- BNTP servers ensure an accurate time stamp on logging and debugging information.
- CThere can only be one NTP server on an enterprise network.
- DAll NTP servers synchronize directly to a stratum 1 time source.
- ENTP servers control the mean time between failures (MTBF) for key network devices.
101What is true concerning physical and logical topologies?
- APhysical topologies display the IP addressing scheme of each network.
- BLogical topologies refer to how a network transfers data between devices.
- CThe logical topology is always the same as the physical topology.
- DPhysical topologies are concerned with how a network transfers frames.
102Which layer of the hierarchical design model is a control boundary between the other layers?
- Aaccess
- Bnetwork
- Cdistribution
- Dcore
103Which protocol or service allows network administrators to receive system messages that are provided by network devices?
- ANTP
- BNetFlow
- CSNMP
- Dsyslog
104What is a function of a proxy firewall?
- Auses signatures to detect patterns in network traffic
- Bdrops or forwards traffic based on packet header information
- Cconnects to remote servers on behalf of clients
- Dfilters IP traffic between bridged interfaces
105What is the function of the distribution layer of the three-layer network design model?
- Aaggregating access layer connections
- Bproviding high speed connection to the network edge
- Cproviding secure access to the Internet
- Dproviding direct access to the network
106Which LAN topology requires a central intermediate device to connect end devices?
- Astar
- Bring
- Cbus
- Dmesh
107Which device can control and manage a large number of corporate APs?
- Aswitch
- BWLC
- Crouter
- DLWAP
108For which discovery mode will an AP generate the most traffic on a WLAN?
- Aactive mode
- Bmixed mode
- Cpassive mode
- Dopen mode
109What is a feature of the TACACS+ protocol?
- AIt utilizes UDP to provide more efficient packet transfer.
- BIt hides passwords during transmission using PAP and sends the rest of the packet in plaintext.
- CIt encrypts the entire body of the packet for more secure communications.
- DIt combines authentication and authorization as one process.
110What is the only attribute used by standard access control lists to identify traffic?
- Asource MAC address
- Bprotocol type
- Csource IP address
- Dsource TCP port
111What type of malware has the primary objective of spreading across the network?
- Avirus
- Bworm
- CTrojan horse
- Dbotnet
112Why would a rootkit be used by a hacker?
- Ato gain access to a device without being detected
- Bto do reconnaissance
- Cto reverse engineer binary files
- Dto try to guess a password
113Which type of hacker is motivated to protest against political and social issues?
- Acybercriminal
- Bscript kiddie
- Cvulnerability broker
- Dhacktivist
114What is a characteristic of a Trojan horse as it relates to network security?
- AExtreme quantities of data are sent to a particular network device interface.
- BAn electronic dictionary is used to obtain a password to be used to infiltrate a key network device.
- CToo much information is destined for a particular memory block, causing additional memory areas to be affected.
- DMalware is contained in a seemingly legitimate executable program.
115What is a botnet?
- Aa group of web servers that provide load balancing and fault tolerance
- Ban online video game intended for multiple players
- Ca network that allows users to bring their own technology
- Da network of infected computers that are controlled as a group
116Which type of Trojan horse security breach uses the computer of the victim as the source device to launch other attacks?
- ADoS
- BFTP
- Cdata-sending
- Dproxy
117What is the primary goal of a DoS attack?
- Ato prevent the target server from being able to handle additional requests
- Bto scan the data on the target server
- Cto facilitate access to external networks
- Dto obtain all addresses in the address book within the server
118What is a main purpose of launching an access attack on network systems?
- Ato prevent other users from accessing the system
- Bto scan for accessible networks
- Cto gather information about the network
- Dto retrieve data
119What causes a buffer overflow?
- Alaunching a security countermeasure to mitigate a Trojan horse
- Battempting to write more data to a memory location than that location can hold
- Csending repeated connections such as Telnet to a particular device, thus denying other data sources
- Dsending too much information to two or more interfaces of the same device, thereby causing dropped packets
- Edownloading and installing too many software updates at one time
120A company pays a significant sum of money to hackers in order to regain control of an email and data server. Which type of security attack was used by the hackers?
- ADoS
- Bspyware
- CTrojan horse
- Dransomware
121What is the term used to describe an email that is targeting a specific person employed at a financial institution?
- Aspam
- Bspyware
- Cvishing
- Dtarget phishing
- Espear phishing
122Which access attack method involves a software program that attempts to discover a system password by the use of an electronic dictionary?
- Apacket sniffer attack
- Bdenial of service attack
- Cbuffer overflow attack
- Dbrute-force attack
- Eport redirection attack
- FIP spoofing attack
123In what way are zombies used in security attacks?
- AThey are infected machines that carry out a DDoS attack.
- BThey are maliciously formed code segments used to replace legitimate applications.
- CThey target specific individuals to gain corporate or personal information.
- DThey probe a group of machines for open ports to learn which services are running
124What are two evasion methods used by hackers? (Choose two.)
- Ascanning
- Bencryption
- Caccess attack
- Dphishing
- Eresource exhaustion
125What are two purposes of launching a reconnaissance attack on a network? (Choose two.)
- Ato retrieve and modify data
- Bto scan for accessibility
- Cto escalate access privileges
- Dto prevent other users from accessing the system
- Eto gather information about the network and devices
126What are three techniques used in social engineering attacks? (Choose three.)
- Avishing
- Bphishing
- Cpretexting
- Dbuffer overflow
- Eman-in-the-middle
- Fsending junk email
127An attacker is using a laptop as a rogue access point to capture all network traffic from a targeted user. Which type of attack is this?
- Aport redirection
- Btrust exploitation
- Cbuffer overflow
- Dman in the middle
128A user is curious about how someone might know a computer has been infected with malware. What are two common malware behaviors? (Choose two.)
- AThe computer emits a hissing sound every time the pencil sharpener is used.
- BThe computer freezes and requires reboots.
- CNo sound emits when an audio CD is played.
- DThe computer gets increasingly slower to respond.
- EThe computer beeps once during the boot process.
129Which type of security attack would attempt a buffer overflow?
- Aransomware
- Breconnaissance
- CDoS
- Dscareware
130What is a significant characteristic of virus malware?
- AVirus malware is only distributed over the Internet.
- BOnce installed on a host system, a virus will automatically propagate itself to other systems.
- CA virus is triggered by an event on the host system.
- DA virus can execute independently of the host system
131A senior citizen receives a warning on the computer that states that the operating system registry is corrupt and to click a particular link to repair it. Which type of malware is being used to try to create the perception of a computer threat to the user?
- ADoS
- Bscareware
- Cphishing
- Dadware
132What is the motivation of a white hat attacker?
- Afine tuning network devices to improve their performance and efficiency
- Btaking advantage of any vulnerability for illegal personal gain
- Cstudying operating systems of various platforms to develop a new system
- Ddiscovering weaknesses of networks and systems to improve the security level of these systems
133What is a ping sweep?
- Aa network scanning technique that indicates the live hosts in a range of IP addresses.
- Ba query and response protocol that identifies information about a domain, including the addresses that are assigned to that domain.
- Ca software application that enables the capture of all network packets that are sent across a LAN.
- Da scanning technique that examines a range of TCP or UDP port numbers on a host to detect listening services
134What is the term used when a malicious party sends a fraudulent email disguised as being from a legitimate, trusted source?
- ATrojan
- Bvishing
- Cphishing
- Dbackdoor
135What are the three major components of a worm attack? (Choose three.)
- Aan enabling vulnerability
- Ba propagation mechanism
- Ca payload
- Da probing mechanism
- Ea penetration mechanism
- Fan infecting vulnerability
136Which security threat installs on a computer without the knowledge of the user and then monitors computer activity?
- Aspyware
- Bviruses
- Cworms
- Dadware
137What are two monitoring tools that capture network traffic and forward it to network monitoring devices? (Choose two.)
- ASPAN
- Bnetwork tap
- CSNMP
- DSIEM
- EWireshark
138Which technology is an open source SIEM system?
- AWireshark
- BStealWatch
- CSplunk
- DELK
139What network attack seeks to create a DoS for clients by preventing them from being able to obtain a DHCP lease?
- AIP address spoofing
- BDHCP starvation
- CCAM table attack
- DDHCP spoofing
140Which protocol would be the target of a cushioning attack?
- ADHCP
- BHTTP
- CARP
- DDNS
141Which network monitoring capability is provided by using SPAN?
- ANetwork analysts are able to access network device log files and to monitor network behavior.
- BStatistics on packets flowing through Cisco routers and multilayer switches can be captured.
- CTraffic exiting and entering a switch is copied to a network monitoring device.
- DReal-time reporting and long-term analysis of security events are enabled.
142Which type of DNS attack involves the cybercriminal compromising a parent domain and creating multiple subdomains to be used during the attacks?
- Ashadowing
- Bamplification and reflection
- Ctunneling
- Dcache poisoning
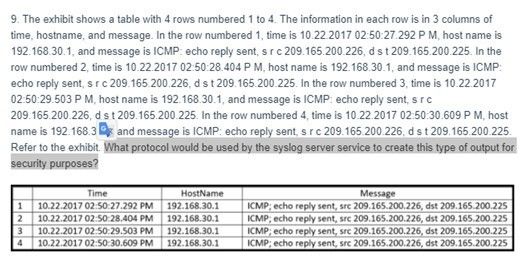
143Refer to the exhibit. What protocol would be used by the syslog server service to create this type of output for security purposes?
- ANTP
- BAAA
- CICMP
- DSNMP
144What is the result of a passive ARP poisoning attack?
- AConfidential information is stolen.
- BNetwork clients experience a denial of service.
- CData is modified in transit or malicious data is inserted in transit.
- DMultiple subdomains are created.
145Which term is used for bulk advertising emails flooded to as many end users as possible?
- Aspam
- Badware
- Cbrute force
- Dphishing
146Which capability is provided by the aggregation function in SIEM?
- Areducing the volume of event data by consolidating duplicate event records
- Bsearching logs and event records of multiple sources for more complete forensic analysis
- Cpresenting correlated and aggregated event data in real-time monitoring
- Dincreasing speed of detection and reaction to security threats by examining logs from many systems and applications
147Which protocol is attacked when a cybercriminal provides an invalid gateway in order to create a man-in-the-middle attack?
- AHTTP or HTTPS
- BICMP
- CDNS
- DDHCP
148Which network monitoring tool can provide a complete audit trail of basic information of all IP flows on a Cisco router and forward the data to a device?
- ASPAN
- BWireshark
- CNetFlow
- DSIEM
149What are two methods used by cybercriminals to mask DNS attacks? (Choose two.)
- Adomain generation algorithms
- Bshadowing
- Cfast flux
- Dreflection
- Etunneling
150Which protocol is exploited by cybercriminals who create malicious iFrames?
- AHTTP
- BARP
- CDNS
- DDHCP
151Which SIEM function is associated with speeding up detection of security threats by examining logs and events from different systems?
- Aforensic analysis
- Bretention
- Ccorrelation
- Daggregation
152In which TCP attack is the cybercriminal attempting to overwhelm a target host with half-open TCP connections?
- Areset attack
- Bsession hijacking attack
- Cport scan attack
- DSYN flood attack
153In which type of attack is falsified information used to redirect users to malicious Internet sites?
- AARP cache poisoning
- BDNS amplification and reflection
- CDNS cache poisoning
- Ddomain generation
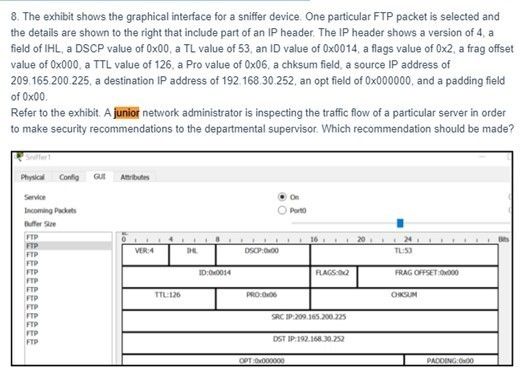
154Refer to the exhibit. A junior network administrator is inspecting the traffic flow of a particular server in order to make security recommendations to the departmental supervisor. Which recommendation should be made?
- AA more secure protocol should be used.
- BThe total length (TL) field indicates an unsecure Layer 4 protocol is being used.
- CThe person accessing the server should never access it from a device using a private IP address.
- DThe person accessing the server should use the private IP address of the server.
155Which network monitoring tool saves captured packets in a PCAP file?
- AWireshark
- BSIEM
- CSNMP
- DNetFlow
156Which cyber attack involves a coordinated attack from a botnet of zombie computers?
- AICMP redirect
- BMITM
- CDDoS
- Daddress spoofing
157How is optional network layer information carried by IPv6 packets?
- Ainside an options field that is part of the IPv6 packet header
- Binside the Flow Label field
- Cinside the payload carried by the IPv6 packet
- Dinside an extension header attached to the main IPv6 packet header
158What type of attack targets an SQL database using the input field of a user?
- ACross-site scripting
- BSQL injection
- Cbuffer overflow
- DXML injection
159What network monitoring technology enables a switch to copy and forward traffic sent and received on multiple interfaces out another interface toward a network analysis device?
- Aport mirroring
- BNetFlow
- CSNMP
- Dnetwork tap
160A web server administrator is configuring access settings to require users to authenticate first before accessing certain web pages. Which requirement of information security is addressed through the configuration?
- Aavailability
- Bconfidentiality
- Cintegrity
- Dscalability
161What component of a security policy explicitly defines the type of traffic allowed on a network and what users are allowed and not allowed to do?
- Apassword policies
- Bidentification and authentication policies
- Cremote access policies
- Dacceptable use policies
162What is the principle of least privilege access control model?
- AUser access to data is based on object attributes.
- BUsers are granted rights on an as-needed approach.
- CUsers are granted the strictest access control possible to data.
- DUsers control access to data they own.
163Which statement describes a difference between RADIUS and TACACS+?
- ARADIUS is supported by the Cisco Secure ACS software whereas TACACS+ is not.
- BRADIUS encrypts only the password whereas TACACS+ encrypts all communication.
- CRADIUS separates authentication and authorization whereas TACACS+ combines them as one process.
- DRADIUS uses TCP whereas TACACS+ uses UDP.
164What is the purpose of mobile device management (MDM) software?
- AIt is used to create a security policy.
- BIt is used to implement security policies, setting, and software configurations on mobile devices.
- CIt is used by threat actors to penetrate the system.
- DIt is used to identify potential mobile device vulnerabilities.
165What service determines which resources a user can access along with the operations that a user can perform?
- Aauthentication
- Bbiometric
- Cauthorization
- Daccounting
- Etoken
166A company has a file server that shares a folder named Public. The network security policy specifies that the Public folder is assigned Read-Only rights to anyone who can log into the server while the Edit rights are assigned only to the network admin group. Which component is addressed in the AAA network service framework?
- Aautomation
- Baccounting
- Cauthentication
- Dauthorization
167In threat intelligence communications, what set of specifications is for exchanging cyberthreat information between organizations?
- ATrusted automated exchange of indicator information (TAXII)
- BStructured threat information expression (STIX)
- CAutomated indicator sharing (AIS)
- DCommon vulnerabilities and exposures (CVE)
168What three items are components of the CIA triad? (Choose three.)
- Aintegrity
- Bavailability
- Cconfidentiality
- Daccess
- Escalability
- Fintervention
169A company is experiencing overwhelming visits to a main web server. The IT department is developing a plan to add a couple more web servers for load balancing and redundancy. Which requirement of information security is addressed by implementing the plan?
- Aintegrity
- Bscalability
- Cavailability
- Dconfidentiality
170Which AAA component can be established using token cards?
- Aauthorization
- Bauthentication
- Cauditing
- Daccounting
171Which method is used to make data unreadable to unauthorized users?
- AEncrypt the data.
- BFragment the data.
- CAdd a checksum to the end of the data.
- DAssign it a username and password.
172Which two areas must an IT security person understand in order to identify vulnerabilities on a network? (Choose two.)
- Anumber of systems on each network
- Bnetwork baseline data
- Cdata analysis trends
- Dhardware used by applications
- Eimportant applications used
173Which three services are provided by the AAA framework? (Choose three.)
- Aautoconfiguration
- Bautomation
- Cauthorization
- Dauthentication
- Eautobalancing
- Faccounting
174How does BYOD change the way in which businesses implement networks?
- ABYOD provides flexibility in where and how users can access network resources.
- BBYOD requires organizations to purchase laptops rather than desktops.
- CBYOD users are responsible for their own network security, thus reducing the need for organizational security policies.
- DBYOD devices are more expensive than devices that are purchased by an organization.
175Which technology provides the framework to enable scalable access security?
- AAutoSecure
- Brole-based CLI access
- Cauthentication, authorization, and accounting
- DSimple Network Management Protocol
- ECisco Configuration Professional communities
176Which device is usually the first line of defense in a layered defense-in-depth approach?
- Aaccess layer switch
- Binternal router
- Cedge router
- Dfirewall
177In a defense-in-depth approach, which three options must be identified to effectively defend a network against attacks? (Choose three.)
- Aassets that need protection
- Blocation of attacker or attackers
- Ctotal number of devices that attach to the wired and wireless network
- Dthreats to assets
- Evulnerabilities in the system
- Fpast security breaches
178Which section of a security policy is used to specify that only authorized individuals should have access to enterprise data?
- Astatement of authority
- Bstatement of scope
- Ccampus access policy
- DInternet access policy
- Eidentification and authentication policy
- Facceptable use policy
179Which type of access control applies the strictest access control and is commonly used in military or mission critical applications?
- Amandatory access control (MAC)
- Bdiscretionary access control (DAC)
- Cattribute-based access control (ABAC)
- DNon-discretionary access control
180Which algorithm is used to automatically generate a shared secret for two systems to use in establishing an IPsec VPN?
- ASSL
- BDES
- CAH
- DDH
- EESP
- F3DES
181A security specialist is tasked to ensure that files transmitted between the headquarters office and the branch office are not altered during transmission. Which two algorithms can be used to achieve this task? (Choose two.)
- A3DES
- BHMAC
- CAES
- DSHA-1
- EMD5
182In which way does the use of HTTPS increase the security monitoring challenges within enterprise networks?
- AHTTPS traffic can carry a much larger data payload than HTTP can carry.
- BHTTPS traffic is much faster than HTTP traffic.
- CHTTPS traffic does not require authentication.
- DHTTPS traffic enables end-to-end encryption.
183What technology has a function of using trusted third-party protocols to issue credentials that are accepted as an authoritative identity?
- Ahashing algorithms
- Bdigital signatures
- Csymmetric keys
- DPKI certificates
184Which three algorithms are designed to generate and verify digital signatures? (Choose three.)
- AIKE
- BDSA
- CRSA
- DECDSA
- EAES
- F3DES
185What are two properties of a cryptographic hash function? (Choose two.)
- AComplex inputs will produce complex hashes.
- BHash functions can be duplicated for authentication purposes.
- CThe hash function is one way and irreversible.
- DThe input for a particular hash algorithm has to have a fixed size.
- EThe output is a fixed length.
186Which statement is a feature of HMAC?
- AHMAC uses a secret key that is only known to the sender and defeats man-in-the-middle attacks.
- BHMAC uses protocols such as SSL or TLS to provide session layer confidentiality.
- CHMAC uses a secret key as input to the hash function, adding authentication to integrity assurance.
- DHMAC is based on the RSA hash function.
187Which two statements describe the characteristics of symmetric algorithms? (Choose two.)
- AThey are commonly used with VPN traffic.
- BThey use a pair of a public key and a private key.
- CThey are commonly implemented in the SSL and SSH protocols.
- DThey provide confidentiality, integrity, and availability.
- EThey are referred to as a pre-shared key or secret key.
188Which encryption algorithm is an asymmetric algorithm?
- AAES
- BSEAL
- CDH
- D3DES
189Which statement describes the use of certificate classes in the PKI?
- AEmail security is provided by the vendor, not by a certificate.
- BA vendor must issue only one class of certificates when acting as a CA.
- CA class 5 certificate is more trustworthy than a class 4 certificate.
- DThe lower the class number, the more trusted the certificate.
190What is the focus of cryptanalysis?
- Adeveloping secret codes
- Bbreaking encrypted codes
- Cimplementing encrypted codes
- Dhiding secret codes
191Two users must authenticate each other using digital certificates and a CA. Which option describes the CA authentication procedure?
- AThe users must obtain the certificate of the CA and then their own certificate.
- BThe CA is always required, even after user verification is complete.
- CCA certificates are retrieved out-of-band using the PSTN, and the authentication is done in-band over a network.
- DAfter user verification is complete, the CA is no longer required, even if one of the involved certificates expires.
192When implementing keys for authentication, if an old key length with 4 bits is increased to 8 bits, which statement describes the new key space?
- AThe key space is increased by 3 times.
- BThe key space is increased by 8 times.
- CThe key space is increased by 15 times.
- DThe key space is increased by 16 times.
193What is the service framework that is needed to support large-scale public key-based technologies?
- APKI
- BRSA
- C3DES
- DHMAC
194What are the two important components of a public key infrastructure (PKI) used in network security? (Choose two.)
- Asymmetric encryption algorithms
- Bcertificate authority
- Cintrusion prevention system
- Ddigital certificates
- Epre-shared key generation
195A company is developing a security policy to ensure that OSPF routing updates are authenticated with a key. What can be used to achieve the task?
- ASHA-1
- BHMAC
- CAES
- DMD5
- E3DES
196An online retailer needs a service to support the nonrepudiation of the transaction. Which component is used for this service?
- Athe private key of the retailer
- Bthe digital signatures
- Cthe unique shared secret known only by the retailer and the customer
- Dthe public key of the retailer
197Which statement describes the Software-Optimized Encryption Algorithm (SEAL)?
- AIt uses a 112-bit encryption key.
- BIt requires more CPU resources than software-based AES does.
- CIt is an example of an asymmetric algorithm.
- DSEAL is a stream cipher.
198What role does an RA play in PKI?
- Aa super CA
- Ba subordinate CA
- Ca backup root CA
- Da root CA
199What technology allows users to verify the identity of a website and to trust code that is downloaded from the Internet?
- Aencryption
- Basymmetric key algorithm
- Cdigital signature
- Dhash algorithm
200Which three services are provided through digital signatures? (Choose three.)
- Aaccounting
- Bauthenticity
- Ccompression
- Dnonrepudiation
- Eintegrity
- Fencryption
Información
- Descripción
- Advanced (State Exam) Fundamentals of Information Security [Teachers: Abdulanova Altynay, Sagymbekova Azhar; STATE EXAM] ▼ Test sobre Fundamentals of Information Security [State Exam | Part 1], creado por Good Guy Beket el 18/03/2019.
- Autor
- Good Guy Beket
- Idioma
- English
- Visitas
- 936
- Etiquetas
- Valoración
- Aún sin valoraciones Valora este test