
Flashcards
OCR GCSE - Computer Science - Paper 1 - System Security
Cards in this deck (21)
- 1What is a Passive Attack?> Someone monitors data travelling on a network
> Intercepts any sensitive information they find
> Network-monitoring hardware and software (such as packet sniffers) are used
> Hard to detect, best defence is encryption - 2What is an Active Attack?> Someone attacks a network with malware
> Easier to detect than passive attacks
> Firewall can be used as a defence - 3What is an Insider Attack?Someone within an organisation exploits their network access rights to steal information
- 4What is a Brute Force Attack?> Type of active attack
> Gain information by cracking passwords through trial and error
> Automated software to produce hundreds, or thousands, of likely password combinations
> Sometimes using real words with predictable numbers (e.g. jelly321)
> Simple measures like locking accounts after a certain number of failed attempts and using strong passwords reduces the risk of these attacks - 5What is a (D)DoS Attack?> (Distributed) Denial-of-Service attack
> Hacker tries to stop users from accessing a network / website
> Floods the network with useless traffic
> Makes the network extremely slow or inaccessible
> Distributed: malware is used on unsuspecting computers which creates network traffic on many computers that are not owned by the hacker - 6What is Malware?> Malicious software
> Designed to cause harm or damage to a computer
> Usually to ask for money or monitor user actions to be sold - 7What are some Examples of Actions of Malware?> Deleting / Modifying files
> Scareware - telling the user their computer is infected with loads of viruses (it's not) to scare them into clicking on fake links / paying for problems to be fixed
> Ransomware - encrypts all files on the computer with a message demanding a large sum of money to be paid to receive the files back or they get deleted
> Spyware - secretly monitors user actions (e.g. key presses for passwords), and sends the info to hackers
> Rootkits - altering permissions giving other malware and hackers administrator-privileges
> Opening backdoors - holes in security to be used for future attacks - 8What are Viruses?> Malware that attach themselves to certain files (usually executables and scripts)
> Users spread them by copying infected files
> Users activate them by opening the files, which runs malicious code - 9What are Worms?> Malware that are like viruses but self-replicate without the user copying files
> Spread very quickly
> Exploit weaknesses in network security - 10What are Trojan Horses?> Malware disguised as legitimate software
> Do not replicate themselves
> Users install them, without realising they have a hidden purpose
> Often a fake game / piece of software - 11What is Social Engineering?Gaining sensitive information or illegal access to networks by influencing people, either by pretending you are a respectable company (usually microsoft idk why?), or threatening to hack / delete data
- 12What is Phishing?> Criminals send emails or texts claiming to be from a well-known business
> Often (but not always) containing a spoof version of the company's website
> Request that the user update their personal information (e.g. password and bank details)
> Instead of updating anything, the fake website sells the data to criminals, who can access their genuine account - 13What can Indicate Phishing Emails?> From a normal mail domain (e.g. @gmail.com)
> Por grammerr nd spelilgn mistaykez
> Pixelated or old logos
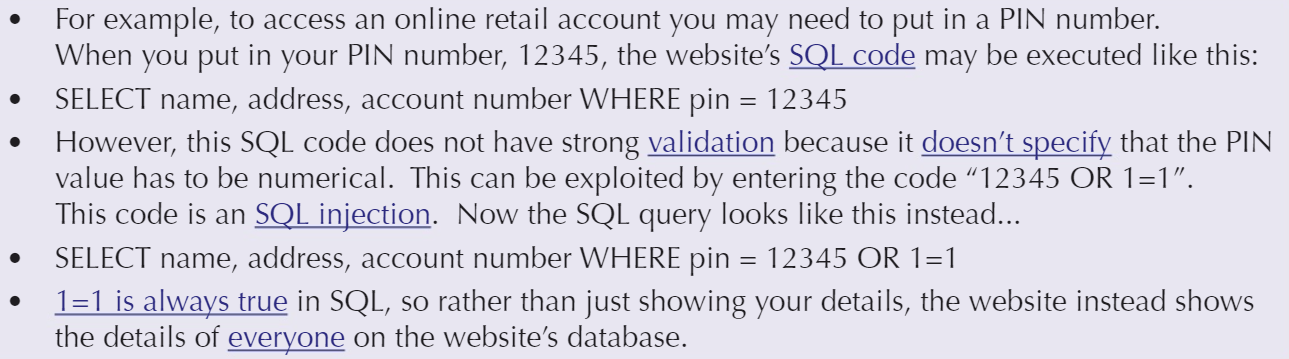
> The fake website's URL is incorrect (e.g. if it's from microsoft, the URL is NOT microsoft.com, but something like microsoft-tech-support-help.com) - 14What is SQL Injection?> SQL - Structured Query Language, used for databases
> Typed into a website's input box, but runs unintentional code
> Easy way to get past a firewall - 15What is a Network Policy?Set of rules and procedures that an organisation follows to ensure the network is protected against attacks
- 16What would a Good Network Policy Contain?> Regular tests for security weaknesses
> Require strong passwords
> Enforce user-access levels (limits people who can access sensitive information)
> Anti-malware and firewall software
> Encryption of sensitive data - 17What is Penetration Testing?> Organisations employ specialists to simulate potential attacks on networks
> Used to identify possible weaknesses in network security
> Results are reported back with no harm done to the actual network - 18What is Network Forensics?> Investigations undertaken to find the cause of (already undergoing) attacks on a network
> Organisation captures data packets as they enter the network
> Packets are analysed to discover how the network was attacked
> Used to prevent future attacks - 19What are the Characteristics of a Strong Password?> Long
> Combination of letters, numbers, and symbols
> Changed regularly
> Less / No dictionary words
> An extremely strong password would be literal nonsense: a#qWy9m@9*$v - 20What are User-Access Levels?> Control which part of the network groups of users can access
> E.g. business managers have a higher access level to access more sensitive data, like pay information, whereas employees would not have access
> Helps prevent insider attacks and reduces the number of accounts which can be brute-forced - 21What is Anti-Malware?> Software designed to find and stop malware from damaging a network
> Includes anti-virus programs and firewalls
> Firewalls block unauthorised access by examining all data entering and exiting the network, blocking potential threats
Information
- Description
- GCSE Computing Flashcards on OCR GCSE - Computer Science - Paper 1 - System Security, created by Malachy Moran-Tun on 12/04/2021.
- Created by
- Malachy Moran-Tun
- Views
- 22
- Rating