
Quiz
NS4
Crie uma conta grátis para terminar este quiz
Salve seu progresso e veja sua nota final.
Já tem uma conta? Inicie sessão
Perguntas do quiz (50)
1Which configuration objects can be selected for the Source field of a firewall policy? (Choose
two.)- AFirewall service
- BUser or user group
- CIP Pool
- DFQDN address
2If the Services field is configured in a Virtual IP (VIP), which statement is true when central NAT
is used?- AThe Services field prevents SNAT and DNAT from being combined in the same policy.
- BThe Services field is used when you need to bundle several VIPs into VIP groups.
- CThe Services field removes the requirement to create multiple VIPs for different services.
- DThe Services field prevents multiple sources of traffic from using multiple services to connect to a
single computer.
3Which of the following statements about central NAT are true? (Choose two.)
- AIP tool references must be removed from existing firewall policies before enabling central NAT.
- BCentral NAT can be enabled or disabled from the CLI only.
- CSource NAT, using central NAT, requires at least one central SNAT policy.
- DDestination NAT, using central NAT, requires a VIP object as the destination address in a firewall.
4Examine the exhibit, which shows the partial output of an IKE real-time debug.
Which of the following statement about the output is true?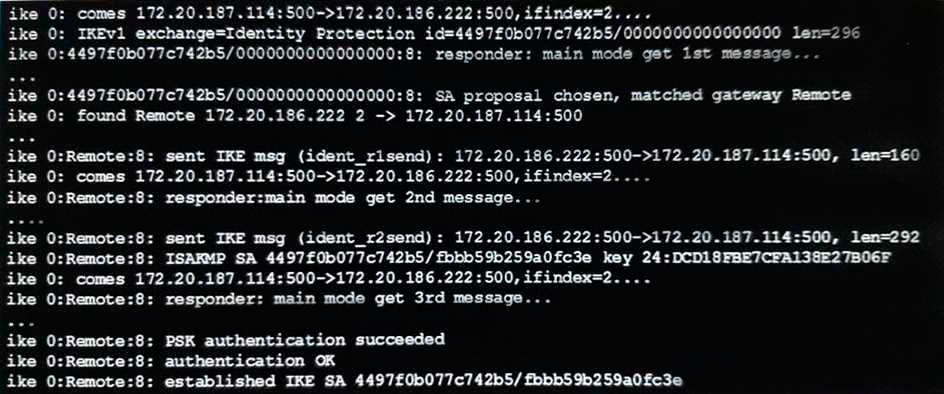
- AThe VPN is configured to use pre-shared key authentication.
- BExtended authentication (XAuth) was successful.
- CRemote is the host name of the remote IPsec peer.
- DPhase 1 went down.
5An administrator is configuring an antivirus profiles on FortiGate and notices that Proxy
Options is not listed under Security Profiles on the GUI. What can cause this issue?- AFortiGate needs to be switched to NGFW mode.
- BProxy options section is hidden by default and needs to be enabled from the Feature Visibility
menu. - CProxy options are no longer available starting in FortiOS 5.6.
- DFortiGate is in flow-based inspection mode.
6Which of the following services can be inspected by the DLP profile? (Choose three.)
- ANFS
- BFTP
- CIMAP
- DCIFS
- EHTTP-POST
7Examine the following web filtering log. Which statement about the log message is true?

- AThe action for the category Games is set to block.
- BThe usage quota for the IP address 10.0.1.10 has expired
- CThe name of the applied web filter profile is default.
- DThe web site miniclip.com matches a static URL filter whose action is set to Warning.
8Which of the following static routes are not maintained in the routing table?
- ANamed Address routes
- BDynamic routes
- CISDB routes
- DPolicy routes
9An administrator is attempting to allow access to https://fortinet.com through a firewall policy
that is configured with a web filter and an SSL inspection profile configured for deep inspection.
Which of the following are possible actions to eliminate the certificate error generated by deep
inspection? (Choose two.)- AImplement firewall authentication for all users that need access to fortinet.com.
- BManually install the FortiGate deep inspection certificate as a trusted CA.
- CConfigure fortinet.com access to bypass the IPS engine.
- DConfigure an SSL-inspection exemption for fortinet.com.
10If traffic matches a DLP filter with the action set to Quarantine IP Address, what action does
FortiGate take?- AIt notifies the administrator by sending an email.
- BIt provides a DLP block replacement page with a link to download the file.
- CIt blocks all future traffic for that IP address for a configured interval.
- DIt archives the data for that IP address.
11An administration wants to throttle the total volume of SMTP sessions to their email server.
Which of the following DoS sensors can be used to achieve this?- Atcp_port_scan
- Bip_dst_session
- Cudp_flood
- Dip_src_session
12View the certificate shown to the exhibit, and then answer the following question:
The CA issued this certificate to which entity?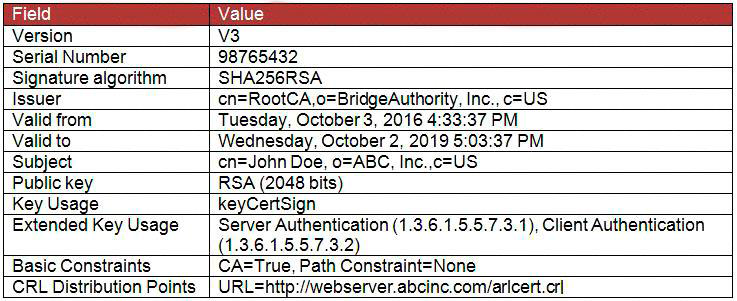
- AA root CA
- BA person
- CA bridge CA
- DA subordinate CA
13What information is flushed when the chunk-size value is changed in the config dlp settings?
- AThe database for DLP document fingerprinting
- BThe supported file types in the DLP filters
- CThe archived files and messages
- DThe file name patterns in the DLP filters
14View the exhibit.
VDOM1 is operating in transparent mode VDOM2 is operating in NAT Route mode. There is an
inteface VDOM link between both VDOMs. A client workstation with the IP address 10.0.1.10/24 is
connected to port2. A web server with the IP address 10.200.1.2/24 is connected to port1.
What is required in the FortiGate configuration to route and allow connections from the client
workstation to the web server? (Choose two.)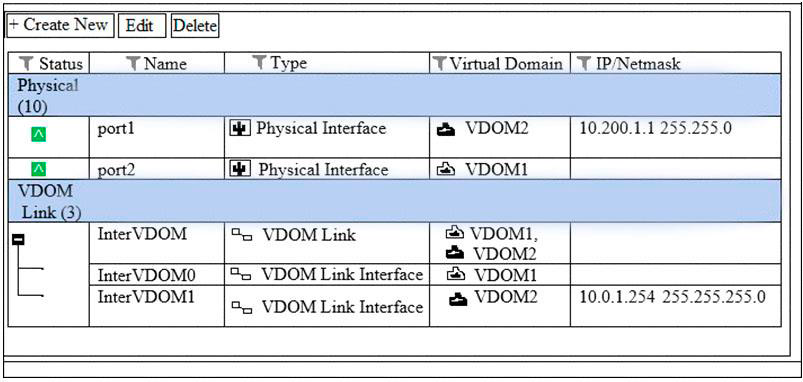
- AA static or dynamic route in VDOM2 with the subnet 10.0.1.0/24 as the destination.
- BA static or dynamic route in VDOM1 with the subnet 10.200.1.0/24 as the destination.
- COne firewall policy in VDOM1 with port2 as the source interface and InterVDOM0 as the
destination interface. - DOne firewall policy in VDOM2 with InterVDOM1 as the source interface and port1 as the
destination interface.
15Which of the following statements about backing up logs from the CLI and downloading logs from the GUI are true? (Choose two.)
- ALog downloads from the GUI are limited to the current filter view
- BLog backups from the CLI cannot be restored to another FortiGate.
- CLog backups from the CLI can be configured to upload to FTP as a scheduled time
- DLog downloads from the GUI are stored as LZ4 compressed files.
16Examine the routing database shown in the exhibit, and then answer the following question:
Which of the following statements are correct? (Choose two.)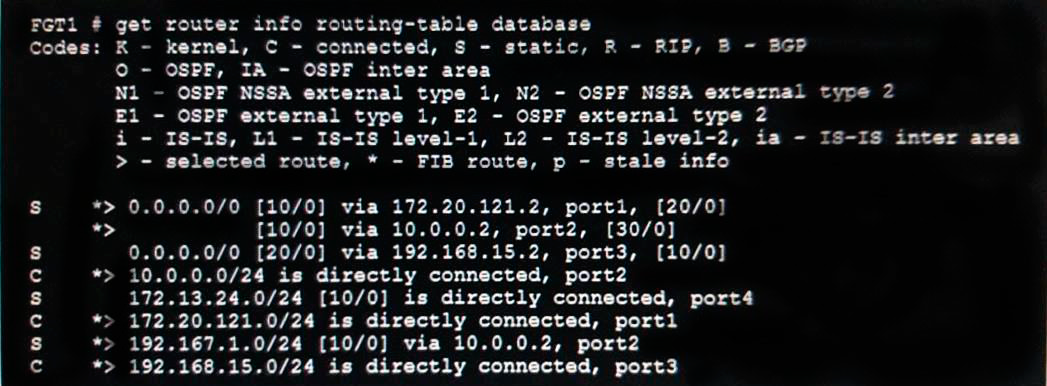
- AThe port3 default route has the highest distance.
- BThe port3 default route has the lowest metric.
- CThere will be eight routes active in the routing table.
- DThe port1 and port2 default routes are active in the routing table.
17Which downstream FortiGate VDOM is used to join the Security Fabric when split-task VDOM
is enabled on all FortiGate devices?- AFG-traffic VDOM
- BRoot VDOM
- CCustomer VDOM
- DGlobal VDOM
18Examine the exhibit, which contains a session diagnostic output.
Which of the following statements about the session diagnostic output is true?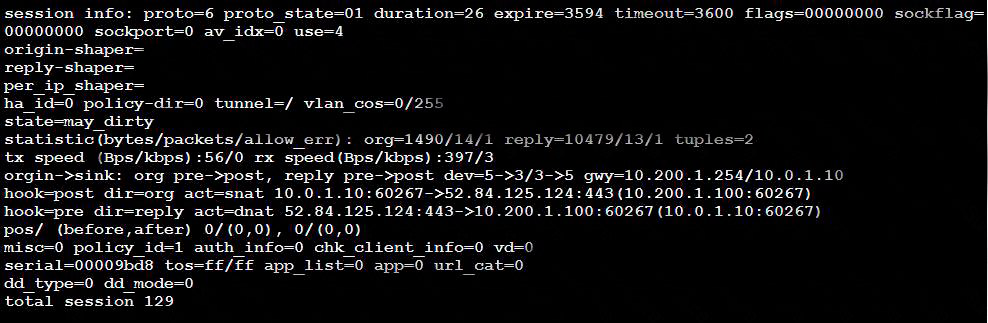
- AThe session is in ESTABLISHED state.
- BThe session is in LISTEN state.
- CThe session is in TIME_WAIT state.
- DThe session is in CLOSE_WAIT state.
19Examine the network diagram shown in the exhibit, and then answer the following question:
A firewall administrator must configure equal cost multipath (ECMP) routing on FGT1 to ensure both
port1 and port3 links are used at the same time for all traffic destined for 172.20.2.0/24. Which of
the following static routes will satisfy this requirement on FGT1? (Choose two.)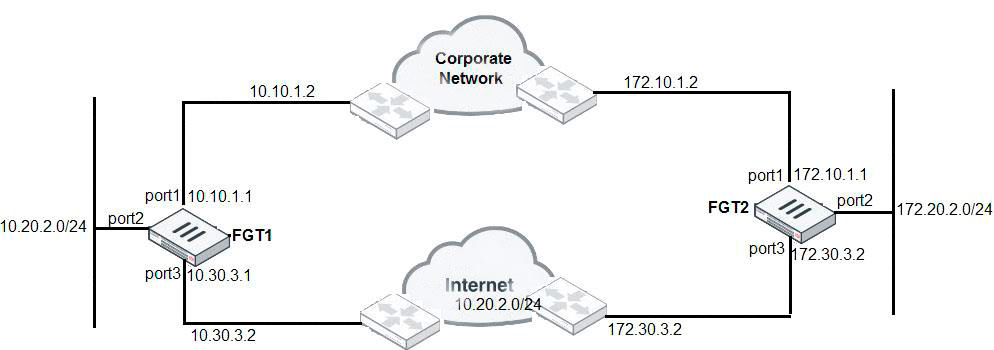
- A172.20.2.0/24 (1/0) via 10.10.1.2, port1 [0/0]
- B172.20.2.0/24 (25/0) via 10.10.3.2, port3 [5/0]
- C172.20.2.0/24 (1/150) via 10.10.1.2, port3 [10/0]
- D172.20.2.0/24 (1/150) via 10.30.3.2, port3 [10/0]
20Examine this FortiGate configuration:
config system global
ser av-failopen pass
end
Examine the output of the following debug command:
Based on the diagnostic outputs above, how is the FortiGate handling the traffic for new sessions that
require inspection?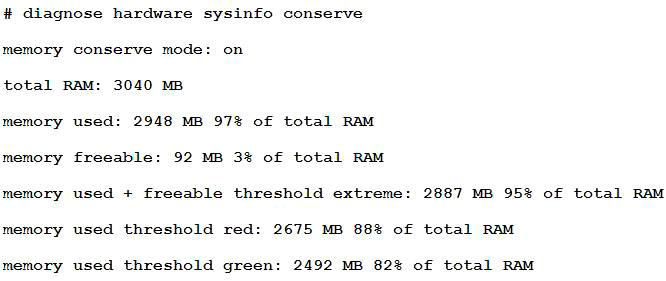
- AIt is allowed, but with no inspection
- BIt is allowed and inspected as long as the inspection is flow based
- CIt is dropped.
- DIt is allowed and inspected, as long as the only inspection required is antivirus.
21HTTP Public Key Pinning (HPKP) can be an obstacle to implementing full SSL inspection. What
solutions could resolve this problem? (Choose two.)- AEnable Allow Invalid SSL Certificates for the relevant security profile.
- BChange web browsers to one that does not support HPKP.
- CExempt those web sites that use HPKP from full SSL inspection.
- DInstall the CA certificate (that is required to verify the web server certificate) stores of users' computers.
22Examine the exhibit, which shows the output of a web filtering real time debug.
Why is the site www.bing.com being blocked?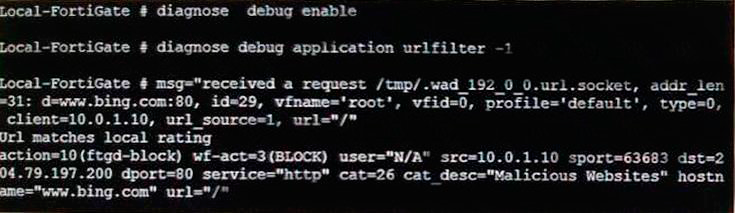
- AThe web site www.bing.com is categorized by FortiGuard as Malicious Websites.
- BThe user has not authenticated with the FortiGate yet.
- CThe web server IP address 204.79.197.200 is categorized by FortiGuard as Malicious Websites.
- DThe rating for the web site www.bing.com has been locally overridden to a category that is being
blocked.
23A FortiGate is operating in NAT mode and configured with two virtual LAN (VLAN) sub
interfaces added to the physical interface.
Which statements about the VLAN sub interfaces can have the same VLAN ID, only if they have IP
addresses in different subnets.- AThe two VLAN sub interfaces can have the same VLAN ID, only if they have IP addresses in
different subnets. - BThe two VLAN sub interfaces must have different VLAN IDs.
- CThe two VLAN sub interfaces can have the same VLAN ID, only if they belong to different VDOMs.
- DThe two VLAN sub interfaces can have the same VLAN ID, only if they have IP addresses in the
same subnet.
- AThe two VLAN sub interfaces can have the same VLAN ID, only if they have IP addresses in
24Examine the network diagram and the existing FGTI routing table shown in the exhibit, and
then answer the following question:
An administrator has added the following static route on FGTI.
DESTINATION: 172.20.1.0/244
GATEWAY: 172.11.12.1
INTERFACE: port1
ADMINISTARTIVE DISTANCE: 10
Since the change, the new static route is not showing up in the routing table. Given the information
provided, which of the following describes the cause of this problem?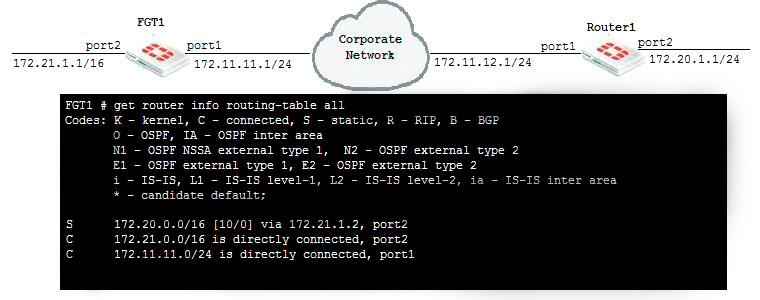
- AThe new route's destination subnet overlaps an existing route.
- BThe new route's Distance value should be higher than 10.
- CThe Gateway IP address is not in the same subnet as port1.
- DThe Priority is 0, which means that this route will remain inactive.
25Which of the following statements about NTLM authentication are correct? (Choose two.)
- AIt is useful when users log in to DCs that are not monitored by a collector agent.
- BIt takes over as the primary authentication method when configured alongside FSSO.
- CMulti-domain environments require DC agents on every domain controller.
- DNTLM-enabled web browsers are required.
26Examine the exhibit, which contains a virtual IP and firewall policy configuration.
The WAN (port1) interface has the IP address 10.200.1.1/24. The LAN (port2) interface has the IP
address
The first firewall policy has NAT enabled on the outgoing interface address. The second firewall policy
is configured with a VIP as the destination address.
Which IP address will be used to source NAT the Internet traffic coming from a workstation with the
IP address 10.0.1.10/24?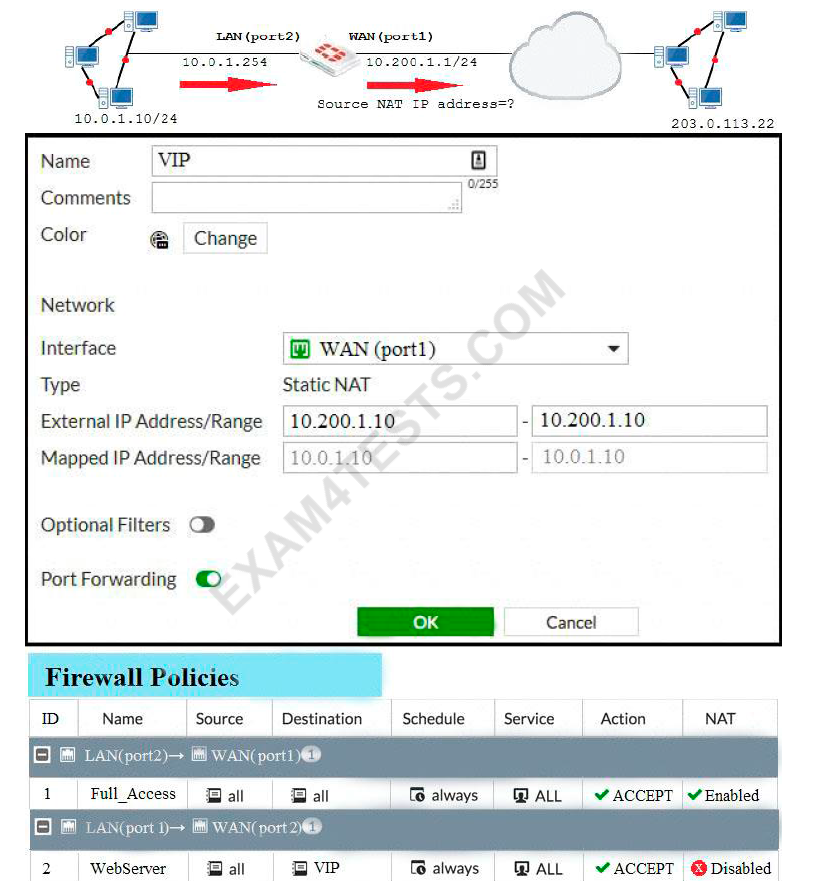
- A10.200.1.10
- BAny available IP address in the WAN (port1) subnet 10.200.1.0/24
- C10.200.1.1
- D10.0.1.254
27Which statements about antivirus scanning mode are true? (Choose two.)
- AIn proxy-based inspection mode antivirus buffers the whole file for scarring before sending it to
the client. - BIn flow-based inspection mode, you can use the CLI to configure antivirus profiles to use protocol
option profiles. - CIn proxy-based inspection mode, if a virus is detected, a replacement message may not be
displayed immediately. - DIn quick scan mode, you can configure antivirus profiles to use any of the available signature data
bases.
- AIn proxy-based inspection mode antivirus buffers the whole file for scarring before sending it to
28Which of the following statements are true when using WPAD with the DHCP discovery
method? (Choose two.)- AIf the DHCP method fails, browsers will try the DNS method.
- BThe browser needs to be preconfigured with the DHCP server's IP address.
- CThe browser sends a DHCPONFORM request to the DHCP server.
- DThe DHCP server provides the PAC file for download.
29Which statements correctly describe transparent mode operation? (Choose three.)
- AAll interfaces of the transparent mode FortiGate device must be on different IP subnets.
- BEthernet packets are forwarded based on destination MAC addresses, not IP addresses.
- CThe transparent FortiGate is visible to network hosts in an IP traceroute.
- DIt permits inline traffic inspection and firewalling without changing the IP scheme of the network.
- EFortiGate acts as transparent bridge and forwards traffic at Layer 2.
30A team manager has decided that while some members of the team need access to particular
website, the majority of the team does not. Which configuration option is the most effective option
to support this request?- AImplement a web filter category override for the specified website.
- BImplement web filter authentication for the specified website
- CImplement web filter quotas for the specified website.
- DImplement DNS filter for the specified website.
31Examine the IPS sensor configuration shown in the exhibit, and then answer the question
below.
An administrator has configured the WINDOWS_SERVERS IPS sensor in an attempt to determine
whether the influx of HTTPS traffic is an attack attempt or not. After applying the IPS sensor,
FortiGate is still not generating any IPS logs for the HTTPS traffic.
What is a possible reason for this?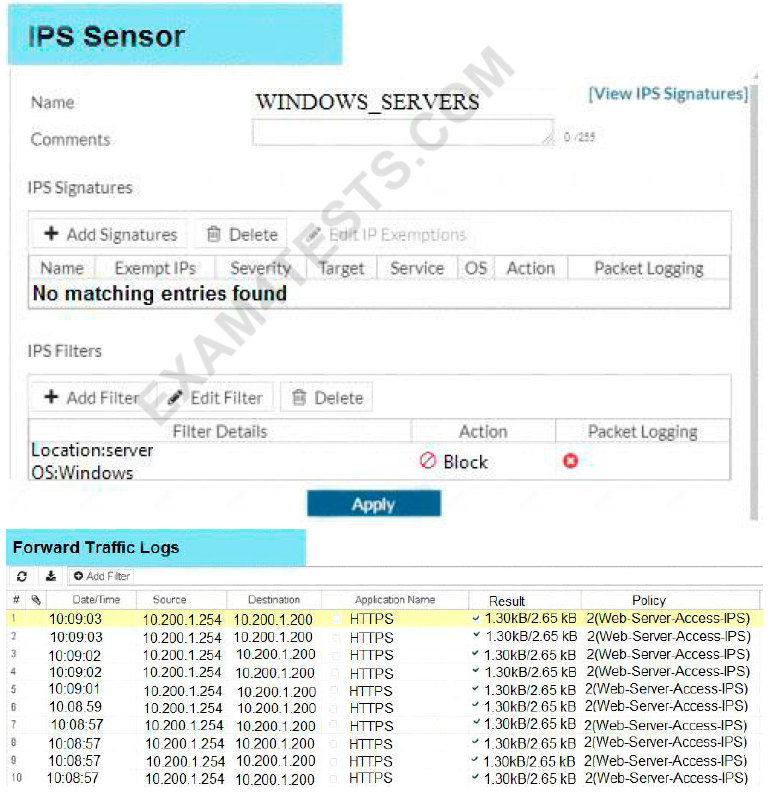
- AThe IPS filter is missing the Protocol: HTTPS option.
- BThe HTTPS signatures have not been added to the sensor.
- CA DoS policy should be used, instead of an IPS sensor.
- DA DoS policy used, instead of an IPS sensor.
- EThe firewall policy is not using a full SSL inspection profile.
32View the exhibit.
Why is the administrator getting the error shown in the exhibit?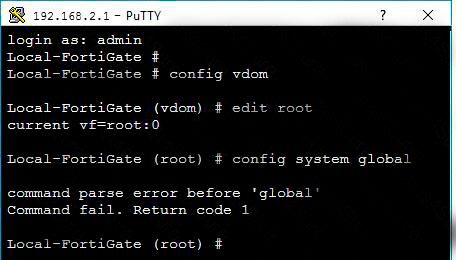
- AThe administrator must first enter the command edit global.
- BThe administrator admin does not have the privileges required to configure global settings.
- CThe global settings cannot be configured from the root VDOM context.
- DThe command config system global does not exist in FortiGate.
33View the exhibit.
Based on this output, which statements are correct? (Choose two.)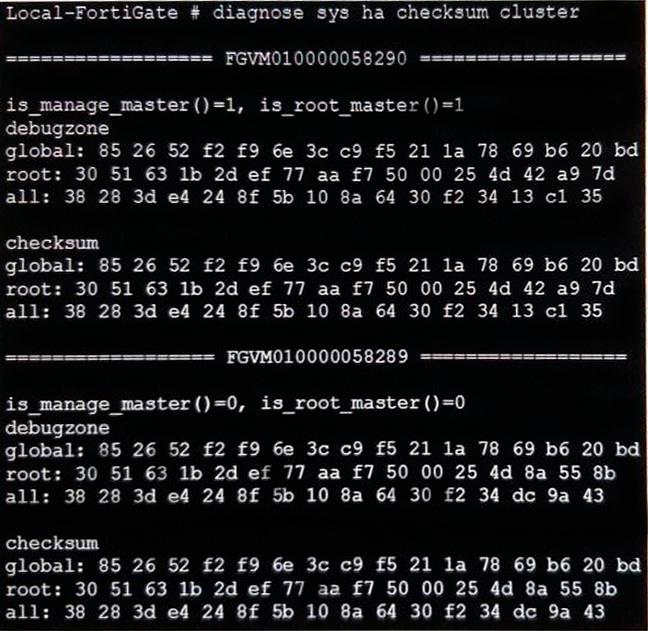
- AThe all VDOM is not synchronized between the primary and secondary FortiGate devices.
- BThe root VDOM is not synchronized between the primary and secondary FortiGate devices.
- CThe global configuration is synchronized between the primary and secondary FortiGate devices.
- DThe FortiGate devices have three VDOMs.
34A company needs to provide SSL VPN access to two user groups. The company also needs to
display different welcome messages on the SSL VPN login screen for both user groups.
What is required in the SSL VPN configuration to meet these requirements?- ADifferent SSL VPN realms for each group.
- BTwo separate SSL VPNs in different interfaces mapping the same ssl.root.
- CTwo firewall policies with different captive portals.
- DDifferent virtual SSL VPN IP addresses for each group.
35View the exhibit.
Which of the following statements are correct? (Choose two.)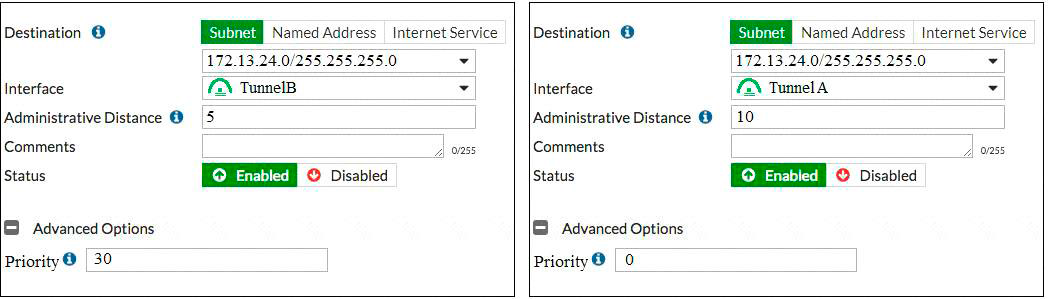
- AThis setup requires at least two firewall policies with the action set to IPsec.
- BDead peer detection must be disabled to support this type of IPsec setup.
- CThe TunnelB route is the primary route for reaching the remote site. The TunnelA route is used only if the TunnelB VPN is down.
- DThis is a redundant IPsec setup.
36What types of traffic and attacks can be blocked by a web application firewall (WAF) profile?
(Choose three.)- ATraffic to botnetservers
- BTraffic to inappropriate web sites
- CServer information disclosure attacks
- DCredit card data leaks
- ESQL injection attacks
37An administrator has configured central DNAT and virtual IPs. Which of the following can be
selected in the firewall policy Destination field?- AA VIP group
- BThe mapped IP address object of the VIP object
- CA VIP object
- DAn IP pool
38Examine this output from a debug flow:
Why did the FortiGate drop the packet?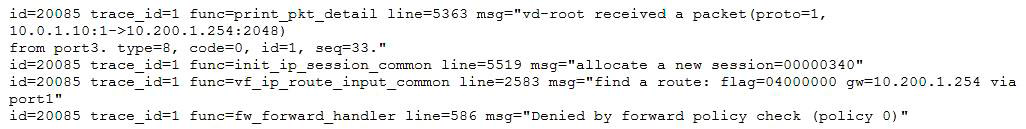
- AThe next-hop IP address is unreachable.
- BIt failed the RPF check.
- CIt matched an explicitly configured firewall policy with the action DENY.
- DIt matched the default implicit firewall policy.
39View the exhibit.
What does this raw log indicate? (Choose two.)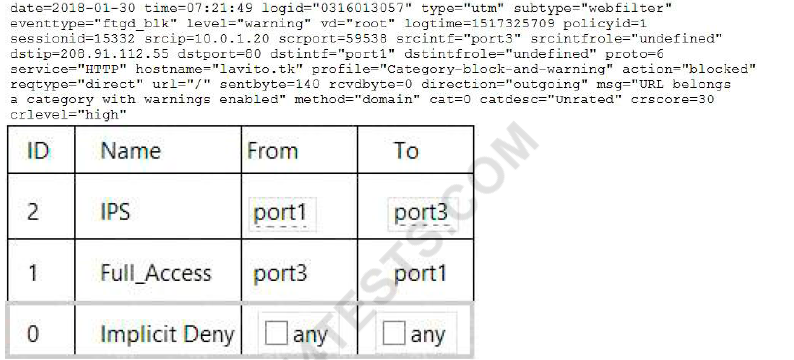
- AFortiGate blocked the traffic.
- Btype indicates that a security event was recorded.
- C10.0.1.20 is the IP address for lavito.tk.
- Dpolicyid indicates that traffic went through the IPS firewall policy.
40View the exhibit. Which of the following statements is true regarding the configuration
settings?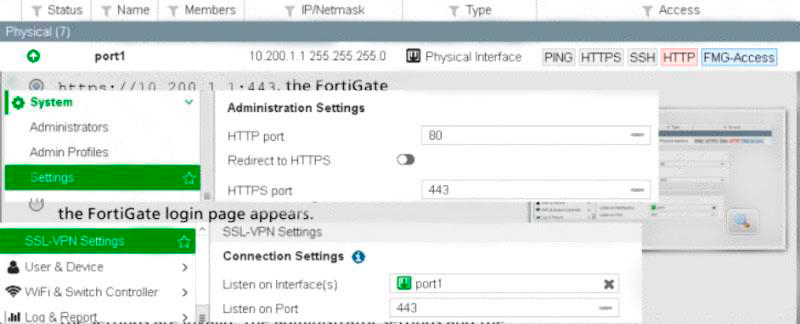
- AWhen a remote user accesses https://11.200.1.1:443, the FortiGate login page appears.
- BWhen a remote user accesses https://10.200.1.1:443, the FortiGate login page appears.
- CWhen a remote user accesses http: //10.200.1.1 :443, the FortiGate login page appears.
- DWhen a remote user accesses http: /110.200.1.1:443, the SSL VPN login page appears.
- EThe settings are invalid. The administrator settings and the SSL VPN settings cannot use the same port.
41Which certificate value can FortiGate use to determine the relationship between the issuer
and the certificate?- ASubject Key Identifier value
- BSMMIE Capabilities value
- CSubject value
- DSubject Alternative Name value
42To complete the final step of a Security Fabric configuration, an administrator must authorize
all the devices on which device?- AFortiManager
- BRoot FortiGate
- CFortiAnalyzer
- DDownstream FortiGate
43Which statements best describe auto discovery VPN (ADVPN). (Choose two.)
- AIt requires the use of dynamic routing protocols so that spokes can learn the routes to other spokes.
- BADVPN is only supported with IKEv2.
- CTunnels are negotiated dynamically between spokes.
- DEvery spoke requires a static tunnel to be configured to other spokes so that phase 1 and phase 2 proposals are defined in advance.
44Which of the following conditions must be met in order for a web browser to trust a web
server certificate signed by a third-party CA?- AThe public key of the web server certificate must be installed on the browser.
- BThe web-server certificate must be installed on the browser.
- CThe CA certificate that signed the web-server certificate must be installed on the browser.
- DThe private key of the CA certificate that signed the browser certificate must be installed on the browser.
45View the exhibit.
Based on the configuration shown in the exhibit, what statements about application control behavior
are true?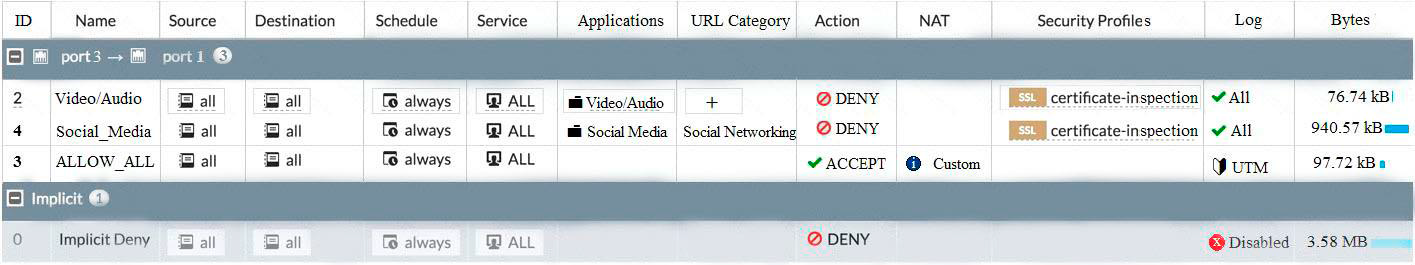
- AAccess to all unknown applications will be allowed.
- BAccess to browser-based Social.Media applications will be blocked.
- CAccess to mobile social media applications will be blocked.
- DAccess to all applications in Social.Media category will be blocked.
46An administrator needs to create an SSL-VPN connection for accessing an internal server
using the bookmark Port Forward. What step is required for this configuration?- AConfigure an SSL VPN realm for clients to use the port forward bookmark.
- BConfigure the client application to forward IP traffic through FortiClient.
- CConfigure the virtual IP address to be assigned t the SSL VPN users.
- DConfigure the client application to forward IP traffic to a Java applet proxy.
47A FortiGate device has multiple VDOMs. Which statement about an administrator account
configured with the default prof_admin profile is true?- AIt can create administrator accounts with access to the same VDOM.
- BIt cannot have access to more than one VDOM.
- CIt can reset the password for the admin account.
- DIt can upgrade the firmware on the FortiGate device.
48When override is enabled, which of the following shows the process and selection criteria
that are used to elect the primary FortiGate in an HA cluster?- AConnected monitored ports > HA uptime > priority > serial number
- BPriority > Connected monitored ports > HA uptime > serial number
- CConnected monitored ports > priority > HA uptime > serial number
- DHA uptime > priority > Connected monitored ports > serial number
49Which Statements about virtual domains (VDOMs) arc true? (Choose two.)
- ATransparent mode and NAT/Route mode VDOMs cannot be combined on the same FortiGate.
- BEach VDOM can be configured with different system hostnames.
- CDifferent VLAN sub-interface of the same physical interface can be assigned to different VDOMs.
- DEach VDOM has its own routing table.
50Which of the following conditions are required for establishing an IPSec VPN between two
FortiGate devices?
(Choose two.)- AIf XAuth is enabled as a server in one peer, it must be enabled as a client in the other peer.
- BIf the VPN is configured as route-based, there must be at least one firewall policy with the action set to IPSec.
- CIf the VPN is configured as DialUp User in one peer, it must be configured as either Static IP Address or Dynamic DNS in the other peer.
- DIf the VPN is configured as a policy-based in one peer, it must also be configured as policy-based in the other peer.
Informações
- Descrição
- Quiz sobre NS4, criado por Carlos Garcia em 27-04-2021.
- Autor
- Carlos Garcia
- Idioma
- Español
- Visualizações
- 415
- Avaliação
- 5,0 de 5 · 1 avaliação Avalie este quiz