
Mapa mental
Domain 2 - Asset Security
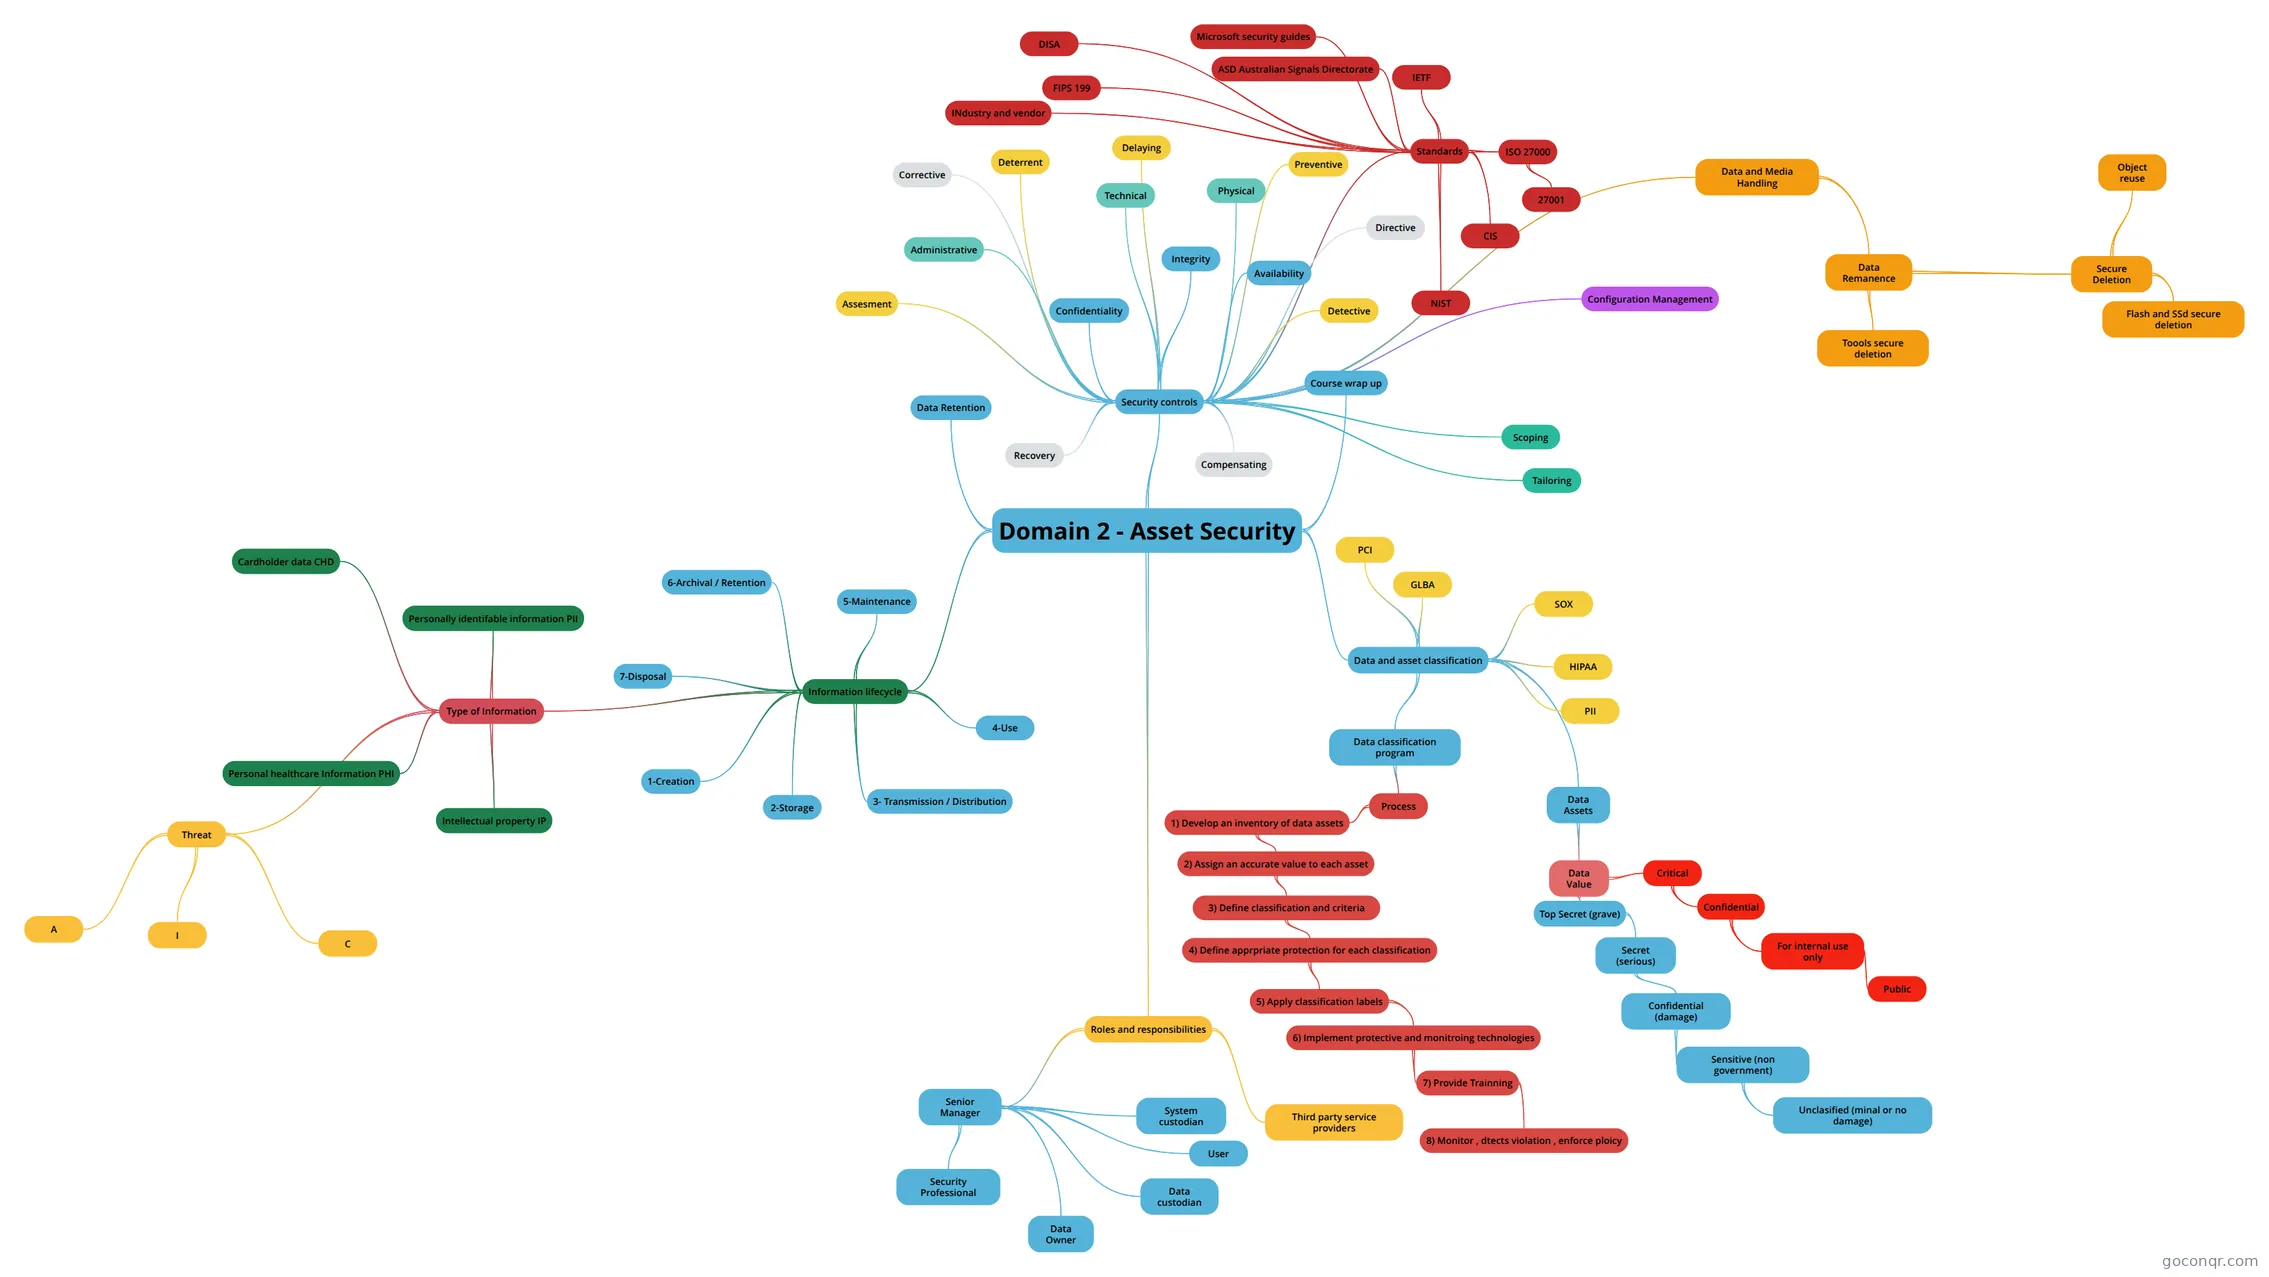
Mind map: Domain 2 - Asset Security
Conteúdo do mapa
Domain 2 - Asset Security
Information lifecycle
- 1-Creation
- creation of database
- 2-Storage
- save as, where retain
- 3- Transmission / Distribution
- Access to this information Data redundancy 2 copy. Easy , quickly access.
- 4-Use
- Storage, with network.
- 5-Maintenance
- Update
- 6-Archival / Retention
- outdate value decrease. cost money in vital components. law and regulation retain data for a period of time. 75 years federal retention
- 7-Disposal
- retention expiral, secure dispose. some unauthorize individual is not able to record this information
- Type of Information
- Located In house = Saqn , byod Not in house= cloud, third party , laptops, BYOD,removable media, email
- Allows / Control Access Technical, Administrative and Physical controls = Firewalls , routeres, permission /ACLs DLP, cryptography policies, locks , fences. Isolate / segment the sensitive data away.
- Intellectual property IP
- Trade secrets, patents, copirights, trademarks R&D , business financial data, customer list
- Personally identifable information PII
- Customers , employees, suppliers if expose theft of Identity of individual.
- Personal healthcare Information PHI
- Hippa laws
- Cardholder data CHD
- Threat
- C
- ,User account or system compromise loss or theft of laptop, eavesdropping shoulder surfing, sniffer, dupmer diving
- I
- Errors and omissions, fraud, man in the middle can not trust.
- A
- hard disk drive crash sever failure network failure corruption DoS DDoS
- C
- 1-Creation
Roles and responsibilities
- Senior Manager
- Must drive the entire security program Defines the tolerance for risk Relies on security professional for vision Approves specific countermeasures
- Security Professional
- Provides security vision to mmanagement Risk assessment/ management assits develop policy documents assists with proposal, implementation and maintenance of countermeasures Performs monitoring auditing, security assessments
- Data Owner
- Often a division manager reponsible especially profit/loss
- System custodian
- Privileged tecnitian responsible for implementing approved security controls. following policy Hardware and OS patching Electricity humidity.
- Data custodian
- Privileged technician responsible for implementing approved security controls. following policy. backup, practice restore, data restore, database admin
- User
- Need to access the information Input and process data, produce reports, act on results
- Third party service providers
- Entities that store , process or transmit data. Processors Cloud services ¡ IaaS PaaS saaS, Storage, Security. Third parties remain compliance. Ip PII privacy, HIPAA SOX GLBA PCI
- Senior Manager
Data and asset classification
- must be included / defined as a project with policies Mandatory for every data element (file database email) Data owner = responsible for completion and upkeep Data classification task are likely delegated to subordinate manager and users. System and data custodian is responsible for implementation and maintenance of rpotections.
- Data classification program
- Managers and end users must know, understand with data classification Monitoring and dtection of villations is required Managers are enforcers
- Exceptions: For business need Freedom of information eDiscovery Court order
- Classification level should be reviewed annually Asset value changes over time too low too high Declassification when it is ok to declassify release to public
- Process
- 1) Develop an inventory of data assets 2) Assign a value to each asset 3) Define classifications and criteria 4)Define protections for each classification 5) Apply classification 6)Implement protectie and monitoring 7) Provide training 8) Monitor , detect violation , enforce policy
- 1) Develop an inventory of data assets
- Files, databases, emails, printed, removable media Know where it is owner users Data in transit wired corporate network, Data at rest: On serverrs, workstations, laptop, personal devices on hard disk drives, backup tapes, optical disks on USB external disk drives , thumb drives on the video display printed data Multiple copies, location
- 2) Assign an accurate value to each asset
- Losses if the C, I, or A is compromised what competition would pay to know the secret Penalties / Liability / Litigation Fraud potential Losses if poor business desisions are made.
- 3) Define classification and criteria
- 4) Define apprpriate protection for each classification
- Accessible only to specific individuals need to know / least privilege Multi factor / mutual authentication Encryption for data at rest and in transit Do not distribute externally without NDA Data redundancy, col location Monitoring auditing violation
- 5) Apply classification labels
- Apply labels, redisigning backups to align with classifications Labels in header , footer , watermark, metada
- 6) Implement protective and monitroing technologies
- Strong authentication technologies permission acls tpm, vpn ssl, ssh data loss prevention (DLP) Message digests, hash values backups mirroiring shadowning
- 7) Provide Trainning
- All Users must know and follow data classification Users must know how to use protective technologies Compliance is not optional Penalties for violation Annual training at onboarding
- 8) Monitor , dtects violation , enforce ploicy
- Security team uses technologies to monitor, detect First tier managers must detect violation Enforcement must be cosistent Too much risk to the enterprise if users cannot comply with policies
- 4) Define apprpriate protection for each classification
- HIPAA
- SOX
- GLBA
- PCI
- PII
- Data Assets
- Inventory of data assets = Files , databases, emails, printed reports, removable media. Know where itis owner, users Data in transit.
- Data at rest on servers, workstation , laptop hard drives, backup tapes, video display, printed data, multiple copies , location
- Data Value
- Losses if the C, I, or A is compromised What the competition would pay to know the secret Penalties / liability / litigation Fraud potential Losses if poor business decisions are made because of inaccurate data or lack of data
- Top Secret (grave)
- Secret (serious)
- Confidential (damage)
- Sensitive (non government)
- Unclasified (minal or no damage)
- Sensitive (non government)
- Confidential (damage)
- Secret (serious)
- Critical
- Confidential
- For internal use only
- Public
- For internal use only
- Confidential
Data Retention
- Data must be securely maintained. (C,I and A) laws and regulation specify required retention.
- 2 to 10 year PCI 7 years federal has a 75 year. Fisma. requirements.
- Defining and constructing data retention For IP protected data, log data Secured communication channels and storage Encryption hashes, backups, read only Least privilege audit access separation of duties Prohibit storing data
- Enssure retention policies, processes Consider limitation and storage (PII, PHI, CHD) Some states
Security controls
- Security Controls: Confidentiality Integrity Availability
- Confidentiality
- Integrity
- Availability
- Administrative
- Policies, rules, regulations, laws, customs, culture, protocols
- functional through users awareness, an expectation of compliance and knowledge
- Technical
- Software implemented, like permissions, encryption, firewall rules, AV signature database, IDS / IPS DATA CUSTODIAM
- Physical
- Walls doors, securtity guards, dogs, IDS/IPS.
- Deterrent
- convince the attacker not to attack
- Delaying
- slow him down during
- Preventive
- Intended to stop the attack . during
- Detective
- Identify the attacck as soon as posible .during after reduce your looses.
- Assesment
- Assessment = Evaluate the seriousness of the attack
- Corrective
- intitial response to stop the losses, spread during.
- Recovery
- Response - longer term reponse to return - after
- Compensating
- Alternative controls
- Directive
- Informational , usually direction and for safety
- Standards
- CIS
- Center for Internet Security
- ISO 27000
- International orgainzation doe standardization
- 27001
- NIST
- Special Publication SP 800 Ciber Security
- IETF
- Internet Engineering Task Force Fequest for comment
- ASD Australian Signals Directorate
- ASD 1) Patch the OS 2) Patch applications, applets, add ons 3)Whitelist and conrol application Installations 4) Restrict adminsitrative access to least privilege
- FIPS 199
- Unclasifiec contect - Federal Information Processing Standards
- DISA
- STIG Security Technical Implementation Guide STIG DISA Defense Inormation Systems Agency
- INdustry and vendor
- Microsoft security guides
- CIS
- Scoping
- what parts of the standards are to be applied and where
- Tailoring
- Compensating alternate controls being used because the required controls
- Configuration Management
- Configuration documented as a baseline for future comparison Ideally most systems are in compliance Gold standard Silver standard snowflakes
- Formalized change management procedures Changes may only be made with approved change management request Preapproval for standard Docuemnted baseline must be updated as part of change manganagement versioning.
- Periodic audits using baseline Generate maintain and report baseline Configuration Integrity violation warrrants investigation and remediation
- Configuration integrity violations: Accidental misconfiguration Unauthorized change Documentation update missed Willful reconfiguration to allow breach
- Data and Media Handling
- printed should be destroyed Dumpster diving not usually illegal no owner trespass maybe consider secure disposal by armed guard.
- Data Remanence
- Magnetic media, DPU, HD, Magnetic backup SSD. wipeup ram garbage collection.
- Overwritten - One or more overwrites 3 times. write 33 times. Zeroized = all bits set to zero. All data bits set to 0s. Degaussed = Removes magnetic impulses . Magneting media. Ring down. generate strong polarized field. Physical destruction. SSD. have to relocated content to make space to other content. even if it deleate but does not clean all data. overwrite all information. Trim funtion. RUN ATL security funtion. Reset drive to original state. the only way to erase SSD.
- Toools secure deletion
- hardware drives.Secure Erase HDDERase.exe Darik book and Nuke (DBAN) Linux distribution Microsoft Cipher utility (free space) SDelete utility (file level) Linux shred u utility
- Secure Deletion
- Physicaldestruction Paper and optical disk shredder burning , crushing , drilling , grinding
- Flash and SSd secure deletion
- Standard disk secure delete tools fail SSD Trim utility does not ensure secure deletion: Secure Deletion: ATA Secure Erase - Resets all bits. Vendor supplied toolkit parted Magic Linux distribution / Internal secure Erase Physical destruction.
- Object reuse
- CPU registers, cache memory RAM Using these memory location , memory should be overwritten with garbage. called garbage collection.
Course wrap up
Informações
- Descrição
- Mapa Mental sobre Domain 2 - Asset Security, criado por Marcos Alvarado em 03-11-2017.
- Criado por
- Marcos Alvarado
- Visualizações
- 2
- Avaliação