
Flashcards
VPN Site to Site
Flashcards do conjunto (19)
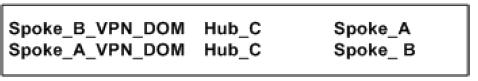
- 1$FWDIR/conf/vpn_route.conf. This configuration file, vpn_route.conf, is a text file that contains the name of network objects. The format is: Destination, Next hop, Install on Security Gateway (with tabbed spaces separating the elements). What is the purpose of this file?In this instance, Spoke_B_VPN_Dom is the name of the network object group that contains spoke B's VPN domain. Hub C is the name of the Security Gateway enabled for VPN routing. Spoke_A_VPN_Dom is the name of the network object that represents Spoke A's encryption domain
- 2Check Point Internal Certificate Authority (ICA) is part of the VPN trust entities. What are the functions of ICA?The ICA is part of the Check Point suite used for creating SIC trusted connection between Security Gateways, authenticating administrators and third party servers. The ICA provides certificates for internal Security Gateways and remote access clients which negotiate the VPN link
- 3is a VTI part of a domain-based VPN or route-based VPN?A virtual interface is a member of an existing, Route Based, VPN tunnel
- 4What is a VPN Domain?A group of computers and networks connected to a VPN tunnel by one VPN gateway that handles encryption and protects the VPN Domain members.
A VPN Domain is a collection of internal networks that use Security Gateways to send and receive VPN traffic. Define the resources that are included in the VPN Domain for each Security Gateway. - 5What is a VPN Community?A named collection of VPN domains, each protected by a VPN gateway. It joins the Security Gateways into a VPN community, also it is a collection of VPN tunnels and their attributes. Network resources of different VPN Domains can securely communicate with each other through VPN tunnels that terminate at the Security Gateways in the VPN communities
- 6What is the difference between VPN traffic routing in a domain-based VPN and a route-based VPN?Domain-based VPN or Policy based VPN: A method to route encrypted traffic with parameters defined by Security Gateways. Route-Based VPN: VPN traffic is routed according to the routing settings (static or dynamic) of the Security Gateway operating system. The Security Gateway uses a VTI (VPN Tunnel Interface) to send the VPN traffic as if it were a physical interface. The VTIs of Security Gateways in a VPN community connect and can support dynamic routing protocols.
- 7What features does Link Selection provide?It enable the Security Gateway to find the best possible route for VPN traffic and select the interfaces that are used for VPN traffic to internal and external networks. It also configure the IP addresses that are used for VPN traffic and use route probing to select available VPN tunnels
- 8What are the routing methods for a star VPN community?VPN routing for satellites:To center and to other Satellites through center. To center, or through the center to other satellites, to internet and other VPN targets
- 9What is a VTI?A VTI is an operating system level virtual interface that can be used as a Security Gateway to the VPN domain of the peer Security Gateway
Each VTI is associated with a single tunnel to a Security Gateway. The tunnel itself with all of its properties is defined, as before, by a VPN Community linking the two Security Gateways
All traffic destined to the VPN domain of a peer Security Gateway is routed through the "associated" VTI - 10Can a route-based VPN be deployed between two devices in different VPN communities?Route Based VPN can only be implemented between two Security Gateways within the same community.
- 11What types of VTIs can be used in a route-based VPN?Numbered and Unnumbered
- 12In what type of VTI is it necessary to assign local and remote IP addresses for the VPN?Numbered. You configure a local and remote IP address for each numbered VPN Tunnel Interface (VTI). For each Security Gateway, you configure a local IP address, a remote address, and the local IP address source for outbound connections to the tunnel. The remote IP address must be the local IP address on the remote peer Security Gateway.
- 13What is Shell VPN and what is it used for?Using the new VPN Command Line Interface (VPN Shell), the administrator creates a VPN Tunnel Interface on the enforcement module for each peer Security Gateway, and "associates" the interface with a peer Security Gateway. The VPN Tunnel Interface may be numbered or unnumbered.
- 14What considerations should be taken into account when using numbered VTIs in a Cluster environment?considerations
Each member must have a unique source IP address.
Every interface on each member requires a unique IP address.
All VTIs going to the same remote peer must have the same name.
Cluster IP addresses are required. - 15What is the purpose of proxy interface configuration when using unnumbered VTIs?For unnumbered VTIs, you define a proxy interface for each Security Gateway. Each Security Gateway uses the proxy interface IP address as the source for outbound traffic. Unnumbered interfaces let you assign and manage one IP address for each interface. Proxy interfaces can be physical or loopback interfaces, the VTI is associated with a proxy interface from which the virtual interface inherits an IP address.
Traffic initiated by the Security Gateway and routed through the virtual interface will have the physical or loopback interface's IP Address as the source IP - 16What are the routing protocols supported in a route-based VPN?Dynamic Routing Protocols
BGP4
OSPFv2
RIPv1
RIPv2 - 17In a route-based VPN, which elements are still necessary, and which can be ignored?Security Gateway objects are still required, as well as VPN communities (and access control policies) to define which tunnels are available. However, VPN encryption domains for each peer Security Gateway are no longer necessary
- 18Can two types of VPN (route and domain) coexist in the same security gateway?If you configure a Security Gateway for Domain Based VPN and Route Based VPN, Domain Based VPN takes precedence by default.
- 19If in the same security gateway there are two types of VPN (route and domain), how do you force the route-based VPN to have priority over the domain-based VPN?To force Route Based VPN to take priority, you must create a dummy (empty) group and assign it to the VPN domain
Informações
- Descrição
- O usuário eliminou as informações de disciplina FlashCards sobre VPN Site to Site, criado por Usuário eliminado em 29-05-2019.
- Criado por
- Usuário eliminado · mai 2019
- Atualizado
- 17 jun 2019
- Visualizações
- 64
- Histórico
-
- Criado por brian gustavo triviño taborda · 10 mai 2019
- Copiado por brian gustavo triviño taborda · 29 mai 2019
- Avaliação