
Quiz
Web filtering
Perguntas do quiz (17)
1Which of the following is default inspection mode in FortiOS 5.6?
- Aa. Proxy-based
- Bb. Flow-based with NGFW mode set to profile- based
2How does NGFW policy-based mode differ from profile-based mode?
- Aa. Policy-based flow inspection supports web profile overrides.
- Bb. Policy-based flow inspection defines URL filters directly under the firewall policy.
3Which of the following statements about proxy-based web filtering is true?
- Aa. Requires more resources than flow-based
- Bb. Transparently analyzes the TCP flow of the traffic
4Inspection modes
- AFlow based
Proxy - BPolicy based
Route based
- AFlow based
5NGFW mode
- AProxy
Flow-based - BProfile-based
Policy-based
- AProxy
6NGFW mode only applicable to Proxy inspection mode
- AVerdadeiro
- BFalso
7Default inspection mode in FortiOS 5.6
- AFlow-based
Profile-based - BProxy
Policy-based
- AFlow-based
8Requires administrators to create and configure application control and web filtering profiles. then apply them to the selected firewall policy.
- AProfile-based
- BPolicy-based
9Allows administrators to apply application control and web filtering directly to a firewall policy, without having to configure application control and web filtering profiles.
Requires administrators to apply a single SSL/SSH inspection profile to all firewall policies.- AProfile-based
- BPolicy-based
10Antivirus configuration is always profile-based, regardless of the NGFW mode selection
- AVerdadeiro
- BFalso
11?
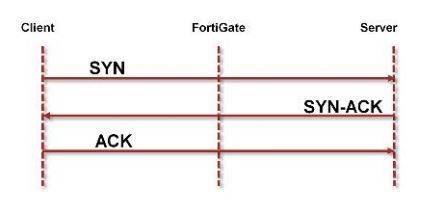
- AFlow-based
- BProxy
12Default inspection mode in FortiOS 5.6
Uses single-pass direct filter approach (DFA) pattern matching to identify possible attacks or threats
File is scanned on a flow basis as it passes through FortiGate
Requires fewer processing resources
Faster scanning- AFlow-based
- BProxy
13?
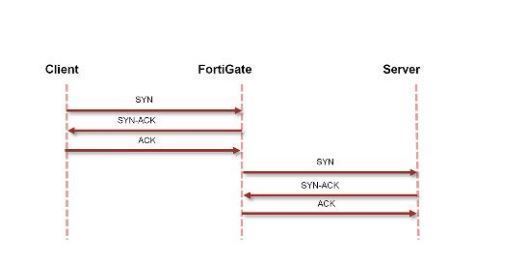
- AFlow-based
- BProxy
14More thorough inspection
Adds latency
-Complete content is scanned
Two TCP connections
- From client to FortiGate acting as proxy server
-From FortiGate to server
Communication is terminated on Layer 4
More resource intensive
Provides a higher level of threat protection- AFlow-based
- BProxy-based
15Which of the following is default inspection mode in FortiOS 5.6?
- AA. Proxy-based.
- BB. Flow-based with NGFW mode set to profile-based.
16How does NGFW policy-based mode differ from profile-based mode?
- AA. Policy-based flow inspection supports web profile overrides.
- BB. Policy-based flow inspection defines URL filters directly under the firewall policy.
17Which of the following statements about proxy-based web filtering is true?
- AA. Requires more resources than flow-based
- BB. Transparently analyzes the TCP flow of the traffic
Informações
- Descrição
- NSE4 6.0 NSE4 6.0 Quiz sobre Web filtering, criado por Marcos Avila em 16-08-2018.
- Autor
- Marcos Avila
- Idioma
- Español
- Visualizações
- 346
- Etiquetas
- Avaliação
- Ainda sem avaliações Avalie este quiz