
Quiz
Quix2 - 50Q
Crie uma conta grátis para terminar este quiz
Salve seu progresso e veja sua nota final.
Já tem uma conta? Inicie sessão
Perguntas do quiz (50)
1What is the formula used to determine risk?
- AA. Risk = Threat * Vulnerability
- BB. Risk = Threat / Vulnerability
- CC. Risk = Asset * Threat
- DD. Risk = Asset / Threat
2The following graphic shows the NIST risk management framework
with step 4 missing. What is the missing step?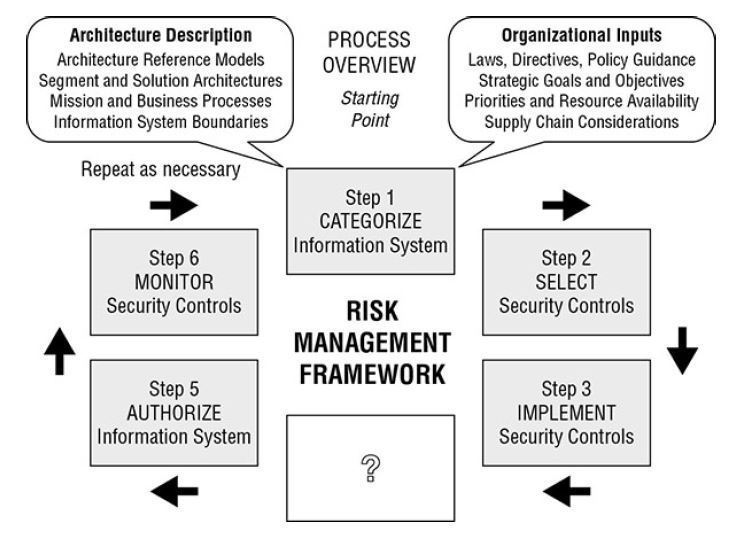
- AA. Assess security controls.
- BB. Determine control gaps.
- CC. Remediate control gaps.
- DD. Evaluate user activity.
3HAL Systems recently decided to stop offering public NTP services
because of a fear that its NTP servers would be used in amplification
DDoS attacks. What type of risk management strategy did HAL
pursue with respect to its NTP services?- AA. Risk mitigation
- BB. Risk acceptance
- CC. Risk transference
- DD. Risk avoidance
4Susan is working with the management team in her company to
classify data in an attempt to apply extra security controls that will
limit the likelihood of a data breach. What principle of information
security is Susan trying to enforce?- AA. Availability
- BB. Denial
- CC. Confidentiality
- DD. Integrity
5Which one of the following components should be included in an
organization’s emergency response guidelines?- AA. List of individuals who should be notified of an emergency
incident - BB. Long-term business continuity protocols
- CC. Activation procedures for the organization’s cold sites
- DD. Contact information for ordering equipment
- AA. List of individuals who should be notified of an emergency
6Who is the ideal person to approve an organization’s business
continuity plan?- AA. Chief information officer
- BB. Chief executive officer
- CC. Chief information security officer
- DD. Chief operating officer
7Which of the following is not one of the European Union’s General
Data Protection Regulation (GDPR) principles?- AA. Information must be processed fairly.
- BB. Information must be deleted within one year of acquisition.
- CC. Information must be maintained securely.
- DD. Information must be accurate.
8Ben’s company, which is based in the European Union, hires a thirdparty
organization that processes data for it. Who has responsibility to
protect the privacy of the data and ensure that it isn’t used for
anything other than its intended purpose?- AA. Ben’s company is responsible.
- BB. The third-party data processor is responsible.
- CC. The data controller is responsible.
- DD. Both organizations bear equal responsibility.
9When a computer is removed from service and disposed of, the
process that ensures that all storage media has been removed or
destroyed is known as what?- AA. Sanitization
- BB. Purging
- CC. Destruction
- DD. Declassification
10Linux systems that use bcrypt are using a tool based on what DES
alternative encryption scheme?- AA. 3DES
- BB. AES
- CC. Diffie–Hellman
- DD. Blowfish
11Susan works in an organization that labels all removable media with
the classification level of the data it contains, including public data.
Why would Susan’s employer label all media instead of labeling only
the media that contains data that could cause harm if it was exposed?- AA. It is cheaper to order all prelabeled media
- BB. It prevents sensitive media from not being marked by mistake.
- CC. It prevents reuse of public media for sensitive data.
- DD. Labeling all media is required by HIPAA.
12Data stored in RAM is best characterized as what type of data?
- AA. Data at rest
- BB. Data in use
- CC. Data in transit
- DD. Data at large
13Rhonda is considering the use of new identification cards for
physical access control in her organization. She comes across a
military system that uses the card shown here. What type of card is
this?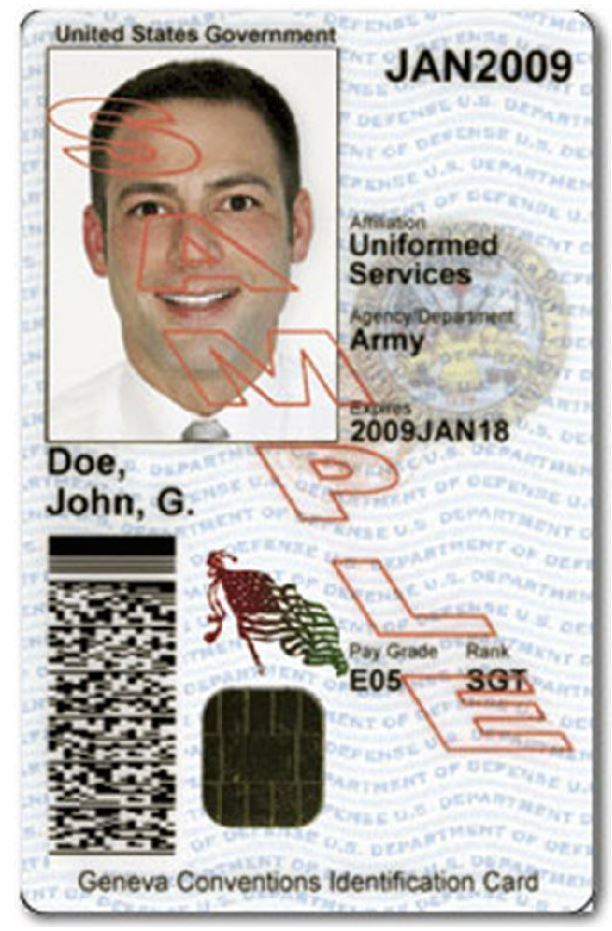
- AA. Smart card
- BB. Proximity card
- CC. Magnetic stripe card
- DD. Phase three card
14Gordon is concerned about the possibility that hackers may be able
to use the Van Eck radiation phenomenon to remotely read the
contents of computer monitors in his facility. What technology
would protect against this type of attack?- AA. TCSEC
- BB. SCSI
- CC. GHOST
- DD. TEMPEST
15In the diagram shown here of security boundaries within a
computer system, what component’s name has been replaced with
XXX?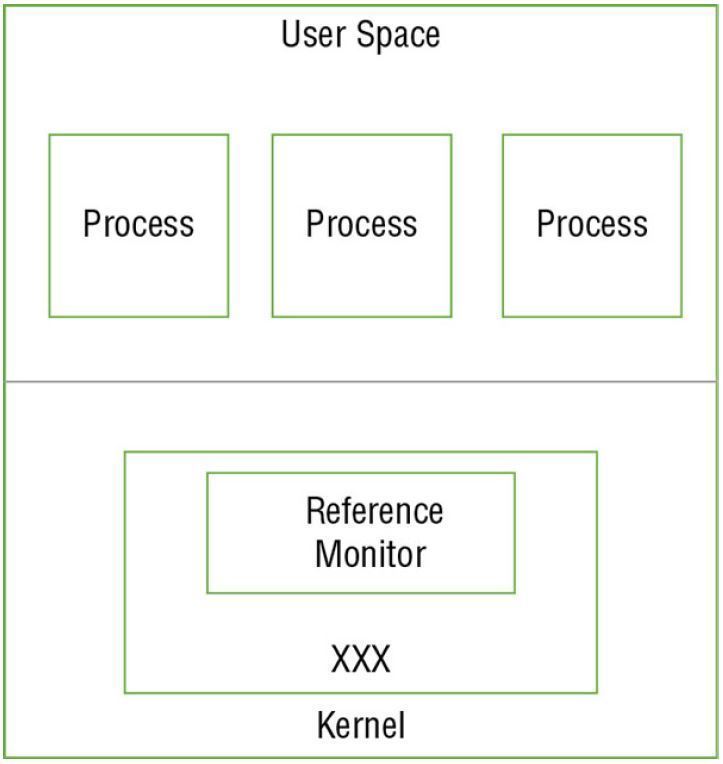
- AA. Kernel
- BB. TCB
- CC. Security perimeter
- DD. User execution
16Sherry conducted an inventory of the cryptographic technologies in
use within her organization and found the following algorithms
and protocols in use. Which one of these technologies should she
replace because it is no longer considered secure?- AA. MD5
- BB. 3DES
- CC. PGP
- DD. WPA2
17What action can you take to prevent accidental data disclosure due
to wear leveling on an SSD device before reusing the drive?- AA. Reformatting
- BB. Disk encryption
- CC. Degaussing
- DD. Physical destruction
18Tom is a cryptanalyst and is working on breaking a cryptographic
algorithm’s secret key. He has a copy of an intercepted message
that is encrypted, and he also has a copy of the decrypted version of
that message. He wants to use both the encrypted message and its
decrypted plaintext to retrieve the secret key for use in decrypting
other messages. What type of attack is Tom engaging in?- AA. Chosen ciphertext
- BB. Chosen plaintext
- CC. Known plaintext
- DD. Brute force
19A hacker recently violated the integrity of data in James’s company
by modifying a file using a precise timing attack. The attacker
waited until James verified the integrity of a file’s contents using a
hash value and then modified the file between the time that James
verified the integrity and read the contents of the file. What type of
attack took place?- AA. Social engineering
- BB. TOCTOU
- CC. Data diddling
- DD. Parameter checking
20What standard governs the creation and validation of digital
certificates for use in a public key infrastructure?- AA. X.509
- BB. TLS
- CC. SSL
- DD. 802.1x
21What is the minimum fence height that makes a fence difficult to
climb easily, deterring most intruders?- AA. 3 feet
- BB. 4 feet
- CC. 5 feet
- DD. 6 feet
22Johnson Widgets strictly limits access to total sales volume
information, classifying it as a competitive secret. However,
shipping clerks have unrestricted access to order records to
facilitate transaction completion. A shipping clerk recently pulled
all of the individual sales records for a quarter and totaled them up
to determine the total sales volume. What type of attack occurred?- AA. Social engineering
- BB. Inference
- CC. Aggregation
- DD. Data diddling
23What physical security control broadcasts false emanations
constantly to mask the presence of true electromagnetic
emanations from computing equipment?- AA. Faraday cage
- BB. Copper-infused windows
- CC. Shielded cabling
- DD. White noise
24In a software as a service cloud computing environment, who is
normally responsible for ensuring that appropriate firewall
controls are in place to protect the application?- AA. Customer’s security team
- BB. Vendor
- CC. Customer’s networking team
- DD. Customer’s infrastructure management team
25The source ports have been
omitted from the figure, but you may assume that they are
specified correctly for the purposes of answering questions.
Which one of the following rules is not shown in the rulebase but will
be enforced by the firewall?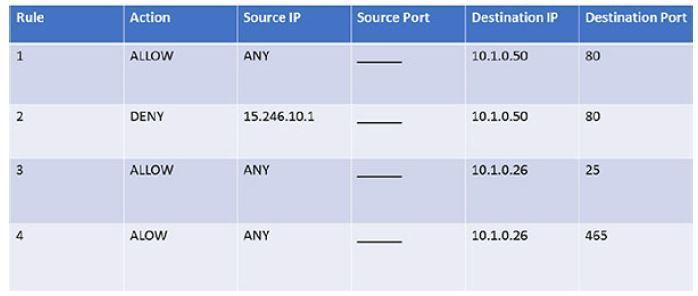
- AA. Stealth
- BB. Implicit deny
- CC. Connection proxy
- DD. Egress filter
26The source ports have been
omitted from the figure, but you may assume that they are
specified correctly for the purposes of answering questions.
What type of server is running at IP address 10.1.0.26?- AA. Email
- BB. Web
- CC. FTP
- DD. Database
27The source ports have been
omitted from the figure, but you may assume that they are
specified correctly for the purposes of answering questions.
The system at 15.246.10.1 attempts HTTP and HTTPS connections to
the web server running at 10.1.0.50. Which one of the following
statements is true about that connection?- AA. Both connections will be allowed.
- BB. Both connections will be blocked.
- CC. The HTTP connection will be allowed, and the HTTPS connection
will be blocked. - DD. The HTTP connection will be blocked, and the HTTPS connection
will be allowed.
28The source ports have been
omitted from the figure, but you may assume that they are
specified correctly for the purposes of answering questions.
What value should be used to fill in the source port for rule #3?- AA. 25
- BB. 465
- CC. 80
- DD. Any
29Data streams occur at what three layers of the OSI model?
- AA. Application, Presentation, and Session
- BB. Presentation, Session, and Transport
- CC. Physical, Data Link, and Network
- DD. Data Link, Network, and Transport
30Chris needs to design a firewall architecture that can support a DMZ, a
database, and a private internal network in a secure manner that
separates each function. What type of design should he use, and how
many firewalls does he need?- AA. A four-tier firewall design with two firewalls
- BB. A two-tier firewall design with three firewalls
- CC. A three-tier firewall design with at least one firewall
- DD. A single-tier firewall design with three firewalls
31A new customer at a bank that uses fingerprint scanners to
authenticate its users is surprised when he scans his fingerprint and is
logged in to another customer’s account. What type of biometric factor
error occurred?- AA. A registration error
- BB. A Type 1 error
- CC. A Type 2 error
- DD. A time of use, method of use error
32What type of access control is typically used by firewalls?
- AA. Discretionary access controls
- BB. Rule-based access controls
- CC. Task-based access control
- DD. Mandatory access controls
33When you input a user ID and password, you are performing what
important identity and access management activity?- AA. Authorization
- BB. Validation
- CC. Authentication
- DD. Login
34During a port scan using nmap, Joseph discovers that a system shows
two ports open that cause him immediate worry:
21/open
23/open
What services are likely running on those ports?- AA. SSH and FTP
- BB. FTP and Telnet
- CC. SMTP and Telnet
- DD. POP3 and SMTP
35Saria’s team is working to persuade their management that their
network has extensive vulnerabilities that attackers could exploit. If
she wants to conduct a realistic attack as part of a penetration test,
what type of penetration test should she conduct?- AA. Crystal box
- BB. Gray box
- CC. White box
- DD. Black box
36What method is commonly used to assess how well software testing
covered the potential uses of an application?- AA. A test coverage analysis
- BB. A source code review
- CC. A fuzz analysis
- DD. A code review report
37Testing that is focused on functions that a system should not allow are
an example of what type of testing?- AA. Use case testing
- BB. Manual testing
- CC. Misuse case testing
- DD. Dynamic testing
38What type of monitoring uses simulated traffic to a website to monitor
performance?- AA. Log analysis
- BB. Synthetic monitoring
- CC. Passive monitoring
- DD. Simulated transaction analysis
39Which of the following vulnerabilities is unlikely to be found by a web
vulnerability scanner?- AA. Path disclosure
- BB. Local file inclusion
- CC. Race condition
- DD. Buffer overflow
40Jim uses a tool that scans a system for available services and then
connects to them to collect banner information to determine what
version of the service is running. It then provides a report detailing
what it gathers, basing results on service fingerprinting, banner
information, and similar details it gathers combined with CVE
information. What type of tool is Jim using?- AA. A port scanner
- BB. A service validator
- CC. A vulnerability scanner
- DD. A patch management tool
41Mark is considering replacing his organization’s customer relationship
management (CRM) solution with a new product that is available in
the cloud. This new solution is completely managed by the vendor,
and Mark’s company will not have to write any code or manage any
physical resources. What type of cloud solution is Mark considering?- AA. IaaS
- BB. CaaS
- CC. PaaS
- DD. SaaS
42Which one of the following information sources is useful to security
administrators seeking a list of information security vulnerabilities in
applications, devices, and operating systems?- AA. OWASP
- BB. Bugtraq
- CC. Microsoft Security Bulletins
- DD. CVE
43Which of the following would normally be considered an example of a
disaster when performing disaster recovery planning?
I. Hacking incident
II. Flood
III. Fire
IV. Terrorism- AA. II and III only
- BB. I and IV only
- CC. II, III, and IV only
- DD. I, II, III, and IV
44Glenda would like to conduct a disaster recovery test and is seeking a
test that will allow a review of the plan with no disruption to normal
information system activities and as minimal a commitment of time as
possible. What type of test should she choose?- AA. Tabletop exercise
- BB. Parallel test
- CC. Full interruption test
- DD. Checklist review
45Which one of the following is not an example of a backup tape rotation
scheme?- AA. Grandfather/Father/Son
- BB. Meet in the middle
- CC. Tower of Hanoi
- DD. Six Cartridge Weekly
46Victor created a database table that contains information on his
organization’s employees. The table contains the employee’s user ID,
three different telephone number fields (home, work, and mobile),
the employee’s office location, and the employee’s job title. There are
16 records in the table. What is the degree of this table?- AA. 3
- BB. 4
- CC. 6
- DD. 16
47Carrie is analyzing the application logs for her web-based application
and comes across the following string:
../../../../../../../../../etc/passwd
What type of attack was likely attempted against Carrie’s application?- AA. Command injection
- BB. Session hijacking
- CC. Directory traversal
- DD. Brute force
48When should a design review take place when following an SDLC
approach to software development?- AA. After the code review
- BB. After user acceptance testing
- CC. After the development of functional requirements
- DD. After the completion of unit testing
49Tracy is preparing to apply a patch to her organization’s enterprise
resource planning system. She is concerned that the patch may
introduce flaws that did not exist in prior versions, so she plans to
conduct a test that will compare previous responses to input with
those produced by the newly patched application. What type of
testing is Tracy planning?- AA. Unit testing
- BB. Acceptance testing
- CC. Regression testing
- DD. Vulnerability testing
50What term is used to describe the level of confidence that software is
free from vulnerabilities, either intentionally designed into the
software or accidentally inserted at any time during its life cycle, and
that the software functions in the intended manner?- AA. Validation
- BB. Accreditation
- CC. Confidence interval
- DD. Assurance
Informações
- Descrição
- Good Luck! :D
- Autor
- Requiemdust Sheena
- Idioma
- English
- Visualizações
- 166
- Etiquetas
- Avaliação
- 5,0 de 5 · 1 avaliação Avalie este quiz