
Quiz
CCNP 300-115 TOPIC SEGURIDAD
Perguntas do quiz (31)
1A Cisco Catalyst switch that is prone to reboots continues to rebuild the DHCP snooping
database. What is the solution to avoid the snooping database from being rebuilt after every
device reboot?- AA DHCP snooping database agent should be configured.
- BEnable DHCP snooping for all VLANs that are associated with the switch.
- CDisable Option 82 for DHCP data insertion.
- DUse IP Source Guard to protect the DHCP binding table entries from being lost upon rebooting.
- EApply ip dhcp snooping trust on all interfaces with dynamic addresses.
2Which portion of AAA looks at what a user has access to?
- Aauthorization
- Bauthentication
- Caccounting
- Dauditing
3Which command creates a login authentication method named “login” that will primarily use
RADIUS and fail over to the local user database?- A(config)# aaa authentication login default radius local
- B(config)# aaa authentication login login radius local
- C(config)# aaa authentication login default local radius
- D(config)# aaa authentication login radius local
4A server with a statically assigned IP address is attached to a switch that is provisioned for DHCP
snooping. For more protection against malicious attacks, the network team is considering enabling
dynamic ARP inspection alongside DHCP snooping. Which solution ensures that the server
maintains network reachability in the future?- ADisable DHCP snooping information option.
- BConfigure a static DHCP snooping binding entry on the switch.
- CTrust the interface that is connected to the server with the ip dhcp snooping trust command.
- DVerify the source MAC address of all untrusted interfaces with ip dhcp snooping verify macaddress
command.
5A network engineer wants to ensure Layer 2 isolation of customer traffic using a private VLAN.
Which configuration must be made before the private VLAN is configured?- ADisable VTP and manually assign VLANs.
- BEnsure all switches are configured as VTP server mode.
- CConfigure VTP Transparent Mode.
- DEnable VTP version 3.
6DHCP snooping and IP Source Guard have been configured on a switch that connects to several
client workstations. The IP address of one of the workstations does not match any entries found in
the DHCP binding database. Which statement describes the outcome of this scenario?- APackets from the workstation will be rate limited according to the default values set on the switch.
- BThe interface that is connected to the workstation in question will be put into the errdisabled state.
- CTraffic will pass accordingly after the new IP address is populated into the binding database.
- DThe packets originating from the workstation are assumed to be spoofed and will be discarded.
7A DHCP configured router is connected directly to a switch that has been provisioned with DHCP
snooping. IP Source Guard with the ip verify source port-security command is configured under
the interfaces that connect to all DHCP clients on the switch. However, clients are not receiving an
IP address via the DHCP server. Which option is the cause of this issue?- AThe DHCP server does not support information option 82.
- BThe DHCP client interfaces have storm control configured.
- CStatic DHCP bindings are not configured on the switch.
- DDHCP snooping must be enabled on all VLANs, even if they are not utilized for dynamic address
allocation.
8A switch is added into the production network to increase port capacity. A network engineer is
configuring the switch for DHCP snooping and IP Source Guard, but is unable to configure ip
verify source under several of the interfaces. Which option is the cause of the problem?- AThe local DHCP server is disabled prior to enabling IP Source Guard.
- BThe interfaces are configured as Layer 3 using the no switchport command.
- CNo VLANs exist on the switch and/or the switch is configured in VTP transparent mode
- DThe switch is configured for sdm prefer routing as the switched database management template.
- EThe configured SVIs on the switch have been removed for the associated interfaces.
9The command storm-control broadcast level 75 65 is configured under the switch port
connected to the corporate mail server. In which three ways does this command impact the traffic?
(Choose three.)- ASNMP traps are sent by default when broadcast traffic reaches 65% of the lower-level threshold.
- BThe switchport is disabled when unicast traffic reaches 75% of the total interface bandwidth.
- CThe switch resumes forwarding broadcasts when they are below 65% of bandwidth.
- DOnly broadcast traffic is limited by this particular storm control configuration.
- EMulticast traffic is dropped at 65% and broadcast traffic is dropped at 75% of the total interface
bandwidth - FThe switch drops broadcasts when they reach 75% of bandwidth.
10After port security is deployed throughout an enterprise campus, the network team has been
overwhelmed with port reset requests. They decide to configure the network to automate the
process of re-enabling user ports. Which command accomplishes this task?- Aswitch(config)# errdisable recovery interval 180
- Bswitch(config)# errdisable recovery cause psecure-violation
- Cswitch(config)# switchport port-security protect
- Dswitch(config)# switchport port-security aging type inactivity
- Eswitch(config)# errdisable recovery cause security-violation
11The network monitoring application alerts a network engineer of a client PC that is acting as a
rogue DHCP server. Which two commands help trace this PC when the MAC address is known?
(Choose two.)- Aswitch# show mac address-table
- Bswitch# show port-security
- Cswitch# show ip verify source
- Dswitch# show ip arp inspection
- Eswitch# show mac address-table address <mac address>
12While troubleshooting a network outage, a network engineer discovered an unusually high level of
broadcast traffic coming from one of the switch interfaces. Which option decreases consumption of
bandwidth used by broadcast traffic?- Astorm control
- BSDM routing
- CCisco IOS parser
- Dintegrated routing and bridging
- EDynamic ARP Inspection
13Which command globally enables AAA on a device?
- Aaaa new-model
- Baaa authentication
- Caaa authorization
- Daaa accounting
14Which AAA Authorization type includes PPP, SLIP, and ARAP connections?
- Anetwork
- BIP mobile
- CEXEC
- Dauth-proxy
15Which authentication service is needed to configure 802.1x?
- ARADIUS with EAP Extension
- BTACACS+
- CRADIUS with CoA
- DRADIUS using VSA
16Refer to the exhibit.
Which login credentials are required when connecting to the console port in this output?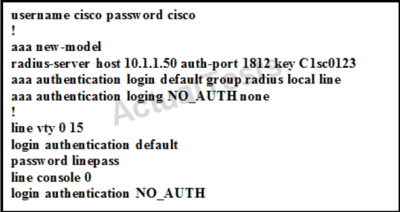
- Anone required
- Busername cisco with password cisco
- Cno username with password linepass
- Dlogin authentication default
17Refer to the exhibit.
When a network administrator is attempting an SSH connection to the device, in which order does
the device check the login credentials?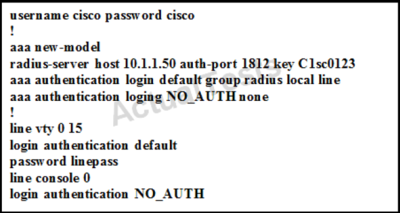
- ARADIUS server, local username, line password
- BRADIUS server, line password, local username
- CLine password, local username, RADIUS server
- DLine password, RADIUS server, local username
18Which type of information does the DHCP snooping binding database contain?
- Auntrusted hosts with leased IP addresses
- Btrusted hosts with leased IP addresses
- Cuntrusted hosts with available IP addresses
- Dtrusted hosts with available IP addresses
19Which switch feature determines validity based on IP-to-MAC address bindings that are stored in a
trusted database?- ADynamic ARP Inspection
- Bstorm control
- CVTP pruning
- DDHCP snooping
20Which command is needed to enable DHCP snooping if a switchport is connected to a DHCP
server?- Aip dhcp snooping trust
- Bip dhcp snooping
- Cip dhcp trust
- Dip dhcp snooping information
21Which private VLAN access port belongs to the primary VLAN and can communicate with all
interfaces, including the community and isolated host ports?- Apromiscuous port
- Bisolated port
- Ccommunity port
- Dtrunk port
22Which private VLAN can have only one VLAN and be a secondary VLAN that carries unidirectional
traffic upstream from the hosts toward the promiscuous ports and the gateway?- Aisolated VLAN
- Bprimary VLAN
- Ccommunity VLAN
- Dpromiscuous VLAN
23Which database is used to determine the validity of an ARP packet based on a valid IP-to-MAC
address binding?- ADHCP snooping database
- Bdynamic ARP database
- Cdynamic routing database
- Dstatic ARP database
24When IP Source Guard with source IP filtering is enabled on an interface, which feature must be
enabled on the access VLAN for that interface?- ADHCP snooping
- Bstorm control
- Cspanning-tree portfast
- Dprivate VLAN
25Which switch feature prevents traffic on a LAN from being overwhelmed by continuous multicast or
broadcast traffic?- Astorm control
- Bport security
- CVTP pruning
- DVLAN trunking
26Which command would a network engineer apply to error-disable a switchport when a packet-storm is detected?
- Arouter(config-if)#storm-control action shutdown
- Brouter(config-if)#storm-control action trap
- Crouter(config-if)#storm-control action error
- Drouter(config-if)#storm-control action enable
27A network engineer configures port security and 802.1x on the same interface. Which option
describes what this configuration allows?- AIt allows port security to secure the MAC address that 802.1x authenticates.
- BIt allows port security to secure the IP address that 802.1x authenticates.
- CIt allows 802.1x to secure the MAC address that port security authenticates.
- DIt allows 802.1x to secure the IP address that port security authenticates.
28Which feature describes MAC addresses that are dynamically learned or manually configured,
stored in the address table, and added to the running configuration?- Asticky
- Bdynamic
- Cstatic
- Dsecure
29On which interface can port security be configured?
- Astatic trunk ports
- Bdestination port for SPAN
- CEtherChannel port group
- Ddynamic access point
30When you configure private VLANs on a switch, which port type connects the switch to the
gateway router?- Apromiscuous
- Bcommunity
- Cisolated
- Dtrunked
31When you configure a private VLAN, which type of port must you configure the gateway router port
as?- Apromiscuous port
- Bisolated port
- Ccommunity port
- Daccess port
Informações
- Descrição
- topic security
- Autor
- Alexander Gomez
- Idioma
- Español
- Visualizações
- 151
- Etiquetas
- Avaliação
- Ainda sem avaliações Avalie este quiz