
Quiz
CET_TARDE - Security Fundamentals 2017 - Part 2
Este quiz tem tipos de pergunta que abrem no player de sempre.
Perguntas do quiz (125)
1A flood of packets with invalid source-IP addresses requests a connection on the network. The server busily tries to respond, resulting in valid requests being ignored. What type of attack occurred?
- ATrojan horse
- BBrute force
- CPing of death
- DSYN flooding
2What environment would be best suited for a two-firewall network design?
- Alarge corporate environment
- BA home environment with 10 or fewer hosts
- CA home environment that needs VPN access
- DA smaller, less congested business environment
3While surfing the Internet, a user notices a box claiming a prize has been won. The user opens the box unaware that a program is being installed. An intruder now accesses the computer and retrieves personal information. What type of attack occurred?
- AWorm
- BVirus
- CTrojan horse
- DDenial of service
4Which two statements are true concerning anti-spam software? (Choose two.)
- AAnti-spam software can be loaded on either the end-user PC or the ISP server, but not both.
- BWhen anti-spam software is loaded, legitimate e-mail may be classified as spam by mistake.
- CInstalling anti-spam software should be a low priority on the network.
- DEven with anti-spam software installed, users should be careful when opening e-mail attachments.
- EVirus warning e-mails that are not identified as spam via antispam software should be forwarded to other users immediately.
5What type of advertising is typically annoying and associated with a specific website that is being visited?
- AAdware
- BPopups
- CSpyware
- DTracking cookies
6What part of the security policy states what applications and usages are permitted or denied?
- ADentification and authentication
- BRemote access
- CAcceptable use
- DIncident handling
7To which part of the network does the wireless access point part of a Linksys integrated router connect?
- ADMZ
- BExternal
- CInternal
- DA network other than the wired network
8Identify three techniques used in social engineering. (Choose three.)
- AFishing
- BVishing
- CPhishing
- DSpamming
- EPretexting
- FJunk mailing
9What is a widely distributed approach to marketing on the Internet that advertises to as many individual users as possible via IM or e-mail?
- ABrute force
- BSpam
- CSpyware
- DTracking cookies
10Which acronym refers to an area of the network that is accessible by both internal, or trusted, as well as external, or untrusted, host devices?
- ASPI
- BDMZ
- CISR
- DISP
11During a pretexting event, how is a target typically contacted?
- ABy e-mail
- BBy phone
- CIn person
- DThrough another person
12What is a major characteristic of a Worm?
- AMalicious software that copies itself into other executable programs
- BTricks users into running the infected software
- CA set of computer instructions that lies dormant until triggered by a specific event
- DExploits vulnerabilities with the intent of propagating itself across a network
13What term is used to describe a dedicated hardware device that provides firewall services?
- AServer-based
- BIntegrated
- CPersonal
- DAppliance-based
14What best practice relates to wireless access point security?
- AActivation of a popup stopper
- BA change of the default IP address
- CAn update in the antivirus software definitions
- DPhysically securing the cable between the access point and client
15Which statement is true about port forwarding within a Linksys integrated router?
- AOnly external traffic that is destined for specific internal ports is permitted. All other traffic is denied.
- BOnly external traffic that is destined for specific internal ports is denied. All other traffic is permitted.
- COnly internal traffic that is destined for specific external ports is permitted. All other traffic is denied.
- DOnly internal traffic that is destined for specific external ports is denied. All other traffic is permitted.
16What statement is true about security configuration on a Linksys integrated router?
- AA DMZ is not supported.
- BThe router is an example of a server-based firewall.
- CThe router is an example of an application-based firewall.
- DInternet access can be denied for specific days and times.
17What is one function that is provided by a vulnerability analysis tool?
- AIt provides various views of possible attack paths.
- BIt identifies missing security updates on a computer.
- CIt identifies wireless weak points such as rogue access points.
- DIt identifies all network devices on the network that do not have a firewall installed.
- EIt identifies MAC and IP addresses that have not been authenticated on the network.
18Which statement is true regarding anti-virus software?
- AOnly e-mail programs need to be protected.
- BOnly hard drives can be protected.
- COnly after a virus is known can an anti-virus update be created for it.
- DOnly computers with a direct Internet connection need it.
19Many best practices exist for wired and wireless network security. The list below has one item that is not a best practice. Identify the recommendation that is not a best practice for wired and wireless security.
- APeriodically update anti-virus software.
- BBe aware of normal network traffic patterns.
- CPeriodically update the host operating system.
- DActivate the firewall on a Linksys integrated router.
- EConfigure login permissions on the integrated router.
- FDisable the wireless network when a vulnerability analysis is being performed.
20Refer to the graphic. In the Linksys Security menu, what does the SPI Firewall Protection option Enabled provide?
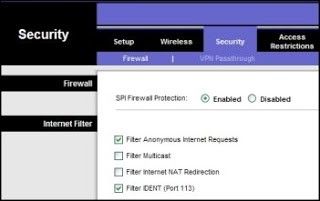
- AIt prevents packets based on the application that makes the request.
- BIt allows packets based on approved internal MAC or IP addresses.
- CIt requires that packets coming into the router be responses to internal host requests.
- DIt translates an internal address or group of addresses into an outside, public address.
21Passwords that contain recognizable words are vulnerable to a:
- Areplay attack
- Bdictionary attack
- Chashing attack
- DDenial of service attack
22A digitally signed e-mail message:
- Ais encrypted
- Bvalidates the sender
- Cis virus-free
- Dvalidates the recipient
23Which password attack uses all possible alpha numeric combinations?
- Adictionary attack
- Bsocial engineering
- Cbrute force attack
- Drainbow table attack
24What is the minimum OS to configure BitLocker?
- AWindows Vista Enterprise
- BWindows 7 Enterprise
- CWindows XP Pro
- DWindows 2000
25Account lockout policies are used to prevent which type of security attack?
- Apasswords being reused immediately
- Busers sharing passwords
- Cbrute force attacks
- Dsocial engineering
26A group of users has access to Folder A and all of its contents. You need to prevent some users from accessing a subfolder inside folder A. What should you do first?
- AChange the owner
- BHide the folder
- CBlock inheritance
- DDisable folder sharing
27Which enables you to change the permissions on a folder?
- AAuditing
- BTake ownership
- CExtended attributes
- DModify
28You want to make your computer resistant to online hackers and malicious software. What should you do?
- ATurn on Windows Firewall
- BConfigure a forward proxy
- CEnable spam filtering
- DInstall anti-virus software
29The primary purpose of Network Access Protection (NAP) is to prevent:
- Aloss of data from client computers on a network
- Busers on a network from installing software
- Cunauthorized users from accessing a network
- Dnon-compliant systems from connection to a network
30Many Internet sites that you visit require a username and password. How should you secure these passwords?
- AEnable session caching
- BSave them to a text file
- CSave them to an encrypted file
- DReuse the same password
- EConfigure the browser to save passwords
31The purpose of a digital certificate is to verify that a:
- Adigital document is complete
- Bcomputer is virus-free
- Cprivate key belongs to a sender
- Dpublic key belongs to a sender
32In IE8, InPrivate Browsing feature prevents:
- Aunauthorized private data input
- Bunencrypted communication between the client computer and the server
- Cany session data from being stored on the computer
- Duser credentials from being sent over the Internet
33Physically securing servers prevents:
- ADOS attacks
- Bman-in-the-middle attacks
- Ccompromise os the certificate chain
- Dtheft
34The Windows Firewall protects computers from:
- Aemail virus
- Bphishing scams
- Cunencrypted network access
- Dunauthorized network connections
35Role separation improve server security by:
- Aplacing servers on separate VLAN’s
- Benforcing principle of least privilege
- Cinstalling applications on separate hard disk
- Dphysically separating high security servers from others server
36Which one of the following describes spam?
- AGathering information about a person or organisation without their knowledge.
- BPerforming an unauthorised, usually malicious, action such as erasing files.
- CPutting unnecessary load on the network by making copies of files.
- DSending unwanted bulk messages.
37Which one of the following can protect a computer from the risk of unwanted emails?
- AAnti-spam software.
- BAnti-virus software.
- CAnti-spyware software.
- DPC diagnostic software.
38Which one of the following could lead to the spread of a malicious program?
- AUsing only software that has been checked for viruses.
- BMaintaining regularly updated anti-virus software.
- COpening only virus-checked file attachments from known sources.
- DUsing a USB Flash Drive from an unknown source to exchange data.
39Which one of the following describes why it is important to update antivirussoftware regularly?
- ATo protect your computer from all known viruses.
- BTo ensure the software identifies old viruses.
- CTo protect your computer from unwanted bulk messages.
- DTo prevent the spread of malicious programs on the Internet.
40Which one of the following describes what you should do if you receive a chain letter email?
- AForward the email.
- BDownload it onto your system.
- CDelete the email.
- DSend a read receipt.
41Which one of the following describes a computer hacker?
- AA skilled programmer who uses authorised access to exploit information available on a computer.
- BA skilled programmer who secretly invades computers without authorisation.
- CA skilled programmer who writes programs to train new employees.
- DA skilled programmer who helps in the installation of new software for an organisation.
42Which one of the following describes why firewalls are used?
- ATo prevent unauthorised access by incoming transmissions.
- BTo prevent destruction of a computer in the event of a fire.
- CTo enable easy downloading of data from web sites.
- DTo detect and disable viruses already on a computer.
43Which one of the following is MOST likely to be a hoax?
- AAn email from a friend you have not seen recently.
- BAn email with an attachment sent by a colleague using their personal email address.
- CAn email asking you to go to a website for a free computer scan.
- DAn email advertisement from a local shop you subscribe to.
44Which one of the following is the reason that users should log on with ausername and password?
- ATo be aware of who is in the building.
- BTo check up on the time-keeping of users.
- CTo protect computers against unauthorised use.
- DTo enable a personalised greeting for each user.
45Which one of the following statements about a password is TRUE?
- AIt must be changed only if it is compromised.
- BIt cannot contain special character symbols.
- CIt must be registered with the system administrator.
- DIt should be changed regularly.
46Which one of the following should be used to change your password?
- AControl Panel.
- BAnti-virus software.
- CWindows Firewall.
- DInternet Explorer.
47Which one of the following shows respect for confidentiality of information?
- ADiscussing confidential information over the telephone.
- BDisclosing confidential information only to authorised individuals.
- CUploading confidential information to a shared web site.
- DEmailing confidential information to a colleague.
48Which one of the following would be considered the BEST way to store a PIN number?
- AKeep a written note of it with you bank cards.
- BStore it on your computer.
- CMemorise it.
- DKeep a written note of it in your office drawer.
49Which one of the following describes why users should lock their computer when leaving their desk?
- ATo prevent unauthorised access to data.
- BTo prevent a waste of electricity.
- CTo prevent data from getting corrupted.
- DTo prevent the computer from malfunctioning.
50Which one of the following is an example of phishing?
- AAn email warning the recipient of a computer virus threat.
- BAn email directing the recipient to forward the email to friends.
- CAn email directing the recipient to enter personal details on a fake website.
- DAn email directing the recipient to download an attachment.
51Which one of the following is unsafe online activity?
- AUsing a screen name or nick name that cannot identify you.
- BMeeting someone you met online face-to-face in the company of your parents.
- CKeeping your social network profile private.
- DGiving your home address to someone you met in a chat room.
52Which one of the following describes a public network?
- AA network where devices outside the network cannot see or communicate directly with computers on the network.
- BA network where devices outside the network can see but cannot communicate directly with computers on the network.
- CA network where devices outside the network can see and communicate directly with computers on the network.
- DA network where devices outside the network cannot see but can communicate directly with computers on the network.
53Which one of the following describes how confidential information should be sent using an unsecured network?
- AIn an unsigned email.
- BIn an encrypted format.
- CIn a compressed format.
- DIn an attachment.
54Which one of the following statements about wireless networks is TRUE?
- AThey cannot be intercepted by unknown users.
- BThey limit accessibility to other users.
- CThey limit visibility to other users.
- DThey can be accessible to other users.
55Which one of the following is the recommended action to prevent the risk of access to a network by other users?
- ADisconnect the computer from the network.
- BComplain to the System Administrator.
- CChange the default WEP or WPA access key to one that only you know.
- DAdjust the Internet security settings.
56Which one of the following describes Bluetooth?
- AShort-range wired protocol for exchanging data.
- BShort-range wireless protocol for exchanging data.
- CLong-range wireless protocol for exchanging data.
- DLong-range wired protocol for exchanging data.
57Which one of the following describes why Bluetooth device settings should be adjusted?
- ATo increase the range of the device.
- BTo improve the quality of reception.
- CTo prevent the risk of unauthorised access.
- DTo reduce interference from other devices.
58Which one of the following would result in the loss of contact details if it were stolen?
- APrinter
- BMobile Phone.
- CModem
- DMP3
59Which one of the following should you do to ensure that your USB storage device is kept safe and secure?
- AOnly use it in private surroundings.
- BDo not access it using a Bluetooth device.
- CUse firewall software.
- DNever leave it unattended.
60Which one of the following departments would usually hold guidelines and procedures for the secure use of IT within an organisation?
- AThe IT Department.
- BThe Marketing Department.
- CThe Sales Department.
- DThe Finance Department.
61Which one of the following describes why you should follow guidelines and procedures while using IT resources in an organisation?
- ATo ensure easy access to information on your computer.
- BTo ensure the secure use of IT resources.
- CTo ensure the IT Department is able to monitor all activity.
- DTo ensure the Finance Department is able to monitor the costs of IT resources.
62Which one of the following should you approach if you are unsure of the IT security procedure to follow when uninstalling an application on your computer?
- AA technically well-informed team member.
- BA senior colleague in the Finance Department.
- CThe Maintenance Department.
- DThe Systems Administrator.
63Which one of the following describes how a breach in IT security should be reported?
- AUsing the telephone.
- BBy emailing to the IT Manager.
- CUsing any means of communication.
- DUsing the method listed in the organisation’s security policy.
64Which one of the following describes how to find out about an organisation’s privacy policy?
- ABy reading the office newsletter.
- BBy reading the policy in the organisation’s policy manual.
- CBy speaking to the Finance Department.
- DBy speaking to the Sales Department.
65Which one of the following would prevent the theft of a laptop?
- AAnti-virus software.
- BSpyware
- CA security cable.
- DA webcam
66Bridging is a process of sending packets from source to destination on OSI layer 3. Select the correct answer if the underlined text does not make the statement correct. Select “No change is needed” if the underlined text makes the statement correct.
- ARouting
- BSwitching
- CRepeating
- DNo change is needed.
67Windows Firewall is a built-in. host-based, stateless firewall. Select the correct answer if the underlined text does not make the statement correct. Select “No change is needed” if the underlined text makes the statement correct.
- AStateful
- BNetwork layer
- CPacket filter
- DNo change is needed
68The primary purpose of Network Access Protection (NAP) is to prevent:
- ALoss of data from client computers on a network.
- BNon-compliant systems from connecting to a network.
- CUsers on a network from installing software.
- DUnauthorized users from accessing a network.
69Your company maintains a Web server that is accessible to the public. It should be placed in a/an:
- Aprimary DNS zone.
- Benterprise domain.
- Cperimeter network.
- DVirtual Private Network (VPN).
70A network sniffer is software or hardware that:
- Acaptures and analyzes network communication.
- Brecords user activity and transmits it to the server
- Cprotects workstations from intrusions.
- Dcatalogs network data to create a secure index
71Which enables an employee to connect securely to a corporate network by using the Internet?
- AVirtual Private Networking (VPN)
- BRemote Desktop Protocol (RDP)
- CNetwork Address Translation (NAT)
- DNetwork Access Protection (NAP)
72You are trying to establish communications between a client computer and server. The server is not responding. You confirm that both the client and the server have network connectivity. Which should you check next?
- AData Execution Prevention
- BMicrosoft Update
- CActive Directory Domains and Trusts
- DWindows Firewall
73You have an application that communicates by using plain text. You want to secure communications between the application and a server at the network layer. What should you implement?
- AIPSec
- BSFTP
- CTLS
- DSSH
74Which technology enables you to filter communications between a program and the Internet?
- AAntivirus software
- BBitLocker To Go
- CRADIUS Server
- DSoftware firewall
75The primary purpose of Network Access Protection (NAP) is to prevent:
- Aloss of data from client computers on a network.
- Bnon-compliant systems from connecting to a network.
- Cunauthorized users from accessing a network.
- Dusers on a network from installing software.
76A malicious user who intercepts and modifies communications is known as a:
- Ared hat hacker
- Bman-in-the-middle
- Cnetwork sniffer.
- Dwhite hate hacker.
77Which three file system objects can you specify the NTFS permissions for? (Choose three.)
- AParents
- BFolders
- CExtensions
- DFiles
- ESubfolders
78You need to prevent unauthorized users from reading a specific file on a portable computer if the portable computer is stolen. What should you implement?
- AAdvanced Encryption Standard (AES)
- BFolder level permissions
- CFile-level permissions
- DDistributed File System (DFS)
- EBitLocker
79Basic security questions used to reset a password are susceptible to:
- Asocial engineering.
- Bhashing
- Cnetwork sniffing.
- DTrojan horses.
80Which displays a user’s level of access to a particular file or folder on the server?
- AThe Resultant Set of Policy
- BThe object's Effective Permission
- CThe client computer's registry
- DThe object's Advanced Attributes
81When conducting a security audit, the first step is to:
- Aset up a virus quarantine area.
- Binventory the company's technology assets.
- Cset up the system logs to audit security events.
- Dinstall auditing software on your servers.
82Biometrics are used to:
- Astudy hacking behavior.
- Bperform security audits.
- Cauthenticate users.
- Dmeasure the attack surface.
83A group of users has access to Folder A and all of its contents. You need to prevent some of the users from accessing a sub-folder inside Folder A.
- ADisable folder sharing
- BChange the owner
- CBlock inheritance
- DHide the folder
84How can you confirm whether a computer on your network is the target of a brute force attack?
- ARun the show all access command
- BUse antivirus software to scan the computer
- CCheck your Windows folder for unsigned files
- DCheck the security log for failed authentication attempts
85The default password length for a Windows Server domain controller is:
- A0
- B5
- C7
- D14
86Which is the minimum requirements to create BitLocker To Go media on a client computer?
- AWindows Vista Enterprise Edition
- BWindows 2000 Professional Service Pack 4
- CWindows 7 Enterprise Edition
- DWindows XP Professional Service Pack 3
87Software designed to infiltrate or damage a computer without the user’s consent is referred to as:
- AEmbedded
- BFreeware
- CMalware
- DUnsigned
88You need to be able to track file access. Which type of auditing should you implement?
- AObject access
- BProcess tracking
- CDirectory services
- DLogon events
89A solution designed to detect unauthorized user activities, attacks, and network compromises that can also take action to prevent a breach from occurring.
- Aintrusion prevention systems (IPS)
- Bintrusion detection systems (IDS)
- CDNS Security Extensions (DNSsec)
- DUnified Threat Management (UTM)
90A conceptual model, created by the International Organization for Standardization (ISO) to describe a network architecture that allows the passage of data between computer systems. Although never fully utilized as model for a protocol, the OSI model is nonetheless the standard for discussing how networking works.
- ASecure Content Management (SCM)
- BDMZ (demilitarized zone)
- Cstateful inspection
- DOpen Systems Interconnect (OSI)
91A system that is designed to protect a computer or a computer network from network-based attacks. A firewall does this by filtering the data packets that are traversing the network.
- AFirewall
- Bhost firewall
- CHoneypot
- DHoney net
92An attack against the cached information on your DNS server.
- AHoneypot
- BDNS spoofing
- CDNS poisoning
- DSpoofing
93The consistency, accuracy, and validity of data or information. One of the goals of a successful information security program is to ensure that data is protected against any unauthorized or accidental changes.
- ARisk
- BAvailability
- CThreat
- DIntegrity
94Answer Area
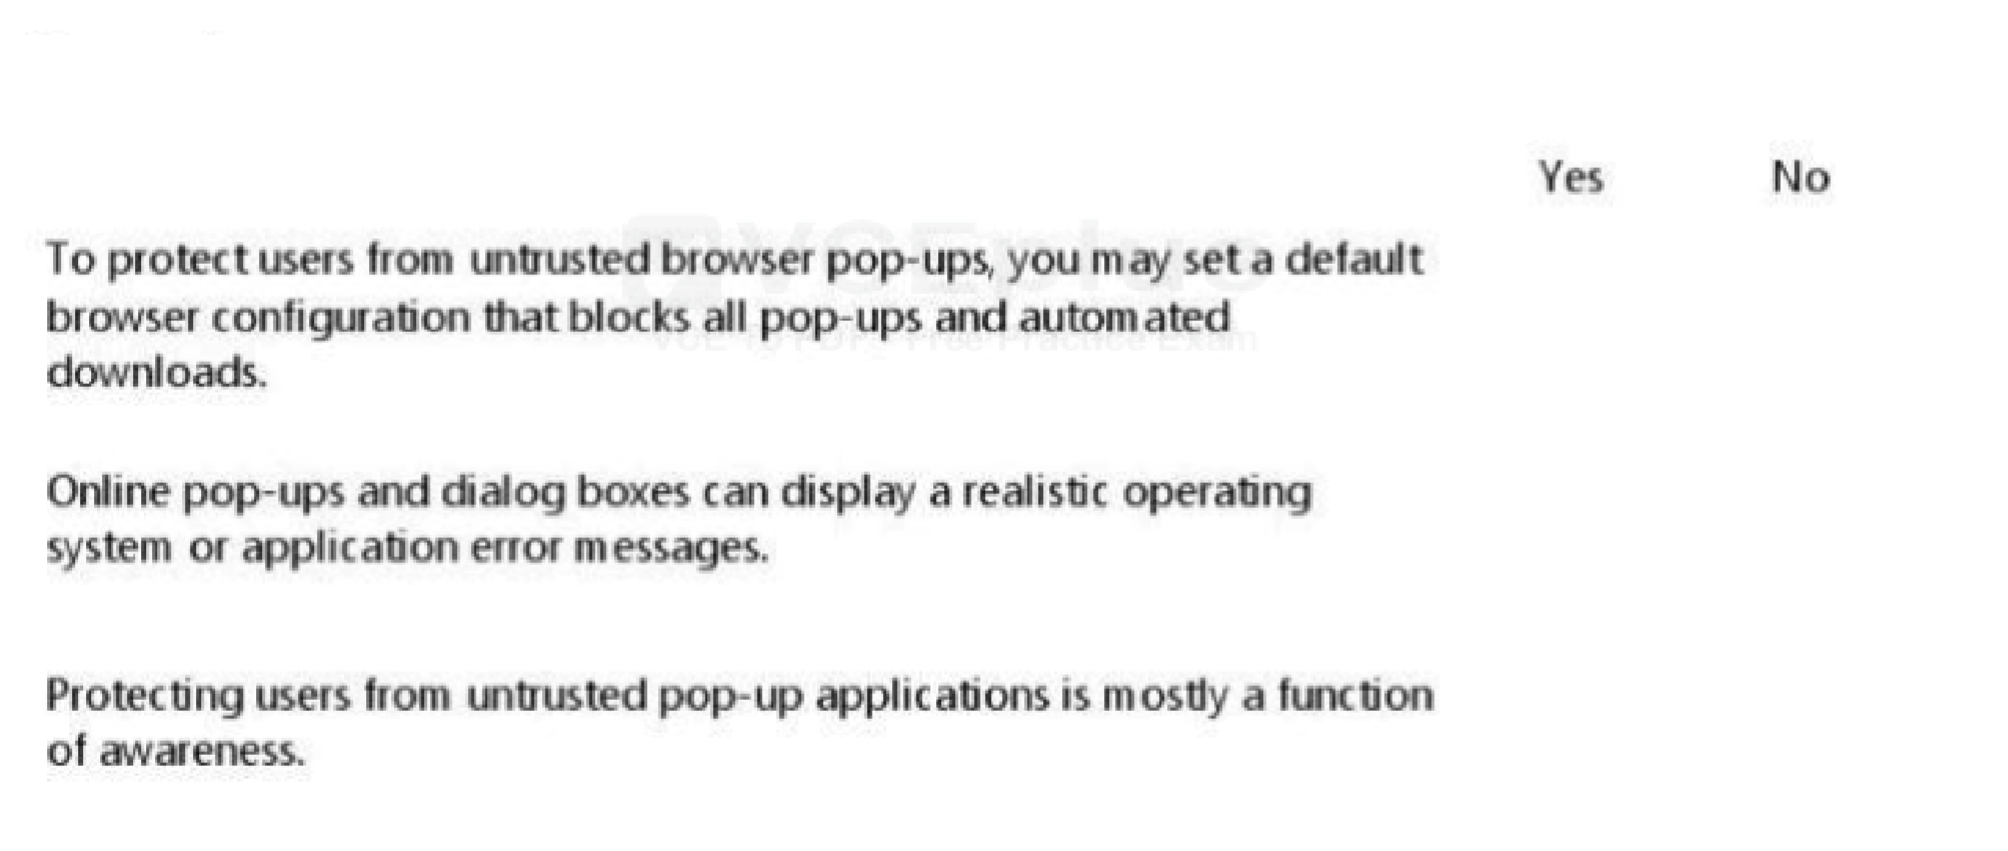
- AYes
- BNo
- CYes
- DNo
- EYes
- FNo
95Answer Area
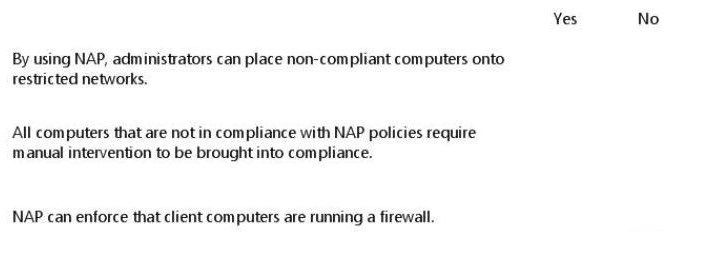
- AYes
- BNo
- CYes
- DNo
- EYes
- FNo
96You are preparing a local audit policy for your workstation. No auditing is enabled. The settings of your policy are shown in the following image:
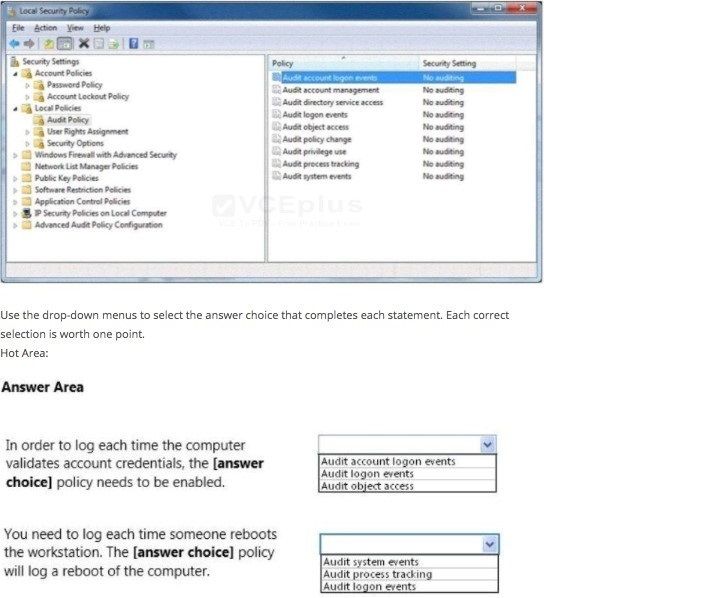
- AAudit Account logon events
- BAudit logon events
- CAudit Object access
- DAudit system events
- EAudit process traking
- FAudit logon events
97To keep third-party content providers from tracking your movements on the web, enable InPrivate Browsing.
Select the correct answer if the underlined text does not make the statement correct. Select “No change is needed” if the underlined text makes the statement correct.- AInPrivate Filtering
- BSmartScreen Filter
- CCompatibility Mode
- DNo change is needed
98Humongous Insurance needs to set up a domain controller in a branch office. Unfortunately, the server cannot be sufficiently secured from access by employees in that office, so the company is installing a Primary Domain Controller.
Select the correct answer if the underlined text does not make the statement correct. Select “No change is needed” if the underlined text makes the statement correct.- ARead-Only Domain Controller
- BBackup Domain Controller
- CActive Directory Server
- DNo change is needed.
99Dumpster diving refers to a physical threat that a hacker might use to look for information about a computer network.
Select the correct answer if the underlined text does not make the statement correct. Select “No change is needed” if the underlined text makes the statement correct.- AMinimum password age
- BMaximum password duration
- CPassword complexity
- DNo change is needed.
100Which attack listens to network traffic of a computer resource?
- AResource gathering
- BDenial of service
- CARP poisoning
- DEavesdropping
- ELogic bomb
101To implement WPA2 Enterprise, you would need a/an:
- ARADIUS server
- BSSL server
- CWEP server
- DVPN server
102The company that you work for wants to set up a secure network, but they do not have any servers. Which three security methods require the use of a server? (Choose three.)
- A802.1x
- BWPA2 Personal
- CWPA2 Enterprise
- DRADIUS
- E802.11ac
103You suspect a user’s computer is infected by a virus. What should you do first?
- ARestart the computer in safe mode
- BReplace the computer’s hard disk drive
- CDisconnect the computer from the network
- DInstall antivirus software on the computer
104Malware is any kind of unwanted software that is installed without your consent.
Select the correct answer if the underlined text does not make the statement correct. Select “No change is needed” if the underlined text makes the statement correct.- AViruses are
- BWorms are
- CTrojans are
- DNo change is needed.
105You need to be able to track file access. Which type of auditing should you implement?
- AObject access
- BDirectory services
- CLogon events
- DProcess tracking
106Which networking protocol provides centralized authentication, authorization and accounting?
- ASMTP
- BRADIUS
- CHTTPS
- DOpenID
107A Virtual Private Network (VPN) is a/an:
- ATunnel that prevents information that passes through it from being modified or stolen
- BPerimeter network that contains secure virtual servers
- CVirtual communication method that stores data transmitted in private environment
- DIntrusion Prevention System that filters unauthorized communications in the enterprise network
108Kerberos prevents (Choose two):
- AFile corruption
- BSpyware distribution
- CReplay attacks
- DEavesdropping
- EDenial of Service attacks
109You are network administrator. All computers run the Microsoft Internet Explorer browser. You need to prevent web cookies from being saved. What you should you enforce?
- ASmartScreen Filter (ajuda a identificar sites de phishing e de software maligno)
- BInPrivate Browsing
- CAntivirus protection
- DCross-Site Scripting Filter (ficheiros HTML)
110What are three ways you can reduce the number of opportunities that attackers have to exploit potential weaknesses or vulnerabilities? (Choose three)
- AEmploy content filtering for web browsers
- BRestrict access to system services
- CEmploy layered defenses
- DApply the principle of least privilege
- EElevate all accounts to administrator accounts
1118. For each of the following statements, select Yes if the statement is true. Otherwise, select No. Each correct selection is worth one point.
-A wireless MAC filter list allows only specified devices to receive packets sent from an access point [blank_start]NO[blank_end]
-A wireless MAC filter list can be used to either allow or deny access to the wireless network [blank_start]YES[blank_end]
-A wireless MAC filter list automatically applies encryption to a connection [blank_start]NO[blank_end]- AYES
- BNO
- CYES
- DNO
- EYES
- FNO
112Encrypting a hard disk is an example of ensuring:
- ALeast privilege
- BConfidentiality
- CIntegrity
- DSecurity by default
113Installing uninterruptible power sources to your servers is an example of ensuring:
- AIntegrity
- BAvailability
- CAccessibility
- DA backup strategy
114Media Access Control (MAC) filtering enables you to:
- ASet access permission to a shared folder
- BLimit access to a network based on the client computer’s network adapter
- CPrevent communications between specific IP addresses
- DRestrict communications to specific website
115Settings a database to run on a cluster of servers is an example of applying:
- AAccessibility
- BConfidentiality
- CAvailability
- DIntegrity
116You have a new computer and want to restrict other people from replacing the operating system. Which action prevents a user from installing an alternate operating system by using physical media if the user has physical access to the computer.
- APassword protecting the computer BIOS
- BRemoving the user from the administrators group
- CInstalling drive-level encryption
- DDisabling removable devices and drives
117You need to give a standard user permission to run a program as an administrator. How should you set up the program shortcut to accomplish this?
- AIn a different Compatibility Mode
- BBy using a smart card
- CIn a separate memory space
- DBy utilizing RunAs
118Your anti-spam program is blocking emails from a particular sender. your company needs to receive emails from this sender. What should you do?
- AAdd the email address to the whitelist
- BAccept RSS feeds from their domain
- CList the sender’s email address in DNS
- DReconfigure the SMS Gateway
119You want to prevent external users from acquiring information about your network. You should implement a:
- AProxy server
- BFirewall
- CLayer-3 switch
- DRouter
120For each of the following statements, select Yes if the statement is true. Otherwise, select No. Each correct selection is worth one point.
Securing network communication through IPSec packet signing ensures data integrity while in transit [blank_start]YES[blank_end]
IPSec packet ensures that the data is invulnerable to eavesdropping attacks [blank_start]YES[blank_end]
Most websites use IPSec to secure communications between their web servers and client web browsers. [blank_start]NO[blank_end]- AYES
- BNO
- CYES
- DNO
- EYES
- FNO
121You have an application that communicates by using plain text. You want to secure communications between the application and server at the network layer. What should you implement?
- ASFTP
- BSSH
- CIPSec
- DTLS
122The process of creating a barrier between domain members and non-domain members by using IPSec policies is referred to as:
- AServer isolation
- BDomain isolation
- CServer filtering
- DDomain filtering
123An authentication protocol used by Windows stand-alone systems is:
- ASMB
- BNTLM
- CNetBIOS
- DEAP
- EKerberos
124An authentication protocol widely used in 802.11 environments is:
- ASMB
- BNTLM
- CNetBIOS
- DEAP
- EKerberos
125A strong authentication protocol preferred by Windows Server 2012 R2 is:
- ASMB
- BNTLM
- CNetBIOS
- DEAP
- EKerberos
Informações
- Descrição
- Security Fundamentals Quizzes
- Autor
- Hawerth Castro
- Idioma
- Português
- Visualizações
- 787
- Etiquetas
- Avaliação
- Ainda sem avaliações Avalie este quiz