
Quiz
Exam A CEH9
Create a free account to finish this quiz
Save your progress and see your final score.
Already have an account? Sign in
Questions in this quiz (150)
1QUESTION 1
Which of the following countermeasure can specifically protect against both the MAC Flood and MAC Spoofing attacks?- AA. Configure Port Security on the switch
- BB. Configure Port Recon on the switch
- CC. Configure Switch Mapping
- DD. Configure Multiple Recognition on the switch
2QUESTION 2
Jimmy, an attacker, knows that he can take advantage of poorly designed input validation routines to create or alter SQL commands to gain access to private data or execute commands in the database. What technique does Jimmy use to compromise a database?- AA. Jimmy can submit user input that executes an operating system command to compromise a target
system - BB. Jimmy can gain control of system to flood the target system with requests, preventing legitimate users from gaining access
- CC. Jimmy can utilize an incorrect configuration that leads to access with higher-than expected privilege of the database
- DD. Jimmy can utilize this particular database threat that is an SQL injection technique to penetrate a target system
- AA. Jimmy can submit user input that executes an operating system command to compromise a target
3QUESTION 3
This IDS defeating technique works by splitting a datagram (or packet) into multiple fragments and the IDS will not spot the true nature of the fully assembled datagram. The datagram is not reassembled until it reaches its final destination. It would be a processor-intensive task for IDS to reassemble all fragments itself, and on a busy system the packet will slip through the IDS onto the network. What is this technique called- AA. IP Routing or Packet Dropping
- BB. IDS Spoofing or Session Assembly
- CC. IP Fragmentation or Session Splicing
- DD. IP Splicing or Packet Reassembly
4QUESTION 4
If a competitor wants to cause damage to your organization, steal critical secrets, or put you out of business, they just have to find a job opening, prepare someone to pass the interview, have that person hired, and they will be in the organization.
How would you prevent such type of attacks?- AA. It is impossible to block these attacks
- BB. Hire the people through third-party job agencies who will vet them for you
- CC. Conduct thorough background checks before you engage them
- DD. Investigate their social networking profiles
5QUESTION 5
This type of Port Scanning technique splits TCP header into several packets so that the packet filters are not able to detect what the packets intends to do.- AA. UDP Scanning
- BB. IP Fragment Scanning
- CC. Inverse TCP flag scanning
- DD. ACK flag scanning
6QUESTION 6
Joel and her team have been going through tons of garbage, recycled paper, and other rubbish in order to find some information about the target they are attempting to penetrate. How would you call this type of activity?- AA. Dumpster Diving
- BB. Scanning
- CC. CI Gathering
- DD. Garbage Scooping
7QUESTION 7
Anonymizer sites access the Internet on your behalf, protecting your personal information from disclosure. An anonymizer protects all of your computer's identifying information while it surfs for you, enabling you to remain at least one step removed from the sites you visit.
You can visit Web sites without allowing anyone to gather information on sites visited by you. Services that provide anonymity disable pop-up windows and cookies, and conceal visitor's IP address.
These services typically use a proxy server to process each HTTP request. When the user requests a Web page by clicking a hyperlink or typing a URL into their browser, the service retrieves and displays the information using its own server. The remote server (where the requested Web page resides) receives information on the anonymous Web surfing service in place of your information.
In which situations would you want to use anonymizer? (Select 3 answers)- AA. Increase your Web browsing bandwidth speed by using Anonymizer
- BB. To protect your privacy and Identity on the Internet
- CC. To bypass blocking applications that would prevent access to Web sites or parts of sites that you want to visit.
- DD. Post negative entries in blogs without revealing your IP identity
8QUESTION 8
What type of attack is shown in the following diagram?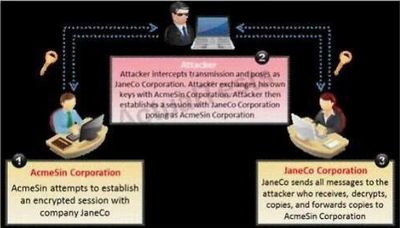
- AA. Man-in-the-Middle (MiTM) Attack
- BB. Session Hijacking Attack
- CC. SSL Spoofing Attack
- DD. Identity Stealing Attack
9QUESTION 9
Jack Hacker wants to break into Brown Co.'s computers and obtain their secret double fudge cookie recipe. Jack calls Jane, an accountant at Brown Co., pretending to be an administrator from Brown Co. Jack tells Jane that there has been a problem with some accounts and asks her to verify her password with him ''just to double check our records.'' Jane does not suspect anything amiss, and parts with her password. Jack can now access Brown Co.'s computers with a valid user name and password, to steal the cookie recipe.
What kind of attack is being illustrated here?- AA. Reverse Psychology
- BB. Reverse Engineering
- CC. Social Engineering
- DD. Spoofing Identity
- EE. Faking Identity
10QUESTION 10
How do you defend against ARP Spoofing? Select three.- AA. Use ARPWALL system and block ARP spoofing attacks
- BB. Tune IDS Sensors to look for large amount of ARP traffic on local subnets
- CC. Use private VLANS
- DD. Place static ARP entries on servers, workstation and routers
11QUESTION 11
TCP SYN Flood attack uses the three-way handshake mechanism.
1. An attacker at system A sends a SYN packet to victim at system B.
2. System B sends a SYN/ACK packet to victim A.
3. As a normal three-way handshake mechanism system A should send an ACK packet to system B, however, system A does not send an ACK packet to system B. In this case client B is waiting for an ACK packet from client A.
This status of client B is called _________________- AA. "half-closed"
- BB. "half open"
- CC. "full-open"
- DD. "xmas-open"
12QUESTION 12
Lori is a Certified Ethical Hacker as well as a Certified Hacking Forensics Investigator working as an IT security consultant. Lori has been hired on by Kiley Innovators, a large marketing firm that recently underwent a string of thefts and corporate espionage incidents. Lori is told that a rival marketing company came out with an exact duplicate product right before Kiley Innovators was about to release it. The executive team believes that an employee is leaking information to the rival company. Lori questions all employees, reviews server logs, and firewall logs; after which she finds nothing. Lori is then given permission to search through the corporate email system. She searches by email being sent to and sent
from the rival marketing company.
She finds one employee that appears to be sending very large email to this other marketing company, even
though they should have no reason to be communicating with them. Lori tracks down the actual emails sent
and upon opening them, only finds picture files attached to them. These files seem perfectly harmless,
usually containing some kind of joke. Lori decides to use some special software to further examine the
pictures and finds that each one had hidden text that was stored in each picture.
What technique was used by the Kiley Innovators employee to send information to the rival marketing
company?- AA. The Kiley Innovators employee used cryptography to hide the information in the emails sent
- BB. The method used by the employee to hide the information was logical watermarking
- CC. The employee used steganography to hide information in the picture attachments
- DD. By using the pictures to hide information, the employee utilized picture fuzzing
13QUESTION 13
You run nmap port Scan on 10.0.0.5 and attempt to gain banner/server information from services running on ports 21, 110 and 123.
Here is the output of your scan results:
Which of the following nmap command did you run?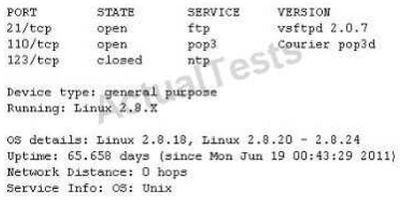
- AA. nmap -A -sV -p21, 110, 123 10.0.0.5
- BB. nmap -F -sV -p21, 110, 123 10.0.0.5
- CC. nmap -O -sV -p21, 110, 123 10.0.0.5
- DD. nmap -T -sV -p21, 110, 123 10.0.0.5
14QUESTION 14
How do you defend against Privilege Escalation?- AA. Use encryption to protect sensitive data
- BB. Restrict the interactive logon privileges
- CC. Run services as unprivileged accounts
- DD. Allow security settings of IE to zero or Low
- EE. Run users and applications on the least privileges
15QUESTION 15
What does ICMP (type 11, code 0) denote?- AA. Source Quench
- BB. Destination Unreachable
- CC. Time Exceeded
- DD. Unknown Type
16QUESTION 16
You are the security administrator of Jaco Banking Systems located in Boston. You are setting up ebanking website (http://www.ejacobank.com) authentication system. Instead of issuing banking customer with a single password, you give them a printed list of 100 unique passwords. Each time the customer needs to log into the e-banking system website, the customer enters the next password on the list. If someone sees them type the password using shoulder surfing, MiTM or keyloggers, then no damage is done because the password will not be accepted a second time. Once the list of 100 passwords is almost finished, the system automatically sends out a new password list by encrypted e-mail to the customer.
You are confident that this security implementation will protect the customer from password abuse.
Two months later, a group of hackers called "HackJihad" found a way to access the one-time password list issued to customers of Jaco Banking Systems. The hackers set up a fake website (http://www.e-jacobank.com) and used phishing attacks to direct ignorant customers to it. The fake website asked users for their ebanking username and password, and the next unused entry from their one-time password sheet. The hackers collected 200 customer's username/passwords this way. They transferred money from the customer's bank account to various offshore accounts.
Your decision of password policy implementation has cost the bank with USD 925, 000 to hackers. You immediately shut down the e-banking website while figuring out the next best security solution What effective security solution will you recommend in this case?- AA. Implement Biometrics based password authentication system. Record the customers face image to the authentication database
- BB. Configure your firewall to block logon attempts of more than three wrong tries
- CC. Enable a complex password policy of 20 characters and ask the user to change the password
immediately after they logon and do not store password histories - DD. Implement RSA SecureID based authentication system
17QUESTION 17
More sophisticated IDSs look for common shellcode signatures. But even these systems can be bypassed, by using polymorphic shellcode. This is a technique common among virus writers ?it basically hides the true nature of the shellcode in different disguises. How does a polymorphic shellcode work?- AA. They encrypt the shellcode by XORing values over the shellcode, using loader code to decrypt the
shellcode, and then executing the decrypted shellcode - BB. They convert the shellcode into Unicode, using loader to convert back to machine code then executing them
- CC. They reverse the working instructions into opposite order by masking the IDS signatures
- DD. They compress shellcode into normal instructions, uncompress the shellcode using loader code and
then executing the shellcode
- AA. They encrypt the shellcode by XORing values over the shellcode, using loader code to decrypt the
18QUESTION 18
SYN Flood is a DOS attack in which an attacker deliberately violates the three-way handshake and opens a large number of half-open TCP connections. The signature of attack for SYN Flood contains- AA. The source and destination address having the same value
- BB. A large number of SYN packets appearing on a network without the corresponding reply packets
- CC. The source and destination port numbers having the same value
- DD. A large number of SYN packets appearing on a network with the corresponding reply packets
19QUESTION 19
Which of the following type of scanning utilizes automated process of proactively identifying vulnerabilities of the computing systems present on a network?- AA. Port Scanning
- BB. Single Scanning
- CC. External Scanning
- DD. Vulnerability Scanning
20QUESTION 20
The following script shows a simple SQL injection. The script builds an SQL query by concatenating hardcoded strings together with a string entered by the user:
The user is prompted to enter the name of a city on a Web form. If she enters Chicago, the query assembled by the script looks similar to the following:
SELECT * FROM OrdersTable WHERE ShipCity = 'Chicago'
How will you delete the OrdersTable from the database using SQL Injection?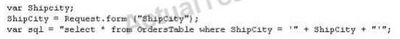
- AA. Chicago'; drop table OrdersTable --
- BB. Delete table'blah'; OrdersTable --
- CC. EXEC; SELECT * OrdersTable > DROP --
- DD. cmdshell'; 'del c:\sql\mydb\OrdersTable' //
21QUESTION 21
What are the limitations of Vulnerability scanners? (Select 2 answers)- AA. There are often better at detecting well-known vulnerabilities than more esoteric ones
- BB. The scanning speed of their scanners are extremely high
- CC. It is impossible for any, one scanning product to incorporate all known vulnerabilities in a timely manner
- DD. The more vulnerabilities detected, the more tests required
- EE. They are highly expensive and require per host scan license
22QUESTION 22
Stephanie works as senior security analyst for a manufacturing company in Detroit. Stephanie manages
network security throughout the organization. Her colleague Jason told her in confidence that he was able
to see confidential corporate information posted on the external website http://www.jeansclothesman.com.
He tries random URLs on the company's website and finds confidential information leaked over the web. Jason says this happened about a month ago. Stephanie visits the said URLs, but she finds nothing. She is very concerned about this, since someone should be held accountable if there was sensitive information posted on the website. Where can Stephanie go to see past versions and pages of a website?- AA. She should go to the web page Samspade.org to see web pages that might no longer be on the website
- BB. If Stephanie navigates to Search.com; she will see old versions of the company website
- CC. Stephanie can go to Archive.org to see past versions of the company website
- DD. AddressPast.com would have any web pages that are no longer hosted on the company's website
23QUESTION 23
Dan is conducting penetration testing and has found a vulnerability in a Web Application which gave him the sessionID token via a cross site scripting vulnerability. Dan wants to replay this token. However, the session ID manager (on the server) checks the originating IP address as well. Dan decides to spoof his IP address in order to replay the sessionID. Why do you think Dan might not be able to get an interactive session?- AA. Dan cannot spoof his IP address over TCP network
- BB. The scenario is incorrect as Dan can spoof his IP and get responses
- CC. The server will send replies back to the spoofed IP address
- DD. Dan can establish an interactive session only if he uses a NAT
24QUESTION 24
Jason works in the sales and marketing department for a very large advertising agency located in Atlanta. Jason is working on a very important marketing campaign for his company's largest client. Before the project could be completed and implemented, a competing advertising company comes out with the exact same marketing materials and advertising, thus rendering all the work done for Jason's client unusable. Jason is questioned about this and says he has no idea how all the material ended up in the hands of a competitor.
Without any proof, Jason's company cannot do anything except move on. After working on another high profile client for about a month, all the marketing and sales material again ends up in the hands of another competitor and is released to the public before Jason's company can finish the project. Once again, Jason says that he had nothing to do with it and does not know how this could have happened. Jason is given leave with pay until they can figure out what is going on.
Jason's supervisor decides to go through his email and finds a number of emails that were sent to the competitors that ended up with the marketing material. The only items in the emails were attached jpg files, but nothing else. Jason's supervisor opens the picture files, but cannot find anything out of the ordinary with them.
What technique has Jason most likely used?- AA. Stealth Rootkit Technique
- BB. ADS Streams Technique
- CC. Snow Hiding Technique
- DD. Image Steganography Technique
25QUESTION 25
What type of Virus is shown here?- AA. Cavity Virus
- BB. Macro Virus
- CC. Boot Sector Virus
- DD. Metamorphic Virus
- EE. Sparse Infector Virus
26An attacker finds a web page for a target organization that supplies contact information for the company.
Using available details to make the message seem authentic, the attacker drafts e-mail to an employee on
the contact page that appears to come from an individual who might reasonably request confidential
information, such as a network administrator.
The email asks the employee to log into a bogus page that requests the employee's user name and
password or click on a link that will download spyware or other malicious programming.
Google's Gmail was hacked using this technique and attackers stole source code and sensitive data from
Google servers. This is highly sophisticated attack using zero-day exploit vectors, social engineering and
malware websites that focused on targeted individuals working for the company.
What is this deadly attack called?
- ASpear phishing attack
- BTrojan server attack
- CJavelin attack
- DSocial networking attack
27Vulnerability scanners are automated tools that are used to identify vulnerabilities and misconfigurations of
hosts. They also provide information regarding mitigating discovered vulnerabilities.
Which of the following statements is incorrect?
- AVulnerability scanners attempt to identify vulnerabilities in the hosts scanned
- BVulnerability scanners can help identify out-of-date software versions, missing patches, or system
upgrades - CThey can validate compliance with or deviations from the organization's security policy
- DVulnerability scanners can identify weakness and automatically fix and patch the vulnerabilities without user intervention
28How does traceroute map the route a packet travels from point A to point B?
- AUses a TCP timestamp packet that will elicit a time exceeded in transit message
- BManipulates the value of the time to live (TTL) within packet to elicit a time exceeded in transit message
- CUses a protocol that will be rejected by gateways on its way to the destination
- DManipulates the flags within packets to force gateways into generating error messages
29How do you defend against DHCP Starvation attack?

- AEnable ARP-Block on the switch
- BEnable DHCP snooping on the switch
- CConfigure DHCP-BLOCK to 1 on the switch
- DInstall DHCP filters on the switch to block this attack
30What type of session hijacking attack is shown in the exhibit?

- ACross-site scripting Attack
- BSQL Injection Attack
- CToken sniffing Attack
- DSession Fixation Attack
31The SYN flood attack sends TCP connections requests faster than a machine can process them.
Attacker creates a random source address for each packet
SYN flag set in each packet is a request to open a new connection to the server from the spoofed IP
address
Victim responds to spoofed IP address, then waits for confirmation that never arrives (timeout wait is
about 3 minutes)
Victim's connection table fills up waiting for replies and ignores new connections
Legitimate users are ignored and will not be able to access the server
How do you protect your network against SYN Flood attacks?- ASYN cookies. Instead of allocating a record, send a SYN-ACK with a carefully constructed sequence
number generated as a hash of the clients IP address, port number, and other information. When the
client responds with a normal ACK, that special sequence number will be included, which the server
then verifies. Thus, the server first allocates memory on the third packet of the handshake, not the first - BRST cookies - The server sends a wrong SYN/ACK back to the client. The client should then generate a
RST packet telling the server that something is wrong. At this point, the server knows the client is valid
and will now accept incoming connections from that client normally - CCheck the incoming packet's IP address with the SPAM database on the Internet and enable the filter
using ACLs at the Firewall - DStack Tweaking. TCP stacks can be tweaked in order to reduce the effect of SYN floods.
Reduce the timeout before a stack frees up the memory allocated for a connection - EMicro Blocks. Instead of allocating a complete connection, simply allocate a micro record of 16- bytes
for the incoming SYN object
- ASYN cookies. Instead of allocating a record, send a SYN-ACK with a carefully constructed sequence
32What type of port scan is shown below?

- AIdle Scan
- BFIN Scan
- CXMAS Scan
- DWindows Scan
33Stephanie works as a records clerk in a large office building in downtown Chicago. On Monday, she went to
a mandatory security awareness class (Security5) put on by her company's IT department. During the
class, the IT department informed all employees that everyone's Internet activity was thenceforth going to
be monitored.
Stephanie is worried that her Internet activity might give her supervisor reason to write her up, or worse get
her fired. Stephanie's daily work duties only consume about four hours of her time, so she usually spends
the rest of the day surfing the web. Stephanie really enjoys surfing the Internet but definitely does not want
to get fired for it.
What should Stephanie use so that she does not get in trouble for surfing the Internet?- AStealth IE
- BStealth Anonymizer
- CStealth Firefox
- DCookie Disabler
34Neil is a network administrator working in Istanbul. Neil wants to setup a protocol analyzer on his network
that will receive a copy of every packet that passes through the main office switch. What type of port will
Neil need to setup in order to accomplish this?- ANeil will have to configure a Bridged port that will copy all packets to the protocol analyzer
- BNeil will need to setup SPAN port that will copy all network traffic to the protocol analyzer.
- CHe will have to setup an Ether channel port to get a copy of all network traffic to the analyzer
- DHe should setup a MODS port which will copy all network traffic.
35In TCP communications there are 8 flags; FIN, SYN, RST, PSH, ACK, URG, ECE, CWR. These flags have
decimal numbers assigned to them:
FIN = 1
SYN = 2
RST = 4
PSH = 8
ACK = 16
URG = 32
ECE = 64
CWR = 128
Jason is the security administrator of ASPEN Communications. He analyzes some traffic using Wireshark
and has enabled the following filters.
What is Jason trying to accomplish here?
- ASYN, FIN, URG and PSH
- BSYN, SYN/ACK, ACK
- CRST, PSH/URG, FIN
- DACK, ACK, SYN, URG
36Jayden is a network administrator for her company. Jayden wants to prevent MAC spoofing on all the Cisco
switches in the network. How can she accomplish this?- AJayden can use the commanD. ip binding set.
- BJayden can use the commanD. no ip spoofing.
- CShe should use the commanD. no dhcp spoofing
- DShe can use the commanD. ip dhcp snooping binding.
37Peter extracts the SID list from Windows 2008 Server machine using the hacking tool "SIDExtracter". Here
is the output of the SIDs: From the above list identify the user account with System Administrator privileges?
- AJohn
- BRebecca
- CSheela
- DShawn
- ESomia
- FChang
- GMicah
38What is the problem with this ASP script (login.asp)?

- AThe ASP script is vulnerable to Cross Site Scripting attack
- BThe ASP script is vulnerable to Session Splice attack
- CThe ASP script is vulnerable to XSS attack
- DThe ASP script is vulnerable to SQL Injection attack
39Google uses a unique cookie for each browser used by an individual user on a computer. This cookie
contains information that allows Google to identify records about that user on its database. This cookie is
submitted every time a user launches a Google search, visits a site using AdSense etc. The information
stored in Google's database, identified by the cookie, includes
- Everything you search for using Google
- Every web page you visit that has Google Adsense ads
How would you prevent Google from storing your search keywords?- ABlock Google Cookie by applying Privacy and Security settings in your web browser
- BDisable the Google cookie using Google Advanced Search settings on Google Search page
- CDo not use Google but use another search engine Bing which will not collect and store your search
keywords - DUse MAC OS X instead of Windows 7. Mac OS has higher level of privacy controls by default.
40How many bits encryption does SHA-1 use?
- A64 bits
- B128 bits
- C256 bits
- D160 bits
41In Trojan terminology, what is required to create the executable file chess.exe as shown below?

- AMixer
- BConverter
- CWrapper
- DZipper
42Syslog is a standard for logging program messages. It allows separation of the software that generates
messages from the system that stores them and the software that reports and analyzes them. It also
provides devices, which would otherwise be unable to communicate a means to notify administrators of
problems or performance.
What default port Syslog daemon listens on?
- A242
- B312
- C416
- D514
43This attack uses social engineering techniques to trick users into accessing a fake Web site and divulging
personal information. Attackers send a legitimate-looking e-mail asking users to update their information on
the company's Web site, but the URLs in the e-mail actually point to a false Web site.- AWiresharp attack
- BSwitch and bait attack
- CPhishing attack
- DMan-in-the-Middle attack
44Which of the following statements would NOT be a proper definition for a Trojan Horse?
- AAn authorized program that has been designed to capture keyboard keystroke while the user is unaware of such activity being performed
- BAn unauthorized program contained within a legitimate program. This unauthorized program performs functions unknown (and probably unwanted) by the user
- CA legitimate program that has been altered by the placement of unauthorized code within it; this code
performs functions unknown (and probably unwanted) by the user - DAny program that appears to perform a desirable and necessary function but that (because of
unauthorized code within it that is unknown to the user) performs functions unknown (and definitely
unwanted) by the user
45What is the correct command to run Netcat on a server using port 56 that spawns command shell when
connected?
- Anc -port 56 -s cmd.exe
- Bnc -p 56 -p -e shell.exe
- Cnc -r 56 -c cmd.exe
- Dnc -L 56 -t -e cmd.exe
46SNMP is a connectionless protocol that uses UDP instead of TCP packets (True or False)
- ATrue
- BFalse
47TCP/IP Session Hijacking is carried out in which OSI layer?
- ADatalink layer
- BTransport layer
- CNetwork layer
- DPhysical layer
48In which part of OSI layer, ARP Poisoning occurs?
- ATransport Layer
- BDatalink Layer
- CPhysical Layer
- DApplication layer
49You want to hide a secret.txt document inside c:\windows\system32\tcpip.dll kernel library using ADS
streams. How will you accomplish this?- Acopy secret.txt c:\windows\system32\tcpip.dll kernel>secret.txt
- Bcopy secret.txt c:\windows\system32\tcpip.dll:secret.txt
- Ccopy secret.txt c:\windows\system32\tcpip.dll |secret.txt
- Dcopy secret.txt >< c:\windows\system32\tcpip.dll kernel secret.txt
50You just purchased the latest DELL computer, which comes pre-installed with Windows 7, McAfee antivirus
software and a host of other applications. You want to connect Ethernet wire to your cable modem and start
using the computer immediately. Windows is dangerously insecure when unpacked from the box, and there
are a few things that you must do before you use it.- ANew installation of Windows should be patched by installing the latest service packs and hotfixes
- BKey applications such as Adobe Acrobat, Macromedia Flash, Java, Winzip etc., must have the latest
security patches installed - CInstall a personal firewall and lock down unused ports from connecting to your computer
- DInstall the latest signatures for Antivirus software
- EConfigure "Windows Update" to automatic
- FCreate a non-admin user with a complex password and logon to this account
- GYou can start using your computer as vendors such as DELL, HP and IBM would have already installed
the latest service packs.
51In the context of Trojans, what is the definition of a Wrapper?
- AAn encryption tool to protect the Trojan
- BA tool used to bind the Trojan with a legitimate file
- Ctool used to calculate bandwidth and CPU cycles wasted by the Trojan
- DA tool used to encapsulate packets within a new header and footer
52Your computer is infected by E-mail tracking and spying Trojan. This Trojan infects the computer with a
single file - emos.sys
Which step would you perform to detect this type of Trojan?
- AScan for suspicious startup programs using msconfig
- BScan for suspicious network activities using Wireshark
- CScan for suspicious device drivers in c:\windows\system32\drivers
- DScan for suspicious open ports using netstat
53Which type of hacker represents the highest risk to your network?
- Ablack hat hackers
- Bgrey hat hackers
- Cdisgruntled employees
- Dscript kiddies
54Shayla is an IT security consultant, specializing in social engineering and external penetration tests. Shayla
has been hired on by Treks Avionics, a subcontractor for the Department of Defense. Shayla has been
given authority to perform any and all tests necessary to audit the company's network security.
No employees for the company, other than the IT director, know about Shayla's work she will be doing.
Shayla's first step is to obtain a list of employees through company website contact pages. Then she
befriends a female employee of the company through an online chat website. After meeting with the female
employee numerous times, Shayla is able to gain her trust and they become friends. One day, Shayla
steals the employee's access badge and uses it to gain unauthorized access to the Treks Avionics offices.
What type of insider threat would Shayla be considered?- AShe would be considered an Insider Affiliate
- BBecause she does not have any legal access herself, Shayla would be considered an Outside Affiliate
- CShayla is an Insider Associate since she has befriended an actual employee
- DSince Shayla obtained access with a legitimate company badge; she would be considered a Pure
Insider
55What port number is used by Kerberos protocol?
- A88
- B44
- C487
- D419
56What does FIN in TCP flag define?
- AUsed to abort a TCP connection abruptly
- BUsed to close a TCP connection
- CUsed to acknowledge receipt of a previous packet or transmission
- DUsed to indicate the beginning of a TCP connection
57Annie has just succeeded in stealing a secure cookie via a XSS attack. She is able to replay the cookie
even while the session is invalid on the server. Why do you think this is possible?- AIt works because encryption is performed at the application layer (single encryption key)
- BThe scenario is invalid as a secure cookie cannot be replayed
- CIt works because encryption is performed at the network layer (layer 1 encryption)
- DAny cookie can be replayed irrespective of the session status
58This attack technique is used when a Web application is vulnerable to an SQL Injection but the results of
the Injection are not visible to the attacker.- AUnique SQL Injection
- BBlind SQL Injection
- CGeneric SQL Injection
- DDouble SQL Injection
59A common technique for luring e-mail users into opening virus-launching attachments is to send messages
that would appear to be relevant or important to many of their potential recipients. One way of
accomplishing this feat is to make the virus-carrying messages appear to come from some type of business
entity retailing sites, UPS, FEDEX, CITIBANK or a major provider of a common service.
Here is a fraudulent e-mail claiming to be from FedEx regarding a package that could not be delivered. This
mail asks the receiver to open an attachment in order to obtain the FEDEX tracking number for picking up
the package. The attachment contained in this type of e-mail activates a virus.
Vendors send e-mails like this to their customers advising them not to open any files attached with the mail,
as they do not include attachments.
Fraudulent e-mail and legit e-mail that arrives in your inbox contain the fedex.com as the sender of the mail.
How do you ensure if the e-mail is authentic and sent from fedex.com?
- AVerify the digital signature attached with the mail, the fake mail will not have Digital ID at all
- BCheck the Sender ID against the National Spam Database (NSD)
- CFake mail will have spelling/grammatical errors
- DFake mail uses extensive images, animation and flash content
60What file system vulnerability does the following command take advantage of? type c:\anyfile.exe > c:\winnt
\system32\calc.exe:anyfile.exe- AHFS
- BBackdoor access
- CXFS
- DADS
61You are the Security Administrator of Xtrinity, Inc. You write security policies and conduct assessments to
protect the company's network. During one of your periodic checks to see how well policy is being observed
by the employees, you discover an employee has attached cell phone 3G modem to his telephone line and
workstation. He has used this cell phone 3G modem to dial in to his workstation, thereby bypassing your
firewall. A security breach has occurred as a direct result of this activity. The employee explains that he
used the modem because he had to download software for a department project. How would you resolve
this situation?- AReconfigure the firewall
- BEnforce the corporate security policy
- CInstall a network-based IDS
- DConduct a needs analysis
62In what stage of Virus life does a stealth virus gets activated with the user performing certain actions such
as running an infected program?- ADesign
- BElimination
- CIncorporation
- DReplication
- ELaunch
- FDetection
63What is a sniffing performed on a switched network called?
- ASpoofed sniffing
- BPassive sniffing
- CDirect sniffing
- DActive sniffing
64A rootkit is a collection of tools (programs) that enable administrator-level access to a computer. This
program hides itself deep into an operating system for malicious activity and is extremely difficult to detect.
The malicious software operates in a stealth fashion by hiding its files, processes and registry keys and
may be used to create a hidden directory or folder designed to keep out of view from a user's operating
system and security software
What privilege level does a rootkit require to infect successfully on a Victim's machine?
- AUser level privileges
- BRing 3 Privileges
- CSystem level privileges
- DKernel level privileges
65Which Steganography technique uses Whitespace to hide secret messages?
- Asnow
- Bbeetle
- Cmagnet
- Dcat
66Cyber Criminals have long employed the tactic of masking their true identity. In IP spoofing, an attacker
gains unauthorized access to a computer or a network by making it appear that a malicious message has
come from a trusted machine, by "spoofing" the IP address of that machine.
How would you detect IP spoofing?- ACheck the IPID of the spoofed packet and compare it with TLC checksum. If the numbers match then it
is spoofed packet - BProbe a SYN Scan on the claimed host and look for a response SYN/FIN packet, if the connection
completes then it is a spoofed packet - CTurn on 'Enable Spoofed IP Detection' in Wireshark, you will see a flag tick if the packet is spoofed
- DSending a packet to the claimed host will result in a reply. If the TTL in the reply is not the same as the
packet being checked then it is a spoofed packet
- ACheck the IPID of the spoofed packet and compare it with TLC checksum. If the numbers match then it
67David is a security administrator working in Boston. David has been asked by the office's manager to block
all POP3 traffic at the firewall because he believes employees are spending too much time reading
personal email. How can David block POP3 at the firewall?- ADavid can block port 125 at the firewall
- BDavid can block all EHLO requests that originate from inside the office
- CDavid can stop POP3 traffic by blocking all HELO requests that originate from inside the office.
- DDavid can block port 110 to block all POP3 traffic.
68You want to capture Facebook website traffic in Wireshark. What display filter should you use that shows all
TCP packets that contain the word 'facebook'?- Adisplay==facebook
- Btraffic.content==facebook
- Ctcp contains facebook
- Dlist.display.facebook
69XSS attacks occur on Web pages that do not perform appropriate bounds checking on data entered by
users. Characters like < > that mark the beginning/end of a tag should be converted into HTML entities.
What is the correct code when converted to html entities?
- AOption A
- BOption B
- COption C
- DOption D
70Most cases of insider abuse can be traced to individuals who are introverted, incapable of dealing with
stress or conflict, and frustrated with their job, office politics, and lack of respect or promotion. Disgruntled
employees may pass company secrets and intellectual property to competitors for monitory benefits.
Here are some of the symptoms of a disgruntled employee:- AFrequently leaves work early, arrive late or call in sick
- BSpends time surfing the Internet or on the phone
- CResponds in a confrontational, angry, or overly aggressive way to simple requests or comments
- DAlways negative; finds fault with everything
These disgruntled employees are the biggest threat to enterprise security. How do you deal with these threats? (Select 2 answers) - ELimit access to the applications they can run on their desktop computers and enforce strict work hour
rules - FBy implementing Virtualization technology from the desktop to the data centre, organizations can isolate
different environments with varying levels of access and security to various employees - GOrganizations must ensure that their corporate data is centrally managed and delivered to users just
and when needed - HLimit Internet access, e-mail communications, access to social networking sites and job hunting portals
71Fake Anti-Virus, is one of the most frequently encountered and persistent threats on the web. This malware
uses social engineering to lure users into infected websites with a technique called Search Engine
Optimization.
Once the Fake AV is downloaded into the user's computer, the software will scare them into believing their
system is infected with threats that do not really exist, and then push users to purchase services to clean up
the non-existent threats.
The Fake AntiVirus will continue to send these annoying and intrusive alerts until a payment is made.
What is the risk of installing Fake AntiVirus?
- AVictim's Operating System versions, services running and applications installed will be published on
Blogs and Forums - BVictim's personally identifiable information such as billing address and credit card details, may be
extracted and exploited by the attacker - COnce infected, the computer will be unable to boot and the Trojan will attempt to format the hard disk
- DDenial of Service attack will be launched against the infected computer crashing other machines on the connected network
- AVictim's Operating System versions, services running and applications installed will be published on
72How would you describe an attack where an attacker attempts to deliver the payload over multiple packets
over long periods of time with the purpose of defeating simple pattern matching in IDS systems without
session reconstruction? A characteristic of this attack would be a continuous stream of small packets.- ASession Hijacking
- BSession Stealing
- CSession Splicing
- DSession Fragmentation
73Jake works as a system administrator at Acme Corp. Jason, an accountant of the firm befriends him at the
canteen and tags along with him on the pretext of appraising him about potential tax benefits. Jason waits
for Jake to swipe his access card and follows him through the open door into the secure systems area. How
would you describe Jason's behavior within a security context?- ASmooth Talking
- BSwipe Gating
- CTailgating
- DTrailing
74While performing a ping sweep of a local subnet you receive an ICMP reply of Code 3/Type 13 for all the
pings you have sent out. What is the most likely cause of this?- AThe firewall is dropping the packets
- BAn in-line IDS is dropping the packets
- CA router is blocking ICMP
- DThe host does not respond to ICMP packets
75Consider the following code:
URL:http://www.certified.com/search.pl?text=<script>alert(document.cookie)</script>
If an attacker can trick a victim user to click a link like this, and the Web application does not validate input,
then the victim's browser will pop up an alert showing the users current set of cookies. An attacker can do
much more damage, including stealing passwords, resetting your home page, or redirecting the user to
another Web site.
What is the countermeasure against XSS scripting?- ACreate an IP access list and restrict connections based on port number
- BReplace "<" and ">" characters with "& l t;" and "& g t;" using server scripts
- CDisable Javascript in IE and Firefox browsers
- DConnect to the server using HTTPS protocol instead of HTTP
76Samuel is the network administrator of DataX Communications, Inc. He is trying to configure his firewall to
block password brute force attempts on his network. He enables blocking the intruder's IP address for a
period of 24 hours' time after more than three unsuccessful attempts. He is confident that this rule will
secure his network from hackers on the Internet.
But he still receives hundreds of thousands brute-force attempts generated from various IP addresses
around the world. After some investigation he realizes that the intruders are using a proxy somewhere else
on the Internet which has been scripted to enable the random usage of various proxies on each request so
as not to get caught by the firewall rule.
Later he adds another rule to his firewall and enables small sleep on the password attempt so that if the
password is incorrect, it would take 45 seconds to return to the user to begin another attempt. Since an
intruder may use multiple machines to brute force the password, he also throttles the number of
connections that will be prepared to accept from a particular IP address.
This action will slow the intruder's attempts.
Samuel wants to completely block hackers brute force attempts on his network.
What are the alternatives to defending against possible brute-force password attacks on his site?- AEnforce a password policy and use account lockouts after three wrong logon attempts even though this might lock out legit users
- BEnable the IDS to monitor the intrusion attempts and alert you by e-mail about the IP address of the intruder so that you can block them at the Firewall manually
- CEnforce complex password policy on your network so that passwords are more difficult to brute force
- DYou cannot completely block the intruders attempt if they constantly switch proxies
77What type of Trojan is this?

- ARAT Trojan
- BE-Mail Trojan
- CDefacement Trojan
- DDestructing Trojan
- EDenial of Service Trojan
78Maintaining a secure Web server requires constant effort, resources, and vigilance from an organization.
Securely administering a Web server on a daily basis is an essential aspect of Web server security.
Maintaining the security of a Web server will usually involve the following steps:
1. Configuring, protecting, and analyzing log files
2. Backing up critical information frequently
3. Maintaining a protected authoritative copy of the organization's Web content
4. Establishing and following procedures for recovering from compromise
5. Testing and applying patches in a timely manner
6. Testing security periodically.
In which step would you engage a forensic investigator?- A1
- B2
- C3
- D4
- E5
- F6
79In Buffer Overflow exploit, which of the following registers gets overwritten with return address of the exploit
code?- AEEP
- BESP
- CEAP
- DEIP
80Web servers often contain directories that do not need to be indexed. You create a text file with search
engine indexing restrictions and place it on the root directory of the Web Server.
User-agent: *
Disallow: /images/
Disallow: /banners/
Disallow: /Forms/
Disallow: /Dictionary/
Disallow: /_borders/
Disallow: /_fpclass/
Disallow: /_overlay/
Disallow: /_private/
Disallow: /_themes/
What is the name of this file?- Arobots.txt
- Bsearch.txt
- Cblocklist.txt
- Dspf.txt
81An attacker has successfully compromised a remote computer. Which of the following comes as one of the
last steps that should be taken to ensure that the compromise cannot be traced back to the source of the
problem?- AInstall patches
- BSetup a backdoor
- CInstall a zombie for DDOS
- DCover your tracks
82Attackers target HINFO record types stored on a DNS server to enumerate information. These are
information records and potential source for reconnaissance. A network administrator has the option of
entering host information specifically the CPU type and operating system when creating a new DNS record.
An attacker can extract this type of information easily from a DNS server.
Which of the following commands extracts the HINFO record?
- AOption A
- BOption B
- COption C
- DOption D
83Bret is a web application administrator and has just read that there are a number of surprisingly common
web application vulnerabilities that can be exploited by unsophisticated attackers with easily available tools
on the Internet. He has also read that when an organization deploys a web application, they invite the world
to send HTTP requests. Attacks buried in these requests sail past firewalls, filters, platform hardening, SSL,
and IDS without notice because they are inside legal HTTP requests. Bret is determined to weed out
vulnerabilities.
What are some of the common vulnerabilities in web applications that he should be concerned about?- ANon-validated parameters, broken access control, broken account and session management, cross-site scripting and buffer overflows are just a few common vulnerabilities
- BVisible clear text passwords, anonymous user account set as default, missing latest security patch, no
firewall filters set and no SSL configured are just a few common vulnerabilities - CNo SSL configured, anonymous user account set as default, missing latest security patch, no firewall
filters set and an inattentive system administrator are just a few common vulnerabilities - DNo IDS configured, anonymous user account set as default, missing latest security patch, no firewall
filters set and visible clear text passwords are just a few common vulnerabilities
84What is War Dialing?
- AWar dialing involves the use of a program in conjunction with a modem to penetrate the modem/PBXbased systems
- BWar dialing is a vulnerability scanning technique that penetrates Firewalls
- CIt is a social engineering technique that uses Phone calls to trick victims
- DInvolves IDS Scanning Fragments to bypass Internet filters and stateful Firewalls
85Steven the hacker realizes the network administrator of Acme Corporation is using syskey in Windows
2008 Server to protect his resources in the organization. Syskey independently encrypts the hashes so that
physical access to the server, tapes, or ERDs is only first step to cracking the passwords. Steven must
break through the encryption used by syskey before he can attempt to use brute force dictionary attacks on
the hashes. Steven runs a program called "SysCracker" targeting the Windows 2008 Server machine in
attempting to crack the hash used by Syskey. He needs to configure the encryption level before he can
launch the attack. How many bits does Syskey use for encryption?- A40-bit encryption
- B128-bit encryption
- C256-bit encryption
- D64-bit encryption
86Bob waits near a secured door, holding a box. He waits until an employee walks up to the secured door and
uses the special card in order to access the restricted area of the target company. Just as the employee
opens the door, Bob walks up to the employee (still holding the box) and asks the employee to hold the
door open so that he can enter. What is the best way to undermine the social engineering activity of
tailgating?- AIssue special cards to access secure doors at the company and provide a one-time only brief
description of use of the special card - BEducate and enforce physical security policies of the company to all the employees on a regular basis
- CSetup a mock video camera next to the special card reader adjacent to the secure door
- DPost a sign that states, "no tailgating" next to the special card reader adjacent to the secure door
- AIssue special cards to access secure doors at the company and provide a one-time only brief
87Ursula is a college student at a University in Amsterdam. Ursula originally went to college to study
engineering but later changed to marine biology after spending a month at sea with her friends. These
friends frequently go out to sea to follow and harass fishing fleets that illegally fish in foreign waters. Ursula
eventually wants to put companies practicing illegal fishing out of business. Ursula decides to hack into the
parent company's computers and destroy critical data knowing fully well that, if caught, she probably would
be sent to jail for a very long time. What would Ursula be considered?- AUrsula would be considered a gray hat since she is performing an act against illegal activities.
- BShe would be considered a suicide hacker.
- CShe would be called a cracker
- DUrsula would be considered a black hat
88Attacking well-known system defaults is one of the most common hacker attacks. Most software is shipped
with a default configuration that makes it easy to install and setup the application. You should change the
default settings to secure the system.
Which of the following is NOT an example of default installation?- AMany systems come with default user accounts with well-known passwords that administrators forget to change
- BOften, the default location of installation files can be exploited which allows a hacker to retrieve a file
from the system - CMany software packages come with "samples" that can be exploited, such as the sample programs on
IIS web services - DEnabling firewall and anti-virus software on the local system
89This tool is widely used for ARP Poisoning attack. Name the tool.

- ACain and Able
- BBeat Infector
- CPoison Ivy
- DWebarp Infector
90BankerFox is a Trojan that is designed to steal users' banking data related to certain banking entities.
When they access any website of the affected banks through the vulnerable Firefox 3.5 browser, the Trojan
is activated and logs the information entered by the user. All the information entered in that website will be
logged by the Trojan and transmitted to the attacker's machine using covert channel.
BankerFox does not spread automatically using its own means. It needs an attacking user's intervention in
order to reach the affected computer.
What is the most efficient way an attacker located in remote location to infect this banking Trojan on a
victim's machine?
- APhysical access - the attacker can simply copy a Trojan horse to a victim's hard disk infecting the
machine via Firefox add-on extensions - BCustom packaging - the attacker can create a custom Trojan horse that mimics the appearance of a
program that is unique to that particular computer - CDownloading software from a website? An attacker can offer free software, such as shareware
programs and pirated mp3 files
- APhysical access - the attacker can simply copy a Trojan horse to a victim's hard disk infecting the
91In the context of password security: a simple dictionary attack involves loading a dictionary file (a text file full
of dictionary words) into a cracking application such as L0phtCrack or John the Ripper, and running it
against user accounts located by the application. The larger the word and word fragment selection, the
more effective the dictionary attack is. The brute force method is the most inclusive - though slow. Usually,
it tries every possible letter and number combination in its automated exploration. If you would use both
brute force and dictionary combined together to have variations of words, what would you call such an
attack?- AFull Blown Attack
- BThorough Attack
- CHybrid Attack
- DBruteDict Attack
92You receive an e-mail with the following text message.
"Microsoft and HP today warned all customers that a new, highly dangerous virus has been discovered
which will erase all your files at midnight. If there's a file called hidserv.exe on your computer, you have
been infected and your computer is now running a hidden server that allows hackers to access your
computer. Delete the file immediately. Please also pass this message to all your friends and colleagues as
soon as possible."
You launch your antivirus software and scan the suspicious looking file hidserv.exe located in
c:\windows directory and the AV comes out clean meaning the file is not infected. You view the file
signature and confirm that it is a legitimate Windows system file "Human Interface Device Service".
What category of virus is this?- AVirus hoax
- BSpooky Virus
- CStealth Virus
- DPolymorphic Virus
93Choose one of the following pseudo codes to describe this statement:
"If we have written 200 characters to the buffer variable, the stack should stop because it cannot hold any
more data."- AIf (I > 200) then exit (1)
- BIf (I < 200) then exit (1)
- CIf (I <= 200) then exit (1)
- DIf (I >= 200) then exit (1)
94One of the effective DoS/DDoS countermeasures is 'Throttling'. Which statement correctly defines this
term?- ASet up routers that access a server with logic to adjust incoming traffic to levels that will be safe for the
server to process - BProviders can increase the bandwidth on critical connections to prevent them from going down in the
event of an attack - CReplicating servers that can provide additional failsafe protection
- DLoad balance each server in a multiple-server architecture
- ASet up routers that access a server with logic to adjust incoming traffic to levels that will be safe for the
95Attackers footprint target Websites using Google Hacking techniques. Google hacking is a term that refers
to the art of creating complex search engine queries. It detects websites that are vulnerable to numerous
exploits and vulnerabilities. Google operators are used to locate specific strings of text within the search
results.
The configuration file contains both a username and a password for an SQL database. Most sites with
forums run a PHP message base. This file gives you the keys to that forum, including FULL ADMIN access
to the database. WordPress uses config.php that stores the database Username and Password.
Which of the below Google search string brings up sites with "config.php" files?- ASearch:index config/php
- BWordpress:index config.php
- Cintitle:index.of config.php
- DConfig.php:index list
96Which of the following tool would be considered as Signature Integrity Verifier (SIV)?
- ANmap
- BSNORT
- CVirusSCAN
- DTripwire
97Bob has set up three web servers on Windows Server 2008 IIS 7.0. Bob has followed all the
recommendations for securing the operating system and IIS. These servers are going to run numerous ecommerce
websites that are projected to bring in thousands of dollars a day. Bob is still concerned about
the security of these servers because of the potential for financial loss. Bob has asked his company's
firewall administrator to set the firewall to inspect all incoming traffic on ports 80 and 443 to ensure that no
malicious data is getting into the network.
Why will this not be possible?- AFirewalls cannot inspect traffic coming through port 443
- BFirewalls can only inspect outbound traffic
- CFirewalls cannot inspect traffic at all, they can only block or allow certain ports
- DFirewalls cannot inspect traffic coming through port 80
98Which of the following statement correctly defines ICMP Flood Attack? (Select 2 answers)

- ABogus ECHO reply packets are flooded on the network spoofing the IP and MAC address
- BThe ICMP packets signal the victim system to reply and the combination of traffic saturates the
bandwidth of the victim's network - CECHO packets are flooded on the network saturating the bandwidth of the subnet causing denial of
service - DA DDoS ICMP flood attack occurs when the zombies send large volumes of ICMP_ECHO_REPLY
packets to the victim system.
99Which type of scan does NOT open a full TCP connection?
- AStealth Scan
- BXMAS Scan
- CNull Scan
- DFIN Scan
100Lori was performing an audit of her company's internal Sharepoint pages when she came across the
following codE. What is the purpose of this code?
- AThis JavaScript code will use a Web Bug to send information back to another server.
- BThis code snippet will send a message to a server at 192.154.124.55 whenever the "escape" key is
pressed. - CThis code will log all keystrokes
- DThis bit of JavaScript code will place a specific image on every page of the RSS feed
101What sequence of packets is sent during the initial TCP three-way handshake?
- ASYN, SYN-ACK, ACK
- BSYN, URG, ACK
- CSYN, ACK, SYN-ACK
- DFIN, FIN-ACK, ACK
102Steve scans the network for SNMP enabled devices. Which port number Steve should scan?
- A150
- B161
- C169
- D69
103You are footprinting an organization and gathering competitive intelligence. You visit the company's website
for contact information and telephone numbers but do not find them listed there. You know they had the
entire staff directory listed on their website 12 months ago but now it is not there. Is there any way you can
retrieve information from a website that is outdated?- AVisit Google's search engine and view the cached copy
- BCrawl the entire website and store them into your computer
- CVisit Archive.org web site to retrieve the Internet archive of the company's website
- DVisit the company's partners and customers website for this information
104You are the CIO for Avantes Finance International, a global finance company based in Geneva. You are
responsible for network functions and logical security throughout the entire corporation. Your company has
over 250 servers running Windows Server, 5000 workstations running Windows Vista, and 200 mobile
users working from laptops on Windows 7.
Last week, 10 of your company's laptops were stolen from salesmen while at a conference in Amsterdam.
These laptops contained proprietary company information. While doing damage assessment on the
possible public relations nightmare this may become, a news story leaks about the stolen laptops and also
that sensitive information from those computers was posted to a blog online.
What built-in Windows feature could you have implemented to protect the sensitive information on these
laptops?- AYou should have used 3DES which is built into Windows
- BIf you would have implemented Pretty Good Privacy (PGP) which is built into Windows, the sensitive
information on the laptops would not have leaked out - CYou should have utilized the built-in feature of Distributed File System (DFS) to protect the sensitive
information on the laptops - DYou could have implemented Encrypted File System (EFS) to encrypt the sensitive files on the laptops
105A Trojan horse is a destructive program that masquerades as a benign application. The software initially
appears to perform a desirable function for the user prior to installation and/or execution, but in addition to
the expected function steals information or harms the system.
The challenge for an attacker is to send a convincing file attachment to the victim, which gets easily
executed on the victim machine without raising any suspicion. Today's end users are quite knowledgeable
about malwares and viruses. Instead of sending games and fun executables, Hackers today are quite
successful in spreading the Trojans using Rogue security software.
What is Rogue security software?
- AA flash file extension to Firefox that gets automatically installed when a victim visits rogue software
disabling websites - BA Fake AV program that claims to rid a computer of malware, but instead installs spyware or other
malware onto the computer. This kind of software is known as rogue security software - CRogue security software is based on social engineering technique in which the attackers lures victim to
visit spear phishing websites - DThis software disables firewalls and establishes reverse connecting tunnel between the victim's
machine and that of the attacker
- AA flash file extension to Firefox that gets automatically installed when a victim visits rogue software
106Which of the following is NOT part of CEH Scanning Methodology?
- ACheck for Live systems
- BCheck for Open Ports
- CBanner Grabbing
- DPrepare Proxies
- ESocial Engineering attacks
- FScan for Vulnerabilities
- GDraw Network Diagrams
107Lee is using Wireshark to log traffic on his network. He notices a number of packets being directed to an
internal IP from an outside IP where the packets are ICMP and their size is around 65, 536 bytes. What is
Lee seeing here?- ALee is seeing activity indicative of a Smurf attack
- BMost likely, the ICMP packets are being sent in this manner to attempt IP spoofing
- CLee is seeing a Ping of death attack
- DThis is not unusual traffic, ICMP packets can be of any size.
108This method is used to determine the Operating system and version running on a remote target system.
What is it called?- AService Degradation
- BOS Fingerprinting
- CManual Target System
- DIdentification Scanning
109William has received a Chess game from someone in his computer programming class through email.
William does not really know the person who sent the game very well, but decides to install the game
anyway because he really likes Chess.
After William installs the game, he plays it for a couple of hours. The next day, William plays the Chess
game again and notices that his machine has begun to slow down. He brings up his Task Manager and
sees the following programs running:
What has William just installed?
- AZombie Zapper (ZoZ)
- BRemote Access Trojan (RAT)
- CBot IRC Tunnel (BIT)
- DRoot Digger (RD)
110John the hacker is sniffing the network to inject ARP packets. He injects broadcast frames onto the wire to
conduct MiTM attack. What is the destination MAC address of a broadcast frame?- A0xFFFFFFFFFFFF
- B0xDDDDDDDDDDDD
- C0xAAAAAAAAAAAA
- D0xBBBBBBBBBBBB
111You are gathering competitive intelligence on an organization. You notice that they have jobs listed on a few
Internet job-hunting sites. There are two jobs for network and system administrators. How can this help you
in foot printing the organization?- ATo learn about the IP range used by the target network
- BTo identify the number of employees working for the company
- CTo test the limits of the corporate security policy enforced in the company
- DTo learn about the operating systems, services and applications used on the network
112TCP packets transmitted in either direction after the initial three-way handshake will have which of the
following bit set?- ASYN flag
- BACK flag
- CFIN flag
- DXMAS flag
113The programmers on your team are analyzing the free, open source software being used to run FTP
services on a server in your organization. They notice that there is excessive number of functions in the
source code that might lead to buffer overflow. These C++ functions do not check bounds. Identify the line
in the source code that might lead to buffer overflow?
- A9A.9
- B17B.17
- C20C.20
- D32D.32
- E35E.35
114What framework architecture is shown in this exhibit?

- ACore Impact
- BMetasploit
- CImmunity Canvas
- DNessus
115Which of the following steganography utilities exploits the nature of white space and allows the user to
conceal information in these white spaces?- AImage Hide
- BSnow
- CGif-It-Up
- DNiceText
116You have chosen a 22 character word from the dictionary as your password. How long will it take to crack
the password by an attacker?- A16 million years
- B5 minutes
- C23 days
- D200 years
117While testing web applications, you attempt to insert the following test script into the search area on the
company's web site:
<script>alert('Testing Testing Testing')</script>
Later, when you press the search button, a pop up box appears on your screen with the text "Testing
Testing Testing". What vulnerability is detected in the web application here?- ACross Site Scripting
- BPassword attacks
- CA Buffer Overflow
- DA hybrid attack
118What techniques would you use to evade IDS during a Port Scan? (Select 4 answers)
- AUse fragmented IP packets
- BSpoof your IP address when launching attacks and sniff responses from the server
- COverload the IDS with Junk traffic to mask your scan
- DUse source routing (if possible)
- EConnect to proxy servers or compromised Trojaned machines to launch attacks
119serious financial losses. He planned the attack carefully and carried out the attack at the appropriate
moment.
Meanwhile, Trent, an administrator at Brownies Inc., realized that their main financial transaction server had
been attacked. As a result of the attack, the server crashed and Trent needed to reboot the system, as no
one was able to access the resources of the company. This process involves human interaction to fix it.
What kind of Denial of Service attack was best illustrated in the scenario above?- ASimple DDoS attack
- BDoS attacks which involves flooding a network or system
- CDoS attacks which involves crashing a network or system
- DDoS attacks which is done accidentally or deliberately
120Johnny is a member of the hacking group Orpheus1. He is currently working on breaking into the
Department of Defense's front end Exchange Server. He was able to get into the server, located in a DMZ,
by using an unused service account that had a very weak password that he was able to guess. Johnny
wants to crack the administrator password, but does not have a lot of time to crack it. He wants to use a
tool that already has the LM hashes computed for all possible permutations of the administrator password.
What tool would be best used to accomplish this?- ASMBCrack
- BSmurfCrack
- CPSCrack
- DRainbowTables
121In this type of Man-in-the-Middle attack, packets and authentication tokens are captured using a sniffer.
Once the relevant information is extracted, the tokens are placed back on the network to gain access.
- AToken Injection Replay attacks
- BShoulder surfing attack
- CRainbow and Hash generation attack
- DDumpster diving attack
122The FIN flag is set and sent from host A to host B when host A has no more data to transmit (Closing a
TCP connection). This flag releases the connection resources. However, host A can continue to receive
data as long as the SYN sequence numbers of transmitted packets from host B are lower than the packet
segment containing the set FIN flag.- ATrue
- BFalse
123Jason is the network administrator of Spears Technology. He has enabled SNORT IDS to detect attacks
going through his network. He receives Snort SMS alerts on his iPhone whenever there is an attempted
intrusion to his network.
He receives the following SMS message during the weekend.
An attacker Chew Siew sitting in Beijing, China had just launched a remote scan on Jason's network with
the hping command.
Which of the following hping2 command is responsible for the above snort alert?
- Achenrocks:/home/siew # hping -S -R -P -A -F -U 192.168.2.56 -p 22 -c 5 -t 118
- Bchenrocks:/home/siew # hping -F -Q -J -A -C -W 192.168.2.56 -p 22 -c 5 -t 118
- Cchenrocks:/home/siew # hping -D -V -R -S -Z -Y 192.168.2.56 -p 22 -c 5 -t 118
- Dchenrocks:/home/siew # hping -G -T -H -S -L -W 192.168.2.56 -p 22 -c 5 -t 118
124Leesa is the senior security analyst for a publicly traded company. The IT department recently rolled out an
intranet for company use only with information ranging from training, to holiday schedules, to human
resources data. Leesa wants to make sure the site is not accessible from outside and she also wants to
ensure the site is Sarbanes-Oxley (SOX) compliant. Leesa goes to a public library as she wants to do some
Google searching to verify whether the company's intranet is accessible from outside and has been indexed
by Google. Leesa wants to search for a website title of "intranet" with part of the URL containing the word
"intranet" and the words "human resources" somewhere in the webpage.
What Google search will accomplish this?- Arelated:intranet allinurl:intranet:"human resources"
- Bcache:"human resources" inurl:intranet(SharePoint)
- Cintitle:intranet inurl:intranet+intext:"human resources"
- Dsite:"human resources"+intext:intranet intitle:intranet
125Bob has been hired to do a web application security test. Bob notices that the site is dynamic and must
make use of a back end database. Bob wants to see if SQL Injection would be possible. What is the first
character that Bob should use to attempt breaking valid SQL request?- ASemi Column
- BDouble Quote
- CSingle Quote
- DExclamation Mark
126Hampton is the senior security analyst for the city of Columbus in Ohio. His primary responsibility is to
ensure that all physical and logical aspects of the city's computer network are secure from all angles. Bill is
an IT technician that works with Hampton in the same IT department. Bill's primary responsibility is to keep
PC's and servers up to date and to keep track of all the agency laptops that the company owns and lends
out to its employees. After Bill setup a wireless network for the agency, Hampton made sure that everything
was secure. He instituted encryption, rotating keys, turned off SSID broadcasting, and enabled MAC
filtering. According to agency policy, only company laptops are allowed to use the wireless network, so
Hampton entered all the MAC addresses for those laptops into the wireless security utility so that only those
laptops should be able to access the wireless network.
Hampton does not keep track of all the laptops, but he is pretty certain that the agency only purchases Dell
laptops. Hampton is curious about this because he notices Bill working on a Toshiba laptop one day and
saw that he was on the Internet. Instead of jumping to conclusions, Hampton decides to talk to Bill's boss
and see if they had purchased a Toshiba laptop instead of the usual Dell. Bill's boss said no, so now
Hampton is very curious to see how Bill is accessing the Internet. Hampton does site surveys every couple
of days, and has yet to see any outside wireless network signals inside the company's building.
How was Bill able to get Internet access without using an agency laptop?- ABill spoofed the MAC address of Dell laptop
- BBill connected to a Rogue access point
- CToshiba and Dell laptops share the same hardware address
- DBill brute forced the Mac address ACLs
127LAN Manager Passwords are concatenated to 14 bytes, and split in half. The two halves are hashed
individually. If the password is 7 characters or less, than the second half of the hash is always:- A0xAAD3B435B51404EE
- B0xAAD3B435B51404AA
- C0xAAD3B435B51404BB
- D0xAAD3B435B51404CC
128When writing shellcodes, you must avoid ____________ because these will end the string.

- ARoot bytes
- BNull bytes
- CChar bytes
- DUnicode bytes
129Jess the hacker runs L0phtCrack's built-in sniffer utility that grabs SMB password hashes and stores them
for offline cracking. Once cracked, these passwords can provide easy access to whatever network
resources the user account has access to. But Jess is not picking up hashes from the network. Why?- AThe network protocol is configured to use SMB Signing
- BThe physical network wire is on fibre optic cable
- CThe network protocol is configured to use IPSEC
- DL0phtCrack SMB sniffing only works through Switches and not Hubs
130Harold works for Jacobson Unlimited in the IT department as the security manager. Harold has created a
security policy requiring all employees to use complex 14 character passwords. Unfortunately, the members
of management do not want to have to use such long complicated passwords so they tell Harold's boss this
new password policy should not apply to them. To comply with the management's wishes, the IT
department creates another Windows domain and moves all the management users to that domain. This
new domain has a password policy only requiring 8 characters.
Harold is concerned about having to accommodate the managers, but cannot do anything about it. Harold
is also concerned about using LanManager security on his network instead of NTLM or NTLMv2, but the
many legacy applications on the network prevent using the more secure NTLM and NTLMv2. Harold pulls
the SAM files from the DC's on the original domain and the new domain using Pwdump6.
Harold uses the password cracking software John the Ripper to crack users' passwords to make sure they
are strong enough. Harold expects that the users' passwords in the original domain will take much longer to
crack than the management's passwords in the new domain. After running the software, Harold discovers
that the 14 character passwords only took a short time longer to crack than the 8 character passwords.
Why did the 14 character passwords not take much longer to crack than the 8 character passwords?- AHarold should have used Dumpsec instead of Pwdump6
- BHarold's dictionary file was not large enough
- CHarold should use LC4 instead of John the Ripper
- DLanManger hashes are broken up into two 7 character fields
131You establish a new Web browser connection to Google. Since a 3-way handshake is required for any TCP
connection, the following actions will take place.
DNS query is sent to the DNS server to resolve www.google.com
- DNS server replies with the IP address for Google?
- SYN packet is sent to Google.
- Google sends back a SYN/ACK packet
- Your computer completes the handshake by sending an ACK
- The connection is established and the transfer of data commences
Which of the following packets represent completion of the 3-way handshake?- A4th packet
- B3rdpacket
- C6th packet
- D5th packet
132E-mail tracking is a method to monitor and spy the delivered e-mails to the intended recipient.
Select a feature, which you will NOT be able to accomplish with this probe?- AWhen the e-mail was received and read
- BSend destructive e-mails
- CGPS location and map of the recipient
- DTime spent on reading the e-mails
- EWhether or not the recipient visited any links sent to them
- FTrack PDF and other types of attachments
- GSet messages to expire after specified time
- HRemote control the User's E-mail client application and hijack the traffic
133Which of the following Trojans would be considered 'Botnet Command Control Center'?
- AYouKill DOOM
- BDamen Rock
- CPoison Ivy
- DMatten Kit
134What type of Virus is shown here?

- AMacro Virus
- BCavity Virus
- CBoot Sector Virus
- DMetamorphic Virus
- ESparse Infector Virus
135John is using a special tool on his Linux platform that has a database containing signatures to be able to
detect hundreds of vulnerabilities in UNIX, Windows, and commonly used web CGI/ASPX scripts.
Moreover, the database detects DDoS zombies and Trojans as well. What would be the name of this tool?- Ahping2
- Bnessus
- Cnmap
- Dmake
136Fred is scanning his network to ensure it is as secure as possible. Fred sends a TCP probe packet to a
host with a FIN flag and he receives a RST/ACK response. What does this mean?- AThis response means the port he is scanning is open.
- BThe RST/ACK response means the port Fred is scanning is disabled
- CThis means the port he is scanning is half open.
- DThis means that the port he is scanning on the host is closed
137_____________ is a type of symmetric-key encryption algorithm that transforms a fixed-length block of
plaintext (unencrypted text) data into a block of ciphertext (encrypted text) data of the same length- AStream Cipher
- BBlock Cipher
- CBit Cipher
- DHash Cipher
138Your company has blocked all the ports via external firewall and only allows port 80/443 to connect to the
Internet. You want to use FTP to connect to some remote server on the Internet.
How would you accomplish this?- AUse HTTP Tunneling
- BUse Proxy Chaining
- CUse TOR Network
- DUse Reverse Chaining
139You have successfully gained access to a victim's computer using Windows 2003 Server SMB
Vulnerability. Which command will you run to disable auditing from the cmd?- Astoplog stoplog ?
- BEnterPol /nolog
- CEventViewer o service
- Dauditpol.exe /disable
140How do you defend against MAC attacks on a switch?

- ADisable SPAN port on the switch
- BEnable SNMP Trap on the switch
- CConfigure IP security on the switch
- DEnable Port Security on the switch
141In which location, SAM hash passwords are stored in Windows 7?
- Ac:\windows\system32\config\SAM
- Bc:\winnt\system32\machine\SAM
- Cc:\windows\etc\drivers\SAM
- Dc:\windows\config\etc\SAM
142File extensions provide information regarding the underlying server technology. Attackers can use this
information to search vulnerabilities and launch attacks. How would you disable file extensions in Apache
servers?- AUse disable-eXchange
- BUse mod_negotiation
- CUse Stop_Files
- DUse Lib_exchanges
143Bob has a good understanding of cryptography, having worked with it for many years. Cryptography is used
to secure data from specific threats, but it does not secure the application from coding errors. It can provide
data privacy; integrity and enable strong authentication but it cannot mitigate programming errors. What is a
good example of a programming error that Bob can use to explain to the management how encryption will
not address all their security concerns?- ABob can explain that using a weak key management technique is a form of programming error
- BBob can explain that using passwords to derive cryptographic keys is a form of a programming error
- CBob can explain that a buffer overflow is an example of programming error and it is a common mistake associated with poor programming technique
- DBob can explain that a random number generator can be used to derive cryptographic keys but it uses a weak seed value and this is a form of a programming error
144Finding tools to run dictionary and brute forcing attacks against FTP and Web servers is an easy task for
hackers. They use tools such as arhontus or brutus to break into remote servers.
A command such as this, will attack a given 10.0.0.34 FTP and Telnet servers simultaneously with a list of
passwords and a single login namE. linksys. Many FTP-specific password-guessing tools are also available
from major security sites.
What defensive measures will you take to protect your network from these attacks?
- ANever leave a default password
- BNever use a password that can be found in a dictionary
- CNever use a password related to your hobbies, pets, relatives, or date of birth.
- DUse a word that has more than 21 characters from a dictionary as the password
- ENever use a password related to the hostname, domain name, or anything else that can be found with
whois
145One of the most common and the best way of cracking RSA encryption is to begin to derive the two prime
numbers, which are used in the RSA PKI mathematical process. If the two numbers p and q are discovered
through a _____________ process, then the private key can be derived- AFactorization
- BPrime Detection
- CHashing
- DBrute-forcing
146Data is sent over the network as clear text (unencrypted) when Basic Authentication is configured on Web
Servers.- ATrue
- BFalse
147NetBIOS over TCP/IP allows files and/or printers to be shared over the network. You are trying to intercept
the traffic from a victim machine to a corporate network printer. You are attempting to hijack the printer
network connection from your laptop by sniffing the wire. Which port does SMB over TCP/IP use?- A443
- B139
- C179
- D445
148One of the ways to map a targeted network for live hosts is by sending an ICMP ECHO request to the
broadcast or the network address. The request would be broadcasted to all hosts on the targeted network.
The live hosts will send an ICMP ECHO Reply to the attacker's source IP address.
You send a ping request to the broadcast address 192.168.5.255
There are 40 computers up and running on the target network. Only 13 hosts send a reply while others do
not. Why?
- AWindows machines will not generate an answer (ICMP ECHO Reply) to an ICMP ECHO request aimed
at the broadcast address or at the network address - BLinux machines will not generate an answer (ICMP ECHO Reply) to an ICMP ECHO request aimed at
the broadcast address or at the network address - CYou should send a ping request with this command ping ? 192.168.5.0-255
- DYou cannot ping a broadcast address. The above scenario is wrong
- AWindows machines will not generate an answer (ICMP ECHO Reply) to an ICMP ECHO request aimed
149Charlie is the network administrator for his company. Charlie just received a new Cisco router and wants to
test its capabilities out and to see if it might be susceptible to a DoS attack resulting in its locking up. The IP
address of the Cisco switch is 172.16.0.45. What command can Charlie use to attempt this task?- ACharlie can use the commanD. ping -l 56550 172.16.0.45 -t.
- BCharlie can try using the commanD. ping 56550 172.16.0.45
- CBy using the command ping 172.16.0.45 Charlie would be able to lockup the router
- DHe could use the commanD. ping -4 56550 172.16.0.45
150What type of encryption does WPA2 use?
- ADES 64 bit
- BAES-CCMP 128 bit
- CMD5 48 bit
- DSHA 160 bit
Information
- Description
- Informática y Comunicaciones Quiz on Exam A CEH9, created by ma elideth avila on 24/01/2017.
- Author
- ma elideth avila
- Language
- Español
- Views
- 14
- Tags
- Rating
- 5.0 out of 5 · 1 rating Rate this quiz