
Karteikarten
Tags and Digests
Karten in diesem Stapel (11)
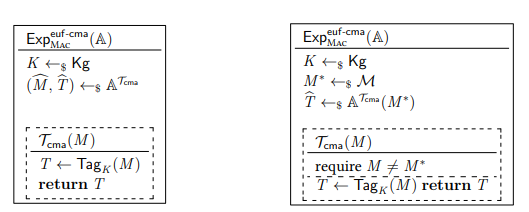
- 1What's a MAC?Kg randomly generates a key, Tag takes a key and a message to output a tag. Vfy takes a tag and message pair and outputs either valid or invalid
- 2Two different forgeries and their differences?EUF adversary chooses any message, in UUF the target message is presented to the adversary
- 3What is CBC-MAC?CBC encrypts the message with an all zero nonce and outputs the final block of C as the tag.
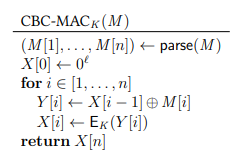
- 4Problems with MAC?Theyhave to be the same length, to deal with arbitary padding the padding has to be a multiple of the block length and should be injective so each M has a different padding otherwise collisions can occur
Not good for public use since everyone needs the same key - 5What's a Hash Function?Takes a message to a digest where the digest set length is smaller than that of the message
- 6Protections against Hash Function collision attacks?
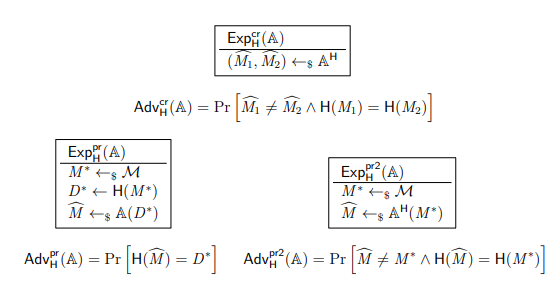
- 7How to do reductions?Recall what the stronger one does and it's capabilites
The stronger one can't use anything but it's own oracle
Use the weaker to get it's own oracle and feed this into the stronger oracle
Return this to the weaker oracle to get your output - 8Some ways of generalising attacks?Longer forgeries: Add an arbitary number of blocks as long as the resulting tag is T
More freedom in first block message - 9Pros and Cons with truncation?Tag guessing attack will suceed with 2^-t which is less than 2^-l
Length extension attack has 2^t-n - 10Why is padding a bad idea?Tag doesn't depend on anything but the final 128 bits
After seeing key-message it's trivial to recover - 11—
Informationen
- Beschreibung
- Cryptography Karteikarten am Tags and Digests, erstellt von Philip Masters am 07/01/2020.
- Erstellt von
- Philip Masters · Jan 2020
- Aktualisiert
- 8 Jan 2020
- Aufrufe
- 0
- Bewertung