
Quiz
Sec+
Dieses Quiz enthält Fragetypen, die sich im gewohnten Player öffnen.
Fragen in diesem Quiz (200)
1Which of the following is used to encrypt web application data?
- AMD5
- BAES
- CSHA2
- DSHA
- ERSA
2A security administrator has generated an SSH key pair to authenticate to a new server. Which of the
following should the security administrator do NEXT to use the keys securely for authentication? (Select
TWO).- AInstall the public key on the server.
- BInstall the private key on the server.
- CEncrypt the public key.
- DEncrypt the private key.
- EInstall both keys on the server
- FSecurely wipe the certificate signing request.
3A user needs to transmit confidential information to a third party. Which of the following should be used to
encrypt the message?- AAES
- BSHA-2
- CSSL
- DRSA
4A company is executing a strategy to encrypt and sign all proprietary data in transit. The company recently
deployed PKI services to support this. Which of the following protocols supports the strategy and employs
certificates generated by the PKI? (Select THREE)- AS/MIME
- BTLS
- CHTTP-DIGEST
- DSAML
- ESIP
- FIPSec
- GKerberos
5A security engineer wants to add SSL to the public web server. Which of the following would be the FIRST
step to implement the SSL certificate?- ADownload the web certificate.
- BInstall the intermediate certificate.
- CGenerate a CSR.
- DEncrypt the private key.
6A systems administrator has implemented multiple websites using host headers on the same server. The
server hosts two websites that require encryption and other websites where encryption is optional. Which of
the following should the administrator implement to encrypt web traffic for the require websites?- AExtended domain validation
- BTLS host certificate
- COCSP stapling
- DWildcard certificate
7An organization uses application whitelisting to help prevent zero-day attacks. Malware was recently identified
on one client, which was able to run despite the organization's application whitelisting approach. The forensics
team has identified the malicious file, conducted a post-incident analysis, and compared this with the original
system baseline. The team sees the following output:
filename hash
original winSCP.exe 2d da b1 4a 98 fc f1 98 06 b1 e5 26 b2 df e5 5b 3e cb 83 e1
lastest winSCP.exe a3 4a c2 4b 85 fa f2 dd 0b ba f4 16 b2 df f2 4b 3f ac 4a e1
Which of the following identifies the flaw in the team's application whitelisting approach?- ATheir approach uses executable names and not hashes for the whitelist
- BSHA-1 has known collision vulnerabilities and should not be used
- CThe original baseline never captured the lastest file signature
- DZero-day attacks require the lastest fiel signatures, and they never updated these
8A security analyst wants to ensure the integrity of a file downloaded from the Internet The name of the file is
code.zip. The analyst uses the vendor website to determine the 160-bit fingerprint of the input, and then
reviews the following output:
8532f8c0bcb335cf231ec09e02da8f77e921e4c0 code.zip
Which of the following can be determined from this output?- AA message digest of 160 bits should be SHA-1 hash. The message digest listed is for MD5.
- BA message digest of 160 bits should be SHA-1 hash. The message digest listed is for SHA-1.
- CA message digest of 160 bits should be MD5 hash. The message digest listed is for MD5.
- DA message digest of 160 bits should be MD5 hash. The message digest listed is for SHA-1.
9A security analyst is trying to improve the security posture of an organization. The analyst has determined
there is a significant risk of pass-the-hash attacks on the desktop computers within the company. Which of
the following would help to reduce the risk of this type of attack?- ARequire the desktop OS to use a stronger password hash.
- BPrevent credentials from being cached on the desktops.
- CUse TLS encryption in which plain text credentials are transmitted.
- DUse salts on the password hashes to prevent offline cracking attempts.
- ERequire that passwords meet high length and complexity requirements.
10A forensics analyst is investigating a hard drive for evidence of suspected illegal activity. Which of the
following should the analyst do FIRST?- ACreate a hash of the hard drive.
- BExport the Internet history
- CSave a copy of the case number and date as a text file in the root directory.
- DBack up the pictures directory for further inspection
11A cryptographer has developed a new proprietary hash function for a company and solicited employees to test the function before recommending its implementation. An employee takes the plaintext version of a
document and hashes it, then changes the original plaintext document slightly and hashes it, and continues
repeating this process until two identical hash values are produced from two different documents. Which of
the following BEST describes this cryptographic attack?- ABrute force
- BKnown plaintext
- CReplay
- DCollision
12A computer forensics team is performing an integrity check on key systems files. The team is comparing the
signatures of original baseline files with the latest signatures. The original baseline was taken on March 2,
2016, and was established to be clean of malware and uncorrupted. The latest file signatures were generated
yesterday. One file is known to be corrupted, but when the team compares the signatures of the original and
latest files, the team sees the following:
Original: 2d da b1 4a 98 fc f1 98 06 b1 e5 5b 3e cb 83 e1
Latest: 2d da b1 4a 98 fc f1 98 06 b1 e5 5b 3e cb 83 e1
Which of the following is MOST likely the situation?- AThe forensics team must have reverted the system to the original [date] which resulted in an identical hash calculation.
- BThe original baseline was compromised, so the corrupted file was [xxxx] on the system.
- CThe signature comparison is using two different algorithms that happen to have generated the same
values. - DThe algorithm used to calculate the hash has a collision weakness, and an attacker has exploited it.
13A technician suspects that a desktop was compromised with a rootkit. After removing the hard drive from the
desktop and running an offline file integrity check, the technician reviews the following output:
File name Expected hash Installed hash
Available Installed
version version
notepad.exe 48D403AD1FAB103BD04732ACB4B3A922 48D403AD1FAB103BD04732ACB4B3A922
49.33.21 48.100.2
kernel.dll AB502DE1A78AD1FAB1010AB3AFD45021 1AC406DE49564AD1FAB1019DDA264120
1.01.200 1.01.200
lsass.exe 0987352AB3823AAD1FAB1083AB94D2EE 0987352AB3823AAD1FAB1083AB94D3EE
0.900.20 0.900.12
httpd.exe AD1FAB10492839FAB109283AA38549AA AD1FAB10492839FAB109283AA38549AA
10.200.1 10.200.0
Based on the above output, which of the following is the malicious file?- Anotepad.exe
- Blsass.exe
- Ckernel.dll
- Dhttpd.exe
14Which of the following provides/supports PFS?
- AAES
- BRC4
- CDHE
- DHMAC
15Using an ROT13 cipher to protect confidential information for unauthorized access is known as:
- Asteganography
- Bobfuscation
- Cnon-repudiation
- Ddiffusion
16Which of the following provides the BEST protection for sensitive information and data stored in cloud-based
services but still allows for full functionality and searchability of data within the cloud-based services?- AData encryption
- BData masking
- CAnonymization
- DTokenization
17Which of the following is unique to a stream cipher?
- AIt encrypts 128 bytes at a time.
- BIt uses AES encryption.
- CIt perform as bit-level encryption.
- DIt is used in HTTPS.
18An accountant is attempting to log in to the internal accounting system and receives a message that the
website's certificate is fraudulent. The accountant finds instructions for manually installing the new trusted root onto the local machine. Which of the following would be the company's BEST option for this situation in the future?- AUtilize a central CRL
- BImplement certificate management
- CEnsure access to KMS
- DUse a stronger cipher suite
19Given the following:
> md5.exe file1.txt
> AD1FAB1033773DC6A1E6021B7F503A210
> md5.exe file2.txt
> AD1FAB1033773DC6A1E6021B7F503A210
Which of the following concepts of cryptography is shown?- ACollision
- BSalting
- CSteganography
- DStream cipher
20A company's bank has reported that multiple corporate credit cards have been stolen over the past several
weeks. The bank has provided the names of the affected cardholders to the company's forensics team to
assist in the cyber-incident investigation. An incident responder learns the following information:
* The timeline of stolen card numbers corresponds closely with affected users making Internet-based
purchases from diverse websites via enterprise desktop PCs.
* All purchase connections were encrypted, and the company uses an SSL inspection proxy for the inspection
of encrypted traffic of the hardwired network.
* Purchases made with corporate cards over the corporate guest WiFi network, where no SSL inspection
occurs, were unaffected.
Which of the following is the MOST likely root cause?- AHTTPS sessions are being downgraded to insecure cipher suites
- BThe SSL inspection proxy is feeding events to a compromised SIEM
- CThe payment providers are insecurely processing credit card charges
- DThe adversary has not yet established a presence on the guest WiFi network
21Which of the following are used to substantially increase the computation time required to crack a password?
(Select TWO)- ABCRYPT
- BSubstitution cipher
- CECDHE
- DPBKDF2
- EDiffle-Hellman
22A web server, which is configured to use TLS with AES-GCM-256, SHA-384, and ECDSA, recently suffered
an information loss breach. Which of the following is MOST likely the cause?- AInsufficient key bit length
- BWeak cipher suite
- CUnauthenticated encryption method
- DPoor implementation
23Which of the following implements a stream cipher?
- AFile-level encryption
- BIKEv2 exchange
- CSFTP data transfer
- DS/MIME encryption
24A security administrator is choosing an algorithm to generate password hashes. Which of the following would
offer the BEST protection against offline brute force attacks?- AMD5
- B3DES
- CAES
- DSHA-1
25Which of the following categories would the use of proximity cards, smart cards, and RSA tokens be
considered when they are used together?- AMultifactor authenticatoin
- BAdministrative control
- CAccess control
- DBiometrics
26A computer forensics analyst collected a flash drive that contained a single file with 500 pages of text. Which
of the following algorithms should the analyst use to validate the integrity of the file?- A3DES
- BAES
- CMD5
- DRSA
27A user needs to transmit confidential information to a third party. Which of the following should be used to
encrypt the message?- AAES
- BSHA-2
- CSSL
- DRSA
28Which of the following encryption algorithms is used primarily to secure data at rest?
- AAES
- BSSL
- CTLS
- DRSA
29Which of the following is an algorithm family that was developed for use cases in which power consumption
and lower computing power are constraints?- AElliptic curve
- BRSA
- CDiffie-Hellman
- DSHA
30If two employees are encrypting traffic between them using a single encryption key, which of the following
algorithms are they using?- ARSA
- B3DES
- CDSA
- DSHA-2
31Which of the following algorithms would be used to provide non-repudiation of a file transmission?
- AAES
- BRSA
- CMD5
- DSHA
32Which of the following algorithms has the SMALLEST key size?
- ADES
- BTwofish
- CRSA
- DAES
33A security analyst discovers that a company’s username and password database was posted on an Internet
forum. The usernames and password are stored in plain text. Which of the following would mitigate the
damage done by this type of data exfiltration in the future?- ACreate DLP controls that prevent documents from leaving the network.
- BImplement salting and hashing.
- CConfigure the web content filter to block access to the forum.
- DIncrease password complexity requirements.
34After running an online password cracking tool, an attacker recovers the following password:
gh;jSKSTOi;618&
Based on the above information, which of the following technical controls have been implemented (Select
TWO).- AComplexity
- BEncryption
- CHashing
- DLength
- ESalting
- FStretching
35Given the information below:
MD5HASH document.doc 049eab40fd36cabd1fab10b3cdf4a883
MD5HASH image.jpg 049eab40fd36cabd1fab10b3cdf4a883
Which of the following concepts are described above? (Select TWO).- ASalting
- BCollision
- CSteganography
- DHashing
- EKey stretching
36A database administrator needs to ensure all passwords are stored in a secure manner, so the administrator
adds randomly generated data to each password before string. Which of the following techniques BEST
explains this action?- APredictability
- BKey stretching
- CSalting
- DHashing
37Which of the following is a random value appended to a credential that makes the credential less susceptible
to compromise when hashed?- ANonce
- BSalt
- COTP
- DBlock cipher
38An attachment that was emailed to finance employees contained an embedded message. The security
administrator investigates and finds the intent was to conceal the embedded information from public view.
Which of the following BEST describes this type of message?- AObfuscation
- BSteganography
- CDiffusion
- DBCRYPT
39A user wants to send a confidential message to a customer to ensure unauthorized users cannot access the
information. Which of the following can be used to ensure the security of the document while is transit and at
rest?- ABCRYPT
- BPGP
- CFTPS
- DS/MIME
40Which of the following can be used to increase the time needed to brute force a hashed password?
- ABCRYPT
- BECDHE
- CElliptic curve
- DDiffie-Hellman
41Which of the following encryption algorithms require one encryption key? (Select TWO).
- AMD5
- B3DES
- CBCRYPT
- DRC4
- EDSA
42A security engineer wants to introduce key stretching techniques to the account database to make password
guessing attacks more difficult. Which of the following should be considered to achieve this? (Select TWO).- ADigital signature
- Bbcrypt
- CPerfect forward secrecy
- DSHA-256
- EP-384
- FPBKDF2
- GRecord-level encryption
43A security administrator is hardening a VPN connection. Recently, company pre-shared keys were hijacked
during an MITM attack and reused to breach the VPN connection. Which of the following should the security
administrator do to BEST address this issue?- AImplement PKI
- BImplement IPSec
- CImplement TLS
- DImplement PFS
44An analyst needs to set up a method for securely transferring files between systems. One of the requirements
is to authenticate the IP header and the payload. Which of the following services would BEST meet the
criteria?- ATLS
- BPFS
- CESP
- DAH
45A computer incident first responder collected a flash drive that contained a single file with 500 pages of text. Which of the following algorithms should they use to validate the integrity of the file?
- A3DES
- BAES
- CMD5
- DRSA
46If two employees are encrypting traffic between them using a single encryption key, which of the following algorithms are they using?
- ARSA
- B3DES
- CDSA
- DSHA-2
47Which of the following algorithms is used to provide non-repudiation of a file transmission?
- AAES
- BRSA
- CMD5
- DSHA
48Mike is sending David an encrypted message using a symmetric encryption algorithm. What key should he use to encrypt the message?
- AMike's public key
- BMike's private key
- CDavid's public key
- DShared secret key
49Alan's team needs to perform computations on sensitive personal information but does not need access to the underlying data. What technology can the team use to perform these calculations without accessing the data?
- AQuantum computing
- BBlockchain
- CHomomorphic encryption
- DCertificate pinning
50Norm is using full-disk encryption technology to protect the contents of laptops against theft. What goal of cryptography is he attempting to achieve?
- AIntegrity
- BNonrepudiation
- CAuthentication
- DConfidentiality
51Brian discovers that a user suspected of stealing sensitive information is posting many image files to a message board. What technique might the individual be using to hide sensitive information in those images?
- ASteganography
- BHomomorphic encryption
- CReplay attack
- DBirthday attack
52Which one of the following statements about cryptographic keys is incorrect?
- AAll cryptographic keys should be kept secret.
- BLonger keys are better than shorter keys when the same algorithm is used.
- CAsymmetric algorithms generally use longer keys than symmetric algorithms.
- DDigital certificates are designed to share public keys.
53What type of cipher operates on one character of text at a time?
- ABlock cipher
- BBit cipher
- CStream cipher
- DBalanced cipher
54Vince is choosing a symmetric encryption algorithm for use in his organization. He would like to choose the strongest algorithm from the choices below. What algorithm should he choose?
- ADES
- B3DES
- CRSA
- DAES
55Acme Widgets has 10 employees and they all need the ability to communicate with one another using a symmetric encryption system. The system should allow any two employees to securely communicate without other employees eavesdropping. If an 11th employee is added to the organization, how many new keys must be added to the system?
- A1
- B2
- C10
- D11
56Glenn recently obtained a wildcard certificate for *. mydomain.com. Which one of the following domains would not be covered by this certificate?
- Amydomain.com
- Bcore.mydomain.com
- Cdev.www.mydomain.com
- Dmail.mydomain.com
57Which one of the following servers is almost always an offline CA in a large PKI deployment?
- ARoot CA
- BIntermediate CA
- CRA
- DInternal CA
58Which one of the following certificate formats is closely associated with Windows binary certificate files?
- ADER
- BPEM
- CPFX
- DP7B
59David would like to send Mike a message using an asymmetric encryption algorithm. What key should he use to encrypt the message?
- ADavid's public key
- BDavid's private key
- CMike's public key
- DMike's private key
60When Mike receives the message that David encrypted for him, what key should he use to decrypt the message?
- ADavid's public key
- BDavid's private key
- CMike's public key
- DMike's private key
61If David wishes to digitally sign the message that he is sending Mike, what key would he use to create the digital signature?
- ADavid's public key
- BDavid's private key
- CMike's public key
- DMike's private key
62When Mike receives the digitally signed message from David, what key should he use to verify the digital signature?
- ADavid's public key
- BDavid's private key
- CMike's public key
- DMike's private key
63A cybersecurity administrator has a reduced team and needs to operate an on-premises network and security infrastructure efficiently. To help with the situation, the administrator decides to hire a service provider. Which of the following should the administrator use?
- ASDP
- BAAA
- CIaaS
- DMSSP
- EMicroservices
64A security engineer needs to Implement the following requirements:
- All Layer 2 switches should leverage Active Directory tor authentication.
- All Layer 2 switches should use local fallback authentication If Active Directory Is offline.
- All Layer 2 switches are not the same and are manufactured by several vendors.
Which of the following actions should the engineer take to meet these requirements? (Select TWO).- AImplement RADIUS.
- BConfigure AAA on the switch the local login as secondary.
- CConfigure port security on the switch with the secondary login method.
- DImplement TACACS+
- EEnable the local firewall on the Active Directory server.
- FImplement a DHCP server.
65A company is upgrading its wireless infrastructure to WPA2-Enterprise using EAP-TLS. Which of the following must be part of the security architecture to achieve AAA? (Select TWO)
- ADNSSEC
- BReverse proxy
- CVPN Concentrator
- DPKI
- EActive Directory
- FRADIUS
66A company is launching a new internet platform for its clients. The company does not want to implement its own authorization solution but instead wants to rely on the authorization provided by another platform. Which of the following is the BEST approach to implement the desired solution?
- AOAuth
- BTACACS+
- CSAML
- DRADIUS
67A consultant is configuring a vulnerability scanner for a large, global organization in multiple countries. The consultant will be using a service account to scan systems with administrative privileges on a weekly basis, but there is a concern that hackers could gain access to the account and pivot through the global network. Which of the following would be BEST to help mitigate this concern?
- ACreate consultant accounts for each region, each configured with push MFA notifications.
- BCreate one global administrator account and enforce Kerberos authentication
- CCreate different accounts for each region. limit their logon times, and alert on risky logins
- DCreate a guest account for each region. remember the last ten passwords, and block password reuse
68A security analyst receives the configuration of a current VPN profile and notices the authentication is only applied to the IP datagram portion of the packet. Which of the following should the analyst implement to authenticate the entire packet?
- AAH
- BESP
- CSRTP
- DLDAP
69The Chief Security Officer (CSO) at a major hospital wants to implement SSO to help improve in the
environment patient data, particularly at shared terminals. The Chief Risk Officer (CRO) is concerned that training and guidance have been provided to frontline staff, and a risk analysis has not been performed. Which of the following is the MOST likely cause of the CRO's concerns?- ASSO would simplify username and password management, making it easier for hackers to pass guess accounts.
- BSSO would reduce password fatigue, but staff would still need to remember more complex passwords.
- CSSO would reduce the password complexity for frontline staff.
- DSSO would reduce the resilience and availability of system if the provider goes offline.
70A cybersecurity analyst needs to implement secure authentication to third-party websites without users'
passwords. Which of the following would be the BEST way to achieve this objective?- AOAuth
- BSSO
- CSAML
- DPAP
71An organization needs to implement more stringent controls over administrator/root credentials and service accounts. Requirements for the project include:
* Check-in/checkout of credentials
* The ability to use but not know the password
* Automated password changes
* Logging of access to credentials
Which of the following solutions would meet the requirements?- AOAuth 2.0
- BSecure Enclave
- CA privileged access management system
- DAn OpenID Connect authentication system
72A company uses wireless for all laptops and keeps a very detailed record of its assets, along with a
comprehensive list of devices that are authorized to be on the wireless network. The Chief Information Officer (CIO) is concerned about a script kiddie potentially using an unauthorized device to brute force the wireless PSK and obtain access to the internal network. Which of the following should the company implement to BEST prevent this from occurring?- ABDU Guard
- BWPA-EAP
- CIP filtering
- DA WIDS
73A network technician is installing a guest wireless network at a coffee shop. When a customer purchases an Item, the password for the wireless network is printed on the recent so the customer can log in. Which of the following will the technician MOST likely configure to provide the highest level of security with the least amount of overhead?
- AWPA-EAP
- BWEP-TKIP
- CWPA-PSK
- DWPS-PIN
74After entering a username and password, and administrator must gesture on a touch screen. Which of the following demonstrates what the administrator is providing?
- AMultifactor authentication
- BSomething you can do
- CBiometric
- DTwo-factor authentication
75An organization wants to implement a third factor to an existing multifactor authentication. The organization already uses a smart card and password. Which of the following would meet the organization's needs for a third factor?
- ADate of birth
- BFingerprint
- CPIN
- DTPM
76A security administrator currently spends a large amount of time on common security tasks, such aa report generation, phishing investigations, and user provisioning and deprovisioning This prevents the administrator from spending time on other security projects. The business does not have the budget to add more staff members. Which of the following should the administrator implement?
- ADAC
- BABAC
- CSCAP
- DSOAR
77An organization is developing an authentication service for use at the entry and exit ports of country borders. The service will use data feeds obtained from passport systems, passenger manifests, and high- definition video feeds from CCTV systems that are located at the ports. The service will incorporate machine-learning techniques to eliminate biometric enrollment processes while still allowing authorities to identify passengers with increasing accuracy over time. The more frequently passengers travel, the more accurately the service will identify them. Which of the following biometrics will MOST likely be used, without the need for enrollment? (Choose two.)
- AVoice
- BGait
- CVein
- DFacial
- ERetina
- FFingerprinting
78A company wants to provide centralized authentication for its wireless system. The wireless authentication
system must integrate with the directory back end. Which of the following is a AAA solution that will provide
the required wireless authentication?- ATACACS+
- BMSCHAPv2
- CRADIUS
- DLDAP
79Which of the following is an example of federated access management?
- AWindows passing user credentials on a peer-to-peer network
- BApplying a new user account with a complex password
- CImplementing a AAA framework from network access
- Dusing a popular website login to provide access to another website
80A technician has installed a new AAA server, which will be used by the network team to control access to a
company's routers and switches. The technician completes the configuration by adding the network team
members to the NETWORK_TEAM group, and then adding the NETWORK_TEAM group to the appropriate
ALLOW_ACCESS access list. Only members of the network team should have access to the company's
routers and switches.
NETWORK_TEAM
Lee
Andrea
Pete
ALLOW_ACCESS
DOMAIN_USERS
AUTHENTICATED_USERS
NETWORK_TEAM
Members of the network team successfully test their ability to log on to various network devices configured to
use the AAA server. Weeks later, an auditor asks to review the following access log sample:
5/26/2017 10:20 PERMIT: LEE
5/27/2017 13:45 PERMIT: ANDREA
5/27/2017 09:12 PERMIT: LEE
5/28/2017 16:37 PERMIT: JOHN
5/29/2017 08:53 PERMIT: LEE- AConfigure the ALLOW_ACCESS group logic to use AND rather than OR.
- BMove the NETWORK_TEAM group to the top of the ALLOW_ACCESS access list.
- CDisable group nesting for ALLOW_ACCESS group in the AAA server.
- DRemove the DOMAIN_USERS group from the ALLOW_ACCESS group.
81A security analyst is hardening a large-scale wireless network. The primary requirements are the following:
- Must use authentication through EAP-TLS certificates
- Must use an AAA server
- Must use the most secure encryption protocol
Given these requirements, which of the following should the analyst implement and recommend? (Select
TWO).- A802.1x
- B802.3
- CLDAP
- DTKIP
- ECCMP
- FWPA2-PSK
82Two large organizations have signed a cooperative agreement that will require their employees to log on each
others' networks on a regular basis. Each company implements NAC. Which of the following should be
implemented if each company wants to continue using its own separate credentials while using the other
company's network?- AEAP-TLS
- BWPA2-Enterprise
- CRADIUS Federation
- DOnline CA
83A security administrator at a large company is installing a Shibboleth component to enable its employees to
use the company's credentials when working at other peer organizations that support the same federation
model. Which of the following are required components that the administrator must install at the local
company? (Select TWO)- ARADIUS
- BSSL/TLS certificate
- CIdP
- DTACACS+
- EOAuth
84A systems administrator is auditing the company's Active Directory environment. It is quickly noted that the
username "company\bsmith" is interactively logged into several desktops across the organization. Which of
the following has the systems administrator MOST likely come across?- AShared account
- BShared credentials
- CFalse positive
- DLocal account
85A security analyst is mitigating a pass-the-hash vulnerability on a Windows infrastructure. Given the
requirement, which of the following should the security analyst do to MINIMIZE the risk?- AEnable CHAP
- BDisable MD5
- CEnable Kerberos
- DDisable PAP
86Which of the following is the MAIN disadvantage of using SSO
- AThe architecture can introduce a single point of failure
- BUsers need to authenticate for each resource they access.
- CIt requires an organization to configure federation.
- DThe authentication is transparent to the user.
87A network administrator at a large organization is reviewing methods to improve the security of the wired LAN. Any security improvement must be centrally managed and allow corporate-owned devices to have access to the intranet but limit others to Internet access only. Which of the following should the administrator
recommend?- A802.1X utilizing the current PKI infrastructure
- BSSO to authenticate corporate users
- CMAC address filtering with ACLs on the router
- DPAM for users account management
88Which of the following is a component of multifactor authentication?
- ARADIUS
- BSSO
- CTransistive trust
- DOTP
89A company has migrated to two-factor authentication for accessing the corporate network, VPN, and SSO.
Several legacy applications cannot support multifactor authentication and must continue to use usernames
and passwords. Which of the following should be implemented to ensure the legacy applications are as secure
as possible while ensuring functionality? (Select TWO)- APrivileged accounts
- BPasswords reuse restrictions
- CPassword complexity requirements
- DPassword recovery
- EAccount disablement
90An organization needs to integrate with a third-party cloud application. The organization has 15000 users and
does not want to allow the cloud provider to query its LDAP authentication server directly. Which of the
following is the BEST way for the organization to integrate with the cloud application?- AUpload a separate list of users and passwords with a batch import.
- BDistribute hardware tokens to the users for authentication to the cloud.
- CImplement SAML with the organization's server acting as the identity provider.
- DConfigure a RADIUS federation between the organization and the cloud provider.
91A security engineer at a manufacturing company is implementing a third-party cloud application. Rather than
creating users manually in the application, the engineer decides to use the SAML protocol. Which of the
following is being used for this implementation?- AThe manufacturing company is the service provider, and the cloud company is the identify provider.
- BThe manufacturing company is the authorization provider, and the cloud company is the service provider.
- CThe manufacturing company is the identity provider and the cloud company is the OAuth provider.
- DThe manufacturing company is the identity provider, and the cloud company is the service provider.
- EThe manufacturing company is the service provider, and the cloud company is the authorization provider.
92A security administrator is configuring a RADIUS server for wireless authentication. The configuration must
ensure client credentials are encrypted end-to-end between the client and the authenticator. Which of the
following protocols should be configured on the RADIUS server? (Select TWO).- APAP
- BMSCHAP
- CPEAP
- DNTLM
- ESAML
93A company has purchased a new SaaS application and is in the process of configuring it to meet the
company's needs. The director of security has requested that the SaaS application be integrated into the
company's IAM processes. Which of the following configurations should the security administrator set up in
order to complete this request?- ALDAP
- BRADIUS
- CSAML
- DNTLM
94A systems engineer is setting up a RADIUS server to support a wireless network that uses certificate authentication. Which of the following protocols must be supported by both the RADIUS server and the WAPs?
- ACCMP
- BTKIP
- CWPS
- DEAP
95Which of the following uses tokens between the identity provider and the service provider to authenticate and authorize users to resources?
- ARADIUS
- BSSH
- COAuth
- DMSCHAP
96A systems administrator wants to implement a secure wireless network requiring wireless clients to pre-register with the company and install a PKI client certificate prior to being able to connect to the wireless network. Which of the following systems should the system administrator configure?
- AEAP-TTLS
- BEAP-TLS
- CEAP-FAST
- DEAP with PEAP
- EEAP with MSCHAPv2
97A company wants to configure its wireless network to require username and password authentication. Which of the following should the systems administrator implement?
- AWPS
- BPEAP
- CTKIP
- DPKI
98A security analyst needs to make a recommendation for restricting access to certain segments of the network using only data-link layer security. Which of the following controls will the analyst MOST likely recommend?
- AMAC
- BACL
- CBPDU
- DARP
99A system in the network is used to store proprietary secrets and needs the highest level of security possible. Which of the following should a security administrator implement to ensure the system cannot be reached from the Internet?
- AVLAN
- BAir gap
- CNAT
- DFirewall
100A security administrator checks the table of a network switch, which shows the following output:
VLAN Physical Address Type Port
1 001a:42ff:5113 Dynamic GE0/5
1 0faa:abcf:ddee Dynamic GE0/5
1 c6a9:6616:758e Dynamic GE0/5
1 a1a3:b6a3:1212 Dynamic GE0/5
1 6025:2ad8:bca2 Dynamic GE0/5
1 b935:f995:b00b Dynamic GE0/5
Which of the following is happening to this switch?- AMAC Flooding
- BDNS poisoning
- CMAC cloning
- DARP Poisoning
101A smart switch has the ability to monitor electrical levels and shut off power to a building in the event of power surge or other fault situation. The switch was installed on a wired network in a hospital and is monitored by the facilities department via a cloud application. The security administrator isolated the switch on a separate VLAN and set up a patch routine. Which of the following steps should also be taken to harden the smart switch?
- ASet up an air gap for the switch.
- BChange the default password for the switch.
- CPlace the switch In a Faraday cage.
- DInstall a cable lock on the switch
102A network engineer is troubleshooting wireless network connectivity issues that were reported by users. The issues are occurring only in the section of the building that is closest to the parking lot. Users are intermittently experiencing slow speeds when accessing websites and are unable to connect to network drives. The issues appear to increase when
laptop users return to their desks after using their devices in other areas of the building. There have also been reports of users being required to enter their credentials on web pages in order to gain access to them. Which of the following is the MOST likely cause of this issue?- AAn external access point is engaging in an evil-twin attack.
- BThe signal on the WAP needs to be increased in that section of the building
- CThe certificates have expired on the devices and need to be reinstalled
- DThe users in that section of the building are on a VLAN that is being blocked by the firewall.
103After segmenting the network, the network manager wants to control the traffic between the segments. Which of the following should the manager use to control the network traffic?
- ADMZ
- BVPN
- CVLAN
- DACL
104A company has just completed a vulnerability scan of its servers. A legacy application that monitors the HVAC system is the datacenter presents several challenges, as the application vendor is no longer in business. Which of the following secure network architect concepts would BEST protect the other company if the legacy server were to be exploited?
- AVirtualization
- BAir gap
- CVLAN
- DExtranet
105The phones at a business are being replaced with VoIP phones that get plugged in-line between the switch and PC. The voice and data networks still need to be kept separate. Which of the following would allow for this?
- ANAT
- BIntranet
- CSubnetting
- DVLAN
106A law office has been leasing dark fiber from a local telecommunications company to connect a remote office to company headquarters. The telecommunications company has decided to discontinue its dark fiber product and is offering an MPLS connection, which the law office feels is too expensive. Which of the following is the BEST solution for the law office?
- ARemote access VPN
- BVLAN
- CVPN concentrator
- DSite-to-site VPN
107A network technician is setting up a new branch for a company. The users at the new branch will need to access resources securely as if they were at the main location Which of the following networking concepts would BEST accomplish this?
- AVirtual network segmentation
- BPhysical network segmentation
- CSite-to-site VPN
- DOut-of-band access
- ELogical VLANs
108Which of the following BEST explains the difference between a credentialed scan and a non-credentialed scan?
- AA credentialed scan sees devices in the network, including those behind NAT, while a non-credentialed scan sees outward-facing applications.
- BA credentialed scan will not show up in systems logs because the scan is running with the necessary authorization, while non-credentialed scan activity will appear in the logs.
- CA credentialed scan generates significantly more false positives, while a non-credential scan generates fewer false positives.
- DA credentialed scan sees the system the way an authorized user sees the system, while a non-credentialed scan sees the system as a guest.
109In which of the following situations would it be BEST to use a detective control type for mitigation?
- AA company implemented a network load balancer to ensure 99.999% availability of its web application.
- BA company designed a backup solution to increase the chances of restoring services in case of a natural disaster.
- CA company purchased an application-level firewall to isolate traffic between the accounting department and the information technology department.
- DA company purchased an IPS system, but after reviewing the requirements, the appliance was supposed to monitor, not block, any traffic.
110Joe, a user at a company, clicked an email link led to a website that infected his workstation. Joe, was connected to the network, and the virus spread to the network shares. The protective measures failed to stop this virus, and it has continued to evade detection. Which of the following should administrator implement to protect the environment from this malware?
- AInstall a definition-based antivirus.
- BImplement an IDS/IPS
- CImplement a heuristic behavior-detection solution.
- DImplement CASB to protect the network shares.
111A network administrator has been asked to install an IDS to improve the security posture of an organization. Which of the following control types is an IDS?
- ACorrective
- BPhysical
- CDetective
- DAdministrative
112After reading a security bulletin, a network security manager is concerned that a malicious actor may have breached the network using the same software flaw. The exploit code is publicly available and has been reported as being used against other industries in the same vertical. Which of the following should the network security manager consult FIRST to determine a priority list for forensic review?
- AThe vulnerability scan output
- BThe IDS logs
- CThe full packet capture data
- DThe SIEM alerts
113An organization wants to implement a method to correct risks at the system/application layer. Which of the following is the BEST method to accomplish this goal?
- AIDS/IPS
- BIP tunneling
- CWeb application firewall
- DPatch management
114The application team within a company is asking the security team to investigate why its application is slow after an upgrade. The source of the team's application is 10.13.136.9, and the destination IP is 10.17.36.5, The security analyst pulls the logs from the endpoint security software but sees nothing is being blocked. The analyst then looks at the UTM firewall logs and sees the following:
Session Source Destination Protocol Port Action IPS DoS
12699 10.13.136.9 10.17.36.5 TCP 80 ALLOW YES NO
12699 10.13.136.9 10.17.36.5 TCP 443 ALLOW YES NO
12699 10.13.136.9 10.17.36.5 TCP 1433 DENY YES NO
12719 10.13.136.8 10.17.36.5 TCP 87 DENY YES NO
12719 10.13.136.9 10.17.36.5 TCP 88 ALLOW YES NO
12719 10.13.136.9 10.17.36.5 TCP 636 ALLOW YES NO
12899 10.13.136.6 10.17.36.9 UDP 9877 DENY NO NO
Which of the following should the security analyst request NEXT based on the UTM firewall analysis?- ARequest the application team to all TCP port 87 to listen on 10.17.36.5.
- BRequest the network team to open port 1433 from 10.13.136.9 to 10.17.36.5.
- CRequest the network team to turn off IPS for 10.13.136.8 going to 10.17.36.5.
- DRequest the application team to reconfigure the application and allow RPC communication.
115Joe, a user at a company, clicked an email link that led to a website that infected his workstation. Joe was connected to the network, and the virus spread to the network shares. The protective measures failed to stop this virus, and it has continued to evade detection. Which of the following should a security administrator implement to protect the environment from this malware?
- AInstall a definition-based antivirus.
- BImplement an IDS/IPS.
- CImplement a heuristic behavior-detection solution.
- DImplement CASB to protect the network shares.
116After patching computers with the latest application security patches/updates, users are unable to open certain applications. Which of the following will correct the issue?
- AModifying the security policy for patch management tools
- BModifying the security policy for HIDS/HIPS
- CModifying the security policy for DLP
- DModifying the security policy for media control
117A large industrial system's smart generator monitors the system status and sends alerts to third-party
maintenance personnel when critical failures occur. While reviewing the network logs the company's security manager notices the generator's IP is sending packets to an internal file server's IP. Which of the following mitigations would be BEST for the security manager to implement while maintaining alerting capabilities?- ASegmentation
- BFirewall whitelisting
- CContainment
- DIsolation
118The CSIRT is reviewing the lessons learned from a recent incident. A worm was able to spread unhindered throughout the network and infect a large number of computers and servers. Which of the following recommendations would be BEST to mitigate the impacts of a similar incident in the future?
- AInstall a NIDS device at the boundary.
- BSegment the network with firewalls.
- CUpdate all antivirus signatures daily.
- DImplement application blacklisting.
119A pharmaceutical sales representative logs on to a laptop and connects to the public WiFi to check emails and update reports. Which of the following would be BEST to prevent other devices on the network from directly accessing the laptop? (Choose two.)
- ATrusted Platform Module
- BA host-based firewall
- CDLP solution
- DFull disk encryption
- EVPN
- FAntivirus software
120Several employees return to work the day after attending an industry trade show. That same day, the security manager notices several malware alerts coming from each of the employee's workstations. The security manager investigates but finds no signs of an attack on the perimeter firewall or the NIDS. Which of the following is MOST likely causing the malware alerts?
- AA worm that has propagated itself across the intranet, which was initiated by presentation media
- BA fileless virus that is contained on a vCard that is attempting to execute an attack
- CA Trojan that has passed through and executed malicious code on the hosts
- DA USB flash drive that is trying to run malicious code but is being blocked by the host firewall
121A company recently experienced a data breach and the source was determined to be an executive who was charging a phone in a public area. Which of the following would MOST likely have prevented this breach?
- AFirewall
- BDevice pin
- CUSB data blocker
- DBiometrics
122A company has drafted an insider-threat policy that prohibits the use of external storage devices. Which of the following would BEST protect the company from data exfiltration via removable media?
- AMonitoring large data transfer transactions in the firewall logs
- BDeveloping mandatory training to educate employees about the removable media policy
- CImplementing a group policy to block user access to system files
- DBlocking removable-media devices and write capabilities using a host-based security tool
123A financial organization has adopted a new secure, encrypted document-sharing application to help with its customer loan process. Some important PII needs to be shared across this new platform, but it is getting blocked by the DLP systems. Which of the following actions will BEST allow the PII to be shared with the secure application without compromising the organization's security posture?
- AConfigure the DLP policies to allow all PII
- BConfigure the firewall to allow all ports that are used by this application
- CConfigure the antivirus software to allow the application
- DConfigure the DLP policies to whitelist this application with the specific PII
- EConfigure the application to encrypt the PII
124A recently discovered zero-day exploit utilizes an unknown vulnerability in the SMB network protocol to rapidly infect computers. Once infected, computers are encrypted and held for ransom. Which of the following would BEST prevent this attack from reoccurring?
- AConfigure the perimeter firewall to deny inbound external connections to SMB ports.
- BEnsure endpoint detection and response systems are alerting on suspicious SMB connections.
- CDeny unauthenticated users access to shared network folders.
- DVerify computers are set to install monthly operating system, updates automatically.
125A company needs to centralize its logs to create a baseline and have visibility on its security events. Which of the following technologies will accomplish this objective?
- ASecurity information and event management
- BA web application firewall
- CA vulnerability scanner
- DA next generation firewall
126An organization routes all of its traffic through a VPN Most users are remote and connect into a corporate datacenter that houses confidential information There is a firewall at the Internet border followed by a DLP appliance, the VPN server and the datacenter itself. Which of the following is the WEAKEST design element?
- AThe DLP appliance should be integrated into a NGFW.
- BSplit-tunnel connections can negatively impact the DLP appliance's performance
- CEncrypted VPN traffic will not be inspected when entering or leaving the network
- DAdding two hops in the VPN tunnel may slow down remote connections
127Users at an organization have been installing programs from the internet on their workstations without first proper authorization. The organization maintains a portal from which users can install standardized programs. However, some users have administrative access on their workstations to enable legacy programs to function property. Which of the following should the security administrator consider implementing to address this issue?
- AApplication code signing
- BApplication whitelisting
- CData loss prevention
- DWeb application firewalls
128A security Administrator is reviewing the following firewall configuration after receiving reports that users are unable to connect to remote websites:
10 PERMIT FROM:ANY TO:ANY PORT:80
20 PERMIT FROM:ANY TO:ANY PORT:443
30 DENY FROM:ANY TO:ANY PORT:ANY
Which of the following is MOST secure solution the administrator can implement to fix this issue?- AAdd the following rule to the firewall: 5 PERMIT FROM:ANY TO:ANY PORT:53
- BReplace rule number 10 with the following: 10 PERMIT FROM:ANY TO:ANY PORT:22
- CInsert the following rule in the firewall: 25 PERMIT FROM:ANY TO:ANY PORTS:ANY
- DRemove the following rule from the firewall: 30 DENY FROM:ANY TO:ANY PORT:ANY
129An employee workstation with an IP address of 201.211.38.211/24 reports it is unable to submit print jobs to a network printer at 204.211.38.52/24 after a firewall upgrade. The active firewall rules are as follows:
IP Address Protocol Port Number Action
204.211.38.1/24 ALL ALL Permit
204.211.38.211/24 ALL ALL Permit
204.211.38.52/24 UDP 631 Permit
204.211.38.52/24 TCP 25 Deny
Assuming port numbers have not been changed from their defaults, which of the following should be modified to allow printing to the network printer?- AThe permit statement for 204.211.38.52/24 should be changed to TCP port 631 instead of UDP.
- BThe deny statement for 204.211.38.52/24 should be changed to a permit statement.
- CThe permit statement for 204.211.38.52/24 should be changed to UDP port 443 instead of 631.
- DThe permit statement for 204.211.38.211/24 should be changed to TCP port 631 only instead of ALL.
130An organization's research department uses workstations in an air-gapped network. A computer released products based on files that originated in the research department. Which of the following should management do to improve the security and confidentiality of the research files?
- AImplement multifactor authentication on the workstations
- BConfigure removable media controls on the workstations
- CInstall a web application firewall in the research department
- DInstall HIDS on each of the research workstations
131A customer calls a technician and needs to remotely connect to a web server to change some code manually. The technician needs to configure the user’s machine with protocols to connect to the UNIX web server, which is behind a firewall. Which of the following protocols does the technician MOST likely need to configure?
- ASSH
- BSFTP
- CHTTPS
- DSNMP
132A member of the human resources department is searching for candidate resumes and encounters the following error message when attempting to access popular job search websites:
Site Cannot Be Displayed: Unauthorized Access
Policy Violation: Job Search
User Group: Retail_Employee_Access
Client Address: 10.13.78.145
DNS Server: 10.1.1.9
Proxy IP Address: 10.1.1.29
Contact your systems administrator for assistance.
Which of the following would resolve this issue without compromising the company’s security policy?- ARenew the DNS settings and IP address on the employee’s computer.
- BAdd the employee to a less restrictive group on the content filter.
- CRemove the proxy settings from the employee’s web browser
- DCreate an exception for the job search sites in the host-based firewall on the employee’s computer.
133A security analyst wants to limit the use of USB and external drives to protect against malware, as well as protect files leaving a user’s computer. Which of the following is the BEST method to use?
- AFirewall
- BRouter
- CAntivirus software
- DData loss prevention
134A member of the human resources department received the following email message after sending an email containing benefit and tax information to a candidate:
"Your message has been quarantined for the following policy violation: external_potential_PII. Please contact
the IT security administrator for further details."
Which of the following BEST describes why the message was received?- AThe DLP system flagged the message
- BThe mail gateway prevented the message from being sent to personal email addresses
- CThe company firewall blocked the recipient's IP address
- DThe file integrity check failed for the attached files
135A Chief Security Officer (CSO) is concerned about the amount of PII that is stored locally on each salesperson's laptop. The sales department has a higher-than-average rate of lost equipment. Which of the following recommendations would BEST address the CSO's concern?
- ADeploy an MDM solution
- BImplement managed FDE
- CReplace all hard drives with SEDs
- DInstall DLP agents on each laptop
136An organization with a low tolerance for user inconvenience wants to protect laptop hard drives against loss or data theft. Which of the following would be the MOST acceptable?
- ASED
- BHSM
- CDLP
- DTPM
137A startup company is using multiple SaaS and IaaS platforms to stand up a corporate infrastructure and build out a customer-facing web application. Which of the following solutions would be BEST to provide security, manageability, and visibility into the platforms?
- ASIEM
- BDLP
- CCASB
- DSWG
138A security audit has revealed that a process control terminal is vulnerable to malicious users installing and
executing software on the system. The terminal is beyond end-of-life support and cannot be upgraded, so it is
placed on a protected network segment. Which of the following would be MOST effective to implement to
further mitigate the reported vulnerability?- ADNS sinkholing
- BDLP rules on the terminal
- CAn IP blacklist
- DApplication whitelisting
139A security analyst has received an alert about being sent via email. The analyst's Chief information Security Officer (CISO) has made it clear that PII must be handled with extreme care From which of the following did the alert MOST likely originate?
- AS/MIME
- BDLP
- CIMAP
- DHIDS
140A RAT that was used to compromise an organization's banking credentials was found on a user's computer. The RAT evaded antivirus detection. It was installed by a user who has local administrator rights to the system as part of a remote management tool set. Which of the following recommendations would BEST prevent this from reoccurring?
- ACreate a new acceptable use policy
- BSegment the network into trusted and untrusted zones
- CEnforce application whitelisting
- DImplement DLP at the network boundary
141Which of the following would BEST identify and remediate a data-loss event in an enterprise using third-party, web-based services and file-sharing platforms?
- ASIEM
- BCASB
- CUTM
- DDLP
142During a recent audit, several undocumented and unpatched devices were discovered on the internal network. Which of the following can be done to prevent similar occurrences?
- ARun weekly vulnerability scans and remediate any missing patches on all company devices.
- BImplement rogue system detection and configure automated alerts for new devices.
- CInstall DLP controls and prevent the use of USB drives on devices.
- DConfigure the WAPs to use NAC and refuse connections that do not pass the health check.
143A salesperson often uses a USB drive to save and move files from a corporate laptop. The corporate laptop was recently updated, and now the files on the USB are read-only. Which of the following was recently added to the laptop?
- AAntivirus software
- BFile integrity check
- CHIPS
- DDLP
144A user attempts to send an email to an external domain and quickly receives a bounce-back message. The user then contacts the help desk stating the message is important and needs to be delivered immediately. While digging through the email logs, a systems administrator finds the email and bounce-back details:
Your email has been rejected because it appears to contain SSN information.
Sending SSN information via email to external recipients violates company policy.
Which of the following technologies successfully stopped the email from being sent?- ADLP
- BUTM
- CWAF
- DDEP
145The director of information security at a company has recently directed the security engineering team to implement new security technologies aimed at reducing the impact of insider threats. Which of the following tools has the team MOST likely deployed? (Select TWO)
- ADLP
- BUTM
- CSFTP
- DSSH
- ESSL
146A root cause analysis reveals that a web application outage was caused by one of the company's developers uploading a newer version of the third-party libraries that were shared among several applications. Which of the following implementations would be BEST to prevent the issue from reoccurring?
- ACASB
- BSWG
- CContainerization
- DAutomated failover
147A company has decided to move its operations to the cloud. It wants to utilize technology that will prevent users from downloading company applications for personal use, restrict data that is uploaded, and have visibility into which applications are being used across the company. Which of the following solutions will BEST meet these requirements?
- AAn NGFW
- BA CASB
- CApplication whitelisting
- DAn NG-SWG
148A network administrator is concerned about users being exposed to malicious content when accessing company cloud applications. The administrator wants to be able to block access to sites based on an AUP. The users must also be protected because many of them work from home or at remote locations, providing on-site technical support. Which of the following should the administrator employ to meet these criteria?
- AImplement NAC
- BImplement a SWG
- CImplement an URL filter
- DImplement an MDM
149A network engineer needs to build a solution that will allow guests at the company's headquarters to access the Internet via WiFi. This solution should not allow access to the internal corporate network, but it should require guests to sign off on the acceptable use policy before accessing the Internet. Which of the following should the engineer employ to meet these requirements?
- AImplement open PSK on the APs
- BDeploy a WAF
- CConfigure WIPS on the APs
- DInstall a captive portal
150A security engineer is installing a WAF to protect the company's website from malicious web requests over SSL. Which of the following is needed to meet the objective?
- AA reverse proxy
- BA decryption certificate
- CA split-tunnel VPN
- DLoad balanced servers
151A user recently entered a username and password into a recruiting application website that had been forged to look like the legitimate site Upon investigation, a security analyst the identifies the following:
* The legitimate websites IP address is 10.1.1.20 and eRecruit local resolves to the IP
* The forged website's IP address appears to be 10.2.12.99. based on NetFlow records
* AH three at the organization's DNS servers show the website correctly resolves to the legitimate IP
* DNS query logs show one of the three DNS servers returned a result of 10.2.12.99 (cached) at the approximate time of the suspected compromise.
Which of the following MOST likely occurred?- AA reverse proxy was used to redirect network traffic
- BAn SSL strip MITM attack was performed
- CAn attacker temporarily pawned a name server
- DAn ARP poisoning attack was successfully executed
152Which of the following are requirements that must be configured for PCI DSS compliance? (Select TWO).
- ATesting security systems and processes regularly
- BInstalling and maintaining a web proxy to protect cardholder data
- CAssigning a unique ID to each person with computer access
- DEncrypting transmission of cardholder data across private networks
- EBenchmarking security awareness training for contractors
- FUsing vendor-supplied default passwords for system passwords
153Ann, a user, reports she is receiving emails that appear to be from organizations to which she belongs, but the emails contain links to websites that do not belong to those organizations. Which of the following security scenarios does this describe?
- AA hacker is using Ann’s social media information to create a spear phishing attack.
- BThe DNS servers for the organizations have been hacked and are pointing to malicious sites.
- CThe company’s mail system has changed the organization’s links to point to a proxy server for security.
- DAnn’s computer is infected with adware that has changed the email links.
154A company recently experienced data exfiltration via the corporate network. In response to the breach, a security analyst recommends deploying an out-of-band IDS solution. The analyst says the solution can be implemented without purchasing any additional network hardware. Which of the following solutions will be used to deploy the IDS?
- ANetwork tap
- BNetwork proxy
- CHoneypot
- DPort mirroring
155An incident response analyst at a large corporation is reviewing proxy log data. The analyst believes a malware infection may have occurred. Upon further review, the analyst determines the computer responsible for the suspicious network traffic is used by the Chief Executive Officer (CEO). Which of the following is the best NEXT step for the analyst to take?
- ACall the CEO directly to ensure awareness of the event.
- BRun a malware scan on the CEO's workstation.
- CReimage the CEO's workstation.
- DDisconnect the CEO's workstation from the network.
156Which of the following development models entails several iterative and incremental software development methodologies such as Scrum?
- ASpiral
- BWaterfall
- CAgile
- DRapid
157Which of the following models is considered as iterative approach with frequent testing?
- AAgile
- BWaterfall
- CDevOps
- DSandboxing
158A security analyst has been asked to investigate a situation after the SOC started to receive alerts from the SIEM. The analyst first looks at the domain controller and finds the following events (see 1st photo)
To better understand what is going on, the analyst runs a command and receives the following output (see 2nd photo)
Based on the analyst's findings, which of the following attacks is being executed?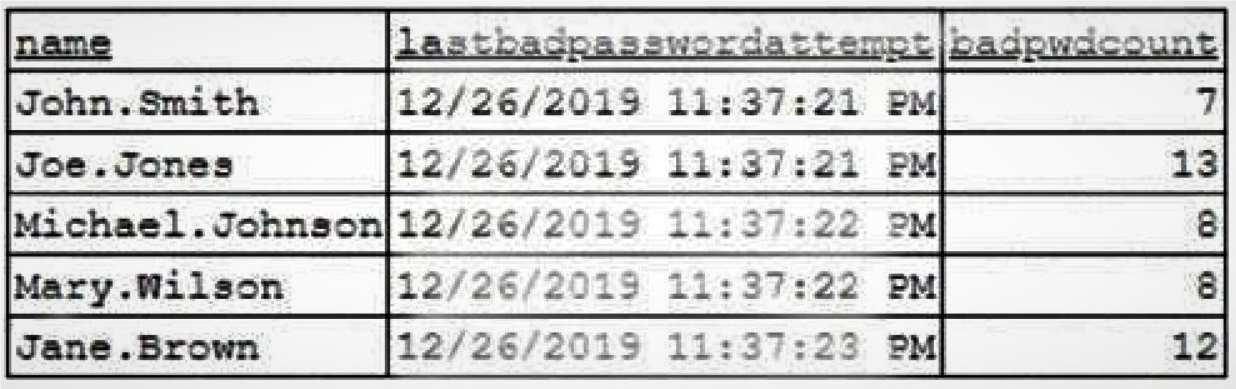
- ACredential harvesting
- BKeylogger
- CBrute-force
- DSpraying
159A security analyst is looking for a solution to help communicate to the leadership team the severity levels of the organization's vulnerabilities. Which of the following would BEST meet this need?
- ACVE
- BSIEM
- CSOAR
- DCVSS
160A security analyst receives a SIEM alert that someone logged in to the appadmin test account, which is only used for the early detection of attacks. The security analyst then reviews the following application log:
Which of the following can the security analyst conclude?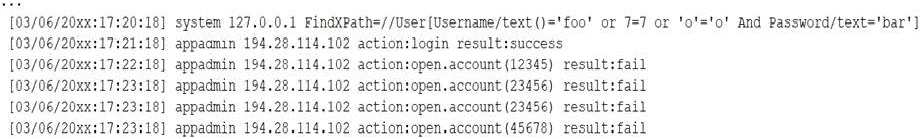
- AA replay attack is being conducted against the application.
- BAn injection attack is being conducted against a user authentication system.
- CA service account password may have been changed, resulting in continuous failed logins within the application.
- DA credentialed vulnerability scanner attack is testing several CVEs against the application.
161A security analyst is reviewing information regarding recent vulnerabilities. Which of the following will the analyst MOST likely consult to validate which platforms have been affected?
- AOSINT
- BSIEM
- CCVSS
- DCVE
162A security analyst is investigating an incident to determine what an attacker was able to do on a compromised laptop. The analyst reviews the following SIEM log:
Which of the following describes the method that was used to compromise the laptop?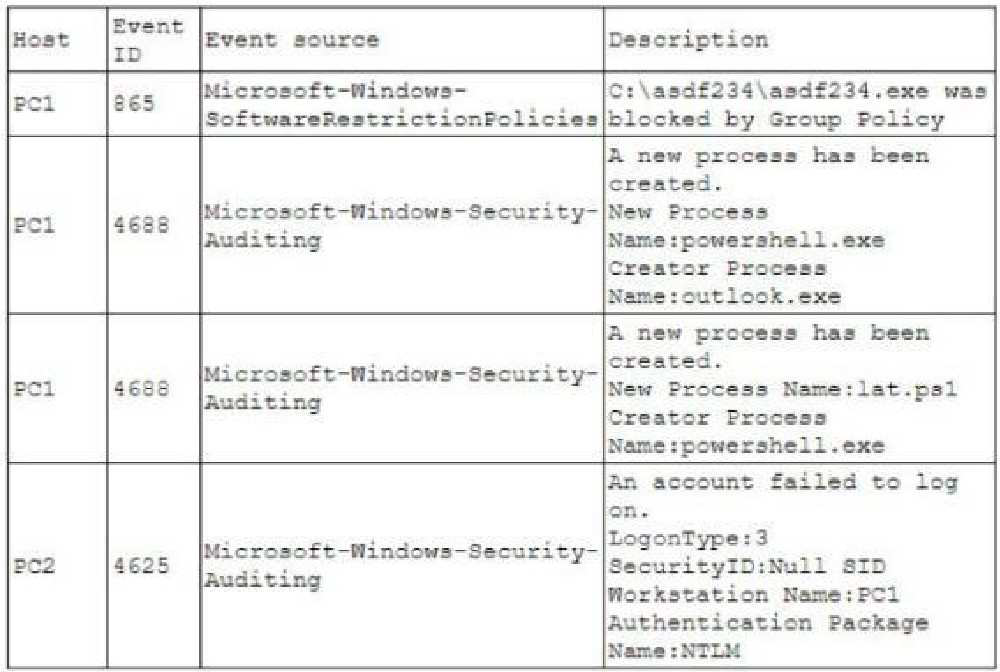
- AAn attacker was able to move laterally from PC1 to PC2 using a pass-the-hash attack
- BAn attacker was able to bypass application whitelisting by emailing a spreadsheet attachment with an embedded PowerShell in the file
- CAn attacker was able to install malware to the CAasdf234 folder and use it to gain administrator nights and launch Outlook
- DAn attacker was able to phish user credentials successfully from an Outlook user profile
163A penetration tester was able to connect to a company’s internal network and perform scans and staged attacks for the duration of the testing period without being noticed. The SIEM didn’t alert the security team to the presence of the penetration tester’s devices on the network. Which of the following would provide the security team with notification in a timely manner?
- AImplement rogue system detection and sensors.
- BCreate a trigger on the IPS and alert the security team when unsuccessful logins occur.
- CDecrease the correlation threshold for alerts on the SIEM.
- DRun a credentialed vulnerability scan.
164A security administrator is implementing a SIEM and needs to ensure events can be compared against each other based on when the events occurred and were collected. Which of the following does the administrator need to implement to ensure this can be accomplished?
- ATOTP
- BTKIP
- CNTP
- DHOTP
165Which of the following describes the ability of code to target a hypervisor from inside?
- AFog computing
- BVM escape
- CImage forgery
- DContainer breakout
166A company is planning to utilize its legacy desktop systems by converting them into dummy terminals and moving all heavy applications and storage to a centralized server that hosts all of the company’s required desktop applications. Which of the following describes the BEST deployment method to meet these requirements?
- AIaaS
- BVM Sprawl
- CVDI
- DPaaS
167Which of the following BEST explains why sandboxing is a best practice of testing software from an untrusted vendor prior to an enterprise deployment?
- AIt allows the software to run in an unconstrained environment with full network access.
- BIt eliminates the possibility of privilege escalation attacks against the local VM host.
- CIt facilitates the analysis of possible malware by allowing it to run until resources are exhausted.
- DIt restricts the access of the software to a contained logical space and limits possible damage.
168Which of the cloud model provides clients with servers, storage, and networks, but nothing else?
- ASaaS
- BPaaS
- CIaaS
- DDaaS
169A small retail business has a local store and a newly established and growing online storefront. A recent storm caused a power outage to the business and the local ISP, resulting in several hours of lost sales and delayed order processing. The business owner now needs to ensure two things:
- Protection from power outages
- Always-available connectivity in case of an outage.
The owner has decided to implement battery backup for the computer equipment. Which of the following would BEST fulfill the owner's second need?- ALease a telecommunications line to provide POTS for dial-up access
- BConnect the business router to its own dedicated UPS
- CPurchase services from a cloud provider for high availability
- DReplace the business's wired network with a wireless network
170A Chief Information Security Officer (CISO) is concerned about the organization’s ability to continue business operations in the event of a prolonged DDoS attack on its local datacenter that consumes server resources. Which of the following will the CISO MOST likely recommend to mitigate this risk?
- AUpgrade the bandwidth available into the datacenter.
- BImplement a hot-site failover location.
- CSwitch to complete SaaS offering to customers.
- DImplement a challenge response test on all end-user queries.
- EMigrate to a geographically dispersed cloud datacenter.
171An organization had implemented a two-step verification process to protect user access to data that is stored
in the cloud. Each employee now uses an email address or mobile number to receive a code to access the
data. Which of the following authentication methods did the organization implement?- AToken key
- BStatic code
- CPush notification
- DHOTP
172To reduce costs and overhead, an organization wants to move from an on-premises email solution to a cloud-based email solution. At this time, no other services will be moving. Which of the following cloud models would BEST meet the needs of the organization?
- AMaaS
- BIaaS
- CSaaS
- DPaaS
173address the following:
- Centrally managing mobile devices
- Data loss prevention
Which of the following recommendations should the administrator include in the assessment? (Select TWO).- AImplement encryption.
- BImplement hashing.
- CImplement an MDM with mobile device hardening.
- DImplement a VPN with secure connection to webmail.
- EImplement and allow cloud storage features on the network.
174A financial institution would like to store its customer data in the cloud but still allow the data to be accessed and manipulated while encrypted. Doing so would prevent the cloud service provider from being able to decipher the data due to its sensitivity. The financial institution is not concerned about computational overheads and slow speeds. Which of the following cryptographic techniques would BEST meet the requirements?
- AAsymmetric
- BSymmetric
- CHomomorphic
- DEphereal
175Which of the following is a risk that is specifically associated with hosting applications in the public cloud?
- AUnsecured root accounts
- BZero-day
- CShared tenancy
- DInsider threat
176An organization has decided to host its web application and database in the cloud. Which of the following BEST describes the security concerns for this decision?
- AAccess to the organization’s servers could be exposed to other cloud-provider clients.
- BThe cloud vendor is a new attack vector within the supply chain.
- COutsourcing the code development adds risk to the cloud provider.
- DVendor support will cease when the hosting platforms reach EOL.
177SSH (Secure Shell)
Port# = [blank_start]22[blank_end]
Protocol = [blank_start]TCP[blank_end]- A22
- BTCP
178Telnet
Port # = [blank_start]23[blank_end]
Protocol = [blank_start]TCP[blank_end]- A23
- BTCP
179HTTP (HyperText Transfer Protocol)
Port# = [blank_start]80[blank_end]
Protocol = [blank_start]TCP[blank_end]- A80
- BTCP
180HTTPS (Secure HTTP)
Port# = [blank_start]443[blank_end]
Protocol = [blank_start]TCP[blank_end]- A443
- BTCP
181SMTP
Port# = [blank_start]25[blank_end]
Protocol = [blank_start]TCP[blank_end]- A25
- BTCP
182POP
Port# = [blank_start]110[blank_end]
Protocol = [blank_start]TCP[blank_end]- A110
- BTCP
183IMAP
Port# = [blank_start]143[blank_end]
Protocol = [blank_start]TCP[blank_end]- A143
- BTCP
184LDAP
Port# = [blank_start]389[blank_end]
Protocol = [blank_start]both[blank_end]- A389
- Bboth
185LDAPS (Secure LDAP)
Port# = [blank_start]636[blank_end]
Protocol = [blank_start]both[blank_end]- A636
- Bboth
186RADIUS
Port # = [blank_start]1812[blank_end]
Protocol = [blank_start]both[blank_end]- A1812
- Bboth
187NTP
Port # = [blank_start]123[blank_end]
Protocol = [blank_start]UDP[blank_end]- A123
- BUDP
188DHCP
Server Port # = [blank_start]67[blank_end]
Client Port # = [blank_start]68[blank_end]
Protocol = [blank_start]UDP[blank_end]- A67
- B68
- CUDP
189DNS
Port# = [blank_start]53[blank_end]
Protocol = [blank_start]UDP[blank_end]- A53
- BUDP
190SIP (Session Initiation Protocol)
Non-TLS Port# = [blank_start]5060[blank_end]
TLS Port# = [blank_start]5061[blank_end]
Protocol = [blank_start]both[blank_end]- A5060
- B5061
- Cboth
191H.323
Port# = [blank_start]1720[blank_end]
Protocol = [blank_start]TCP[blank_end]- A1720
- BTCP
192A network administrator would like to configure a site-to-site VPN utilizing iPSec. The administrator wants the tunnel to be established with data integrity encryption, authentication and anti- replay functions Which of the following should the administrator use when configuring the VPN?
- AAH
- BEDR
- CESP
- DDNSSEC
193Phishing and spear-phishing attacks have been occurring more frequently against a company's staff. Which of the following would MOST likely help mitigate this issue?
- ADNSSEC and DMARC
- BDNS query logging
- CExact mail exchanger records in the DNS
- DThe addition of DNS conditional forwarders
194An organization’s Chief Information Officer (CIO) read an article that identified leading hacker trends and attacks, one of which is the alteration of URLs to IP addresses resulting in users being redirected to malicious websites. To reduce the chances of this happening in the organization, which of the following secure protocols should be implemented?
- ADNSSEC
- BIPSec
- CLDAPS
- DHTTPS
195As part of a corporate merger, two companies are combining resources. As a result, they must transfer files through the Internet in a secure manner. Which of the following protocols would BEST meet this objective? (Select TWO).
- ALDAPS
- BSFTP
- CHTTPS
- DDNSSEC
- ESRTP
196Users are attempting to access a company's website but are transparently redirected to another website. The users confirm the URL is correct. Which of the following would BEST prevent this issue in the future?
- ADNSSEC
- BHTTPS
- CIPSec
- DTLS/SSL
197A security analyst has been asked to implement secure protocols to prevent cleartext credentials from being transmitted over the internal network. Which of the following protocols is the security analyst MOST likely to implement? (Select TWO).
- ASNMPv3
- BS/MIME
- CDNSSEC
- DSSH
- ESFTP
198A systems administrator recently issued a public/private key pair that will be used for the company’s DNSSEC implementation. Which of the following configurations should the systems administrator implement NEXT?
- ACreate a DNSKEY resource with the public key.
- BInstall the private key using the RRSIG record.
- CPoint the DS record to the company authoritative servers.
- DAdd TCP port 443 to the DNS listener.
199A document that appears to be malicious has been discovered in an email that was sent to a company's Chief Financial Officer (CFO). Which of the following would be BEST to allow a security analyst to gather information and confirm it is a malicious document without executing any code it may contain?
- AOpen the document on an air-gapped network
- BView the document's metadata for origin clues
- CSearch for matching file hashes on malware websites
- DDetonate the document in an analysis sandbox
200A well-known organization has been experiencing attacks from APTs. The organization is concerned that custom malware is being created and emailed into the company or installed on USB sticks that are dropped in parking lots. Which of the following is the BEST defense against this scenario?
- AConfiguring signature-based antivirus io update every 30 minutes
- BEnforcing S/MIME for email and automatically encrypting USB drives upon insertion.
- CImplementing application execution in a sandbox for unknown software.
- DFuzzing new files for vulnerabilities if they are not digitally signed
Informationen
- Beschreibung
- Security+ Computer Studies Quiz am Sec+, erstellt von Andrew C am 04/05/2021.
- Autor
- Andrew C
- Sprache
- English
- Aufrufe
- 10
- Schlagwörter
- Bewertung
- Noch keine Bewertungen Bewerte dieses Quiz