
Mapa mental
CHAPTER 13 Securing Routing Protocols and the Control Plane
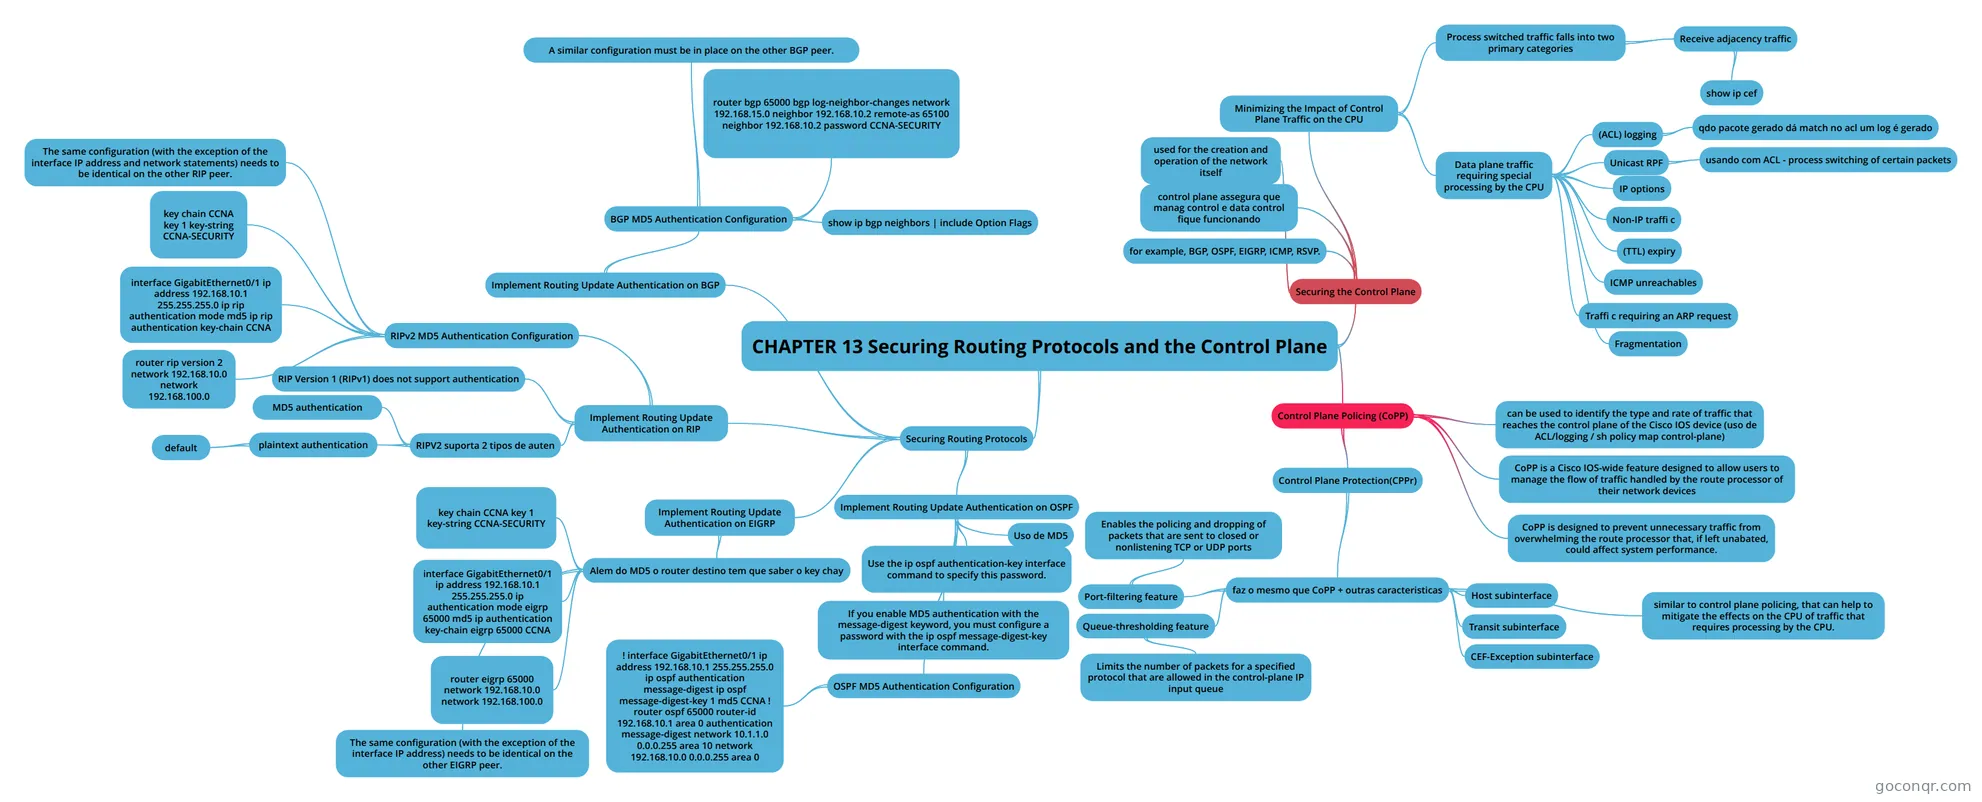
Mapa mental: Securing routing protocols and the control plane
Contenido del mapa
CHAPTER 13 Securing Routing Protocols and the Control Plane
- This chapter begins with a discussion of how to secure the control plane of a router, and specifically through the use of control plane policing (CoPP) and control plane protection (CPPr). The chapter then covers the use of routing update authentication for the following routing protocols: Routing Information Protocol (RIP), Open Shortest Path First (OSPF), Enhanced Interior Gateway Routing Protocol (EIGRP), and Border Gateway Protocol (BGP).
Securing the Control Plane
- control plane assegura que manag control e data control fique funcionando
- used for the creation and operation of the network itself
- for example, BGP, OSPF, EIGRP, ICMP, RSVP.
- Minimizing the Impact of Control Plane Traffic on the CPU
- Process switched traffic falls into two primary categories
- Receive adjacency traffic
- show ip cef
- Receive adjacency traffic
- Data plane traffic requiring special processing by the CPU
- Although this chapter focuses on control plane traffic, there is still a need to address certain data plane traffic (that is, traffic which has a destination beyond, or through, the network device in question). The following types of data plane traffic require special processing by the CPU resulting in a performance impact on the CPU:
- (ACL) logging
- qdo pacote gerado dá match no acl um log é gerado
- Unicast RPF
- usando com ACL - process switching of certain packets
- IP options
- (TTL) expiry
- ICMP unreachables
- Traffi c requiring an ARP request
- Non-IP traffi c
- Fragmentation
- Process switched traffic falls into two primary categories
Control Plane Policing (CoPP)
- can be used to identify the type and rate of traffic that reaches the control plane of the Cisco IOS device (uso de ACL/logging / sh policy map control-plane)
- CoPP is a Cisco IOS-wide feature designed to allow users to manage the flow of traffic handled by the route processor of their network devices
- CoPP is designed to prevent unnecessary traffic from overwhelming the route processor that, if left unabated, could affect system performance.
- Control Plane Protection(CPPr)
- faz o mesmo que CoPP + outras caracteristicas
- Host subinterface
- Transit subinterface
- similar to control plane policing, that can help to mitigate the effects on the CPU of traffic that requires processing by the CPU.
- Port-filtering feature
- Enables the policing and dropping of packets that are sent to closed or nonlistening TCP or UDP ports
- CEF-Exception subinterface
- Queue-thresholding feature
- Limits the number of packets for a specified protocol that are allowed in the control-plane IP input queue
- faz o mesmo que CoPP + outras caracteristicas
Securing Routing Protocols
- Implement Routing Update Authentication on OSPF
- Uso de MD5
- Use the ip ospf authentication-key interface command to specify this password.
- If you enable MD5 authentication with the message-digest keyword, you must configure a password with the ip ospf message-digest-key interface command.
- OSPF MD5 Authentication Configuration
- ! interface GigabitEthernet0/1 ip address 192.168.10.1 255.255.255.0 ip ospf authentication message-digest ip ospf message-digest-key 1 md5 CCNA ! router ospf 65000 router-id 192.168.10.1 area 0 authentication message-digest network 10.1.1.0 0.0.0.255 area 10 network 192.168.10.0 0.0.0.255 area 0
- Implement Routing Update Authentication on EIGRP
- Alem do MD5 o router destino tem que saber o key chay
- key chain CCNA key 1 key-string CCNA-SECURITY
- interface GigabitEthernet0/1 ip address 192.168.10.1 255.255.255.0 ip authentication mode eigrp 65000 md5 ip authentication key-chain eigrp 65000 CCNA
- router eigrp 65000 network 192.168.10.0 network 192.168.100.0
- The same configuration (with the exception of the interface IP address) needs to be identical on the other EIGRP peer.
- Alem do MD5 o router destino tem que saber o key chay
- Implement Routing Update Authentication on RIP
- RIPV2 suporta 2 tipos de auten
- plaintext authentication
- default
- MD5 authentication
- plaintext authentication
- RIP Version 1 (RIPv1) does not support authentication
- RIPv2 MD5 Authentication Configuration
- key chain CCNA key 1 key-string CCNA-SECURITY
- interface GigabitEthernet0/1 ip address 192.168.10.1 255.255.255.0 ip rip authentication mode md5 ip rip authentication key-chain CCNA
- router rip version 2 network 192.168.10.0 network 192.168.100.0
- The same configuration (with the exception of the interface IP address and network statements) needs to be identical on the other RIP peer.
- RIPV2 suporta 2 tipos de auten
- Implement Routing Update Authentication on BGP
- BGP MD5 Authentication Configuration
- router bgp 65000 bgp log-neighbor-changes network 192.168.15.0 neighbor 192.168.10.2 remote-as 65100 neighbor 192.168.10.2 password CCNA-SECURITY
- A similar configuration must be in place on the other BGP peer.
- show ip bgp neighbors | include Option Flags
- BGP MD5 Authentication Configuration
- Implement Routing Update Authentication on OSPF
Información
- Descripción
- Cisco 210 - 260 CCNA security Estudo principal Mapa Mental sobre CHAPTER 13 Securing Routing Protocols and the Control Plane, creado por alessandro moreira el 19/10/2016.
- Creado por
- alessandro moreira
- Visitas
- 2
- Valoración