
Test
Practice Test 2-1
Crea una cuenta gratis para terminar este test
Guarda tu progreso y consulta tu resultado final.
¿Ya tienes cuenta? Inicia sesión
Preguntas del test (46)
1What is the benefit of VNet peering?
- AEnhanced security
- BRegulatory compliance
- CMore bandwidth
- DVM connectivity using private IPs
2Which port is used to remotely manage Linux hosts?
- A22
- B443
- C3389
- D80
3You want all outbound subnet traffic to first be sent to a firewall appliance for inspection. Which IP address should you specify for the firewall?
- AFirewall public IP
- B0.0.0.0/0
- C127.0.0.0/0
- DFirewall private IP
4Which statement best describes encrypting stored data?
- AProtecting data in transit
- BProtecting data at rest
- CProtecting data in process
- DProtecting data in archives
5You are configuring a DNAT rule in Azure Firewall to allow incoming SSH management of Linux VMs. Which IP addresses should you specify in the DNAT rule?
- AVM public IP
- BVM private IP
- CFirewall public IP
- DFirewall private IP
6You have manually deployed a cloud-based Linux virtual machine. Which type of cloud service model is this?
- AIaaS
- BPaaS
- CSaaS
- DSECaaS
7Which cloud items can a network security group be associated with?
- AVNet
- BvNIC
- CVPC
- DSubnet
8What is the purpose of the STAR registry?
- AAssurance of cloud provider security accreditations
- BStorage of custom application container images
- CCloud provider SLA listing
- DCentralized cloud-based IAM
9Which term is the most closely associated with autoscaling?
- AAutomation
- BHorizontal scaling
- CVertical scaling
- DTemplate
10Which type of cloud is owned and used by a single organization?
- APrivate
- BPublic
- CCommunity
- DHybrid
11What is contained within a cloud-based virtual network?
- ASubnets
- BNetwork security groups
- CResource groups
- DRoute tables
12Which types of rules can be configured with Azure Firewall?
- AHTTP
- BDNAT
- CApplication
- DProxy
13What is the most common consequence of SLA uptime requirements violations?
- AService credits
- BFree unlimited service usage
- CDamages awarded
- DLawsuit
14What is used to determine the order in which cloud security group rules are processed?
- AIP address
- BUDP port number
- CTCP port number
- DPriority value
15Which port is used to remotely manage Windows hosts?
- A443
- B3389
- C80
- D22
16Which cloud computing characteristic refers to paying for services used?
- AMetered usuage
- BRapid elasticity
- CPooled resources
- DBroad network access
17Which types of items can be stored in a cloud key vault?
- AEncryption keys
- BLinux root passwords
- CWindows admin passwords
- DPKI certificates
18A video-game developer has received reports of players who are cheating. All game players each have five capabilities that are ranked on a scale of 1 to 10 points, with 10 total points available for balance. Players can move these points between capabilities at any time. The programming logic is as follows:
• A player asks to move points from one capability to another
•. The source capability must have enough points to allow the move
•. The destination capability must not exceed 10 after the move
•. The move from source capability to destination capability is then completed
The timestamps of the game logs show each step of the transfer process takes about 900ms However,
the timestamps of the cheating players show capability transfers at the exact same time. The cheating
players have 10 points in multiple capabilities.
Which of the following is MOST likely being exploited to allow these capability transfers?- ATOC/TOU
- BCSRF
- CMemory leak
- DXSS
- ESQL injection
- FInteger overflow
19An organization has established the following controls matrix:
(See Attached Image)
The following control sets have been defined by the organization and are applied in an aggregate fashion:
✑ Systems containing PII are protected with the minimum control set.
✑ Systems containing medical data are protected at the moderate level.
✑ Systems containing cardholder data are protected at the high level.
The organization is preparing to deploy a system that protects the confidentially of a database containing
PII and medical data from clients. Based on the controls classification, which of the following controls would BEST meet these requirements?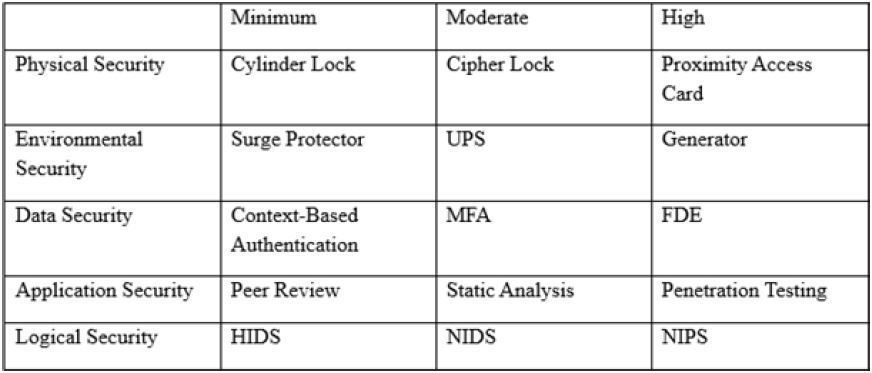
- AProximity card access to the server room, context-based authentication, UPS, and full-disk encryption for the database server.
- BCipher lock on the server room door, FDE, surge protector, and static analysis of all application code.
- CPeer review of all application changes, static analysis of application code, UPS, and penetration testing of the complete system.
- DIntrusion detection capabilities, network-based IPS, generator, and context-based authentication.
20A new cluster of virtual servers has been set up in a lab environment and must be audited before being allowed on the production network. The security manager needs to ensure unnecessary services are disabled and all system accounts are using strong credentials. Which of the following tools should be used? (Choose two.)
- AFuzzer
- BSCAP scanner
- CPacket analyzer
- DPassword cracker
- ENetwork enumerator
- FSIEM
21A large enterprise with thousands of users is experiencing a relatively high frequency of malicious activity from the insider threats. Much of the activity appears to involve internal reconnaissance that results in targeted attacks against privileged users and network file shares.
Given this scenario, which of the following would MOST likely prevent or deter these attacks?
(Choose two.)- AConduct role-based training for privileged users that highlights common threats against them and covers best practices to thwart attacks
- BIncrease the frequency at which host operating systems are scanned for vulnerabilities, and decrease the amount of time permitted between vulnerability identification and the application of corresponding patches
- CEnforce command shell restrictions via group policies for all workstations by default to limit which native operating system tools are available for use
- DModify the existing rules of behavior to include an explicit statement prohibiting users from enumerating user and file directories using available tools and/or accessing visible resources that do not directly pertain to their job functions
- EFor all workstations, implement full-disk encryption and configure UEFI instances to require complex passwords for authentication
- FImplement application blacklisting enforced by the operating systems of all machines in the enterprise
22A recent assessment identified that several users’ mobile devices are running outdated versions of
endpoint security software that do not meet the company’s security policy. Which of the following should be performed to ensure the users can access the network and meet the company’s security requirements?- AVulnerability assessment
- BRisk assessment
- CPatch management
- DDevice quarantine
- EIncident management
23A business is growing and starting to branch out into other locations. In anticipation of opening an office in a different country, the Chief Information Security Officer (CISO) and legal team agree they need to meet the following criteria regarding data to open the new office:
✑ Store taxation-related documents for five years
✑ Store customer addresses in an encrypted format
✑ Destroy customer information after one year
✑ Keep data only in the customer’s home country
Which of the following should the CISO implement to BEST meet these requirements?
(Choose three.)- ACapacity planning policy
- BData retention policy
- CData classification standard
- DLegal compliance policy
- EData sovereignty policy
- FBackup policy
- GAcceptable use policy
- HEncryption standard
24Following a recent security incident on a web server, the security analyst takes HTTP traffic captures for further investigation. The analyst suspects certain jpg files have important data hidden within them. Which of the following tools will help get all the pictures from within the HTTP traffic captured to a specified folder?
- Atshark
- Bmemdump
- Cnbtstat
- Ddd
25The government is concerned with remote military missions being negatively being impacted by the use of technology that may fail to protect operational security.
To remediate this concern, a number of solutions have been implemented, including the following:
✑ End-to-end encryption of all inbound and outbound communication, including personal email and chat
sessions that allow soldiers to securely communicate with families.
✑ Layer 7 inspection and TCP/UDP port restriction, including firewall rules to only allow TCP port 80 and
443 and approved applications
✑ A host-based whitelist of approved websites and applications that only allow mission-related tools and sites
✑ The use of satellite communication to include multiple proxy servers to scramble the source IP address
Which of the following is of MOST concern in this scenario?- AMalicious actors intercepting inbound and outbound communication to determine the scope of the mission
- BFamily members posting geotagged images on social media that were received via email from soldiers
- CThe effect of communication latency that may negatively impact real-time communication with mission control
- DThe use of centrally managed military network and computers by soldiers when communicating with external parties
26A user workstation was infected with a new malware variant as a result of a drive-by download. The security administrator reviews key controls on the infected workstation and discovers the following:
(See Attached Image)
Which of the following would BEST prevent the problem from reoccurring in the future? (Choose two.)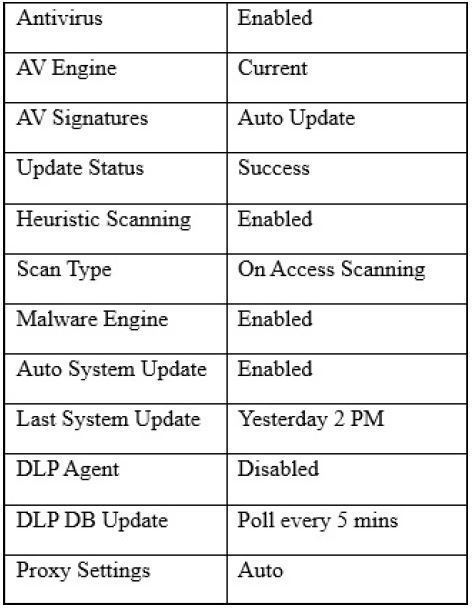
- AInstall HIPS
- BEnable DLP
- CInstall EDR
- DInstall HIDS
- EEnable application blacklisting
- FImprove patch management processes
27A university’s help desk is receiving reports that Internet access on campus is not functioning. The
network administrator looks at the management tools and sees the 1Gbps Internet is completely
saturated with ingress traffic.
The administrator sees the following output on the Internet router:
(See Attached Image)
The administrator calls the university’s ISP for assistance, but it takes more than four hours to speak to a network engineer who can resolve the problem.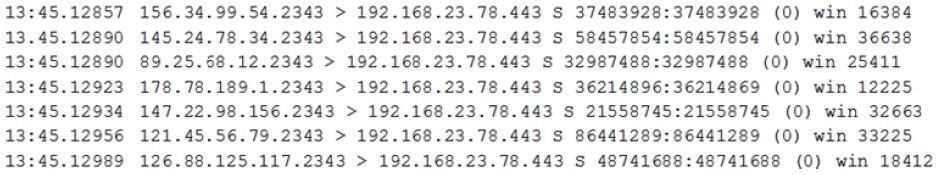
- AThe ISP engineer should null route traffic to the web server immediately to restore Internet connectivity. The university should implement a remotely triggered black hole with the ISP to resolve this more quickly in the future.
- BA university web server is under increased load during enrollment. The ISP engineer should immediately increase bandwidth to 2Gbps to restore Internet connectivity. In the future, the university should pay for more bandwidth to handle spikes in web server traffic.
- CThe ISP engineer should immediately begin blocking IP addresses that are attacking the web server to restore Internet connectivity. In the future, the university should install a WAF to prevent this attack from happening again.
- DThe ISP engineer should begin refusing network connections to the web server immediately to restore Internet connectivity on campus. The university should purchase an IPS device to stop DDoS attacks in the future.
28An internal penetration tester was assessing a recruiting page for potential issues before it was pushed to the production website. The penetration tester discovers an issue that must be corrected before the page goes live. The web host administrator collects the log files below and gives them to the development team so improvements can be made to the security design of the website.
(See Attached Image)
Which of the following types of attack vector did the penetration tester use?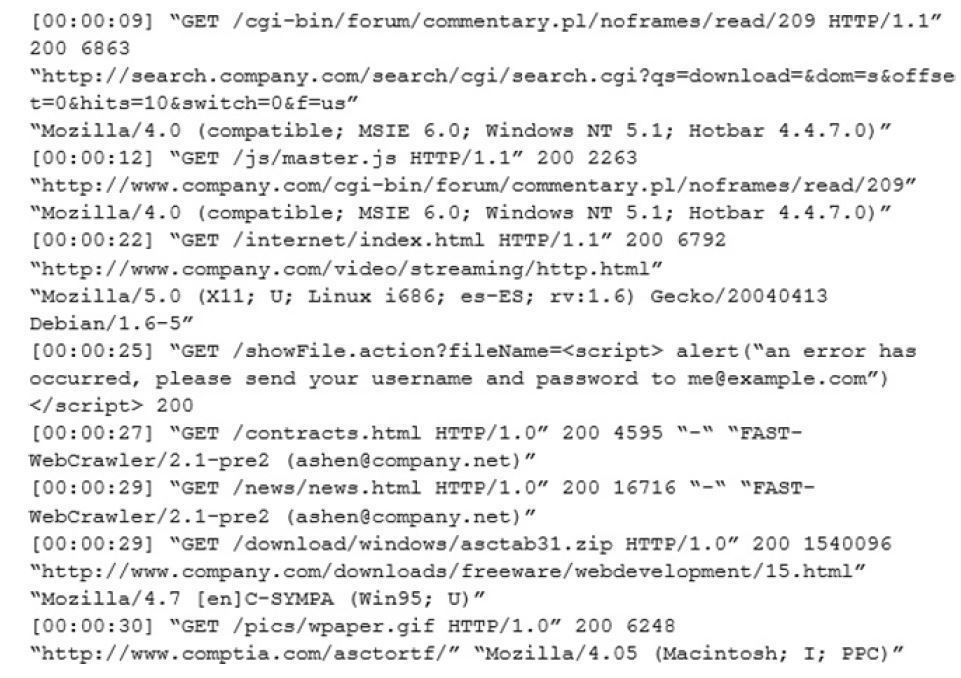
- ASQL injection
- BCSRF
- CBrute force
- DXSS
- ETOC/TOU
29A government entity is developing requirements for an RFP to acquire a biometric authentication system.
When developing these requirements, which of the following considerations is MOST critical to the verification and validation of the SRTM?- ALocal and national laws and regulations
- BSecure software development requirements
- CEnvironmental constraint requirements
- DTestability of requirements
30An organization is currently working with a client to migrate data between a legacy ERP system and a cloud-based ERP tool using a global PaaS provider. As part of the engagement, the organization is performing data deduplication and sanitization of client data to ensure compliance with regulatory requirements.
Which of the following is the MOST likely reason for the need to sanitize the client data?- AData aggregation
- BData sovereignty
- CData isolation
- DData volume
- EData analytics
31A developer emails the following output to a security administrator for review:
(See Attached Image)
Which of the following tools might the security administrator use to perform further security assessment of this issue?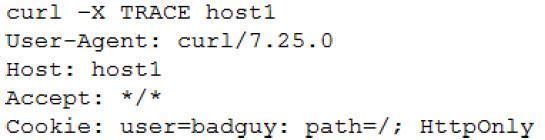
- APort scanner
- BVulnerability scanner
- CFuzzer
- DHTTP interceptor
32A security administrator wants to implement two-factor authentication for network switches and routers. The solution should integrate with the company’s RADIUS server, which is used for authentication to the network infrastructure devices.
The security administrator implements the following:
✑ An HOTP service is installed on the RADIUS server.
✑ The RADIUS server is configured to require the HOTP service for authentication.
The configuration is successfully tested using a software supplicant and enforced across all network devices. Network administrators report they are unable to log onto the network devices because they are not being prompted for the second factor.
Which of the following should be implemented to BEST resolve the issue?- AReplace the password requirement with the second factor. Network administrators will enter their username and then enter the token in place of their password in the password field.
- BConfigure the RADIUS server to accept the second factor appended to the password. Network administrators will enter a password followed by their token in the password field.
- CReconfigure network devices to prompt for username, password, and a token. Network administrators will enter their username and password, and then they will enter the token.
- DInstall a TOTP service on the RADIUS server in addition to the HOTP service. Use the HOTP on older devices that do not support two-factor authentication. Network administrators will use a web portal to log onto these devices.
33After investigating virus outbreaks that have cost the company $1000 per incident, the company’s Chief Information Security Officer (CISO) has been researching new antivirus software solutions to use and be fully supported for the next two years. The CISO has narrowed down the potential solutions to four candidates that meet all the company’s performance and capability requirements:
(See Attached Picture)
Using the table above, which of the following would be the BEST business-driven choice among five possible solutions?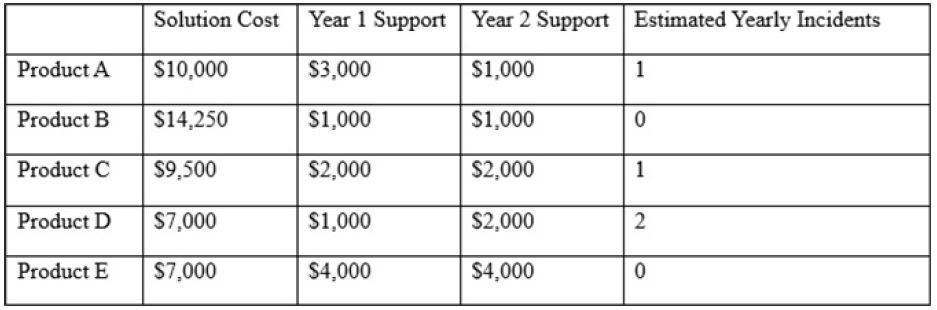
- AProduct A
- BProduct B
- CProduct C
- DProduct D
- EProduct E
34A company is transitioning to a new VDI environment, and a system engineer is responsible for developing a sustainable security strategy for the VDIs.
Which of the following is the MOST appropriate order of steps to be taken?- AFirmware update, OS patching, HIDS, antivirus, baseline, monitoring agent
- BOS patching, baseline, HIDS, antivirus, monitoring agent, firmware update
- CFirmware update, OS patching, HIDS, antivirus, monitoring agent, baseline
- DBaseline, antivirus, OS patching, monitoring agent, HIDS, firmware update
35A security engineer is employed by a hospital that was recently purchased by a corporation. Throughout the acquisition process, all data on the virtualized file servers must be shared by departments within both organizations.
The security engineer considers data ownership to determine:- Athe amount of data to be moved.
- Bthe frequency of data backups.
- Cwhich users will have access to which data.
- Dwhen the file server will be decommissioned.
36 A project manager is working with a team that is tasked to develop software applications in a structured environment and host them in a vendor’s cloud-based infrastructure. The organization will maintain responsibility for the software but will not manage the underlying server applications.
Which of the following does the organization plan to leverage?- ASaaS
- BPaaS
- CIaaS
- DHybrid Cloud
- ENetwork Virtualization
37 the BEST method for the company to prove Vie authenticity of the message?
- Aissue PlN-enabled hardware tokens
- BCreate a CA win all users
- CConfigure the server to encrypt all messages in transit
- Dinclude a hash in the body of the message
38A software development manager is running a project using agile development methods. The company cybersecurity engineer has noticed a high number of vulnerabilities have been making it into production code on the project.
Which of the following methods could be used in addition to an integrated development environment to reduce the severity of the issue?- AConduct a penetration test on each function as it is developed
- BDevelop a set of basic checks for common coding errors
- CAdopt a waterfall method of software development
- DImplement unit tests that incorporate static code analyzers
39A security engineer has implemented an internal user access review tool so service teams can
baseline user accounts and group memberships. The tool is functional and popular among its initial set of onboarded teams. However, the tool has not been built to cater to a broader set of internal teams yet. The engineer has sought feedback from internal stakeholders, and a list of summarized requirements is as follows:
✑ The tool needs to be responsive so service teams can query it, and then perform an automated response action.
✑ The tool needs to be resilient to outages so service teams can perform the user access review at any point in time and meet their own SLAs.
✑ The tool will become the system-of-record for approval, reapproval, and removal life cycles of group memberships and must allow for data retrieval after failure.
Which of the following need specific attention to meet the requirements listed above? (Choose three.)- AScalability
- BLatency
- CAvailability
- DUsability
- ERecoverability
- FMaintainability
40A security engineer has been hired to design a device that will enable the exfiltration of data from within a well-defended network perimeter during an authorized test. The device must bypass all firewalls and NIDS in place, as well as allow for the upload of commands from a centralized command and control answer. The total cost of the device must be kept to a minimum in case the device is discovered during an assessment.
Which of the following tools should the engineer load onto the device being designed?- ACustom firmware with rotating key generation
- BAutomatic MITM proxy
- CTCP beacon broadcast software
- DReverse shell endpoint listener
41A software development firm wants to validate the use of standard libraries as part of the software development process. Each developer performs unit testing prior to committing changes to the code repository.
Which of the following activities would be BEST to perform after a commit but before the creation of a branch?- AStatic analysis
- BHeuristic analysis
- CDynamic analysis
- DWeb application vulnerability scanning
- EPenetration testing
42A company recently implemented a new cloud storage solution and installed the required synchronization client on all company devices. A few months later, a breach of sensitive data was discovered. Root cause analysis shows the data breach happened from a lost personal mobile device.
Which of the following controls can the organization implement to reduce the risk of similar breaches?- ABiometric authentication
- BCloud storage encryption
- CApplication containerization
- DHardware anti-tamper
43A secure facility has a server room that currently is controlled by a simple lock and key and several administrators have copies of the key. To maintain regulatory compliance, a second lock, which is controlled by an application on the administrators' smartphones, is purchased and installed. The application has various authentication methods that can be used.
The criteria for choosing the most appropriate method are:
• It cannot be invasive to the end-user.
• It must be utilized as a second factor.
• Information sharing must be avoided.
• It must have a low false acceptance rate.
Which of the following BEST meets the criteria?- AFacial recognition
- BSwipe pattern
- CFingerprint scanning
- DComplex passcode
- EToken card
44A security analyst is reviewing the corporate MDM settings and notices some disabled settings, which consequently permit users to download programs from untrusted developers and manually install them. After some conversations, it is confirmed that these settings were disabled to support the internal development of mobile applications. The security analyst is now recommending that developers and testers have a separate device profile allowing this and that the rest of the organization’s users do not have the ability to manually download and install untrusted applications.
Which of the following settings should be toggled to achieve the goal? (Choose two.)- AOTA updates
- BRemote wiping
- CSide loading
- DSandboxing
- EContainerization
- FSigned applications
45An application development company implements object reuse to reduce life-cycle costs for the company and its clients. Despite the overall cost savings, which of the following BEST describes a security risk to customers inherent within this model?
- AConfigurations of applications will affect multiple products.
- BReverse engineering of applications will lead to intellectual property loss
- CSoftware patch deployment will occur less often
- DHomogeneous vulnerabilities will occur across multiple products
46A Chief Information Security Officer (CISO) is reviewing technical documentation from various regional offices and notices some key differences between these groups. The CISO has not discovered any governance documentation. The CISO creates the following chart to visualize the differences among the networking used.
(See Attached Image)
Which of the following would be the CISO’s MOST immediate concern?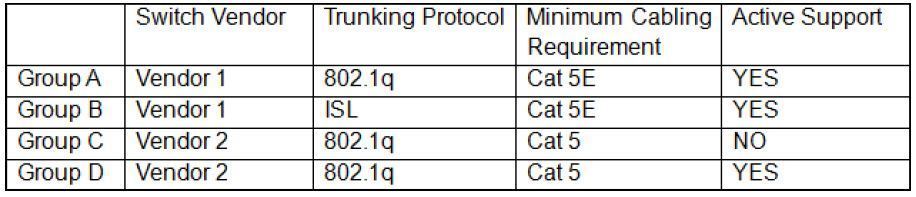
- AThere are open standards in use on the network.
- BNetwork engineers have ignored defacto standards.
- CNetwork engineers are not following SOPs.
- DThe network has competing standards in use.
Información
- Descripción
- Practice Test 2-1
- Autor
- Arthur Casto
- Idioma
- English
- Visitas
- 265
- Historial
- Creado el 18 ene 2022 · actualizado el 20 ene 2022
- Etiquetas
- Valoración
- Aún sin valoraciones Valora este test