
Test
CCNA Security HW 3 & 4 (also exam review)
Preguntas del test (16)
1Which statement describes a stateful firewall?
- AIt can only filter packets based on limited Layer 3 and 4 information.
- BIt can filter packets based on information at Layers 3, 4, 5 and 7 of the OSI reference model.
- CIt can expand the number of IP addresses available and can hide network addressing design.
- DIt can determine if the connection is in the initiation, data transfer, or termination phase.
2What are two characteristics of ACLs? (Choose two.)
- AExtended ACLs can filter on destination TCP and UDP ports.
- BStandard ACLs can filter on source TCP and UDP ports.
- CExtended ACLs can filter on source and destination IP addresses.
- DStandard ACLs can filter on source and destination IP addresses.
- EStandard ACLs can filter on source and destination TCP and UDP ports.
3In general which ICMP message type should be stopped inbound?
- Aecho
- Becho-reply
- Cunreachable
- Dsource quench
4Which two types of addresses should be denied inbound on a router interface that attaches to the Internet? (Choose two.)
- Aprivate IP addresses
- Bpublic IP addresses
- CNAT translated IP addresses
- Dany IP address that starts with the number 127
- Eany IP address that starts with the number 1
5Where is the firewall policy applied when using Classic Firewall?
- Asecurity zones
- Bself zone
- Cmultiple zones
- Dinterfaces
6Consider the following access list command applied outbound on a router serial interface:
access-list 100 deny icmp 192.168.10.0 0.0.0.255 any echo reply
What is the effect of applying this access list command?- AThe only traffic denied is ICMP-based traffic. All other traffic is allowed.
- BThe only traffic denied is echo-replies sourced from the 192.168.10.0/24 network. All other traffic is allowed.
- CUsers on the 192.168.10.0/24 network are not allowed to transmit traffic to any other destination.
- DNo traffic will be allowed outbound on the serial interface.
7What is the result in the self zone if a router is the source or destination of traffic?
- ANo traffic is permitted.
- BAll traffic is permitted.
- COnly traffic that originates in the router is permitted.
- DOnly traffic that is destined for the router is permitted.
8Consider the configured access list.
R1# show access-lists
extended IP access list 100
deny tcp host 10.1.1.2 host 10.1.1.1 eq telnet
deny tcp host 10.1.2.2 host 10.1.2.1 eq telnet
permit ip any any (15 matches)
What are two characteristics of this access list? (Choose two.)- AThe access list has been applied to an interface.
- BA network administrator would not be able to tell if the access list has been applied to an interface or not.
- CThe 10.1.2.1 device is not allowed to telnet to the 10.1.2.2 device.
- DAny device on the 10.1.1.0/24 network (except the 10.1.1.2 device) can telnet to the router that has the IP address 10.1.1.1 assigned.
- EOnly the 10.1.1.2 device can telnet to the router that has the 10.1.1.1 IP address assigned.
- FAny device can telnet to the 10.1.2.1 device.
9Refer to the exhibit. If a hacker on the outside network sends an IP packet with source address 172.30.1.50, destination address 10.0.0.3, source port 23, and destination port 2447, what does the Cisco IOS firewall do with the packet?
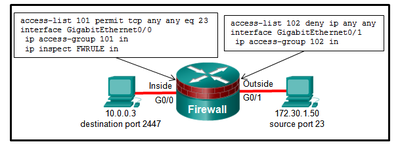
- AThe packet is forwarded, and an alert is generated.
- BThe packet is forwarded, and no alert is generated.
- CThe initial packet is dropped, but subsequent packets are forwarded.
- DThe packet is dropped.
10Which command is used to activate an IPv6 ACL named ENG_ACL on an interface so that the router filters traffic prior to accessing the routing table?
- Aipv6 access-class ENG_ACL in
- Bipv6 access-class ENG_ACL out
- Cipv6 traffic-filter ENG_ACL in
- Dipv6 traffic-filter ENG_ACL out
11Refer to the exhibit. Which statement describes the function of the ACEs?
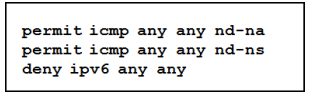
- AThese ACEs allow for IPv6 neighbor discovery traffic.
- BThese ACEs must be manually added to the end of every IPv6 ACL to allow IPv6 routing to occur.
- CThese ACEs automatically appear at the end of every IPv6 ACL to allow IPv6 routing to occur.
- DThese are optional ACEs that can be added to the end of an IPv6 ACL to allow ICMP messages that are defined in object groups named nd-na and nd-ns.
12A router has been configured as a classic firewall and an inbound ACL applied to the external interface. Which action does the router take after inbound-to-outbound traffic is inspected and a new entry is created in the state table?
- AA dynamic ACL entry is added to the external interface in the inbound direction.
- BThe internal interface ACL is reconfigured to allow the host IP address access to the Internet.
- CThe entry remains in the state table after the session is terminated so that it can be reused by the host.
- DWhen traffic returns from its destination, it is reinspected, and a new entry is added to the state table.
13If the provided statements are in the same ACL, which statement should be listed first in the ACL according to best practice?
- Apermit ip any any
- Bpermit udp 172.16.0.0 0.0.255.255 host 172.16.1.5 eq snmptrap
- Cpermit tcp 172.16.0.0 0.0.3.255 any established
- Dpermit udp any any range 10000 20000
- Edeny udp any host 172.16.1.5 eq snmptrap
- Fdeny tcp any any eq telnet
14Which command will verify a Zone-Based Policy Firewall configuration?
- Ashow interfaces
- Bshow protocols
- Cshow zones
- Dshow running-config
15Refer to the exhibit. The network "A" contains multiple corporate servers that are accessed by hosts from the Internet for information about the corporation. What term is used to describe the network marked as "A"?
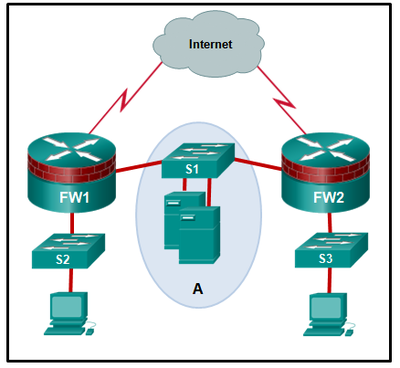
- ADMZ
- Binternal network
- Cperimeter security boundary
- Duntrusted network
16When a Cisco IOS Zone-Based Policy Firewall is being configured, which two options can be configured to a traffic class? (Choose two of the best.)
- Alog
- Bhold
- Cdrop
- Dinspect
- Ecopy
- Fforward
Información
- Descripción
- CCNA Security HW 3 & 4 (also exam review) Professor Shirong Du University of Akron
- Autor
- Anthony Schulmeister
- Idioma
- English
- Visitas
- 2.372
- Etiquetas
- Valoración
- Aún sin valoraciones Valora este test