
Quiz
CCNA Security Chapter 4 Exam
Questions in this quiz (23)
1Refer to the exhibit. If a hacker on the outside network sends an IP packet with source address 172.30.1.50, destination address 10.0.0.3, source port 23, and destination port 2447, what does the Cisco IOS firewall do with the packet?
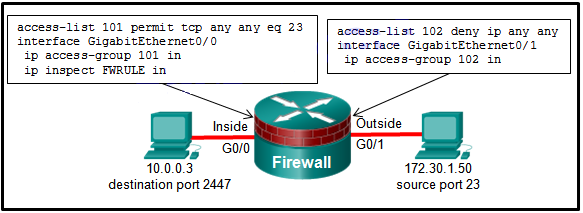
- AThe initial packet is dropped, but subsequent packets are forwarded
- BThe packet is forwarded, and an alert is generated
- CThe packet is forwarded, and no alert is generated
- DThe packet is dropped
2To facilitate the troubleshooting process, which inbound ICMP message should be permitted on an outside interface?
- Aecho request
- Btime-stamp request
- Cecho reply
- Dtime-stamp reply
- Erouter advertisement
3Which command is used to activate an IPv6 ACL named ENG_ACL on an interface so that the router filters traffic prior to accessing the routing table
- Aipv6 access-class ENG_ACL in
- Bipv6 traffic-filter ENG_ACL out
- Cipv6 traffic-filter ENG_ACL in
- Dipv6 access-class ENG_ACL out
4Which statement describes a typical security policy for a DMZ firewall configuration
- ATraffic that originates from the inside interface is generally blocked entirely or very selectively permitted to the outside interface
- BTraffic that originates from the DMZ interface is selectively permitted to the outside interface
- CTraffic that originates from the outside interface is permitted to traverse the firewall to the inside interface with few or no restrictions
- DReturn traffic from the inside that is associated with traffic originating from the outside is permitted to traverse from the inside interface to the outside interface
- Eeturn traffic from the outside that is associated with traffic originating from the inside is permitted to traverse from the outside interface to the DMZ interface
5 Refer to the exhibit. Which statement describes the function of the ACEs
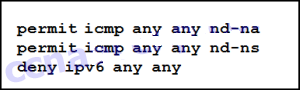
- AThese ACEs allow for IPv6 neighbor discovery traffic
- BThese ACEs automatically appear at the end of every IPv6 ACL to allow IPv6 routing to occur
- CThese are optional ACEs that can be added to the end of an IPv6 ACL to allow ICMP messages that are defined in object groups named nd-na and nd-ns
- DThese ACEs must be manually added to the end of every IPv6 ACL to allow IPv6 routing to occur
6When an inbound Internet-traffic ACL is being implemented, what should be included to prevent the spoofing of internal networks
- AACEs to prevent traffic from private address spaces
- BACEs to prevent broadcast address traffic
- CACEs to prevent ICMP traffic
- DACEs to prevent HTTP traffic
- EACEs to prevent SNMP traffic
7In addition to the criteria used by extended ACLs, what conditions are used by a classic firewall to filter traffic
- ATCP/UDP source and destination port numbers
- BTCP/IP protocol numbers
- CIP source and destination addresses
- Dapplication layer protocol session information
8A router has been configured as a classic firewall and an inbound ACL applied to the external interface. Which action does the router take after inbound-to-outbound traffic is inspected and a new entry is created in the state table
- AWhen traffic returns from its destination, it is reinspected, and a new entry is added to the state table
- BThe internal interface ACL is reconfigured to allow the host IP address access to the Internet
- CThe entry remains in the state table after the session is terminated so that it can be reused by the host
- DA dynamic ACL entry is added to the external interface in the inbound direction
9If the provided ACEs are in the same ACL, which ACE should be listed first in the ACL according to best practice
- Apermit udp 172.16.0.0 0.0.255.255 host 172.16.1.5 eq snmptrap
- Bdeny udp any host 172.16.1.5 eq snmptrap
- Cdeny tcp any any eq telnet
- Dpermit ip any any
- Epermit udp any any range 10000 20000
- Fpermit tcp 172.16.0.0 0.0.3.255 any established
10A company is deploying a new network design in which the border router has three interfaces. Interface Serial0/0/0 connects to the ISP, GigabitEthernet0/0 connects to the DMZ, and GigabitEthernet/01 connects to the internal private network. Which type of traffic would receive the least amount of inspection (have the most freedom of travel)
- Atraffic that is going from the private network to the DMZ
- Btraffic that is returning from the DMZ after originating from the private network
- Ctraffic that originates from the public network and that is destined for the DMZ
- Dtraffic that is returning from the public network after originating from the private network
11Refer to the exhibit. The ACL statement is the only one explicitly configured on the router. Based on this information, which two conclusions can be drawn regarding remote access network connections?(Choose two.)

- ASSH connections from the 192.168.2.0/24 network to the 192.168.1.0/24 network are allowed
- BTelnet connections from the 192.168.1.0/24 network to the 192.168.2.0/24 network are allowed
- CTelnet connections from the 192.168.1.0/24 network to the 192.168.2.0/24 network are blocked
- DSSH connections from the 192.168.1.0/24 network to the 192.168.2.0/24 network are allowed
- ESSH connections from the 192.168.1.0/24 network to the 192.168.2.0/24 network are blocked
- FTelnet connections from the 192.168.2.0/24 network to the 192.168.1.0/24 network are allowed
12Consider the following access list.
access-list 100 permit ip host 192.168.10.1 any
access-list 100 deny icmp 192.168.10.0 0.0.0.255 any echo
access-list 100 permit ip any any
Which two actions are taken if the access list is placed inbound on a router Gigabit Ethernet port that has the IP address 192.168.10.254 assigned? (Choose two.)- ADevices on the 192.168.10.0/24 network are not allowed to reply to any ping requests
- BA Telnet or SSH session is allowed from any device on the 192.168.10.0 into the router with this access list assigned
- COnly Layer 3 connections are allowed to be made from the router to any other network device
- DDevices on the 192.168.10.0/24 network can sucessfully ping devices on the 192.168.11.0 network
- EOnly the network device assigned the IP address 192.168.10.1 is allowed to access the router
13What is one benefit of using a stateful firewall instead of a proxy server
- Aability to perform user authentication
- Bbetter performance
- Cability to perform packet filtering
- Dprevention of Layer 7 attacks
14What is one limitation of a stateful firewall
- Aweak user authentication
- Bcannot filter unnecessary traffic
- Cnot as effective with UDP- or ICMP-based traffic
- Dpoor log information
15When a Cisco IOS Zone-Based Policy Firewall is being configured via CLI, which step must be taken after zones have been created
- AAssign interfaces to zones
- BEstablish policies between zones
- CIdentify subsets within zones
- DDesign the physical infrastructure
16A network administrator is implementing a Classic Firewall and a Zone-Based Firewall concurrently on a router. Which statement best describes this implementation
- AAn interface must be assigned to a security zone before IP inspection can occur
- BBoth models must be implemented on all interfaces
- CThe two models cannot be implemented on a single interface
- DA Classic Firewall and Zone-Based Firewall cannot be used concurrently
17Which two rules about interfaces are valid when implementing a Zone-Based Policy Firewall? (Choose two.)
- AIf one interface is a zone member, but the other is not, all traffic will be passed.
- BIf neither interface is a zone member, then the action is to pass traffic.
- CIf both interfaces are members of the same zone, all traffic will be passed
- DIf one interface is a zone member and a zone-pair exists, all traffic will be passed
- EIf both interfaces belong to the same zone-pair and a policy exists, all traffic will be passed
18Which command will verify a Zone-Based Policy Firewall configuration
- Ashow interfaces
- Bshow zones
- Cshow running-config
- Dshow protocols
19 Refer to the exhibit. The network “A” contains multiple corporate servers that are accessed by hosts from the Internet for information about the corporation. What term is used to describe the network marked as “A”?
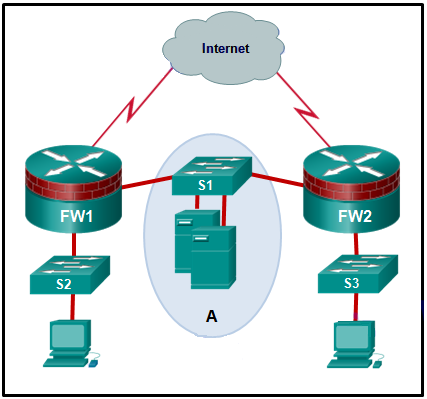
- Ainternal network
- Buntrusted network
- Cperimeter security boundary
- DDMZ
20Which type of packet is unable to be filtered by an outbound ACL
- Amulticast packet
- BICMP packet
- Cbroadcast packet
- Drouter-generated packet
21When a Cisco IOS Zone-Based Policy Firewall is being configured, which two actions can be applied to a traffic class? (Choose two.)
- Adrop
- Blog
- Cforward
- Dhold
- Einspect
- Fcopy
22Fill in the blank.
A ____ firewall monitors the state of connections as network traffic flows into and out of the organization.- Astateful
- Bnonstateful
23Fill in the blank.
The ____ action in a Cisco IOS Zone-Based Policy Firewall is similar to a permit statement in an ACL.- Apass
- Bnonpass
Information
- Description
- Chapter 4 Exam
- Author
- d94829 d94829
- Language
- English
- Views
- 1,100
- Tags
- Rating
- No ratings yet Rate this quiz