
Notas
Identification and Authentication
Conteúdo das notas (15)
Página 1
Identification
Definition
ensures that an entity requesting access to resources by using a certain set of credentials is the true owner of the credentials
associates a particular user (or software process) with an action performed on a network system
Página 2
Identity Management
Definition
issues and problems that must be overcome in implementing the identification and authentication system across different networks and applications
Mitigation
Password Reset
automates the password reset process
reduces the administration costs
making the reset process secure can be problematic
Single sign-on
all network resources and applications accept the same set of credentials
user only needs to authenticate once per session
requires application compatibility
difficult to make secure or practical across third party networks
Página 3
Authentication
Definition
method of validating a particular entity or individual’s unique credentials
concentrates on identifying if a particular individual has right credentials
Factors
Something you know (Knowledge)
Password, PIN, pattern (on Android phones)
Something you have (Possession)
USB token or smart card, hardware token or phone for one-time password
Something you are (Inherence)
Physical characteristics such as finger print, retina pattern, voice print
Something you do
Keystroke patters (e.g. signature) or tracing over a picture password
Somewhere you are
Approved IP address or GPS location
Methods
User Name & Password Authentication
Tokens
Biometrics
Geolocation
Keystroke Authentication
Multifactor Authentication
Mutual Authentication
Multifactor Authentication
requires validation of two or more authentication factors.
e.x. a combination of who you are, what you have, what you know, where you are, and what you do
Página 4
Data States
Data at-rest
data that is on some sort of persistent storage media e.x. Hard drive, SSD, flash drive, etc.
possible to encrypt data
can apply permissions
Data in-transit
data transmitted over a network or in motion
lesser protection as it travels
protected by a transport encryption protocol e.x. IPsec for IP-based network, Secure Socket Layer / Transport Layer Security (SSL / TLS) for TCP/IP application protocols such as HTTPS
Data in-use
data is in volatile memory
almost always decrypted
rootkit access to the computer may be able to access it
Página 5
Cryptographic Terminology
Cryptography
scrambling information so it appears unreadable to attackers
transforms information into secure form
Encryption
changing original text into a secret message using cryptography
Decryption
changing secret message back to original form
Cleartext data
data stored or transmitted without encryption
Plaintext
data to be encrypted
input into an encryption algorithm
Ciphertext
an encrypted message
Cipher
specific set of actions used to encrypt data at low level
Key
mathematical value entered into the algorithm to produce cipher text
reverse process uses the key to decrypt the message
Página 6
Cipher Types
Substitution Cipher
involves replacing units (a letter or blocks of letters) in the plaintext with different ciphertext
rotate or scramble letters of the alphabet
Transposition Cipher
stay the same in plaintext and ciphertext but their order is changed, according to some mechanism
Mathematical Ciphers
uses an operation that is simple to perform one way (when all the values are known) but difficult to reverse
also referred to as trapdoor functions
attacks can be rendered computationally impossible with a large range of values
Página 7
Keys
Key Length
number of bits in a key used by a cipher
using a longer key makes the encryption scheme stronger
Key Space
range of keyvalues available to use with an algorithm
equivalent to 2 to the power of the key length
Página 8
Five Basic Information Protections
Confidentiality
ensures that authorized parties can view the information
encrypted information can only be viewed by those who has the key
Integrity
ensures that the information is correct
encrypted information cannot be changed except by those with the key
Availability
ensures data is accessible to authorized users
provided the decryption key to access the information
Authenticity
provides proof of the geniuneness of the user
can prove that the sender is legit
Nonrepudian
proves user performed an action
can prevent users from denying they were involved in a transaction
Página 9
Hashing Algorithms
Hash functions
mostly used for integrity of data and password storage
two most commonly used hash algorithm are Message Digest Algorithm (MDA / MD5) and Secure Hash Algorithm (SHA)
Message Digest Algorithm
no longer considered secure for use for password hashing
Secure Hash Algorithm (SHA)
created to address weaknesses in MDA
two versions of the standard used is SHA-2(longer digests (notably 256 bits and 512 bits). SHA-2 also addresses the weaknesses found in SHA-1) and SHA-3(Developed in 2015 as another alternative to SHA-0, SHA-1 and MD5)
widely implemented as part of security standards and protocols
Cryptographic Hash algorithm
produces a fixed length string from a variable length string
impossible to recover the original message from the digest (one-way)
unlikely that different messages produce the same digest (a collision)
Página 10
Online Password Attacks
Process
attackers directly interact with the authentication service (login form or VPN)
submit passwords using either a database of known passwords (and variations) or a list of passwords that have been cracked offline
attacks can be mitigated by restricting the number or rate of logon attempts and by shunning logon attempts from "known bad" IP addresses as well as having strong passwords
Página 11
Password Crackers
Definition
software works on the basis of exploiting known vulnerabilities in password transmission and storage algorithms
can perform "brute force" attacks and use precompiled dictionaries and rainbow tables to break naïvely chosen passwords
can work on a database of hashed passwords (known as offline attack)
e.x. Cain and Abel, Jack the Ripper, THC Hydra
Página 12
Types of Password Attacks
Brute force Attack
attempts every possible combination in the key space in order to derive a plaintext from ciphertext
key space is determined by the number of bits used
selecting a suitable key length with a strong password mitigates against brute force attacks
A safe password will have:
At least one letter in upper case
Another one in lower case
There will be at least one digit
And one symbol
12 characters long is optimum
Dictionary Attack
used where there is a good chance of guessing the likely value of the plaintext
enumerates values in the dictionary
Rainbow Tables
refine the dictionary approach
uses a precomputed lookup table of all possible passwords and their matching hashes
not all possible hash values are stored as this would require too much memory
values are computed in "chains" and only the first and last values
hash value of a stored password can then be looked up in the table and the corresponding plaintext discovered
Pass-the-Hash
if the hash is obtained, it is possible to present the it to authenticate to network protocols such as CIFS
starts with a local administrator account on a domain PC being compromised
runs malware with local admin privileges
malware then scans system memory for cached password hashes being processed by the lsass.exe
obtain the credentials of a domain administrator logging on locally or remotely and then replay the domain administrator hash to obtain wider privileges across the network
Página 13
Symmetric Key Cryptosystems
Defintion
same key is used for both encryption and decryption
Pros
Extremely secure
Relatively fast
Cons
Key distribution (requires a secure communication channel to share key between parties)
Key management(each party have to maintain a unique shared key with every other communicating party)
Symmetric Key Cryptosystem Types
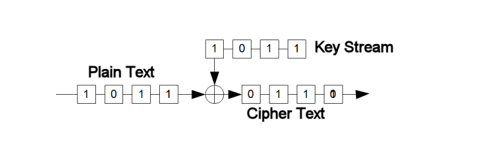
Stream Cipher
plaintext digit is encrypted one at a time with the corresponding digit of the keystream to give a digit of the ciphertext
execute at a higher speed than block ciphers
have lower hardware complexity
can be susceptible to serious security problems if used incorrectly
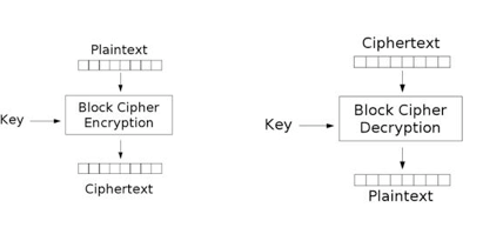
Block Cipher
works on entire block of plaintext at a time
separate blocks of 8 to 16 bytes encrypted independently
more secure because output is more random
Página 14
Asymmetric Key Cryptosystems
Definition
uses public and private keys to encrypt and decrypt data
Pros
address key distribution and management problems of symmetric key cryptosystem
satisfies authentication and nonrepudiation
Cons
rely on the recipient’s public key to secure messages
ensuring the authenticity of the public key is a problem
vulnerable to Man-in-the-Middle attacks
Public Key Concept
All users create 2 keys
Key 1 - The Secret Key
Key 2 - The Public Key
A Secret Lock is plaintext encrypted using Secret Key
A Public Lock is plaintext encrypted using the Public Key
A Secret Key opens a Public Lock
A Public Key opens a Private Lock
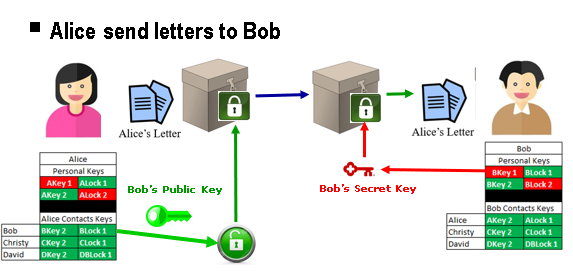
Anyone with Bob’s Public Key can send Bob secure messages
Only Bob has the Secret Key so only Bob and retrieve the letters
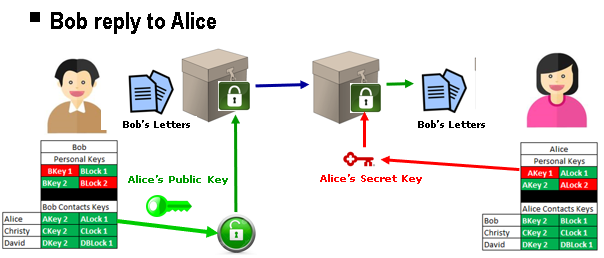
Anyone with Alice’s Public Key can send Alice secure messages
Only Alice has the Secret Key so only Alice and retrieve the letters
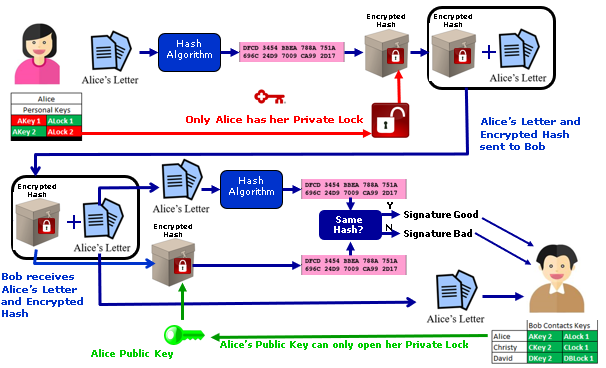
Digital Signature
Authentication
verifies the sender
Non-Repudiation
prevents sender from disowning the message
Integrity
proves message integrity
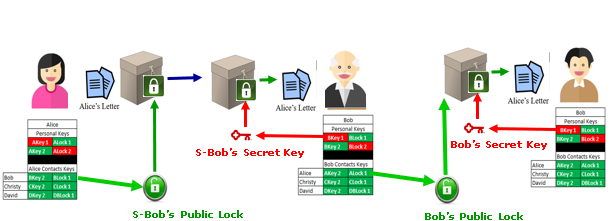
S-Bob fools Alice into accepting his Public Lock as Bob’s Public Lock
Alice send letters to S-Bob, thinking S-Bob is Bob
S-Bob intercepts Alice letters, then re-forwards it to Bob
Página 15
Public Key Infrastrucuture
Definition
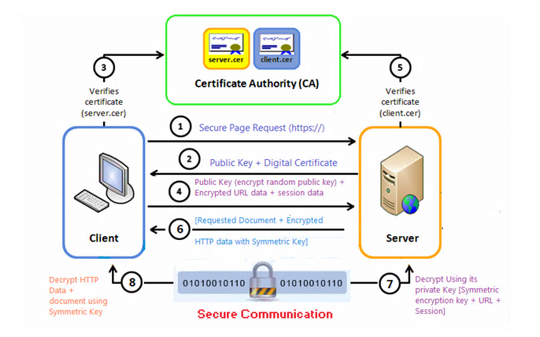
aims to ensure the authenticity of the owners of public keys.
public keys are distributed in the form of a Digital Certificate
Digital Certificate
a wrapper for a subject's (or end entity's) public key
validity of the certificate is guaranteed by a trusted entity called a Certificate Authority (CA)
also contains information about the subject and the certificate's issuer
digitally signed to prove that it was issued to the subject by a particular CA.
Certificate Authority
responsible for issuing and guaranteeing certificates
private CAs can be set up within an organization for internal communications
public or business-to-business communications the CA must be trusted by both parties
Certificate Types
SSL Web Server
Machine / Computer
Email / User Certificate
Code Signing
Root Certificate
Self-signed Certificate
Informações
- Descrição
- Information Security (Identification and Authentication ) Notas sobre Identification and Authentication, criado por Wesley Qua em 10-12-2018.
- Criado por
- Wesley Qua
- Visualizações
- 1
- Avaliação