
Quiz
2a Web application vulnerabilities
Este quiz tem tipos de pergunta que abrem no player de sempre.
Perguntas do quiz (16)
1For each risk on OWASP top 10, it describes:
> [blank_start]threat[blank_end] [blank_start]agent[blank_end]: who carry out the attack
> [blank_start]vulnerability[blank_end]: how is it possible
>[blank_start]impact[blank_end] : what can happen
> how to d[blank_start]etect[blank_end]
>how to p[blank_start]revent[blank_end]- Arevent
- Betect
- Cimpact
- Dvulnerability
- Ethreat
- Fagent
2A1 Injections:
> Examples: S[blank_start]QL[blank_end], L[blank_start]DAP[blank_end]
> Vulnerability: S[blank_start]pecial[blank_end] character sequences in user inputs can trigger an a[blank_start]ction[blank_end] in the context
> Impact: The [blank_start]meaning[blank_end] of a request can be modified- Ameaning
- Bpecial
- Cction
- DQL
- EDAP
3A1 - Injection - [blank_start]SQL[blank_end] injection
> [blank_start]Blind[blank_end] injection: When there is no [blank_start]error[blank_end] message and no other output we can get feedback by inserting an operation that takes [blank_start]time[blank_end] to execute
>> catid = 2 union select
if([blank_start]substring[blank_end](user_password,1,1)=char(50), [blank_start]waitfor[blank_end](50),null) from users where user_id=1;
>>> "%' AND LENGTH ((SELECT password FROM users WHERE name = 'inspector_derrick')) = {} [blank_start]AND[blank_end] '1' = '[blank_start]1[blank_end]"
> [blank_start]OR[blank_end] '1' = '1' > return all rows
> url: /personalities[blank_start]?[blank_end]id=2[blank_start]'[blank_end] UNION SELECT name, message FROM contact_messages WHERE mail = 'james@bond.mi5"- ASQL
- BBlind
- Ctime
- Derror
- Esubstring
- Fwaitfor
- GAND
- H1
- IOR
- J?
- K'
4A1 Injection - [blank_start]LDAP[blank_end] injection
LDAP is the lightweight directory access protocol to [blank_start]query[blank_end] directories to..
> verify a user's password
> read a user's attribute
>> & = and, | = or, [blank_start]*[blank_end] = wildcard
eg. (&(name=admin)([blank_start]&[blank_end]))(pwd=...))
> (&) is always [blank_start]true[blank_end] and pwd=... is [blank_start]ignor[blank_end]ed
> In 2017, Joomla bug: using a [blank_start]wildcard[blank_end] we can guess one character at a time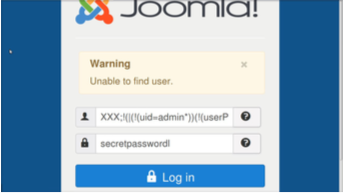
- ALDAP
- Bquery
- C*
- D&
- Etrue
- Fignor
- Gwildcard
5A1 - Injection - [blank_start]command[blank_end] injection:
Runtime runtime = Runtime.getRuntime();
String[] cmd = new String[3];
cmd[0] = "cmd.exe" ;
cmd[1] = "/C";
cmd[2] = "dir " + *chosen_dir*;
Process proc = runtime.exec(cmd);
> If [blank_start]chosen_dir[blank_end] is ’photo & rmdir /s /q photo’ u'll remove photo!- Acommand
- Bchosen_dir
6A1 Injection protection:
> [blank_start]Input[blank_end] [blank_start]validation[blank_end] : refuse the characters u don't want with a regex
> Encode data: [blank_start]escape[blank_end] special characters
>> in SQL: ' becomes \'
>> in HTML: < becomes <
>> in LDAP: ( becomes \28
> use [blank_start]prepared[blank_end] [blank_start]statement[blank_end] in SQL:
PreparedStatement pstmt =
con.prepareStatement(
"SELECT pwhash FROM table WHERE name = ? and
pass = ?"
);
pstmt.setString(1, name_received);
pstmt.setString(2, pass_received);- AInput
- Bvalidation
- Cescape
- Dprepared
- Estatement
7A4 - XML External entities:
> XML = markup language
> elements are delimited by start and stop tags : <name> peter </name>
> [blank_start]Document[blank_end] type [blank_start]definition[blank_end] (DTD): h[blank_start]eader[blank_end] of a XML files tat declares the type of data, which can contain MACROS ( [external] [blank_start]entities[blank_end])
>> Billion laugh attack
>>
<!ENTITY xxe SYSTEM "file:///etc/passwd" >]>
<foo>&xxe;</foo>
The server will replac &xxe by the content of [blank_start]passwd[blank_end] file.
The user can submit the above XML and have its content returned in a response >> access to any f[blank_start]ile[blank_end] on the system.
Solution: Do not accept XML that contains [blank_start]DTD[blank_end] specifications!
setFeature("http://apache.org/xml/features/[blank_start]dis[blank_end]allow-[blank_start]doctype[blank_end]decl",true);- Adoctype
- Bdis
- CDTD
- DDocument
- Edefinition
- Feader
- Gentities
- Hpasswd
- Iile
8A5 - Broken access control
> Access control = [blank_start]direct[blank_end] [blank_start]reference[blank_end]s
> when a u[blank_start]ser[blank_end]-submitted parameter = direct reference to a r[blank_start]esource[blank_end], a user may try to change to access to other resources
Having:
http://bad.com/display_photos?template=css/p.css
POST /users {"action":"unsubscribe", "user":"100293"}
>> What if I tried
http://bad.com/display_transactions?account=100299- Adirect
- Breference
- Cser
- Desource
9A5 - [blank_start]Broken[blank_end] access [blank_start]control[blank_end] Protection:
> Use an [blank_start]indirect[blank_end] reference, eg:
https://bad.com/display_transactions?account=savings
> Protect reference with a Hash-[blank_start]Mac[blank_end]:
/display_transaction?employee_id=100293&HMAC=434A345B0
>> if you change employee_id you will need to change the [blank_start]HMAC[blank_end] also, but you don't know the secret key- AHMAC
- BMac
- Cindirect
- DBroken
- Econtrol
10A5 - Broken access control Protection:
> For every URL, verify if the user has the [blank_start]right[blank_end]s to access it!
ex.
https://example.com/welcome ← anybody
https://example.com/myprofile ← only logged-in users
https://example.com/add_user ← only admins- Aright
11A7 - [blank_start]Cross[blank_end] site [blank_start]Scripting[blank_end] (XSS) = [blank_start]Injection[blank_end] in web pages:
> H[blank_start]TML[blank_end] and J[blank_start]avascrip[blank_end]t
> Impact:
>> Steal [blank_start]session[blank_end] [blank_start]cookie[blank_end]s
>> Display [blank_start]forged[blank_end] forms : trick the user to do unwanted actions, eg. transfer money
>> Complete control over browser
eg
//acme.com/search?q=+<script>alert('hacked')</script>
//acme.com/search?q=+<script src="hacker.com/a.js">- Aforged
- Bsession
- Ccookie
- DInjection
- EScripting
- FCross
- Gavascrip
- HTML
12A7 XSS Types:
> [blank_start]Reflexive[blank_end]: The attack is sent with the request and reflected in the response. You must convince a victim to [blank_start]click[blank_end] on a [blank_start]link[blank_end]
> [blank_start]Persistent[blank_end]: You can insert the attack into a page (e.g. comments). All f[blank_start]ollow[blank_end]ing visitors of the page will be attacked
> [blank_start]DOM[blank_end] based: The attack happens completely in the browser
e.g. JavaScript accesses a part of the URL that contains the attack- AReflexive
- Bclick
- Clink
- DPersistent
- Eollow
- FDOM
13A7 XSS Protection:
> Va[blank_start]lidat[blank_end]e inputs when receiving them
> En[blank_start]code[blank_end] characters when putting them into an HTML page
> Use a fr[blank_start]amework[blank_end]
> Use Content Security Policy in the HTTP headers: [blank_start]Content[blank_end]-Security-[blank_start]Policy[blank_end]: default-src '[blank_start]self[blank_end]';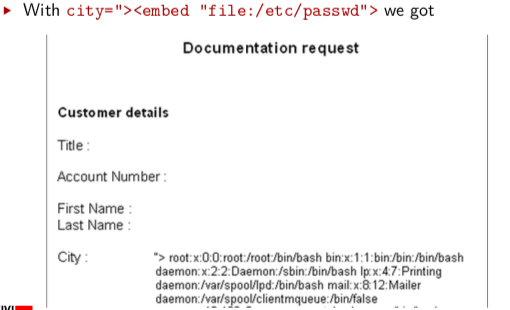
- Alidat
- Bcode
- Camework
- DContent
- EPolicy
- Fself
14public class GuestBook extends HttpServlet {
String name;
protected void doPost (HttpServletRequest req, HttpServletResponse res) {
name = req.getParameter("name");
...
out.println([blank_start]encodeForHTML[blank_end](name) + ", thanks for visiting!");
} }- AencodeForHTML
15XSS prevention:
public String preventXSS(String input, String mask) {
return input.replaceAll("script", mask);
}
We need to prevent all combinations of [blank_start]case[blank_end]s: ScriPt, scRIpt- Acase
16OSCommand injection protection:
String btype = request.getParameter("backuptype");
String cmd = new String("cmd.exe /K \"
c:\\util\\rmanDB.bat "
+[blank_start]encodeForOSCommand[blank_end](btype)+
"&&c:\\utl\\cleanup.bat\"")
System.Runtime.getRuntime().exec(cmd);- AencodeForOSCommand
Informações
- Descrição
- - Information security (2 Web app & Software vulnerabilities) Quiz sobre 2a Web application vulnerabilities, criado por Yawen Hou em 08-06-2019.
- Autor
- Yawen Hou
- Idioma
- English
- Visualizações
- 1
- Etiquetas
- Avaliação
- Ainda sem avaliações Avalie este quiz