
Quiz
Fundamentals of Information Security [State Exam | Part 2 + 23 new questions]
Questions in this quiz (146)
1What are two methods to maintain certificate revocation status? (Choose two.)
- Asubordinate CA
- BOCSP
- CDNS
- DLDAP
- ECRL
2The following message was encrypted using a Caesar cipher with a key of 2:
fghgpf vjg ecuvng
What is the plaintext message?- Ainvade the castle
- Bdefend the castle
- Cdefend the region
- Dinvade the region
3What is the purpose of a digital certificate?
- AIt ensures that the person who is gaining access to a network device is authorized.
- BIt provides proof that data has a traditional signature attached.
- CIt guarantees that a website has not been hacked.
- DIt authenticates a website and establishes a secure connection to exchange confidential data
4A company is developing a security policy for secure communication. In the exchange of critical messages between a headquarters office and a branch office, a hash value should only be recalculated with a predetermined code, thus ensuring the validity of data source. Which aspect of secure communications is addressed?
- Adata integrity
- Bnon-repudiation
- Corigin authentication
- Ddata confidentiality
5In most host-based security suites, which function provides robust logging of security-related events and sends logs to a central location?
- Aintrusion detection and prevention
- Banti-phishing
- Ctelemetry
- Dsafe browsing
6On a Windows host, which tool can be used to create and maintain blacklists and whitelists?
- AGroup Policy Editor
- BLocal Users and Groups
- CComputer Management
- DTask Manager
7Which statement describes agentless antivirus protection?
- AHost-based antivirus systems provide agentless antivirus protection.
- BThe antivirus protection is provided by the router that is connected to a cloud service.
- CThe antivirus protection is provided by the ISP.
- DAntivirus scans are performed on hosts from a centralized system.
8The IT security personnel of an organization notice that the web server deployed in the DMZ is frequently targeted by threat actors. The decision is made to implement a patch management system to manage the server. Which risk management strategy method is being used to respond to the identified risk?
- Arisk avoidance
- Brisk retention
- Crisk reduction
- Drisk sharing
9In addressing a risk that has low potential impact and relatively high cost of mitigation or reduction, which strategy will accept the risk and its consequences?
- Arisk reduction
- Brisk avoidance
- Crisk retention
- Drisk sharing
10What is a host-based intrusion detection system (HIDS)?
- AIt identifies potential attacks and sends alerts but does not stop the traffic.
- BIt detects and stops potential direct attacks but does not scan for malware.
- CIt is an agentless system that scans files on a host for potential malware.
- DIt combines the functionalities of antimalware applications with firewall protection.
11What type of antimalware program is able to detect viruses by recognizing various characteristics of a known malware file?
- Abehavior-based
- Bagent-based
- Csignature-based
- Dheuristic-based
12Which device in a LAN infrastructure is susceptible to MAC address-table overflow and spoofing attacks?
- Afirewall
- Bworkstation
- Cserver
- Dswitch
13Which criterion in the Base Metric Group Exploitability metrics reflects the proximity of the threat actor to the vulnerable component?
- Auser interaction
- Battack vector
- Cattack complexity
- Dprivileges required
14In addressing an identified risk, which strategy aims to stop performing the activities that create risk?
- Arisk reduction
- Brisk avoidance
- Crisk retention
- Drisk sharing
15Which statement describes the term iptables?
- AIt is a file used by a DHCP server to store current active IP addresses.
- BIt is a DHCP application in Windows.
- CIt is a DNS daemon in Linux.
- DIt is a rule-based firewall application in Linux.
16For network systems, which management system addresses the inventory and control of hardware and software configurations?
- Aasset management
- Bvulnerability management
- Crisk management
- Dconfiguration management
17Which statement describes the anomaly-based intrusion detection approach?
- AIt compares the signatures of incoming traffic to a known intrusion database.
- BIt compares the antivirus definition file to a cloud based repository for latest updates.
- CIt compares the operations of a host against a well-defined security policy.
- DIt compares the behavior of a host to an established baseline to identify potential intrusions.
18What is the first step taken in risk assessment?
- AIdentify threats and vulnerabilities and the matching of threats with vulnerabilities.
- BEstablish a baseline to indicate risk before security controls are implemented.
- CCompare to any ongoing risk assessment as a means of evaluating risk management effectiveness.
- DPerform audits to verify threats are eliminated.
19Which statement describes the threat-vulnerability (T-V) pairing?
- AIt is the identification of threats and vulnerabilities and the matching of threats with vulnerabilities.
- BIt is the comparison between known malware and system risks.
- CIt is the detection of malware against a central vulnerability research center.
- DIt is the advisory notice from a vulnerability research center.
20Which security procedure would be used on a Windows workstation to prevent access to a specific set of websites?
- Awhitelisting
- BHIDS
- Cblacklisting
- Dbaselining
21Which statement describes the use of a Network Admission Control (NAC) solution?
- AIt provides network access to only authorized and compliant systems.
- BA Network Admission Control solution provides filtering of potentially malicious emails before they reach the endpoint.
- CIt provides endpoint protection from viruses and malware.
- DIt provides filtering and blacklisting of websites being accessed by end users.
22Which type of antimalware software detects and mitigates malware by analyzing suspicious activities?
- Aheuristics-based
- Bpacket-based
- Cbehavior-based
- Dsignature-based
23Which regulatory compliance regulation sets requirements for all U.S. public company boards, management and public accounting firms regarding the way in which corporations control and disclose financial information?
- AGramm-Leach-Bliley Act (GLBA)
- BHealth Insurance Portability and Accountability Act (HIPAA)
- CFederal Information Security Management Act of 2002 (FISMA)
- DSarbanes-Oxley Act of 2002 (SOX)
24Which statement describes the term attack surface?
- AIt is the total sum of vulnerabilities in a system that is accessible to an attacker.
- BIt is the group of hosts that experiences the same attack.
- CIt is the network interface where attacks originate.
- DIt is the total number of attacks toward an organization within a day.
25Which step in the Vulnerability Management Life Cycle determines a baseline risk profile to eliminate risks based on asset criticality, vulnerability threat, and asset classification?
- Aassess
- Bdiscover
- Cverify
- Dprioritize assets
26When a network baseline is being established for an organization, which network profile element indicates the time between the establishment of a data flow and its termination?
- Asession duration
- Bcritical asset address space
- Cports used
- Dtotal throughput
27Which two classes of metrics are included in the CVSS Base Metric Group? (Choose two.)
- AModified Base
- BConfidentiality Requirement
- CExploit Code Maturity
- DExploitability
- EImpact metrics
28In network security assessments, which type of test employs software to scan internal networks and Internet facing servers for various types of vulnerabilities?
- Arisk analysis
- Bpenetration testing
- Cvulnerability assessment
- Dstrength of network security testing
29Which two criteria in the Base Metric Group Exploitability metrics are associated with the complexity of attacks? (Choose two)
- Ascope
- Battack complexity
- Cuser interaction
- Dattack vector
- Eprivileges required
30Which statement describes the Cisco Threat Grid Glovebox?
- AIt is a network-based IDS/IPS.
- BIt is a firewall appliance.
- CIt is a host-based intrusion detection system (HIDS) solution to fight against malware
- DIt is a sandbox product for analyzing malware behaviors.
31How does using HTTPS complicate network security monitoring?
- AHTTPS cannot protect visitors to a company-provided web site.
- BHTTPS can be used to infiltrate DNS queries.
- CWeb browser traffic is directed to infected servers.
- DHTTPS adds complexity to captured packets.
32Which protocol is used to send e-mail messages between two servers that are in different e-mail domains?
- APOP3
- BSMTP
- CHTTP
- DIMAP4
33What are two ways that ICMP can be a security threat to a company? (Choose two.)
- Aby collecting information about a network
- Bby corrupting network IP data packets
- Cby providing a conduit for DoS attacks
- Dby corrupting data between email servers and email recipients
- Eby the infiltration of web pages
34Which function is provided by the Sguil application?
- AIt makes Snort-generated alerts readable and searchable.
- BIt detects potential network intrusions.
- CIt reports conversations between hosts on the network.
- DIt prevents malware from attacking a host.
35Which two options are network security monitoring approaches that use advanced analytic techniques to analyze network telemetry data? (Choose two.)
- ANetFlow
- BSnorby
- CNBAD
- DNBA
- EIPFIX
- FSguil
36A system administrator has recommended to the CIO a move of some applications from a Windows server to a Linux server. The proposed server will use ext4 partitions and serve as a web server, file server, and print server. The CIO is considering the recommendation, but has some questions regarding security.
Which two methods does Linux use to log data in order to identify a security event? (Choose two.)- AApache access logs
- BEvent Viewer
- CNetFlow
- DSPAN
- Esyslog
37A system administrator has recommended to the CIO a move of some applications from a Windows server to a Linux server. The proposed server will use ext4 partitions and serve as a web server, file server, and print server. The CIO is considering the recommendation, but has some questions regarding security.
What is a daemon?- Aa background process that runs without the need for user interaction
- Ba record to keep track of important events
- Ca type of security attack
- Dan application that monitors and analyzes suspicious activity
38A system administrator has recommended to the CIO a move of some applications from a Windows server to a Linux server. The proposed server will use ext4 partitions and serve as a web server, file server, and print server. The CIO is considering the recommendation, but has some questions regarding security.
Because the company uses discretionary access control (DAC) for user file management, what feature would need to be supported on the server?- Aaccess based on security clearance held
- Bprinciple of least privilege
- Crole-based access control
- Duser-based data access control
39A system administrator has recommended to the CIO a move of some applications from a Windows server to a Linux server. The proposed server will use ext4 partitions and serve as a web server, file server, and print server. The CIO is considering the recommendation, but has some questions regarding security.
What are two benefits of using an ext4 partition instead of ext3? (Choose two.)- Acompatibility with CDFS
- Bcompatibility with NTFS
- Cdecreased load time
- Dimproved performance
- Ean increase in the number of supported devices
- Fincrease in the size of supported files
40How can IMAP be a security threat to a company?
- AIt can be used to encode stolen data and send to a threat actor.
- BAn email can be used to bring malware to a host.
- CEncrypted data is decrypted.
- DSomeone inadvertently clicks on a hidden iFrame.
41A system administrator runs a file scan utility on a Windows PC and notices a file lsass.exe in the Program Files directory. What should the administrator do?
- AOpen the Task Manager, right-click on the lsass process and choose End Task.
- BUninstall the lsass application because it is a legacy application and no longer required by Windows.
- CMove it to Program Files (x86) because it is a 32bit application.
- DDelete the file because it is probably malware.
42How does a web proxy device provide data loss prevention (DLP) for an enterprise?
- Aby checking the reputation of external web servers
- Bby functioning as a firewall
- Cby inspecting incoming traffic for potential exploits
- Dby scanning and logging outgoing traffic
43A system analyst is reviewing syslog messages and notices that the PRI value of a message is 26. What is the severity value of the message?
- A1
- B2
- C3
- D6
44Which statement describes session data in security logs?
- AIt is a record of a conversation between network hosts.
- BIt can be used to describe or predict network behavior.
- CIt reports detailed network activities between network hosts.
- DIt shows the result of network sessions.
45In a Cisco AVC system, in which module is NetFlow deployed?
- AManagement and Reporting
- BMetrics Collection
- CControl
- DApplication Recognition
46What port number would be used if a threat actor was using NTP to direct DDoS attacks?
- A443
- B25
- C69
- D123
47Which information can be provided by the Cisco NetFlow utility?
- AIDS and IPS capabilities
- Bsecurity and user account restrictions
- Cpeak usage times and traffic routing
- Dsource and destination UDP port mapping
48What is Tor?
- Aa type of Instant Messaging (IM) software used on the darknet
- Ba way to share processors between network devices across the Internet
- Ca rule created in order to match a signature of a known exploit
- Da software platform and network of P2P hosts that function as Internet routers
49Which statement describes statistical data in network security monitoring processes?
- AIt shows the results of network activities between network hosts.
- BIt contains conversations between network hosts.
- CIt is created through an analysis of other forms of network data.
- DIt lists each alert message along with statistical information.
50Refer to the exhibit. A network administrator is reviewing an Apache access log message. What is the status of the access request by the client?

- AThe request was unsuccessful because of server errors.
- BThe request was fulfilled successfully.
- CThe request was redirected to another web server.
- DThe request was unsuccessful because of client errors.
51How might corporate IT professionals deal with DNS-based cyber threats?
- AMonitor DNS proxy server logs and look for unusual DNS queries.
- BUse IPS/IDS devices to scan internal corporate traffic.
- CLimit the number of simultaneously opened browsers or browser tabs.
- DLimit the number of DNS queries permitted within the organization.
52Refer to the exhibit. A junior network engineer is handed a print-out of the network information shown. Which protocol or service originated the information shown in the graphic?
- ANetFlow
- BTACACS+
- CRADIUS
- DSyslog
53Which technology is used in Cisco Next-Generation IPS devices to consolidate multiple security layers into a single platform?
- AFirePOWER
- BWinGate
- CApache Traffic Server
- DSquid
54Refer to the exhibit. How is the traffic from the client web browser being altered when connected to the destination website of www.cisco.com?
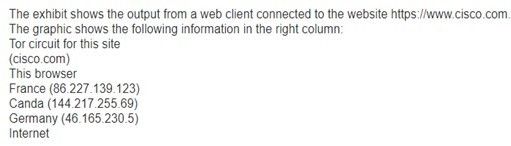
- ATraffic is sent in plain-text by the user machine and is encrypted by the TOR node in France and decrypted by the TOR node in Germany.
- BTraffic is encrypted by the user machine and sent directly to the cisco.com server to be decrypted.
- CTraffic is encrypted by the user machine, and the TOR network only routes the traffic through France, Canada, Germany, and delivers it to cisco.com.
- DTraffic is encrypted by the user machine, and the TOR network encrypts next-hop information on a hop-by-hop basis.
55Which Windows log contains information about installations of software, including Windows updates?
- Asetup logs
- Bapplication logs
- Csystem logs
- Dsecurity logs
56Which Windows log records events related to login attempts and operations related to file or object access?
- Asetup logs
- Bsecurity logs
- Capplication logs
- Dsystem logs
57What does it indicate if the timestamp in the HEADER section of a syslog message is preceded by a period or asterisk symbol?
- AThe timestamp represents the round trip duration value.
- BThe syslog message indicates the time an email is received.
- CThere is a problem associated with NTP.
- DThe syslog message should be treated with high priority.
58Which two application layer protocols manage the exchange of messages between a client with a web browser and a remote web server? (Choose two.)
- AHTTPS
- BDHCP
- CHTML
- DDNS
- EHTTP
59Which protocol is a name resolution protocol often used by malware to communicate with command-and-control (CnC) servers?
- AIMAP
- BHTTPS
- CDNS
- DICMP
60How is the hash value of files useful in network security investigations?
- AIt helps identify malware signatures
- BIt is used to decode files
- CIt verifies confidentiality of files
- DIt is used as a key for encryption
61Which tool is a Security Onion integrated host-based intrusion detection system?
- AOSSEC
- BSguil
- CELSA
- DSnort
62Which type of evidence supports an assertion based on previously obtained evidence?
- ADirect evidence
- BCorroborating evidence
- CBest evidence
- DIndirect evidence
63Which tool is developed by Cisco and provides an interactive dashboard that allows investigation of the threat landscape?
- AWireshark
- BTalos
- CSguil
- DSnort
64Which term is used to describe the process of converting log entries into a common format?
- AStandardization
- BNormalization
- CClassification
- DSystemization
65According to NIST, which step in the digital forensics process involves extracting relevant information from data?
- ACollection
- BExamination
- CAnalysis
- DReporting
66A law office uses a Linux host as the firewall device for the network. The IT administrator is adding a rule to the firewall iptables to block internal hosts from connecting to a remote device that has the IP address 209.165.202.133. Which command should the administrator use?
- AIPTABLES –I FORWARD –P TCP –D 209.165.202.133 –DPORT 7777 –J DROP
- BIPTABLES –I INPUT –P TCP –D 209.165.202.133 –DPORT 7777 –J DROP
- CIPTABLES –I PASS –P TCP –D 209.165.202.133 –DPORT 7777 –J DROP
- DIPTABLES –I OUTPUT –P TCP –D 209.165.202.133 –DPORT 7777 –J DROP
67What procedure should be avoided in a digital forensics investigation?
- ASecure physical access to the computer under investigation
- BReboot the affected system upon arrival
- CMake a copy of the hard drive
- DRecover deleted files
68Which statement describes a feature of timestamps in Linux?
- AHuman readable timestamps measure the number of seconds that have passed since January 1, 1970.
- BAll devices generate human readable and unix epoch timestamps
- CIt is easier to work with Unix epoch timestamps for addition and subtraction operations
- DUnix epoch timestamps are easier for humans to interpret
69Which tool is included with Security Onion that is used by Snort to automatically download new rules?
- ASguil
- BWireshark
- CPulledPork
- DELSA
70Which tool would an analyst use to start a workflow investigation?
- ASguil
- BBro
- CSnort
- DELSA
71What is indicated by a Snort signature ID that is below 3464?
- AThe SID was created by Sourcefire and distributed under a GPL agreement
- BThis is a custom signature developed by the organization to address locally observed rules
- CThe SID was created by members of emerging threats
- DThe SID was created by the Snort community and is maintained in community rules
72How does an application program interact with the operating system?
- AAccessing BIOS or UEFI
- BMaking API calls
- CSending files
- DUsing processes
73A threat actor has successfully breached the network firewall without being detected by the IDS system. What condition describes the lack of alert?
- ATRUE NEGATIVE
- BTRUE POSITIVE
- CFALSE POSITIVE
- DFALSE NEGATIVE
74Use the following scenario to answer the questions. a company has just had a cybersecurity incident. The threat actor or actors appeared to have a goal of network disruption and appeared to use a common security hack tool that overwhelmed a particular server with a large amount of traffic, which rendered the server inoperable.
How would a certified cybersecurity analyst classify this type of threat actor?- AAmateur
- BHacktivist
- CState-sponsored
- DTerrorist
75Use the following scenario to answer the questions. a company has just had a cybersecurity incident. The threat actor or actors appeared to have a goal of network disruption and appeared to use a common security hack tool that overwhelmed a particular server with a large amount of traffic, which rendered the server inoperable.
The security team at this company has removed the compromised server and preserved it with the security hack still embedded. What type of evidence is this?- ABest
- BClassified
- CCorroborating
- DIndirect
76Use the following scenario to answer the questions. a company has just had a cybersecurity incident. The threat actor or actors appeared to have a goal of network disruption and appeared to use a common security hack tool that overwhelmed a particular server with a large amount of traffic, which rendered the server inoperable.
Which type of attack was achieved?- AAccess
- BDoS
- CDDoS
- DSocial engineering
77Use the following scenario to answer the questions. a company has just had a cybersecurity incident. the threat actor or actors appeared to have a goal of network disruption and appeared to use a common security hack tool that overwhelmed a particular server with a large amount of traffic, which rendered the server inoperable.
What would be the threat attribution in this case?- AEvaluating the server alert data
- BObtaining the most volatile evidence
- CDetermining who is responsible for the attack
- DReporting the incident to the proper authorities
78Use the following scenario to answer the questions. a company has just had a cybersecurity incident. the threat actor or actors appeared to have a goal of network disruption and appeared to use a common security hack tool that overwhelmed a particular server with a large amount of traffic, which rendered the server inoperable.
What are three common tools used to carry out this type of attack? (Choose three.)- APing sweep
- BTCP SYN flood
- CBuffer overflow
- DIP, MAC and DHCP Spoofing
- ESmurf attack
- FMan-in-the-middle
79Refer to the exhibit. A network security specialist issues the command tcpdump to capture events. What is the function provided by the ampersand symbol used in the command?
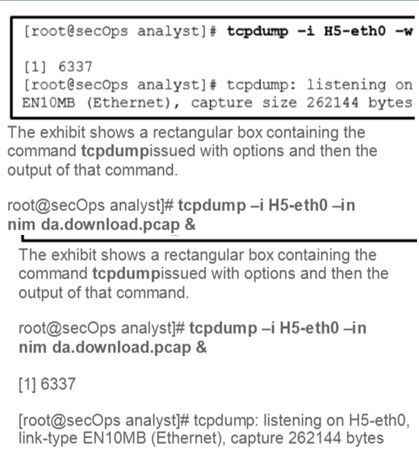
- AIt instructs the tcpdump to capture data that starts with the symbol.
- BIt tells the Linux shell to execute the tcpdump process in the background.
- CIt tells the Linux shell to display the captured data on the console.
- DIt tells the Linux shell to execute the tcpdump process indefinitely.
80Refer to the exhibit. A cybersecurity analyst is using Sguil to verify security alerts. How is the current view sorted?
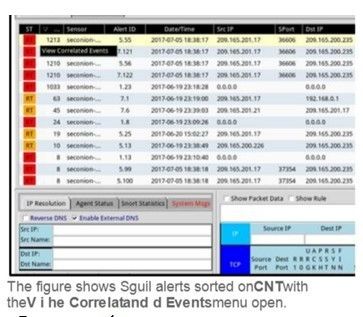
- ABy sensor number
- BBy source IP
- CBy frequency
- DBy Date/Time
81Which three procedures in Sguil are provided to security analysts to address alerts? (Choose three.)
- AExpire false positives
- BPivot to other information sources and tools
- CConstruct queries using query builder
- DEscalate an uncertain alert
- ECorrelate similar alerts into a single line
- FCategorize true positives
82Which two strings will be matched by the regular expression? (Choose two.)
Level[^12]- ALevel4
- BLevel3
- CLevel2
- DLevel1
- ELevel12
83Which statement describes the status after the Security Onion VM is started?
- ASguil becomes enabled via the sudo Sguil –e terminal command
- BAwk becomes enabled via the sudo awk terminal command
- CPullpork is used by ELSA as an open source search engine
- DSnort is enabled by default
84What are the three core functions provided by the Security Onion? (Choose three.)
- ABusiness continuity planning
- BFull packet capture
- CAlert analysis
- DIntrusion detection
- ESecurity device management
- FThreat containment
85Refer to the exhibit. A network security analyst is using the Follow TCP Stream feature in Wireshark to rebuild the TCP transaction. However, the transaction data seems indecipherable. What is the explanation for this?
- AThe transaction data is encoded with base64
- BThe transaction data is a binary file
- CThe data shown is line noise
- DThe transaction data is corrupted
86What is the tool that has alert records linked directly to the search functionality of the Enterprise Log Search and Archive (ELSA)?
- ASguil
- BWireshark
- CCapMe
- DSnort
87Refer to the exhibit. A network security analyst is examining captured data using Wireshark. The captured frames indicate that a host is downloading malware from a server. Which source port is used by the host to request the download?
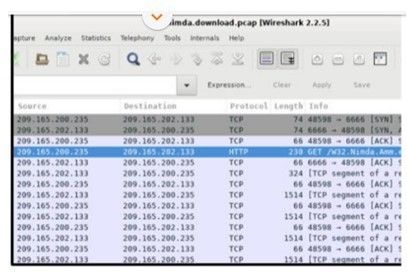
- A66
- B1514
- C6666
- D48598
88Which two types of unreadable network traffic could be eliminated from data collected by NSM? (Choose two.)
- ARouting updates traffic
- BSTP traffic
- CSSL traffic
- DIPSec traffic
- EBroadcast traffic
89When dealing with security threats and using the Cyber Kill Chain model, which two approaches can an organization use to help block potential exploitations of a system? (Choose two.)
- ACollect email and web logs for forensic reconstruction.
- BAnalyze the infrastructure path used for delivery.
- CAudit endpoints to forensically determine origin of exploit.
- DConduct full malware analysis.
- EConduct employee awareness training and email testing.
90Which action should be included in a plan element that is part of a computer security incident response capability (CSIRC)?
- ADetail how incidents should be handled based on the mission and functions of an organization.
- BDevelop metrics for measuring the incident response capability and its effectiveness.
- CCreate an organizational structure and definition of roles, responsibilities, and levels of authority.
- DPrioritize severity ratings of security incidents.
91What is the objective the threat actor in establishing a two-way communication channel between the target system and a CnC infrastructure?
- Ato allow the threat actor to issue commands to the software that is installed on the target
- Bto steal network bandwidth from the network where the target is located
- Cto launch a buffer overflow attack
- Dto send user data stored on the target to the threat actor
92After containment, what is the first step of eradicating an attack?
- AHold meetings on lessons learned.
- BChange all passwords.
- CPatch all vulnerabilities.
- DIdentify all hosts that need remediation.
93What is defined in the SOP of a computer security incident response capability (CSIRC)?
- Athe procedures that are followed during an incident response
- Bthe metrics for measuring incident response capabilities
- Cthe roadmap for increasing incident response capabilities
- Dthe details on how an incident is handled
94A school has a web server mainly used for parents to view school events, access student performance indicators, and communicate with teachers. The network administrator suspects a security-related event has occurred and is reviewing what steps should be taken.
The threat actor has already placed malware on the server causing its performance to slow. The network administrator has found and removed the malware as well as patched the security hole where the threat actor gained access. The network administrator can find no other security issue. What stage of the Cyber Kill Chain did the threat actor achieve?- Aactions on objectives
- Bcommand and control
- Cdelivery
- Dexploitation
- Einstallation
95A school has a web server mainly used for parents to view school events, access student performance indicators, and communicate with teachers. The network administrator suspects a security-related event has occurred and is reviewing what steps should be taken.
If the web server runs Microsoft IIS, which Windows tool would the network administrator use to view the access logs?- AEvent Viewer
- Bnet command
- CPowerShell
- DTask Manager
96A school has a web server mainly used for parents to view school events, access student performance indicators, and communicate with teachers. The network administrator suspects a security-related event has occurred and is reviewing what steps should be taken.
Reports of network slowness lead the network administrator to review server alerts. The administrator confirms that an alert was an actual security incident. Which type of security alert classification would this be?- Afalse negative
- Bfalse positive
- Ctrue negative
- Dtrue positive
97A school has a web server mainly used for parents to view school events, access student performance indicators, and communicate with teachers. The network administrator suspects a security-related event has occurred and is reviewing what steps should be taken.
The network administrator believes that the threat actor used a commonly available tool to slow the server down. The administrator concludes that based on the source IP address identified in the alert, the threat actor was probably one of the students. What type of hacker would the student be classified as?- Ablack hat
- Bgray hat
- Cred hat
- Dwhite hat
98What is the goal of an attack in the installation phase of the Cyber Kill Chain?
- ACreate a back door in the target system to allow for future access.
- BEstablish command and control (CnC) with the target system.
- CUse the information from the reconnaissance phase to develop a weapon against the target.
- DBreak the vulnerability and gain control of the target.
99Which meta-feature element in the Diamond Model describes information gained by the adversary?
- Aresources
- Bmethodology
- Cdirection
- Dresults
100What is a benefit of using the VERIS community database?
- AIt can be used to discover how other organizations dealt with a particular type of security incident.
- BCompanies who pay to contribute and access the database are protected from security threats.
- CIt can be used to discover the name of known threat actors.
- DThe database can be easily compressed.
101When a security attack has occurred, which two approaches should security professionals take to mitigate a compromised system during the Actions on Objectives step as defined by the Cyber Kill Chain model? (Choose two.)
- ABuild detections for the behavior of known malware.
- BTrain web developers for securing code.
- CDetect data exfiltration, lateral movement, and unauthorized credential usage.
- DPerform forensic analysis of endpoints for rapid triage.
- ECollect malware files and metadata for future analysis.
102A threat actor has identified the potential vulnerability of the web server of an organization and is building an attack. What will the threat actor possibly do to build an attack weapon?
- AObtain an automated tool in order to deliver the malware payload through the vulnerability.
- BInstall a webshell on the web server for persistent access.
- CCreate a point of persistence by adding services.
- DCollect credentials of the web server developers and administrators.
103Which action is taken in the postincident phase of the NIST incident response life cycle?
- ADocument the handling of the incident.
- Bidentify and validate incidents.
- CConduct CSIRT response training.
- DImplement procedures to contain threats.
104Which top-level element of the VERIS schema would allow a company to log who the actors were, what actions affected the asset, which assets were affected, and how the asset was affected?
- Aincident description
- Bincident tracking
- Cdiscovery and response
- Dvictim demographics
105What is the role of vendor teams as they relate to CSIRT?
- ACoordinate incident handling across multiple CSIRTs.
- BHandle customer reports concerning security vulnerabilities.
- CUse data from many sources to determine incident activity trends.
- DProvide incident handling to other organizations as a fee-based service.
106According to information outlined by the Cyber Kill Chain, which two approaches can help identify reconnaissance threats? (Choose two.)
- AAnalyze web log alerts and historical search data.
- BAudit endpoints to forensically determine origin of exploit.
- CBuild playbooks for detecting browser behavior.
- DConduct full malware analysis.
- EUnderstand targeted servers, people, and data available to attack.
107To ensure that the chain of custody is maintained, what three items should be logged about evidence that is collected and analyzed after a security incident has occurred? (Choose three.)
- Ameasures used to prevent an incident
- Btime and date the evidence was collected
- Cextent of the damage to resources and assets
- Dvulnerabilities that were exploited in an attack
- Eserial numbers and hostnames of devices used as evidence
- Flocation of all evidence
108Which schema or model was created to anonymously share quality information about security events to the security community?
- AVERIS
- BDiamond
- CCSIRT
- DCyber Kill Chain
109What is the purpose of the policy element in a computer security incident response capability of an organization, as recommended by NIST?
- AIt provides a roadmap for maturing the incident response capability.
- BIt provides metrics for measuring the incident response capability and effectiveness.
- CIt defines how the incident response teams will communicate with the rest of the organization and with other organizations.
- DIt details how incidents should be handled based on the organizational mission and functions.
110What information is gathered by the CSIRT when determining the scope of a security incident?
- Athe processes used to preserve evidence
- Bthe strategies and procedures used for incident containment
- Cthe networks, systems, and applications affected by an incident
- Dthe amount of time and resources needed to handle an incident
111What is the main purpose of exploitations by a threat actor through the weapon delivered to a target during the Cyber Kill Chain exploitation phase?
- ALaunch a DoS attack
- BSend a message back to CnC controlled by the threat actor
- CBreak the vulnerability and gain control of the target
- DEstablish a back door into the system
112Which term is used in the Diamond Model of intrusion to describe a tool that a threat actor uses toward a target system?
- Ainfrastructure
- Bcapability
- Cweaponization
- Dadversary
113What is the role of a Computer Emergency Response Team?
- AReceive, review, and respond to security incidents in an organization.
- BProvide national standards as a fee-based service.
- CCoordinate security incident handling across multiple CSIRTs.
- DProvide security awareness, best practices, and security vulnerability information to a specific population.
114A threat actor collects information from web servers of an organization and searches for employee contact information. The information collected is further used to search personal information on the Internet. To which attack phase do these activities belong according to the Cyber Kill Chain model?
- AActions on objectives
- BExploitation
- CReconnaissance
- DWeaponization
115In which phase of the NIST incident response life cycle is evidence gathered that can assist subsequent investigations by authorities?
- APreparation
- BContainment, Eradication and Recovery
- CPostincident activities
- DDetection and analysis
116The company will be using both Linux- and Windows- based hosts. Which two solutions would be used in a distributed firewall network design? (Choose two).
- AIptable
- BSIEM
- CSnort
- DWindows Table
117The IT company is recommending the use of PKI applications. In which two instances might the entrepreneur make use of PKIs? (Choose two.)
- A802 is authentication
- BHTTPS web-service
- CFTP transfers
- DLocal NTP server
- EFile and directory permission
118The entrepreneur is concerned about company employees having uninterrupted access to important resources and data. Which of the CIA triad components would address the concern?
- AAuthentication
- BConfidentiality
- CIntegrity
- DAvailability
119Use the following scenario to answer the questions. An entrepreneur is starting a small business and is considering the server services needed for the startup company. The company handling the IT service is presenting options to the company. The company will be using both Linux- and Windows-based hosts. Which two solutions would be used in a distributed firewall network design? (Choose two.)
- AIptable
- BWindows Firewall
- CSnort
- DSIEM
- EWireshark
120What is the Stream Ciphers?
- AStream ciphers operate on each bit (instead of block)
- BRandom answer (do not click, dumbass)
121Grey Hat Hackers are..
- ACommit crimes and do unethical things but not for personal gain or to cause damage.
- BMay compromise network and then disclose the problem so the organization can fix the problem.
- CRandom answer1
- DRandom answer2
122“Vulnerability Broker” Threat Actors ...
- ADiscover exploits and report them to vendors, sometimes for prizes or rewards.
- BRandom answer 1 (click here to get free $500!)
123Definition of the attack " Sniffer "…
- Aan application or device that can read, monitor, and capture network data exchanges and read network packets
- BRandom answer 1 (do not click)
124Which type of security threat can be described as software that attaches itself to another program to execute a specific unwanted function?
- Avirus
- Bworm
- Cproxy Trojan horse
- DDenial of Service Trojan horse
125What is the significant characteristic of worm malware?
Hint:
Virus requires a host program to run, worms can run by themselves. Automatically replicates itself and spreads across the network from system to system- AA worm can execute independently of the host system.
- BA worm must be triggered by an event on the host system.
- CWorm malware disguises itself as legitimate software.
- DOnce installed on a host system, a worm does not replicate itself
126What is the purpose of a reconnaissance attack on a computer network?
- AAlso known as information gathering, reconnaissance attacks perform unauthorized discovery and mapping of systems, services, or vulnerabilities.
- BRandom answer 1
127Type of access attack that attempts to manipulate individuals into performing actions or divulging confidential information needed to access a network.
- ASocial engineering attacks
- BRandom answer 1
128What kind of DDOS term are malware designed to infect a host and communicate with a handler system and can also log keystrokes, gather passwords, capture and analyze packets, and more?
- ABots
- BRandom answer 1
129What term DDoS attack refers to a group of zombies infected using self-propagating malware (i.e., bots) and are controlled by handlers?
- ABotnet
- BRandom answer 1 (do not click)
130What term DDoS attack refers to a master command-and-control server controlling groups of zombies?
- AHandlers
- BBots
- CBotnet
- DBotmaster
131What term DDoS attack refers to a group of compromised hosts (i.e. agents) that run malicious code referred to as robots (i.e. bots) ?
- AZombies
- BHandlers
- CBotmaster
- DScrum master
132What term DDoS attack refers to the malware designed to infect a host and communicate with a handler system. It can also log keystrokes, gather passwords, capture and analyze packets, and more...
- ABots
- BZombies
- CHandlers
- DHandlermaster
133What term DDoS attack refers to a group of zombies infected using self-propogating malware (i.e. bots) and are controlled by handlers.
- ABotnet
- BHandlers
- CHandlermaster
- DScrum master
134What DDOS attack term refers to the threat actor in control of the botnet handlers?
- ABotmaster
- BZombies
- CZombie master
- DScrum master
135Types of attacks targeting IP:
- ADOS
- Bbuffer overflow
- CRandom answer 1 (do not click here)
136The DoS attacks...
- AOriginates from multiple, coordinated sources
- BCompromises many hosts
- CRandom answer 1
137ICMP attacks...
- ACan be used to identify hosts on a network, the structure of a network, and determine the operating systems at use on the network.
Can also be used as a vehicle for various types of DoS attacks.
ICMP can also be used for data exfiltration through ICMP traffic from inside the network. - BTo carry diagnostic messages and to report error conditions when routes, hosts, and ports are unavailable.
ICMP messages are generated by devices when a network error or outage occurs. - CRandom answer 1 (do not click here)
- ACan be used to identify hosts on a network, the structure of a network, and determine the operating systems at use on the network.
138Two major sources of DoS attacks (choose two):
- AMaliciously Formatted Packets
- BOverwhelming Quantity of Traffic
- CRandom answer 1 (don't click)
139Which tool is used to provide a list of open ports on network devices?
- ANmap
- BSguil
- CELSA
- DSecurity Onion
140The security policy of an organization allows employees to connect to the office intranet from their homes. Which type of security policy is this?
- Aremote access
- BRandom answer 1
141What is IPS?
- AIntrusion prevention system that stops trigger packets
- BRandom answer
142What is the ACL?
- AIs a series of commands that control whether a device forwards or drops packets based on information found in the packet header
- BRandom answer
143What is the The syslog logging service?
- ASerivce that allows networking devices to send their system messages across the network to syslog servers.
- BService that provides three primary functions:
Gather logging information for monitoring and troubleshooting;
Select the type of logging information that is captured;
Specify the destination of captured syslog messages. - CRandom answer 1
144________ is an usually part of a router firewall, which permits or denies traffic based on Layer 3 and Layer 4 information.
- APacket filtering (Stateless) firewalls
- BRandom answer
145This type firewalls filters IP traffic between a pair of bridged interfaces
- ATransparent firewall
- BRandom answer
146What systems provide real time reporting and long-term analysis of security events?
- ASecurity Information Event Management (SIEM)
- BRandom answer
Information
- Description
- Advanced Fundamentals of Information Security [Teachers: Abdulanova Altynay, Sagymbekova Azhar; STATE EXAM] ▼ (State Exam) Quiz on Fundamentals of Information Security [State Exam | Part 2 + 23 new questions], created by Good Guy Beket on 26/03/2019.
- Author
- Good Guy Beket
- Language
- English
- Views
- 956
- Tags
- Rating
- No ratings yet Rate this quiz