
Quiz
Untitled
This quiz has question types that open in the usual player.
Questions in this quiz (112)
1An engineer receives a security alert that traffic with a known TOR exit node has occurred on the network.
What is the impact of this traffic?- ARansomware communicating after infection.
- BUsers downloading copyrighted content.
- CData exfiltration.
- DUser circumvention of the firewall.
2What is an example of social engineering attacks?
- AReceiving an unexpected email from an unknown person with an attachment from someone in the same company.
- BReceiving an email from human resources requesting a visit to their secure website to update contact information.
- CSending a verbal request to an administrator who knows how to change an account password.
- DReceiving an invitation to the department's weekly WebEx meeting.
3Refer to the exhibit. What is occurring in this network?
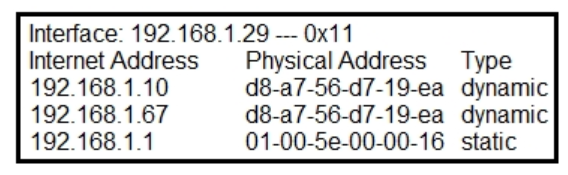
- AARP cache poisoning.
- BDNS cache poisoning.
- CMAC address table overflow.
- DMAC flooding attack.
4Which data format is the most efficient to build a baseline of traffic seen over an extended period of time?
- ASyslog messages.
- BFull packet capture.
- CNetflow.
- DFirewall event log.
5Which action prevents buffer overflow attacks?
- AVariable randomization.
- BUsing web based applications.
- CInput sanitization.
- DUsing a Linux operating system.
6Which type of attack occurs when an attacker is successful in eavesdropping on a conversation between two IP phones?
- AKnown-plaintext.
- BReplay.
- CDictionary.
- DMan-in-the-middle.
7Refer to the exhibit. What should be interpreted from this packet capture?
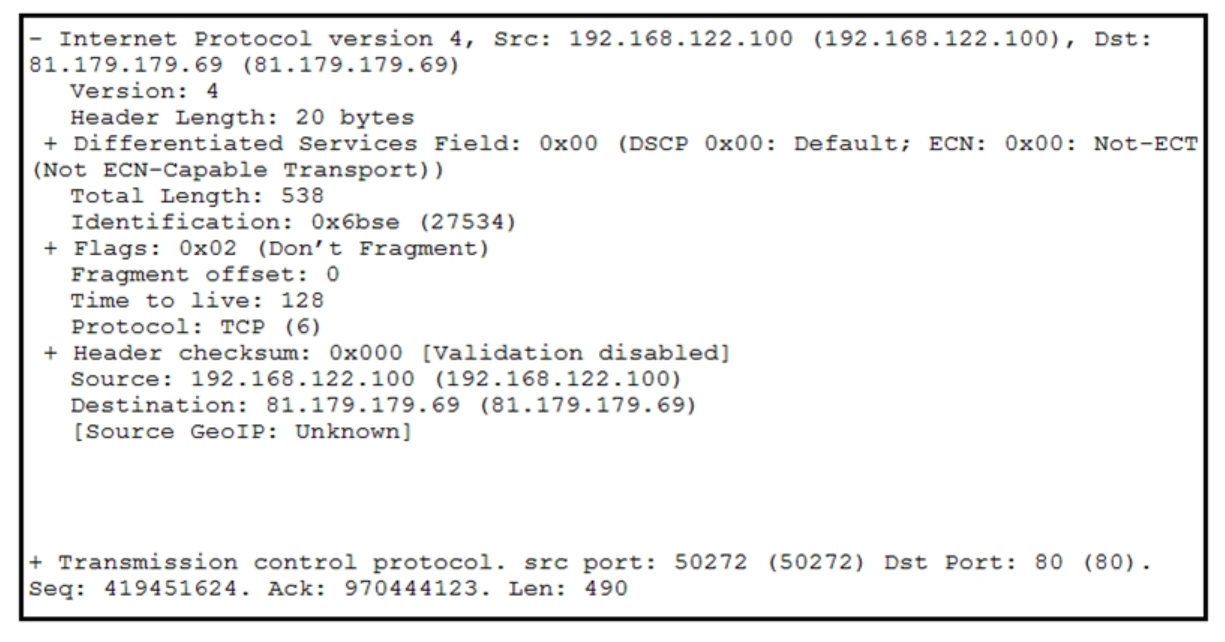
- A81.179.179.69 is sending a packet from port 80 to port 50272 of IP address 192.168.122.100 using UDP protocol.
- B192.168.122.100 is sending a packet from port 50272 to port 80 of IP address 81.179.179.69 using TCP protocol.
- C192.168.122.100 is sending a packet from port 80 to port 50272 of IP address 81.179.179.69 using UDP protocol.
- D81.179.179.69 is sending a packet from port 50272 to port 80 of IP address 192.168.122.100 using TCP UDP protocol.
8What are the two characteristics of the full packet captures? (Choose two.)
- AIdentifying network loops and collision domains.
- BTroubleshooting the cause of security and performance issues.
- CReassembling fragmented traffic from raw data.
- DDetecting common hardware faults and identify faulty assets.
- EProviding a historical record of a network transaction.
9Refer to the exhibit. An engineer is analyzing this Cuckoo Sandbox report for a PDF file that has been downloaded from an email. What is the state of this file?
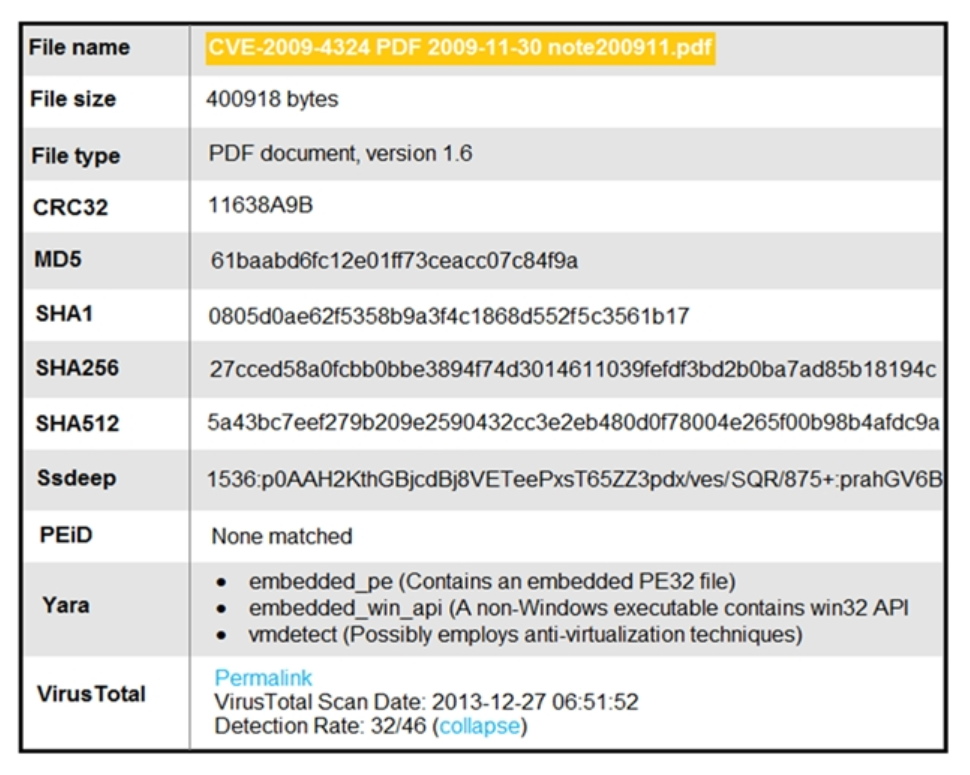
- AThe file has an embedded executable and was matched by PEiD threat signatures for further analysis.
- BThe file has an embedded non-Windows executable but no suspicious features are identified.
- CThe file has an embedded Windows 32 executable and the Yara field lists suspicious features for further analysis.
- DThe file was matched by PEiD threat signatures but no suspicious features are identified since the signature list is up to date.
10DRAG DROP -
Drag and drop the technology on the left onto the data type the technology provides on the right.
Select and Place:
Session Data - [blank_start]tcpdump[blank_end]
Full Packet Capture - [blank_start]Cisco Umbrella[blank_end]
Stateful Firewall - [blank_start]Transaction data[blank_end]
Snort - [blank_start]Connection Event[blank_end]- Atcpdump
- BCisco Umbrella
- CTransaction data
- DConnection Event
11Refer to the exhibit. What is occurring in this network traffic?
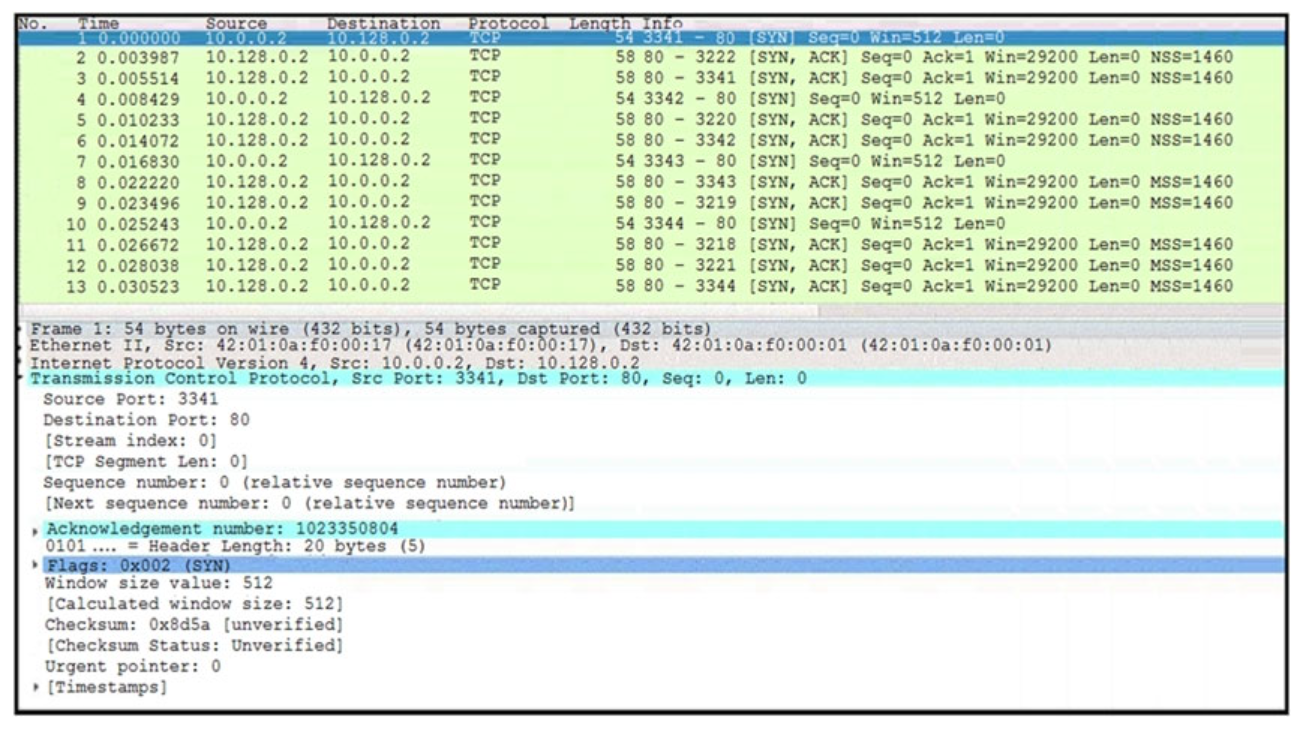
- AHigh rate of SYN packets being sent from a multiple source towards a single destination IP.
- BHigh rate of ACK packets being sent from a single source IP towards multiple destination IPs.
- CFlood of ACK packets coming from a single source IP to multiple destination IPs.
- DFlood of SYN packets coming from a single source IP to a single destination IP.
12An engineer needs to have visibility on TCP bandwidth usage, response time, and latency, combined with deep packet inspection to identify unknown software by its network traffic flow. Which two features of Cisco Application Visibility and Control should the engineer use to accomplish this goal? (Choose two.)
- AManagement and reporting,
- BTraffic filtering.
- CAdaptive AVC.
- DMetrics collection and exporting.
- EApplication recognition.
13Which security technology guarantees the integrity and authenticity of all messages transferred to and from a web application?
- AHypertext Transfer Protocol.
- BSSL Certificate.
- CTunneling.
- DVPN.
14An engineer is investigating a case of the unauthorized usage of the Tcpdump tool. The analysis revealed that a malicious insider attempted to sniff traffic on a specific interface. What type of information did the malicious insider attempt to obtain?
- ATagged protocols being used on the network.
- BAll firewall alerts and resulting mitigations.
- CTagged ports being used on the network.
- DAll information and data within the datagram,
15At a company party a guest asks questions about the company's user account format and password complexity. How is this type of conversation classified?
- APhishing attack.
- BPassword Revelation Strategy.
- CPiggybacking.
- DSocial Engineering.
16One of the objectives of information security is to protect the CIA of information and systems.
What does CIA mean in this context?- AConfidentiality, identity, and authorization.
- BConfidentiality, integrity, and authorization.
- CConfidentiality, identity, and availability.
- DConfidentiality, integrity, and availability.
17What is rule-based detection when compared to statistical detection?
- AProof of a user's identity.
- BProof of a user's action.
- CLikelihood of user's action.
- DFalsification of a user's identity.
18A user received a malicious attachment but did not run it.
Which category classifies the intrusion?- AWeaponization.
- BReconnaissance.
- CInstallation,
- DDelivery.
19Which data format is the most efficient to build a baseline of traffic seen over an extended period of time?
- ASyslog messages.
- BFull packet capture.
- CNetFlow.
- DFirewall event logs.
20Refer to the exhibit.
What information is depicted?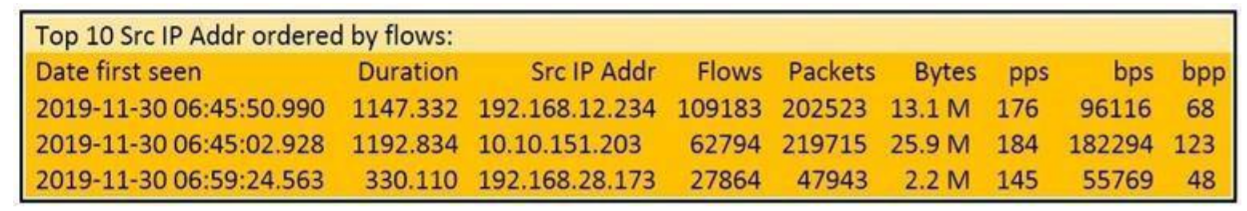
- AIIS Data.
- BNetFlow Data.
- CNetwork discovery event.
- DIPS Event Data.
21What is the difference between a threat and a risk?
- AThreat represents a potential danger that could take advantage of a weakness in a system.
- BRisk represents the known and identified loss or danger in the system.
- CRisk represents the nonintentional interaction with uncertainty in the system.
- DThreat represents a state of being exposed to an attack or a compromise either physically or logically.
22An engineer runs a suspicious file in a sandbox analysis tool to see the outcome. The analysis report shows that outbound callouts were made post infection.
Which two pieces of information from the analysis report are needed to investigate the callouts? (Choose two.)- ASignatures.
- BHost IP Addresses.
- CFile size.
- DDropped Files.
- EDomain Names.
23Refer to the exhibit. Which packet contains a file that is extractable within Wireshark?
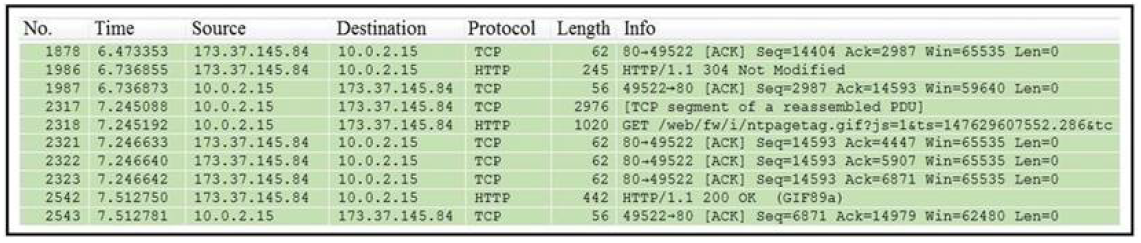
- A2317
- B1986
- C2318
- D2542
24Which type of evidence supports a theory or an assumption that results from initial evidence?
- AProbabilistic
- BIndirect
- CBest
- DCorroborative
25Drag and drop the access control models from the left onto the correct descriptions on the right.
Object owner determines permissions: [blank_start]DAC[blank_end]
OS determines permissions: [blank_start]MAC[blank_end]
Role of the subject determines permissions: [blank_start]RBAC[blank_end]
Attributes of the subject determine permissions: [blank_start]ABAC[blank_end]- ADAC
- BMAC
- CRBAC
- DABAC
26Which category relates to improper use or disclosure of PII data?
- ALegal
- BCompliance
- CRegulated
- DContractual
27What is a purpose of a vulnerability management framework?
- AIdentifies, removes, and mitigates system vulnerabilities.
- BDetects and removes vulnerabilities in source code.
- CConducts vulnerability scans on the network.
- DManages a list of reported vulnerabilities.
28What is the function of a command and control server?
- AIt enumerates open ports on a network device.
- BIt drops secondary payload into malware.
- CIt is used to regain control of the network after a compromise.
- DIt sends instruction to a compromised system.
29What does an attacker use to determine which network ports are listening on a potential target device?
- AMan-in-the-middle
- BPort scanning
- CSQL injection
- DPing sweep
30Which attack method intercepts traffic on a switched network?
- ADenial or service.
- BARP cache poisoning.
- CDHCP snooping.
- DCommand and control.
31Which type of data collection requires the largest amount of storage space?
- AAlert Data.
- BTransaction Data.
- CSession Data.
- DFull Packet Capture.
32What specific type of analysis is assigning values to the scenario to see expected outcomes?
- ADeterministic
- BExploratory
- CProbabilistic
- DDescriptive
33How does certificate authority impact a security system?
- AIt authenticates client identity when requesting SSL certificate.
- BIt validates domain identity of a SSL certificate.
- CIt authenticates domain identity when requesting SSL certificate.
- DIt validates client identity when communicating with the server.
34What is the difference between mandatory access control (MAC) and discretionary access control (DAC)?
- AMAC is controlled by the discretion of the owner and DAC is controlled by an administrator.
- BMAC is the strictest of all levels of control and DAC is object-based access.
- CDAC is controlled by the operating system and MAC is controlled by an administrator
- DDAC is the strictest of all levels of control and MAC is object-based access
35Which evasion technique is a function of ransomware?
- AExtended sleep calls.
- BEncryption.
- CResource exhaustion.
- DEncoding.
36Which regex matches only on all lowercase letters?
- A[az]+
- B[^az]+
- Caz+
- Da*z+
37What are the two characteristics of the full packet captures? (Choose two.)
- AIdentifying network loops and collision domains.
- BTroubleshooting the cause of security and performance issues.
- CReassembling fragmented traffic from raw data.
- DDetecting common hardware faults and identify faulty assets.
- EProviding a historical record of a network transaction.
38Which signature impacts network traffic by causing legitimate traffic to be blocked?
- AFalse negative.
- BTrue positive.
- CTrue negative.
- DFalse positive.
39An intruder attempted malicious activity and exchanged emails with a user and received corporate information, including email distribution lists. The intruder asked
the user to engage with a link in an email. When the fink launched, it infected machines and the intruder was able to access the corporate network.
Which testing method did the intruder use?- ASocial Engineering.
- BEavesdropping.
- CPiggybacking.
- DTailgating.
40Which evasion technique is indicated when an intrusion detection system begins receiving an abnormally high volume of scanning from numerous sources?
- AResource exhaustion.
- BTunneling.
- CTraffic fragmentation.
- DTiming attack.
41While viewing packet capture data, an analyst sees that one IP is sending and receiving traffic for multiple devices by modifying the IP header.
Which technology makes this behavior possible?- AEncapsulation
- BTOR
- CTunneling
- DNAT
42Which artifact is used to uniquely identify a detected file?
- AFile Timestamp.
- BFile Extension.
- CFile Size.
- DFile Hash.
43Refer to the exhibit. What does the message indicate?
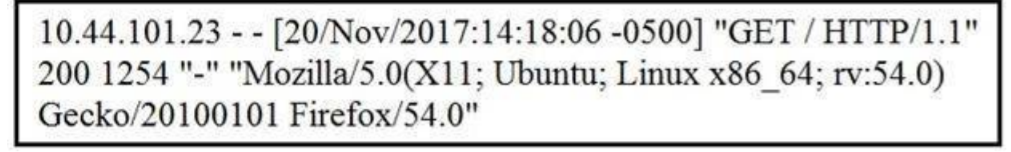
- AAn access attempt was made from the Mosaic web browser.
- BA successful access attempt was made to retrieve the password file.
- CA successful access attempt was made to retrieve the root of the website.
- DA denied access attempt was made to retrieve the password file.
44Which event artifact is used to identity HTTP GET requests for a specific file?
- ADestination IP address.
- BTCP ACK.
- CHTTP status code.
- DURI
45Which system monitors local system operation and local network access for violations of a security policy?
- AHost-based intrusion detection.
- BSystems-based sandboxing.
- CHost-based firewall.
- DAntivirus.
46Which NIST IR category stakeholder is responsible for coordinating incident response among various business units, minimizing damage, and reporting to
regulatory agencies?- ACSIRT
- BPSIRT
- CPublic affairs
- DManagement
47A security engineer deploys an enterprise-wide host/endpoint technology for all of the company's corporate PCs. Management requests the engineer to block a selected set of applications on all PCs.
Which technology should be used to accomplish this task?- AApplication whitelisting/blacklisting.
- BNetwork NGFW.
- CHost-based IDS.
- DAntivirus/antispyware software.
48Refer to the exhibit. What does the output indicate about the server with the IP address 172.18.104.139?
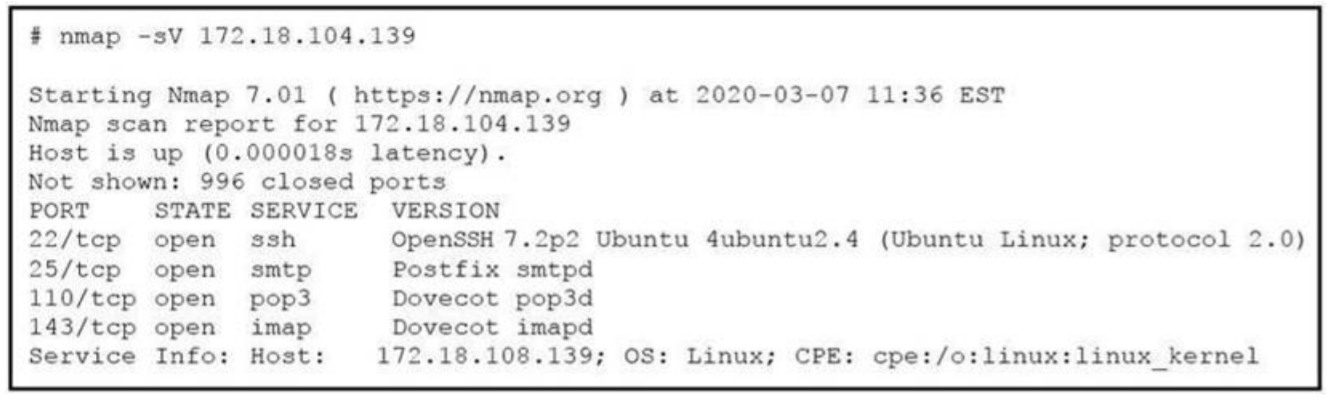
- AOpen ports of a web server.
- BOpen ports on an FTP server.
- COpen ports of an email server.
- DRunning processes of the server.
49What is the difference between the ACK flag and the RST flag in the NetFlow log session?
- AThe RST flag confirms the beginning of the TCP connection, and the ACK flag responds when the data for the payload is complete.
- BThe ACK flag confirms the beginning of the TCP connection, and the RST flag responds when the data for the payload is complete.
- CThe RST flag confirms the receipt of the prior segment, and the ACK flag allows for the spontaneous termination of a connection.
- DThe ACK flag confirms the receipt of the prior segment, and the RST flag allows for the spontaneous termination of a connection.
50Which two elements are used for profiling a network? (Choose two.)
- ATotal throughout
- BSession duration
- CRunning processes
- DOS fingerprint
- EListening ports
51When communicating via TLS, the client initiates the handshake to the server and the server responds back with its certificate for identification.
Which information is available on the server certificate?- AServer name, trusted subordinate CA, and private.
- BTrusted subordinate CA, public key, and cipher suites.
- CTrusted CA name, cipher suites, and private key.
- DServer name, trusted CA, and public key.
52Which list identifies the information that the client sends to the server in the negotiation phase of the TLS handshake?
- AClientStart, ClientKeyExchange, cipher-suites it supports, and suggested compression methods.
- BClientStart, TLS versions it supports, cipher-suites it supports, and suggested compression methods.
- CClientHello, TLS versions it supports, cipher-suites it supports, and suggested compression methods.
- DClientHello, ClientKeyExchange, cipher-suites it supports, and suggested compression methods.
53Which security technology allows only a set of pre-approved applications to run on a system?
- AApplication-level blacklisting.
- BHost-based IPS.
- CApplication-level whitelisting.
- DAntivirus.
54Which type of attack occurs when an attacker is successful in eavesdropping on a conversation between two IP phones?
- AKnown-plaintext.
- BReplay.
- CDictionary.
- DMan-in-the-middle.
55A SOC analyst is investigating an incident that involves a Linux system that is identifying specific sessions. Which identifier tracks an active program?
- AApplication identification number.
- BActive process identification number.
- CRuntime identification number.
- Dprocess identification number.
56How is attacking a vulnerability categorized?
- AAction on objectives.
- BDelivery.
- CExploitation.
- DInstallation.
57What are two social engineering techniques? (Choose two.)
- APrivilege Escalation.
- BDDoS attack.
- CPhishing.
- DMan-in-the-middle.
- EPharming.
58Which attack is the network vulnerable to when a stream cipher like RC4 is used twice with the same key?
- AForgery attack.
- BPlaintext-only attack.
- CCiphertext-only attack.
- DMan-in-the-middle attack.
59What is a difference between SOAR and SIEM?
- ASOAR platforms are used for threat and vulnerability management, but SIEM applications are not.
- BSIEM applications are used for threat and vulnerability management, but SOAR platforms are not.
- CSOAR receives information from a single platform and delivers it to a SIEM.
- DSIEM receives information from a single platform and delivers it to a SOAR.
60Refer to the exhibit.
Which two elements in the table are parts of the 5-tuple? (Choose two.)
- AFirst Packet.
- BInitial User.
- CIngress Security Zone.
- DSource Port.
- EInitiator IP.
61Why is encryption challenging to security monitoring?
- AEncryption analysis is used by attackers to monitor VPN tunnels.
- BEncryption is used by threat actors as a method of evasion and obfuscation.
- CEncryption introduces additional processing requirements by the CPU.
- DEncryption introduces larger packet sizes to analyze and store.
62Which event is user interaction?
- AGaining root access.
- BExecuting remote code.
- CReading and writing file permission.
- DOpening a malicious file.
63Which security principle requires more than one person is required to perform a critical task?
- ALeast privilege.
- BNeed to know.
- CSeparation of duties.
- DDue diligence.
64What is a benefit of agent-based protection when compared to agentless protection?
- AIt lowers maintenance costs.
- BIt provides a centralized platform.
- CIt collects and detects all traffic locally.
- DIt manages numerous devices simultaneously.
65Which principle is being followed when an analyst gathers information relevant to a security incident to determine the appropriate course of action?
- ADecision making.
- BRapid Response.
- CData Mining.
- DDue Diligence.
66One of the objectives of information security is to protect the CIA of information and systems.
What does CIA mean in this context?- AConfidentiality, identity, and authorization.
- BConfidentiality, integrity, and authorization.
- CConfidentiality, identity, and availability.
- DConfidentiality, integrity, and availability.
67Which process is used when IPS events are removed to improve data integrity?
- AData availability.
- BData normalization.
- CData signature.
- DData protection.
68An analyst is investigating an incident in a SOC environment.
Which method is used to identify a session from a group of logs?- ASequence numbers.
- BIP identifier.
- C5-tuple.
- DTimestamps.
69What is the practice of giving employees only those permissions necessary to perform their specific role within an organization?
- ALeast privilege.
- BNeed to know.
- CIntegrity validation.
- DDue diligence.
70What is the virtual address space for a Windows process?
- APhysical location of an object in memory.
- BSet of pages that reside in the physical memory.
- CSystem-level memory protection feature built into the operating system.
- DSet of virtual memory addresses that can be used.
71Which security principle is violated by running all processes as root or administrator?
- APrinciple of least privilege.
- BRole-based access control.
- CSeparation of duties.
- DTrusted computing base.
72What is the difference between deep packet inspection and stateful inspection?
- ADeep packet inspection is more secure than stateful inspection on Layer 4.
- BStateful inspection verifies contents at Layer 4 and deep packet inspection verifies connection at Layer 7.
- CStateful inspection is more secure than deep packet inspection on Layer 7.
- DDeep packet inspection allows visibility on Layer 7 and stateful inspection allows visibility on Layer 4.
73Drag and drop the security concept on the left onto the example of that concept on the right.
Network is compromised - [blank_start]Exploit[blank_end]
Lack of an access list - [blank_start]Vulnerability[blank_end]
Configuration Review - [blank_start]Risk Assessment[blank_end]Leakage of confidential information - [blank_start]Threat[blank_end]- AExploit
- BVulnerability
- CRisk Assessment
- DThreat
74What is the difference between statistical detection and rule-based detection models?
- ARule-based detection involves the collection of data in relation to the behavior of legitimate users over a period of time.
- BStatistical detection defines legitimate data of users over a period of time and rule-based detection defines it on an IF/THEN basis.
- CStatistical detection involves the evaluation of an object on its intended actions before it executes that behavior.
- DRule-based detection defines legitimate data of users over a period of time and statistical detection defines it on an IF/THEN basis.
75A network engineer discovers that a foreign government hacked one of the defense contractors in their home country and stole intellectual property. What is the threat agent in this situation?
- AThe intellectual property that was stolen.
- BThe defense contractor who stored the intellectual property.
- CThe method used to conduct the attack.
- DThe foreign government that conducted the attack.
76What is the practice of giving an employee access to only the resources needed to accomplish their job?
- APrinciple of least privilege.
- BOrganizational separation.
- CSeparation of duties.
- DNeed to know principle.
77Which metric is used to capture the level of access needed to launch a successful attack?
- APrivileges required.
- BUser interaction.
- CAttack complexity.
- DAttack vector.
78What is the difference between an attack vector and attack surface?
- AAn attack surface identifies vulnerabilities that require user input or validation; and an attack vector identifies vulnerabilities that are independent of user actions.
- BAn attack vector identifies components that can be exploited; and an attack surface identifies the potential path an attack can take to penetrate the network.
- CAn attack surface recognizes which network parts are vulnerable to an attack; and an attack vector identifies which attacks are possible with these vulnerabilities.
- DAn attack vector identifies the potential outcomes of an attack; and an attack surface launches an attack using several methods against the identified vulnerabilities.
79Which metric in CVSS indicates an attack that takes a destination bank account number and replaces it with a different bank account number?
- AIntegrity.
- BConfidentiality.
- CAvailability.
- DScope.
80A security specialist notices 100 HTTP GET and POST requests for multiple pages on the web servers. The agent in the requests contains PHP code that, if executed, creates and writes to a new PHP file on the webserver. Which event category is described?
- AReconnaissance
- BAction on objectives
- CInstallation
- DExploitation
81When trying to evade IDS/IPS devices, which mechanism allows the user to make the data incomprehensible without a specific key, certificate, or password?
- AFragmentation.
- BPivoting.
- CEncryption.
- DStenography.
82An employee reports that someone has logged into their system and made unapproved changes, files are out of order, and several documents have been placed in the recycle bin. The security specialist reviewed the system logs, found nothing suspicious, and was not able to determine what occurred. The software is up to date; there are no alerts from antivirus and no failed login attempts. What is causing the lack of data visibility needed to detect the attack?
- AThe threat actor used a dictionary-based password attack to obtain credentials.
- BThe threat actor gained access to the system by known credentials.
- CThe threat actor used the teardrop technique to confuse and crash login services.
- DThe threat actor used an unknown vulnerability of the operating system that went undetected.
83A company receptionist received a threatening call referencing stealing assets and did not take any action assuming it was a social engineering attempt. Within
48 hours, multiple assets were breached, affecting the confidentiality of sensitive information. What is the threat actor in this incident?- ACompany assets that are threatened.
- BCustomer assets that are threatened.
- CPerpetrators of the attack.
- DVictims of the attack.
84What is the relationship between a vulnerability and a threat?
- AA threat exploits a vulnerability.
- BA vulnerability is a calculation of the potential loss caused by a threat.
- CA vulnerability exploits a threat.
- DA threat is a calculation of the potential loss caused by a vulnerability.
85What is the principle of defense-in-depth?
- AAgentless and agent-based protection for security are used.
- BSeveral distinct protective layers are involved.
- CAccess control models are involved.
- DAuthentication, authorization, and accounting mechanisms are used.
86Drag and drop the uses on the left onto the type of security system on the right.
Ensures protection of individual devices: [blank_start]Endpoint[blank_end]
Detects intrusion attempts: [blank_start]Network[blank_end]
Monitors host for suspicious activity: [blank_start]Endpoint[blank_end]
Monitors incoming traffic and connection: [blank_start]Network[blank_end]- AEndpoint
- BNetwork
- CEndpoint
- DNetwork
- EEndpoint
- FNetwork
- GEndpoint
- HNetwork
87What is the difference between the rule-based detection when compared to behavioral detection?
- ARule-Based detection is searching for patterns linked to specific types of attacks, while behavioral is identifying per signature.
- BRule-Based systems have established patterns that do not change with new data, while behavioral changes.
- CBehavioral systems are predefined patterns from hundreds of users, while Rule-Based only flags potentially abnormal patterns using signatures.
- DBehavioral systems find sequences that match a particular attack signature, while Rule-Based identifies potential attacks.
88Which open-sourced packet capture tool uses Linux and Mac OS X operating systems?
- ANetScout
- Btcpdump
- CSolarWinds
- Dnetsh
89Refer to the exhibit. Which kind of attack method is depicted in this string?
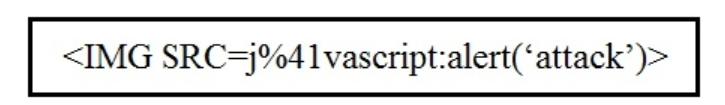
- ACross-site scripting.
- BMan-in-the-middle.
- CSQL injection.
- DDenial of service.
90Which two components reduce the attack surface on an endpoint? (Choose two.)
- ASecure boot,
- BLoad balancing.
- CIncreased audit log levels.
- DRestricting USB ports.
- EFull packet capture at the endpoint.
91What is an attack surface as compared to a vulnerability?
- AAny potential danger to an asset.
- BThe sum of all paths for data into and out of the environment.
- CAn exploitable weakness in a system or its design.
- DThe individuals who perform an attack.
92How does an SSL certificate impact security between the client and the server?
- ABy enabling an authenticated channel between the client and the server.
- BBy creating an integrated channel between the client and the server.
- CBy enabling an authorized channel between the client and the server.
- DBy creating an encrypted channel between the client and the server.
93Refer to the exhibit. Which type of log is displayed?
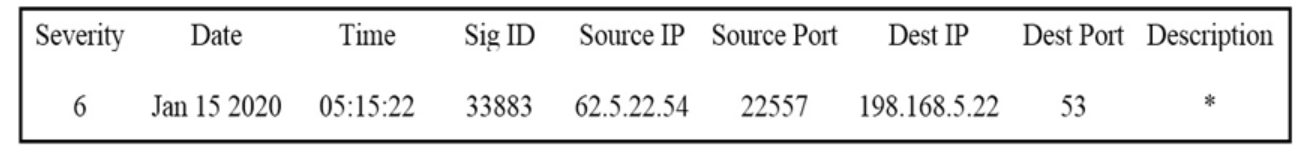
- AIDS
- BProxy
- CNetFlow
- Dsys
94Refer to the exhibit. What type of log is displayed?

- Aproxy
- BNetFlow
- CIDS
- Dsys
95How is NetFlow different from traffic mirroring?
- ANetFlow collects metadata and traffic mirroring clones data.
- BTraffic mirroring impacts switch performance and NetFlow does not.
- CTraffic mirroring costs less to operate than NetFlow.
- DNetFlow generates more data than traffic mirroring.
96What makes HTTPS traffic difficult to monitor?
- ASSL interception.
- BPacket header size.
- CSignature detection time.
- DEncryption.
97How does an attacker observe network traffic exchanged between two users?
- APort Scanning.
- BMan-in-the-middle.
- CCommand injection.
- DDenial of service.
98Which type of data consists of connection level, application-specific records generated from network traffic?
- ATransaction data.
- BLocation data.
- CStatistical data.
- DAlert data.
99An engineer needs to discover alive hosts within the 192.168.1.0/24 range without triggering intrusive portscan alerts on the IDS device using Nmap. Which command will accomplish this goal?
- AMiTM
- BTCP Connections
- CPing of death
- DUDP Flooding
- ECode red
100An engineer needs to discover alive hosts within the 192.168.1.0/24 range without triggering intrusive portscan alerts on the IDS device using Nmap. Which command will accomplish this goal?
- Anmap --top-ports 192.168.1.0/24
- Bnmap ג€"sP 192.168.1.0/24
- Cnmap -sL 192.168.1.0/24
- Dnmap -sV 192.168.1.0/24
101An analyst is investigating a host in the network that appears to be communicating to a command and control server on the Internet. After collecting this packet capture, the analyst cannot determine the technique and payload used for the communication.
Which obfuscation technique is the attacker using?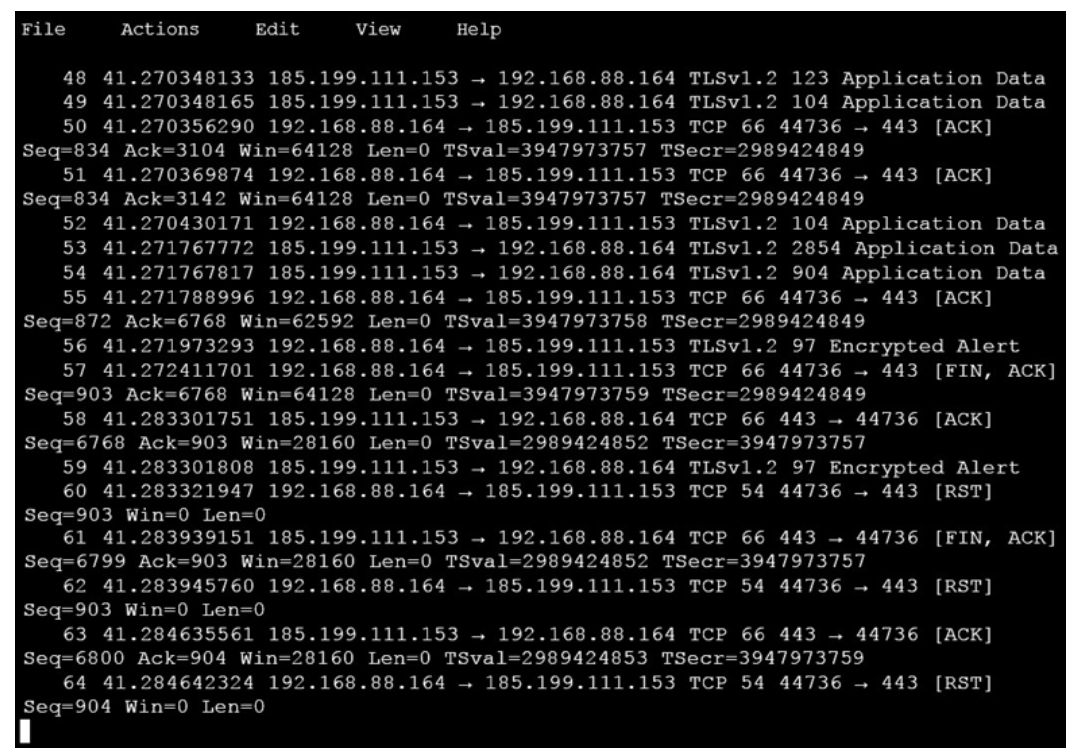
- ABase64Encoding
- BTransport layer security encryption.
- CSHA-256 hashing.
- DROT13 encryption.
102What are two differences in how tampered and untampered disk images affect a security incident? (Choose two.)
- AUntampered images are used in the security investigation process
- BTampered images are used in the security investigation process
- CThe image is tampered if the stored hash and the computed hash match
- DTampered images are used in the incident recovery process
- EThe image is untampered if the stored hash and the computed hash match
103Which step in the incident response process researches an attacking host through logs in a SIEM?
- ADetection and analysis.
- BPreparation.
- CEradication.
- DContainment.
104TBC
Which piece of information is needed to search for additional downloads of this file by other hosts?- AFile type
- BFile size
- CFile name
- DFile hash value
105Refer to the exhibit. What is the potential threat identified in this Stealthwatch dashboard?
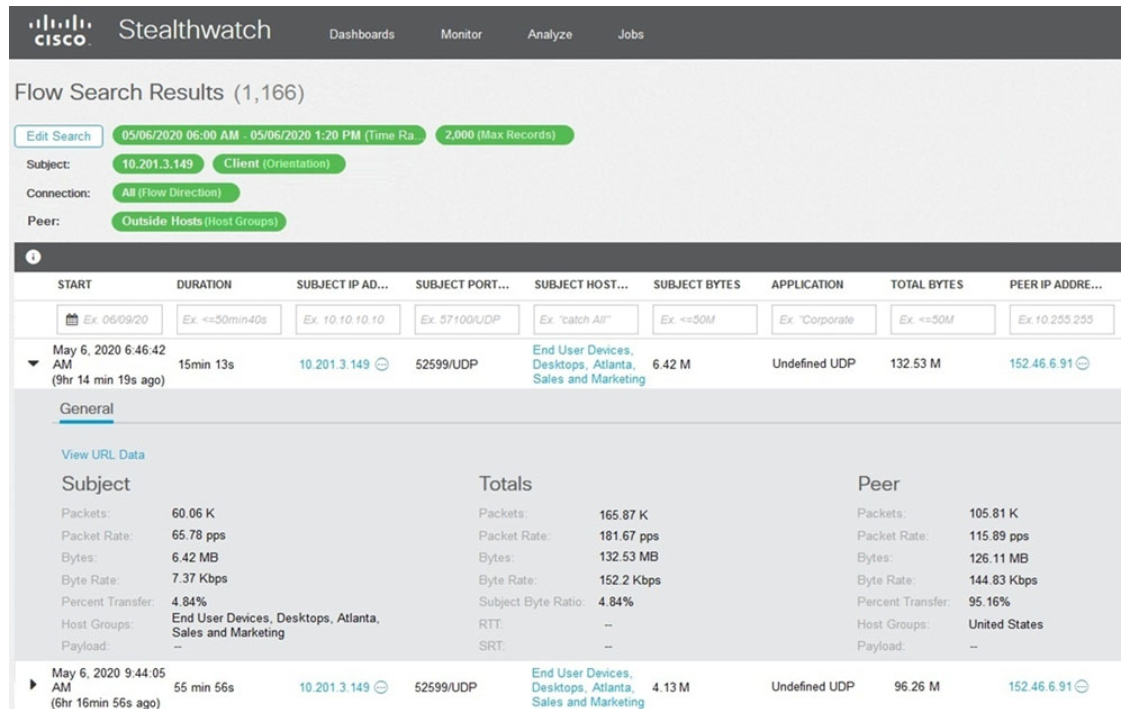
- AHost 10.201.3.149 is sending data to 152.46.6.91 using TCP/443.
- BHost 152.46.6.91 is being identified as a watchlist country for data transfer.
- CTraffic to 152.46.6.149 is being denied by an Advanced Network Control policy.
- DHost 10.201.3.149 is receiving almost 19 times more data than is being sent to host 152.46.6.91.
106Refer to the exhibit. What is the potential threat identified in this Stealthwatch dashboard?
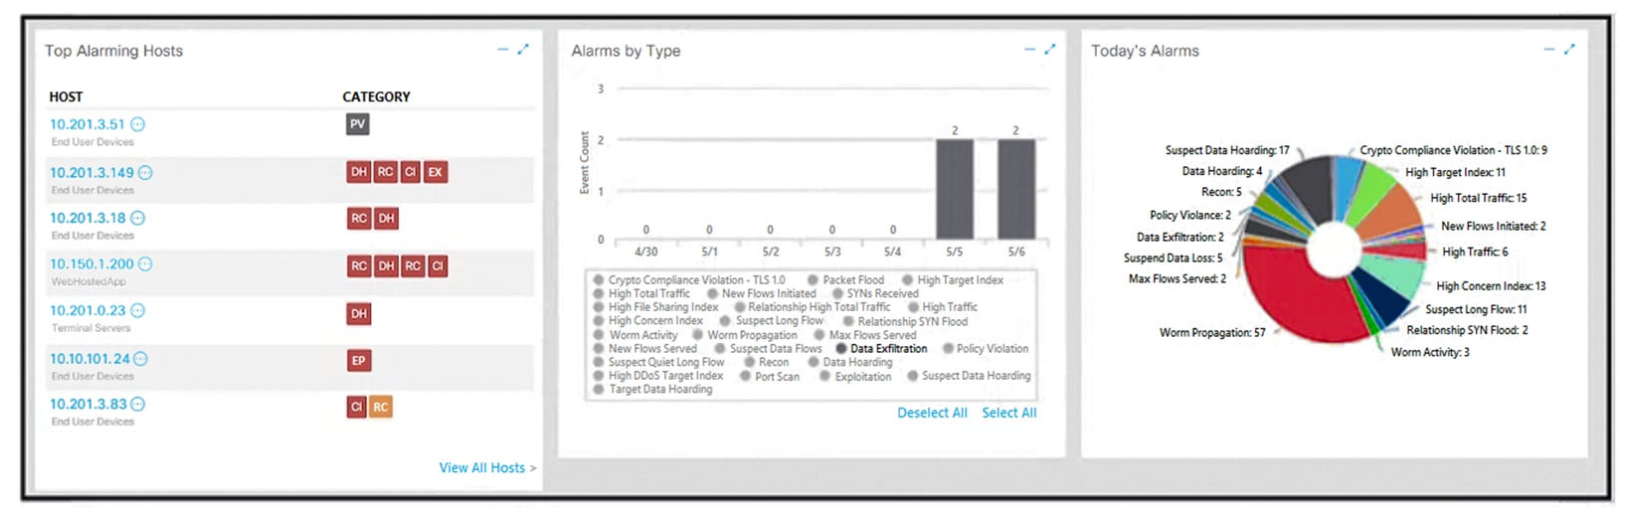
- AA policy violation is active for host 10.10.101.24.
- BA host on the network is sending a DDoS attack to another inside host.
- CThere are two active data exfiltration alerts.
- DA policy violation is active for host 10.201.3.149.
107An investigator is examining a copy of an ISO file that is stored in CDFS format.
What type of evidence is this file?- Adata from a CD copied using Mac-based system
- Bdata from a CD copied using Linux system
- Cdata from a DVD copied using Windows system
- Ddata from a CD copied using Windows
108Which piece of information is needed for attribution in an investigation?
- Aproxy logs showing the source RFC 1918 IP addresses
- BRDP allowed from the Internet
- Cknown threat actor behavior
- D802.1x RADIUS authentication pass arid fail logs
109What does cyber attribution identify in an investigation?
- Acause of an attack
- Bexploit of an attack
- Cvulnerabilities exploited
- Dthreat actors of an attack
110A security engineer has a video of a suspect entering a data center that was captured on the same day that files in the same data center were transferred to a competitor.
Which type of evidence is this?- Abest evidence
- Bprima facie evidence
- Cindirect evidence
- Dphysical evidence
111Refer to the exhibit. Which event is occurring?

- AA binary named "submit" is running on VM cuckoo1.
- BA binary is being submitted to run on VM cuckoo1
- CA binary on VM cuckoo1 is being submitted for evaluation
- DA URL is being evaluated to see if it has a malicious binary
112Refer to the exhibit. In which Linux log file is this output found?
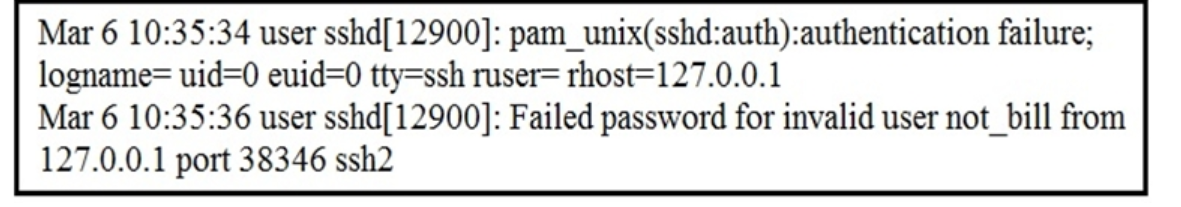
- A/var/log/authorization.log
- B/var/log/dmesg
- Cvar/log/var.log
- D/var/log/auth.log
Information
- Description
- Quiz on Untitled, created by Aimee M on 19/08/2021.
- Author
- Aimee M
- Language
- English
- Views
- 3
- Tags
- Rating
- No ratings yet Rate this quiz