
Mindmap
5.15 Windows ACL's
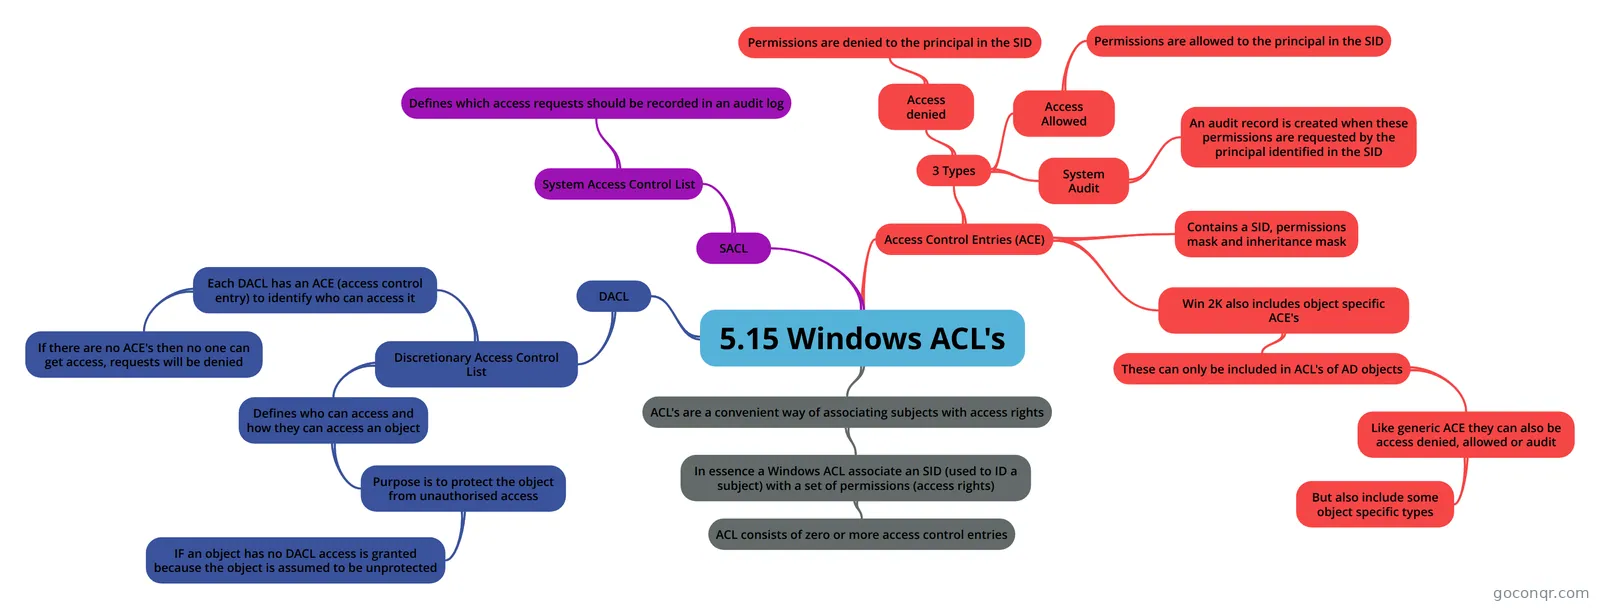
Mind map: Windows ACL's
Inhalt der Mindmap
5.15 Windows ACL's
ACL's are a convenient way of associating subjects with access rights
- In essence a Windows ACL associate an SID (used to ID a subject) with a set of permissions (access rights)
- ACL consists of zero or more access control entries
- In essence a Windows ACL associate an SID (used to ID a subject) with a set of permissions (access rights)
DACL
- Discretionary Access Control List
- Defines who can access and how they can access an object
- Purpose is to protect the object from unauthorised access
- IF an object has no DACL access is granted because the object is assumed to be unprotected
- Purpose is to protect the object from unauthorised access
- Each DACL has an ACE (access control entry) to identify who can access it
- If there are no ACE's then no one can get access, requests will be denied
- Defines who can access and how they can access an object
- Discretionary Access Control List
SACL
- System Access Control List
- Defines which access requests should be recorded in an audit log
- System Access Control List
Access Control Entries (ACE)
- 3 Types
- Access denied
- Permissions are denied to the principal in the SID
- Access Allowed
- Permissions are allowed to the principal in the SID
- System Audit
- An audit record is created when these permissions are requested by the principal identified in the SID
- Access denied
- Contains a SID, permissions mask and inheritance mask
- Win 2K also includes object specific ACE's
- These can only be included in ACL's of AD objects
- Like generic ACE they can also be access denied, allowed or audit
- But also include some object specific types
- Like generic ACE they can also be access denied, allowed or audit
- These can only be included in ACL's of AD objects
- 3 Types
Informationen
- Beschreibung
- Masters Comp Sec Mindmap am 5.15 Windows ACL's, erstellt von Craig Parker am 21/12/2014.
- Erstellt von
- Craig Parker
- Aufrufe
- 7
- Bewertung