
Quiz
EX200 - 001 - RHEL6
This quiz has question types that open in the usual player.
Questions in this quiz (15)
1Configure your Host Name, IP Address, Gateway and DNS.
Host name: station.domain40.example.com
/etc/sysconfig/network
hostname=abc.com
hostname abc.com
IP Address: 172.24.40.40/24
Gateway: 172.24.40.1
DNS: 172.24.40.1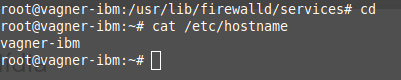
- Aifcfg-eth0
2Add 3 users: harry, natasha, tom.
The requirements: The Additional group of the two users: harry, Natasha is the admin group.
The user: tom's login shell should be non-interactive.- AAnswer: # useradd -G admin harry
# useradd -G admin natasha
# useradd -s /sbin/nologin tom
# id harry;id Natasha (Show additional group)
# cat /etc/passwd - BNA
- AAnswer: # useradd -G admin harry
3Create a catalog under /home named admins. Its respective group is requested to be the admin group. The group users could read and write, while other users are not allowed to access it.
The files created by users from the same group should also be the admin group.- A# cd /home/
# mkdir admins /
# chown .admin admins/
# chmod 770 admins/
# chmod g+s admins/ - BNA
- A# cd /home/
4Configure a task: plan to run echo hello command at 14:23 every day.
- A# which echo
# crontab -e
23 14 * * * /bin/echo hello
# crontab -l (Verify) - BNA
- A# which echo
5Create a 2G swap partition which take effect automatically at boot-start, and it should not affect the original swap partition.
- A# fdisk /dev/sda
p
(check Partition table)
n
(create new partition: press e to create extended partition, press p to create the main partition, and the extended partition is further divided into logical partitions)
Enter
+2G
t
l
W
partx -a /dev/sda
partprobe
mkswap /dev/sda8
Copy UUID
swapon -a
vim /etc/fstab
UUID=XXXXX swap swap defaults 0 0
(swapon -s) - BNA
- A# fdisk /dev/sda
6Create a user named alex, and the user id should be 1234, and the password should be alex111.
- A# useradd -u 1234 alex
# passwd alex
alex111
alex111 - BNA
- A# useradd -u 1234 alex
7Install a FTP server, and request to anonymous download from /var/ftp/pub catalog. (it needs you to configure yum direct to the already existing file server. )
- A# cd /etc/yum.repos.d
# vim local.repo
[local]
name=local.repo
baseurl=file:///mnt
enabled=1
gpgcheck=0
# yum makecache
# yum install -y vsftpd
# service vsftpd restart
# chkconfig vsftpd on
# chkconfig --list vsftpd
# vim /etc/vsftpd/vsftpd.conf
anonymous_enable=YES - BNA
- A# cd /etc/yum.repos.d
8Configure a HTTP server, which can be accessed through http://station.domain40.example.com.
Please download the released page from http://ip/dir/example.html.- A# yum install -y httpd
# chkconfig httpd on
# cd /var/www/html
# wget http://ip/dir/example.html
# cp example.com index.html
# vim /etc/httpd/conf/httpd.conf
NameVirtualHost 192.168.0.254:80
<VirtualHost 192.168.0.254:80>
DocumentRoot /var/www/html/
ServerName station.domain40.example.com
</VirtualHost> - BNA
- A# yum install -y httpd
9Configure the verification mode of your host account and the password as LDAP. And it can ldapuser40. The password is set as "password". And the certificate login successfully through can be downloaded from http://ip/dir/ldap.crt. After the user logs on , the user has no host directory unless you configure the autofs in the following questions.
- A# yum groupinstall directory-client (1.krb5-workstation 2.pam-krb5 3.sssd)
# system-config-authentication
1.User Account Database: LDAP
2.LDAP Search Base DN: dc=example,dc=com
3.LDAP Server: ldap://instructor.example.com (In domain form, not write IP) 4.Download CA Certificate
5.Authentication Method: LDAP password
6.Apply
getent passwd ldapuser40 - Bsystem-config-authentication
LDAP Server: ldap//instructor.example.com (In domain form, not write IP)
- A# yum groupinstall directory-client (1.krb5-workstation 2.pam-krb5 3.sssd)
10Configure autofs to make sure after login successfully, it has the home directory autofs, which is shared as /rhome/ldapuser40 at the ip: 172.24.40.10. and it also requires that, other ldap users can use the home directory normally.
- A# chkconfig autofs on
# cd /etc/
# vim /etc/auto.master
/rhome /etc/auto.ldap
# cp auto.misc auto.ldap
# vim auto.ladp
ldapuser40 -rw,soft,intr 172.24.40.10:/rhome/ldapuser40
* -rw,soft,intr 172.16.40.10:/rhome/&
# service autofs stop
# server autofs start
# showmount -e 172.24.40.10
# su - ladpuser40 - BNA
- A# chkconfig autofs on
11Configure the system synchronous as 172.24.40.10.
- A# system-config-date
- BAnswer: Graphical Interfaces:
System-->Administration-->Date & Time
12Change the logical volume capacity named vo from 190M to 300M. and the size of the floating range should set between 280 and 320. (This logical volume has been mounted in advance.)
- A# vgdisplay
(Check the capacity of vg, if the capacity is not enough, need to create pv , vgextend , lvextend)
# lvdisplay (Check lv)
# lvextend -L +110M /dev/vg2/lv2
# resize2fs /dev/vg2/lv2
mount -a
(Verify)
------------------------------------------------------------------------------- (Decrease lvm)
# umount /media
# fsck -f /dev/vg2/lv2
# resize2fs -f /dev/vg2/lv2 100M
# lvreduce -L 100M /dev/vg2/lv2
# mount -a
# lvdisplay (Verify) - B# e2fsck -f /dev/vg1/lvm02
# resize2fs -f /dev/vg1/lvm02
# mount /dev/vg1/lvm01 /mnt
# lvreduce -L 1G -n /dev/vg1/lvm02
# lvdisplay (Verify)
- A# vgdisplay
13Create a volume group, and set 16M as a extends. And divided a volume group containing 50 extends on volume group lv, make it as ext4 file system, and mounted automatically under /mnt/data.
- AAnswer: # pvcreate /dev/sda7 /dev/sda8
# vgcreate -s 16M vg1 /dev/sda7 /dev/sda8
# lvcreate -l 50 -n lvm02
# mkfs.ext4 /dev/vg1/lvm02
http://www.gratisexam.com/# blkid /dev/vg1/lv1
# vim /etc/fstab
# mkdir -p /mnt/data
UUID=xxxxxxxx /mnt/data ext4 defaults 0 0
# vim /etc/fstab
# mount -a
# mount
(Verify) - BNA
- AAnswer: # pvcreate /dev/sda7 /dev/sda8
14The Additional group of the two users: user2, user3 is the admin group Password: redhat
- AAnswer: # useradd -G admin user2
# useradd -G admin user3
# passwd user2
redhat
# passwd user3
redhat - BNA
- AAnswer: # useradd -G admin user2
15Copy /etc/fstab to /var/tmp name admin, the user1 could read, write and modify it, while user2 without any permission.
- AAnswer: # cp /etc/fstab /var/tmp/
# chgrp admin /var/tmp/fstab
# setfacl -m u:user1:rwx /var/tmp/fstab
# setfacl -m u:user2:--- /var/tmp/fstab
# ls -l
-rw-rw-r--+ 1 root admin 685 Nov 10 15:29 /var/tmp/fstab - BNA
- AAnswer: # cp /etc/fstab /var/tmp/
Information
- Description
- Teste
- Author
- Vagner Aragão
- Language
- Português
- Views
- 43
- History
- Created on 31 Jan 2019 · updated on 1 Feb 2019
- Tags
- Rating
- No ratings yet Rate this quiz