
Quiz
70-411 - MCSA: Administering Windows Server 2012 - Exam 5
Questions in this quiz (40)
1Your network contains AD named contoso.com. The domain contains RADIUS server named Server1 that runs Windows Server 2012. You add a VPN server named Server2 to the network. On Server1, you created several network policies. You need to configure Server1 to accept authentication requests from Server2. Which tool should you use on Server1?
- ASet-RemoteAccessRadius
- BCMAK
- CNPS
- DRouting and Remote Access
2How to configure IIS to accept the authentication kerberos or ntlm?
- Acscript adsutil.vbs set w3svc/Website/root/NTAuthenticationProviders "Negotiate,NTLM"
- Bcscript adsutil.vbs set w3svc/Website/root/NTAuthenticationProviders "NTLM"
- Ccscript adsutil.vbs set w3svc/Website/root/NTAuthenticationProviders "Negotiate
3You have a server that runs Windows Server 2012. You have an offline image named Windows2012.vhd that contains an installation of Windows Server 2012. You plan to apply several updates to Windows2012.vhd. You need to mount Windows2012.vhd to H:\. Which tool should you use?
- ADevice Manager
- BDiskpart
- CMountvol
- DServer Manager
4Your network contains an Active Directory domain named contoso.com. The domain contains client computers that run either Windows XP, Windows 7, or Windows 8. Network Policy Server (NPS) is deployed to the domain. You plan to create a system health validator (SHV). You need to identify which policy settings can be applied to all of the computers. Which three policy settings should you identify? (Each correct answer presents part of the solution. Choose three.)
- AA firewall is enabled for all network connections
- BAn antispyware application is on
- CAutomatic updating is enabled
- DAntivirus is up to date
- EAntispyware is up to date
5Your network contains an Active Directory domain named contoso.com. The domain contains a RADIUS server named Server1 that runs Windows Server 2012. You add a VPN server named Server2 to the network. On Server1, you create several network policies. You need to configure Server1 to accept authentication requests from Server2. Which tool should you use on Server1?
- AAdd-RemoteAccessRadius
- BNew-NPSRadiusClient
- CRemote Access Management Console
- DRouting and Remote Access
6Your network contains an Active Directory forest named contoso.com. The forest contains a single domain. All domain controllers run Windows Server 2012. The domain contains two domain controllers. DC1 is a physical server and has a daily task to snapshot Active Directory. DC2 is a Hyper-V virtual machine that has a daily task to snapshot of the VM and daily systemstate backups. You discover that a support technician accidentally removed 100 users from an Active Directory group named Group1 an hour ago. You need to restore the membership of Group1. What should you do?
- AApply a virtual machine snapshot to VM1
- BPerform an authorative restore
- CPerform a non-authorative restore
- DPerform tombstone reanimation
7Your network contains an Active Directory domain named contoso.com. All domain controllers run Windows Server 2012. The domain contains two organizational units (OUs) named OU1 and OU2 in the root of the domain. Two Group Policy objects (GPOs) named GPO1 and GP02 are created. GPO1 is linked to OU1. GPO2 is linked to OU2. OU1 contains a client computer named Computer1. OU2 contains a user named User1. You need to ensure that the GPOs applied to Computer1 are applied to User1 when User1 logs on. What should you configure?
- ABlock Inheritance
- BGroup Policy loopback processing mode
- CItem-level targeting
- DWMI Filtering
8Your network contains an Active Directory domain named contoso.com. The domain contains a domain controller named DC1 that runs Windows Server 2012. You mount an Active Directory snapshot on DC1. You need to expose the snapshot as an LDAP server. Which tool should you use?
- Aadsi edit
- Bntdsutil
- Cdsamain
- Dldp
9You have a server named Server1 that has a Server Core Installation on Windows Server 2012. You need to view the time-to-live (TTL) value of a host name that is cached on Server1. What should you run?
- Adnscacheugc.exe
- Bipconfig.exe /displaydns
- Cnslookup.exe
- DShow-DNSServerCache
10The contoso.com domain contains a a DNS server named Server1 that host a primary zone. Server2 contains a a secondary zone for the contoso.com domain You need to configure how long Server2 queries Server1 to renew the zone. What should you configure?
- ARetry interval
- BMinimum TTL
- CRefresh Interval
- DAuthority Record
11You are a network administrator of an Active Directory domain named contoso.com. You have a server named Server1 that runs Windows Server 2012. Server1 has the DHCP Server server role and the Network Policy Server role service installed. You enable Network Access Protection (NAP) on all of the DHCP scopes on Server1. You need to create a DHCP policy that will apply to all of the NAP non-compliant DHCP clients. Which criteria should you specify when you create the DHCP policy?
- AThe relay agent information
- BThe user class
- CThe vendor class
- DThe client identifier
12Your network contains an Active Directory domain named adatum.com. The domain contains a server named Server1 that runs Windows Server 2012. Server1 is configured as a Network Policy Server (NPS) server and as a DHCP server. The network contains two subnets named Subnet1 and Subnet2. Server1 has a DHCP scope for each subnet. You need to ensure that noncompliant computers on Subnet1 receive different network policies than noncompliant computers on Subnet2. Which two settings should you configure? (Each correct answer presents part of the solution. Choose two.)
- AThe NAP-Capable Computers conditions
- BThe NAS Port Type constraints
- CThe Health Policies conditions
- DThe MS-Service Class conditions
- EThe Called Station ID constraints
13Your network contains an Active Directory forest. The forest contains two domains named contoso.com and fabrikam.com. All of the DNS servers in both of the domains run Windows Server 2012. The network contains two servers named Server1 and Server2. Server1 hosts an Active Directory-integrated zone for contoso.com. Server2 hosts an Active Directory-integrated zone for fabrikam.com. Server1 and Server2 connect to each other by using a WAN link. Client computers that connect to Server1 for name resolution cannot resolve names in fabrikam.com. You need to configure Server1 to resolve names in fabrikam.com. The solution must NOT require that changes be made to the fabrikam.com zone on Server2. What should you create?
- AA secondary zone
- BA stub zone
- CA trust anchor
- DA zone delegation
14Your network contains an Active Directory domain named contoso.com. All domain controllers run Windows Server 2012. One of the domain controllers is named DC1. The DNS zone for the contoso.com zone is Active Directory-integrated and has the default settings. A server named Server1 is a DNS server that runs a UNIX-based operating system. You plan to use Server1 as a secondary DNS server for the contoso.com zone. You need to ensure that Server1 can host a secondary copy of the contoso.com zone. What should you do?
- AFrom Windows PowerShell, run the Set-DNSServerForwarder cmdlet and specify the contoso.com zone as a target.
- BFrom Windows PowerShell, run the Set-DNSServerSetting cmdlet and specify DC1 as the target
- CFrom Windows PowerShell, run the Set-DNSServerPrimaryZone cmdlet and specify the contoso.com zone as a target.
- DFrom DNS Manager, modify the Advanced settings of DC1
15Your network contains an Active Directory domain named contoso.com. All domain controllers run Windows Server 2012. An organizational unit (OU) named OU1 contains 200 client computers that run Windows 8 Enterprise. A Group Policy object (GPO) named GPO1 is linked to OU1. You make a change to GPO1. You need to force all of the computers in OU1 to refresh their Group Policy settings immediately. The solution must minimize administrative effort. Which tool should you use?
- ASecedit command
- BSet-ADComputer cmdlet
- CActive Directory Users and Computers
- DInvoke-GPUpdate cmdlet
16Your network contains an Active Directory domain named adatum.com. You have a standard primary zone named adatum.com. You need to provide a user named User1 the ability to modify records in the zone. Other users must be prevented from modifying records in the zone. What should you do first?
- AFrom the properties of the zone, modify the start of authority (SOA) record
- BRun the Zone Signing Wizard for the zone
- CRun the New Delegation Wizard for the zone
- DFrom the properties of the zone, change the zone type
17Your network contains two Active Directory domains named contoso.com and adatum.com. The contoso.com domain contains a server named Server1.contoso.com. The adatum.com domain contains a server named server2.adatum.com. Server1 and Server2 run Windows Server 2012 and have the DirectAccess and VPN (RRAS) role service installed. Server1 has the default network policies and the default connection request policies. You need to configure Server1 to perform authentication and authorization of VPN connection requests to Server2. Only users who are members of Adatum\Group1 must be allowed to connect. Which two actions should you perform on Server1? (Each correct answer presents part of the solution. Choose two.)
- ANetwork policies
- BConnection request policies
- CCreate a network policy
- DCreate a connection request policy
18Your network contains an Active Directory domain named contoso.com. The domain contains a server named Server1 that runs Windows Server 2012. Server1 has the following role services installed: DirectAccess and VPN (RRAS) Network Policy Server Remote users have client computers that run either Windows XP, Windows 7, or Windows 8. You need to ensure that only the client computers that run Windows 7 or Windows 8 can establish VPN connections to Server1. What should you configure on Server1?
- AA vendor-specific RADIUS attribute of a Network Policy Server (NPS) connection request policy
- BA condition of a Network Policy Server (NPS) network policy
- CA condition of a network Policy Server (NPS) connection request policy
- DA constraint of a Network Policy Server (NPS) network policy
19Your network contains an Active Directory domain named contoso.com. The domain contains a server named Server1 that runs Windows Server 2012. Server1 has a drive named E that is encrypted by using BitLocker Drive Encryption (BitLocker). A recovery key is stored on drive C. Drive E becomes locked. When you attempt to use the recovery key, you receive the following error message. You need to access the data stored on drive E. What should you run first?
- Amanage-bde -protectors get e:
- Bmanage-bde -unlock e: -recoverykey C:\
- Cdisable-bitlocker -mountpoint E:
- Dunlock-bitlocker -mountpoint e: -recoverykeypath C:
20Your network contains an Active Directory domain named contoso.com. All user accounts reside in an organizational unit (OU) named OU1. You create a Group Policy object (GPO) named GPO1. You link GPO1 to OU1. You configure the Group Policy preference of GPO1 to add a shortcut named Link1 to the desktop of each user. You discover that when a user deletes Link1, the shortcut is removed permanently from the desktop. You need to ensure that if a user deletes Link1, the shortcut is added to the desktop again. What should you do?
- AModify the Link1 shortcut preference of GPO1
- BEnable loopback processing of GPO1
- CEnforce GPO1
- DModify the Security Filtering settings of GPO1
21Your network contains an Active Directory forest named contoso.com. The forest contains two sites named Main and Branch. The Main site contains 400 desktop computers and the Branch site contains 150 desktop computers. All of the desktop computers run Windows 8. In Main, the network contains a member server named Server1 that runs Windows Server 2012. You install the Windows Server Update Services server role on Server1. You need to ensure that Windows updates obtained from Windows Server Update Services (WSUS) are the same for the computers in each site. You want to achieve this goal by using the minimum amount of administrative effort. What should you do?
- AFrom the Update Services console, create computer groups
- BFrom the Update Services console, configure the Computers options
- CFrom the Group Policy Management console, configure the Windows Update Settings
- DFrom the Group Policy Management console, configure the Windows Anytime Upgrade settings
- EFrom the Update Services console, configure the Synchronization Schedule options
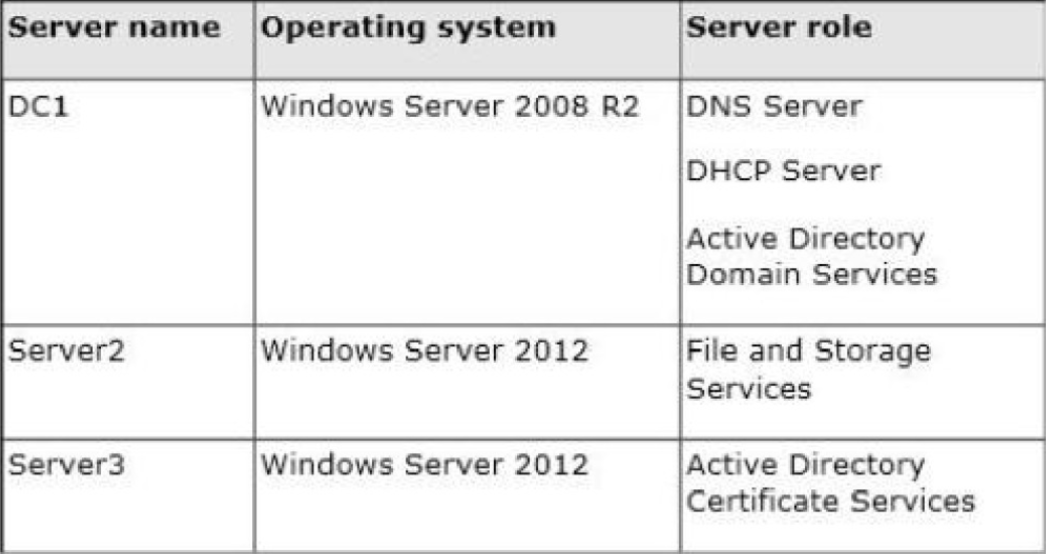
22Your network contains an Active Directory forest named contoso.com. The domain contains three servers. The servers are configured as shown in the following table. You plan to implement the BitLocker Drive Encryption (BitLocker) Network Unlock feature. You need to identify which server role must be deployed to the network to support the planned implementation. Which role should you identify?
- ANetwork Policy and Access Services
- BVolume Activation Services
- CActive Directory Rights Management Services
- DWindows Deployment Services
23Your network contains an Active Directory domain named contoso.com. The domain contains a server named Print1. Your company implements DirectAccess. A user named User1 frequently works at a customer's office. The customer's office contains a print server named Print1. While working at the customer's office, User1 attempts to connect to Print1. User1 connects to the Print1 server in contoso.com instead of the Print1 server at the customer's office. You need to provide User1 with the ability to connect to the Print1 server in the customer's office. Which Group Policy option should you configure?
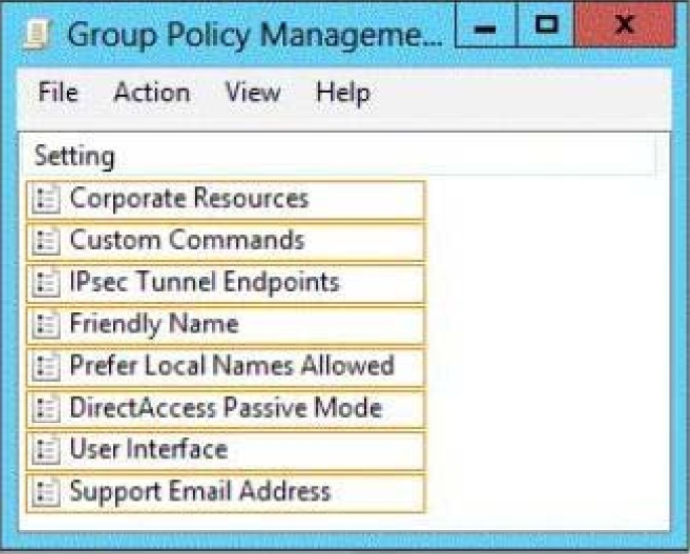
- ACorporate Resources
- BCustom Commands
- CIPsec Tunnel Endpoints
- DFriendly Name
- EPrefer Local Names Allowed
- FDirect Access Passive Mode
- GUser Interface
- HSupport Email Address
24Your network contains an Active Directory domain named contoso.com. All domain controllers run Windows Server 2012. In a remote site, a support technician installs a server named DC10 that runs Windows Server 2012. DC10 is currently a member of a workgroup. You plan to promote DC10 to a read-only domain controller (RODC). You need to ensure that a user named Contoso\User1 can promote DC10 to a RODC in the contoso.com domain. The solution must minimize the number of permissions assigned to User1. What should you do?
- AFrom ntdsutil, run the local roles command
- BFrom Active Directory Users and Computers, pre-create a RODC computer account
- CFrom Active Directory User and Computers, run the Delegation of Control Wizard on the contoso.com domain object
- DJoin DC10 to the domain, Modify the properties of the DC10 computer account.
25Your network contains an Active Directory forest named contoso.com. The forest contains two domains named contoso.com and childl.contoso.com. All domain controllers run Windows Server 2012. The domain contains four domain controllers. The domain controllers are configured as shown . You open Active Directory Users and Computers on a client computer and connect to DC1. You display the members of a group named Group1 as shown. When you view the properties of a user named User102, you receive the error message shown. The error message does not display for any other members of Group1. You need to identify which domain controller causes the issue shown in the error message. Which domain controller should you identify?
- ADC1
- BDC2
- CDC10
- DDC11
26Your network contains an Active Directory domain named contoso.com. All servers run Windows Server 2012. The domain contains a file server named Server1. All client computers run Windows 8. Users share the client computers and frequently log on to different client computers. You need to ensure that when the users save files in the Documents folder, the files are saved automatically to \\Server1\Users\. The solution must minimize the amount of network traffic that occurs when the users log on to the client computers. What should you do?
- AFrom a Group Policy object (GPO), configure the Folder Redirection settings
- BFrom the properties of each user account, configure the Home folder settings
- CFrom the properties of each user account, configure the User profile settings
- DFrom a Group Policy object (GPO), configure the Drive Maps preference
27You have a server named Server1 that runs Windows Server 2012. Server1 has two network adapters and is located in a perimeter network. You need to configure Server1 as a network address translation (NAT) server. Which node should you use to add the NAT routing protocol?
- ARemote Access Clients
- BPorts
- CRemote Access Logging & Policies
- DIPv4 - General
- EIPv4 - Static Routes
- FIPv4 - RIP
- GIPv4 - IGMP
- HIPv4 - DHCP Relay Agents
- IIPv6 - General
- JIPv6 - Static Routes
28You have a server named Server5 that runs Windows Server 2012. Servers has the Windows Deployment Services server role installed. You need to ensure that when client computers connect to Server5 by using PXE, the computers use an unattended file. What should you configure?
- AGeneral
- BPXE Response
- CAD DS
- DBoot
- EClient
- FDHCP
- GMulticast
- HAdvanced
- INetwork
- JTFTP
29Your network contains a server named Server1 that has the Network Policy and Access Services server role installed. All of the network access servers forward connection requests to Server1. You create a new network policy on Server1. You need to ensure that the new policy applies only to connection requests from Microsoft RAS servers that are located on the 192.168.0.0/24 subnet.
- ASet the Called Station ID constraint to 192.168.0.0.24
- BSet the Called Station ID constraint to 192.168.0
- CSet the Client IPv4 Address condition to 192.168.0.0/24
- DSet the Client IPv4 Address condition to 192.168.0
30Your network contains an Active Directory domain named contoso.com. The domain contains a server named Server1. Server1 is configured as a VPN server. You need to configure Server1 to perform network address translation (NAT). What should you do?
- AFrom Network Connections, modify the Internet Protocol Version 6 (TCP/IP v6) settings of each network adapter
- BFrom Routing and Remote Access, add an IPv4 routing protocol
- CFrom Routing and Remote Access, add an IPv6 routing protocol
- DFrom Network Connections, modify the Internet Protocol Version 4 (TCP/IP v4) settings of each network adapter
31Your network contains an Active Directory domain named contoso.com. The domain contains a server named Server1 that has the Remote Access server role installed. DirectAccess is implemented on Server1 by using the default configuration. You discover that DirectAccess clients do not use DirectAccess when accessing websites on the Internet. You need to ensure that DirectAccess clients access all Internet websites by using their DirectAccess connection. What should you do?
- ADisable the DirectAccess Passive Mode setting in the Direct Access Client Settings Group Policy object (GPO)
- BConfigure a DNS suffix search list on the DirectAccess clients
- CEnable the Route all Traffic through the internal network policy settings in the DirectAccess Server Settinvs Group Policy object (GPO)
- DConfigure DirectAccess to enable force tunneling
32You have a DNS server named Server1 that runs Windows Server 2012. On Server1, you create a DNS zone named contoso.com. You need to specify the email address of the person responsible for the zone. Which type of DNS record should you configure?
- AStart of authority (SOA)
- BMail exchanger (MX)
- CHost information (HINFO)
- DMailbox (MB)
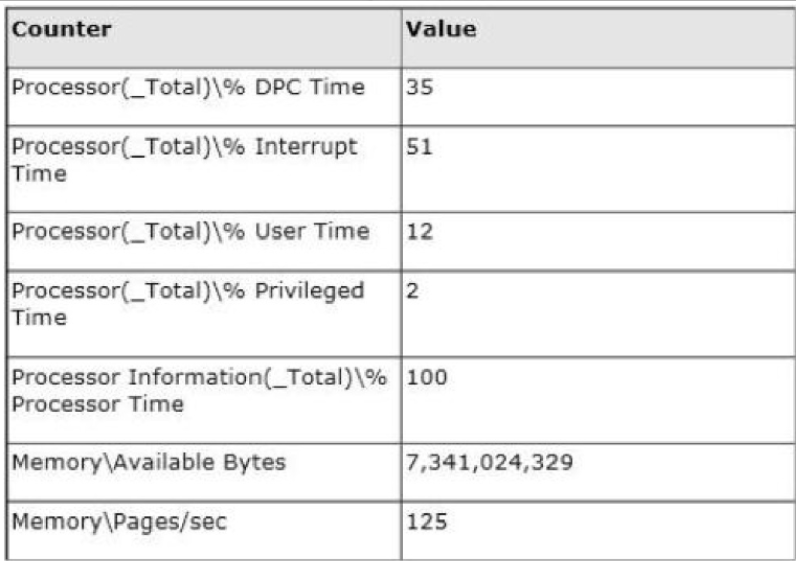
33You have a server named Server1 that runs Windows Server 2012. You discover that the performance of Server1 is poor. The results of a performance report generated on Server1 are shown in the table. You need to identify the cause of the performance issue. What should you identify?
- AExcessive paging
- BNUMA Fragmentation
- CDrive malfunction
- DInsufficient RAM
34Your network contains an Active Directory domain named contoso.com. All servers run Windows Server 2012. An organizational unit (OU) named ResearchServers contains the computer accounts of all research servers. All domain users are configured to have a minimum password length of eight characters. You need to ensure that the minimum password length of the local user accounts on the research servers in the ResearchServers OU is 10 characters. What should you do?
- ACreate a universal group that contains the research servers. Create a Password Settings Object (PSO) and assign the PSO to the group.
- BConfigure a local Group Policy Object (GPO) on each research server.
- CCreate and link a Group Policy object (GPO) to the ResearchServers OU.
- DCreate a global group that contains the research servers. Create a Password Settings object (PSO) and assign the PSO to the group.
35Your network contains an Active Directory domain named contoso.com. The domain contains a server named Server1 that runs Windows Server 2012. Server1 has the Windows Server Update Services server role installed. All client computers are configured to download updates from Server1. You have a Group Policy object (GPO) named GPO1 that is linked to an organizational unit (OU) named Sales_OU. You need to ensure that all of the computers in Sales_OU are added to a Windows Server Update Services (WSUS) computer group named SalesComputers. Which setting should you configure in the GPO?
- AAllow non-administrators to receive update notifications
- BTurn on Software Notifications
- CLet the service shut down when it is idle
- DAllow Automatic Updates immediate installation
- ETurn on recommended updates via Automatic Updates
- FNo auto-restart with logged on users for scheduled automatic updates installations
- GRe-prompt for restart with scheduled installations
- HRescheduled Automatic Updates scheduled installations
- IEnable client-side targeting
- JAllow signed updates from an intranet Microsoft update service location
36Your network contains an Active Directory domain named contoso.com. All domain controllers run Windows Server 2012. The domain contains an Edge Server named Server1. Server1 is configured as a DirectAccess server. Server1 has the following settings:
Internal DNS name: Server1.contoso.com
External DNS name: da1.contoso.com
Internal IPv6 address: 2002:c1a8:6a:3333::1
External IPv4 address: 65.55.37.62
Your company uses split-brain DNS for the contoso.com zone. You run the Remote Access Setup wizard as shown. You need to ensure that client computers on the Internet can establish DirectAccess connections to Server1.
Which additional name suffix entry should you add from the Remote Access Setup wizard?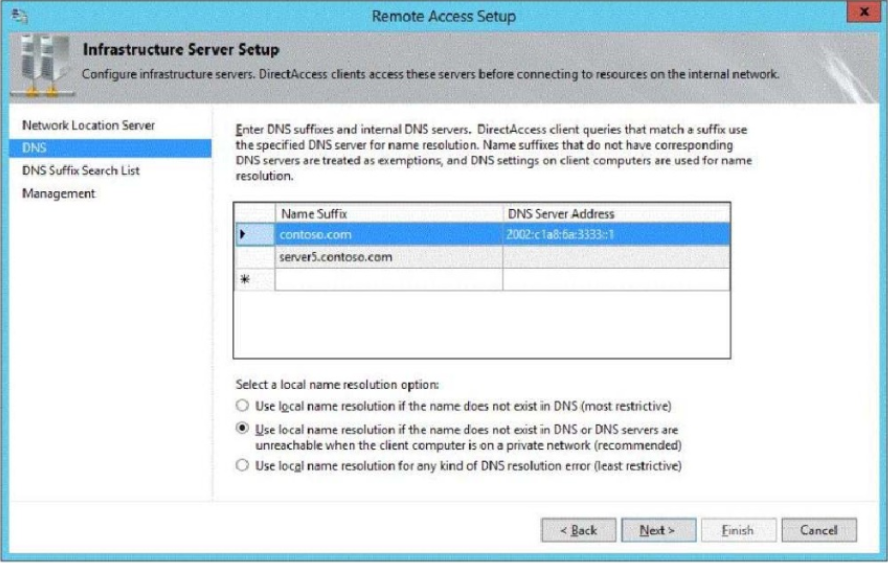
- AA Name Suffix value of da1.contoso.com and a blank DNS Server Address value
- BA Name Suffix value of Server1.contoso.com and a DNS Server Address value of 65.55.37.62
- CA Name Suffix value of Server1.contoso.com and a blank DNS Server Address value
- DA Name Suffix value of da1.contoso.com and a DNS Server Address value of 65.55.37.62
37Your network contains an Active Directory domain named contoso.com. All servers run Windows Server 2012. Client computers run either Windows 7 or Windows 8. All of the client computers have an application named App1 installed. The domain contains a Group Policy object (GPO) named GPO1 that is applied to all of the client computers. You need to add a system variable named App1Data to all of the client computers. Which Group Policy preference should you configure?
- AServices
- BIni Files
- CEnvironment
- DData Sources
38Your network contains an Active Directory forest named contoso.com. The forest contains a single domain. The forest contains two Active Directory sites named Site1 and Site2. You plan to deploy a read-only domain controller (RODC) named DC10 to Site2. You pre-create the DC10 domain controller account by using Active Directory Users and Computers. You need to identify which domain controller will be used for initial replication during the promotion of the RODC. Which tab should you use to identify the domain controller?
- AGeneral
- BOperating System
- CMember Of
- DDelegation
- EPassword Replication Policy
- FLocation
- GManaged By
- HObject
- ISecurity
- JDial-In
39Your network contains an Active Directory forest named contoso.com. Recently, all of the domain controllers that ran Windows Server 2003 were replaced by domain controllers that run Windows Server 2012. From Event Viewer, you discover SYSVOL journal wrap errors on a domain controller named dc10.contoso.com. You need to perform a non-authoritative synchronization of SYSVOL on DC10. Which three actions should you perform on DC10?
- AStart the Distributed File System (DFS) Replication service
- BStop the Distributed File System (DFS) Replication service
- CModify the registry
- DStop the File Replication Service (FRS) service
- EModify the computer object for DC10 in Active Directory
- FStart the File Replication Service (FRS) service
40You manage a server that runs Windows Server 2012. The server has the Windows Deployment Services server role installed. You start a virtual machine named VM1 as shown in the exhibit. (Click the Exhibit button.) You need to configure a pre-staged device for VM1 in the Windows Deployment Services console. Which two values should you assign to the device ID? (Each correct answer presents a complete solution. Choose two.)
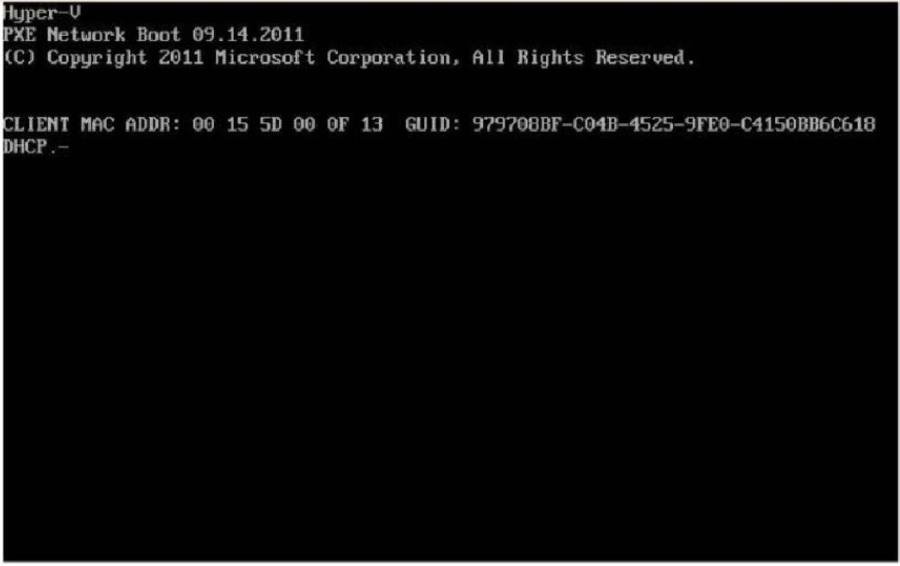
- A979708BFC04B45259FE0C4150BB6C618
- B979708BF-C04B-4525-9FE0-C4150BB6C618
- C00155D000F1300000000000000000000
- D000000000000000000000155D000F13
- E00000000-0000-0000-0000-C4150BB6C618
Information
- Description
- This exam measures your ability to accomplish the technical tasks listed below: Deploy, Manage, and Maintain Servers Configure File and Print Services Configure Network Services and Access Configure a Network Policy Server Infrastructure Configure and Manage Active Directory Configure and Manage Group Policy
- Author
- Mike M
- Language
- English
- Views
- 167
- Tags
- Rating
- No ratings yet Rate this quiz