
Mapa mental
CyberSecurity
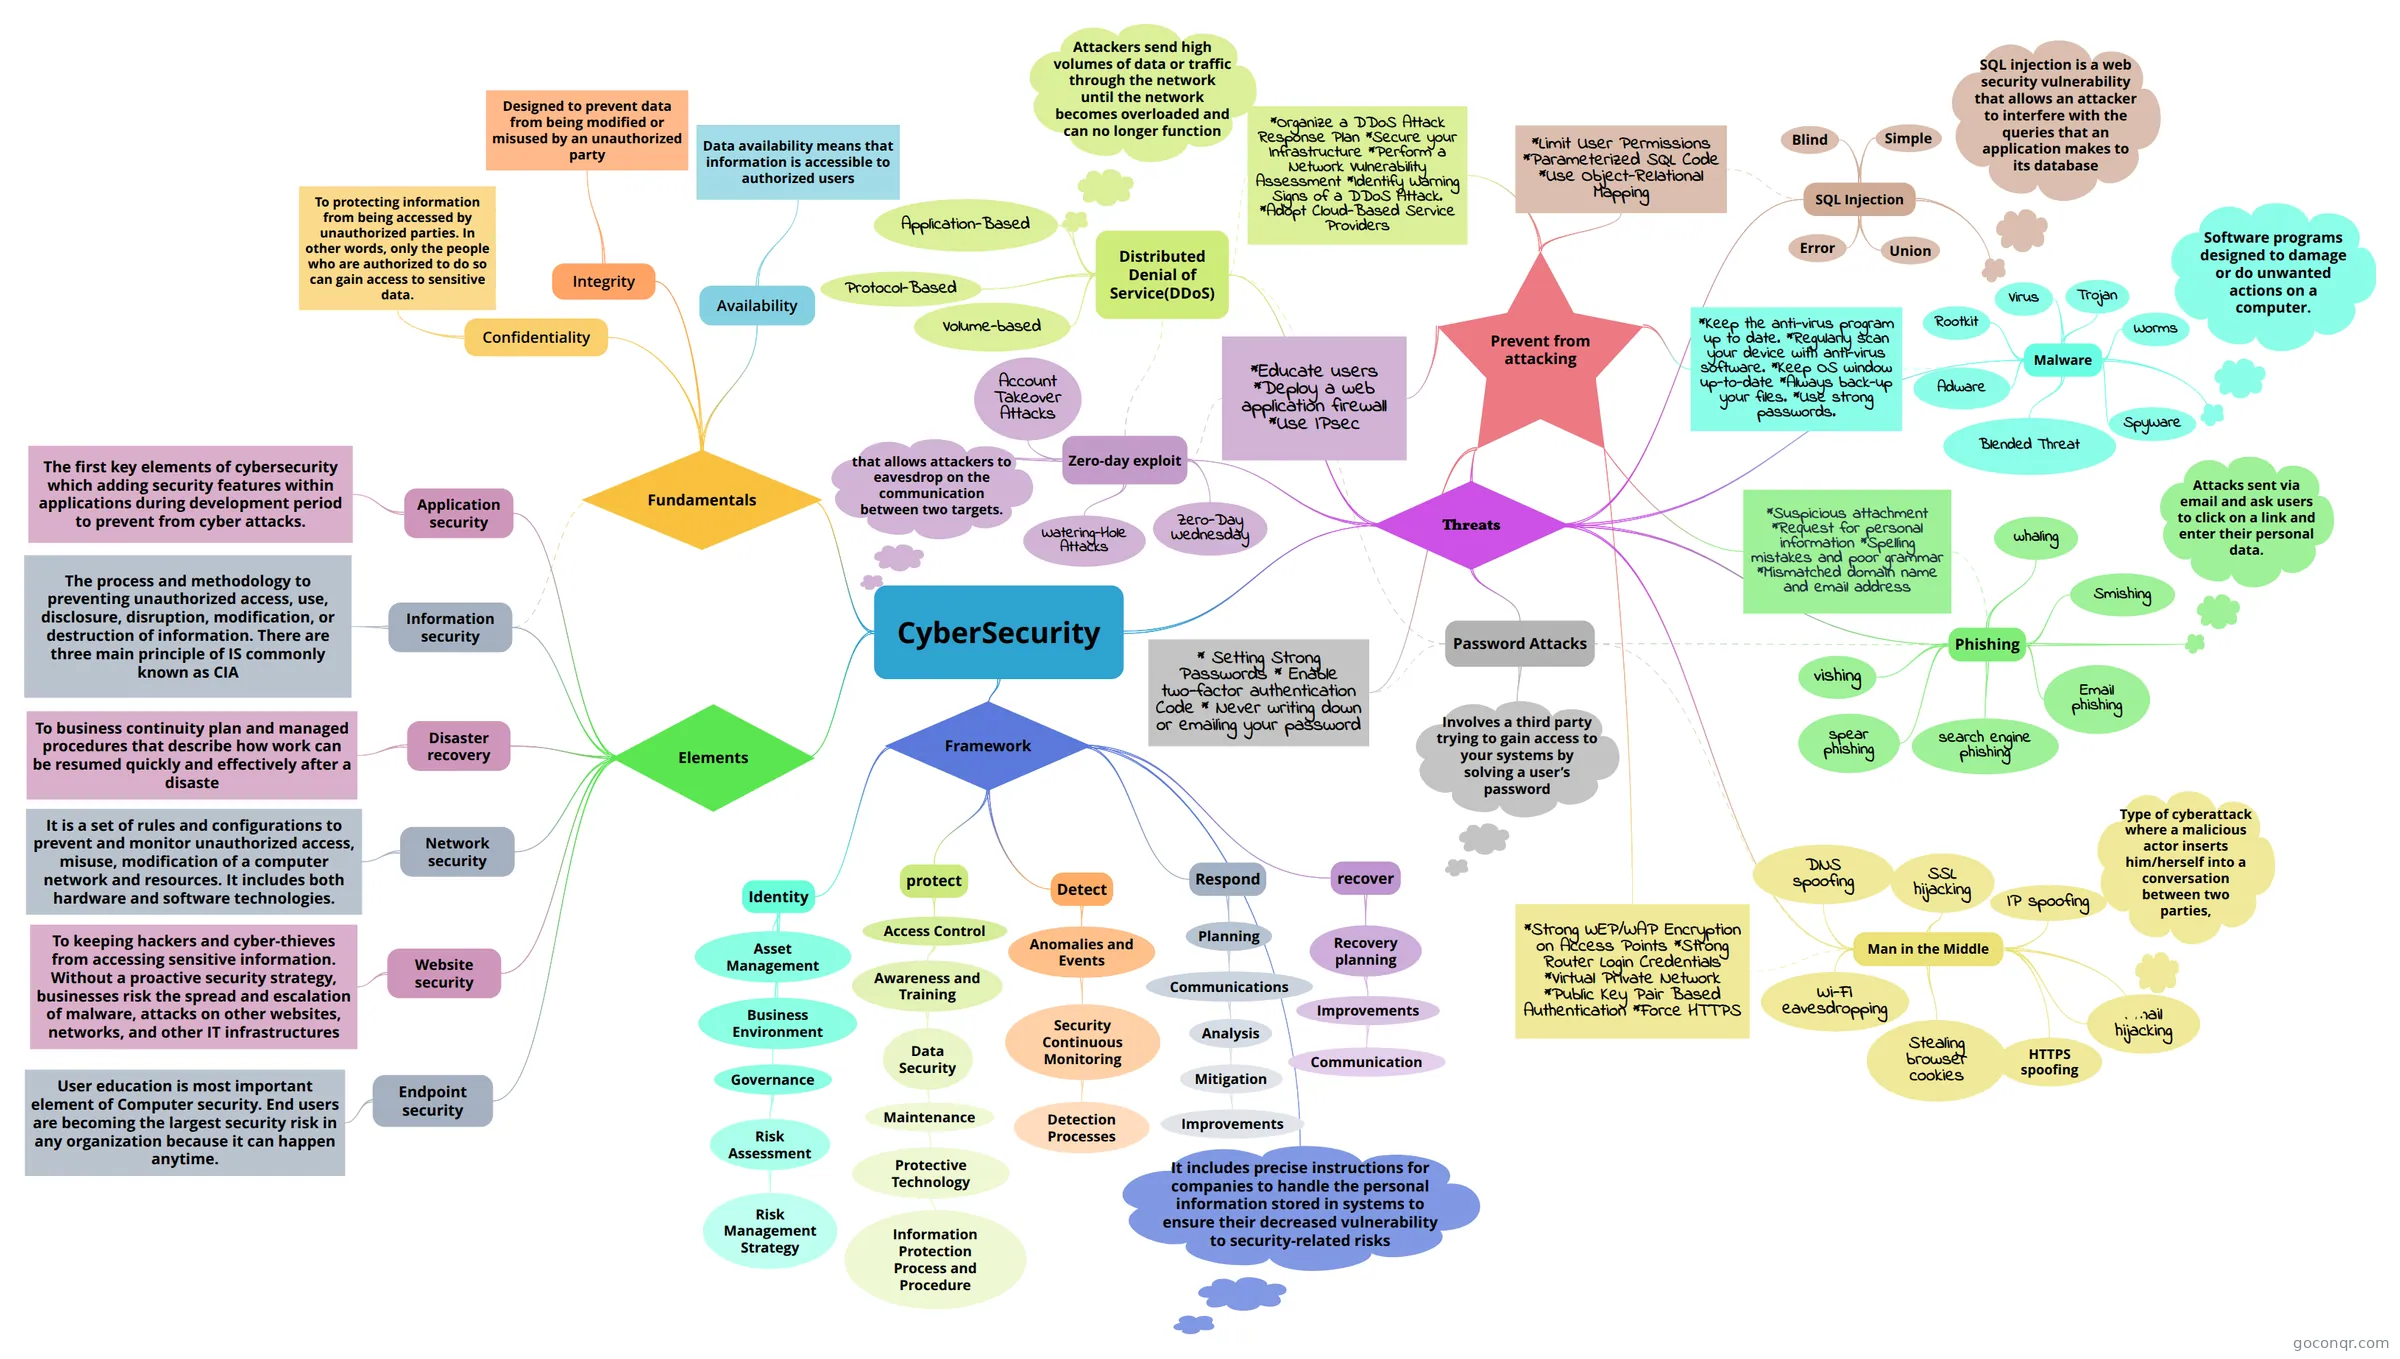
Mind map: Cybersecurity
Contenido del mapa
CyberSecurity
Elements
- Information security
- The process and methodology to preventing unauthorized access, use, disclosure, disruption, modification, or destruction of information. There are three main principle of IS commonly known as CIA
- Application security
- The first key elements of cybersecurity which adding security features within applications during development period to prevent from cyber attacks.
- Disaster recovery
- To business continuity plan and managed procedures that describe how work can be resumed quickly and effectively after a disaste
- Network security
- It is a set of rules and configurations to prevent and monitor unauthorized access, misuse, modification of a computer network and resources. It includes both hardware and software technologies.
- Website security
- To keeping hackers and cyber-thieves from accessing sensitive information. Without a proactive security strategy, businesses risk the spread and escalation of malware, attacks on other websites, networks, and other IT infrastructures
- Endpoint security
- User education is most important element of Computer security. End users are becoming the largest security risk in any organization because it can happen anytime.
- Information security
Fundamentals
- Confidentiality
- To protecting information from being accessed by unauthorized parties. In other words, only the people who are authorized to do so can gain access to sensitive data.
- Integrity
- Designed to prevent data from being modified or misused by an unauthorized party
- Availability
- Data availability means that information is accessible to authorized users
- Confidentiality
Threats
- Malware
- Virus
- Worms
- Trojan
- Rootkit
- SpyWare
- Blended Threat
- Adware
- Software programs designed to damage or do unwanted actions on a computer.
- Phishing
- spear phishing
- whaling
- Smishing
- vishing
- search engine phishing
- Email phishing
- Attacks sent via email and ask users to click on a link and enter their personal data.
- Password Attacks
- Involves a third party trying to gain access to your systems by solving a user’s password
- Distributed Denial of Service(DDoS)
- Volume-based
- Application-Based
- Protocol-Based
- Attackers send high volumes of data or traffic through the network until the network becomes overloaded and can no longer function
- Man in the Middle
- IP spoofing
- DNS spoofing
- HTTPS spoofing
- SSL hijacking
- Email hijacking
- Wi-Fi eavesdropping
- Stealing browser cookies
- Type of cyberattack where a malicious actor inserts him/herself into a conversation between two parties,
- Prevent from attacking
- *Suspicious attachment *Request for personal information *Spelling mistakes and poor grammar *Mismatched domain name and email address
- * Setting Strong Passwords * Enable two-factor authentication Code * Never writing down or emailing your password
- *Limit User Permissions *Parameterized SQL Code *Use Object-Relational Mapping
- *Strong WEP/WAP Encryption on Access Points *Strong Router Login Credentials *Virtual Private Network *Public Key Pair Based Authentication *Force HTTPS
- *Educate users *Deploy a web application firewall *Use IPsec
- *Organize a DDoS Attack Response Plan *Secure your Infrastructure *Perform a Network Vulnerability Assessment *Identify Warning Signs of a DDoS Attack. *Adopt Cloud-Based Service Providers
- *Keep the anti-virus program up to date. *Regularly scan your device with anti-virus software. *Keep OS window up-to-date *Always back-up your files. *Use strong passwords.
- SQL Injection
- Simple
- Blind
- Union
- Error
- SQL injection is a web security vulnerability that allows an attacker to interfere with the queries that an application makes to its database
- Zero-day exploit
- Account Takeover Attacks
- Watering-Hole Attacks
- Zero-Day Wednesday
- that allows attackers to eavesdrop on the communication between two targets.
- Malware
Framework
- Identity
- Asset Management
- Business Environment
- Governance
- Risk Assessment
- Risk Management Strategy
- Risk Assessment
- protect
- Access Control
- Awareness and Training
- Data Security
- Maintenance
- Protective Technology
- Information Protection Process and Procedure
- Protective Technology
- Maintenance
- Data Security
- Awareness and Training
- Access Control
- Detect
- Anomalies and Events
- Security Continuous Monitoring
- Detection Processes
- Security Continuous Monitoring
- Anomalies and Events
- Respond
- Planning
- Communications
- Analysis
- Mitigation
- Improvements
- Mitigation
- Analysis
- Communications
- Planning
- recover
- Recovery planning
- Improvements
- Communication
- Improvements
- Recovery planning
- It includes precise instructions for companies to handle the personal information stored in systems to ensure their decreased vulnerability to security-related risks
- Identity
Información
- Descripción
- Mapa Mental sobre CyberSecurity, creado por Test Training el 04/02/2021.
- Creado por
- Test Training
- Visitas
- 1
- Valoración