
Flashcards
IT security
Flashcards do conjunto (27)
- 1What are the qualities used to define and analyse SecurityConfidentiality - ensuring info is only disclosed to auth'd parties with a need to know
Integrity - Info is consistent and accurate
Availability - Info is ready for use when and where it's needed to fulfil its purpose - 2Why is system security a critical concern?Systems are responsibile for important data and processing
- 3Examples of well known events with major security impactEnigma Machine - WW2 Alan Turing
Edward Snowden
Digital Footprint debates (Google, Twitter, Facebook)
MOD Docs left on the tube - 4What's the issue related to system security?Misuse of system leads to negative outcomes for anyone associated with it
customers
partners
customer's customers
Everyone's reputation - 5Do security standards exist?Dumb question bitch
There's a bewildering array of security standards and regulations
ISO27000
Data Protection Act 1998
SANS Top 20
PCI Security Standards Council - 6What's the scale of the risk?It depends on the nature of the system's purpose and the nature of the organisation the system will operate in
- 7Scales of Security RiskMilitary Systems - identify friend or foe (false ID) nuclear command and control
High Value Financial Systems - BACS, SWIFT DOS/money siphoning
Retail Banking - ATMS: fraud, expose data
Web Browsing: Emails: virus attack data corruption, identity theft - 8What are the impacts to organisations of security exposures?1. Data Theft & Fraud
bottom line/trade secret loss
2. Loss of Trust/Reputation/Data
how people gonna trust you if you can't look after their data
3. Disruption to operations
is biz gone live?
4. Cost of enforcing security
audit & security implement > 50% system cost - 9What type of attacks are the worst?Insider attacks
17% of all qualified security attacks 2013 were because of internal employees deliberately targeting their organisation
THAT'S ALMOST 1/5 - 10What is a good general approach to security?A THREAT BASED ONE
dipshit
Document Assets you wanna protect
Understand threats and vulnerabilities
Design Security Policy
Implement Policy
Monitor n Maintain Policy
all appropriate to level of risk - 11What types of sensitive data are there?DATA: customer info, large DBs, financial info, capital intell, business plans
PROCESSES: one with purchasing power, command control power, containment/SM policy
TANGIBLE: bandwidth, hardware, hardcopy data
INTANGIBLE: reputation, trust, confidence - 12Where do threats arise from in an IT system?MALICIOUS
third party for money/other gain
competitor/party of their behalf
hacker seeking kudos
corrupt insider inflicting damage
UNWITTING
accidental damage to asset
accidental sharing of info
system error - 13What can these threats do to our systems?Observe/capture/forward confidential data
Alter data/outcomes - website defacement
Delete data
Initiate unauth'd processes
Prevent auth'd processes
DOS
Reduce Security
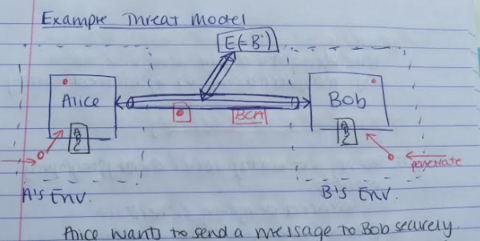
Steal Assets - 14Where do the threats arise in this image:Observe A
Takeover A
Read message in transmission
Corrupt message
Redirect message
Imitate party E(=B)
Takeover B
Observe B - 15What well know attack types/terms are there?Denial of Service
attack on the systems network prevent auth'd user access
typically consume bandwidth or
overload computational resources - 16What well know attack types/terms are there?Malware
Malicious code
spyware, adware, viruses, worms
made common by internet and windows OS - 17What well know attack types/terms are there?Phishing
Masquerading as a known entity in an attempt to acquire sensitive data - 18How do we fight back with IT security?By using cryptography
we protect communications between A and B by encrypting the content of the messages
a system of establishing and sharing encryption keys is required
(enigma alan turing bletchley) - 19Different forms of encryptionThere are many different forms with different levels of protection
Two Basic Types are:
Symmetrical - same key for encrypting and decrypting - cheaper
Assymetrical - different keys for encripting and decrypting - computationally expensive - 20what do cryptographic principles allow us to do?Build protocols and architectures (PKI) which allow us to achieve secuirty objectives
- 21What are the key security engineering objectives?Authorisation
Authentication
Confidentiality
Integrity
Auditable
Non-repudiation - 22Security Architect role and method1. Ensure security is appropriately positioned in project set up
2. Develop a comprehensive view of security
3. Provide traceability in the solution - doc everythang
4. Include explicity security testing in test plans and strategy - 23From the security perspective, what three things do solutions need to balanceCost
Risk
Usability
solution should be "necessary and sufficient" as far as possible - 24what else does the security architect do?oversees the progression across phases in the prokect life cycle across all domains of the system
- 25What work product is key for the security architec?Systems Context Diagram
Identifies all the users of the system, where they are and the tech they use
where information has to flow to and from
what types of access have to be controlled (other users and systems) - 26What else does a security architect have to remember to do?Identify the industry standards that influence the system and constrain how it operates
RBAC
Protective Monitoring
End Point Hardening
Security Awareness Training - 27—
Informações
- Descrição
- Second year MITSA (Security ) FlashCards sobre IT security , criado por Alex Millar em 17-05-2016.
- Criado por
- Alex Millar
- Visualizações
- 0
- Avaliação