
Notizen
PKI - created from Mind Map
Inhalt der Notizen (1)
Seite 1
X.509
CA
CA sign the Digital certificate
RA
VA
Use Cases
Algorithms
Certificate Encode
Certificate Extension Name
`openssl` command
Digital Certificate? or Public Key Certificate
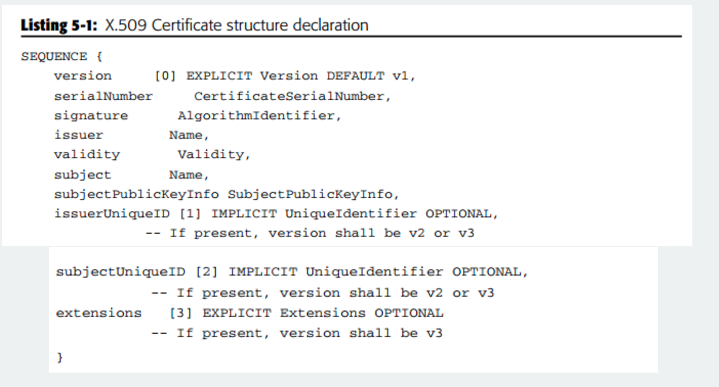
Structure
PEM:Privacy Enhanced Mail
DER:Distinguished Encoding Rules
CRT
PEM
CER
KEY
PFX/P12
JKS
CSR: Certificate Signing Requst
Generate self-sign certificate
Generate CSR
Display the Certificate Information
openssl req -newkey rsa:2048 -new -nodes -x509 -days 3650 -keyout key.pem -out cert.pem
openssl req -newkey rsa:2048 -new -nodes -keyout my.key -out my.csr
PEM
DER
openssl x509 -in certificate.pem -text -noout
openssl x509 -in certificate.der -inform der -text -noout
Public Key + Owner Information + Digital Signature Signed by CA
Abstract Syntax Notation (ASN): describe the structure
TOP level
ASN serves the same purpose as a DTD or an XSD might serve in an XML context
version
serialNumber
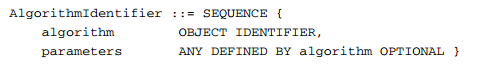
signature
issuer
validity
subject
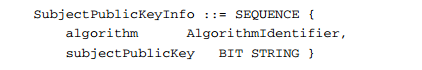
subjectPublicKeyInfo
issuerUniqueID
subjectUniqueID
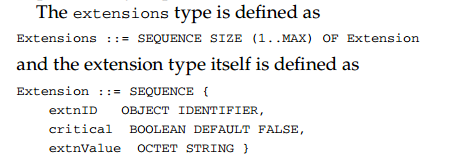
extensions
CA sign
Self-sign for test
object identifier (OID)
MD5withRSA: 1.2.840.113549.1.1.4 = 2A 86 48 86 F7 0D 01 01 04
SHA-1withRSA: 2A 86 48 86 F7 0D 01 01 05
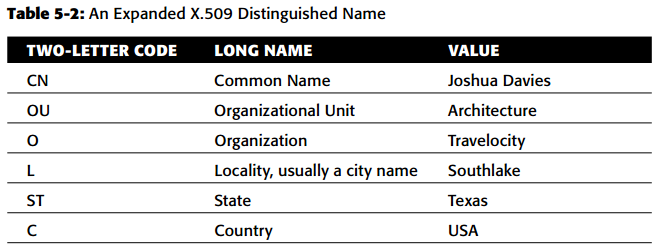
Distinguished Name
SSL(TLS)
SAML
Software Licence
PDF signature
SSH
private key cryptography
public key cryptography
Digest Algorithm
DES,Data Encryption Standard
AES, Advanced Encryption Standard (128,192, 256)
RC4
IDEA
RSA, Rivest, Shamir, Adleman: length>768 has not been cracked. So 1024 basic security and 2018 is more security
Digital Signature Algorithm, DSA, Only signature
Diffie-Hellman: Only for exchange key
ECC, Elliptic curve cryptography
SHA Secure Hash Algorithm
MD5 Message-Digest Algorithm 5
CRC Cyclic Redundancy Check
SHA-1 : 160-bit
SHA-2: SHA256: 256-bit

Informationen
- Beschreibung
- PKI
- Erstellt von
- Xin Meng · Apr 2017
- Aktualisiert
- 27 Apr 2017
- Aufrufe
- 0
- Verlauf
-
- Erstellt von Xin Meng · 27 Apr 2017
- Zu Notiz kopiert von Xin Meng · 27 Apr 2017
- Bewertung