
Mind map
4f - Security of Distributed Databases
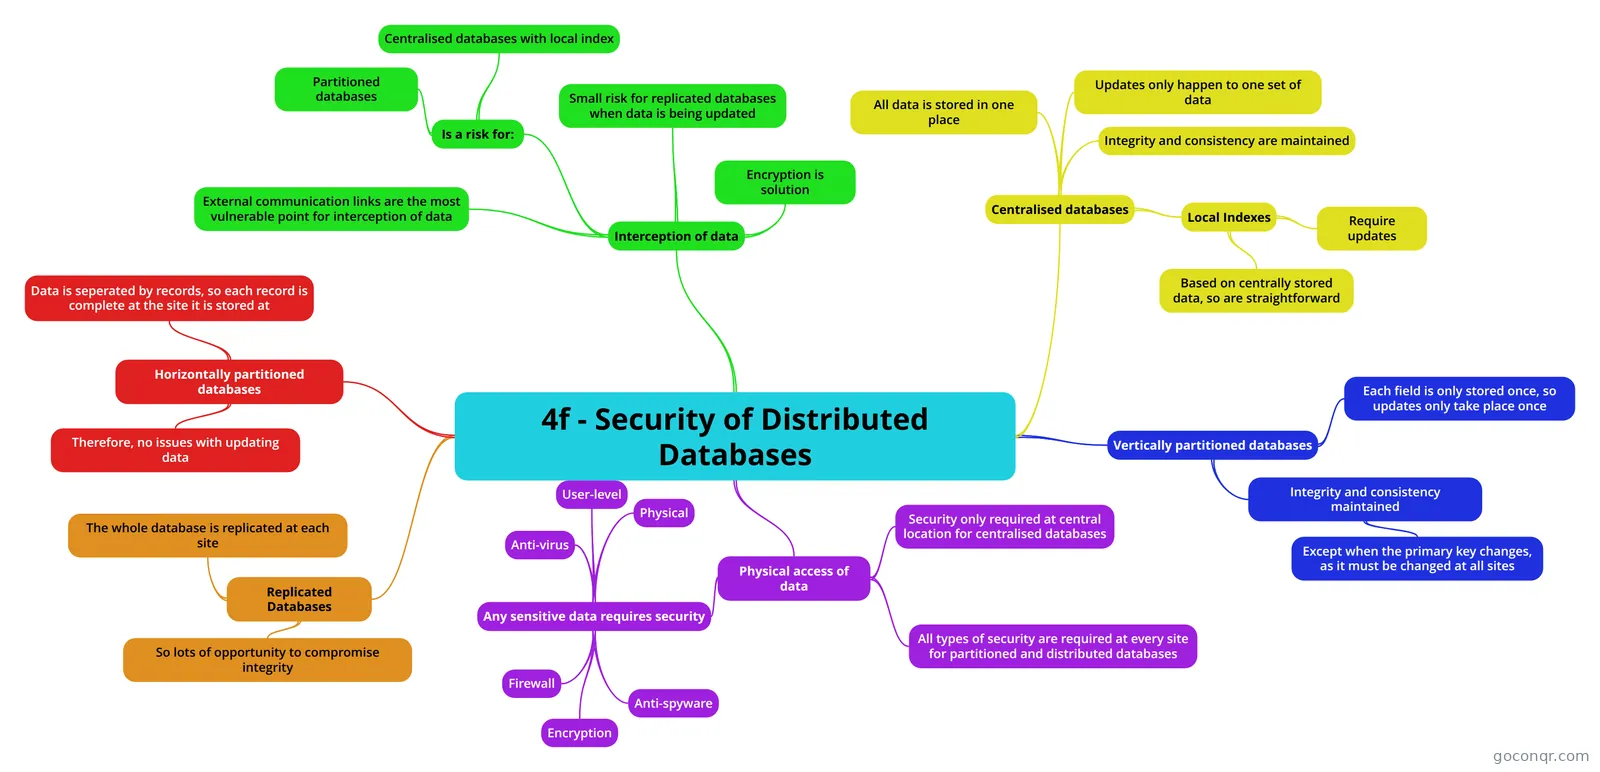
Mind map: security of distributed databases
Map content
4f - Security of Distributed Databases
Interception of data
- External communication links are the most vulnerable point for interception of data
- Is a risk for:
- Partitioned databases
- Centralised databases with local index
- Small risk for replicated databases when data is being updated
- Encryption is solution
Physical access of data
- Any sensitive data requires security
- Physical
- User-level
- Anti-virus
- Firewall
- Anti-spyware
- Encryption
- Security only required at central location for centralised databases
- All types of security are required at every site for partitioned and distributed databases
- Any sensitive data requires security
Centralised databases
- All data is stored in one place
- Updates only happen to one set of data
- Integrity and consistency are maintained
- Local Indexes
- Require updates
- Based on centrally stored data, so are straightforward
Vertically partitioned databases
- Each field is only stored once, so updates only take place once
- Integrity and consistency maintained
- Except when the primary key changes, as it must be changed at all sites
Horizontally partitioned databases
- Data is seperated by records, so each record is complete at the site it is stored at
- Therefore, no issues with updating data
Replicated Databases
- The whole database is replicated at each site
- So lots of opportunity to compromise integrity
Information
- Description
- Mind Map on 4f - Security of Distributed Databases, created by James_Dove on 30/03/2015.
- Created by
- James_Dove
- Views
- 5
- Rating