
Mind map
CHAPTER 2: CRYPTOGRAPHIC TOOLS
Map content
CHAPTER 2: CRYPTOGRAPHIC TOOLS
2.1 CONFIDENTIALITY W/ SYMMETRIC ENCRYPTION
- Symmetric Encryption a.k.a. single-key encryption
- the universal technique for providing confidentiality for transmitted @ stored data
- 5 ingredients o symmetric encryption scheme
- Plaintext
- Encryption algorithm
- Secret key
- Ciphertext
- Decryption algorithm
- 2 requirements for secure use:
- i) need a strong encryption algorithm
- ii) sender & receiver must have obtained copies of the secret key in a secure fashion and must keep the key secure
- Attacking Symmetric Encryption
- 1.Cryptanalytic Attacks
- a) Rely on: - nature of the algorithm
- b) Exploits the character of the algorithm to attempt to deduce a specific plaintext @ the key being used
- 2.Brute-Force Attack - Try all possible keys on some ciphertext until an intelligible transation into plaintext is obtained
- 1.Cryptanalytic Attacks
- Symmetric Block Encryption Algorithms
- Data Encryption Standard (DES)
- 2.Strength concerns: - concerns about algorithm - use of 56-bit key
- 1.The most widely used encryption scheme a.k.a. Data Encryption Algorithm (DEA) - FIPS PUB 46
- Triple DES (3DES)
- 1.Repeats basic DES algorithm 3 times using either 2 @ 3 unique keys
- 2.1st standardized for use in financial apps. in ANSI standard X9.17 in 1985
- 3.Attractions: - underlying encryption algorithm is the same as in DES
- 4.Drawbacks: - uses a 64-bit block size
- Advanced Encryption Standard (AES)
- 1.Needed a replacement for 3DES
- 2.NIST called for proposals for a new AES in 1997
- 3.Selected Rijndael in Nov. 2001
- Practical Security Issues
- 1.Typically symmetric encryption is applied to a unit of data larger than a single 64-bit @ 128-bit block
- 2.Electronic codebook (ECB) mode is the simplest approach to multiple-block encryption
- 3.Modes of operation
- Data Encryption Standard (DES)
- Stream Cipher - produces output 1 element at a time - encrypts plaintext 1 byte at a time
- Block Cipher - produces an output block for each input block - can reuse keys
- Symmetric Encryption a.k.a. single-key encryption
2.2 MSG. AUTHENTICATION & HASH FUNCTIONS
- Msg. Authentication
- 1. Protects against active attacks
- 2. Verifies received msg is authentic
- 3. Can use conventional encryption
- Hash Function Requirements
- 1.Can be applied to a block of data of any size
- 2.Produces a fixed-length output
- 3.H(x) is relatively easy to compute for any given x
- 4.One-way @ pre-image resistant
- 6.Collision resistant @ strong collision resistance
- 5.Computationally infeasible to find y ≠ x such that H(y) = H(x)
- Security of Hash Functions
- 1.There are 2 approaches to attacking a secure hash functions: - cyptanalysis - brute-force attacks
- 2.SHA most widely used hash algorithm
- 3.Additional secure hash function apps. - passwords - intrusion detection
- Msg. Authentication
2.3 PUBLIC KEY ENCRYPTION
- Public-Key Encryption Structure
- 1.Publicly proposed by Diffie & Hellman in 1976
- 2.Based on mathematical functions
- 3.Asymmetric
- 4.Some form of protocol is needed for distribution
- 5 ingredients of a public-key encryption scheme
- Plaintext
- Encryption algorithm
- Public & private keys
- Cipher text
- Decryption key
- Requirements for Public-Key Cryptosystems
- 2.Computationally for sender knowing public key to encrypt messages
- 3.Computationally easy for receiver knowing private key to decrypt cipher text
- 4.Computationally infeasible for opponent to determine private key from public key
- 5.Computationally infeasible for opponent to otherwise recover original message
- 6.Useful if either key can be used for each role
- 1.Computationally easy to create key pairs
- Asymmetric Encryption Algorithms
- 1.RSA (Rivest, Shamir, Adleman)
- 2.Diffie-Hellman key exchange algorithm
- 3.Digital Signature Standard (DSS)
- 4.Elliptic Curve Cryptography (ECC)
- Public-Key Encryption Structure
2.4 DIGITAL SIGNATURES & KEY MGT.
- Digital Signatures
- used for authenticating both source & data integrity
- created by encrypting hash code with private key
- does not provide confidentiality
- Digital Envelopes
- protects a msg. w/out needing to first arrange for sender & receiver to have the same secret key
- equates to the same thing as a sealed envelope containing an unsigned letter
- Digital Signatures
2.5 RANDOM & PSEUDORANDOM NUMBERS
- Random Numbers Uses include generation of:
- keys for public-key algorithms
- stream key for symmetric stream cipher
- session key
- Random Number Requirements
- 1.Randomness Criteria - uniform distribution - independence
- 2.Unpredictability - each number is statistically independent of others numbers in the sequence
- Random vs. Pseudorandom
- 1.Cryptographic apps. typically make use of algorithmic techniques for random no. generation
- 2.Pseudorandom numbers are: - sequences produced that satisfy statistical randomness tests
- 3.True random number generator (TRNG) - uses nondeterministic source to produce randomness
- Random Numbers Uses include generation of:
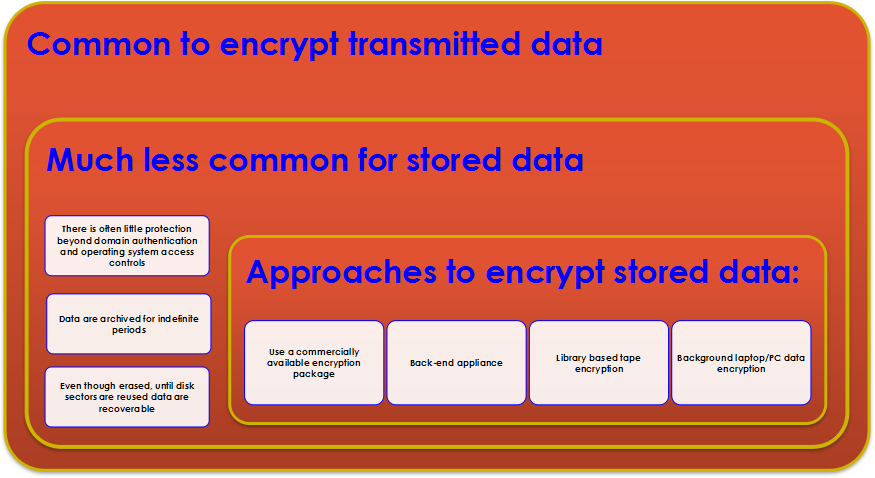
2.6 PRACTICAL APPS. ENCRYPTION OF STORED DATA
Images and files in the map
Information
- Description
- Network Security Mind Map on CHAPTER 2: CRYPTOGRAPHIC TOOLS, created by Nurmarahain Abdull Rahman on 03/11/2016.
- Created by
- Nurmarahain Abdull Rahman
- Views
- 0
- Rating