
Flashcards
System Admin - Intro to cryptography
Cards in this deck (29)
- 1What is cryptography?The process of hiding the meaning of words by changing plain text to ciphertext
- 2What is plaintext?The message in its unencrypted form, conventionally written in lowercase letters
- 3What is ciphertext?The sequence of characters that are actually sent, conventionally written in UPPERCASE letters
- 4What are the two ways to change plaintext in ciphertext?Transposition or substitution
- 5What are transposition ciphers and name an example ?The letters of a message are rearranged one example of this is Rail Fence
- 6How do you generate a transposition ciphertext?The plaintext characters are written alternately on 2 lines and then the lines are joined together, e.g
(First line) t c a d w
(Second line) t a k t a n
(Cipertext) tcadwtaktan - 7How doeS the recipent recover The transposition plaintext?By reversing what was done when creating the ciphertext
- 8What is substitution ciphers?Each letter in the plaintext is substituted by another letter to generate the ciphertext
- 9What is an example of cryptography using substitution and how is it used?Caesar shift
Plain text = attack at dawn
Cipher text = xqqxzh xq axtk - 10How would a recipient read the original message?Same with transposition reverse the process
- 11Both these ciphers are examples of symmetric cryptography what is this?if you know the key and the algorithm then just reverse the encryption process to decrypt the received message.
- 12What are the advantages and disadvantages of symmetric cryptography?+ it is quick to both encrypt & decrypt
- if an enemy/spy works out the algorithm they can decrypt any ciphertext they capture e.g. Shift alphabet and key along by 3 places anyone can figure it out and try all possible shifts to work out the key. - 13How could the sender make it harder for a enemy to capture the message?by changing the key for different letters of the message e.g. Enigma cipher
- 14why is the concept of timeliness important?if by the time the attacker has worked out the key it is no longer useful then the process used is sufficiently secure. the more keys there are the longer it will take the attacker to find the right one
- 15What are modern symmetric algorithms?are designed to be used with computers and manipulate bits rather than whole characters. 2 examples are:
DATA ENCRYPTION STANDARD (DES) - first used in 1977, only practical method to find the key is to try all possible keys.
ADVANCED ENCRYPTION STANDARD (AES) - first used in 2002, keys can be 128-, 192, or 256 bits long ( longer key = greater security) very fast algorithm in hardware and software. - 16What are the key features of modern symmetric algorithms?1. both are BLOCK CIPHERS- data is ciphered in chunks of bits called blocks
2. each block of bits is mixed with a round key and the output is put through a substitution and permutation process called round.
3. each block is put through a number of rounds each using a different round key which increases the strength of encryption
4. decryption is done by reversing the process. - 17current issues with cryptography?DES key only 56 bits long, so it can be easily and quickly enough to be useful to an attacker so no longer secure
AES may be considered secure however side channel attacks have been identified - 18essential points to consider in cryptography- keeping the key secret is crucial
- in an online world, for practical reasons keys have to be sent over the network which is insecure
- how do we send keys over such a network? A solution is PUBLIC KEY CRYPTOGRAPHY - 19What is public key cryptography and what is the earliest example?where multiple keys are used.
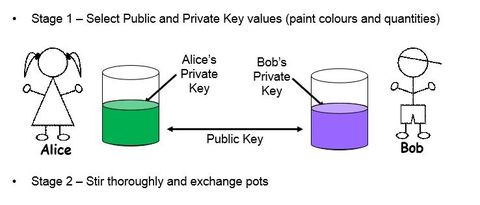
the earliest example of public key cryptography is Diffie-Hellamn Key Exchange which can be used over an insecure network to agree a secret key that can be used with a symmetric encryption algorithm - 20Diffie-Hellman Key Exchange illlustration 1
- 21Diffie-Hellman Key Exchange illlustration 2
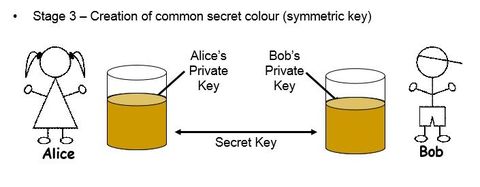
- 22Diffie- Hellamn Key exchange uses three keys:1. A public key both Alice and Bob share
2. A private key known only to Alice
3. A private key known only to Bob - 23issues with diffie-hellamn exchange- Alice and Bob do not prove their identities to each other before communication starts, therefore allowing the possibility of a man in the middle attack.. The solution is to use a PUBLIC KEY INFRASTRUCTURE
- 24What is a public key infrastructure?A PKI is a set of hardware, software, people, policies and procedures needed to create, manage, distribute, use, store and issue digital certificates.
- 25what does a PKI consist of?- A certificate authority (CA) which issues and verifies digital certificates
- A registration authority to verify identities of applicants
- A central directory to store certificates
- A certificate management system
- A certificate policy
WELL KNOWN CA IS VERISIGN - 26what is public key cryptography?often referred to as asymmetric cryptography because 2 keys are used, one to encrypt and the other to decrypt.
- 27What is a digital signature?provide proof or origin of digital documents e.g. digital certificates
- 28what is a message digest?is created of the contents of the certificate using a cryptographic hash function which are mathematical algorithms that produce an output of fixed length for an input of variable length. all hash functions are easy to compute. but cryptographic hash functions aren't.
- 29comments on Public key cryptography-public key cryptography is computationally expensive- usually only used to to secure transfer of keys. bulk data is encrypted using strong symmetric encryption.
-private key must be kept secure as it can be lost or stolen and may be the subject of key escrow
- PKI is a mathematical process it only confirms that the correct key has been used, it does not confirm that the user of that key is who they claim to be.
Information
- Description
- Flashcards on System Admin - Intro to cryptography , created by Robena786 on 09/05/2015.
- Created by
- Robena786
- Views
- 2
- Rating