
Notes
Identity and Access Services
Content of the notes (13)
Page 1
Authorisation
Definition
function of specifying access rights and privileges to resources related to information security
process of ensuring only users who are suppose to have access to certain resources are given access
Page 2
Mandatory Access Control
Definition
based on the idea of security clearance levels
object (resource) and each subject (user/process) is granted a clearance level
are only permitted to access objects at their own clearance level or below
Page 3
Discretionary Access Control (DAC)
Definition
stresses the importance of the owner
granted full control over the resource and is able to grant rights to others
most flexible model
the weakest due to centralized administration of security policies the most difficult to enforce
Page 4
Role-based Access Control (RBAC)
set of organizational roles are defined and users allocated to those roles
gain rights implicitly through being assigned to a role
right to modify roles is reserved to administrative accounts not users
Page 5
Rule-based Access Control (RBAC)
Definition
can refer to any sort of access control model where access control policies are determined by system-enforced rules rather than system users
increasingly being implemented to protect computer and network systems founded on discretionary access from the sort of misconfiguration that can occur through DAC
privileges are restricted, regardless of the user's identity
Page 6
Separation of Duties
Definition
concept of having more than one person required to complete a task.
disseminating the tasks and associated privileges for a specific business process among multiple users
Page 7
Basic Authorisation Principles
Implicit Deny
any request for access is denied unless stated otherwise
Least Privilege
granted rights necessary to perform their job and no more
Single Sign on
authenticate to a system once to gain access to all the resources to which the user has been granted rights
Page 8
Directory Services
Definition
principal means of providing privilege management and authorization
provides a directory services infrastructure that can help organizations manage resources throughout the network
network directory that contains objects and resources
Common Directory Services
Microsoft Active Directory
Sun Java System Directory Server
OpenDS
OpenLDAP
Open Directory
Page 9
LDAP
Definition
not a directory standard
used to query and update a directory
Page 10
RADIUS
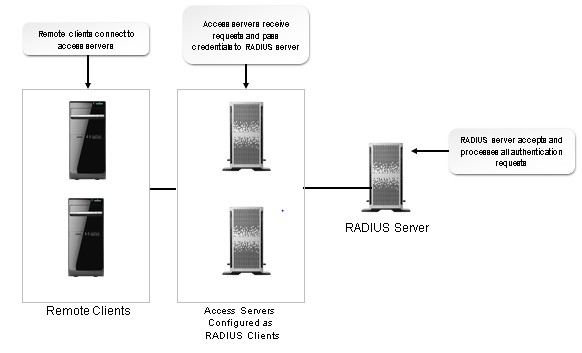
a networking protocol that provides centralized Authentication, Authorization, and Accounting management
was principally used by ISPs to transmit authentication credentials
provides authorization for the connection of devices to Ethernet switch ports and wireless access points
Page 11
TACACS+
family of related protocols handling remote authentication and related services for networked access control through a centralized server
provides centralized authentication and authorization services for remote users
supports multi-factor authentication
accepts login requests and authenticates access credentials
encrypts entire authentication process
includes process-wide encryption for authentication.
replaces TACACS and XTACACS
Page 12
Attacks on Directory Services
Causes Loss(CIA)
confidentiality of the information (read access)
integrity of the information (write access)
access (Denial of Service, preventing network access)
Minimize Risks(ELUL)
limit physical access to Directory Services server
limit the number of Administrators
use separate Administrative Accounts from User Accounts
enforce Strong Password Rules
Page 13
Attacks on LDAP
Why
LDAP provides no security and all transmissions are in plaintext
vulnerable to sniffing and Man-in-the-Middle attacks
vulnerable to overloading by DoS attacks if server that does not require clients to authenticate
Mitigate
disable anonymous and simple authentication access methods
use Kerberos and LDAP for secure communication
use LDAP
Information
- Description
- Information Security (Identity and Access Services) Note on Identity and Access Services, created by Wesley Qua on 10/12/2018.
- Created by
- Wesley Qua
- Views
- 1
- Rating